
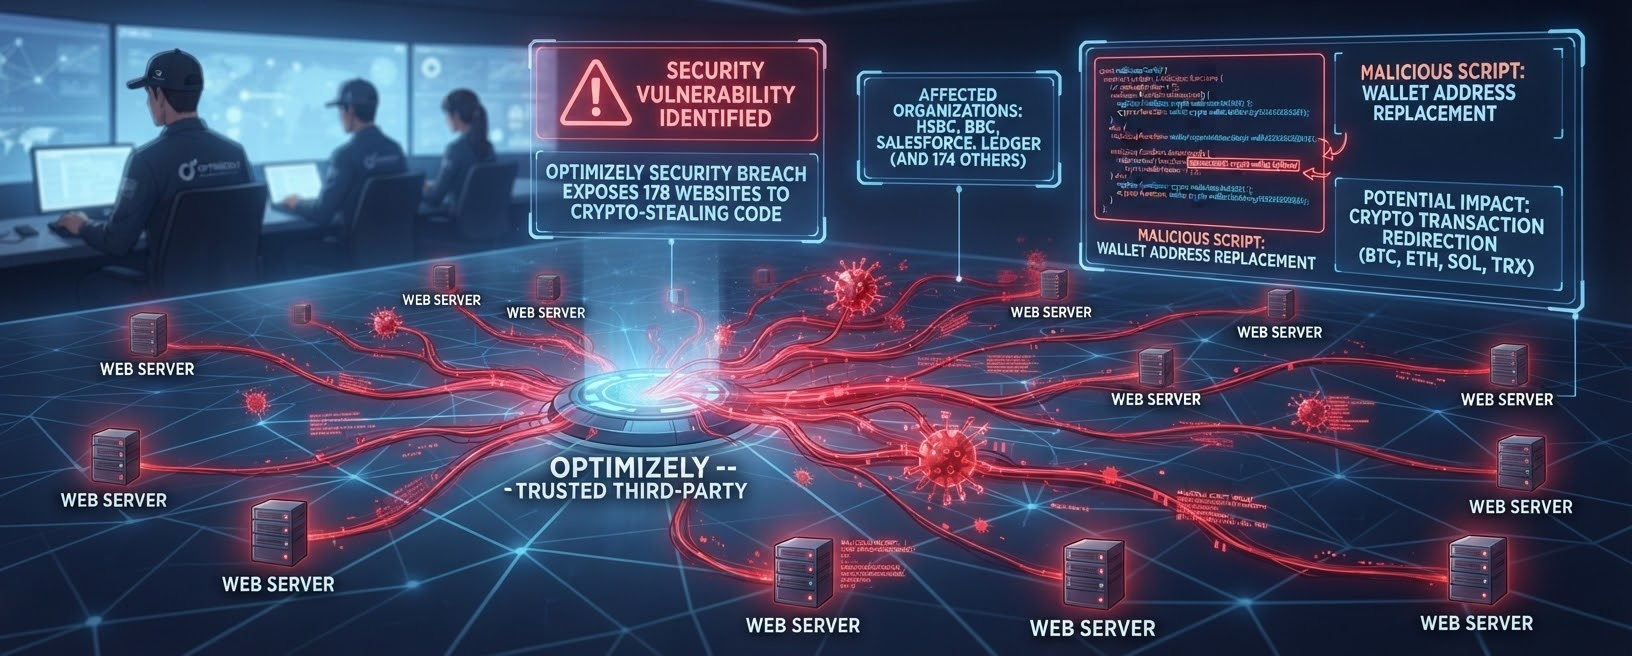

A security vulnerability involving web-testing provider Optimizely allowed malicious crypto-stealing code to appear on websites belonging to 178 organizations on November 16, including HSBC, BBC, Salesforce, and Ledger. The affected websites were not directly hacked. Instead, attackers exploited a trusted third-party script that replaced wallet addresses in forms and copied text, potentially redirecting cryptocurrency transactions across Bitcoin, Ethereum, Solana, Tron, and several other networks. $BTC

According to the report, the attackers collected approximately $7,040, a relatively small amount compared with the scale of the incident. Optimizely stated that the malicious code had been removed and the vulnerability fixed. However, the incident highlights a broader security concern: compromising a single trusted vendor can expose hundreds of websites and their visitors. Similar supply-chain attacks have occurred before, including the 2023 Ledger Connect Kit incident, which resulted in approximately $600,000 in losses, and the 2025 npm package compromise that affected software packages with billions of weekly downloads. $ETH

Although the limited financial losses may indicate that wallet checks and rapid remediation helped contain the damage, Hudson Rock reportedly identified similar malicious code across three other web services. This suggests that the threat may extend beyond a single vendor or incident. The case raises an important question about responsibility when trusted websites unknowingly distribute malicious scripts: should accountability fall on the website operators, third-party vendors, or both? $SOL

Ultimately, this incident demonstrates how vulnerable the crypto ecosystem can be to software supply-chain attacks. Even websites operated by well-known organizations can become channels for wallet manipulation when third-party tools are compromised. Users and businesses alike need stronger security checks for external scripts and should always verify wallet addresses before confirming transactions.