

#tradertraitor
tradertraitor
4,567 views
9 Discussing
Hot
Latest

·
--
Article
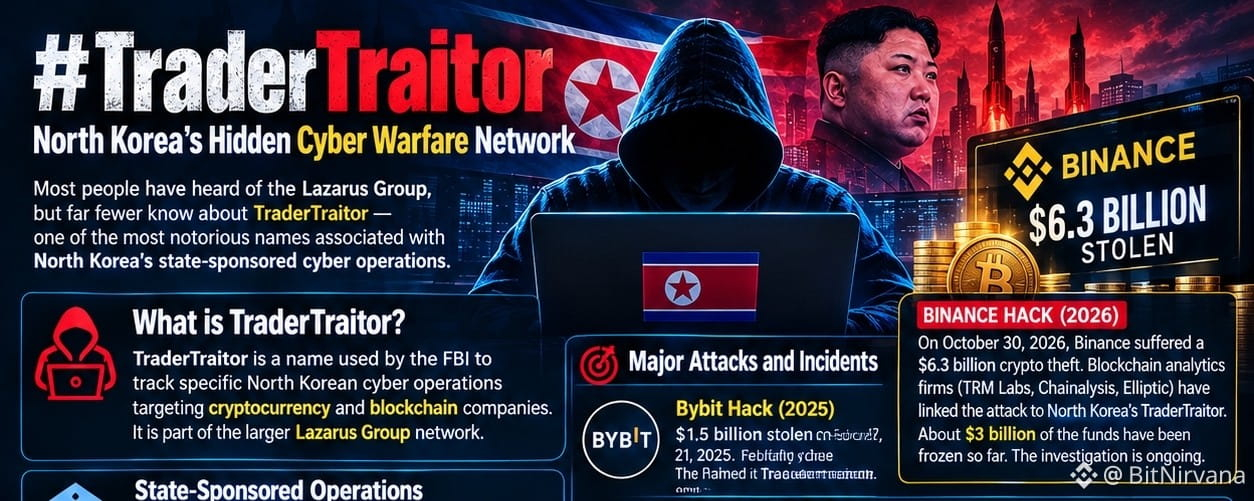
TraderTraitor: North Korea’s Hidden Cyber Warfare Network 🇰🇵Most people have heard of the Lazarus Group, but far fewer know about TraderTraitor — one of the most notorious names associated with North Korea’s state-sponsored cyber operations.
TraderTraitor is not an ordinary hacking group. It is a name used by the FBI to track specific North Korean cyber operations targeting cryptocurrency and blockchain companies.
Here is what makes this group so significant:
🔹 State-Sponsored Operations
The FBI, CISA, and U.S. Treasury have identified TraderTraitor as North Korean state-sponsored cyber activity. It is also associated with the broader Lazarus Group ecosystem.
🔹 Connections to North Korea’s Intelligence Agency
In September 2019, the U.S. Treasury identified Lazarus Group as a North Korean government-controlled entity connected to the Reconnaissance General Bureau (RGB), the country's primary intelligence agency.
🔹 The $1.5 Billion Bybit Hack
On February 21, 2025, Bybit suffered a massive cryptocurrency theft worth approximately $1.5 billion.
On February 26, 2025, the FBI officially attributed the attack to North Korea and referred to the specific malicious cyber activity as TraderTraitor.
🔹 The $308 Million DMM Bitcoin Theft
In May 2024, North Korean cyber actors associated with TraderTraitor stole approximately $308 million from Japan-based DMM Bitcoin.
Investigators revealed that the attackers used a fake LinkedIn recruiter identity and a malicious coding test to compromise an employee.
🔹 A Much Longer History
North Korean cyber operations have also been linked to several major incidents:
• 2016 Bangladesh Bank heist — approximately $81 million stolen, involving Lazarus Group and its associated financial cyber operations.
• 2014 Sony Pictures cyberattack — attributed to North Korea by the FBI and linked to Lazarus Group.
• 2022 Axie Infinity Ronin Bridge hack — approximately $620 million stolen, attributed to Lazarus Group by the FBI.
🔹 Where Does the Money Go?
According to the U.S. Treasury, North Korea uses illicit cyber operations and cryptocurrency theft to generate revenue for the regime, including funding its weapons of mass destruction and ballistic missile programs.
The exact amount of stolen money that reaches specific government programs is difficult to independently establish.
The Bigger Picture
TraderTraitor represents a growing challenge for the global cryptocurrency industry.
These operations do not always begin with sophisticated code. Sometimes, they start with a fake job offer, a LinkedIn message, or a seemingly harmless coding test.
The lesson is clear:
In crypto, the biggest security threat may not always be a smart contract vulnerability. Sometimes, it is the person you trust.
#TraderTraitor #LazarusGroup #NorthKorea #CyberSecurity #CryptoSecurity #Bybit #Blockchain #CyberWarfare
TraderTraitor: North Korea’s Hidden Cyber Warfare Network 🇰🇵
Most people have heard of the Lazarus Group, but far fewer know about TraderTraitor — one of the most notorious names associated with North Korea’s state-sponsored cyber operations.
TraderTraitor is not an ordinary hacking group. It is a name used by the FBI to track specific North Korean cyber operations targeting cryptocurrency and blockchain companies.
Here is what makes this group so significant:
🔹 State-Sponsored Operations
The FBI, CISA, and U.S. Treasury have identified TraderTraitor as North Korean state-sponsored cyber activity. It is also associated with the broader Lazarus Group ecosystem.
🔹 Connections to North Korea’s Intelligence Agency
In September 2019, the U.S. Treasury identified Lazarus Group as a North Korean government-controlled entity connected to the Reconnaissance General Bureau (RGB), the country's primary intelligence agency.
🔹 The $1.5 Billion Bybit Hack
On February 21, 2025, Bybit suffered a massive cryptocurrency theft worth approximately $1.5 billion.
On February 26, 2025, the FBI officially attributed the attack to North Korea and referred to the specific malicious cyber activity as TraderTraitor.
🔹 The $308 Million DMM Bitcoin Theft
In May 2024, North Korean cyber actors associated with TraderTraitor stole approximately $308 million from Japan-based DMM Bitcoin.
Investigators revealed that the attackers used a fake LinkedIn recruiter identity and a malicious coding test to compromise an employee.
🔹 A Much Longer History
North Korean cyber operations have also been linked to several major incidents:
• 2016 Bangladesh Bank heist — approximately $81 million stolen, involving Lazarus Group and its associated financial cyber operations.
• 2014 Sony Pictures cyberattack — attributed to North Korea by the FBI and linked to Lazarus Group.
• 2022 Axie Infinity Ronin Bridge hack — approximately $620 million stolen, attributed to Lazarus Group by the FBI.
🔹 Where Does the Money Go?
According to the U.S. Treasury, North Korea uses illicit cyber operations and cryptocurrency theft to generate revenue for the regime, including funding its weapons of mass destruction and ballistic missile programs.
The exact amount of stolen money that reaches specific government programs is difficult to independently establish.
The Bigger Picture
TraderTraitor represents a growing challenge for the global cryptocurrency industry.
These operations do not always begin with sophisticated code. Sometimes, they start with a fake job offer, a LinkedIn message, or a seemingly harmless coding test.
The lesson is clear:
In crypto, the biggest security threat may not always be a smart contract vulnerability. Sometimes, it is the person you trust.
#TraderTraitor #LazarusGroup #NorthKorea #CyberSecurity #CryptoSecurity #Bybit #Blockchain #CyberWarfare
1
132

·
--
Put simply, this wasn’t a case of private keys being stolen—the signing system was used as an ATM. TRM Labs’ timeline: the attack began at 20:05 UTC on October 29. In 20 minutes, $6.36 billion was moved out of Binance wallets across 10 chains—more than four times the $1.5 billion stolen from Bybit. Binance’s preliminary investigation lines up: an operations engineer’s computer was hacked, and the attacker got into an internal service container and submitted withdrawal requests. No private key leak was found. The wildest part was on Ethereum: the attacker got Binance’s signing system to approve 50 EIP-7702 authorizations in one go, arranged sequentially so one was bound to hit. Binance 14 instantly became the attacker’s vacuum cleaner, sweeping up 167,464 $ETH and 1.615 billion USDT in a single transaction, leaving just 1 ETH behind. After the wallet was replenished, it was swept again. TRM and Chainalysis both point to North Korea’s TraderTraitor, though Binance hasn’t named anyone yet. The roughly $3 billion frozen was all in freezeable stablecoins: Tether froze $1.567 billion, and Circle froze over $800 million. The roughly $2.4 billion in unfreezable $BTC and $ETH is already gone. SAFU holds 15,000 $BTC worth about $1.2 billion—less than a fifth of the losses. The rest will have to be covered by Binance’s own reserves. This is just my personal opinion, for reference only. Once withdrawals resume, will you withdraw to self-custody right away, or keep your funds on Binance and bet it will make everyone whole? Pick a side in the comments.
#$1.5BInLeveragedCryptoBetsLiquidated #BinanceSecurityIncident #TraderTraitor #EIP7702
#$1.5BInLeveragedCryptoBetsLiquidated #BinanceSecurityIncident #TraderTraitor #EIP7702
Padfoot:
先别急着站队,63.6亿这种级别得核对官方公告和链上证据😂 吃瓜可以,别让假瓜把自己的钱包吓跑了。
1
2
1.3k
·
--
Analysts link the attack to the North Korean group TraderTraitor, which was also behind the $1.5 billion Bybit hack in 2025. ZachXBT writes that funds from the Binance and Bitget hacks were mixed through THORChain, keeping $RUNE in the spotlight. These are investigators’ theories, not final conclusions. But one conclusion is already clear: hackers are shifting from looking for bugs in code to attacking people and infrastructure. For $BTC holders, this is another reason to check their own security.
Do you store $BTC on an exchange or in a cold wallet? 👇
#TraderTraitor
Do you store $BTC on an exchange or in a cold wallet? 👇
#TraderTraitor
50
🚨 EXPOSED: Who Hacked Binance? 🚨
This was NOT a normal hacker! 👇
🔴 Hacker Name: TraderTraitor
🔴 Country: North Korea's Elite Government Hacking Unit
🔴 This group has already stolen $2 Billion+ in crypto before!
💻 How they hacked?
- Hacked a Binance DevOps Engineer's laptop
- Gained access to internal service container
- Stole $6.3 BILLION in just 20 MINUTES!
- $1.5B in Bitcoin + $900M in Ethereum
Binance said: "This was not a one-click attack, it was a highly complex process"
$3 Billion has been frozen so far, rest hacker is laundering via Uniswap & Aave.
If Binance can be hacked, are WE safe? 🤔
Comment your thoughts!
#BinanceHack #NorthKorea #TraderTraitor #CryptoHack #Binance

143

·
--
🚨 THE DARK SIDE OF CYBER WARFARE! 🇰🇵 🇰🇵 🇰🇵 🇰🇵 🇰🇵 🇰🇵 🇰🇵 🇰🇵 🇰🇵 🇰🇵
North Korea-linked hacking groups are drawing global attention in the cryptocurrency world.
The name TraderTraitor has been linked to cyber threats targeting the crypto industry.
Is this just cybercrime, or a much bigger geopolitical game? 🌍
🔐 Cybersecurity is no longer optional. Stay alert, protect your assets, and stay SAFU!
#Binance #NorthKorea #TraderTraitor #CyberSecurity #Crypto #Blockchain #SAFU🙏
#KOSPIFalls3.53%BackBelow6000

1
74
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#UniswapA16zSeekDeFiExemptionFromIllinoisCryptoTax
22,332 views
711 Discussing
2
#HKDollarStablecoinHKDAPToLaunchOnSolana
15,978 views
448 Discussing
3
#$1.5BInLeveragedCryptoBetsLiquidated
35,290 views
240 Discussing
4
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
2,483 views
64 Discussing
5
#KOSPIFalls3.53%BackBelow6000
60,479 views
1,070 Discussing
6
#AmazonSharesFallAbout7%InPremarketTrading
26,968 views
572 Discussing
7
#USMidtermElections
234,140 views
2,329 Discussing
8
#StrategySTRCReaches$99.95ForFirstTimeIn165Days
23,199 views
93 Discussing
9
#BinanceWillListPredictPREDICT
90,029 views
1,373 Discussing
10
#SwitzerlandFirstSpotBitcoinETFExpectedToTradeInNovember
3,049 views
107 Discussing