
#snark
snark
1,530 views
6 Discussing
Hot
Latest

·
--
📰 What Vitalik discussed this time was not short-term market trends, but whether the computational cost of cryptography can keep being pushed down.
He believes that SNARKs, fully homomorphic encryption (FHE), and indistinguishable obfuscation (iO) all have a chance to bring the extra overhead below 10x by the end of this decade. This is calculated not from the price of a single piece of hardware, but from energy costs plus amortized computation costs.
🔥 The more aggressive judgment is that each of the three has a 33% chance of reaching the "1+ε" level. In other words, when the scale of computation is large enough, the cost added by encrypted processing may gradually approach the cost of the original computation itself.
💡 For all three technologies to get below 10x overhead, he gives it a 60% probability. But the one most likely to first achieve single-digit overhead, Vitalik thinks, may be SNARKs.
To be honest, this judgment is still his own non-consensus view, not something that has already been realized. Dedicated hash functions and some large language model inference have already reached a similar level, which at least shows that this path is not entirely confined to paper.
🤔 If SNARKs really push computational overhead down to single-digit multiples by the end of this decade, what do you think will change first: blockchain verification, or privacy-preserving computing?
#SNARK #以太坊 #密码学 #隐私计算
📰 What Vitalik discussed this time was not short-term market trends, but whether the computational cost of cryptography can keep being pushed down.
He believes that SNARKs, fully homomorphic encryption (FHE), and indistinguishable obfuscation (iO) all have a chance to bring the extra overhead below 10x by the end of this decade. This is calculated not from the price of a single piece of hardware, but from energy costs plus amortized computation costs.
🔥 The more aggressive judgment is that each of the three has a 33% chance of reaching the "1+ε" level. In other words, when the scale of computation is large enough, the cost added by encrypted processing may gradually approach the cost of the original computation itself.
💡 For all three technologies to get below 10x overhead, he gives it a 60% probability. But the one most likely to first achieve single-digit overhead, Vitalik thinks, may be SNARKs.
To be honest, this judgment is still his own non-consensus view, not something that has already been realized. Dedicated hash functions and some large language model inference have already reached a similar level, which at least shows that this path is not entirely confined to paper.
🤔 If SNARKs really push computational overhead down to single-digit multiples by the end of this decade, what do you think will change first: blockchain verification, or privacy-preserving computing?
#SNARK #以太坊 #密码学 #隐私计算
He believes that SNARKs, fully homomorphic encryption (FHE), and indistinguishable obfuscation (iO) all have a chance to bring the extra overhead below 10x by the end of this decade. This is calculated not from the price of a single piece of hardware, but from energy costs plus amortized computation costs.
🔥 The more aggressive judgment is that each of the three has a 33% chance of reaching the "1+ε" level. In other words, when the scale of computation is large enough, the cost added by encrypted processing may gradually approach the cost of the original computation itself.
💡 For all three technologies to get below 10x overhead, he gives it a 60% probability. But the one most likely to first achieve single-digit overhead, Vitalik thinks, may be SNARKs.
To be honest, this judgment is still his own non-consensus view, not something that has already been realized. Dedicated hash functions and some large language model inference have already reached a similar level, which at least shows that this path is not entirely confined to paper.
🤔 If SNARKs really push computational overhead down to single-digit multiples by the end of this decade, what do you think will change first: blockchain verification, or privacy-preserving computing?
#SNARK #以太坊 #密码学 #隐私计算
5
·
--
𝗔𝗹𝗽𝗵𝗮: 𝗲𝘀𝗽𝗿𝗲𝘀𝘀𝗼𝗙𝗡𝗗𝗡 𝗷𝘂𝘀𝘁 𝗽𝗿𝗼𝘃𝗲𝗱 𝗦𝗡𝗔𝗥𝗞 𝘁𝗵𝗿𝗼𝘂𝗴𝗵𝗽𝘂𝘁 𝘁𝗵𝗮𝘁 𝗼𝘁𝗵𝗲𝗿𝘀 𝗰𝗮𝗻’𝘁 𝗺𝗮𝘁𝗰𝗵 🚀 𝗿𝗲𝗹𝗮𝘁𝗶𝘃𝗲 𝘃𝗮𝗹𝘂𝗲 𝗶𝘀 𝗰𝗮𝘁𝗰𝗵𝗶𝗻𝗴 𝘂𝗽 𝗳𝗮𝘀𝘁
Faster prover → consensus stays tight + fewer bottlenecks, so $ESP has real asymmetric upside vs similar launches
If the market wakes up, this is next 10x then 100x potential
@espressoFNDN #crypto #ZK #SNARK ⚠️
𝗔𝗹𝗽𝗵𝗮: 𝗲𝘀𝗽𝗿𝗲𝘀𝘀𝗼𝗙𝗡𝗗𝗡 𝗷𝘂𝘀𝘁 𝗽𝗿𝗼𝘃𝗲𝗱 𝗦𝗡𝗔𝗥𝗞 𝘁𝗵𝗿𝗼𝘂𝗴𝗵𝗽𝘂𝘁 𝘁𝗵𝗮𝘁 𝗼𝘁𝗵𝗲𝗿𝘀 𝗰𝗮𝗻’𝘁 𝗺𝗮𝘁𝗰𝗵 🚀 𝗿𝗲𝗹𝗮𝘁𝗶𝘃𝗲 𝘃𝗮𝗹𝘂𝗲 𝗶𝘀 𝗰𝗮𝘁𝗰𝗵𝗶𝗻𝗴 𝘂𝗽 𝗳𝗮𝘀𝘁
Faster prover → consensus stays tight + fewer bottlenecks, so $ESP has real asymmetric upside vs similar launches
If the market wakes up, this is next 10x then 100x potential
@espressoFNDN #crypto #ZK #SNARK ⚠️
Faster prover → consensus stays tight + fewer bottlenecks, so $ESP has real asymmetric upside vs similar launches
If the market wakes up, this is next 10x then 100x potential
@espressoFNDN #crypto #ZK #SNARK ⚠️
12

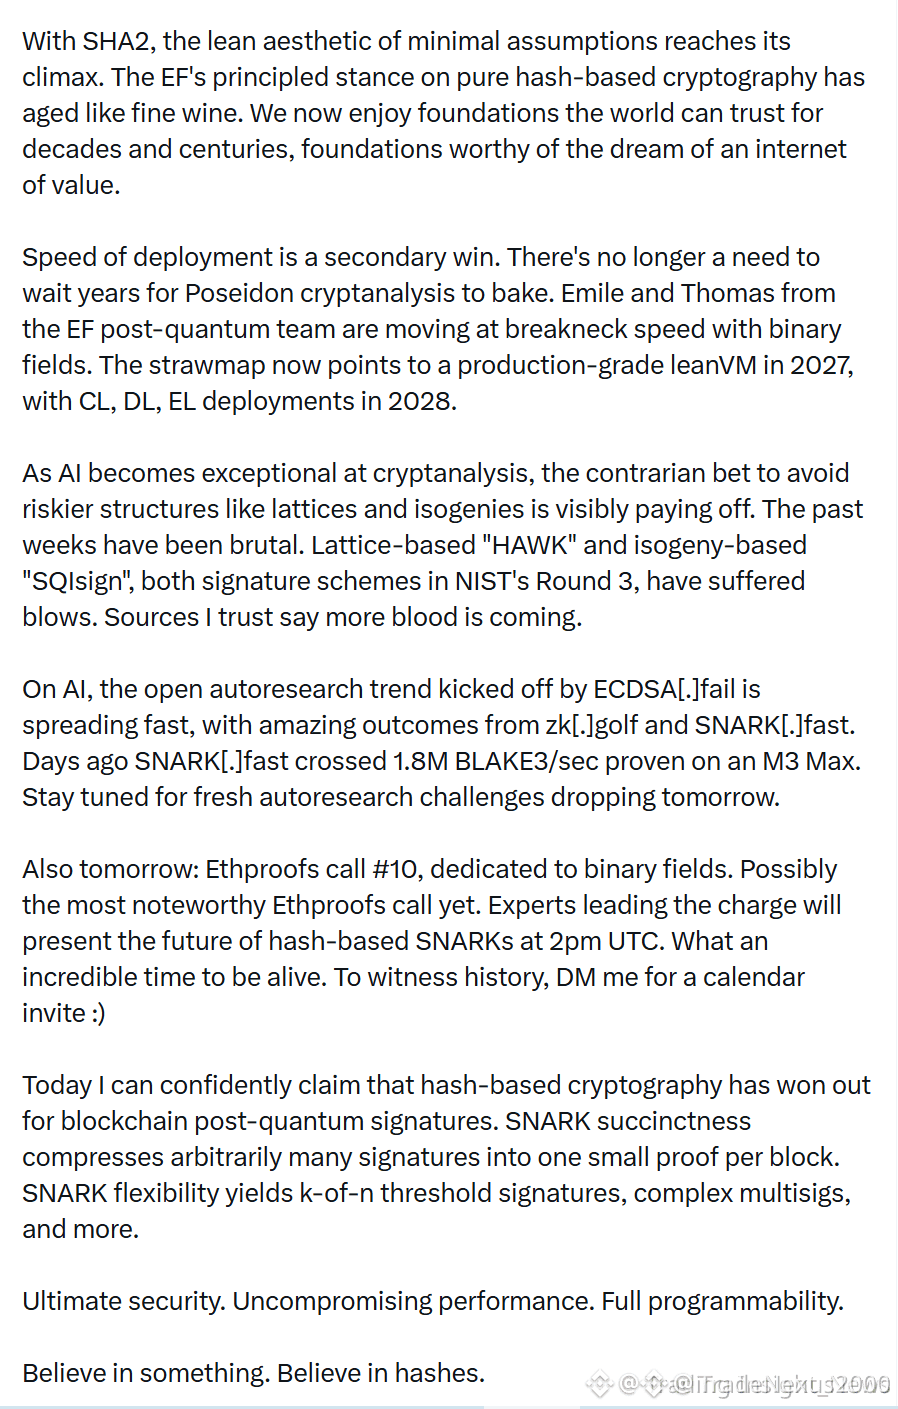
$ETH BETS ON SHA/BLAKE: SNARK INNOVATION FLIPS THE OLD HASH PLAYBOOK 🧠⚙️
The liquidity of innovation often swings toward efficiency, but Ethereum is opting for durability. This isn't a casual tweak; it's a structural pivot away from Poseidon's exotic premises toward the hardened battlefields of SHA and BLAKE. 🛡️
Recent attacks on HAWK and SQIsign validated a deep-seated risk—when novel curves break, the fallout hits every layer. New binary-field SNARKs now push ~1M calls/sec on a laptop, making the ~100x CPU tax on tradition a non-issue. This is smart money securing the post-quantum base camp for the 2027 leanVM and 2028 CL/DL/EL rollout. 🏗️
This feels like a classic range-reclaim of cryptographic standards. Is this a bullish structural signal for Ethereum's long-term execution, or does the added CPU cost slow down domestic rollups? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Ethereum #CryptoNews #SNARK #PostQuantum
📊
$ETH BETS ON SHA/BLAKE: SNARK INNOVATION FLIPS THE OLD HASH PLAYBOOK 🧠⚙️
The liquidity of innovation often swings toward efficiency, but Ethereum is opting for durability. This isn't a casual tweak; it's a structural pivot away from Poseidon's exotic premises toward the hardened battlefields of SHA and BLAKE. 🛡️
Recent attacks on HAWK and SQIsign validated a deep-seated risk—when novel curves break, the fallout hits every layer. New binary-field SNARKs now push ~1M calls/sec on a laptop, making the ~100x CPU tax on tradition a non-issue. This is smart money securing the post-quantum base camp for the 2027 leanVM and 2028 CL/DL/EL rollout. 🏗️
This feels like a classic range-reclaim of cryptographic standards. Is this a bullish structural signal for Ethereum's long-term execution, or does the added CPU cost slow down domestic rollups? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Ethereum #CryptoNews #SNARK #PostQuantum
📊
The liquidity of innovation often swings toward efficiency, but Ethereum is opting for durability. This isn't a casual tweak; it's a structural pivot away from Poseidon's exotic premises toward the hardened battlefields of SHA and BLAKE. 🛡️
Recent attacks on HAWK and SQIsign validated a deep-seated risk—when novel curves break, the fallout hits every layer. New binary-field SNARKs now push ~1M calls/sec on a laptop, making the ~100x CPU tax on tradition a non-issue. This is smart money securing the post-quantum base camp for the 2027 leanVM and 2028 CL/DL/EL rollout. 🏗️
This feels like a classic range-reclaim of cryptographic standards. Is this a bullish structural signal for Ethereum's long-term execution, or does the added CPU cost slow down domestic rollups? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Ethereum #CryptoNews #SNARK #PostQuantum
📊
10
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinReboundsTo$79K
1,877 views
55 Discussing
2
#FedHikeOddsRiseTo89%
52,485 views
873 Discussing
3
#RLUSDSupplyHitsRecord$2.442B
2,619 views
51 Discussing
4
#AvalancheIntegratesIntoUAEPassDigitalVault
56,911 views
894 Discussing
5
#UKSeeksViewsOnTokenizingGold
43,279 views
669 Discussing
6
#AnthropicCEOCallsForAISlowdown
216,401 views
3,186 Discussing
7
#RevolutDataLeakReportedlyPostedAttackersThreatenDailyReleases
4,053 views
84 Discussing
8
#BrazilCentralBankRaisesVASPCapitalRequirements
35,465 views
761 Discussing
9
#BitcoinThirdSingleBlockReorgInFourWeeks
85,605 views
1,575 Discussing
10
#EthereumFallsBelow$2500
6,842 views
94 Discussing