
#pennysia
pennysia
69 views
4 Discussing
Hot
Latest

·
--
Article
Pennysia contract hacked: the attacker stole funds using an approval you granted long agoOn November 13, SlowMist issued a security alert: the Ethereum settlement contract for a project called Pennysia had been exploited. A vulnerability allowing arbitrary external calls in the contract code let the attacker bypass the normal process and directly transfer out tokens that users had previously approved for the contract but had not yet used.
SlowMist began investigating after receiving several reports from users who had lost funds. The total amount lost has yet to be determined, and Pennysia has not presented a compensation plan. So this isn’t a postmortem—it’s a warning about the approval that may still be sitting in your wallet.
Pennysia contract hacked: the attacker stole funds using an approval you granted long ago
On November 13, SlowMist issued a security alert: the Ethereum settlement contract for a project called Pennysia had been exploited. A vulnerability allowing arbitrary external calls in the contract code let the attacker bypass the normal process and directly transfer out tokens that users had previously approved for the contract but had not yet used.
SlowMist began investigating after receiving several reports from users who had lost funds. The total amount lost has yet to be determined, and Pennysia has not presented a compensation plan. So this isn’t a postmortem—it’s a warning about the approval that may still be sitting in your wallet.
SlowMist began investigating after receiving several reports from users who had lost funds. The total amount lost has yet to be determined, and Pennysia has not presented a compensation plan. So this isn’t a postmortem—it’s a warning about the approval that may still be sitting in your wallet.
5

·
--
Pennysia settlement contract exploited: revoke any existing approvals; this was not an exchange hack
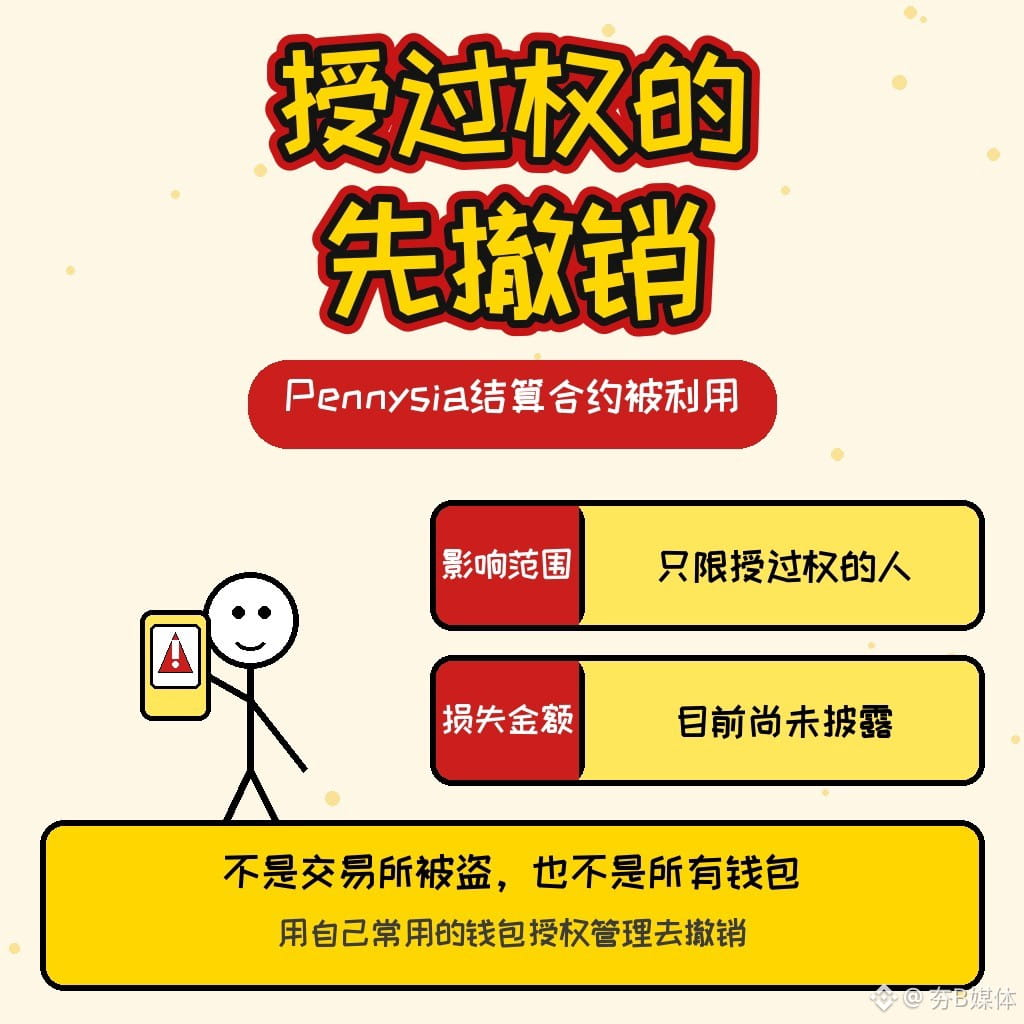
At around 14:57 this afternoon (Hong Kong time), SlowMist issued an alert: After receiving reports of users’ funds being stolen, its investigation found that Pennysia, a decentralized trading aggregator, had suffered an exploit involving an “arbitrary external call” vulnerability in its Settlement contract on Ethereum. The attacker could use token allowances that users had previously granted to the contract and had not yet revoked. Wu Blockchain and Deep Tide subsequently relayed the news, noting that the specific loss amount had not yet been disclosed. At the time of writing, no official statement had been seen from the project.
Who is affected: Only people who had previously approved tokens for this settlement contract—not all wallets, not an exchange hack, and not a site-wide suspension of deposits and withdrawals. The contract address is 0x3aad97e5a91b8e43b7dc830aceb004307678795e. SlowMist recommends that anyone who granted an approval revoke it immediately through the approval management feature in their usual wallet. Don’t click unfamiliar links claiming to “help you revoke” approvals, and don’t give your seed phrase or private key to anyone claiming to be an official representative.
Next, we need to confirm whether the project will issue an official response and the scale of the losses.
Have you ever approved this settlement contract?
This is not investment advice.
Sources: SlowMist X (@SlowMist_Team, around 14:57 HKT on 2026-11-13, https://x.com/SlowMist_Team/status/2121135351377047735); relayed by Wu Blockchain (around 15:05 HKT, https://x.com/wublockchain12/status/2121137326969565576) · Around 15:25 HKT on 2026-11-13
#Pennysia #授权安全 #钱包安全 #夯B媒体 $ETH
Pennysia settlement contract exploited: revoke any existing approvals; this was not an exchange hack
At around 14:57 this afternoon (Hong Kong time), SlowMist issued an alert: After receiving reports of users’ funds being stolen, its investigation found that Pennysia, a decentralized trading aggregator, had suffered an exploit involving an “arbitrary external call” vulnerability in its Settlement contract on Ethereum. The attacker could use token allowances that users had previously granted to the contract and had not yet revoked. Wu Blockchain and Deep Tide subsequently relayed the news, noting that the specific loss amount had not yet been disclosed. At the time of writing, no official statement had been seen from the project.
Who is affected: Only people who had previously approved tokens for this settlement contract—not all wallets, not an exchange hack, and not a site-wide suspension of deposits and withdrawals. The contract address is 0x3aad97e5a91b8e43b7dc830aceb004307678795e. SlowMist recommends that anyone who granted an approval revoke it immediately through the approval management feature in their usual wallet. Don’t click unfamiliar links claiming to “help you revoke” approvals, and don’t give your seed phrase or private key to anyone claiming to be an official representative.
Next, we need to confirm whether the project will issue an official response and the scale of the losses.
Have you ever approved this settlement contract?
This is not investment advice.
Sources: SlowMist X (@SlowMist_Team, around 14:57 HKT on 2026-11-13, https://x.com/SlowMist_Team/status/2121135351377047735); relayed by Wu Blockchain (around 15:05 HKT, https://x.com/wublockchain12/status/2121137326969565576) · Around 15:25 HKT on 2026-11-13
#Pennysia #授权安全 #钱包安全 #夯B媒体 $ETH
At around 14:57 this afternoon (Hong Kong time), SlowMist issued an alert: After receiving reports of users’ funds being stolen, its investigation found that Pennysia, a decentralized trading aggregator, had suffered an exploit involving an “arbitrary external call” vulnerability in its Settlement contract on Ethereum. The attacker could use token allowances that users had previously granted to the contract and had not yet revoked. Wu Blockchain and Deep Tide subsequently relayed the news, noting that the specific loss amount had not yet been disclosed. At the time of writing, no official statement had been seen from the project.
Who is affected: Only people who had previously approved tokens for this settlement contract—not all wallets, not an exchange hack, and not a site-wide suspension of deposits and withdrawals. The contract address is 0x3aad97e5a91b8e43b7dc830aceb004307678795e. SlowMist recommends that anyone who granted an approval revoke it immediately through the approval management feature in their usual wallet. Don’t click unfamiliar links claiming to “help you revoke” approvals, and don’t give your seed phrase or private key to anyone claiming to be an official representative.
Next, we need to confirm whether the project will issue an official response and the scale of the losses.
Have you ever approved this settlement contract?
This is not investment advice.
Sources: SlowMist X (@SlowMist_Team, around 14:57 HKT on 2026-11-13, https://x.com/SlowMist_Team/status/2121135351377047735); relayed by Wu Blockchain (around 15:05 HKT, https://x.com/wublockchain12/status/2121137326969565576) · Around 15:25 HKT on 2026-11-13
#Pennysia #授权安全 #钱包安全 #夯B媒体 $ETH
166
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#USPPIMissMayEaseBTCPressure
10,284 views
349 Discussing
2
#BitcoinCoreDisclosesTorTrafficVulnerability
2,199 views
126 Discussing
3
#WhatWillDriveCryptoandStocks’NextRebound?
104,676 views
1,319 Discussing
4
#BitcoinBreaksBelow200WeekMovingAverage
22,627 views
323 Discussing
5
#SpaceXTeslaMergerTalksWouldCombine30220BTC
8,054 views
172 Discussing
6
#Anthropic’s6xIPODemandSignalsPotentialRecordRaise
34,392 views
607 Discussing
7
#USCryptoETFsLose$1.48BInFiveDays
1,489 views
37 Discussing
8
#KoreaDigitalAssetBasicActFinalDraftExpectedEarlyJanuary
3,167 views
18 Discussing
9
#RippleRLUSDMarketCapSurpassesPayPalPYUSD
4,049 views
101 Discussing
10
#JaneStreetNearlyOctuplesFidelityBitcoinETFHoldings
12,457 views
205 Discussing