
#defisecurity
defisecurity
131,622 views
701 Discussing
Hot
Latest
·
--
🚨 ETH block builders drained ~$3.4M from K3 Capital's sBOLD vault via a copied bot exploit. The attacker prioritized transaction speed, highlighting how MEV strategies amplify risk in DeFi. This underscores the need for robust vault security against sophisticated front-running.
What does this mean for ETH's long-term DeFi security? #Ethereum #DeFiSecurity
$ETH #TradingSignal #CryptoAnalysis
🚨 ETH block builders drained ~$3.4M from K3 Capital's sBOLD vault via a copied bot exploit. The attacker prioritized transaction speed, highlighting how MEV strategies amplify risk in DeFi. This underscores the need for robust vault security against sophisticated front-running.
What does this mean for ETH's long-term DeFi security? #Ethereum #DeFiSecurity
$ETH #TradingSignal #CryptoAnalysis
What does this mean for ETH's long-term DeFi security? #Ethereum #DeFiSecurity
$ETH #TradingSignal #CryptoAnalysis
6

·
--
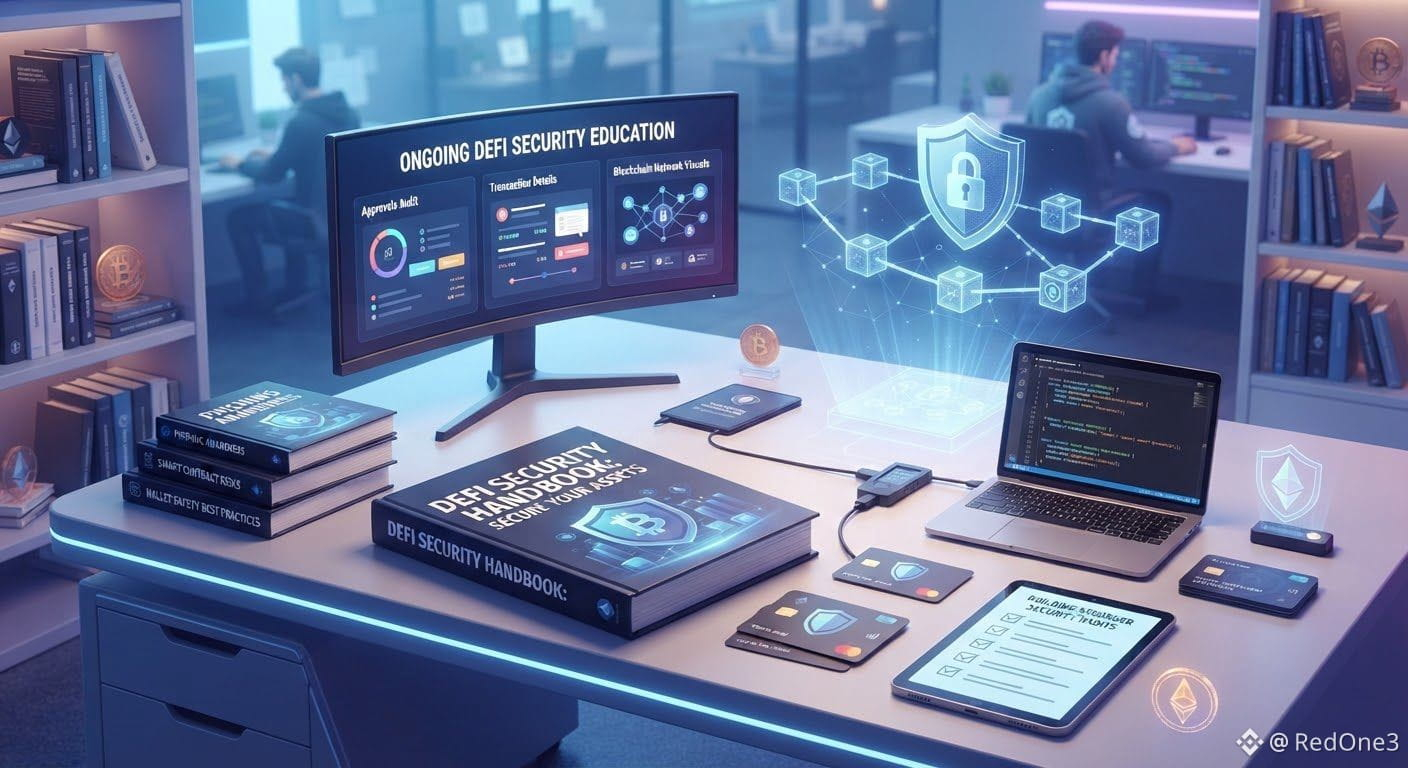
Protect Your Assets by Staying Informed 📚
DeFi security is an ongoing process
Learning about wallet safety, phishing, approvals, smart-contract risks, and transaction details helps build stronger habits over time.
#ReadLearnBuild 😎
#DeFiSecurity #CryptoEducation #WalletSafety #Web3 .
Protect Your Assets by Staying Informed 📚
DeFi security is an ongoing process
Learning about wallet safety, phishing, approvals, smart-contract risks, and transaction details helps build stronger habits over time.
#ReadLearnBuild 😎
#DeFiSecurity #CryptoEducation #WalletSafety #Web3 .
DeFi security is an ongoing process
Learning about wallet safety, phishing, approvals, smart-contract risks, and transaction details helps build stronger habits over time.
#ReadLearnBuild 😎
#DeFiSecurity #CryptoEducation #WalletSafety #Web3 .
67
·
--
🚨 Lighter DEX paused withdrawals following a $10.4M exploit linked to compromised API keys. The team recovered ~$5M in USDC, but $5.4M in funds remain untraceable.
Market implication: Smart-contract exploits erode user trust and trigger immediate risk-off sentiment in DeFi.
#DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
🚨 Lighter DEX paused withdrawals following a $10.4M exploit linked to compromised API keys. The team recovered ~$5M in USDC, but $5.4M in funds remain untraceable.
Market implication: Smart-contract exploits erode user trust and trigger immediate risk-off sentiment in DeFi.
#DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
Market implication: Smart-contract exploits erode user trust and trigger immediate risk-off sentiment in DeFi.
#DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
2
·
--
🚨 Lighter suffered a sudden $15.5M USDC drain, traced to a single API leak. Bitquery identified 10.39M tokens moving out, but a second alleged loss remains unresolved.
The incident highlights the critical risk of API vulnerabilities in DeFi infrastructure.
What does this mean for USDC liquidity confidence? 🤔
#DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
🚨 Lighter suffered a sudden $15.5M USDC drain, traced to a single API leak. Bitquery identified 10.39M tokens moving out, but a second alleged loss remains unresolved.
The incident highlights the critical risk of API vulnerabilities in DeFi infrastructure.
What does this mean for USDC liquidity confidence? 🤔
#DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
The incident highlights the critical risk of API vulnerabilities in DeFi infrastructure.
What does this mean for USDC liquidity confidence? 🤔
#DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
2
Lighter has temporarily paused withdrawals and new pool creation while it investigates a security incident it says appears to involve one compromised external party.
Crypto Briefing reports estimated losses of about $15.48 million in USDC across two market-maker accounts, with leaked API keys and a zero-fee pool maneuver as the suspected path. Those loss and mechanism details are reported estimates—not confirmed in Lighter’s notice. The investigation is ongoing, so it is too early to call this a protocol-level vulnerability.
Conclusion
$USDC
Official Binance USDC/USDT Spot chart: https://www.binance.com/en/trade/USDC_USDT?type=spot
Check the chart for yourself, do your own research, and trade responsibly.
#USDC #DeFiSecurity #CryptoSecurity #Lighter
Lighter has temporarily paused withdrawals and new pool creation while it investigates a security incident it says appears to involve one compromised external party.
Crypto Briefing reports estimated losses of about $15.48 million in USDC across two market-maker accounts, with leaked API keys and a zero-fee pool maneuver as the suspected path. Those loss and mechanism details are reported estimates—not confirmed in Lighter’s notice. The investigation is ongoing, so it is too early to call this a protocol-level vulnerability.
Conclusion
$USDC
Official Binance USDC/USDT Spot chart: https://www.binance.com/en/trade/USDC_USDT?type=spot
Check the chart for yourself, do your own research, and trade responsibly.
#USDC #DeFiSecurity #CryptoSecurity #Lighter
Crypto Briefing reports estimated losses of about $15.48 million in USDC across two market-maker accounts, with leaked API keys and a zero-fee pool maneuver as the suspected path. Those loss and mechanism details are reported estimates—not confirmed in Lighter’s notice. The investigation is ongoing, so it is too early to call this a protocol-level vulnerability.
Conclusion
$USDC
Official Binance USDC/USDT Spot chart: https://www.binance.com/en/trade/USDC_USDT?type=spot
Check the chart for yourself, do your own research, and trade responsibly.
#USDC #DeFiSecurity #CryptoSecurity #Lighter
14

·
--
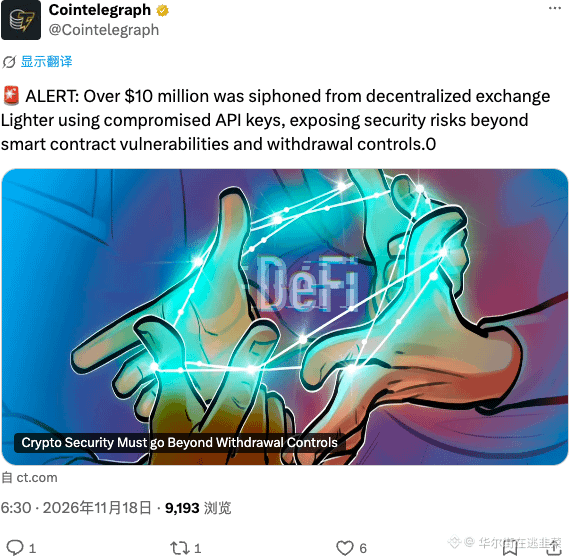
$10 million is gone—not because of a contract vulnerability, but because an API key was leaked. This time, Lighter fell victim to a “backdoor.”
Don’t focus only on code audits when it comes to DeFi security. API key management is the real minefield, and this lesson came at a steep cost.
Factor supply chain security into your risk assessment when choosing projects; don’t just look at TVL.
#Lighter #DeFiSecurity
$10 million is gone—not because of a contract vulnerability, but because an API key was leaked. This time, Lighter fell victim to a “backdoor.”
Don’t focus only on code audits when it comes to DeFi security. API key management is the real minefield, and this lesson came at a steep cost.
Factor supply chain security into your risk assessment when choosing projects; don’t just look at TVL.
#Lighter #DeFiSecurity
Don’t focus only on code audits when it comes to DeFi security. API key management is the real minefield, and this lesson came at a steep cost.
Factor supply chain security into your risk assessment when choosing projects; don’t just look at TVL.
#Lighter #DeFiSecurity
4

·
--
🚨 $ACX INFRASTRUCTURE COMPROMISE: WHY DISCONNECTING YOUR WALLET IS NOT ENOUGH 🛡️
Institutional portfolio defense goes beyond charts; it requires rigorous allowance hygiene. When the $ACX domain registrar experienced external interference, visitors faced malicious frontend interfaces designed to capture dangerous token approvals. 📊
Disconnecting your address from a dApp does not automatically revoke smart contract allowances or Permit2 permissions left active on-chain. ⚡ Smart money participants always audit their active allowances through independent verification tools after any protocol infrastructure anomaly. 💡
Are you actively auditing your on-chain approvals and allowances across all connected networks today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACX #DeFiSecurity #RiskManagement #Crypto
🦈 🔒
🚨 $ACX INFRASTRUCTURE COMPROMISE: WHY DISCONNECTING YOUR WALLET IS NOT ENOUGH 🛡️
Institutional portfolio defense goes beyond charts; it requires rigorous allowance hygiene. When the $ACX domain registrar experienced external interference, visitors faced malicious frontend interfaces designed to capture dangerous token approvals. 📊
Disconnecting your address from a dApp does not automatically revoke smart contract allowances or Permit2 permissions left active on-chain. ⚡ Smart money participants always audit their active allowances through independent verification tools after any protocol infrastructure anomaly. 💡
Are you actively auditing your on-chain approvals and allowances across all connected networks today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACX #DeFiSecurity #RiskManagement #Crypto
🦈 🔒
Institutional portfolio defense goes beyond charts; it requires rigorous allowance hygiene. When the $ACX domain registrar experienced external interference, visitors faced malicious frontend interfaces designed to capture dangerous token approvals. 📊
Disconnecting your address from a dApp does not automatically revoke smart contract allowances or Permit2 permissions left active on-chain. ⚡ Smart money participants always audit their active allowances through independent verification tools after any protocol infrastructure anomaly. 💡
Are you actively auditing your on-chain approvals and allowances across all connected networks today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACX #DeFiSecurity #RiskManagement #Crypto
🦈 🔒
5

·
--
Bearish
🚨 Across Protocol recovered its website after a phishing attack — but some wallets could STILL be exposed
On November 10, attackers reportedly took control of the Across domain through a social engineering attack targeting its registrar, Namecheap
Visitors were redirected to a malicious website that could request dangerous token approvals
Across has now regained control of the domain and says its systems are operational again
But there's a security detail worth understanding 👇
$BNB
{future}(BNBUSDT)
🔐 Disconnecting your wallet does NOT revoke token approvals
⚠️ A malicious approval can remain active even after the phishing website disappears
If you connected your wallet or signed anything on Across during the November 10 incident, review suspicious approvals and Permit2 permissions across affected networks
Revoke unauthorized allowances using a trusted tool reached independently — never through unsolicited recovery links
Across has promised to compensate affected users, but final losses and reimbursement details remain undisclosed
This wasn't a confirmed exploit of the bridge's smart contracts
The attacker targeted something users trusted before reaching those contracts — the official website
A recovered domain doesn't automatically mean a recovered wallet
$ACX
#Across #DeFiSecurity
🚨 Across Protocol recovered its website after a phishing attack — but some wallets could STILL be exposed
On November 10, attackers reportedly took control of the Across domain through a social engineering attack targeting its registrar, Namecheap
Visitors were redirected to a malicious website that could request dangerous token approvals
Across has now regained control of the domain and says its systems are operational again
But there's a security detail worth understanding 👇
$BNB
🔐 Disconnecting your wallet does NOT revoke token approvals
⚠️ A malicious approval can remain active even after the phishing website disappears
If you connected your wallet or signed anything on Across during the November 10 incident, review suspicious approvals and Permit2 permissions across affected networks
Revoke unauthorized allowances using a trusted tool reached independently — never through unsolicited recovery links
Across has promised to compensate affected users, but final losses and reimbursement details remain undisclosed
This wasn't a confirmed exploit of the bridge's smart contracts
The attacker targeted something users trusted before reaching those contracts — the official website
A recovered domain doesn't automatically mean a recovered wallet
$ACX
#Across #DeFiSecurity
On November 10, attackers reportedly took control of the Across domain through a social engineering attack targeting its registrar, Namecheap
Visitors were redirected to a malicious website that could request dangerous token approvals
Across has now regained control of the domain and says its systems are operational again
But there's a security detail worth understanding 👇
$BNB
🔐 Disconnecting your wallet does NOT revoke token approvals
⚠️ A malicious approval can remain active even after the phishing website disappears
If you connected your wallet or signed anything on Across during the November 10 incident, review suspicious approvals and Permit2 permissions across affected networks
Revoke unauthorized allowances using a trusted tool reached independently — never through unsolicited recovery links
Across has promised to compensate affected users, but final losses and reimbursement details remain undisclosed
This wasn't a confirmed exploit of the bridge's smart contracts
The attacker targeted something users trusted before reaching those contracts — the official website
A recovered domain doesn't automatically mean a recovered wallet
$ACX
#Across #DeFiSecurity
41

Article
$120M Aave Reserve Frozen Amid tBTC Bridge VulnerabilityThe Threshold network is navigating a critical security recovery phase after a Linux kernel vulnerability forced a halt of the tBTC bridge on Oct 30. While bridge operations have partially resumed, the situation remains high risk as $120M in Aave reserves stay frozen.
This incident underscores the systemic danger posed by infrastructure level vulnerabilities. Even if smart contracts are secure, the underlying server environment remains a single point of failure for massive liquidity pools.
Traders should monitor the Aave vault status closely. The inability to access $120M in assets during a period of volatility creates significant tail risk for leveraged positions and liquidity providers.
#DeFiSecurity #Aave
$120M Aave Reserve Frozen Amid tBTC Bridge Vulnerability
The Threshold network is navigating a critical security recovery phase after a Linux kernel vulnerability forced a halt of the tBTC bridge on Oct 30. While bridge operations have partially resumed, the situation remains high risk as $120M in Aave reserves stay frozen.
This incident underscores the systemic danger posed by infrastructure level vulnerabilities. Even if smart contracts are secure, the underlying server environment remains a single point of failure for massive liquidity pools.
Traders should monitor the Aave vault status closely. The inability to access $120M in assets during a period of volatility creates significant tail risk for leveraged positions and liquidity providers.
#DeFiSecurity #Aave
This incident underscores the systemic danger posed by infrastructure level vulnerabilities. Even if smart contracts are secure, the underlying server environment remains a single point of failure for massive liquidity pools.
Traders should monitor the Aave vault status closely. The inability to access $120M in assets during a period of volatility creates significant tail risk for leveraged positions and liquidity providers.
#DeFiSecurity #Aave
92
Solana based lending protocol Loopscale has suspended all operations following a massive campaign of 30,000 daily malicious API requests targeting SOL and USDC vaults. Although the team claims user deposits remain safe the incident underscores critical security vulnerabilities in protocol API layers.
#DeFiSecurity
Solana based lending protocol Loopscale has suspended all operations following a massive campaign of 30,000 daily malicious API requests targeting SOL and USDC vaults. Although the team claims user deposits remain safe the incident underscores critical security vulnerabilities in protocol API layers.
#DeFiSecurity
#DeFiSecurity
44
·
--
🚨 Arkéa Bank resumes transfers after a $133M attack, but confirms no crypto loss. Meanwhile, a separate $108.8M USDC trail highlights ongoing bridge vulnerabilities. Market sentiment remains cautious as institutional trust in cross-chain bridges is tested.
**Question:** Will this incident accelerate the shift toward more secure, native layer-2 solutions? #DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
🚨 Arkéa Bank resumes transfers after a $133M attack, but confirms no crypto loss. Meanwhile, a separate $108.8M USDC trail highlights ongoing bridge vulnerabilities. Market sentiment remains cautious as institutional trust in cross-chain bridges is tested.
**Question:** Will this incident accelerate the shift toward more secure, native layer-2 solutions? #DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
**Question:** Will this incident accelerate the shift toward more secure, native layer-2 solutions? #DeFiSecurity
$USDC #TradingSignal #CryptoAnalysis
41
·
--
🚨 Polkadot lost $1.38M due to a re-exploited security flaw from four months prior. The attacker resumed using their own relayer before the XCM fix was applied, but a later upgrade corrected the supply without altering user balances. This highlights the critical importance of timely patch deployment in DeFi security.
💡 Market Implication: DOT faces short-term downside pressure as the exploit renews concerns about network resilience.
🤔 Question: Will this renewed exploit trigger a broader risk-off sentiment across the Polkadot ecosystem?
#Polkadot #DeFiSecurity
$DOT #TradingSignal #CryptoAnalysis
🚨 Polkadot lost $1.38M due to a re-exploited security flaw from four months prior. The attacker resumed using their own relayer before the XCM fix was applied, but a later upgrade corrected the supply without altering user balances. This highlights the critical importance of timely patch deployment in DeFi security.
💡 Market Implication: DOT faces short-term downside pressure as the exploit renews concerns about network resilience.
🤔 Question: Will this renewed exploit trigger a broader risk-off sentiment across the Polkadot ecosystem?
#Polkadot #DeFiSecurity
$DOT #TradingSignal #CryptoAnalysis
💡 Market Implication: DOT faces short-term downside pressure as the exploit renews concerns about network resilience.
🤔 Question: Will this renewed exploit trigger a broader risk-off sentiment across the Polkadot ecosystem?
#Polkadot #DeFiSecurity
$DOT #TradingSignal #CryptoAnalysis
9
Governance, bought in a single transaction — that is what happened to X100 on Saturday evening, and I keep coming back to how little stood in the attackers' way.
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
Governance, bought in a single transaction — that is what happened to X100 on Saturday evening, and I keep coming back to how little stood in the attackers' way.
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
5
·
--
My Crypto Safety Roadmap (Part 8): How I Manage and Revoke Risky Smart Contract Permissions🎈🎈
🔴Interacting with Decentralized Applications (DApps) and DeFi platforms is a major part of my crypto execution, but it introduces a hidden risk that many overlook. In my journey, I discovered that granting "unlimited token approval" to a platform allows its smart contracts to access my assets at any time. If that protocol gets exploited or turns out to be a scam, my connected wallet can be drained instantly. To secure my treasury, I established a strict inspection and cleanup routine.🚀
🔴Today, I never leave permanent or unlimited spending permissions active on my Web3 wallets. I routinely use blockchain scanners and revocation tools like Revoke.cash to audit every single smart contract connection I have made. Whenever I finish a transaction or interact with a new platform, I immediately revoke or minimize the allowed token allowance. Controlling exactly who and what can interact with my digital assets is my ultimate shield against smart contract exploits.🚀
#CryptoSafety #SmartContracts #Web3Security #DeFiSecurity $XAUT $BTC $BNB
💥Not Financial Advice
{spot}(XAUTUSDT)
My Crypto Safety Roadmap (Part 8): How I Manage and Revoke Risky Smart Contract Permissions🎈🎈
🔴Interacting with Decentralized Applications (DApps) and DeFi platforms is a major part of my crypto execution, but it introduces a hidden risk that many overlook. In my journey, I discovered that granting "unlimited token approval" to a platform allows its smart contracts to access my assets at any time. If that protocol gets exploited or turns out to be a scam, my connected wallet can be drained instantly. To secure my treasury, I established a strict inspection and cleanup routine.🚀
🔴Today, I never leave permanent or unlimited spending permissions active on my Web3 wallets. I routinely use blockchain scanners and revocation tools like Revoke.cash to audit every single smart contract connection I have made. Whenever I finish a transaction or interact with a new platform, I immediately revoke or minimize the allowed token allowance. Controlling exactly who and what can interact with my digital assets is my ultimate shield against smart contract exploits.🚀
#CryptoSafety #SmartContracts #Web3Security #DeFiSecurity $XAUT $BTC $BNB
💥Not Financial Advice
🔴Interacting with Decentralized Applications (DApps) and DeFi platforms is a major part of my crypto execution, but it introduces a hidden risk that many overlook. In my journey, I discovered that granting "unlimited token approval" to a platform allows its smart contracts to access my assets at any time. If that protocol gets exploited or turns out to be a scam, my connected wallet can be drained instantly. To secure my treasury, I established a strict inspection and cleanup routine.🚀
🔴Today, I never leave permanent or unlimited spending permissions active on my Web3 wallets. I routinely use blockchain scanners and revocation tools like Revoke.cash to audit every single smart contract connection I have made. Whenever I finish a transaction or interact with a new platform, I immediately revoke or minimize the allowed token allowance. Controlling exactly who and what can interact with my digital assets is my ultimate shield against smart contract exploits.🚀
#CryptoSafety #SmartContracts #Web3Security #DeFiSecurity $XAUT $BTC $BNB
💥Not Financial Advice
2
237

🚨 $ETH SECURITY ALERT: ATTACK WAVES MIRROR A GLOBAL PANDEMIC 🦈
📊 Attackers are now sweeping through the crypto space with the intensity of a pandemic, turning on‑chain breaches into an early warning system for the broader internet. 🪙 Small DeFi projects with thin security nets are the low‑hanging fruit, while heavyweight protocols are deploying AI shields to harden their perimeters. ⚡ This divergence creates a clear liquidity gap: smart money is already repositioning, scouting for resilient assets before the next wave hits.
💡 The pattern suggests a spill‑over effect—once the traditional web feels the pressure, we’ll see a cascade of cross‑industry exploits. 👇 Are you auditing your exposure before the next sweep hits your portfolio?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFiSecurity #CryptoRisk #SmartMoney
🔥 💎
🚨 $ETH SECURITY ALERT: ATTACK WAVES MIRROR A GLOBAL PANDEMIC 🦈
📊 Attackers are now sweeping through the crypto space with the intensity of a pandemic, turning on‑chain breaches into an early warning system for the broader internet. 🪙 Small DeFi projects with thin security nets are the low‑hanging fruit, while heavyweight protocols are deploying AI shields to harden their perimeters. ⚡ This divergence creates a clear liquidity gap: smart money is already repositioning, scouting for resilient assets before the next wave hits.
💡 The pattern suggests a spill‑over effect—once the traditional web feels the pressure, we’ll see a cascade of cross‑industry exploits. 👇 Are you auditing your exposure before the next sweep hits your portfolio?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFiSecurity #CryptoRisk #SmartMoney
🔥 💎
📊 Attackers are now sweeping through the crypto space with the intensity of a pandemic, turning on‑chain breaches into an early warning system for the broader internet. 🪙 Small DeFi projects with thin security nets are the low‑hanging fruit, while heavyweight protocols are deploying AI shields to harden their perimeters. ⚡ This divergence creates a clear liquidity gap: smart money is already repositioning, scouting for resilient assets before the next wave hits.
💡 The pattern suggests a spill‑over effect—once the traditional web feels the pressure, we’ll see a cascade of cross‑industry exploits. 👇 Are you auditing your exposure before the next sweep hits your portfolio?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFiSecurity #CryptoRisk #SmartMoney
🔥 💎
4
⚖️ DeFi Security in Focus After Ostium Oracle Exploit Pauses Trading: Oracles remain critical vulnerability in decentralized finance
On July 16, 2026, security firms report a multimillion-dollar oracle exploit at Ostium, forcing the protocol to pause trading. The incident underscores persistent security challenges in DeFi. Bitcoin $BTC trades at $64,557 as the market assesses implications.
Oracle manipulation has been a recurring attack vector in DeFi. Ethereum $ETH at $1,917 hosts the majority of DeFi protocols and could see increased focus on oracle security solutions.
The Ostium exploit joins a list of high-profile oracle attacks, emphasizing the need for robust, decentralized data infrastructure.
📌 Key Takeaway:
Ostium oracle exploit highlights persistent DeFi security challenges. Oracle integrity remains critical for protocol safety and user trust.
#DeFiSecurity #Oracles
#BinanceAlphaAlert
⚖️ DeFi Security in Focus After Ostium Oracle Exploit Pauses Trading: Oracles remain critical vulnerability in decentralized finance
On July 16, 2026, security firms report a multimillion-dollar oracle exploit at Ostium, forcing the protocol to pause trading. The incident underscores persistent security challenges in DeFi. Bitcoin $BTC trades at $64,557 as the market assesses implications.
Oracle manipulation has been a recurring attack vector in DeFi. Ethereum $ETH at $1,917 hosts the majority of DeFi protocols and could see increased focus on oracle security solutions.
The Ostium exploit joins a list of high-profile oracle attacks, emphasizing the need for robust, decentralized data infrastructure.
📌 Key Takeaway:
Ostium oracle exploit highlights persistent DeFi security challenges. Oracle integrity remains critical for protocol safety and user trust.
#DeFiSecurity #Oracles
#BinanceAlphaAlert
On July 16, 2026, security firms report a multimillion-dollar oracle exploit at Ostium, forcing the protocol to pause trading. The incident underscores persistent security challenges in DeFi. Bitcoin $BTC trades at $64,557 as the market assesses implications.
Oracle manipulation has been a recurring attack vector in DeFi. Ethereum $ETH at $1,917 hosts the majority of DeFi protocols and could see increased focus on oracle security solutions.
The Ostium exploit joins a list of high-profile oracle attacks, emphasizing the need for robust, decentralized data infrastructure.
📌 Key Takeaway:
Ostium oracle exploit highlights persistent DeFi security challenges. Oracle integrity remains critical for protocol safety and user trust.
#DeFiSecurity #Oracles
#BinanceAlphaAlert
32
📰 Ostium Pauses Trading After Multimillion-Dollar Oracle Exploit: Security incident raises concerns about oracle integrity
On July 16, 2026, Ostium pauses trading as security firms report a multimillion-dollar oracle exploit. The incident raises questions about oracle security in decentralized finance. Bitcoin $BTC trades at $64,557 as the broader market digests the news.
Oracle exploits have been a recurring challenge in DeFi, with attackers manipulating price feeds. Ethereum $ETH at $1,917 hosts many protocols that rely on oracle infrastructure.
The Ostium incident highlights the need for robust oracle designs, including decentralized data sources and manipulation-resistant price feeds.
📌 Key Takeaway:
Ostium oracle exploit pause underscores DeFi security challenges. Robust oracle design remains critical for protocol safety.
#DeFiSecurity #OracleExploit
#BinanceAlphaAlert
📰 Ostium Pauses Trading After Multimillion-Dollar Oracle Exploit: Security incident raises concerns about oracle integrity
On July 16, 2026, Ostium pauses trading as security firms report a multimillion-dollar oracle exploit. The incident raises questions about oracle security in decentralized finance. Bitcoin $BTC trades at $64,557 as the broader market digests the news.
Oracle exploits have been a recurring challenge in DeFi, with attackers manipulating price feeds. Ethereum $ETH at $1,917 hosts many protocols that rely on oracle infrastructure.
The Ostium incident highlights the need for robust oracle designs, including decentralized data sources and manipulation-resistant price feeds.
📌 Key Takeaway:
Ostium oracle exploit pause underscores DeFi security challenges. Robust oracle design remains critical for protocol safety.
#DeFiSecurity #OracleExploit
#BinanceAlphaAlert
On July 16, 2026, Ostium pauses trading as security firms report a multimillion-dollar oracle exploit. The incident raises questions about oracle security in decentralized finance. Bitcoin $BTC trades at $64,557 as the broader market digests the news.
Oracle exploits have been a recurring challenge in DeFi, with attackers manipulating price feeds. Ethereum $ETH at $1,917 hosts many protocols that rely on oracle infrastructure.
The Ostium incident highlights the need for robust oracle designs, including decentralized data sources and manipulation-resistant price feeds.
📌 Key Takeaway:
Ostium oracle exploit pause underscores DeFi security challenges. Robust oracle design remains critical for protocol safety.
#DeFiSecurity #OracleExploit
#BinanceAlphaAlert
35
Verified
🚨 BREAKING !!!
NORTH KOREAN HACKER LAUNDERED A WHOPPING $220 MILLION FROM KELP DAO HACK — RECOVERY WINDOW NEARLY CLOSED 💀
On-chain data confirms the hacker group TraderTraitor (linked to North Korea) has laundered almost the entire $220 million through high-security channels like THORChain, Wasabi, Tornado Cash, and Umbra 🛠
Only about $1.7 million remains in the hacker's original wallet — most of the transaction trails have been wiped clean, making the chances of tracing and recovering the assets nearly zero 📊
This is one of the most organized crypto laundering operations to date, showcasing the increasingly sophisticated technical capabilities of state-sponsored hacker groups ⚠️
$220 million has vanished completely. This incident again raises questions about the limits of on-chain tracing tools when faced with mixers and intentional cross-chain bridges.
#CryptoHack #DeFiSecurity
$ETH $BTC $LAB
🚨 BREAKING !!!
NORTH KOREAN HACKER LAUNDERED A WHOPPING $220 MILLION FROM KELP DAO HACK — RECOVERY WINDOW NEARLY CLOSED 💀
On-chain data confirms the hacker group TraderTraitor (linked to North Korea) has laundered almost the entire $220 million through high-security channels like THORChain, Wasabi, Tornado Cash, and Umbra 🛠
Only about $1.7 million remains in the hacker's original wallet — most of the transaction trails have been wiped clean, making the chances of tracing and recovering the assets nearly zero 📊
This is one of the most organized crypto laundering operations to date, showcasing the increasingly sophisticated technical capabilities of state-sponsored hacker groups ⚠️
$220 million has vanished completely. This incident again raises questions about the limits of on-chain tracing tools when faced with mixers and intentional cross-chain bridges.
#CryptoHack #DeFiSecurity
$ETH $BTC $LAB
NORTH KOREAN HACKER LAUNDERED A WHOPPING $220 MILLION FROM KELP DAO HACK — RECOVERY WINDOW NEARLY CLOSED 💀
On-chain data confirms the hacker group TraderTraitor (linked to North Korea) has laundered almost the entire $220 million through high-security channels like THORChain, Wasabi, Tornado Cash, and Umbra 🛠
Only about $1.7 million remains in the hacker's original wallet — most of the transaction trails have been wiped clean, making the chances of tracing and recovering the assets nearly zero 📊
This is one of the most organized crypto laundering operations to date, showcasing the increasingly sophisticated technical capabilities of state-sponsored hacker groups ⚠️
$220 million has vanished completely. This incident again raises questions about the limits of on-chain tracing tools when faced with mixers and intentional cross-chain bridges.
#CryptoHack #DeFiSecurity
$ETH $BTC $LAB
599

XRP Ledger Says "No Flash Loans Here"
A new XRPL Upgrade proposal includes a blunt note: flash loan attacks can't happen on XRP Ledger because transactions can't chain multiple actions together. One transaction, one action. Done.
Ethereum DeFi has lost billions to flash loan exploits. XRPL's design kills that attack vector outright. The catch is you also lose flash loans for arbitrage and quick liquidations. With over $3B n tokenized assets already on XRPL, some teams are betting security beats speed.
Banks are stepping in, geopolitics is heating up, betting markets are exploding, and blockchains are making hard design choices. Intitutions want safety. Traders want options. Builders are picking sides.
#XRPledger #XRP #Flashloans #DeFiSecurity #AMM
XRP Ledger Says "No Flash Loans Here"
A new XRPL Upgrade proposal includes a blunt note: flash loan attacks can't happen on XRP Ledger because transactions can't chain multiple actions together. One transaction, one action. Done.
Ethereum DeFi has lost billions to flash loan exploits. XRPL's design kills that attack vector outright. The catch is you also lose flash loans for arbitrage and quick liquidations. With over $3B n tokenized assets already on XRPL, some teams are betting security beats speed.
Banks are stepping in, geopolitics is heating up, betting markets are exploding, and blockchains are making hard design choices. Intitutions want safety. Traders want options. Builders are picking sides.
#XRPledger #XRP #Flashloans #DeFiSecurity #AMM
A new XRPL Upgrade proposal includes a blunt note: flash loan attacks can't happen on XRP Ledger because transactions can't chain multiple actions together. One transaction, one action. Done.
Ethereum DeFi has lost billions to flash loan exploits. XRPL's design kills that attack vector outright. The catch is you also lose flash loans for arbitrage and quick liquidations. With over $3B n tokenized assets already on XRPL, some teams are betting security beats speed.
Banks are stepping in, geopolitics is heating up, betting markets are exploding, and blockchains are making hard design choices. Intitutions want safety. Traders want options. Builders are picking sides.
#XRPledger #XRP #Flashloans #DeFiSecurity #AMM
156

·
--
$NEWT IS REWRITING DEFI SECURITY WITH PRE-TRANSACTION ENFORCEMENT 🔥
Entry: Not provided
Most security tools start work after funds are gone. Newton Mainnet Beta flips that — it validates every transaction against active policies (OFAC compliance, identity, real-time threat blocking, oracle health) before a single coin moves. Magic Labs, the team behind embedded wallets, already uses it to shift from wallet security to transaction authorization. This is infrastructure, not airdrop hype.
DeFi has never had a layer that enforces rules before execution, on-chain, cross-chain. Are you building something that could benefit from a policy engine that acts before the damage is done?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #Infrastructure #Web3
🔥
$NEWT IS REWRITING DEFI SECURITY WITH PRE-TRANSACTION ENFORCEMENT 🔥
Entry: Not provided
Most security tools start work after funds are gone. Newton Mainnet Beta flips that — it validates every transaction against active policies (OFAC compliance, identity, real-time threat blocking, oracle health) before a single coin moves. Magic Labs, the team behind embedded wallets, already uses it to shift from wallet security to transaction authorization. This is infrastructure, not airdrop hype.
DeFi has never had a layer that enforces rules before execution, on-chain, cross-chain. Are you building something that could benefit from a policy engine that acts before the damage is done?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #Infrastructure #Web3
🔥
Entry: Not provided
Most security tools start work after funds are gone. Newton Mainnet Beta flips that — it validates every transaction against active policies (OFAC compliance, identity, real-time threat blocking, oracle health) before a single coin moves. Magic Labs, the team behind embedded wallets, already uses it to shift from wallet security to transaction authorization. This is infrastructure, not airdrop hype.
DeFi has never had a layer that enforces rules before execution, on-chain, cross-chain. Are you building something that could benefit from a policy engine that acts before the damage is done?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #Infrastructure #Web3
🔥
2
33
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#IsAnthropic’s$1.5TMarketCapJustified?
8,315 views
71 Discussing
2
#BTCRemainsUnderPressureAfterHawkishFOMCMinutes
215,817 views
2,015 Discussing
3
#NvidiaBoardReportedlySplitOverHuang’sReturn
105,124 views
1,073 Discussing
4
#StrategySTRCPreferredSlips3.65%Below$100Par
5,954 views
64 Discussing
5
#MASToUpgradeSGDTestnetToSGDigitalLedger
17,496 views
226 Discussing
6
#CanGTA6'sLaunchLiftTTWOShares?
74,979 views
785 Discussing
7
#Solana2027RoadmapTargetsDoubleComputeCapacity
6,804 views
119 Discussing
8
#InjectiveTokenizedRealEstateMortgagesTop$1.5B
1,020 views
27 Discussing
9
#TetherMakesStrategicInvestmentInSCRYPT
5,197 views
100 Discussing
10
#CapitalGroupAdds1264500StrategyShares
24,968 views
224 Discussing