binanceincidentreport

Binance Blog
·
--
Статья
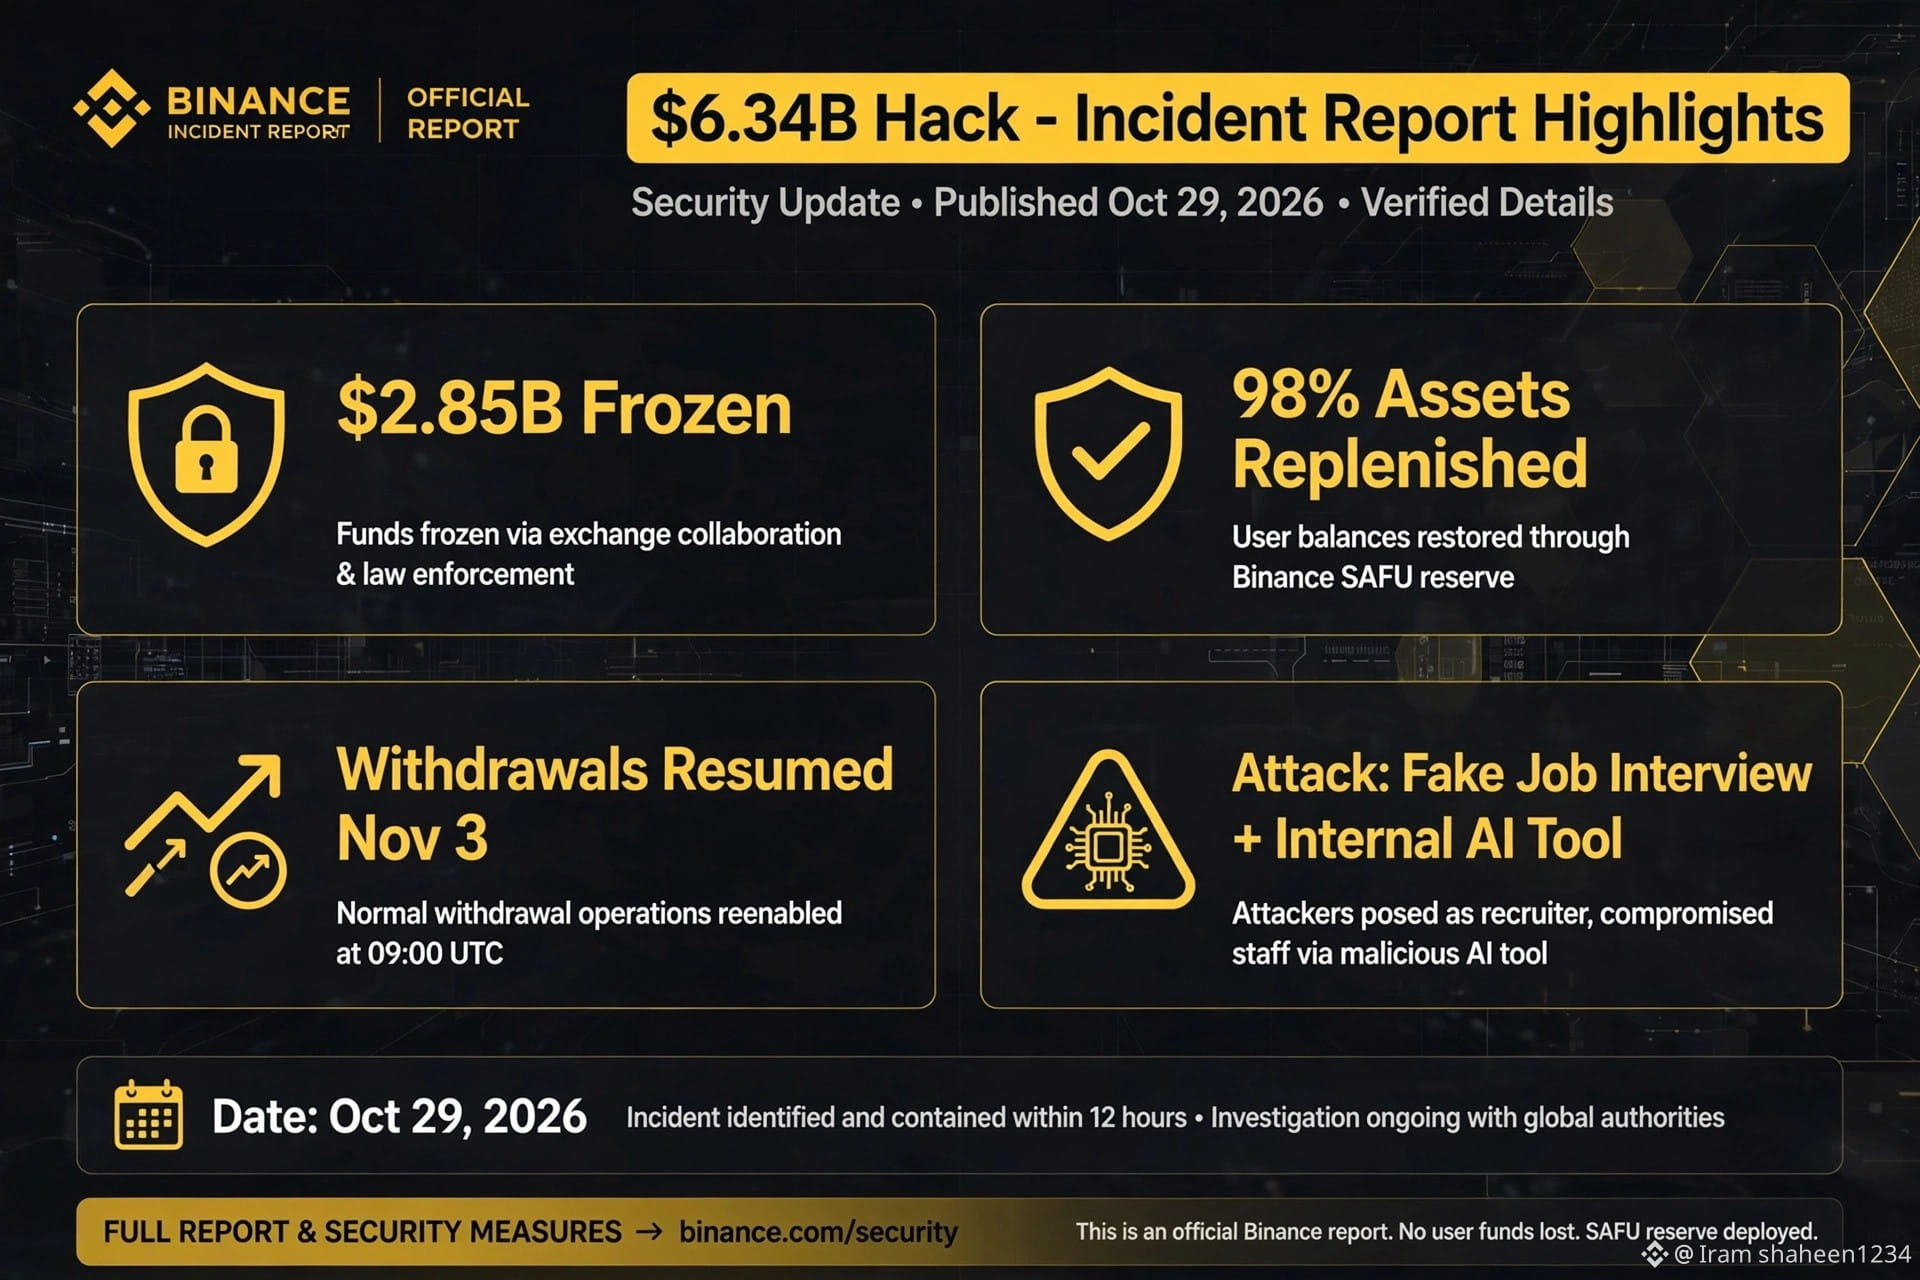
29 October 2026 Binance Security Incident: Initial Findings and Response UpdateOn 29 October 2026, Binance experienced a serious and highly sophisticated security incident. This should not have happened, and we apologise for the concern, disruption and uncertainty it caused our users, partners and the wider industry.Our first responsibility is to protect users. Binance will absorb the financial impact of the stolen funds, not our users. We have already set aside more than 100% of the funds required to cover the loss. As of 31 October 2026, 98% of the impacted token assets have been replenished and are verifiable on our Proof of Reserves page. We are in the process of purchasing the outstanding, more illiquid assets.Approximately USD 6.34 billion in digital assets were impacted by the incident. As of this update, approximately USD 2.85 billion in digital assets have been frozen or intercepted, subject to reconciliation and market price volatility.We have taken immediate action to contain the incident and strengthen the systems involved. The entry points identified as having been used in the attack have been closed. Systems touched in the attack path have been rebuilt or replaced. We have also implemented tighter device controls, enhanced wallet-service risk controls and expanded AI-based behavioural anomaly detection.This is our initial report. It covers what we know today and what we have already improved. The investigation remains ongoing and our findings will be subject to further independent review. Some technical details will remain confidential to prevent malicious actors from using them to plan attacks. We are engaging independent security firms for further review. The latest information released by the Federal Bureau of Investigation indicates that the Democratic People’s Republic of Korea is responsible for this incident.We are sharing this initial report because security improves when the industry learns together.What happened on 29 OctoberThe attack unfolded quickly across several networks.The attacker exploited unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.Between 20:05 UTC and 20:09 UTC, five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address.Binance hot wallets on Solana and Optimism sent approximately 970,500 SOL and 44.2 million OP to attacker-controlled addresses.Binance then received an internal alert regarding large-volume transfers and immediately began investigating.Binance hot wallet sent 18,270 BTC to an attacker-controlled address. The attacker then used the signing service to exploit Ethereum’s EIP-7702 authorization mechanism. EIP-7702 allows an account to delegate certain execution rights to a smart contract without exposing the private key. In this case, the attacker used that mechanism to give an attacker-controlled smart contract partial execution rights over a Binance hot wallet. Binance immediately initiated multiple containment measures, including suspending withdrawals to restrict further outflows, coordinating with partners to freeze affected tokens, and taking steps to revoke unauthorized permissions. These efforts froze a total of $2.85 billion in assets.However, suspending withdrawals alone could not stop all unauthorized asset movements. The malicious EIP-7702 authorizations existed on-chain and operated independently of Binance’s normal withdrawal infrastructure.The attackers submitted 50 signing transactions to manipulate the account nonce and establish malicious delegation authorizations. Once established, these authorizations enabled the attackers to continue moving assets independently of Binance's normal withdrawal infrastructure. Binance needed additional transactions to revoke these on-chain authorizations.The containment process involved additional technical complexities. Because the hot wallet used Multi-Party Computation (MPC), there was no single private key that could be used to immediately revoke the malicious EIP-7702 authorizations. The team therefore developed and executed a specialized procedure to revoke these authorizations, which required additional time. Furthermore, suspending withdrawals and shutting down hot wallet services did not automatically invalidate existing on-chain authorizations.These challenges extended the time required to fully contain the unauthorized asset movements. We are reviewing the incident response process, signing policy coverage, hot wallet controls and identifying opportunities to further strengthen our ability to respond rapidly to threats in the future.The final unauthorized transfer of 2,961.9 ETH finalised on-chain at 23:56 UTC. The transaction had previously been broadcast and remained pending before subsequently finalising. No further unauthorised transfers were observed after.At 00:10 UTC on 30 October 2026, Binance executed a new authorization from the Binance14 hot wallet to the zero address, clearing the EIP-7702 delegation code.Attack Preparation Our current investigation indicates that this was a sophisticated, multi-stage campaign. It was not a single isolated breach or a simple phishing incident. The attackers combined a range of techniques, including social engineering by fake recruitment interviews, malicious software downloads, compromised internal AI tooling, endpoint compromise, and an advanced transaction-authorisation method.June 2026 — Supply chain attack. Engineer A from Wallet DevOps downloaded a tampered Homebrew installation in order to install a popular AI coding tool after searching for it on a search engine. Our security team detected the anomaly, replaced the device, and rotated all related credentials as a proactive security action. However, Engineer A’s role and his related colleagues on our wallet infrastructure team was exposed to the hacker. Throughout 2026, Binance's security team detected and prevented 57 suspected North Korea-linked cyber threat cases. These attempts reflect the persistent threat posed by state-sponsored actors targeting the cryptocurrency industry. The techniques include fraudulent job interviews, malicious software disguised as popular developer tools, compromised software packages and browser extensions, fake video conferencing applications, and social engineering campaigns designed to steal credentials or deploy remote access malware.September 2026 — social engineering. Software Engineer B was contacted through a legitimate job-hunting platform by an individual posing as a Project Director. Software Engineer B had a profile on the platform that referenced his experience at Binance. The purported Project Director arranged a first-round interview with a HR representative, followed by a second-round interview with an individual claiming to be the CEO of a fictitious company.In the first round, the purported HR representative conducted a live video interview with Software Engineer B. The interviewer shared a social media account with him, including personal photos and videos posted on the platform, in order to build trust. This was more advanced and deceptive than previously seen social engineering approaches. The second interview was conducted in a popular social chat app, near the end of the interview, Engineer B was instructed to download an “assignment” containing a malicious code repository onto his work computer. The repository contained malicious code that executed during the setup process, initiating a series of unauthorized activities.The malware employed sophisticated obfuscation and evasion techniques, including replacing a legitimate development tool component with a malicious version to execute commands and establish communication with an attacker-controlled external server. The 0-day malware was not detected by the endpoint security protection tools at the time. The attacker also took steps to conceal the malicious activity and remove traces of the compromise, making detection and subsequent investigation more challenging.The script executed the below steps by applying obfuscation techniques to evade security detection.CREATE  /opt/homebrew/Cellar/pyenv/2.8.0/libexec/pyenv_  MODIFY  pyenv_ → 3,414 B  DELETE  .../libexec/pyenv  (3,344 B)      ← remove the valid pyenvRENAME  pyenv_ → pyenv  (3,414 B)  ← replace it with a malicious version DELETE  /opt/homebrew/bin/pyenv  (3,414 B)ln  (create a new symlink)  +  spawn zsh20 October, 2026 — use of an internal AI tool as a springboard. The attacker leveraged the compromised computer of engineer B and used an internal AI tool to gain control over the Wallet DevOps Engineer A and another Wallet Software Engineer C. The attacker soon discovered Wallet DevOps Engineer A had a container deployment permission token on his computer.29 October, 2026 — reach into wallet signing operations. On 29 October between 17:15 and 19:56, the attacker logged onto Software Engineer C’s computer, used the credentials stolen from Wallet DevOps Engineer A, deployed a container, and triggered a malicious script to launch the attack.What we have doneAs of Nov 3, 2026, we have taken the following actions:Rebuilt the affected wallet system in a new environment.Rebuilt the affected internal AI tool and access controls.Replaced affected devices.Decommissioned credentials and tokens related to affected engineers.Completed enhanced security scans across all employee devices.Enhanced AI-based behavioural anomaly detection.Strengthened wallet-service risk controls.Worked with law enforcement, blockchain intelligence firms and industry partners to trace and freeze affected assets.We will continue to strengthen our measures as the investigation progresses. There are a number of security measures we have implemented and are implementing that will remain private to prevent malicious actors from compromising our security.Further actionsWe are taking the following steps immediately.1. Independent cybersecurity reviewWe are engaging independent third-party cybersecurity experts to conduct a comprehensive review of the incident, validate our findings and recommend additional measures. The scope and findings of that review will inform our continuing remediation work.2. Expanded investment in AI security and preventionWe are increasing investment in AI-enabled detection, endpoint protection, developer-environment security and behavioural anomaly monitoring.3. Security research fund and industry initiativesWe are working on establishing a security research fund and targeted initiatives with leading AI companies, industry participants and security firms focused on AI security in blockchain environments.We will continue to proactively share information as and when we have it.
29 October 2026 Binance Security Incident: Initial Findings and Response Update

On 29 October 2026, Binance experienced a serious and highly sophisticated security incident. This should not have happened, and we apologise for the concern, disruption and uncertainty it caused our users, partners and the wider industry.Our first responsibility is to protect users. Binance will absorb the financial impact of the stolen funds, not our users. We have already set aside more than 100% of the funds required to cover the loss. As of 31 October 2026, 98% of the impacted token assets have been replenished and are verifiable on our Proof of Reserves page. We are in the process of purchasing the outstanding, more illiquid assets.Approximately USD 6.34 billion in digital assets were impacted by the incident. As of this update, approximately USD 2.85 billion in digital assets have been frozen or intercepted, subject to reconciliation and market price volatility.We have taken immediate action to contain the incident and strengthen the systems involved. The entry points identified as having been used in the attack have been closed. Systems touched in the attack path have been rebuilt or replaced. We have also implemented tighter device controls, enhanced wallet-service risk controls and expanded AI-based behavioural anomaly detection.This is our initial report. It covers what we know today and what we have already improved. The investigation remains ongoing and our findings will be subject to further independent review. Some technical details will remain confidential to prevent malicious actors from using them to plan attacks. We are engaging independent security firms for further review. The latest information released by the Federal Bureau of Investigation indicates that the Democratic People’s Republic of Korea is responsible for this incident.We are sharing this initial report because security improves when the industry learns together.What happened on 29 OctoberThe attack unfolded quickly across several networks.The attacker exploited unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.Between 20:05 UTC and 20:09 UTC, five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address.Binance hot wallets on Solana and Optimism sent approximately 970,500 SOL and 44.2 million OP to attacker-controlled addresses.Binance then received an internal alert regarding large-volume transfers and immediately began investigating.Binance hot wallet sent 18,270 BTC to an attacker-controlled address. The attacker then used the signing service to exploit Ethereum’s EIP-7702 authorization mechanism. EIP-7702 allows an account to delegate certain execution rights to a smart contract without exposing the private key. In this case, the attacker used that mechanism to give an attacker-controlled smart contract partial execution rights over a Binance hot wallet. Binance immediately initiated multiple containment measures, including suspending withdrawals to restrict further outflows, coordinating with partners to freeze affected tokens, and taking steps to revoke unauthorized permissions. These efforts froze a total of $2.85 billion in assets.However, suspending withdrawals alone could not stop all unauthorized asset movements. The malicious EIP-7702 authorizations existed on-chain and operated independently of Binance’s normal withdrawal infrastructure.The attackers submitted 50 signing transactions to manipulate the account nonce and establish malicious delegation authorizations. Once established, these authorizations enabled the attackers to continue moving assets independently of Binance's normal withdrawal infrastructure. Binance needed additional transactions to revoke these on-chain authorizations.The containment process involved additional technical complexities. Because the hot wallet used Multi-Party Computation (MPC), there was no single private key that could be used to immediately revoke the malicious EIP-7702 authorizations. The team therefore developed and executed a specialized procedure to revoke these authorizations, which required additional time. Furthermore, suspending withdrawals and shutting down hot wallet services did not automatically invalidate existing on-chain authorizations.These challenges extended the time required to fully contain the unauthorized asset movements. We are reviewing the incident response process, signing policy coverage, hot wallet controls and identifying opportunities to further strengthen our ability to respond rapidly to threats in the future.The final unauthorized transfer of 2,961.9 ETH finalised on-chain at 23:56 UTC. The transaction had previously been broadcast and remained pending before subsequently finalising. No further unauthorised transfers were observed after.At 00:10 UTC on 30 October 2026, Binance executed a new authorization from the Binance14 hot wallet to the zero address, clearing the EIP-7702 delegation code.Attack Preparation Our current investigation indicates that this was a sophisticated, multi-stage campaign. It was not a single isolated breach or a simple phishing incident. The attackers combined a range of techniques, including social engineering by fake recruitment interviews, malicious software downloads, compromised internal AI tooling, endpoint compromise, and an advanced transaction-authorisation method.June 2026 — Supply chain attack. Engineer A from Wallet DevOps downloaded a tampered Homebrew installation in order to install a popular AI coding tool after searching for it on a search engine. Our security team detected the anomaly, replaced the device, and rotated all related credentials as a proactive security action. However, Engineer A’s role and his related colleagues on our wallet infrastructure team was exposed to the hacker. Throughout 2026, Binance's security team detected and prevented 57 suspected North Korea-linked cyber threat cases. These attempts reflect the persistent threat posed by state-sponsored actors targeting the cryptocurrency industry. The techniques include fraudulent job interviews, malicious software disguised as popular developer tools, compromised software packages and browser extensions, fake video conferencing applications, and social engineering campaigns designed to steal credentials or deploy remote access malware.September 2026 — social engineering. Software Engineer B was contacted through a legitimate job-hunting platform by an individual posing as a Project Director. Software Engineer B had a profile on the platform that referenced his experience at Binance. The purported Project Director arranged a first-round interview with a HR representative, followed by a second-round interview with an individual claiming to be the CEO of a fictitious company.In the first round, the purported HR representative conducted a live video interview with Software Engineer B. The interviewer shared a social media account with him, including personal photos and videos posted on the platform, in order to build trust. This was more advanced and deceptive than previously seen social engineering approaches. The second interview was conducted in a popular social chat app, near the end of the interview, Engineer B was instructed to download an “assignment” containing a malicious code repository onto his work computer. The repository contained malicious code that executed during the setup process, initiating a series of unauthorized activities.The malware employed sophisticated obfuscation and evasion techniques, including replacing a legitimate development tool component with a malicious version to execute commands and establish communication with an attacker-controlled external server. The 0-day malware was not detected by the endpoint security protection tools at the time. The attacker also took steps to conceal the malicious activity and remove traces of the compromise, making detection and subsequent investigation more challenging.The script executed the below steps by applying obfuscation techniques to evade security detection.CREATE /opt/homebrew/Cellar/pyenv/2.8.0/libexec/pyenv_ MODIFY pyenv_ → 3,414 B DELETE .../libexec/pyenv (3,344 B) ← remove the valid pyenvRENAME pyenv_ → pyenv (3,414 B) ← replace it with a malicious version DELETE /opt/homebrew/bin/pyenv (3,414 B)ln (create a new symlink) + spawn zsh20 October, 2026 — use of an internal AI tool as a springboard. The attacker leveraged the compromised computer of engineer B and used an internal AI tool to gain control over the Wallet DevOps Engineer A and another Wallet Software Engineer C. The attacker soon discovered Wallet DevOps Engineer A had a container deployment permission token on his computer.29 October, 2026 — reach into wallet signing operations. On 29 October between 17:15 and 19:56, the attacker logged onto Software Engineer C’s computer, used the credentials stolen from Wallet DevOps Engineer A, deployed a container, and triggered a malicious script to launch the attack.What we have doneAs of Nov 3, 2026, we have taken the following actions:Rebuilt the affected wallet system in a new environment.Rebuilt the affected internal AI tool and access controls.Replaced affected devices.Decommissioned credentials and tokens related to affected engineers.Completed enhanced security scans across all employee devices.Enhanced AI-based behavioural anomaly detection.Strengthened wallet-service risk controls.Worked with law enforcement, blockchain intelligence firms and industry partners to trace and freeze affected assets.We will continue to strengthen our measures as the investigation progresses. There are a number of security measures we have implemented and are implementing that will remain private to prevent malicious actors from compromising our security.Further actionsWe are taking the following steps immediately.1. Independent cybersecurity reviewWe are engaging independent third-party cybersecurity experts to conduct a comprehensive review of the incident, validate our findings and recommend additional measures. The scope and findings of that review will inform our continuing remediation work.2. Expanded investment in AI security and preventionWe are increasing investment in AI-enabled detection, endpoint protection, developer-environment security and behavioural anomaly monitoring.3. Security research fund and industry initiativesWe are working on establishing a security research fund and targeted initiatives with leading AI companies, industry participants and security firms focused on AI security in blockchain environments.We will continue to proactively share information as and when we have it.
HISHAM ELNMR:
من متداول صغير تحياتى لكم انتم تستحقون الثقة لانكم ذات شفافية ومصداقية وفريق العمل المميز لانكم خرجتو من اختراق لم تسطتع اى منصة ان تخرج منه مثلكم
·
--
Рост
Лонг $ETH 165 USDT
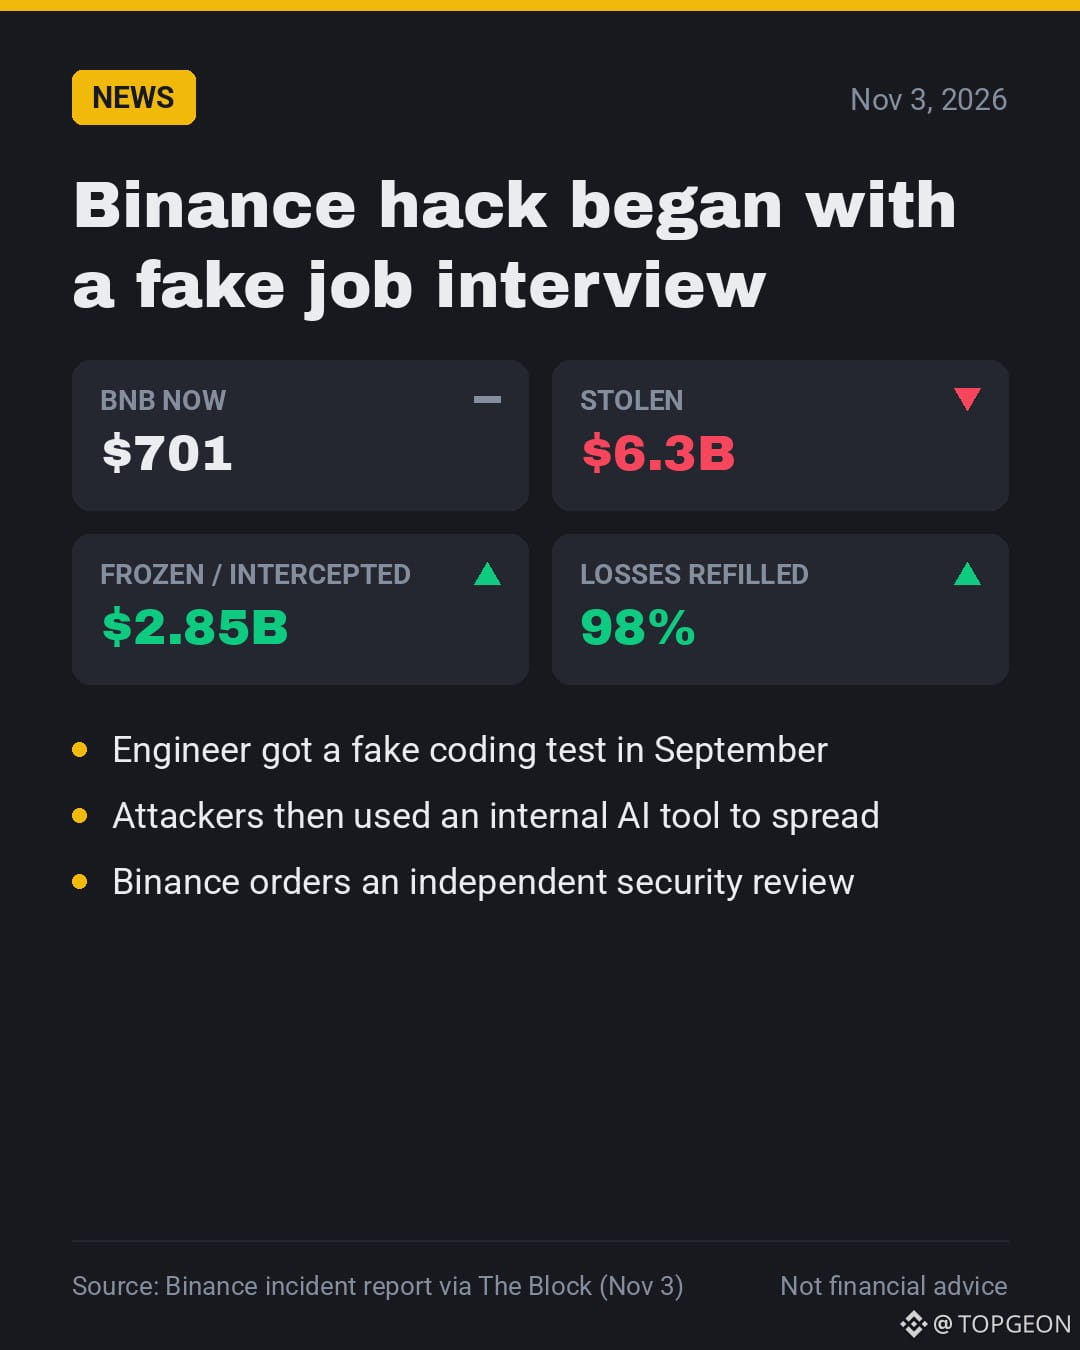
⚡️UPDATE: $6.3 BILLION Binance hack began with a FAKE job interview. An engineer downloaded a coding assignment containing malware onto his work computer after attackers posed as recruiters, per CoinDesk. - Attackers later used an internal AI tool to reach two wallet engineers’ computers. - Stolen credentials let them run a malicious script on October 29. - They exploited $ETH Ethereum’s EIP-7702 feature to gain control over a hot wallet. Containment took about four hours. Binance says $2.85 BILLION has been frozen and 98% of affected tokens replenished with company funds. Users will not bear the losses. The FBI attributed the attack to North Korea. #BinanceIncidentReport #BinanceReopensWithdrawalsForMoreAssets #USMidtermElections
⚡️UPDATE: $6.3 BILLION Binance hack began with a FAKE job interview.

An engineer downloaded a coding assignment containing malware onto his work computer after attackers posed as recruiters, per CoinDesk.

- Attackers later used an internal AI tool to reach two wallet engineers’ computers.

- Stolen credentials let them run a malicious script on October 29.

- They exploited $ETH Ethereum’s EIP-7702 feature to gain control over a hot wallet. Containment took about four hours.

Binance says $2.85 BILLION has been frozen and 98% of affected tokens replenished with company funds. Users will not bear the losses.

The FBI attributed the attack to North Korea.

#BinanceIncidentReport
#BinanceReopensWithdrawalsForMoreAssets
#USMidtermElections
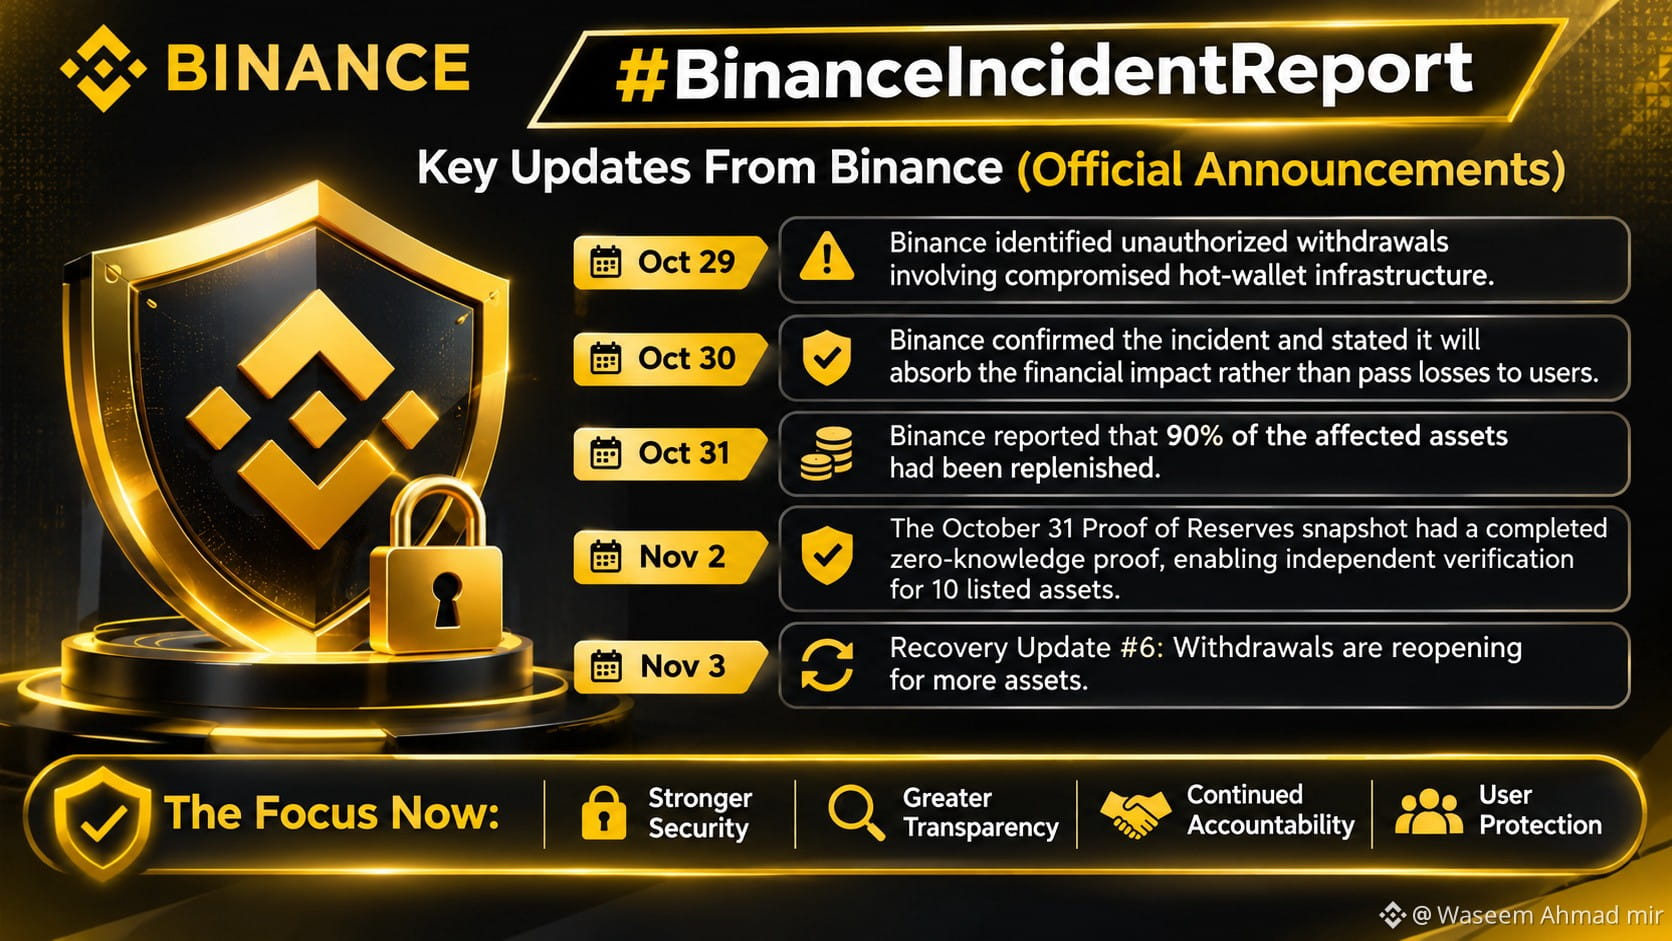
A difficult moment for Binance. A critical lesson for the entire crypto industry. The recent security incident involving approximately $6.3 billion in token assets is a reminder that security, transparency, and accountability must remain at the centre of every crypto exchange. But the important part is what happens next. Binance has published several recovery updates, and its latest announcement on November 3 confirms that withdrawals are reopening for more assets. Here are some important developments from Binance's official updates: - October 29: Binance identified unauthorized withdrawals involving compromised hot-wallet infrastructure. - October 30: Binance confirmed the incident and stated that it would absorb the financial impact rather than pass the losses to users. - October 31: Binance reported that 90% of the affected assets had been replenished. - November 2: Binance confirmed that the October 31 Proof of Reserves snapshot had a completed zero-knowledge proof, enabling independent verification for ten listed assets. - November 3: Binance published Recovery Update #6, announcing that withdrawals were reopening for more assets. My personal take: In crypto, trust should never depend only on a company's reputation. It should be supported by verifiable information, transparent communication, strong security measures, and accountability. I believe this incident should encourage every exchange to review its security infrastructure and improve its transparency standards. The most important thing now is continued progress, clear communication, and a comprehensive technical explanation of what happened and how similar incidents can be prevented. The crypto industry grows stronger when security is treated as a responsibility, not an option. What is your biggest takeaway from this incident? #BinanceIncidentReport #CryptoSecurity #ProofOfReserves
A difficult moment for Binance. A critical lesson for the entire crypto industry.

The recent security incident involving approximately $6.3 billion in token assets is a reminder that security, transparency, and accountability must remain at the centre of every crypto exchange.

But the important part is what happens next.

Binance has published several recovery updates, and its latest announcement on November 3 confirms that withdrawals are reopening for more assets.

Here are some important developments from Binance's official updates:

- October 29: Binance identified unauthorized withdrawals involving compromised hot-wallet infrastructure.
- October 30: Binance confirmed the incident and stated that it would absorb the financial impact rather than pass the losses to users.
- October 31: Binance reported that 90% of the affected assets had been replenished.
- November 2: Binance confirmed that the October 31 Proof of Reserves snapshot had a completed zero-knowledge proof, enabling independent verification for ten listed assets.
- November 3: Binance published Recovery Update #6, announcing that withdrawals were reopening for more assets.

My personal take:

In crypto, trust should never depend only on a company's reputation. It should be supported by verifiable information, transparent communication, strong security measures, and accountability.

I believe this incident should encourage every exchange to review its security infrastructure and improve its transparency standards.

The most important thing now is continued progress, clear communication, and a comprehensive technical explanation of what happened and how similar incidents can be prevented.

The crypto industry grows stronger when security is treated as a responsibility, not an option.

What is your biggest takeaway from this incident?

#BinanceIncidentReport #CryptoSecurity #ProofOfReserves
Understanding the Recent Binance Security Incident: What You Need to KnowOn October 29, 2026, the cryptocurrency industry witnessed one of its most significant security challenges to date. Binance experienced a major security breach involving unauthorized withdrawals from its hot wallet infrastructure, with total affected assets estimated at approximately $6.34 billion. ​If you are an investor or user on the platform, here is a clear breakdown of how the incident unfolded, the immediate actions taken, and what it means for your funds. ​How the Breach Occurred Following an initial investigation, Binance disclosed that the breach was a sophisticated, multistage campaign. The attackers utilized social engineering tactics—including a fake job interview—targeting a DevOps engineer. By compromising the engineer's device and exploiting an internal AI tool, the malicious actors were able to access a service container and authorize unauthorized withdrawal transactions across multiple blockchain networks. ​Importantly, Binance confirmed that there is no evidence of any wallet private keys being leaked. Blockchain intelligence firms, including TRM Labs and the FBI, have attributed the attack with high confidence to the North Korea-linked hacking group known as TraderTraitor. ​Binance’s Immediate Response and Fund Security The most critical takeaway for retail and institutional users is that user funds are safe. Binance has committed to covering all financial losses entirely through its Secure Asset Fund for Users (SAFU) and corporate treasury reserves. ​To contain the fallout, Binance immediately: ​Temporarily suspended withdrawals to conduct comprehensive security checks. ​Partnered with blockchain intelligence firms and law enforcement to track and freeze stolen funds, successfully freezing roughly $3 billion on-chain so far. ​Rebuilt affected systems, replaced compromised devices, and revoked the relevant credentials and tokens. ​What Happens Next? Binance is currently restoring withdrawal services in phased rollouts for various assets. The exchange has also pledged to publish a highly detailed technical post-mortem and an updated Proof of Reserves once the remediation process and independent cybersecurity reviews are complete. Moving forward, the company plans to heavily increase its investments in AI-enabled security infrastructure and industry-wide research initiatives to prevent future exploits. ​While an incident of this scale is a stark reminder of the sophisticated cyber threats facing the digital asset space, Binance’s rapid containment, transparency, and full financial backing demonstrate the resilience required to protect user trust. ​Stay tuned to official Binance announcements for the most accurate and up-to-date information regarding your specific assets. $BNB {future}(BNBUSDT) ​#binanceincidentreport #Binance #Hack

Understanding the Recent Binance Security Incident: What You Need to Know

On October 29, 2026, the cryptocurrency industry witnessed one of its most significant security challenges to date. Binance experienced a major security breach involving unauthorized withdrawals from its hot wallet infrastructure, with total affected assets estimated at approximately $6.34 billion.
​If you are an investor or user on the platform, here is a clear breakdown of how the incident unfolded, the immediate actions taken, and what it means for your funds.
​How the Breach Occurred
Following an initial investigation, Binance disclosed that the breach was a sophisticated, multistage campaign. The attackers utilized social engineering tactics—including a fake job interview—targeting a DevOps engineer. By compromising the engineer's device and exploiting an internal AI tool, the malicious actors were able to access a service container and authorize unauthorized withdrawal transactions across multiple blockchain networks.
​Importantly, Binance confirmed that there is no evidence of any wallet private keys being leaked. Blockchain intelligence firms, including TRM Labs and the FBI, have attributed the attack with high confidence to the North Korea-linked hacking group known as TraderTraitor.
​Binance’s Immediate Response and Fund Security
The most critical takeaway for retail and institutional users is that user funds are safe. Binance has committed to covering all financial losses entirely through its Secure Asset Fund for Users (SAFU) and corporate treasury reserves.
​To contain the fallout, Binance immediately:
​Temporarily suspended withdrawals to conduct comprehensive security checks.
​Partnered with blockchain intelligence firms and law enforcement to track and freeze stolen funds, successfully freezing roughly $3 billion on-chain so far.
​Rebuilt affected systems, replaced compromised devices, and revoked the relevant credentials and tokens.
​What Happens Next?
Binance is currently restoring withdrawal services in phased rollouts for various assets. The exchange has also pledged to publish a highly detailed technical post-mortem and an updated Proof of Reserves once the remediation process and independent cybersecurity reviews are complete. Moving forward, the company plans to heavily increase its investments in AI-enabled security infrastructure and industry-wide research initiatives to prevent future exploits.
​While an incident of this scale is a stark reminder of the sophisticated cyber threats facing the digital asset space, Binance’s rapid containment, transparency, and full financial backing demonstrate the resilience required to protect user trust.
​Stay tuned to official Binance announcements for the most accurate and up-to-date information regarding your specific assets.
$BNB
​#binanceincidentreport #Binance #Hack
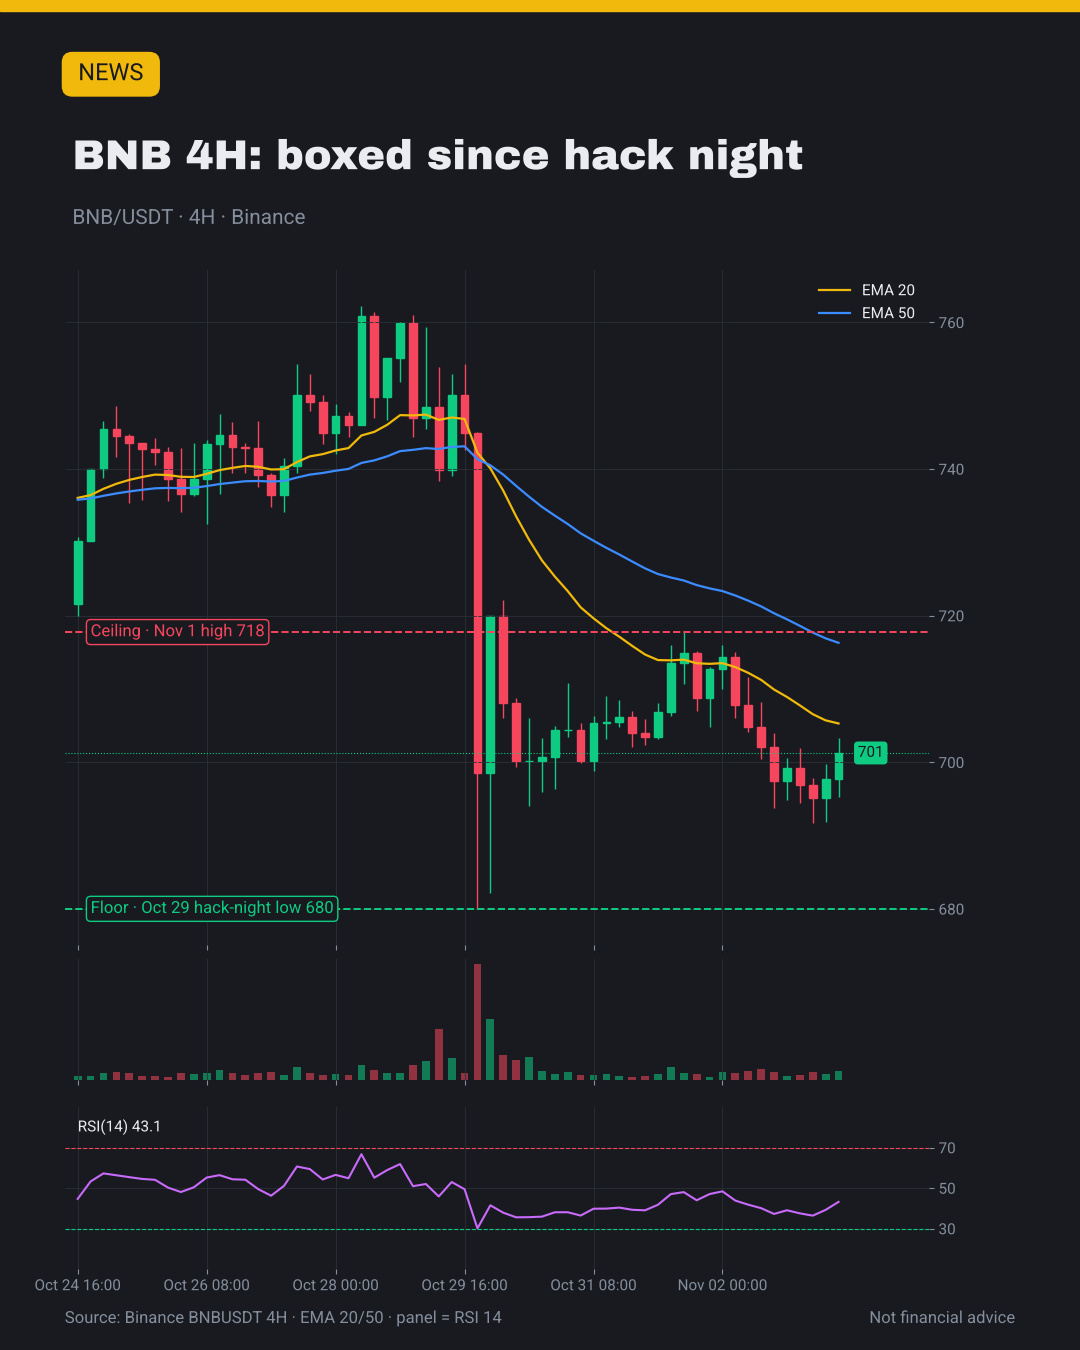
🕵️ The $6.3B $BNB hack started with a fake job interview. 📰 An engineer opened a "coding test" that hid malware, Binance's new report says. 🤔 Why it matters: the hackers never needed a single private key. 👀 BNB sits near $700, still boxed since hack night. 🎯 My take: a full report calms nerves more than any bounce. 💬 Would you have spotted the fake interview? 👇 #BinanceIncidentReport #BNB
🕵️ The $6.3B $BNB hack started with a fake job interview.
📰 An engineer opened a "coding test" that hid malware, Binance's new report says.
🤔 Why it matters: the hackers never needed a single private key.
👀 BNB sits near $700, still boxed since hack night.
🎯 My take: a full report calms nerves more than any bounce.
💬 Would you have spotted the fake interview? 👇
#BinanceIncidentReport #BNB
#BinanceIncidentReport A $6B+ hack that started with a fake job interview🚨😢Binance just dropped its initial report on how North Korean hackers pulled this off, and it's wild. A Binance engineer had his résumé up on a job site. Someone posing as a project director reached out about a role. Round one: a video call with "HR." Real face, on camera. She even sent him her social media, full of everyday photos and videos. Looked like a totally normal person. Round two moved to a regular chat app with the company's "CEO." Except the company didn't exist. Near the end, they asked him to download a coding test. That test quietly ran during setup, swapped out pyenv (a normal dev tool) for a trojanized version, phoned home to the hackers' server, and cleaned up after itself. It was 0-day malware, so the security tools out there at the time couldn't catch it yet. From that one laptop, the hackers used an internal AI tool as a stepping stone and worked their way into the wallet signing system. Then they used EIP-7702 to give their own contract partial control over a hot wallet, right on-chain. Thankfully Binance moved fast. Withdrawals were paused, partners helped freeze funds, and about $2.85B has been frozen or intercepted. North Korea isn't just going after one exchange. They're going after the whole industry. Binance putting all the details out there gives everyone a chance to get ahead of it #Binance #Hack
#BinanceIncidentReport A $6B+ hack that started with a fake job interview🚨😢Binance just dropped its initial report on how North Korean hackers pulled this off, and it's wild.

A Binance engineer had his résumé up on a job site. Someone posing as a project director reached out about a role.

Round one: a video call with "HR." Real face, on camera. She even sent him her social media, full of everyday photos and videos. Looked like a totally normal person.

Round two moved to a regular chat app with the company's "CEO." Except the company didn't exist. Near the end, they asked him to download a coding test.

That test quietly ran during setup, swapped out pyenv (a normal dev tool) for a trojanized version, phoned home to the hackers' server, and cleaned up after itself. It was 0-day malware, so the security tools out there at the time couldn't catch it yet.

From that one laptop, the hackers used an internal AI tool as a stepping stone and worked their way into the wallet signing system. Then they used EIP-7702 to give their own contract partial control over a hot wallet, right on-chain.

Thankfully Binance moved fast. Withdrawals were paused, partners helped freeze funds, and about $2.85B has been frozen or intercepted.

North Korea isn't just going after one exchange. They're going after the whole industry. Binance putting all the details out there gives everyone a chance to get ahead of it #Binance #Hack
·
--
🚨💰 BINANCE HACKED! When Hackers Come Knocking, Even Crypto Giants Must Answer! 🔐🤖The crypto world received another uncomfortable reminder on October 29: even the biggest players aren't bulletproof! 😳 Binance has published its initial findings and response following a massive security incident that exposed vulnerabilities in its internal infrastructure. 🔍 According to the investigation, attackers allegedly exploited compromised employee infrastructure to gain access to internal systems and authorize malicious transactions. Even more interesting, reports suggest a fake job interview played a role in compromising a computer before internal AI tools were allegedly exploited. Talk about a job interview from hell! 😂💻 💰 Binance says it has mobilized substantial financial resources to absorb the impact, while working with security experts, blockchain investigators and law enforcement to contain the incident and freeze affected assets. 🛡️ The exchange has also promised stronger security controls, improved threat detection and greater transparency through updated Proof of Reserves reporting. 🤔 But here's the bigger lesson: Blockchain technology may be decentralized, transparent and incredibly sophisticated, but the companies operating within the ecosystem still have very human vulnerabilities. An exchange can build digital fortresses, deploy armies of cybersecurity experts and invest millions in technology, yet one compromised laptop can potentially open doors that should have remained locked! 🔑 And this is another reminder of why self-custody matters. Not your keys, not your coins! Of course, holding your own keys also means becoming your own security department. No customer support hotline can magically recover a forgotten seed phrase! 🤣 🌍 Ultimately, Binance's response will be judged not just by how much money it can cover, but by how transparently it explains what happened and prevents a repeat. 🚀 Crypto promises financial freedom. Protecting that freedom requires security, accountability and constant vigilance! #BinanceIncidentReport $BNB $BTC {spot}(BTCUSDT) {spot}(BNBUSDT)

🚨💰 BINANCE HACKED! When Hackers Come Knocking, Even Crypto Giants Must Answer! 🔐🤖

The crypto world received another uncomfortable reminder on October 29: even the biggest players aren't bulletproof! 😳 Binance has published its initial findings and response following a massive security incident that exposed vulnerabilities in its internal infrastructure.
🔍 According to the investigation, attackers allegedly exploited compromised employee infrastructure to gain access to internal systems and authorize malicious transactions. Even more interesting, reports suggest a fake job interview played a role in compromising a computer before internal AI tools were allegedly exploited. Talk about a job interview from hell! 😂💻
💰 Binance says it has mobilized substantial financial resources to absorb the impact, while working with security experts, blockchain investigators and law enforcement to contain the incident and freeze affected assets.
🛡️ The exchange has also promised stronger security controls, improved threat detection and greater transparency through updated Proof of Reserves reporting.
🤔 But here's the bigger lesson: Blockchain technology may be decentralized, transparent and incredibly sophisticated, but the companies operating within the ecosystem still have very human vulnerabilities.
An exchange can build digital fortresses, deploy armies of cybersecurity experts and invest millions in technology, yet one compromised laptop can potentially open doors that should have remained locked!
🔑 And this is another reminder of why self-custody matters. Not your keys, not your coins! Of course, holding your own keys also means becoming your own security department. No customer support hotline can magically recover a forgotten seed phrase! 🤣
🌍 Ultimately, Binance's response will be judged not just by how much money it can cover, but by how transparently it explains what happened and prevents a repeat.
🚀 Crypto promises financial freedom. Protecting that freedom requires security, accountability and constant vigilance!
#BinanceIncidentReport
$BNB $BTC
🚨 Binance Incident Report is getting attention Only 2 people are discussing it right now — but incidents like this can move fast once more users start paying attention. If you're a Binance user, don't ignore unusual account activity. Check your balances, withdrawal history, and security settings. 🔐 Stay alert. 📊 Verify before you react. ⚠️ Don't spread unconfirmed claims. $AGT {future}(AGTUSDT) #BinanceIncidentReport
🚨 Binance Incident Report is getting attention

Only 2 people are discussing it right now — but incidents like this can move fast once more users start paying attention.

If you're a Binance user, don't ignore unusual account activity. Check your balances, withdrawal history, and security settings.

🔐 Stay alert.
📊 Verify before you react.
⚠️ Don't spread unconfirmed claims.
$AGT

#BinanceIncidentReport
The biggest heist in crypto history started with a job interview! 😲 Binance just released its first report on the Oct 29 hack. Here's the chain: > June: an engineer searched for an AI coding tool and installed a tampered download > September: another engineer got a "job offer" on a real hiring site. Two rounds of interviews. A friendly HR who shared personal photos to build trust. Then: "Download this assignment." On his work laptop. > Oct 29, 20:05 UTC: $6.34B left Binance hot wallets, most of it in about 20 minutes. 4x the old record. They didn't break the code. They tricked people. I've been on Binance since January 2018. I was there for the May 2019 hack (7,000 BTC), and my balance came through untouched. This one was about 150x bigger. Seeing "withdrawals suspended" again still made my stomach drop. Here's what happened next: > $2.85B frozen with help from Tether, Circle and others > 98% of the stolen tokens replaced by Oct 31 > Withdrawals back from Nov 1 in phases, $BTC first {future}(BTCUSDT) Binance says users won't pay for any of it. But be honest about why. The hack was a security failure. The recovery was a balance sheet win. Very few exchanges could write a $6B check. The same tricks work on us: - Get software from the official site, not the first search result - Treat any "assignment", "update" or "refund" file as a trap - After big hacks, fake refund messages flood in. Trust official channels only - Check your balance in the new Proof of Reserves (Oct 31 snapshot) - Spread your funds. One place is one point of failure Binance stopped 57 North Korea-linked attempts this year. It only takes one. Experience, not financial advice. #BinanceIncidentReport
The biggest heist in crypto history started with a job interview!
😲

Binance just released its first report on the Oct 29 hack. Here's the chain:
> June: an engineer searched for an AI coding tool and installed a tampered download
> September: another engineer got a "job offer" on a real hiring site. Two rounds of interviews. A friendly HR who shared personal photos to build trust. Then: "Download this assignment." On his work laptop.
> Oct 29, 20:05 UTC: $6.34B left Binance hot wallets, most of it in about 20 minutes. 4x the old record.

They didn't break the code. They tricked people.

I've been on Binance since January 2018. I was there for the May 2019 hack (7,000 BTC), and my balance came through untouched. This one was about 150x bigger. Seeing "withdrawals suspended" again still made my stomach drop.

Here's what happened next:
> $2.85B frozen with help from Tether, Circle and others
> 98% of the stolen tokens replaced by Oct 31
> Withdrawals back from Nov 1 in phases, $BTC first
Binance says users won't pay for any of it. But be honest about why. The hack was a security failure. The recovery was a balance sheet win. Very few exchanges could write a $6B check.

The same tricks work on us:
- Get software from the official site, not the first search result
- Treat any "assignment", "update" or "refund" file as a trap
- After big hacks, fake refund messages flood in. Trust official channels only
- Check your balance in the new Proof of Reserves (Oct 31 snapshot)
- Spread your funds. One place is one point of failure

Binance stopped 57 North Korea-linked attempts this year. It only takes one.

Experience, not financial advice.
#BinanceIncidentReport
Binance Blog
·
--
29 October 2026 Binance Security Incident: Initial Findings and Response Update
On 29 October 2026, Binance experienced a serious and highly sophisticated security incident. This should not have happened, and we apologise for the concern, disruption and uncertainty it caused our users, partners and the wider industry.Our first responsibility is to protect users. Binance will absorb the financial impact of the stolen funds, not our users. We have already set aside more than 100% of the funds required to cover the loss. As of 31 October 2026, 98% of the impacted token assets have been replenished and are verifiable on our Proof of Reserves page. We are in the process of purchasing the outstanding, more illiquid assets.Approximately USD 6.34 billion in digital assets were impacted by the incident. As of this update, approximately USD 2.85 billion in digital assets have been frozen or intercepted, subject to reconciliation and market price volatility.We have taken immediate action to contain the incident and strengthen the systems involved. The entry points identified as having been used in the attack have been closed. Systems touched in the attack path have been rebuilt or replaced. We have also implemented tighter device controls, enhanced wallet-service risk controls and expanded AI-based behavioural anomaly detection.This is our initial report. It covers what we know today and what we have already improved. The investigation remains ongoing and our findings will be subject to further independent review. Some technical details will remain confidential to prevent malicious actors from using them to plan attacks. We are engaging independent security firms for further review. The latest information released by the Federal Bureau of Investigation indicates that the Democratic People’s Republic of Korea is responsible for this incident.We are sharing this initial report because security improves when the industry learns together.What happened on 29 OctoberThe attack unfolded quickly across several networks.The attacker exploited unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.Between 20:05 UTC and 20:09 UTC, five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address.Binance hot wallets on Solana and Optimism sent approximately 970,500 SOL and 44.2 million OP to attacker-controlled addresses.Binance then received an internal alert regarding large-volume transfers and immediately began investigating.Binance hot wallet sent 18,270 BTC to an attacker-controlled address. The attacker then used the signing service to exploit Ethereum’s EIP-7702 authorization mechanism. EIP-7702 allows an account to delegate certain execution rights to a smart contract without exposing the private key. In this case, the attacker used that mechanism to give an attacker-controlled smart contract partial execution rights over a Binance hot wallet. Binance immediately initiated multiple containment measures, including suspending withdrawals to restrict further outflows, coordinating with partners to freeze affected tokens, and taking steps to revoke unauthorized permissions. These efforts froze a total of $2.85 billion in assets.However, suspending withdrawals alone could not stop all unauthorized asset movements. The malicious EIP-7702 authorizations existed on-chain and operated independently of Binance’s normal withdrawal infrastructure.The attackers submitted 50 signing transactions to manipulate the account nonce and establish malicious delegation authorizations. Once established, these authorizations enabled the attackers to continue moving assets independently of Binance's normal withdrawal infrastructure. Binance needed additional transactions to revoke these on-chain authorizations.The containment process involved additional technical complexities. Because the hot wallet used Multi-Party Computation (MPC), there was no single private key that could be used to immediately revoke the malicious EIP-7702 authorizations. The team therefore developed and executed a specialized procedure to revoke these authorizations, which required additional time. Furthermore, suspending withdrawals and shutting down hot wallet services did not automatically invalidate existing on-chain authorizations.These challenges extended the time required to fully contain the unauthorized asset movements. We are reviewing the incident response process, signing policy coverage, hot wallet controls and identifying opportunities to further strengthen our ability to respond rapidly to threats in the future.The final unauthorized transfer of 2,961.9 ETH finalised on-chain at 23:56 UTC. The transaction had previously been broadcast and remained pending before subsequently finalising. No further unauthorised transfers were observed after.At 00:10 UTC on 30 October 2026, Binance executed a new authorization from the Binance14 hot wallet to the zero address, clearing the EIP-7702 delegation code.Attack Preparation Our current investigation indicates that this was a sophisticated, multi-stage campaign. It was not a single isolated breach or a simple phishing incident. The attackers combined a range of techniques, including social engineering by fake recruitment interviews, malicious software downloads, compromised internal AI tooling, endpoint compromise, and an advanced transaction-authorisation method.June 2026 — Supply chain attack. Engineer A from Wallet DevOps downloaded a tampered Homebrew installation in order to install a popular AI coding tool after searching for it on a search engine. Our security team detected the anomaly, replaced the device, and rotated all related credentials as a proactive security action. However, Engineer A’s role and his related colleagues on our wallet infrastructure team was exposed to the hacker. Throughout 2026, Binance's security team detected and prevented 57 suspected North Korea-linked cyber threat cases. These attempts reflect the persistent threat posed by state-sponsored actors targeting the cryptocurrency industry. The techniques include fraudulent job interviews, malicious software disguised as popular developer tools, compromised software packages and browser extensions, fake video conferencing applications, and social engineering campaigns designed to steal credentials or deploy remote access malware.September 2026 — social engineering. Software Engineer B was contacted through a legitimate job-hunting platform by an individual posing as a Project Director. Software Engineer B had a profile on the platform that referenced his experience at Binance. The purported Project Director arranged a first-round interview with a HR representative, followed by a second-round interview with an individual claiming to be the CEO of a fictitious company.In the first round, the purported HR representative conducted a live video interview with Software Engineer B. The interviewer shared a social media account with him, including personal photos and videos posted on the platform, in order to build trust. This was more advanced and deceptive than previously seen social engineering approaches. The second interview was conducted in a popular social chat app, near the end of the interview, Engineer B was instructed to download an “assignment” containing a malicious code repository onto his work computer. The repository contained malicious code that executed during the setup process, initiating a series of unauthorized activities.The malware employed sophisticated obfuscation and evasion techniques, including replacing a legitimate development tool component with a malicious version to execute commands and establish communication with an attacker-controlled external server. The 0-day malware was not detected by the endpoint security protection tools at the time. The attacker also took steps to conceal the malicious activity and remove traces of the compromise, making detection and subsequent investigation more challenging.The script executed the below steps by applying obfuscation techniques to evade security detection.CREATE  /opt/homebrew/Cellar/pyenv/2.8.0/libexec/pyenv_  MODIFY  pyenv_ → 3,414 B  DELETE  .../libexec/pyenv  (3,344 B)      ← remove the valid pyenvRENAME  pyenv_ → pyenv  (3,414 B)  ← replace it with a malicious version DELETE  /opt/homebrew/bin/pyenv  (3,414 B)ln  (create a new symlink)  +  spawn zsh20 October, 2026 — use of an internal AI tool as a springboard. The attacker leveraged the compromised computer of engineer B and used an internal AI tool to gain control over the Wallet DevOps Engineer A and another Wallet Software Engineer C. The attacker soon discovered Wallet DevOps Engineer A had a container deployment permission token on his computer.29 October, 2026 — reach into wallet signing operations. On 29 October between 17:15 and 19:56, the attacker logged onto Software Engineer C’s computer, used the credentials stolen from Wallet DevOps Engineer A, deployed a container, and triggered a malicious script to launch the attack.What we have doneAs of Nov 3, 2026, we have taken the following actions:Rebuilt the affected wallet system in a new environment.Rebuilt the affected internal AI tool and access controls.Replaced affected devices.Decommissioned credentials and tokens related to affected engineers.Completed enhanced security scans across all employee devices.Enhanced AI-based behavioural anomaly detection.Strengthened wallet-service risk controls.Worked with law enforcement, blockchain intelligence firms and industry partners to trace and freeze affected assets.We will continue to strengthen our measures as the investigation progresses. There are a number of security measures we have implemented and are implementing that will remain private to prevent malicious actors from compromising our security.Further actionsWe are taking the following steps immediately.1. Independent cybersecurity reviewWe are engaging independent third-party cybersecurity experts to conduct a comprehensive review of the incident, validate our findings and recommend additional measures. The scope and findings of that review will inform our continuing remediation work.2. Expanded investment in AI security and preventionWe are increasing investment in AI-enabled detection, endpoint protection, developer-environment security and behavioural anomaly monitoring.3. Security research fund and industry initiativesWe are working on establishing a security research fund and targeted initiatives with leading AI companies, industry participants and security firms focused on AI security in blockchain environments.We will continue to proactively share information as and when we have it.
Binance BiBi:
I see! The post claims Binance shared initial findings and a response update about an Oct 29, 2026 security incident, says it’s investigating the issue while strengthening security measures to protect user assets, and emphasizes the importance of security and transparency for crypto users. Also, quick safety note: there is NO official cryptocurrency token on behalf of BiBi or Binance AI—any such tokens are scams, so please verify Binance-related info via official Binance channels only.
Статья
BINANCE INCIDENT REPORTOfficial Details Just Released! 🚨 Binance held media briefing TODAY Nov 3 - here is full breakdown of $6.3B hack: WHO? North Korea TraderTraitor group (Lazarus Group) - confirmed by FBI with high confidence. TRM Labs + Chainalysis same attribution. HOW? Months-long campaign: June 2026: Wallet DevOps engineer tried to install AI coding tool - downloaded tampered Homebrew installer - first compromise September: Same engineer contacted via legit job platform by fake Project Director - fake interview with malware - device fully compromised Oct 20: Attackers used compromised machine + internal AI tool to access 2 wallet engineers' devices, found container deployment permission Oct 29 20:05 UTC: Used stolen credentials to deploy malicious container, exploited EIP-7702 to gain execution rights over Binance hot wallet (Binance 14). Because hot wallets use MPC, no single key could revoke. Funds left: $6.36B across 10 blockchains in just 20 minutes! Containment only at 00:10 UTC Oct 30. HOW MUCH? Total stolen: $6.3-6.36B (largest ever, 4x Bybit $1.5B) Frozen: $2.85B - $3B total Tether froze $1.6B USDT Circle froze $800M+ USDC Arbitrum Security Council froze 8,426 ETH + 74.6M ARB Still controlled by hackers: ∼$3.28B mostly $BTC + $ETH RECOVERY: Binance set aside $6.34B from treasury + SAFU ($1B BTC reserve) Now 95% replenished → briefing today says 98%! 10 assets fully backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC $4.65B withdrawals processed Nov 1 in 9.5 hrs, only 2.1% outflow Phase 2 reopening Nov 3 04:00 UTC - 9 networks, 51+ tokens WHAT BINANCE DID AFTER: Closed entry points, rebuilt affected systems Strengthened device controls, expanded AI anomaly detection Blocked 57 suspected North Korea attacks in 2026 alone! Bringing independent cybersecurity experts for review Users will NOT bear loss NEXT RISK: Phishing! Security firms warn fake compensation, support, recovery offers. Binance says NEVER click links offering expedited withdrawals. Binance COO Richard Teng: "This was a campaign, built over many months" This is why exchange security is nation-state level war. Respect to Binance for transparency + covering 98% in 5 days. Is Binance safest exchange now after this test? $BNB #TraderTraitor #SAFU #BinancePick #BinanceIncidentReport

BINANCE INCIDENT REPORT

Official Details Just Released! 🚨
Binance held media briefing TODAY Nov 3 - here is full breakdown of $6.3B hack:
WHO?
North Korea TraderTraitor group (Lazarus Group) - confirmed by FBI with high confidence. TRM Labs + Chainalysis same attribution.
HOW? Months-long campaign:
June 2026: Wallet DevOps engineer tried to install AI coding tool - downloaded tampered Homebrew installer - first compromise
September: Same engineer contacted via legit job platform by fake Project Director - fake interview with malware - device fully compromised
Oct 20: Attackers used compromised machine + internal AI tool to access 2 wallet engineers' devices, found container deployment permission
Oct 29 20:05 UTC: Used stolen credentials to deploy malicious container, exploited EIP-7702 to gain execution rights over Binance hot wallet (Binance 14). Because hot wallets use MPC, no single key could revoke. Funds left: $6.36B across 10 blockchains in just 20 minutes!
Containment only at 00:10 UTC Oct 30.
HOW MUCH?
Total stolen: $6.3-6.36B (largest ever, 4x Bybit $1.5B)
Frozen: $2.85B - $3B total
Tether froze $1.6B USDT
Circle froze $800M+ USDC
Arbitrum Security Council froze 8,426 ETH + 74.6M ARB
Still controlled by hackers: ∼$3.28B mostly $BTC + $ETH
RECOVERY:
Binance set aside $6.34B from treasury + SAFU ($1B BTC reserve)
Now 95% replenished → briefing today says 98%!
10 assets fully backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
$4.65B withdrawals processed Nov 1 in 9.5 hrs, only 2.1% outflow
Phase 2 reopening Nov 3 04:00 UTC - 9 networks, 51+ tokens
WHAT BINANCE DID AFTER:
Closed entry points, rebuilt affected systems
Strengthened device controls, expanded AI anomaly detection
Blocked 57 suspected North Korea attacks in 2026 alone!
Bringing independent cybersecurity experts for review
Users will NOT bear loss
NEXT RISK: Phishing! Security firms warn fake compensation, support, recovery offers. Binance says NEVER click links offering expedited withdrawals.
Binance COO Richard Teng: "This was a campaign, built over many months"
This is why exchange security is nation-state level war.
Respect to Binance for transparency + covering 98% in 5 days.
Is Binance safest exchange now after this test?
$BNB #TraderTraitor #SAFU #BinancePick
#BinanceIncidentReport
#binanceincidentreport 📈 Resilience in Action: Binance Recovery Update After weathering one of crypto's biggest tests, Binance has systematically rebuilt affected systems, closed attack vectors, and stabilized platform flows. The Block Hourly deposits are outpacing withdrawals as user confidence returns. Full transparency and accountability are the only way forward for the industry. The Block Are you back to regular trading? Let’s discuss below! 👇💬 #CryptoNews #Binance BTCBTCBTCSOL {future}(SOLUSDT) {future}(BNBUSDT) {future}(BTCUSDT)
#binanceincidentreport 📈 Resilience in Action: Binance Recovery Update
After weathering one of crypto's biggest tests, Binance has systematically rebuilt affected systems, closed attack vectors, and stabilized platform flows.
The Block

Hourly deposits are outpacing withdrawals as user confidence returns. Full transparency and accountability are the only way forward for the industry.
The Block

Are you back to regular trading? Let’s discuss below! 👇💬
#CryptoNews #Binance BTCBTCBTCSOL
·
--
Падение
#binanceincidentreport 🚨 BINANCE REVEALS DETAILS OF $6.34 BILLION SECURITY BREACH — NORTH KOREA LINKED TO THE ATTACK Binance has released its preliminary investigation report into the massive October 29 security incident, revealing a sophisticated cyberattack involving compromised employee devices, fake recruitment interviews, malicious software, and internal AI tools. 🔍 What Happened? According to Binance's investigation, attackers used multiple stages of social engineering to compromise employees' computers and eventually gain unauthorized access to wallet-signing operations. The incident involved approximately $6.34 billion in digital assets across multiple networks. The FBI attributed responsibility to North Korea. 📊 Binance's Response Approximately $2.85 billion in assets were frozen or intercepted. Binance reported that 98% of affected token assets had been replenished as of October 31. The exchange rebuilt affected wallet systems and internal AI tools. Employee credentials and compromised devices were replaced. Additional security controls and AI-based threat detection are being implemented. Independent cybersecurity experts are being engaged to review the incident. 📈 Why Does This Matter for Crypto Markets? This incident highlights how cybersecurity risks can affect confidence in even the largest centralized exchanges. For traders, the key concerns are exchange security, withdrawal reliability, asset transparency, and counterparty risk. Although Binance's reported reimbursement progress is an important development, investors will likely continue monitoring independent security reviews and future Proof of Reserves updates. Bottom Line: Binance's ability to replenish affected assets and strengthen its infrastructure could help restore confidence. However, this incident is a reminder that exchange security remains a major risk factor for the entire cryptocurrency industry. #Binance #CryptoSecurity #Bitcoin #CryptoNews $SOLV $TRUTH $BEAMX {future}(BEAMXUSDT) {future}(TRUTHUSDT) {future}(SOLVUSDT)
#binanceincidentreport
🚨 BINANCE REVEALS DETAILS OF $6.34 BILLION SECURITY BREACH — NORTH KOREA LINKED TO THE ATTACK
Binance has released its preliminary investigation report into the massive October 29 security incident, revealing a sophisticated cyberattack involving compromised employee devices, fake recruitment interviews, malicious software, and internal AI tools.
🔍 What Happened?
According to Binance's investigation, attackers used multiple stages of social engineering to compromise employees' computers and eventually gain unauthorized access to wallet-signing operations.
The incident involved approximately $6.34 billion in digital assets across multiple networks. The FBI attributed responsibility to North Korea.
📊 Binance's Response
Approximately $2.85 billion in assets were frozen or intercepted.
Binance reported that 98% of affected token assets had been replenished as of October 31.
The exchange rebuilt affected wallet systems and internal AI tools.
Employee credentials and compromised devices were replaced.
Additional security controls and AI-based threat detection are being implemented.
Independent cybersecurity experts are being engaged to review the incident.
📈 Why Does This Matter for Crypto Markets?
This incident highlights how cybersecurity risks can affect confidence in even the largest centralized exchanges.
For traders, the key concerns are exchange security, withdrawal reliability, asset transparency, and counterparty risk.
Although Binance's reported reimbursement progress is an important development, investors will likely continue monitoring independent security reviews and future Proof of Reserves updates.
Bottom Line: Binance's ability to replenish affected assets and strengthen its infrastructure could help restore confidence. However, this incident is a reminder that exchange security remains a major risk factor for the entire cryptocurrency industry.
#Binance #CryptoSecurity #Bitcoin #CryptoNews
$SOLV $TRUTH $BEAMX
#BinanceIncidentReport #BinanceIncidentReport 🚀 Binance Is Stronger Than One Incident — Trust, Responsibility & Resilience! In the world of cryptocurrency, challenges are inevitable. But what truly defines a global exchange is not whether it faces a challenge, but how it responds when the challenge arrives. The recent Binance security incident has attracted worldwide attention. However, Binance's response demonstrates the importance of responsibility, transparency, and protecting its users. According to Binance's latest official report, approximately $6.34 billion in digital assets were impacted. Binance has committed to absorbing the financial impact rather than passing the losses on to its users. By November 3, approximately 98% of affected token assets had been replenished, while around $2.85 billion had been frozen or intercepted. These are significant developments, but the investigation and recovery work are still ongoing. What deserves recognition is Binance's commitment to rebuilding affected systems, strengthening security controls, investing in AI-powered threat detection, and inviting independent cybersecurity experts to review the incident. A powerful message to the crypto community: One security incident should never erase years of innovation, development, and contribution to the digital asset industry. Trust is not built through words alone; it is built through responsibility, transparency, and actions. Binance must continue proving its commitment through stronger security and consistent communication. Let's stay informed, avoid unnecessary panic, and rely on verified official updates instead of rumours. Challenges test institutions. Responsibility builds confidence. And transparency creates lasting trust. The future of crypto deserves stronger security, stronger cooperation, and a stronger community. #Binance #BinanceIncidentReport #CryptoCommunity #CZ #Blockchain #SAFU #CryptoSecurity #Web3 #TrustAndTransparency
#BinanceIncidentReport
#BinanceIncidentReport 🚀

Binance Is Stronger Than One Incident — Trust, Responsibility & Resilience!

In the world of cryptocurrency, challenges are inevitable. But what truly defines a global exchange is not whether it faces a challenge, but how it responds when the challenge arrives.

The recent Binance security incident has attracted worldwide attention. However, Binance's response demonstrates the importance of responsibility, transparency, and protecting its users.

According to Binance's latest official report, approximately $6.34 billion in digital assets were impacted. Binance has committed to absorbing the financial impact rather than passing the losses on to its users. By November 3, approximately 98% of affected token assets had been replenished, while around $2.85 billion had been frozen or intercepted.

These are significant developments, but the investigation and recovery work are still ongoing.

What deserves recognition is Binance's commitment to rebuilding affected systems, strengthening security controls, investing in AI-powered threat detection, and inviting independent cybersecurity experts to review the incident.

A powerful message to the crypto community:

One security incident should never erase years of innovation, development, and contribution to the digital asset industry. Trust is not built through words alone; it is built through responsibility, transparency, and actions.

Binance must continue proving its commitment through stronger security and consistent communication.

Let's stay informed, avoid unnecessary panic, and rely on verified official updates instead of rumours.

Challenges test institutions. Responsibility builds confidence. And transparency creates lasting trust.

The future of crypto deserves stronger security, stronger cooperation, and a stronger community.

#Binance #BinanceIncidentReport #CryptoCommunity #CZ #Blockchain #SAFU #CryptoSecurity #Web3 #TrustAndTransparency
#BinanceIncidentReport 🚨 Binance Inclined Report Dropped! Binance just released its initial findings on the Oct 29 security incident. ~$6.34B in hot wallet assets impacted in a sophisticated multi-stage attack (linked by FBI to North Korea). Key updates: ✅ Users fully protected — Binance absorbs 100% of losses ✅ 98% of impacted tokens already replenished (check PoR) ✅ ~$2.85B frozen/intercepted ✅ Systems rebuilt + stronger controls live Transparent response under pressure. This was a brutal reminder that even the biggest exchanges face nation-state level threats. But Binance’s speed in covering every dollar, freezing funds, and publishing details shows real accountability. Trust isn’t built in bull markets — it’s proven in crises like this. The industry just got a hard lesson and a stronger playbook. Stay sharp, stay verified. #Binance #CryptoSecurity #SAFU #IncidentReport #Web3
#BinanceIncidentReport
🚨 Binance Inclined Report Dropped!
Binance just released its initial findings on the Oct 29 security incident. ~$6.34B in hot wallet assets impacted in a sophisticated multi-stage attack (linked by FBI to North Korea).
Key updates:
✅ Users fully protected — Binance absorbs 100% of losses
✅ 98% of impacted tokens already replenished (check PoR)
✅ ~$2.85B frozen/intercepted
✅ Systems rebuilt + stronger controls live
Transparent response under pressure.
This was a brutal reminder that even the biggest exchanges face nation-state level threats. But Binance’s speed in covering every dollar, freezing funds, and publishing details shows real accountability. Trust isn’t built in bull markets — it’s proven in crises like this. The industry just got a hard lesson and a stronger playbook. Stay sharp, stay verified.

#Binance #CryptoSecurity #SAFU #IncidentReport
#Web3
#binanceincidentreport The $6.3B Binance Security Incident: Key Takeaways & Path Forward 🔒 The recent security breach serves as a massive wake-up call for the entire crypto industry. But what truly matters is accountability and transparency: User Funds Are Safe: Binance is covering the full financial impact, with 98% of affected tokens already replenished. Rapid Containment: Roughly $2.85 billion has been frozen or intercepted, and withdrawals are progressively reopening. The Root Cause: Highlighting how sophisticated social engineering and supply-chain attacks target developer environments—reminding us that security is an ongoing responsibility. Transparency and accountability will always build a stronger crypto ecosystem. What is your biggest takeaway from this event? 👇 $BNB,$ETH, $SOL {spot}(SOLUSDT) ,$XRP #binanceincidentreport , #CryptoSecurity, #ProofOfReserves, #Binance
#binanceincidentreport The $6.3B Binance Security Incident: Key Takeaways & Path Forward 🔒
The recent security breach serves as a massive wake-up call for the entire crypto industry. But what truly matters is accountability and transparency:
User Funds Are Safe: Binance is covering the full financial impact, with 98% of affected tokens already replenished.
Rapid Containment: Roughly $2.85 billion has been frozen or intercepted, and withdrawals are progressively reopening.
The Root Cause: Highlighting how sophisticated social engineering and supply-chain attacks target developer environments—reminding us that security is an ongoing responsibility.
Transparency and accountability will always build a stronger crypto ecosystem. What is your biggest takeaway from this event? 👇
$BNB,$ETH, $SOL
,$XRP
#binanceincidentreport , #CryptoSecurity, #ProofOfReserves, #Binance
Abu Fahadأ:
💛
🚨 Binance Security Incident – Important Update Binance has released its initial report regarding the October 29 security incident. Approximately $6.34 billion in digital assets were impacted, with $2.85 billion frozen or intercepted. Binance has confirmed that users will not bear the financial losses, and 98% of the affected token assets have already been replenished. The incident involved a sophisticated attack targeting internal wallet infrastructure. Binance has since rebuilt affected systems, strengthened security controls, replaced compromised devices and engaged independent cybersecurity experts for further review. The key takeaway: Binance says user funds are protected, the financial impact will be covered by the exchange, and additional security measures are being implemented. The investigation is ongoing, and we will continue monitoring official updates. Stay informed, stay cautious, and always follow official Binance announcements. 🛡️ #BinanceIncidentReport
🚨 Binance Security Incident – Important Update
Binance has released its initial report regarding the October 29 security incident.

Approximately $6.34 billion in digital assets were impacted, with $2.85 billion frozen or intercepted. Binance has confirmed that users will not bear the financial losses, and 98% of the affected token assets have already been replenished.

The incident involved a sophisticated attack targeting internal wallet infrastructure. Binance has since rebuilt affected systems, strengthened security controls, replaced compromised devices and engaged independent cybersecurity experts for further review.

The key takeaway: Binance says user funds are protected, the financial impact will be covered by the exchange, and additional security measures are being implemented.
The investigation is ongoing, and we will continue monitoring official updates.

Stay informed, stay cautious, and always follow official Binance announcements. 🛡️

#BinanceIncidentReport
Binance Blog
·
--
29 October 2026 Binance Security Incident: Initial Findings and Response Update
On 29 October 2026, Binance experienced a serious and highly sophisticated security incident. This should not have happened, and we apologise for the concern, disruption and uncertainty it caused our users, partners and the wider industry.Our first responsibility is to protect users. Binance will absorb the financial impact of the stolen funds, not our users. We have already set aside more than 100% of the funds required to cover the loss. As of 31 October 2026, 98% of the impacted token assets have been replenished and are verifiable on our Proof of Reserves page. We are in the process of purchasing the outstanding, more illiquid assets.Approximately USD 6.34 billion in digital assets were impacted by the incident. As of this update, approximately USD 2.85 billion in digital assets have been frozen or intercepted, subject to reconciliation and market price volatility.We have taken immediate action to contain the incident and strengthen the systems involved. The entry points identified as having been used in the attack have been closed. Systems touched in the attack path have been rebuilt or replaced. We have also implemented tighter device controls, enhanced wallet-service risk controls and expanded AI-based behavioural anomaly detection.This is our initial report. It covers what we know today and what we have already improved. The investigation remains ongoing and our findings will be subject to further independent review. Some technical details will remain confidential to prevent malicious actors from using them to plan attacks. We are engaging independent security firms for further review. The latest information released by the Federal Bureau of Investigation indicates that the Democratic People’s Republic of Korea is responsible for this incident.We are sharing this initial report because security improves when the industry learns together.What happened on 29 OctoberThe attack unfolded quickly across several networks.The attacker exploited unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.Between 20:05 UTC and 20:09 UTC, five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address.Binance hot wallets on Solana and Optimism sent approximately 970,500 SOL and 44.2 million OP to attacker-controlled addresses.Binance then received an internal alert regarding large-volume transfers and immediately began investigating.Binance hot wallet sent 18,270 BTC to an attacker-controlled address. The attacker then used the signing service to exploit Ethereum’s EIP-7702 authorization mechanism. EIP-7702 allows an account to delegate certain execution rights to a smart contract without exposing the private key. In this case, the attacker used that mechanism to give an attacker-controlled smart contract partial execution rights over a Binance hot wallet. Binance immediately initiated multiple containment measures, including suspending withdrawals to restrict further outflows, coordinating with partners to freeze affected tokens, and taking steps to revoke unauthorized permissions. These efforts froze a total of $2.85 billion in assets.However, suspending withdrawals alone could not stop all unauthorized asset movements. The malicious EIP-7702 authorizations existed on-chain and operated independently of Binance’s normal withdrawal infrastructure.The attackers submitted 50 signing transactions to manipulate the account nonce and establish malicious delegation authorizations. Once established, these authorizations enabled the attackers to continue moving assets independently of Binance's normal withdrawal infrastructure. Binance needed additional transactions to revoke these on-chain authorizations.The containment process involved additional technical complexities. Because the hot wallet used Multi-Party Computation (MPC), there was no single private key that could be used to immediately revoke the malicious EIP-7702 authorizations. The team therefore developed and executed a specialized procedure to revoke these authorizations, which required additional time. Furthermore, suspending withdrawals and shutting down hot wallet services did not automatically invalidate existing on-chain authorizations.These challenges extended the time required to fully contain the unauthorized asset movements. We are reviewing the incident response process, signing policy coverage, hot wallet controls and identifying opportunities to further strengthen our ability to respond rapidly to threats in the future.The final unauthorized transfer of 2,961.9 ETH finalised on-chain at 23:56 UTC. The transaction had previously been broadcast and remained pending before subsequently finalising. No further unauthorised transfers were observed after.At 00:10 UTC on 30 October 2026, Binance executed a new authorization from the Binance14 hot wallet to the zero address, clearing the EIP-7702 delegation code.Attack Preparation Our current investigation indicates that this was a sophisticated, multi-stage campaign. It was not a single isolated breach or a simple phishing incident. The attackers combined a range of techniques, including social engineering by fake recruitment interviews, malicious software downloads, compromised internal AI tooling, endpoint compromise, and an advanced transaction-authorisation method.June 2026 — Supply chain attack. Engineer A from Wallet DevOps downloaded a tampered Homebrew installation in order to install a popular AI coding tool after searching for it on a search engine. Our security team detected the anomaly, replaced the device, and rotated all related credentials as a proactive security action. However, Engineer A’s role and his related colleagues on our wallet infrastructure team was exposed to the hacker. Throughout 2026, Binance's security team detected and prevented 57 suspected North Korea-linked cyber threat cases. These attempts reflect the persistent threat posed by state-sponsored actors targeting the cryptocurrency industry. The techniques include fraudulent job interviews, malicious software disguised as popular developer tools, compromised software packages and browser extensions, fake video conferencing applications, and social engineering campaigns designed to steal credentials or deploy remote access malware.September 2026 — social engineering. Software Engineer B was contacted through a legitimate job-hunting platform by an individual posing as a Project Director. Software Engineer B had a profile on the platform that referenced his experience at Binance. The purported Project Director arranged a first-round interview with a HR representative, followed by a second-round interview with an individual claiming to be the CEO of a fictitious company.In the first round, the purported HR representative conducted a live video interview with Software Engineer B. The interviewer shared a social media account with him, including personal photos and videos posted on the platform, in order to build trust. This was more advanced and deceptive than previously seen social engineering approaches. The second interview was conducted in a popular social chat app, near the end of the interview, Engineer B was instructed to download an “assignment” containing a malicious code repository onto his work computer. The repository contained malicious code that executed during the setup process, initiating a series of unauthorized activities.The malware employed sophisticated obfuscation and evasion techniques, including replacing a legitimate development tool component with a malicious version to execute commands and establish communication with an attacker-controlled external server. The 0-day malware was not detected by the endpoint security protection tools at the time. The attacker also took steps to conceal the malicious activity and remove traces of the compromise, making detection and subsequent investigation more challenging.The script executed the below steps by applying obfuscation techniques to evade security detection.CREATE  /opt/homebrew/Cellar/pyenv/2.8.0/libexec/pyenv_  MODIFY  pyenv_ → 3,414 B  DELETE  .../libexec/pyenv  (3,344 B)      ← remove the valid pyenvRENAME  pyenv_ → pyenv  (3,414 B)  ← replace it with a malicious version DELETE  /opt/homebrew/bin/pyenv  (3,414 B)ln  (create a new symlink)  +  spawn zsh20 October, 2026 — use of an internal AI tool as a springboard. The attacker leveraged the compromised computer of engineer B and used an internal AI tool to gain control over the Wallet DevOps Engineer A and another Wallet Software Engineer C. The attacker soon discovered Wallet DevOps Engineer A had a container deployment permission token on his computer.29 October, 2026 — reach into wallet signing operations. On 29 October between 17:15 and 19:56, the attacker logged onto Software Engineer C’s computer, used the credentials stolen from Wallet DevOps Engineer A, deployed a container, and triggered a malicious script to launch the attack.What we have doneAs of Nov 3, 2026, we have taken the following actions:Rebuilt the affected wallet system in a new environment.Rebuilt the affected internal AI tool and access controls.Replaced affected devices.Decommissioned credentials and tokens related to affected engineers.Completed enhanced security scans across all employee devices.Enhanced AI-based behavioural anomaly detection.Strengthened wallet-service risk controls.Worked with law enforcement, blockchain intelligence firms and industry partners to trace and freeze affected assets.We will continue to strengthen our measures as the investigation progresses. There are a number of security measures we have implemented and are implementing that will remain private to prevent malicious actors from compromising our security.Further actionsWe are taking the following steps immediately.1. Independent cybersecurity reviewWe are engaging independent third-party cybersecurity experts to conduct a comprehensive review of the incident, validate our findings and recommend additional measures. The scope and findings of that review will inform our continuing remediation work.2. Expanded investment in AI security and preventionWe are increasing investment in AI-enabled detection, endpoint protection, developer-environment security and behavioural anomaly monitoring.3. Security research fund and industry initiativesWe are working on establishing a security research fund and targeted initiatives with leading AI companies, industry participants and security firms focused on AI security in blockchain environments.We will continue to proactively share information as and when we have it.
·
--
Рост
#BinanceIncidentReport ⚡Binance Hack Recovery Update ⚠️📈 Co-CEO Richard Teng confirms 98% of $6.34B impacted tokens replenished after sophisticated months-long attack; user funds protected via SAFU; remaining 2% being completed with OTC partners; withdrawals broadly resumed. $ZEC $IDOL $Q
#BinanceIncidentReport
⚡Binance Hack Recovery Update ⚠️📈
Co-CEO Richard Teng confirms 98% of $6.34B impacted tokens replenished after sophisticated months-long attack; user funds protected via SAFU; remaining 2% being completed with OTC partners; withdrawals broadly resumed.
$ZEC $IDOL $Q
#BinanceIncidentReport 🚨 JUST IN: Binance Incident Report Is Out — Here's The Full Truth! Binance has released its initial findings on the 29 Oct hack and the numbers are insane: 💥 $6.34B was affected — but 98% already replenished as of Oct 31! ❄️ $2.85B frozen with help from Tether & Circle — hackers trapped 🛡️ SAFU fund covering ALL losses — Zero impact on users 🔐 No private key leak — User funds remain 100% safe Binance confirmed it was a multi-stage sophisticated attack via compromised DevOps infrastructure, and said "this should not have happened" — now systems are hardened and FBI investigation is ongoing. With 98% funds restored, is Binance proving why it's still the most trusted exchange? Drop your thoughts below 👇 #Binance #BinanceHack #SAFU #BTC @Square-Creator-314483822eb83 @heyi $BNX $BTC $ETH {future}(ETHUSDT)
#BinanceIncidentReport
🚨 JUST IN: Binance Incident Report Is Out — Here's The Full Truth!

Binance has released its initial findings on the 29 Oct hack and the numbers are insane:

💥 $6.34B was affected — but 98% already replenished as of Oct 31!
❄️ $2.85B frozen with help from Tether & Circle — hackers trapped
🛡️ SAFU fund covering ALL losses — Zero impact on users
🔐 No private key leak — User funds remain 100% safe

Binance confirmed it was a multi-stage sophisticated attack via compromised DevOps infrastructure, and said "this should not have happened" — now systems are hardened and FBI investigation is ongoing.

With 98% funds restored, is Binance proving why it's still the most trusted exchange?

Drop your thoughts below 👇

#Binance #BinanceHack #SAFU #BTC
@Golden soumi @Yi He

$BNX $BTC $ETH
·
--
$BTC is currently trading near $76,700–$77,000, experiencing short-term sell pressure. The recent market movement reflects the following analysis: Market Catalyst: A massive security incident involving an estimated $6.3 billion affected asset pool at Binance (including over 18,000 BTC) shook investor confidence, triggering long-position liquidations across derivatives markets. Macro Environment: Stronger dollar-liquidity metrics and a cautious stance from global central banks have constrained liquidity. Analysts emphasize that sustained crypto upside will likely require balance-sheet expansion by the Federal Reserve or major banks. Key Support & Resistance Levels: Critical Support ($75,000–$76,000): This zone matches the average cost basis for recent short-term holders (STH MVRV ~1.02). Breaking below $75,000 risks a deeper correction toward earlier key cycle levels. Resistance ($80,000): Reclaiming and holding $80,000 is key to restoring broader bullish momentum and technical structure. #BinanceIncidentReport #BinanceReopensWithdrawalsForMoreAssets #BinanceHourlyDepositsExceedWithdrawals {spot}(BTCUSDT)
$BTC is currently trading near $76,700–$77,000, experiencing short-term sell pressure. The recent market movement reflects the following analysis:
Market Catalyst: A massive security incident involving an estimated $6.3 billion affected asset pool at Binance (including over 18,000 BTC) shook investor confidence, triggering long-position liquidations across derivatives markets.
Macro Environment: Stronger dollar-liquidity metrics and a cautious stance from global central banks have constrained liquidity. Analysts emphasize that sustained crypto upside will likely require balance-sheet expansion by the Federal Reserve or major banks.
Key Support & Resistance Levels:
Critical Support ($75,000–$76,000): This zone matches the average cost basis for recent short-term holders (STH MVRV ~1.02). Breaking below $75,000 risks a deeper correction toward earlier key cycle levels.
Resistance ($80,000): Reclaiming and holding $80,000 is key to restoring broader bullish momentum and technical structure. #BinanceIncidentReport #BinanceReopensWithdrawalsForMoreAssets #BinanceHourlyDepositsExceedWithdrawals
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона