
#hacker
hacker
Просмотров: 781,061
374 обсуждают
Популярные
Новые
·
--
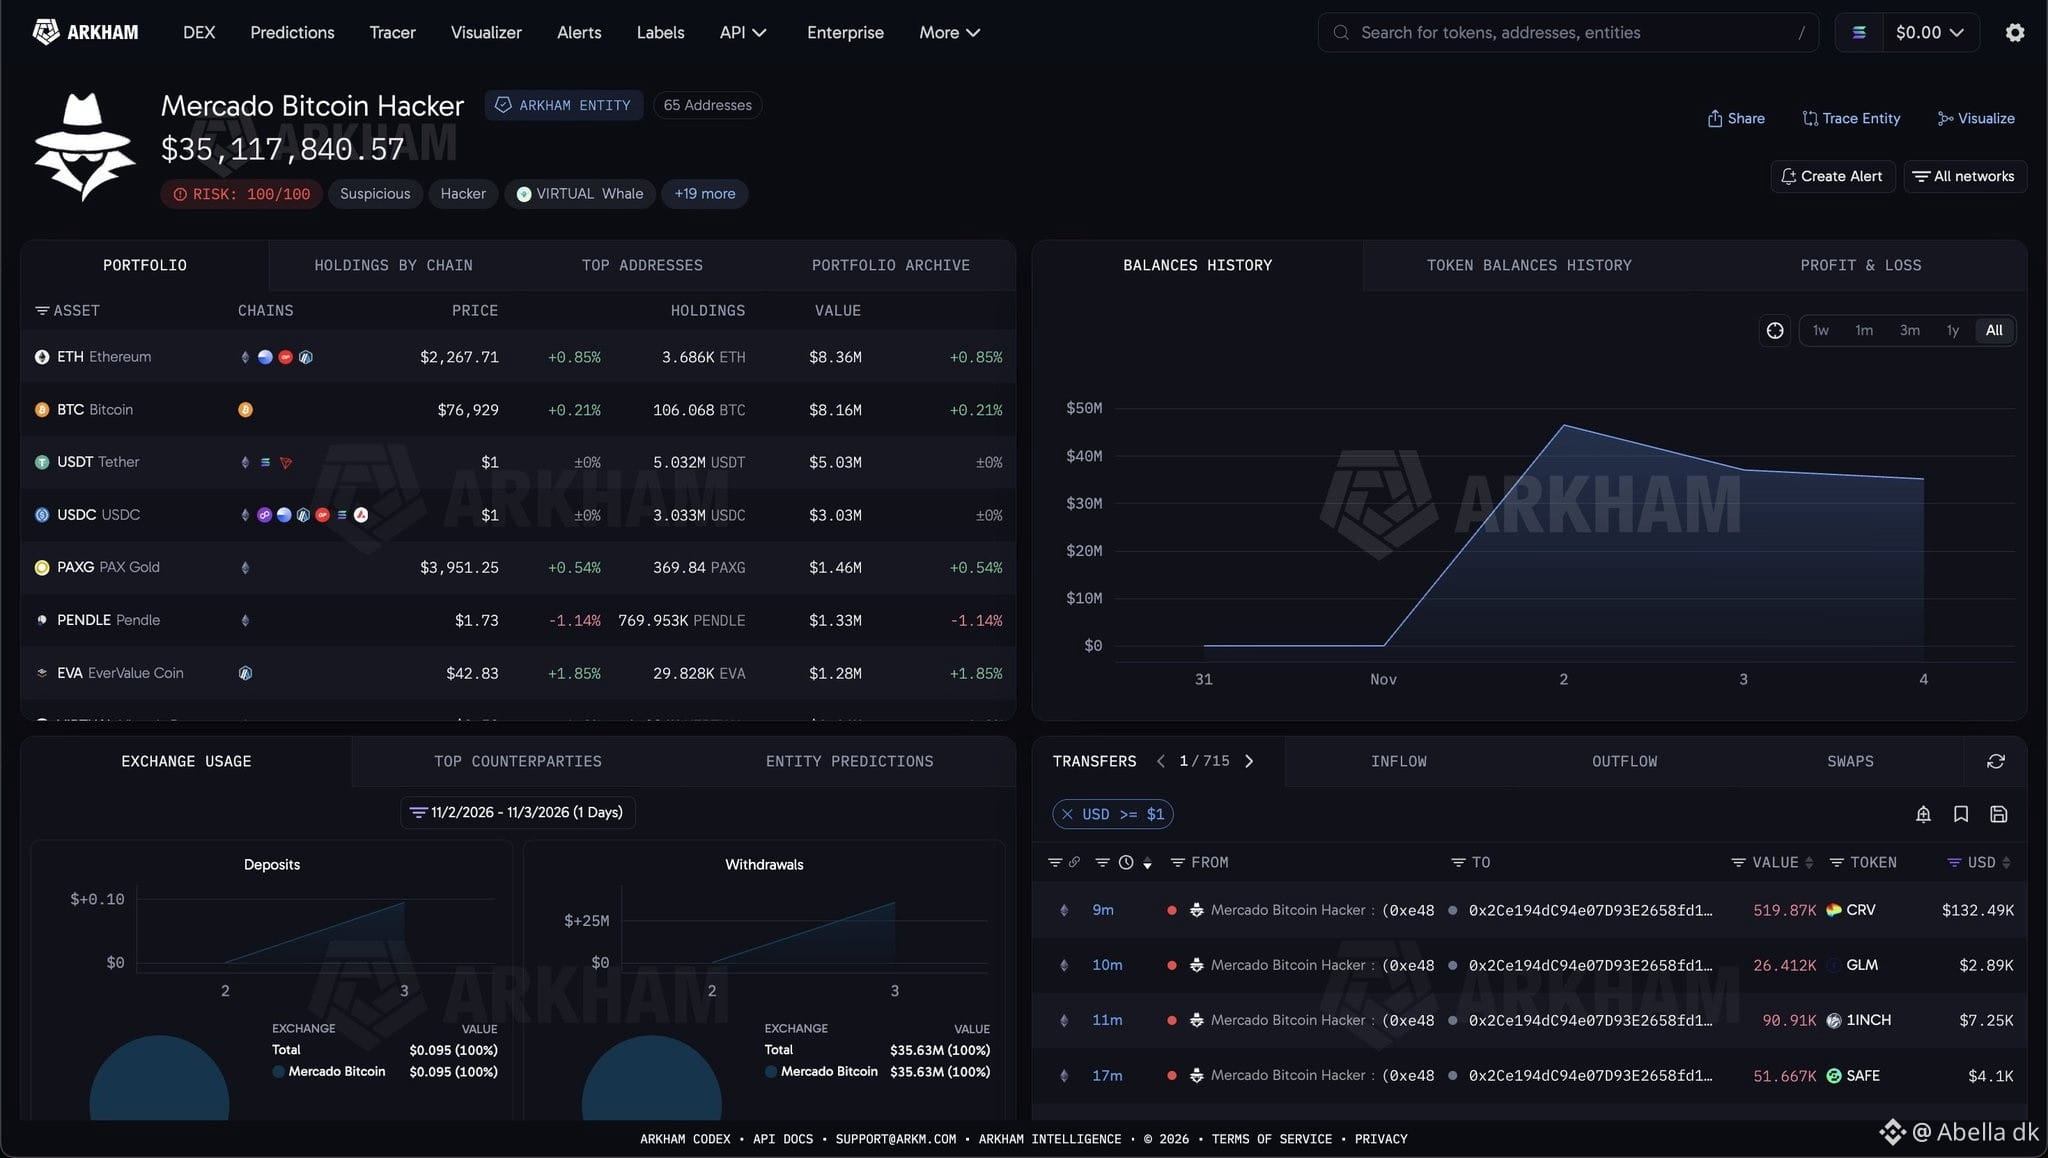
🚨 MERCADO BITCOIN HACKER IS DUMPING STOLEN CRYPTO!
🔥 The Mercado Bitcoin hacker appears to be moving into the next phase of the attack: SELLING OFF THE STOLEN FUNDS!
On-chain tracking shows the attacker has already transferred approximately $11.45 MILLION worth of altcoins to multiple addresses, potentially preparing them for liquidation.
$CLANKER
But here's the interesting part: 👀
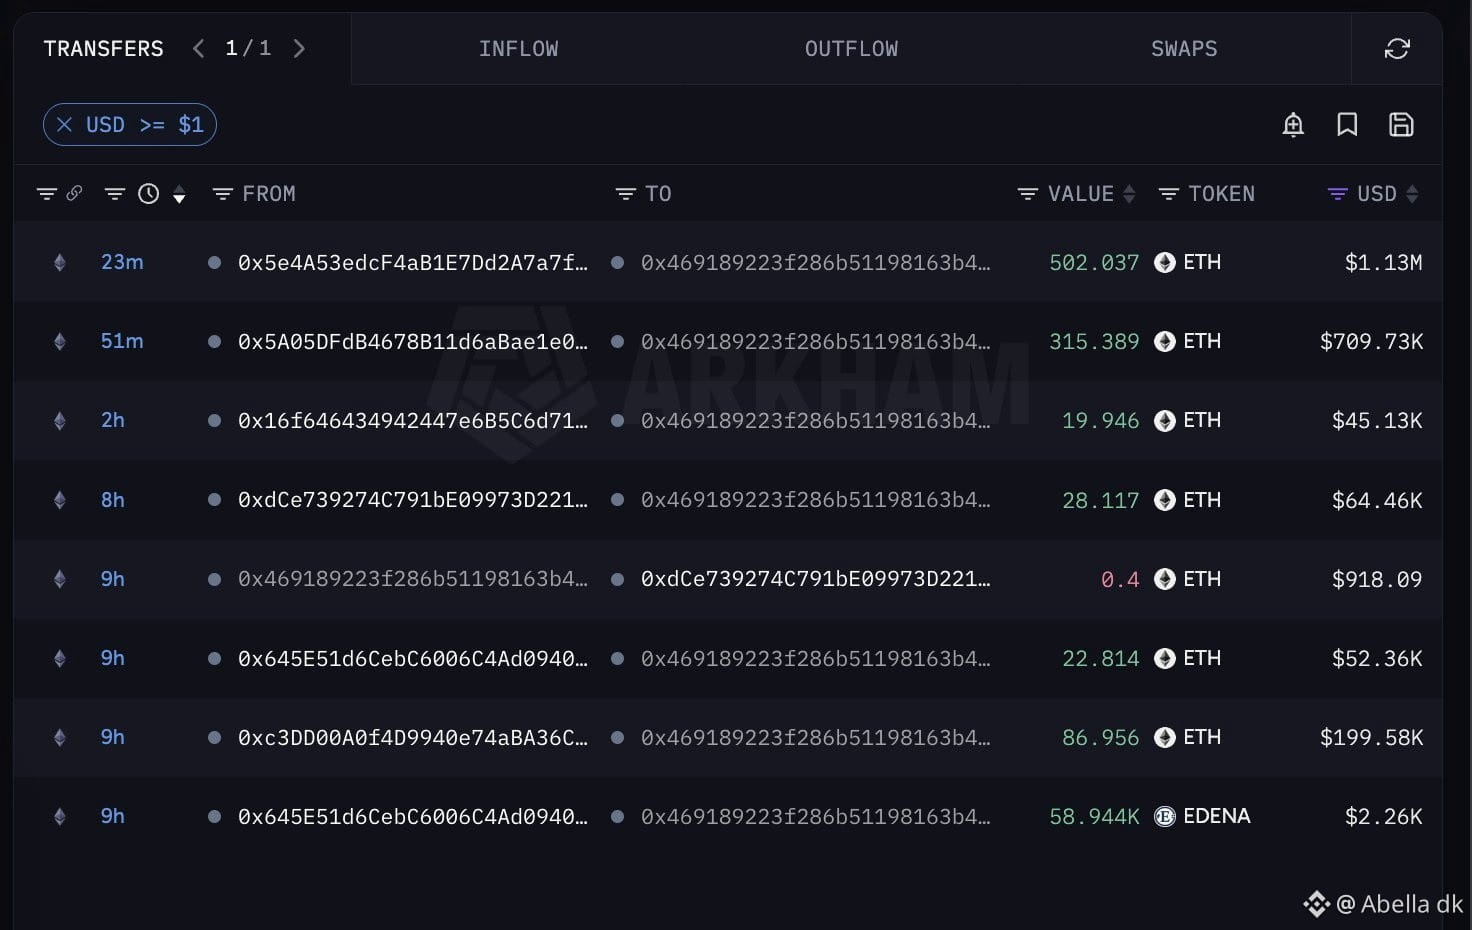
The hacker appears to be consolidating ETH at this wallet:
📍 "0x469189223f286b51198163b4Eb5a1e532669523d"
$BMT
This raises fresh concerns about further fund movements and potential selling pressure across affected tokens.
🚨 The investigation is far from over. Every transaction could reveal another clue.
$AIOT
Is this the beginning of a massive crypto sell-off, or is the hacker preparing another laundering operation?
#Crypto #MercadoBitcoin #Hacker #Ethereum #BlockchainSecurity
🚨 MERCADO BITCOIN HACKER IS DUMPING STOLEN CRYPTO!
🔥 The Mercado Bitcoin hacker appears to be moving into the next phase of the attack: SELLING OFF THE STOLEN FUNDS!
On-chain tracking shows the attacker has already transferred approximately $11.45 MILLION worth of altcoins to multiple addresses, potentially preparing them for liquidation.
$CLANKER
But here's the interesting part: 👀
The hacker appears to be consolidating ETH at this wallet:
📍 "0x469189223f286b51198163b4Eb5a1e532669523d"
$BMT
This raises fresh concerns about further fund movements and potential selling pressure across affected tokens.
🚨 The investigation is far from over. Every transaction could reveal another clue.
$AIOT
Is this the beginning of a massive crypto sell-off, or is the hacker preparing another laundering operation?
#Crypto #MercadoBitcoin #Hacker #Ethereum #BlockchainSecurity
🔥 The Mercado Bitcoin hacker appears to be moving into the next phase of the attack: SELLING OFF THE STOLEN FUNDS!
On-chain tracking shows the attacker has already transferred approximately $11.45 MILLION worth of altcoins to multiple addresses, potentially preparing them for liquidation.
$CLANKER
But here's the interesting part: 👀
The hacker appears to be consolidating ETH at this wallet:
📍 "0x469189223f286b51198163b4Eb5a1e532669523d"
$BMT
This raises fresh concerns about further fund movements and potential selling pressure across affected tokens.
🚨 The investigation is far from over. Every transaction could reveal another clue.
$AIOT
Is this the beginning of a massive crypto sell-off, or is the hacker preparing another laundering operation?
#Crypto #MercadoBitcoin #Hacker #Ethereum #BlockchainSecurity
WhaleTrackerPro:
On the way
11
6
2k
·
--
$$😂 Apparently, $6.3 billion was stolen from Binance by hackers! 💸
After seeing my brother's Binance dollar balance, I think the hackers felt so bad that they'd actually want to add some dollars to my Binance account instead! 😭🤣
#Binance #Hacker #FunnyPost 💸
$$😂 Apparently, $6.3 billion was stolen from Binance by hackers! 💸
After seeing my brother's Binance dollar balance, I think the hackers felt so bad that they'd actually want to add some dollars to my Binance account instead! 😭🤣
#Binance #Hacker #FunnyPost 💸
After seeing my brother's Binance dollar balance, I think the hackers felt so bad that they'd actually want to add some dollars to my Binance account instead! 😭🤣
#Binance #Hacker #FunnyPost 💸
cryptogirl007:
Joking about hackers pitying an empty balance keeps morale intact, but giving yourself room for mental recovery comes before any fresh deposit.
1
4
630
·
--
yyy
·
--
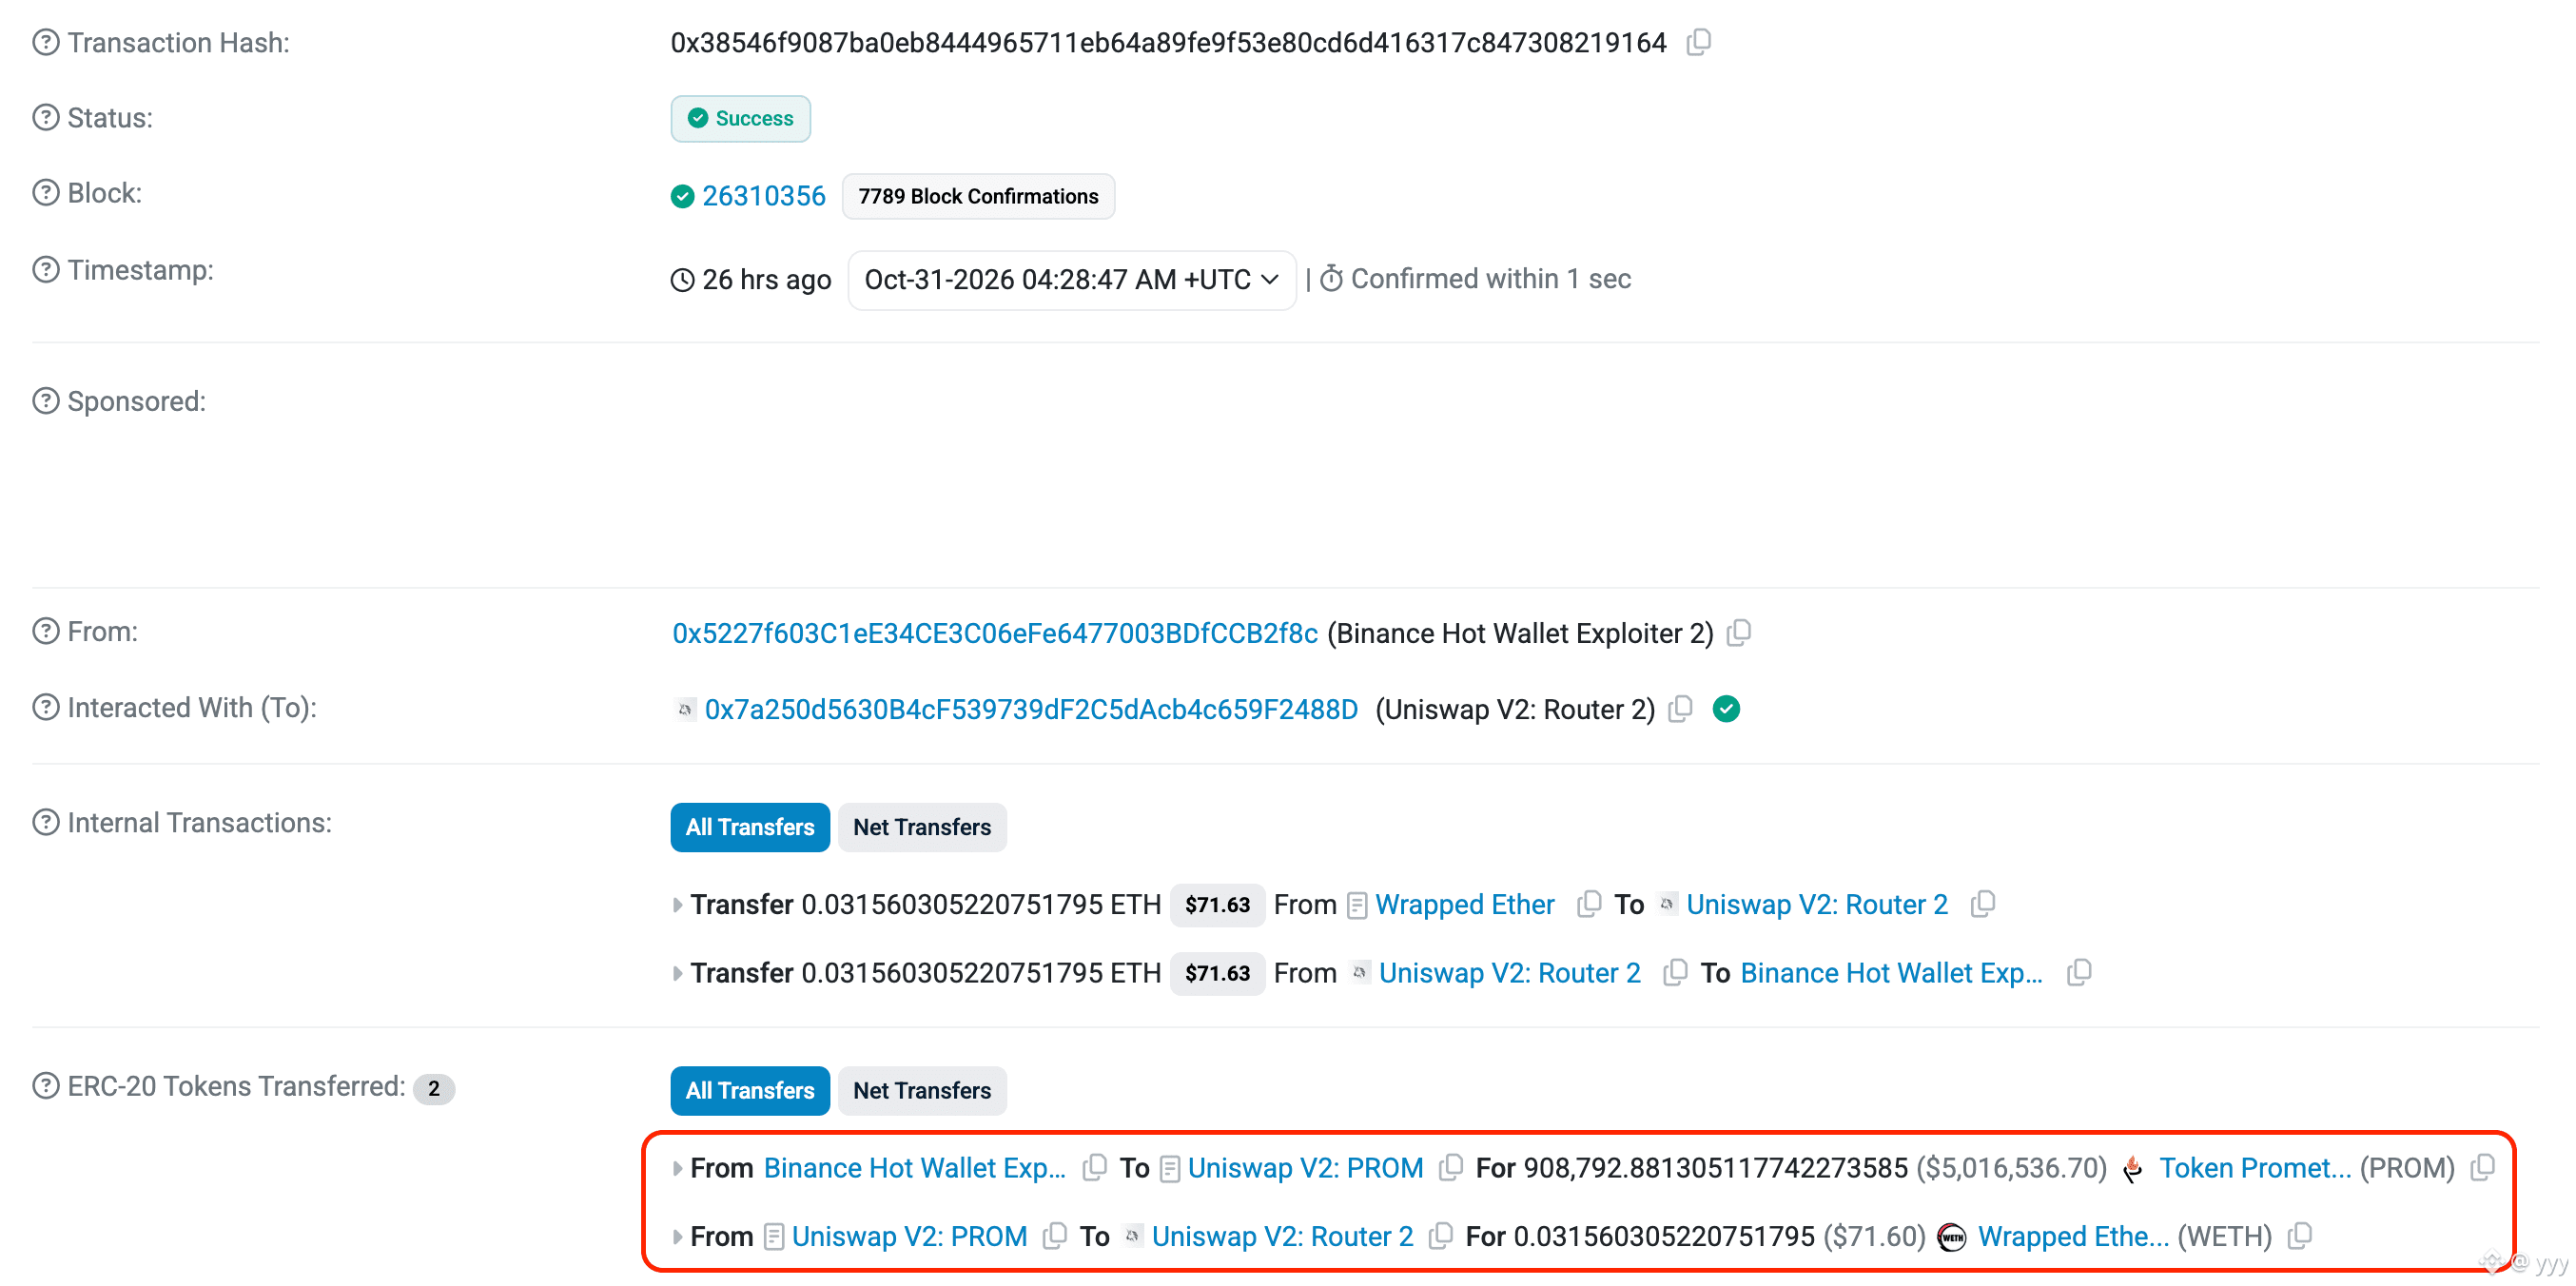
攻击币安的黑客被扒出犯了低级错误,把价值约330万美元的山寨币转到了 $NEWT 代币的合约地址。
相当于直接把币打到黑洞了,永久锁定、无法取回。
在此之前的另一个失误是没有第一时间把Arbitrum 上盗出来的赃款跨链转走,停留了几小时被Arbitrum SC 紧急冻结了。
#Binance #Arbitrum $ARB
相当于直接把币打到黑洞了,永久锁定、无法取回。
在此之前的另一个失误是没有第一时间把Arbitrum 上盗出来的赃款跨链转走,停留了几小时被Arbitrum SC 紧急冻结了。
#Binance #Arbitrum $ARB
1k
·
--
Рост
The Paradox of Blockchain Laundering 🧵👇
Money laundering following the Binance hack has reached an unprecedented level, according to Chainalysis.
Hackers are using automated scripts and micro-transactions to muddy the trail and make it harder to track the stolen funds.
But there’s one detail often overlooked: it’s all happening on the blockchain. 👀
The funds may move, but the trail is permanent:
Public & Immutable: You can't erase a transaction on a public ledger. Every bot-driven transfer leaves a digital footprint.
Complex, Not Invisible: The hackers aren't trying to delete the trail—they are just trying to make it too complex for human analysts to follow in real time.
Deterministic Tracking: Through 3D network visualization and automated analytics, security teams can trace funds across thousands of wallets and freeze assets before they reach exchanges.
The trail stays forever—and the net is closing in.
$BTC $ETH $USDC
#Hacker #Bianance #BinanceToResumePhaseOneOfWithdrawals #FBIConfirmsNorthKoreaIsResponsibleForBinanceCryptoHack #CZDismissesClaimsBinanceHackWasPredicted
{spot}(USDCUSDT)
{spot}(ETHUSDT)
{spot}(BTCUSDT)
The Paradox of Blockchain Laundering 🧵👇
Money laundering following the Binance hack has reached an unprecedented level, according to Chainalysis.
Hackers are using automated scripts and micro-transactions to muddy the trail and make it harder to track the stolen funds.
But there’s one detail often overlooked: it’s all happening on the blockchain. 👀
The funds may move, but the trail is permanent:
Public & Immutable: You can't erase a transaction on a public ledger. Every bot-driven transfer leaves a digital footprint.
Complex, Not Invisible: The hackers aren't trying to delete the trail—they are just trying to make it too complex for human analysts to follow in real time.
Deterministic Tracking: Through 3D network visualization and automated analytics, security teams can trace funds across thousands of wallets and freeze assets before they reach exchanges.
The trail stays forever—and the net is closing in.
$BTC $ETH $USDC
#Hacker #Bianance #BinanceToResumePhaseOneOfWithdrawals #FBIConfirmsNorthKoreaIsResponsibleForBinanceCryptoHack #CZDismissesClaimsBinanceHackWasPredicted
Money laundering following the Binance hack has reached an unprecedented level, according to Chainalysis.
Hackers are using automated scripts and micro-transactions to muddy the trail and make it harder to track the stolen funds.
But there’s one detail often overlooked: it’s all happening on the blockchain. 👀
The funds may move, but the trail is permanent:
Public & Immutable: You can't erase a transaction on a public ledger. Every bot-driven transfer leaves a digital footprint.
Complex, Not Invisible: The hackers aren't trying to delete the trail—they are just trying to make it too complex for human analysts to follow in real time.
Deterministic Tracking: Through 3D network visualization and automated analytics, security teams can trace funds across thousands of wallets and freeze assets before they reach exchanges.
The trail stays forever—and the net is closing in.
$BTC $ETH $USDC
#Hacker #Bianance #BinanceToResumePhaseOneOfWithdrawals #FBIConfirmsNorthKoreaIsResponsibleForBinanceCryptoHack #CZDismissesClaimsBinanceHackWasPredicted
3
84
#HACKER 🇰🇵 **TẠI SAO HACKER TRIỀU TIÊN LẠI GIỎI ĐẾN ĐÁNG SỢ? 😳**
Một đất nước bị cô lập, internet còn hạn chế, vậy mà lại sở hữu những nhóm hacker khiến cả thế giới phải dè chừng.
Lý do là Triều Tiên được cho là tuyển chọn nhân tài công nghệ từ rất sớm, đào tạo bài bản và xem tấn công mạng như một công cụ chiến lược để kiếm ngoại tệ.
💥 **Mới đây, Binance bị hack khoảng 6,3 tỷ USD**, và các nhà điều tra nghi ngờ nhóm hacker có liên hệ với Triều Tiên đứng sau, dù chưa có kết luận chính thức.
Trước đó, vụ Bybit mất khoảng 1,5 tỷ USD năm 2025 cũng được FBI quy trách nhiệm cho hacker Triều Tiên.
Nghĩ cũng lạ, một quốc gia còn nhiều khó khăn về kinh tế lại có thể khiến những ông lớn crypto phải đau đầu.
**Theo anh em, hacker Triều Tiên quá giỏi hay bảo mật các sàn crypto quá kém? 🤔**
#Binance #Crypto #Hacker #GiaCatTrader $BTC
#HACKER 🇰🇵 **TẠI SAO HACKER TRIỀU TIÊN LẠI GIỎI ĐẾN ĐÁNG SỢ? 😳**
Một đất nước bị cô lập, internet còn hạn chế, vậy mà lại sở hữu những nhóm hacker khiến cả thế giới phải dè chừng.
Lý do là Triều Tiên được cho là tuyển chọn nhân tài công nghệ từ rất sớm, đào tạo bài bản và xem tấn công mạng như một công cụ chiến lược để kiếm ngoại tệ.
💥 **Mới đây, Binance bị hack khoảng 6,3 tỷ USD**, và các nhà điều tra nghi ngờ nhóm hacker có liên hệ với Triều Tiên đứng sau, dù chưa có kết luận chính thức.
Trước đó, vụ Bybit mất khoảng 1,5 tỷ USD năm 2025 cũng được FBI quy trách nhiệm cho hacker Triều Tiên.
Nghĩ cũng lạ, một quốc gia còn nhiều khó khăn về kinh tế lại có thể khiến những ông lớn crypto phải đau đầu.
**Theo anh em, hacker Triều Tiên quá giỏi hay bảo mật các sàn crypto quá kém? 🤔**
#Binance #Crypto #Hacker #GiaCatTrader $BTC
Một đất nước bị cô lập, internet còn hạn chế, vậy mà lại sở hữu những nhóm hacker khiến cả thế giới phải dè chừng.
Lý do là Triều Tiên được cho là tuyển chọn nhân tài công nghệ từ rất sớm, đào tạo bài bản và xem tấn công mạng như một công cụ chiến lược để kiếm ngoại tệ.
💥 **Mới đây, Binance bị hack khoảng 6,3 tỷ USD**, và các nhà điều tra nghi ngờ nhóm hacker có liên hệ với Triều Tiên đứng sau, dù chưa có kết luận chính thức.
Trước đó, vụ Bybit mất khoảng 1,5 tỷ USD năm 2025 cũng được FBI quy trách nhiệm cho hacker Triều Tiên.
Nghĩ cũng lạ, một quốc gia còn nhiều khó khăn về kinh tế lại có thể khiến những ông lớn crypto phải đau đầu.
**Theo anh em, hacker Triều Tiên quá giỏi hay bảo mật các sàn crypto quá kém? 🤔**
#Binance #Crypto #Hacker #GiaCatTrader $BTC
2
925

Статья
Подробности самого крупного взлома в истории криптовалют!🤯 История со взломом Binance оказалась гораздо серьёзнее, чем предполагалось вчера. Биржа официально признала инцидент и раскрыла первые результаты расследования!
💵 Главные цифры:
🔴 $6,3 млрд предварительный масштаб взлома.
🟢 Около $3 млрд удалось заморозить совместно с партнёрами.
🔴 Примерно $3,3 млрд пока под контролем хакера.
🧊 Кто и сколько заблокировал:
• Tether более $1,57 млрд USDT.
• Circle около $823 млн USDC.
• Ripple примерно $200 млн.
• World Liberty Financial около $27 млн USD1.
🥷 Как произошёл взлом?
По предварительной версии Binance, хакеры получили доступ к ноутбуку DevOps-инженера, проникли во внутреннюю инфраструктуру и смогли инициировать несанкционированные выводы средств. При этом признаков утечки приватных ключей кошельков не обнаружено.
🔍 По данным Bitquery, атака затронула 17 горячих кошельков Binance в 9 блокчейнах. Основные переводы происходили вечером 29 октября.
⚠️ Что происходит с биржей?
Binance временно приостановила вывод криптовалют для проверки безопасности. Пополнения уже работают, восстановить вывод планируют в течение 48 часов. Binance обещает полностью покрыть потери за счёт фонда SAFU и собственных средств компании.
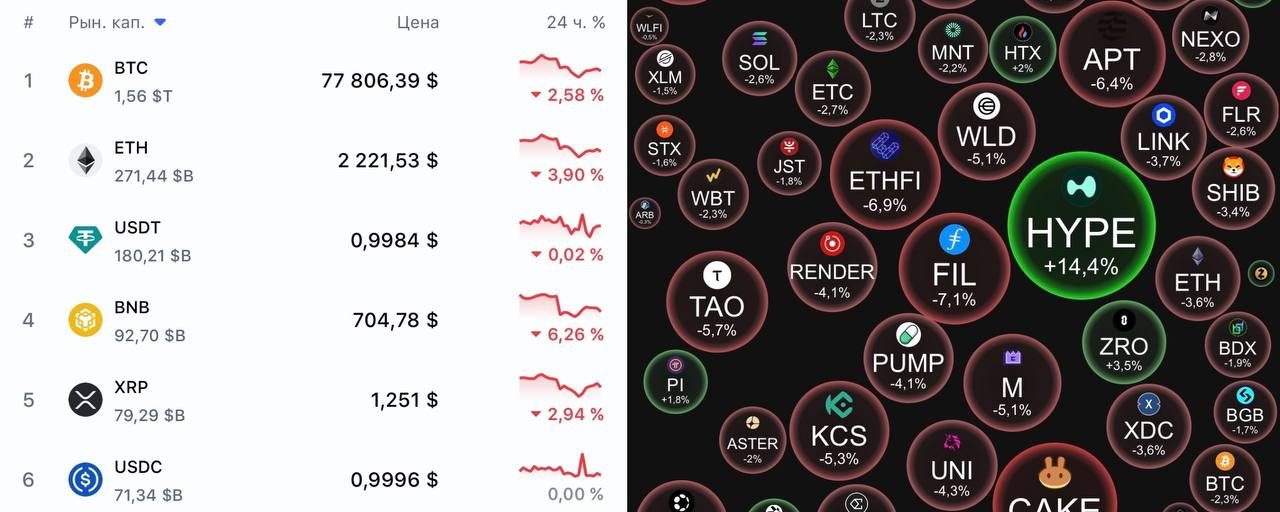
📉 Реакция рынка:
🔻 Bitcoin опускался примерно до $76 400.
🔻 Ethereum до $2 180.
🔻 BNB терял более 8%.
🇰🇵 Аналитики TRM Labs связывают атаку с северокорейской группировкой TraderTraitor, однако официально виновники пока не установлены.
☝️ Для понимания масштабов: предыдущий рекорд принадлежал взлому Bybit в феврале 2025 года около $1,5 млрд. Теперь речь идёт о сумме более чем в четыре раза выше!
🫥 По иронии судьбы 28 октября CZ предупредил пользователей об участившихся утечках данных и призвал усилить защиту аккаунтов, не открывать подозрительные ссылки и вложения, даже от знакомых.
👀
Как писал ранее этот год бъет все рекорды по взломам крипто компаний. По предварительным оценкам ущерб уже составляет около $9.2 миллиардов, а впереди еще два месяца. Вот такой он, Rektober 2026!
#rektober #binance #Hacker
Подробности самого крупного взлома в истории криптовалют!
🤯 История со взломом Binance оказалась гораздо серьёзнее, чем предполагалось вчера. Биржа официально признала инцидент и раскрыла первые результаты расследования!
💵 Главные цифры:
🔴 $6,3 млрд предварительный масштаб взлома.
🟢 Около $3 млрд удалось заморозить совместно с партнёрами.
🔴 Примерно $3,3 млрд пока под контролем хакера.
🧊 Кто и сколько заблокировал:
• Tether более $1,57 млрд USDT.
• Circle около $823 млн USDC.
• Ripple примерно $200 млн.
• World Liberty Financial около $27 млн USD1.
🥷 Как произошёл взлом?
По предварительной версии Binance, хакеры получили доступ к ноутбуку DevOps-инженера, проникли во внутреннюю инфраструктуру и смогли инициировать несанкционированные выводы средств. При этом признаков утечки приватных ключей кошельков не обнаружено.
🔍 По данным Bitquery, атака затронула 17 горячих кошельков Binance в 9 блокчейнах. Основные переводы происходили вечером 29 октября.
⚠️ Что происходит с биржей?
Binance временно приостановила вывод криптовалют для проверки безопасности. Пополнения уже работают, восстановить вывод планируют в течение 48 часов. Binance обещает полностью покрыть потери за счёт фонда SAFU и собственных средств компании.
📉 Реакция рынка:
🔻 Bitcoin опускался примерно до $76 400.
🔻 Ethereum до $2 180.
🔻 BNB терял более 8%.
🇰🇵 Аналитики TRM Labs связывают атаку с северокорейской группировкой TraderTraitor, однако официально виновники пока не установлены.
☝️ Для понимания масштабов: предыдущий рекорд принадлежал взлому Bybit в феврале 2025 года около $1,5 млрд. Теперь речь идёт о сумме более чем в четыре раза выше!
🫥 По иронии судьбы 28 октября CZ предупредил пользователей об участившихся утечках данных и призвал усилить защиту аккаунтов, не открывать подозрительные ссылки и вложения, даже от знакомых.
👀
Как писал ранее этот год бъет все рекорды по взломам крипто компаний. По предварительным оценкам ущерб уже составляет около $9.2 миллиардов, а впереди еще два месяца. Вот такой он, Rektober 2026!
#rektober #binance #Hacker
💵 Главные цифры:
🔴 $6,3 млрд предварительный масштаб взлома.
🟢 Около $3 млрд удалось заморозить совместно с партнёрами.
🔴 Примерно $3,3 млрд пока под контролем хакера.
🧊 Кто и сколько заблокировал:
• Tether более $1,57 млрд USDT.
• Circle около $823 млн USDC.
• Ripple примерно $200 млн.
• World Liberty Financial около $27 млн USD1.
🥷 Как произошёл взлом?
По предварительной версии Binance, хакеры получили доступ к ноутбуку DevOps-инженера, проникли во внутреннюю инфраструктуру и смогли инициировать несанкционированные выводы средств. При этом признаков утечки приватных ключей кошельков не обнаружено.
🔍 По данным Bitquery, атака затронула 17 горячих кошельков Binance в 9 блокчейнах. Основные переводы происходили вечером 29 октября.
⚠️ Что происходит с биржей?
Binance временно приостановила вывод криптовалют для проверки безопасности. Пополнения уже работают, восстановить вывод планируют в течение 48 часов. Binance обещает полностью покрыть потери за счёт фонда SAFU и собственных средств компании.
📉 Реакция рынка:
🔻 Bitcoin опускался примерно до $76 400.
🔻 Ethereum до $2 180.
🔻 BNB терял более 8%.
🇰🇵 Аналитики TRM Labs связывают атаку с северокорейской группировкой TraderTraitor, однако официально виновники пока не установлены.
☝️ Для понимания масштабов: предыдущий рекорд принадлежал взлому Bybit в феврале 2025 года около $1,5 млрд. Теперь речь идёт о сумме более чем в четыре раза выше!
🫥 По иронии судьбы 28 октября CZ предупредил пользователей об участившихся утечках данных и призвал усилить защиту аккаунтов, не открывать подозрительные ссылки и вложения, даже от знакомых.
👀
Как писал ранее этот год бъет все рекорды по взломам крипто компаний. По предварительным оценкам ущерб уже составляет около $9.2 миллиардов, а впереди еще два месяца. Вот такой он, Rektober 2026!
#rektober #binance #Hacker
13
18k
☠️ КРИПТОАПОКАЛИПСИС НАЧАЛСЯ?
🥷 Похоже, крипторынок накрыла настоящая волна взломов!
🔴 Сначала хакеры атаковали Polymarket. Предварительный ущерб оценивается в $3,46 млн.
🔴 Следом Binance! С кошельков биржи зафиксировали подозрительные переводы на сумму до $2,77 млрд.
🚨 CZ подтвердил, что ситуация похожа на взлом Binance! Tether и Circle оперативно заморозили $971 млн USDT и $823 млн USDC, почти $1,8 млрд! Он заявил, что средства пользователей в безопасности, а возможные потери, по его ожиданиям, будут полностью компенсированы.
🔴 Ходят слухи, что ByBit тоже взломали на $500 миллионов, но пока подтверждений нет.
👀
И всё это буквально за несколько часов! Что дальше? Очень надеюсь, что на этом криптоапокалипсис закончится. Октябрь в своем репертуаре!
#crypto #Hacker #Polymarket #Binance
☠️ КРИПТОАПОКАЛИПСИС НАЧАЛСЯ?
🥷 Похоже, крипторынок накрыла настоящая волна взломов!
🔴 Сначала хакеры атаковали Polymarket. Предварительный ущерб оценивается в $3,46 млн.
🔴 Следом Binance! С кошельков биржи зафиксировали подозрительные переводы на сумму до $2,77 млрд.
🚨 CZ подтвердил, что ситуация похожа на взлом Binance! Tether и Circle оперативно заморозили $971 млн USDT и $823 млн USDC, почти $1,8 млрд! Он заявил, что средства пользователей в безопасности, а возможные потери, по его ожиданиям, будут полностью компенсированы.
🔴 Ходят слухи, что ByBit тоже взломали на $500 миллионов, но пока подтверждений нет.
👀
И всё это буквально за несколько часов! Что дальше? Очень надеюсь, что на этом криптоапокалипсис закончится. Октябрь в своем репертуаре!
#crypto #Hacker #Polymarket #Binance
🥷 Похоже, крипторынок накрыла настоящая волна взломов!
🔴 Сначала хакеры атаковали Polymarket. Предварительный ущерб оценивается в $3,46 млн.
🔴 Следом Binance! С кошельков биржи зафиксировали подозрительные переводы на сумму до $2,77 млрд.
🚨 CZ подтвердил, что ситуация похожа на взлом Binance! Tether и Circle оперативно заморозили $971 млн USDT и $823 млн USDC, почти $1,8 млрд! Он заявил, что средства пользователей в безопасности, а возможные потери, по его ожиданиям, будут полностью компенсированы.
🔴 Ходят слухи, что ByBit тоже взломали на $500 миллионов, но пока подтверждений нет.
👀
И всё это буквально за несколько часов! Что дальше? Очень надеюсь, что на этом криптоапокалипсис закончится. Октябрь в своем репертуаре!
#crypto #Hacker #Polymarket #Binance
5
5.3k

No Panic! Stolen Crypto Can Be Traced — It’s Only a Matter of Time
Every stolen BTC, ETH, XRP, and other cryptocurrency leaves a digital trail on the blockchain. Transactions are transparent, and investigators can track where stolen funds move.
Hackers may hide, but their transactions remain recorded forever. With blockchain analytics, cooperation between exchanges, and law enforcement, stolen assets can be traced, frozen, and recovered.
Stay calm. No panic! The blockchain never forgets. Recovery may take time, but stolen crypto is never truly invisible.
$BTC $ETH $XRP #Hacker #StolenBitcoin
No Panic! Stolen Crypto Can Be Traced — It’s Only a Matter of Time
Every stolen BTC, ETH, XRP, and other cryptocurrency leaves a digital trail on the blockchain. Transactions are transparent, and investigators can track where stolen funds move.
Hackers may hide, but their transactions remain recorded forever. With blockchain analytics, cooperation between exchanges, and law enforcement, stolen assets can be traced, frozen, and recovered.
Stay calm. No panic! The blockchain never forgets. Recovery may take time, but stolen crypto is never truly invisible.
$BTC $ETH $XRP #Hacker #StolenBitcoin
Every stolen BTC, ETH, XRP, and other cryptocurrency leaves a digital trail on the blockchain. Transactions are transparent, and investigators can track where stolen funds move.
Hackers may hide, but their transactions remain recorded forever. With blockchain analytics, cooperation between exchanges, and law enforcement, stolen assets can be traced, frozen, and recovered.
Stay calm. No panic! The blockchain never forgets. Recovery may take time, but stolen crypto is never truly invisible.
$BTC $ETH $XRP #Hacker #StolenBitcoin
1
161
·
--
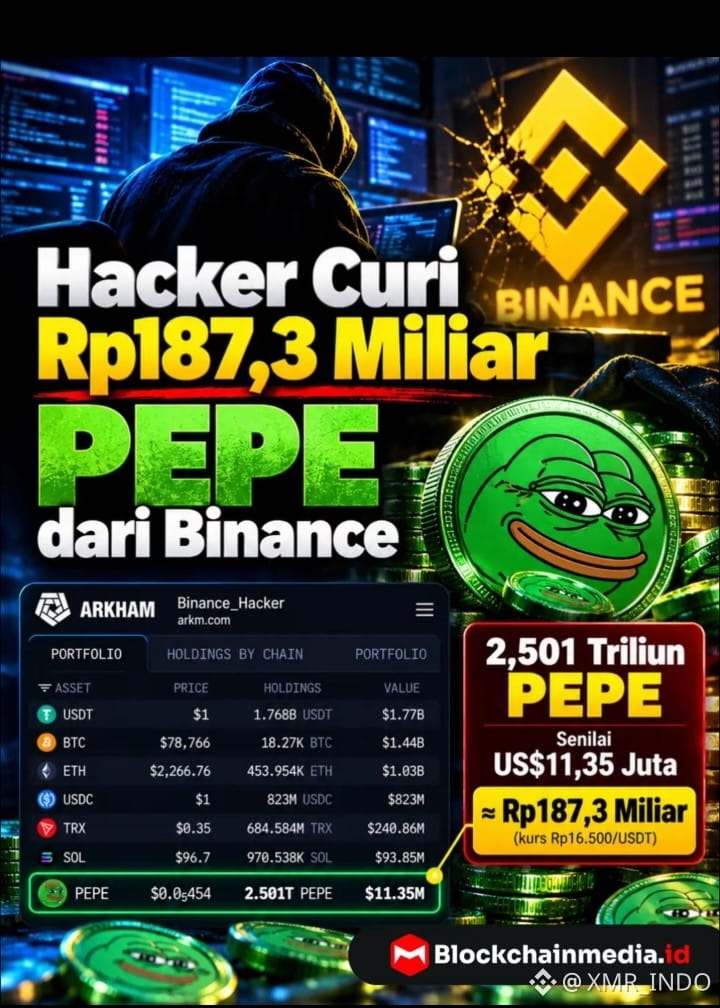
Sebanyak 2,501 triliun token PEPE senilai US$11,35 juta atau sekitar Rp187,3 miliar terdeteksi dalam wallet berlabel "Binance_Hacker" di Arkham Intelligence, Jumat (30/10/2026). $1000PEPE
{future}(1000PEPEUSDT)
merupakan satu dari puluhan aset kripto lainnya yang dikaitkan dengan peretasan Binance senilai lebih dari US$5,8 miliar, berdasarkan laporan Lookonchain. Aset lainnya mencakup BTC, ETH, USDT, USDC, SOL, dan TRX. Pendiri Binance, Changpeng Zhao (CZ), menyatakan dana pengguna aman. Namun, belum dapat dipastikan bahwa seluruh PEPE dalam wallet tersebut merupakan hasil pencurian.
Sumber: Arkham Intelligence, Lookonchain, dan CZ di X. #Binance #PEPE #hacker
Sebanyak 2,501 triliun token PEPE senilai US$11,35 juta atau sekitar Rp187,3 miliar terdeteksi dalam wallet berlabel "Binance_Hacker" di Arkham Intelligence, Jumat (30/10/2026). $1000PEPE
merupakan satu dari puluhan aset kripto lainnya yang dikaitkan dengan peretasan Binance senilai lebih dari US$5,8 miliar, berdasarkan laporan Lookonchain. Aset lainnya mencakup BTC, ETH, USDT, USDC, SOL, dan TRX. Pendiri Binance, Changpeng Zhao (CZ), menyatakan dana pengguna aman. Namun, belum dapat dipastikan bahwa seluruh PEPE dalam wallet tersebut merupakan hasil pencurian.
Sumber: Arkham Intelligence, Lookonchain, dan CZ di X. #Binance #PEPE #hacker
merupakan satu dari puluhan aset kripto lainnya yang dikaitkan dengan peretasan Binance senilai lebih dari US$5,8 miliar, berdasarkan laporan Lookonchain. Aset lainnya mencakup BTC, ETH, USDT, USDC, SOL, dan TRX. Pendiri Binance, Changpeng Zhao (CZ), menyatakan dana pengguna aman. Namun, belum dapat dipastikan bahwa seluruh PEPE dalam wallet tersebut merupakan hasil pencurian.
Sumber: Arkham Intelligence, Lookonchain, dan CZ di X. #Binance #PEPE #hacker
628


·
--
Golpe al corazón de los pronósticos
Un #Hacker vacía casi 1.000 cuentas en #Polymarket y roza los 2.65 millones de dólares
Radiografía de un ciberataque masivo
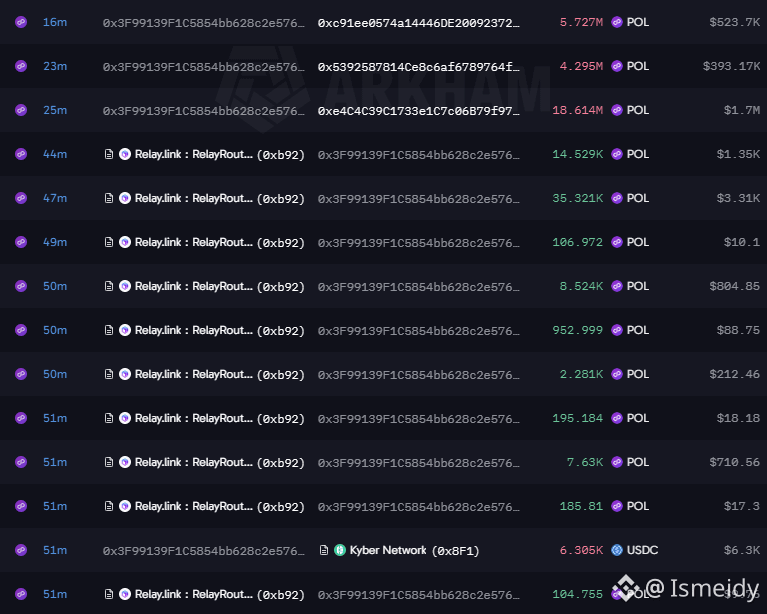
Un total de 995 cuentas de usuarios en Polymarket fueron vaciadas en un ataque cibernético que sustrajo $2,654,211.42.
Los impactos más severos recayeron sobre cuentas específicas con pérdidas individuales estimadas en $341k y $307k.
El atacante convirtió de inmediato la totalidad de los fondos sustraídos al token #POL , una maniobra táctica diseñada para eludir posibles bloqueos o congelamientos de activos.
Falla en la interfaz, no en el código: Los indicios apuntan a un compromiso en el frontend (la interfaz de usuario) de la plataforma y no en los contratos inteligentes, permitiendo la ejecución de retiros no autorizados.
Respuesta inmediata: Ante la brecha de seguridad, Polymarket suspendió y restringió temporalmente sus operaciones mientras despliega una investigación exhaustiva.
$POL
{future}(POLUSDT)
Golpe al corazón de los pronósticos
Un #Hacker vacía casi 1.000 cuentas en #Polymarket y roza los 2.65 millones de dólares
Radiografía de un ciberataque masivo
Un total de 995 cuentas de usuarios en Polymarket fueron vaciadas en un ataque cibernético que sustrajo $2,654,211.42.
Los impactos más severos recayeron sobre cuentas específicas con pérdidas individuales estimadas en $341k y $307k.
El atacante convirtió de inmediato la totalidad de los fondos sustraídos al token #POL , una maniobra táctica diseñada para eludir posibles bloqueos o congelamientos de activos.
Falla en la interfaz, no en el código: Los indicios apuntan a un compromiso en el frontend (la interfaz de usuario) de la plataforma y no en los contratos inteligentes, permitiendo la ejecución de retiros no autorizados.
Respuesta inmediata: Ante la brecha de seguridad, Polymarket suspendió y restringió temporalmente sus operaciones mientras despliega una investigación exhaustiva.
$POL
Un #Hacker vacía casi 1.000 cuentas en #Polymarket y roza los 2.65 millones de dólares
Radiografía de un ciberataque masivo
Un total de 995 cuentas de usuarios en Polymarket fueron vaciadas en un ataque cibernético que sustrajo $2,654,211.42.
Los impactos más severos recayeron sobre cuentas específicas con pérdidas individuales estimadas en $341k y $307k.
El atacante convirtió de inmediato la totalidad de los fondos sustraídos al token #POL , una maniobra táctica diseñada para eludir posibles bloqueos o congelamientos de activos.
Falla en la interfaz, no en el código: Los indicios apuntan a un compromiso en el frontend (la interfaz de usuario) de la plataforma y no en los contratos inteligentes, permitiendo la ejecución de retiros no autorizados.
Respuesta inmediata: Ante la brecha de seguridad, Polymarket suspendió y restringió temporalmente sus operaciones mientras despliega una investigación exhaustiva.
$POL
Demon 170 Etanol E85:
y si fuese cierto por qué $POL no muestra un aumento de precio ni de volumen ? También hackearon los gráficos?
5
24
43.4k
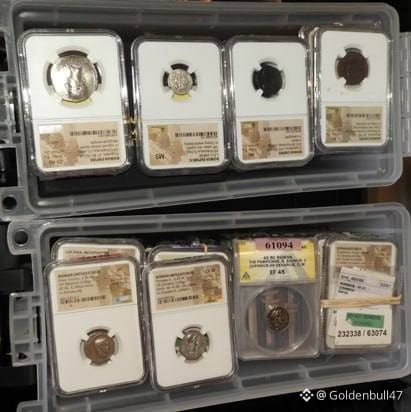
⚪️ The hacker who stole $53,000,000 from Uranium Finance spent some of the money not on yachts, but on rare Pokémon and Magic cards, a Roman coin, and even a fragment of the Wright brothers' airplane.
As a result, the authorities seized part of the collection and about $31 million in cryptocurrency — a very expensive way to build the perfect geek shelf.
#BTC #Hacker
⚪️ The hacker who stole $53,000,000 from Uranium Finance spent some of the money not on yachts, but on rare Pokémon and Magic cards, a Roman coin, and even a fragment of the Wright brothers' airplane.
As a result, the authorities seized part of the collection and about $31 million in cryptocurrency — a very expensive way to build the perfect geek shelf.
#BTC #Hacker
As a result, the authorities seized part of the collection and about $31 million in cryptocurrency — a very expensive way to build the perfect geek shelf.
#BTC #Hacker
110

·
--
黑客团伙ShinyHunters核心成员在约旦被抓,正在与FBI合作调查同伙。这个英语为主的年轻黑客组织专门窃取企业数据并勒索,这次竟然连FBI员工数据都黑了!细节太劲爆了,个人身份、职位信息甚至医疗记录都被盗。他在配合调查并交出电子设备,看来黑客圈子也要大洗牌了。
#网络安全 #黑客攻击 $BTC $ETH
ShinyHunters hacker member busted in Jordan, now working with FBI to rat out his crew. This English-speaking young hacker gang targets companies for data theft and extortion, and they actually hacked FBI employee data! Personal IDs, job info, even medical records compromised. He's cooperating and handing over devices - big shakeup coming in hacker world.
#CyberSecurity #Hacker $BTC $ETH
黑客团伙ShinyHunters核心成员在约旦被抓,正在与FBI合作调查同伙。这个英语为主的年轻黑客组织专门窃取企业数据并勒索,这次竟然连FBI员工数据都黑了!细节太劲爆了,个人身份、职位信息甚至医疗记录都被盗。他在配合调查并交出电子设备,看来黑客圈子也要大洗牌了。
#网络安全 #黑客攻击 $BTC $ETH
ShinyHunters hacker member busted in Jordan, now working with FBI to rat out his crew. This English-speaking young hacker gang targets companies for data theft and extortion, and they actually hacked FBI employee data! Personal IDs, job info, even medical records compromised. He's cooperating and handing over devices - big shakeup coming in hacker world.
#CyberSecurity #Hacker $BTC $ETH
#网络安全 #黑客攻击 $BTC $ETH
ShinyHunters hacker member busted in Jordan, now working with FBI to rat out his crew. This English-speaking young hacker gang targets companies for data theft and extortion, and they actually hacked FBI employee data! Personal IDs, job info, even medical records compromised. He's cooperating and handing over devices - big shakeup coming in hacker world.
#CyberSecurity #Hacker $BTC $ETH
57
·
--
Bitget Exploited for $351.6M: What It Means for Everyday Traders
On September 24, Bitget reported unauthorized transfers totaling approximately $351.6 million from a subset of its hot and warm wallet infrastructure. The exchange stated that cold storage reserves remain unaffected and that user losses will be fully covered by its Protection Fund. Withdrawals have been temporarily suspended.
The incident draws inevitable parallels to FTX, where operational distress in 2022 resulted in halted withdrawals and subsequent regulatory findings of commingled customer assets.
The takeaways for risk management remain clear:
Exchanges Are Execution Venues, Not Vaults: Centralized exchanges should be utilized strictly as tools for trading and liquidity, not for long-term capital storage.
Active Profit Extraction: While actively trading major assets like $BTC , ETH, $BNB , XRP, or $SOL , realized gains should be systematically withdrawn to self-custodial wallets or alternative secure storage setups.
Custody Principle: Capital idle on an exchange is subject to counterparty risk. Not your keys, not your coins.
#Bitget #FTX #CryptoSecurity #Hacker
Bitget Exploited for $351.6M: What It Means for Everyday Traders
On September 24, Bitget reported unauthorized transfers totaling approximately $351.6 million from a subset of its hot and warm wallet infrastructure. The exchange stated that cold storage reserves remain unaffected and that user losses will be fully covered by its Protection Fund. Withdrawals have been temporarily suspended.
The incident draws inevitable parallels to FTX, where operational distress in 2022 resulted in halted withdrawals and subsequent regulatory findings of commingled customer assets.
The takeaways for risk management remain clear:
Exchanges Are Execution Venues, Not Vaults: Centralized exchanges should be utilized strictly as tools for trading and liquidity, not for long-term capital storage.
Active Profit Extraction: While actively trading major assets like $BTC , ETH, $BNB , XRP, or $SOL , realized gains should be systematically withdrawn to self-custodial wallets or alternative secure storage setups.
Custody Principle: Capital idle on an exchange is subject to counterparty risk. Not your keys, not your coins.
#Bitget #FTX #CryptoSecurity #Hacker
On September 24, Bitget reported unauthorized transfers totaling approximately $351.6 million from a subset of its hot and warm wallet infrastructure. The exchange stated that cold storage reserves remain unaffected and that user losses will be fully covered by its Protection Fund. Withdrawals have been temporarily suspended.
The incident draws inevitable parallels to FTX, where operational distress in 2022 resulted in halted withdrawals and subsequent regulatory findings of commingled customer assets.
The takeaways for risk management remain clear:
Exchanges Are Execution Venues, Not Vaults: Centralized exchanges should be utilized strictly as tools for trading and liquidity, not for long-term capital storage.
Active Profit Extraction: While actively trading major assets like $BTC , ETH, $BNB , XRP, or $SOL , realized gains should be systematically withdrawn to self-custodial wallets or alternative secure storage setups.
Custody Principle: Capital idle on an exchange is subject to counterparty risk. Not your keys, not your coins.
#Bitget #FTX #CryptoSecurity #Hacker
195
·
--
Падение
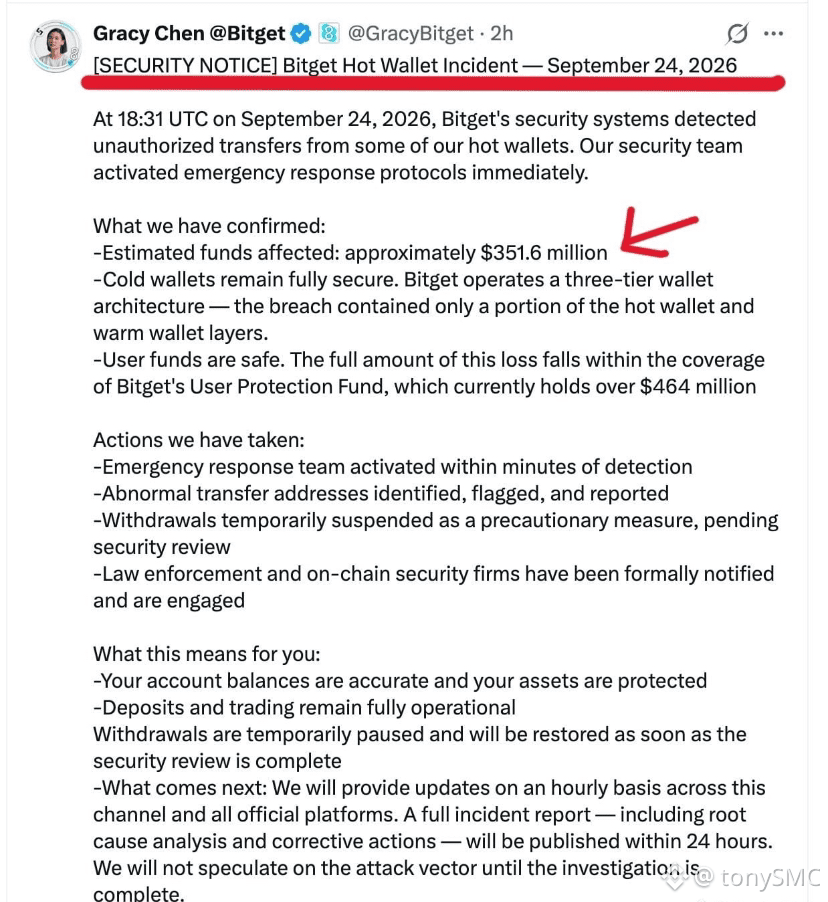
🚨 $351M HIT BITGET — AND $183M IS NOW IN $ETH
Bitget has confirmed approximately $351.6M in assets were affected after unauthorized transfers from parts of its hot and warm-wallet infrastructure.
But the more interesting part is happening on-chain.
The attacker has already converted much of the stolen EVM-chain assets into:
67,982 $ETH
Worth roughly $183M at the reported valuation.
That changes the story.
This isn’t just a wallet-drain event anymore.
It’s a massive on-chain movement that traders can actually watch in real time.
The attacker has been moving across multiple networks and swapping assets into ETH, concentrating a huge amount of value into one asset.
And there’s another number people shouldn’t miss:
102.93M XRP — roughly $157M at the reported valuation — was identified among the stolen assets, making XRP one of the largest individual asset components of the incident.
Bitget says:
• Cold wallets remain secure
• User balances remain accurate
• Deposits and trading continue
• Withdrawals are temporarily suspended
• The loss is covered by its $464M+ User Protection Fund
• Law enforcement and on-chain security firms have been notified
But here’s what I’m watching now 👇
67,982 ETH sitting on the other side of a hack is a number the market can’t ignore.
Where does it move next?
Does it remain in ETH?
Does the attacker bridge it again?
Does liquidity get fragmented across new wallets?
Or do exchanges/security firms manage to freeze part of the remaining assets?
The wallet trail may become the next major story.
Follow the addresses, not the headlines. 👀
#ETH #Bidget #Hacker #Ethereum
{future}(ETHUSDT)
🚨 $351M HIT BITGET — AND $183M IS NOW IN $ETH
Bitget has confirmed approximately $351.6M in assets were affected after unauthorized transfers from parts of its hot and warm-wallet infrastructure.
But the more interesting part is happening on-chain.
The attacker has already converted much of the stolen EVM-chain assets into:
67,982 $ETH
Worth roughly $183M at the reported valuation.
That changes the story.
This isn’t just a wallet-drain event anymore.
It’s a massive on-chain movement that traders can actually watch in real time.
The attacker has been moving across multiple networks and swapping assets into ETH, concentrating a huge amount of value into one asset.
And there’s another number people shouldn’t miss:
102.93M XRP — roughly $157M at the reported valuation — was identified among the stolen assets, making XRP one of the largest individual asset components of the incident.
Bitget says:
• Cold wallets remain secure
• User balances remain accurate
• Deposits and trading continue
• Withdrawals are temporarily suspended
• The loss is covered by its $464M+ User Protection Fund
• Law enforcement and on-chain security firms have been notified
But here’s what I’m watching now 👇
67,982 ETH sitting on the other side of a hack is a number the market can’t ignore.
Where does it move next?
Does it remain in ETH?
Does the attacker bridge it again?
Does liquidity get fragmented across new wallets?
Or do exchanges/security firms manage to freeze part of the remaining assets?
The wallet trail may become the next major story.
Follow the addresses, not the headlines. 👀
#ETH #Bidget #Hacker #Ethereum
Bitget has confirmed approximately $351.6M in assets were affected after unauthorized transfers from parts of its hot and warm-wallet infrastructure.
But the more interesting part is happening on-chain.
The attacker has already converted much of the stolen EVM-chain assets into:
67,982 $ETH
Worth roughly $183M at the reported valuation.
That changes the story.
This isn’t just a wallet-drain event anymore.
It’s a massive on-chain movement that traders can actually watch in real time.
The attacker has been moving across multiple networks and swapping assets into ETH, concentrating a huge amount of value into one asset.
And there’s another number people shouldn’t miss:
102.93M XRP — roughly $157M at the reported valuation — was identified among the stolen assets, making XRP one of the largest individual asset components of the incident.
Bitget says:
• Cold wallets remain secure
• User balances remain accurate
• Deposits and trading continue
• Withdrawals are temporarily suspended
• The loss is covered by its $464M+ User Protection Fund
• Law enforcement and on-chain security firms have been notified
But here’s what I’m watching now 👇
67,982 ETH sitting on the other side of a hack is a number the market can’t ignore.
Where does it move next?
Does it remain in ETH?
Does the attacker bridge it again?
Does liquidity get fragmented across new wallets?
Or do exchanges/security firms manage to freeze part of the remaining assets?
The wallet trail may become the next major story.
Follow the addresses, not the headlines. 👀
#ETH #Bidget #Hacker #Ethereum
1
77
·
--
El #Hacker de Bitget intenta "desaparecer" 3.9 millones de dólares en la oscuridad de Zcash
La ruta del dinero robado se adentra en el anonimato
Las investigaciones sobre el histórico #hackeo a Bitget, valorado en 387.5 millones de dólares, han dado un giro crítico tras detectarse sofisticados movimientos de evasión en la blockchain. El atacante ha comenzado a canalizar los fondos hacia mecanismos de privacidad avanzada para romper la trazabilidad de los analistas on-chain.
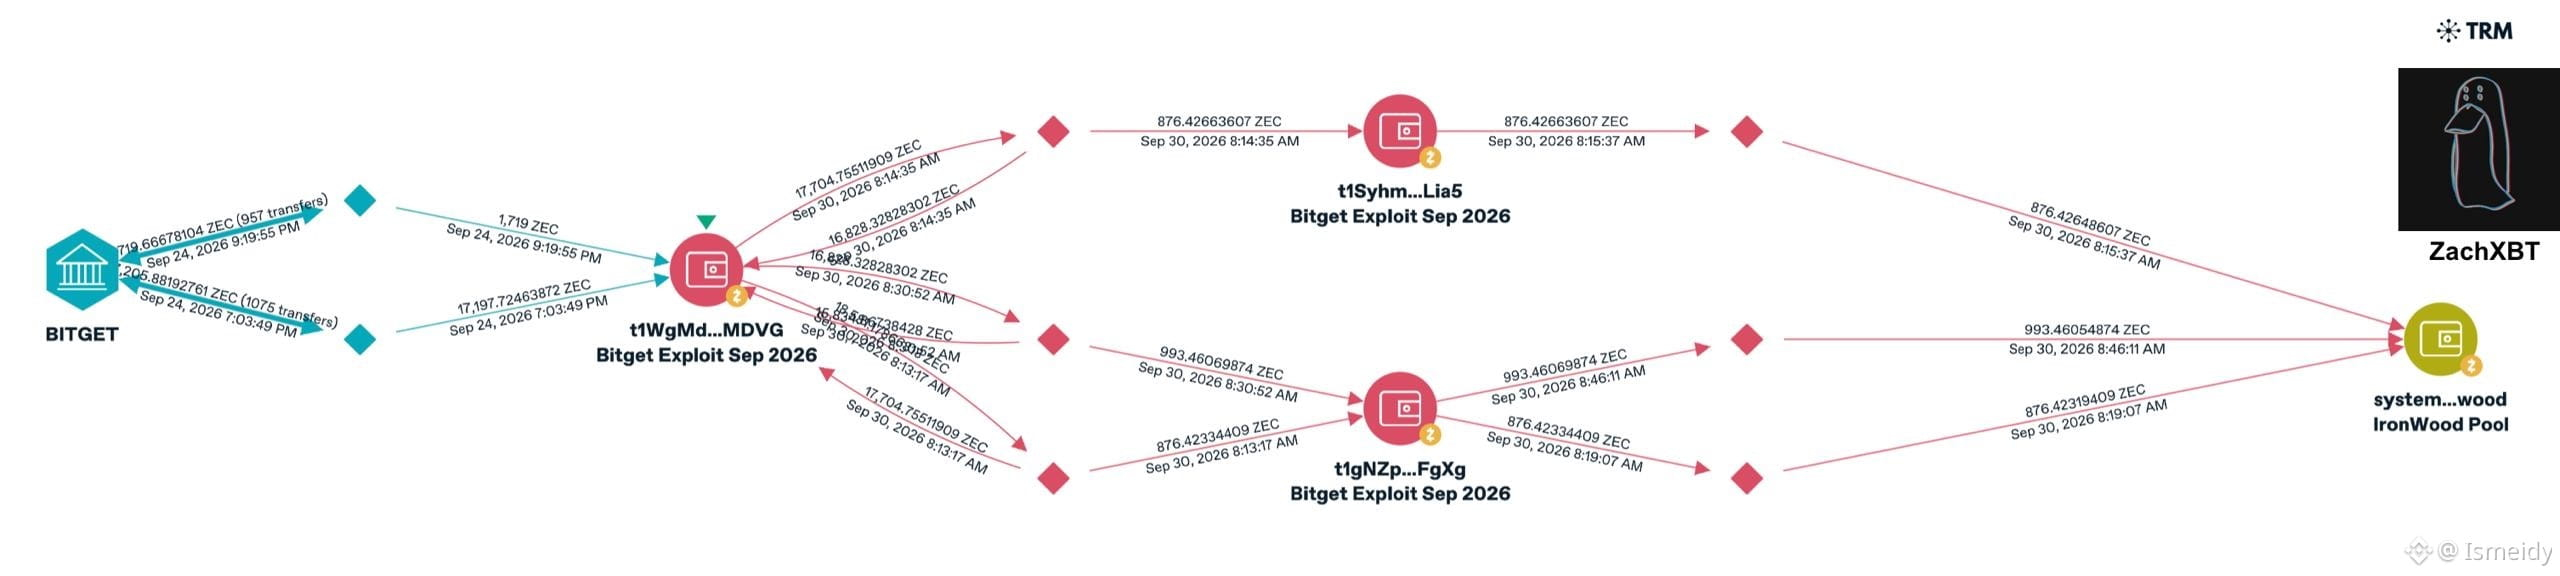
Infiltración en la zona ciega de Zcash: Entre las 08:15 y las 08:46 UTC del 30 de septiembre de 2026, el atacante transfirió 2.746 #zec }(aproximadamente 3.9 millones de dólares) hacia Ironwood, el nuevo fondo/pool protegido (shielded pool) de #Zcash
Estructura de la operación (Mapeo de ZachXBT / TRM Labs)
El investigador de blockchain ZachXBT fue el primero en alertar sobre la maniobra.
La billetera principal identificada por Bitget tras la brecha del 24 de septiembre acumulaba casi 18.917 ZEC.
Los fondos se dividieron a través de dos direcciones intermediarias (t1Syhm...Lia5 y t1gNZp...FgXg) en tres depósitos coordinados antes de ingresar al pool privado.
El desafío técnico para los investigadores: A diferencia de las transacciones públicas donde los flujos son visibles de extremo a extremo, el sistema blindado de Zcash oculta el remitente, el destinatario y los saldos internos. Aunque la entrada al pool Ironwood es rastreable, el rastro contable se pierde por completo dentro del sistema hasta que los fondos decidan salir a una dirección pública.
Diversificación de rutas de lavado: Los depósitos en Zcash representan cerca del 15% del total de ZEC robado. Previamente, análisis de firmas de inteligencia rastrearon la conversión de 6,3 millones de dólares de Ether a Bitcoin utilizando el protocolo descentralizado THORChain, combinando métodos cross-chain transparentes con protocolos de privacidad estricta.
#CryptoNews
$ZEC
{future}(ZECUSDT)
$HYPE
{future}(HYPEUSDT)
$XRP
{future}(XRPUSDT)
El #Hacker de Bitget intenta "desaparecer" 3.9 millones de dólares en la oscuridad de Zcash
La ruta del dinero robado se adentra en el anonimato
Las investigaciones sobre el histórico #hackeo a Bitget, valorado en 387.5 millones de dólares, han dado un giro crítico tras detectarse sofisticados movimientos de evasión en la blockchain. El atacante ha comenzado a canalizar los fondos hacia mecanismos de privacidad avanzada para romper la trazabilidad de los analistas on-chain.
Infiltración en la zona ciega de Zcash: Entre las 08:15 y las 08:46 UTC del 30 de septiembre de 2026, el atacante transfirió 2.746 #zec }(aproximadamente 3.9 millones de dólares) hacia Ironwood, el nuevo fondo/pool protegido (shielded pool) de #Zcash
Estructura de la operación (Mapeo de ZachXBT / TRM Labs)
El investigador de blockchain ZachXBT fue el primero en alertar sobre la maniobra.
La billetera principal identificada por Bitget tras la brecha del 24 de septiembre acumulaba casi 18.917 ZEC.
Los fondos se dividieron a través de dos direcciones intermediarias (t1Syhm...Lia5 y t1gNZp...FgXg) en tres depósitos coordinados antes de ingresar al pool privado.
El desafío técnico para los investigadores: A diferencia de las transacciones públicas donde los flujos son visibles de extremo a extremo, el sistema blindado de Zcash oculta el remitente, el destinatario y los saldos internos. Aunque la entrada al pool Ironwood es rastreable, el rastro contable se pierde por completo dentro del sistema hasta que los fondos decidan salir a una dirección pública.
Diversificación de rutas de lavado: Los depósitos en Zcash representan cerca del 15% del total de ZEC robado. Previamente, análisis de firmas de inteligencia rastrearon la conversión de 6,3 millones de dólares de Ether a Bitcoin utilizando el protocolo descentralizado THORChain, combinando métodos cross-chain transparentes con protocolos de privacidad estricta.
#CryptoNews
$ZEC
$HYPE
$XRP
La ruta del dinero robado se adentra en el anonimato
Las investigaciones sobre el histórico #hackeo a Bitget, valorado en 387.5 millones de dólares, han dado un giro crítico tras detectarse sofisticados movimientos de evasión en la blockchain. El atacante ha comenzado a canalizar los fondos hacia mecanismos de privacidad avanzada para romper la trazabilidad de los analistas on-chain.
Infiltración en la zona ciega de Zcash: Entre las 08:15 y las 08:46 UTC del 30 de septiembre de 2026, el atacante transfirió 2.746 #zec }(aproximadamente 3.9 millones de dólares) hacia Ironwood, el nuevo fondo/pool protegido (shielded pool) de #Zcash
Estructura de la operación (Mapeo de ZachXBT / TRM Labs)
El investigador de blockchain ZachXBT fue el primero en alertar sobre la maniobra.
La billetera principal identificada por Bitget tras la brecha del 24 de septiembre acumulaba casi 18.917 ZEC.
Los fondos se dividieron a través de dos direcciones intermediarias (t1Syhm...Lia5 y t1gNZp...FgXg) en tres depósitos coordinados antes de ingresar al pool privado.
El desafío técnico para los investigadores: A diferencia de las transacciones públicas donde los flujos son visibles de extremo a extremo, el sistema blindado de Zcash oculta el remitente, el destinatario y los saldos internos. Aunque la entrada al pool Ironwood es rastreable, el rastro contable se pierde por completo dentro del sistema hasta que los fondos decidan salir a una dirección pública.
Diversificación de rutas de lavado: Los depósitos en Zcash representan cerca del 15% del total de ZEC robado. Previamente, análisis de firmas de inteligencia rastrearon la conversión de 6,3 millones de dólares de Ether a Bitcoin utilizando el protocolo descentralizado THORChain, combinando métodos cross-chain transparentes con protocolos de privacidad estricta.
#CryptoNews
$ZEC
$HYPE
$XRP
1
3
3.4k
·
--
De una prueba de centavos a un saqueo de $388 millones
La anatomía del audaz #hackeo a Bitget
30 minutos a ciegas, cómo una vulnerabilidad de "Día Cero" permitió el robo de millones en Bitget
El ataque inició a las 18:31 UTC con dos microtransferencias (0,184 ETH y 193 TRX). Al ser montos insignificantes, no activaron los protocolos de riesgo del exchange, dándole al atacante luz verde para avanzar.
El drenaje masivo: Apenas 30 minutos después de la prueba, el #Hacker ejecutó 17 transacciones de gran volumen a través de múltiples redes ( #Ethereum , #xrp , #Zcash , BNB Chain, Base, Arbitrum, Optimism y Avalanche), logrando extraer $361 millones en poco más de una hora.
Ingeniería del ataque (Día Cero): Las carteras frías (cold wallets) y las claves privadas de Bitget no fueron comprometidas. El hacker explotó una vulnerabilidad de día cero en un producto de seguridad de terceros, lo que le permitió inyectar comandos de retiro fraudulentos directamente en el sistema interno y luego borrar sus huellas informáticas.
Reacción y contención: El sistema de conciliación de la plataforma detectó la anomalía tan solo siete minutos después del primer gran retiro, lo que permitió activar el bloqueo global de retiros y frenar el desangre.
Impacto cero para los usuarios: Gracy Chen (CEO) confirmó que las pérdidas serán absorbidas en su totalidad por el Fondo de Protección al Usuario, valorado en $465 millones. Bitget repondrá este fondo en menos de una semana utilizando sus reservas corporativas, las cuales superan los $1.400 millones. "Es grave, pero no existencial", sentenció Chen.
Restauración operativa e investigación: Los retiros de Bitcoin ya se han reanudado (procesando más de 3.000 BTC en la primera hora) y los de ETH volverán el 29 de septiembre. Empresas forenses como Mandiant y SlowMist están en la investigación, y la directiva de Bitget asegura que ya tienen en la mira al grupo sospechoso.
$XRP
{future}(XRPUSDT)
$ZEC
{future}(ZECUSDT)
$BNB
{future}(BNBUSDT)
De una prueba de centavos a un saqueo de $388 millones
La anatomía del audaz #hackeo a Bitget
30 minutos a ciegas, cómo una vulnerabilidad de "Día Cero" permitió el robo de millones en Bitget
El ataque inició a las 18:31 UTC con dos microtransferencias (0,184 ETH y 193 TRX). Al ser montos insignificantes, no activaron los protocolos de riesgo del exchange, dándole al atacante luz verde para avanzar.
El drenaje masivo: Apenas 30 minutos después de la prueba, el #Hacker ejecutó 17 transacciones de gran volumen a través de múltiples redes ( #Ethereum , #xrp , #Zcash , BNB Chain, Base, Arbitrum, Optimism y Avalanche), logrando extraer $361 millones en poco más de una hora.
Ingeniería del ataque (Día Cero): Las carteras frías (cold wallets) y las claves privadas de Bitget no fueron comprometidas. El hacker explotó una vulnerabilidad de día cero en un producto de seguridad de terceros, lo que le permitió inyectar comandos de retiro fraudulentos directamente en el sistema interno y luego borrar sus huellas informáticas.
Reacción y contención: El sistema de conciliación de la plataforma detectó la anomalía tan solo siete minutos después del primer gran retiro, lo que permitió activar el bloqueo global de retiros y frenar el desangre.
Impacto cero para los usuarios: Gracy Chen (CEO) confirmó que las pérdidas serán absorbidas en su totalidad por el Fondo de Protección al Usuario, valorado en $465 millones. Bitget repondrá este fondo en menos de una semana utilizando sus reservas corporativas, las cuales superan los $1.400 millones. "Es grave, pero no existencial", sentenció Chen.
Restauración operativa e investigación: Los retiros de Bitcoin ya se han reanudado (procesando más de 3.000 BTC en la primera hora) y los de ETH volverán el 29 de septiembre. Empresas forenses como Mandiant y SlowMist están en la investigación, y la directiva de Bitget asegura que ya tienen en la mira al grupo sospechoso.
$XRP
$ZEC
$BNB
La anatomía del audaz #hackeo a Bitget
30 minutos a ciegas, cómo una vulnerabilidad de "Día Cero" permitió el robo de millones en Bitget
El ataque inició a las 18:31 UTC con dos microtransferencias (0,184 ETH y 193 TRX). Al ser montos insignificantes, no activaron los protocolos de riesgo del exchange, dándole al atacante luz verde para avanzar.
El drenaje masivo: Apenas 30 minutos después de la prueba, el #Hacker ejecutó 17 transacciones de gran volumen a través de múltiples redes ( #Ethereum , #xrp , #Zcash , BNB Chain, Base, Arbitrum, Optimism y Avalanche), logrando extraer $361 millones en poco más de una hora.
Ingeniería del ataque (Día Cero): Las carteras frías (cold wallets) y las claves privadas de Bitget no fueron comprometidas. El hacker explotó una vulnerabilidad de día cero en un producto de seguridad de terceros, lo que le permitió inyectar comandos de retiro fraudulentos directamente en el sistema interno y luego borrar sus huellas informáticas.
Reacción y contención: El sistema de conciliación de la plataforma detectó la anomalía tan solo siete minutos después del primer gran retiro, lo que permitió activar el bloqueo global de retiros y frenar el desangre.
Impacto cero para los usuarios: Gracy Chen (CEO) confirmó que las pérdidas serán absorbidas en su totalidad por el Fondo de Protección al Usuario, valorado en $465 millones. Bitget repondrá este fondo en menos de una semana utilizando sus reservas corporativas, las cuales superan los $1.400 millones. "Es grave, pero no existencial", sentenció Chen.
Restauración operativa e investigación: Los retiros de Bitcoin ya se han reanudado (procesando más de 3.000 BTC en la primera hora) y los de ETH volverán el 29 de septiembre. Empresas forenses como Mandiant y SlowMist están en la investigación, y la directiva de Bitget asegura que ya tienen en la mira al grupo sospechoso.
$XRP
$ZEC
$BNB
6
11
18.1k
·
--
️ تنبيه مهم لحاملي العملات 😱
تمكن قراصنة من سرقة 593 BTC (ما يقارب 39 مليون دولار) من محافظ Coldcard Mk3 الباردة.
السبب يعود إلى خلل مرتبط بعملية توليد العبارة السرية (Seed Phrase)، مما سمح باشتقاق المفاتيح الخاصة والوصول إلى الأموال.$BNB
🔐 احرص دائمًا على استخدام محافظ باردة موثوقة، ذات سجل قوي وتم اختبارها عبر الزمن.
#HackerAlert #Hacker #BTC
$BTC
{future}(BNBUSDT)
{future}(BTCUSDT)
️ تنبيه مهم لحاملي العملات 😱
تمكن قراصنة من سرقة 593 BTC (ما يقارب 39 مليون دولار) من محافظ Coldcard Mk3 الباردة.
السبب يعود إلى خلل مرتبط بعملية توليد العبارة السرية (Seed Phrase)، مما سمح باشتقاق المفاتيح الخاصة والوصول إلى الأموال.$BNB
🔐 احرص دائمًا على استخدام محافظ باردة موثوقة، ذات سجل قوي وتم اختبارها عبر الزمن.
#HackerAlert #Hacker #BTC
$BTC
تمكن قراصنة من سرقة 593 BTC (ما يقارب 39 مليون دولار) من محافظ Coldcard Mk3 الباردة.
السبب يعود إلى خلل مرتبط بعملية توليد العبارة السرية (Seed Phrase)، مما سمح باشتقاق المفاتيح الخاصة والوصول إلى الأموال.$BNB
🔐 احرص دائمًا على استخدام محافظ باردة موثوقة، ذات سجل قوي وتم اختبارها عبر الزمن.
#HackerAlert #Hacker #BTC
$BTC
101
·
--
A NOTE for holders
😱😱😱😱😱😱😱😱😱😱😱😱😱😱😱
😱😱😱😱😱😱😱😱😱😱😱😱😱😱
Hackers managed to steal 593 BTC (approximately $39 million) from Coldcard Mk3 cold wallets.
The cause was a bug related to seed phrase generation that allowed private keys to be derived.
Choose cold wallets that are well-established and time-tested.
#HackerAlert #Hacker #BTC
$BTC
{future}(BTCUSDT)
$BNB
{future}(BNBUSDT)
A NOTE for holders
😱😱😱😱😱😱😱😱😱😱😱😱😱😱😱
😱😱😱😱😱😱😱😱😱😱😱😱😱😱
Hackers managed to steal 593 BTC (approximately $39 million) from Coldcard Mk3 cold wallets.
The cause was a bug related to seed phrase generation that allowed private keys to be derived.
Choose cold wallets that are well-established and time-tested.
#HackerAlert #Hacker #BTC
$BTC
$BNB
😱😱😱😱😱😱😱😱😱😱😱😱😱😱😱
😱😱😱😱😱😱😱😱😱😱😱😱😱😱
Hackers managed to steal 593 BTC (approximately $39 million) from Coldcard Mk3 cold wallets.
The cause was a bug related to seed phrase generation that allowed private keys to be derived.
Choose cold wallets that are well-established and time-tested.
#HackerAlert #Hacker #BTC
$BTC
$BNB
16
1
91
117k

·
--
Падение
🔥Se empiezan a mover los Bitcoins robados del caso Cold card 😕
En las últimas horas ya se empezaron a mover algunos #bitcoins robados referente al caso del exploit de #Coldcard , esto a través de una técnica llamada “peel Chain” pasando por el mixer Coinjoin. Este hecho no pinta muy bien para los afectados de este incidente, ya que, si se sigue usando esta técnica, la posibilidad de recuperar estos fondos va a ser muy difícil.
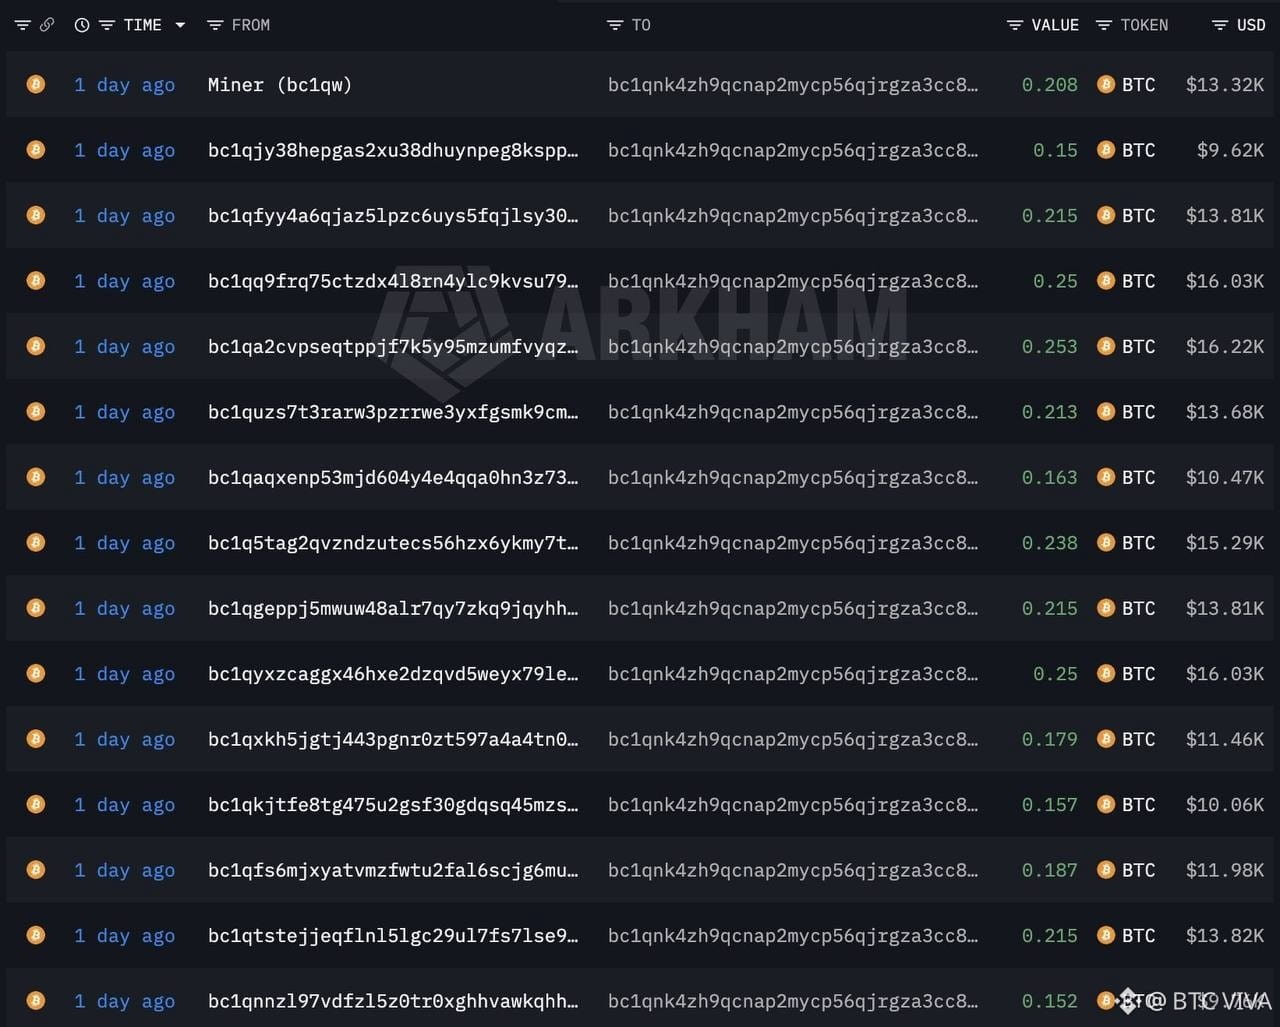
Según datos en cadena, el #Hacker (o hackers) ya han movido 64 #BTC y los hace a través de varios procesos. Primero envía los fondos a una nueva dirección, luego pasa los fondos por un mixer (como coinjoin), después empieza a separalos en unidades más pequeñas, y luego estas unidades los vuelve a mezclar. Esto lo hace con el fin de perder la trazabilidad y poder sacar el dinero fiat.
Lo que está siendo criticado últimamente es el uso del mixer centralizado coinjoin, ya que se sabe a quien pertenece, sin embargo, no están ayudando a congelar los fondos ¿La razón? Para la persona detrás de Coinjoin , “no se puede probar que los fondos son robados” . Este argumento generó indignación entre la comunidad.
Si hasta el momento no se ha hecho una intervención y si el atacante (hacker) sigue usando esta misma técnica, es muy probable que estos fondos no se lleguen a recuperar nunca.
¿Cómo acabará esta historia?
👉Mas actualizaciones cripto ...
Comparte y sigueme para más 👈😎
$BTC
{spot}(BTCUSDT)
🔥Se empiezan a mover los Bitcoins robados del caso Cold card 😕
En las últimas horas ya se empezaron a mover algunos #bitcoins robados referente al caso del exploit de #Coldcard , esto a través de una técnica llamada “peel Chain” pasando por el mixer Coinjoin. Este hecho no pinta muy bien para los afectados de este incidente, ya que, si se sigue usando esta técnica, la posibilidad de recuperar estos fondos va a ser muy difícil.
Según datos en cadena, el #Hacker (o hackers) ya han movido 64 #BTC y los hace a través de varios procesos. Primero envía los fondos a una nueva dirección, luego pasa los fondos por un mixer (como coinjoin), después empieza a separalos en unidades más pequeñas, y luego estas unidades los vuelve a mezclar. Esto lo hace con el fin de perder la trazabilidad y poder sacar el dinero fiat.
Lo que está siendo criticado últimamente es el uso del mixer centralizado coinjoin, ya que se sabe a quien pertenece, sin embargo, no están ayudando a congelar los fondos ¿La razón? Para la persona detrás de Coinjoin , “no se puede probar que los fondos son robados” . Este argumento generó indignación entre la comunidad.
Si hasta el momento no se ha hecho una intervención y si el atacante (hacker) sigue usando esta misma técnica, es muy probable que estos fondos no se lleguen a recuperar nunca.
¿Cómo acabará esta historia?
👉Mas actualizaciones cripto ...
Comparte y sigueme para más 👈😎
$BTC
En las últimas horas ya se empezaron a mover algunos #bitcoins robados referente al caso del exploit de #Coldcard , esto a través de una técnica llamada “peel Chain” pasando por el mixer Coinjoin. Este hecho no pinta muy bien para los afectados de este incidente, ya que, si se sigue usando esta técnica, la posibilidad de recuperar estos fondos va a ser muy difícil.
Según datos en cadena, el #Hacker (o hackers) ya han movido 64 #BTC y los hace a través de varios procesos. Primero envía los fondos a una nueva dirección, luego pasa los fondos por un mixer (como coinjoin), después empieza a separalos en unidades más pequeñas, y luego estas unidades los vuelve a mezclar. Esto lo hace con el fin de perder la trazabilidad y poder sacar el dinero fiat.
Lo que está siendo criticado últimamente es el uso del mixer centralizado coinjoin, ya que se sabe a quien pertenece, sin embargo, no están ayudando a congelar los fondos ¿La razón? Para la persona detrás de Coinjoin , “no se puede probar que los fondos son robados” . Este argumento generó indignación entre la comunidad.
Si hasta el momento no se ha hecho una intervención y si el atacante (hacker) sigue usando esta misma técnica, es muy probable que estos fondos no se lleguen a recuperar nunca.
¿Cómo acabará esta historia?
👉Mas actualizaciones cripto ...
Comparte y sigueme para más 👈😎
$BTC
2
6
10.6k
·
--
"Arreglen el error primero"
Un #Hacker ético roba $320 millones en #LiquidNetwork y exige un parche a #Blockstream para devolver el dinero
Se retiraron aproximadamente 4.000 #BTC de la billetera de la federación de Liquid Network. El atacante aprovechó un fallo en el software Elements para crear L-BTC y procesarlos a través del servicio de compensación de SideSwap, descartando que la clave de autorización estuviera comprometida.
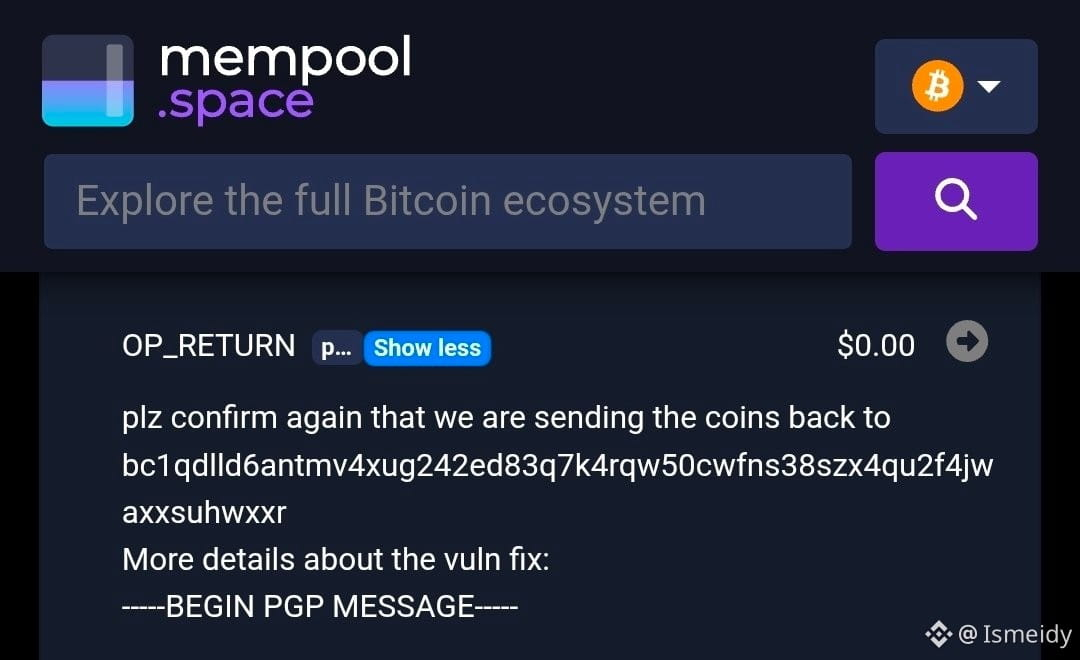
Exigencia 'on-chain': Mediante mensajes cifrados con PGP y registros OP_RETURN en la cadena de bloques, el supuesto hacker ético prometió devolver la mayor parte de los fondos con una sola condición: que Blockstream corrigiera la vulnerabilidad y asegurara la actualización de todos los nodos antes del traspaso.
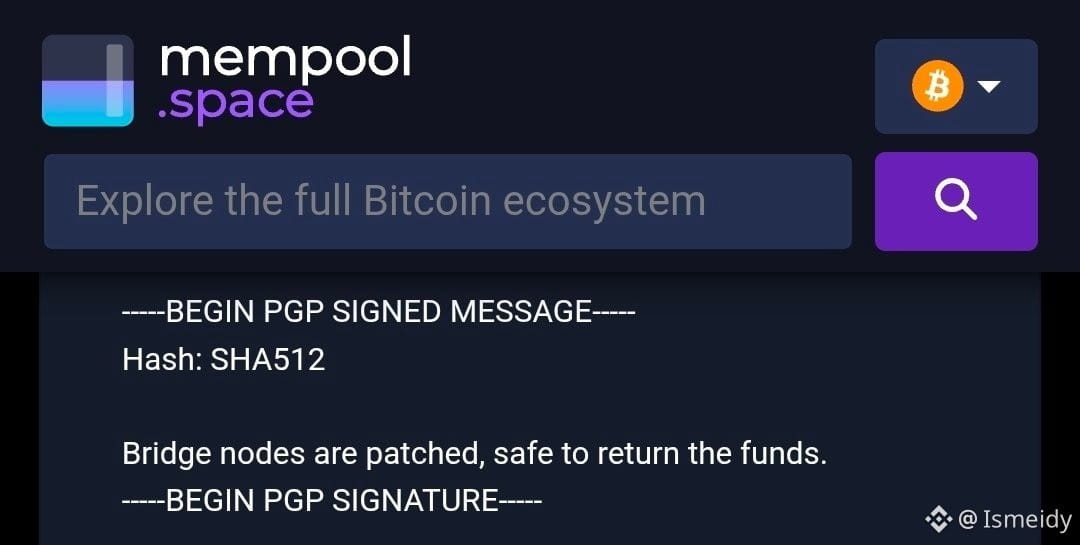
Luz verde de #AdamBack : Blockstream respondió con una firma PGP verificable confirmando que los nodos puente han sido parcheados y que la red está lista para recibir el retorno del capital sin riesgos.
Estado de congelamiento: Pese a la confirmación, los 4.000 BTC permanecen en la billetera del atacante. Como medida preventiva, Liquid Network mantiene totalmente suspendidas las operaciones en sus nodos puente, pausando depósitos, retiros y la actividad en SideSwap.
$BTC
{future}(BTCUSDT)
$XRP
{future}(XRPUSDT)
$SOL
{future}(SOLUSDT)
"Arreglen el error primero"
Un #Hacker ético roba $320 millones en #LiquidNetwork y exige un parche a #Blockstream para devolver el dinero
Se retiraron aproximadamente 4.000 #BTC de la billetera de la federación de Liquid Network. El atacante aprovechó un fallo en el software Elements para crear L-BTC y procesarlos a través del servicio de compensación de SideSwap, descartando que la clave de autorización estuviera comprometida.
Exigencia 'on-chain': Mediante mensajes cifrados con PGP y registros OP_RETURN en la cadena de bloques, el supuesto hacker ético prometió devolver la mayor parte de los fondos con una sola condición: que Blockstream corrigiera la vulnerabilidad y asegurara la actualización de todos los nodos antes del traspaso.
Luz verde de #AdamBack : Blockstream respondió con una firma PGP verificable confirmando que los nodos puente han sido parcheados y que la red está lista para recibir el retorno del capital sin riesgos.
Estado de congelamiento: Pese a la confirmación, los 4.000 BTC permanecen en la billetera del atacante. Como medida preventiva, Liquid Network mantiene totalmente suspendidas las operaciones en sus nodos puente, pausando depósitos, retiros y la actividad en SideSwap.
$BTC
$XRP
$SOL
Un #Hacker ético roba $320 millones en #LiquidNetwork y exige un parche a #Blockstream para devolver el dinero
Se retiraron aproximadamente 4.000 #BTC de la billetera de la federación de Liquid Network. El atacante aprovechó un fallo en el software Elements para crear L-BTC y procesarlos a través del servicio de compensación de SideSwap, descartando que la clave de autorización estuviera comprometida.
Exigencia 'on-chain': Mediante mensajes cifrados con PGP y registros OP_RETURN en la cadena de bloques, el supuesto hacker ético prometió devolver la mayor parte de los fondos con una sola condición: que Blockstream corrigiera la vulnerabilidad y asegurara la actualización de todos los nodos antes del traspaso.
Luz verde de #AdamBack : Blockstream respondió con una firma PGP verificable confirmando que los nodos puente han sido parcheados y que la red está lista para recibir el retorno del capital sin riesgos.
Estado de congelamiento: Pese a la confirmación, los 4.000 BTC permanecen en la billetera del atacante. Como medida preventiva, Liquid Network mantiene totalmente suspendidas las operaciones en sus nodos puente, pausando depósitos, retiros y la actividad en SideSwap.
$BTC
$XRP
$SOL
9
10
13.3k
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#BinanceReopensWithdrawalsForMoreAssets
Просмотров: 583,267
2,696 обсуждают
2
#BTCRebounds80K
Просмотров: 107,862
1,058 обсуждают
3
#Binance98PercentReplenished
Просмотров: 58,232
760 обсуждают
4
#ADPUSPrivateEmployersAdd86000JobsInOctober
Просмотров: 4,809
57 обсуждают
5
#USMidterms-WhatAreMarketsExpecting?
Просмотров: 403,129
2,268 обсуждают
6
#USOctoberNFP-AreRateCutsStillPossible
Просмотров: 425,046
2,988 обсуждают
7
#TRUMPFalls18.1%In24HoursToRecordLow
Просмотров: 1,376
42 обсуждают
8
#USClearsSingleStockPerpetualFutures
Просмотров: 4,041
100 обсуждают
9
#GrayscaleSaysJPMorganAddsBitcoinTo2027LongTermAssumptions
Просмотров: 0
0 обсуждают
10
#HongKongPlansGoldTokensTiedTo400OunceBars
Просмотров: 0
0 обсуждают