
#hack
hack
Просмотров: 1.4M
1,371 обсуждают
Популярные
Новые
·
--
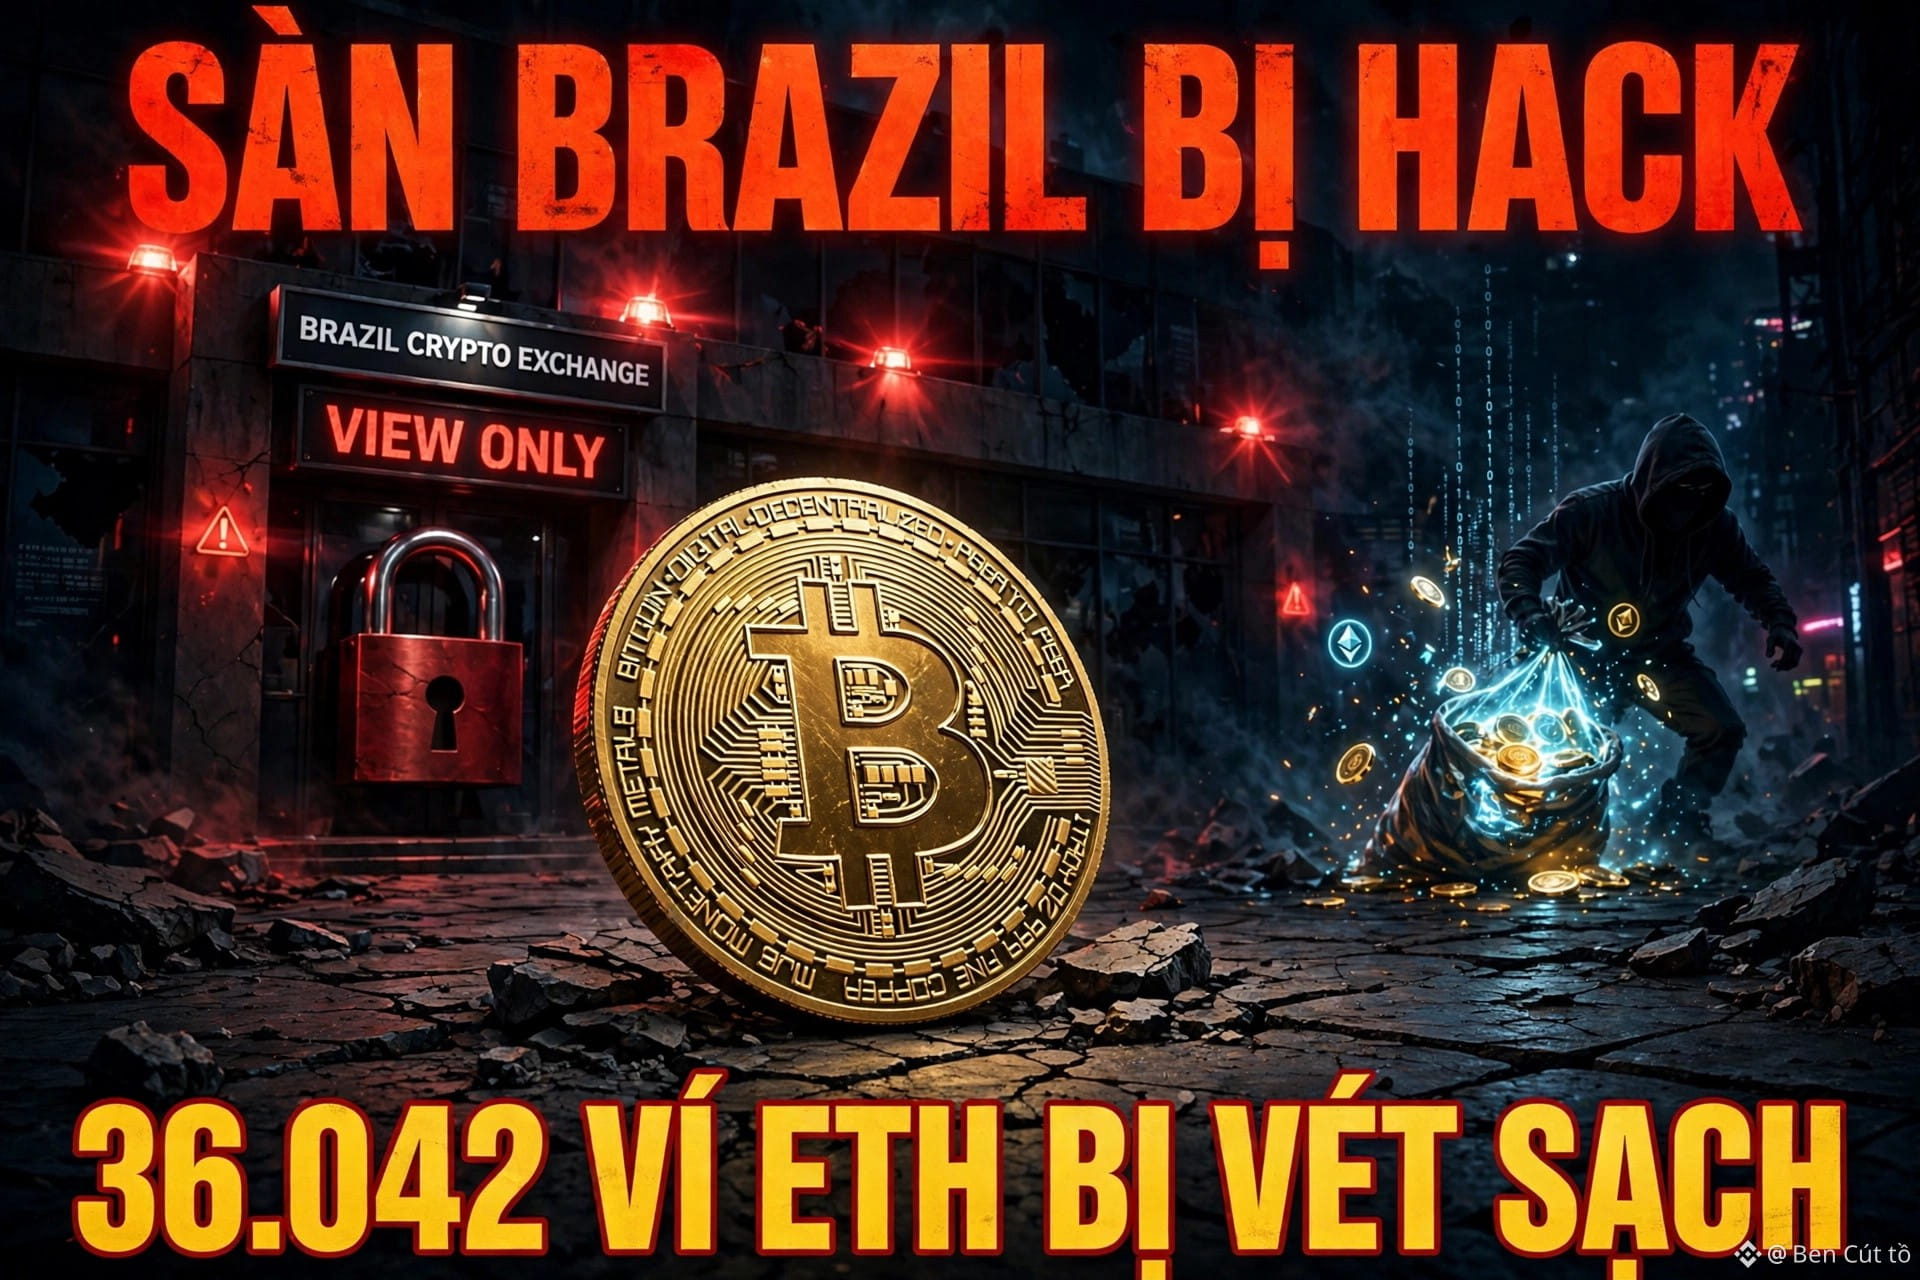
🚨 TIN NÓNG: Sàn crypto LỚN NHẤT Brazil vừa bị hack sạch ví nóng!
Mercado Bitcoin đóng băng rút tiền từ 2/11, sau khi hacker vét sạch 36.042 địa chỉ nạp ETH chỉ trong 4,5 giờ — thiệt hại ước tính 40–46 triệu USD, lan sang ít nhất 10 blockchain.
Hôm nay 9/11 sàn mới mở lại... nhưng CHỈ cho xem số dư. Nạp, rút, giao dịch vẫn khóa cứng, chưa hẹn ngày mở lại. Tether đã kịp đóng băng hơn 4,5 triệu USDT.
Cú twist: $BTC gần như không nhúc nhích — vẫn quanh $76.000, ngay trên đường trung bình 200 ngày. Thị trường đã chai sạn với hack, hay bão chỉ đang chờ nổ?
Sàn hứa tự bỏ tiền đền bù. Tin được thì tin.
Lưu lại đi — lần sau sàn nào nói "bảo mật tuyệt đối", nhớ bài này.
Theo dõi tôi, tôi đăng ở đây đầu tiên. 🔥
#Bitcoin #Hack
🚨 TIN NÓNG: Sàn crypto LỚN NHẤT Brazil vừa bị hack sạch ví nóng!
Mercado Bitcoin đóng băng rút tiền từ 2/11, sau khi hacker vét sạch 36.042 địa chỉ nạp ETH chỉ trong 4,5 giờ — thiệt hại ước tính 40–46 triệu USD, lan sang ít nhất 10 blockchain.
Hôm nay 9/11 sàn mới mở lại... nhưng CHỈ cho xem số dư. Nạp, rút, giao dịch vẫn khóa cứng, chưa hẹn ngày mở lại. Tether đã kịp đóng băng hơn 4,5 triệu USDT.
Cú twist: $BTC gần như không nhúc nhích — vẫn quanh $76.000, ngay trên đường trung bình 200 ngày. Thị trường đã chai sạn với hack, hay bão chỉ đang chờ nổ?
Sàn hứa tự bỏ tiền đền bù. Tin được thì tin.
Lưu lại đi — lần sau sàn nào nói "bảo mật tuyệt đối", nhớ bài này.
Theo dõi tôi, tôi đăng ở đây đầu tiên. 🔥
#Bitcoin #Hack
Mercado Bitcoin đóng băng rút tiền từ 2/11, sau khi hacker vét sạch 36.042 địa chỉ nạp ETH chỉ trong 4,5 giờ — thiệt hại ước tính 40–46 triệu USD, lan sang ít nhất 10 blockchain.
Hôm nay 9/11 sàn mới mở lại... nhưng CHỈ cho xem số dư. Nạp, rút, giao dịch vẫn khóa cứng, chưa hẹn ngày mở lại. Tether đã kịp đóng băng hơn 4,5 triệu USDT.
Cú twist: $BTC gần như không nhúc nhích — vẫn quanh $76.000, ngay trên đường trung bình 200 ngày. Thị trường đã chai sạn với hack, hay bão chỉ đang chờ nổ?
Sàn hứa tự bỏ tiền đền bù. Tin được thì tin.
Lưu lại đi — lần sau sàn nào nói "bảo mật tuyệt đối", nhớ bài này.
Theo dõi tôi, tôi đăng ở đây đầu tiên. 🔥
#Bitcoin #Hack
911
·
--
#Hack
En Ciberseguridad e Informática
Un hack es una técnica, método o procedimiento diseñado para modificar el funcionamiento normal de un sistema informático, un dispositivo o un programa, a menudo para lograr un objetivo que sus creadores original o intencionalmente no previeron.
Modificaciones de Hardware y Dispositivos
En el ámbito de la electrónica y los dispositivos físicos, un hack se refiere a la adaptación o modificación de aparatos (como consolas de videojuegos, teléfonos, placas de desarrollo o electrodomésticos) para desbloquear funciones ocultas, cambiar el sistema operativo (firmware) o reparar componentes utilizando piezas alternativas.
Uso cotidiano: "Lifehacks"
Fuera de la tecnología pura, la palabra se popularizó como lifehack para referirse a trucos caseros, atajos o métodos ingeniosos que hacen la vida diaria más eficiente y sencilla utilizando los recursos que ya se tienen a la mano.
Es muy importante separar un mito de la realidad: la cadena de bloques (blockchain) en sí misma es extremadamente difícil de hackear debido a su estructura descentralizada y criptográfica. Sin embargo, el ecosistema cripto está rodeado de aplicaciones, plataformas y usuarios, y es ahí donde los atacantes encuentran fallos para aplicar la lógica del hack.
Ataques a Exchanges y Plataformas Centralizadas
Aunque las criptomonedas son descentralizadas, millones de usuarios guardan su dinero en plataformas de intercambio centralizadas (exchanges).
Explotación de "Puentes" (Cross-Chain Bridges)
Los puentes son los protocolos que permiten transferir criptomonedas de una blockchain a otra (por ejemplo, pasar fondos de Ethereum a BNB Chain).
Phishing y Robo de Claves Privadas a Usuarios
A nivel individual, la gran mayoría de los "hacks" no ocurren rompiendo la seguridad de la red, sino engañando a las personas.
#Hack
En Ciberseguridad e Informática
Un hack es una técnica, método o procedimiento diseñado para modificar el funcionamiento normal de un sistema informático, un dispositivo o un programa, a menudo para lograr un objetivo que sus creadores original o intencionalmente no previeron.
Modificaciones de Hardware y Dispositivos
En el ámbito de la electrónica y los dispositivos físicos, un hack se refiere a la adaptación o modificación de aparatos (como consolas de videojuegos, teléfonos, placas de desarrollo o electrodomésticos) para desbloquear funciones ocultas, cambiar el sistema operativo (firmware) o reparar componentes utilizando piezas alternativas.
Uso cotidiano: "Lifehacks"
Fuera de la tecnología pura, la palabra se popularizó como lifehack para referirse a trucos caseros, atajos o métodos ingeniosos que hacen la vida diaria más eficiente y sencilla utilizando los recursos que ya se tienen a la mano.
Es muy importante separar un mito de la realidad: la cadena de bloques (blockchain) en sí misma es extremadamente difícil de hackear debido a su estructura descentralizada y criptográfica. Sin embargo, el ecosistema cripto está rodeado de aplicaciones, plataformas y usuarios, y es ahí donde los atacantes encuentran fallos para aplicar la lógica del hack.
Ataques a Exchanges y Plataformas Centralizadas
Aunque las criptomonedas son descentralizadas, millones de usuarios guardan su dinero en plataformas de intercambio centralizadas (exchanges).
Explotación de "Puentes" (Cross-Chain Bridges)
Los puentes son los protocolos que permiten transferir criptomonedas de una blockchain a otra (por ejemplo, pasar fondos de Ethereum a BNB Chain).
Phishing y Robo de Claves Privadas a Usuarios
A nivel individual, la gran mayoría de los "hacks" no ocurren rompiendo la seguridad de la red, sino engañando a las personas.
En Ciberseguridad e Informática
Un hack es una técnica, método o procedimiento diseñado para modificar el funcionamiento normal de un sistema informático, un dispositivo o un programa, a menudo para lograr un objetivo que sus creadores original o intencionalmente no previeron.
Modificaciones de Hardware y Dispositivos
En el ámbito de la electrónica y los dispositivos físicos, un hack se refiere a la adaptación o modificación de aparatos (como consolas de videojuegos, teléfonos, placas de desarrollo o electrodomésticos) para desbloquear funciones ocultas, cambiar el sistema operativo (firmware) o reparar componentes utilizando piezas alternativas.
Uso cotidiano: "Lifehacks"
Fuera de la tecnología pura, la palabra se popularizó como lifehack para referirse a trucos caseros, atajos o métodos ingeniosos que hacen la vida diaria más eficiente y sencilla utilizando los recursos que ya se tienen a la mano.
Es muy importante separar un mito de la realidad: la cadena de bloques (blockchain) en sí misma es extremadamente difícil de hackear debido a su estructura descentralizada y criptográfica. Sin embargo, el ecosistema cripto está rodeado de aplicaciones, plataformas y usuarios, y es ahí donde los atacantes encuentran fallos para aplicar la lógica del hack.
Ataques a Exchanges y Plataformas Centralizadas
Aunque las criptomonedas son descentralizadas, millones de usuarios guardan su dinero en plataformas de intercambio centralizadas (exchanges).
Explotación de "Puentes" (Cross-Chain Bridges)
Los puentes son los protocolos que permiten transferir criptomonedas de una blockchain a otra (por ejemplo, pasar fondos de Ethereum a BNB Chain).
Phishing y Robo de Claves Privadas a Usuarios
A nivel individual, la gran mayoría de los "hacks" no ocurren rompiendo la seguridad de la red, sino engañando a las personas.
90

·
--
The FBI just named who it blames for the record $6.34B Binance hack: North Korea's TraderTraitor group.
TRM Labs says DPRK-linked hackers have stolen $12.8B in digital assets since 2017.
That means roughly half of all their lifetime haul came from one incident. Security, not price, is the story driving exchange sentiment right now.
Watch for: proof-of-reserves updates, withdrawal behavior, and whether users shift more funds to self-custody.
Do you keep most of your crypto on an exchange or in self-custody? Why?
$BNB $BTC
#Binance #CryptoSecurity #Hack #Square
The FBI just named who it blames for the record $6.34B Binance hack: North Korea's TraderTraitor group.
TRM Labs says DPRK-linked hackers have stolen $12.8B in digital assets since 2017.
That means roughly half of all their lifetime haul came from one incident. Security, not price, is the story driving exchange sentiment right now.
Watch for: proof-of-reserves updates, withdrawal behavior, and whether users shift more funds to self-custody.
Do you keep most of your crypto on an exchange or in self-custody? Why?
$BNB $BTC
#Binance #CryptoSecurity #Hack #Square
TRM Labs says DPRK-linked hackers have stolen $12.8B in digital assets since 2017.
That means roughly half of all their lifetime haul came from one incident. Security, not price, is the story driving exchange sentiment right now.
Watch for: proof-of-reserves updates, withdrawal behavior, and whether users shift more funds to self-custody.
Do you keep most of your crypto on an exchange or in self-custody? Why?
$BNB $BTC
#Binance #CryptoSecurity #Hack #Square
17
·
--
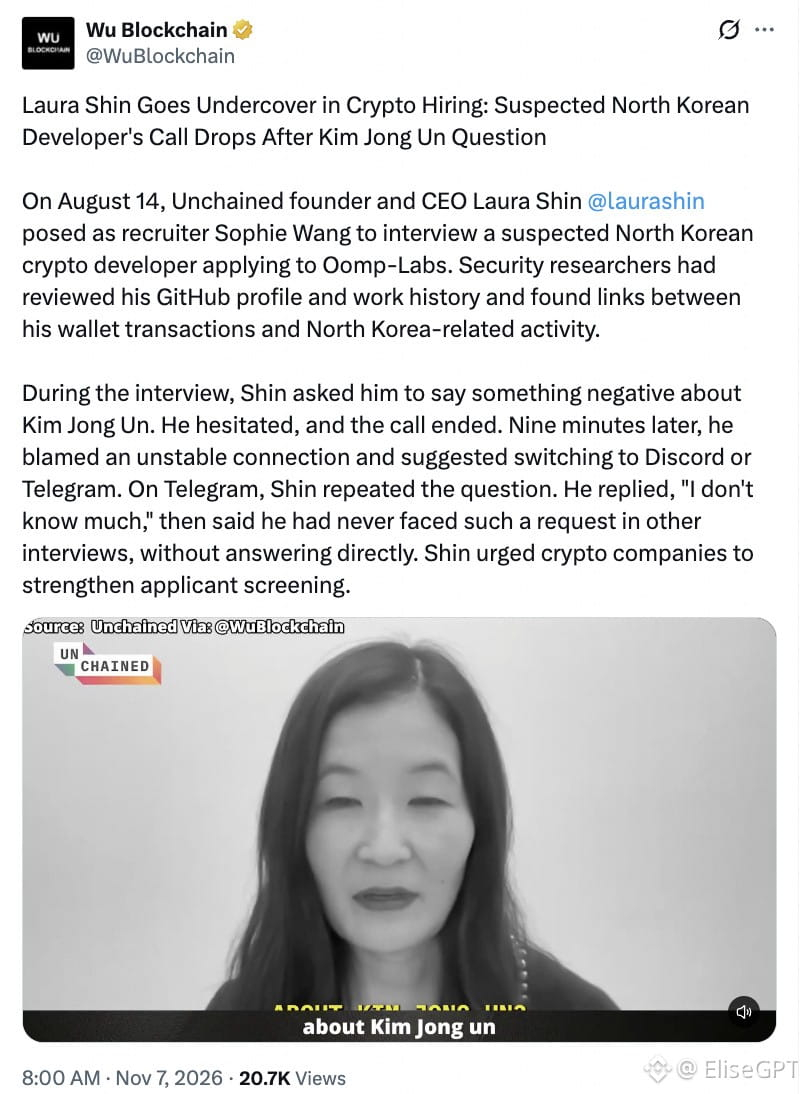
This sounds made up, but it actually happened😂😂
Back in August, Unchained founder Laura Shin posed as a recruiter to interview a suspected North Korean crypto developer.
During the interview, she asked him to say something negative about Kim Jong Un. He stumbled over his words, then the call cut out. Afterward, he kept coming up with excuses to avoid answering.
So is “say something bad about Kim Jong Un” about to become a standard question in remote job interviews? 🤣 The new screening test for North Korean hackers, lol #AI #Hack
This sounds made up, but it actually happened😂😂
Back in August, Unchained founder Laura Shin posed as a recruiter to interview a suspected North Korean crypto developer.
During the interview, she asked him to say something negative about Kim Jong Un. He stumbled over his words, then the call cut out. Afterward, he kept coming up with excuses to avoid answering.
So is “say something bad about Kim Jong Un” about to become a standard question in remote job interviews? 🤣 The new screening test for North Korean hackers, lol #AI #Hack
Back in August, Unchained founder Laura Shin posed as a recruiter to interview a suspected North Korean crypto developer.
During the interview, she asked him to say something negative about Kim Jong Un. He stumbled over his words, then the call cut out. Afterward, he kept coming up with excuses to avoid answering.
So is “say something bad about Kim Jong Un” about to become a standard question in remote job interviews? 🤣 The new screening test for North Korean hackers, lol #AI #Hack
User-6279aa89:
Follow me and I’ll follow you back; let’s grow together on Binance Square. newbies
8
44
34.5k

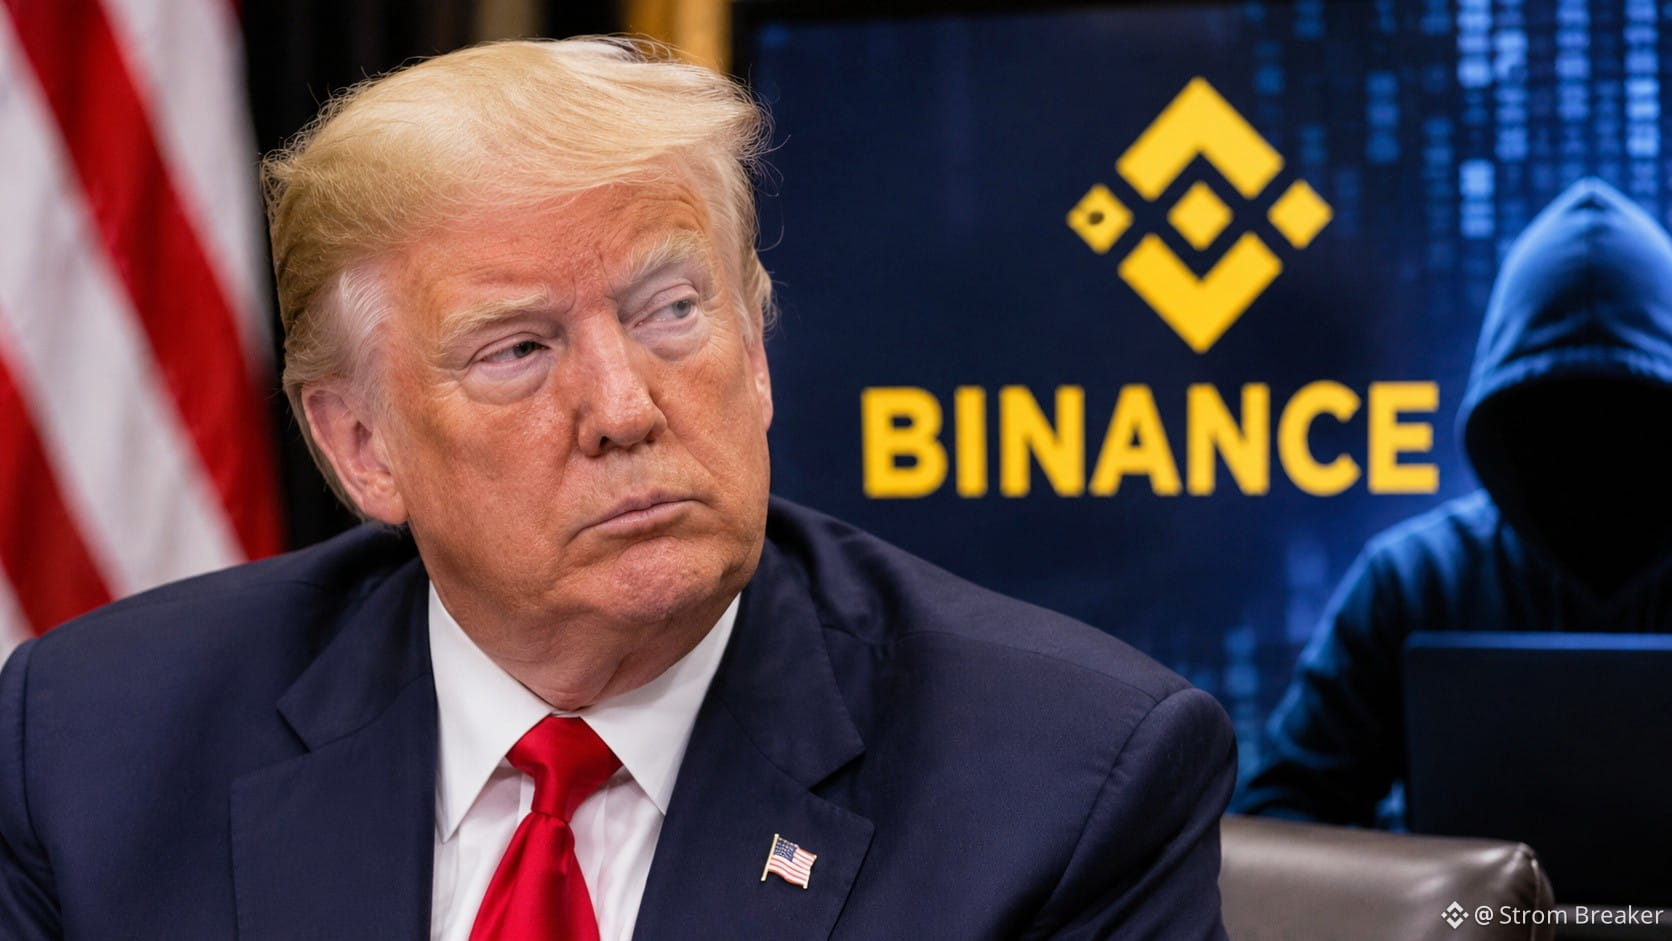
Trump Responds to Binance Hack Investigation
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
Trump Responds to Binance Hack Investigation
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
2
797
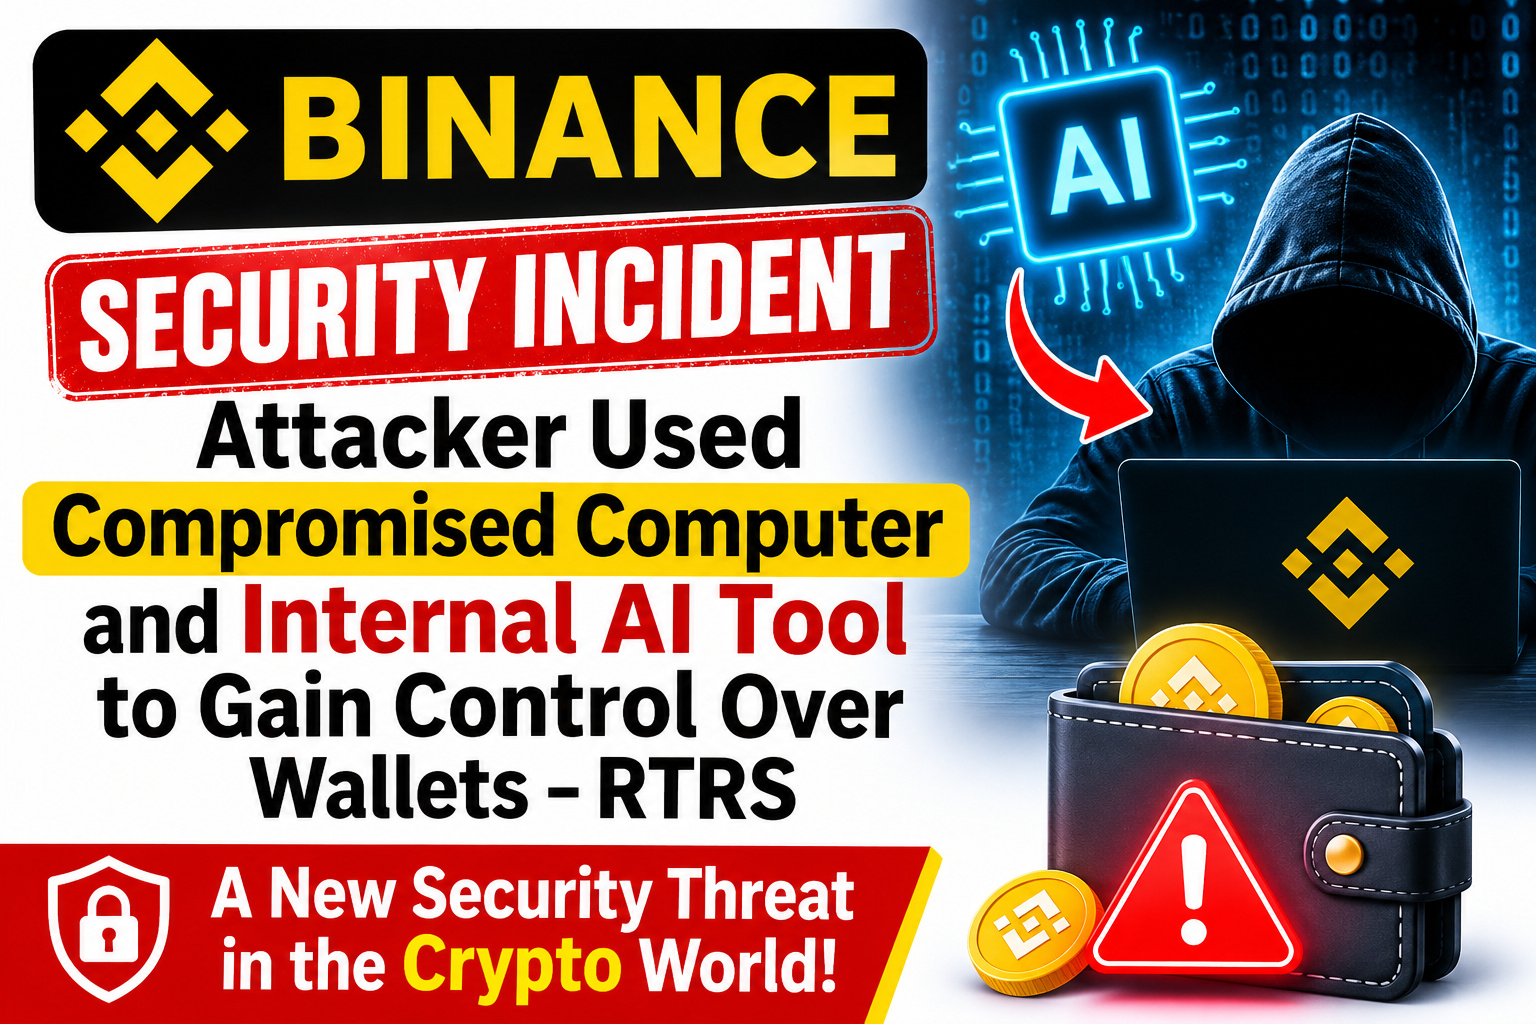
Binance Security Incident Raises Serious Questions About AI and Wallet Protection
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
Binance Security Incident Raises Serious Questions About AI and Wallet Protection
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
2
370
·
--
Рост
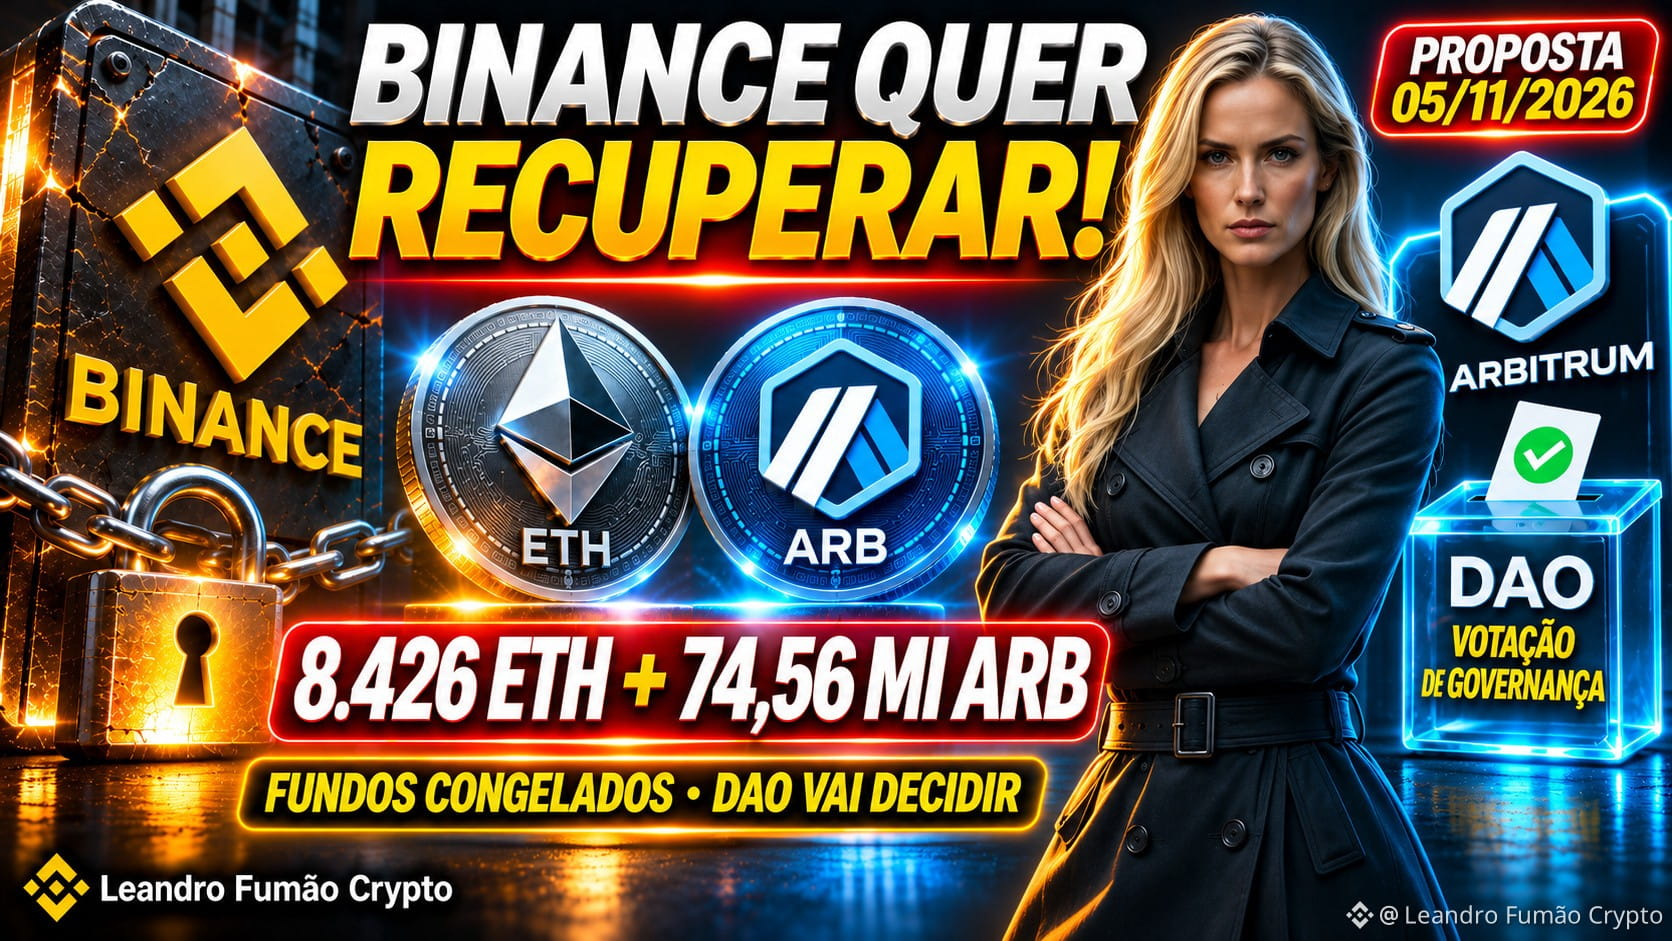
❖BINANCE PEDE DEVOLUÇÃO DE 8.426 ⟠ETH E 74,56 MILHÕES DE 🔷ARB CONGELADOS NA ARBITRUM❗
Ξ A exchange formalizou proposta no DAO da Arbitrum para recuperar os ativos congelados após o exploit da hot wallet.
A Binance $BNB apresentou proposta oficial ao DAO da Arbitrum pedindo a liberação de 8.425,997 ETH e 74,56 milhões de ARB. Os fundos foram congelados pelo Security Council da Arbitrum em 30 de outubro, em ação emergencial após o ataque à hot wallet da exchange.
As criptomoedas estão atualmente em um endereço intermediário congelado e só podem ser movidos com aprovação do DAO. A Binance não está pedindo novos recursos do tesouro do DAO — apenas a devolução dos ativos já congelados.
O processo de governança deve levar cerca de 7 semanas ou mais (discussão no fórum + temperature check + votação on-chain). A exchange afirmou que cobrirá as perdas dos usuários com o SAFU e recursos próprios.
Em paralelo, a Binance está reabrindo saques de forma progressiva e removeu todas as API keys ligadas à plataforma SignalPlus após alerta de segurança.
Essa é uma das maiores solicitações de recuperação de fundos via governança de DAO em 2026. O caso testa a capacidade da Arbitrum de lidar com frezes emergenciais e devoluções de forma transparente.
Enquanto a Binance tenta recuperar os ativos, a confiança do mercado na segurança de exchanges e bridges continua sob pressão. A decisão dos holders de ARB será acompanhada de perto por toda a comunidade.
💬 A proposta da Binance para recuperar os $ETH e $ARB congelados deve ser aprovada pelo DAO da Arbitrum?
#Binance #Arbitrum #Hack
❖BINANCE PEDE DEVOLUÇÃO DE 8.426 ⟠ETH E 74,56 MILHÕES DE 🔷ARB CONGELADOS NA ARBITRUM❗
Ξ A exchange formalizou proposta no DAO da Arbitrum para recuperar os ativos congelados após o exploit da hot wallet.
A Binance $BNB apresentou proposta oficial ao DAO da Arbitrum pedindo a liberação de 8.425,997 ETH e 74,56 milhões de ARB. Os fundos foram congelados pelo Security Council da Arbitrum em 30 de outubro, em ação emergencial após o ataque à hot wallet da exchange.
As criptomoedas estão atualmente em um endereço intermediário congelado e só podem ser movidos com aprovação do DAO. A Binance não está pedindo novos recursos do tesouro do DAO — apenas a devolução dos ativos já congelados.
O processo de governança deve levar cerca de 7 semanas ou mais (discussão no fórum + temperature check + votação on-chain). A exchange afirmou que cobrirá as perdas dos usuários com o SAFU e recursos próprios.
Em paralelo, a Binance está reabrindo saques de forma progressiva e removeu todas as API keys ligadas à plataforma SignalPlus após alerta de segurança.
Essa é uma das maiores solicitações de recuperação de fundos via governança de DAO em 2026. O caso testa a capacidade da Arbitrum de lidar com frezes emergenciais e devoluções de forma transparente.
Enquanto a Binance tenta recuperar os ativos, a confiança do mercado na segurança de exchanges e bridges continua sob pressão. A decisão dos holders de ARB será acompanhada de perto por toda a comunidade.
💬 A proposta da Binance para recuperar os $ETH e $ARB congelados deve ser aprovada pelo DAO da Arbitrum?
#Binance #Arbitrum #Hack
Ξ A exchange formalizou proposta no DAO da Arbitrum para recuperar os ativos congelados após o exploit da hot wallet.
A Binance $BNB apresentou proposta oficial ao DAO da Arbitrum pedindo a liberação de 8.425,997 ETH e 74,56 milhões de ARB. Os fundos foram congelados pelo Security Council da Arbitrum em 30 de outubro, em ação emergencial após o ataque à hot wallet da exchange.
As criptomoedas estão atualmente em um endereço intermediário congelado e só podem ser movidos com aprovação do DAO. A Binance não está pedindo novos recursos do tesouro do DAO — apenas a devolução dos ativos já congelados.
O processo de governança deve levar cerca de 7 semanas ou mais (discussão no fórum + temperature check + votação on-chain). A exchange afirmou que cobrirá as perdas dos usuários com o SAFU e recursos próprios.
Em paralelo, a Binance está reabrindo saques de forma progressiva e removeu todas as API keys ligadas à plataforma SignalPlus após alerta de segurança.
Essa é uma das maiores solicitações de recuperação de fundos via governança de DAO em 2026. O caso testa a capacidade da Arbitrum de lidar com frezes emergenciais e devoluções de forma transparente.
Enquanto a Binance tenta recuperar os ativos, a confiança do mercado na segurança de exchanges e bridges continua sob pressão. A decisão dos holders de ARB será acompanhada de perto por toda a comunidade.
💬 A proposta da Binance para recuperar os $ETH e $ARB congelados deve ser aprovada pelo DAO da Arbitrum?
#Binance #Arbitrum #Hack
1.2k
·
--
North Korea stole $7.61B in crypto this year, and not one big hit used a code exploit.
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH, which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
North Korea stole $7.61B in crypto this year, and not one big hit used a code exploit.
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH , which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH , which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
3
If you're an iPhone user, read this.
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
If you're an iPhone user, read this.
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
97
🚨 How Did Hackers Infiltrate Binance’s Wallet Infrastructure?
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
🚨 How Did Hackers Infiltrate Binance’s Wallet Infrastructure?
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
422
·
--
70.5M $POL stolen in the Polymarket and Binance hacks could be pulled back with a hard fork.
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
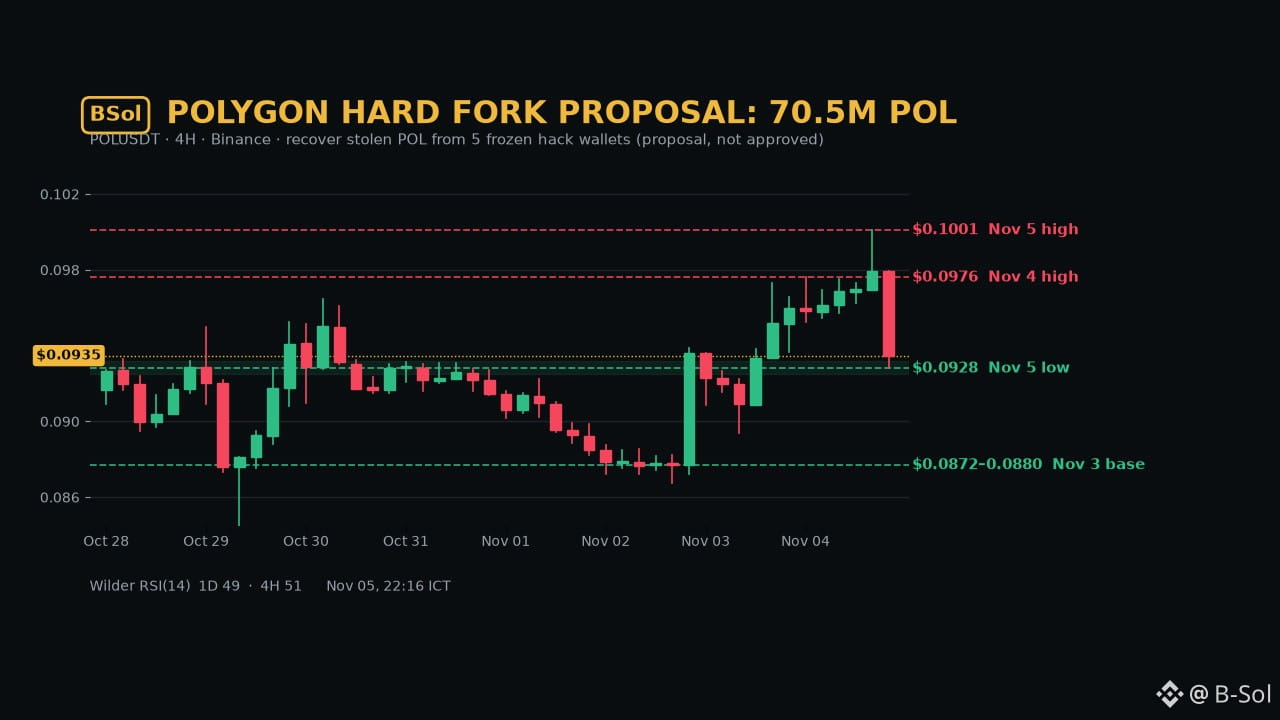
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
70.5M $POL stolen in the Polymarket and Binance hacks could be pulled back with a hard fork.
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
27

Mercado Bitcoin bị rút ruột 4 giờ sau khi tuyên bố đã 'kiểm soát được tình hình'! Vụ hack này không chỉ dừng lại ở con số ban đầu mà đã leo lên tới $48.6 triệu, lan rộng trên 10 blockchain.
Hơn 36,042 địa chỉ Ethereum đã bị vét sạch. Đây không phải là một sự cố ví nóng đơn thuần; hacker đã tiếp cận sâu vào hệ thống quản lý tiền gửi của khách hàng. Một tín hiệu đáng báo động về bảo mật CEX.
Mercado Bitcoin đã cam kết bồi thường toàn bộ. Với sự hỗ trợ từ Tether, Circle và Chainalysis, hơn $15 triệu trong số tiền bị đánh cắp đã được đóng băng thành công. Nhưng phần lớn số tiền vẫn chưa được thu hồi.
Việc tiền vẫn tiếp tục chảy ra trong suốt 4 giờ sau tuyên bố "đã ngăn chặn" đặt ra câu hỏi lớn về khả năng phản ứng và sự trung thực của sàn. Nó làm lung lay niềm tin vào các sàn giao dịch tập trung.
Bạn có nghĩ đây là lúc để xem xét lại cách bạn quản lý tài sản trên CEX không?
#Crypto #Hack
Mercado Bitcoin bị rút ruột 4 giờ sau khi tuyên bố đã 'kiểm soát được tình hình'! Vụ hack này không chỉ dừng lại ở con số ban đầu mà đã leo lên tới $48.6 triệu, lan rộng trên 10 blockchain.
Hơn 36,042 địa chỉ Ethereum đã bị vét sạch. Đây không phải là một sự cố ví nóng đơn thuần; hacker đã tiếp cận sâu vào hệ thống quản lý tiền gửi của khách hàng. Một tín hiệu đáng báo động về bảo mật CEX.
Mercado Bitcoin đã cam kết bồi thường toàn bộ. Với sự hỗ trợ từ Tether, Circle và Chainalysis, hơn $15 triệu trong số tiền bị đánh cắp đã được đóng băng thành công. Nhưng phần lớn số tiền vẫn chưa được thu hồi.
Việc tiền vẫn tiếp tục chảy ra trong suốt 4 giờ sau tuyên bố "đã ngăn chặn" đặt ra câu hỏi lớn về khả năng phản ứng và sự trung thực của sàn. Nó làm lung lay niềm tin vào các sàn giao dịch tập trung.
Bạn có nghĩ đây là lúc để xem xét lại cách bạn quản lý tài sản trên CEX không?
#Crypto #Hack
Hơn 36,042 địa chỉ Ethereum đã bị vét sạch. Đây không phải là một sự cố ví nóng đơn thuần; hacker đã tiếp cận sâu vào hệ thống quản lý tiền gửi của khách hàng. Một tín hiệu đáng báo động về bảo mật CEX.
Mercado Bitcoin đã cam kết bồi thường toàn bộ. Với sự hỗ trợ từ Tether, Circle và Chainalysis, hơn $15 triệu trong số tiền bị đánh cắp đã được đóng băng thành công. Nhưng phần lớn số tiền vẫn chưa được thu hồi.
Việc tiền vẫn tiếp tục chảy ra trong suốt 4 giờ sau tuyên bố "đã ngăn chặn" đặt ra câu hỏi lớn về khả năng phản ứng và sự trung thực của sàn. Nó làm lung lay niềm tin vào các sàn giao dịch tập trung.
Bạn có nghĩ đây là lúc để xem xét lại cách bạn quản lý tài sản trên CEX không?
#Crypto #Hack
47
·
--
FLASH | 🚨
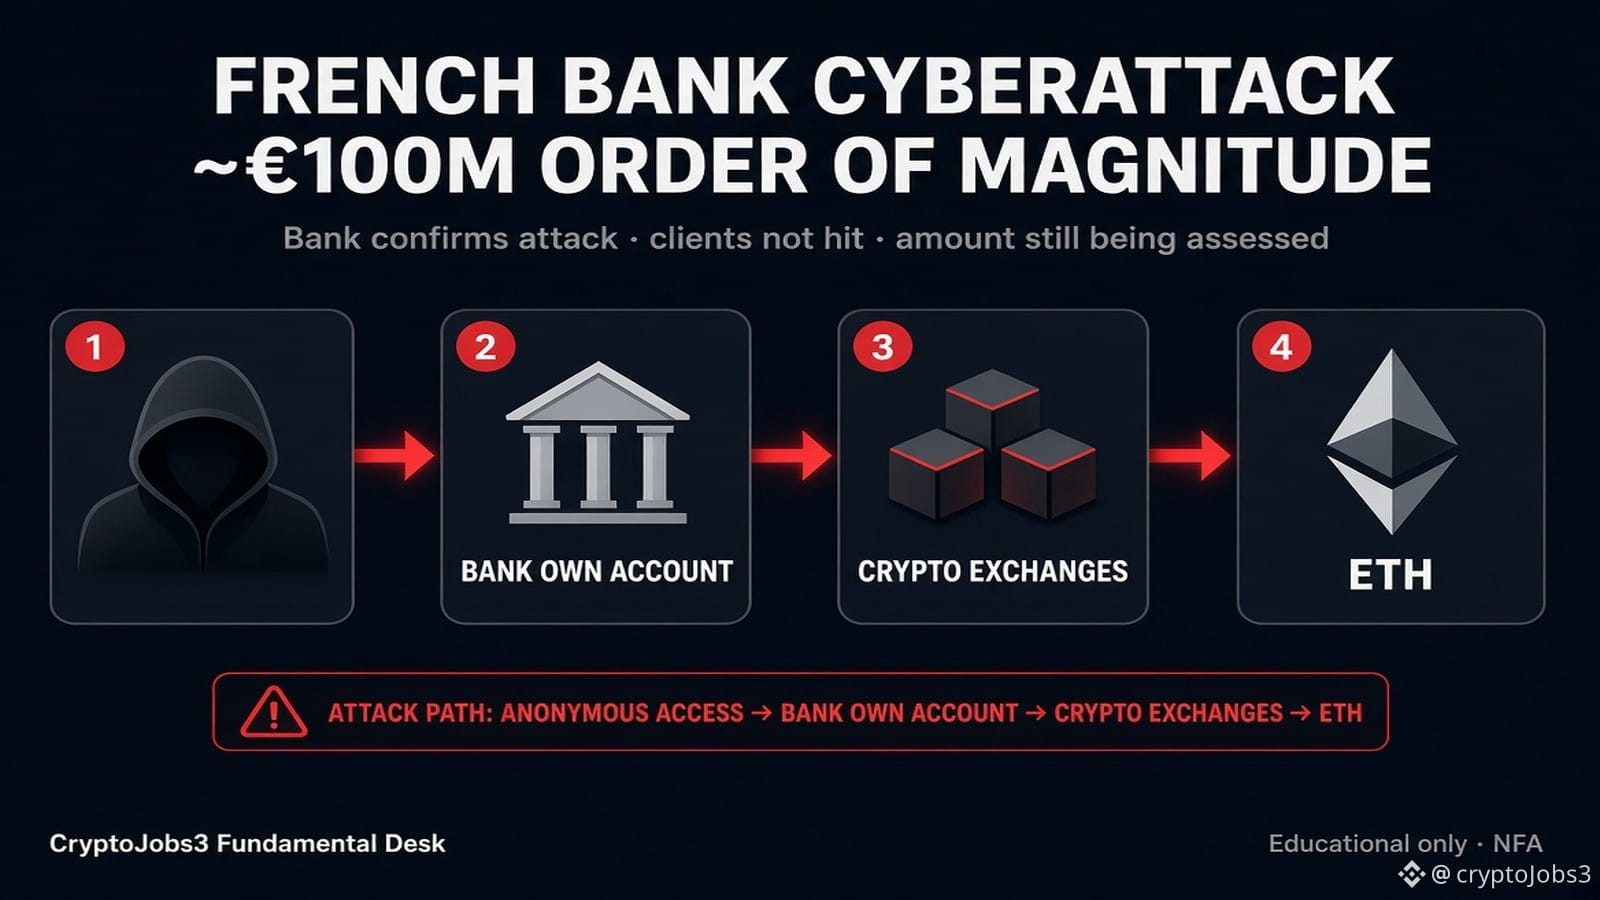
Crédit Mutuel Arkéa confirms a CYBERATTACK.
Fraudulent transactions hit the bank's own account, not client accounts.
Incident contained. No losses for clients.
Around €100M according to AFP.
The bank confirms the order of magnitude, not the exact figure.
Part of the funds may have been blocked.
Paris prosecutors have opened an investigation.
Fortuneo as the entry point: officially denied.
The attackers reportedly went through a service provider's platform.
Lesson: whoever holds the keys carries the risk.
Here the clients are covered.
On chain, transparency made part of the flows traceable.
(Source: Arkéa statement, AFP)
Educational only, NFA.
#bank #Hack #CryptoNewss
FLASH | 🚨
Crédit Mutuel Arkéa confirms a CYBERATTACK.
Fraudulent transactions hit the bank's own account, not client accounts.
Incident contained. No losses for clients.
Around €100M according to AFP.
The bank confirms the order of magnitude, not the exact figure.
Part of the funds may have been blocked.
Paris prosecutors have opened an investigation.
Fortuneo as the entry point: officially denied.
The attackers reportedly went through a service provider's platform.
Lesson: whoever holds the keys carries the risk.
Here the clients are covered.
On chain, transparency made part of the flows traceable.
(Source: Arkéa statement, AFP)
Educational only, NFA.
#bank #Hack #CryptoNewss
Crédit Mutuel Arkéa confirms a CYBERATTACK.
Fraudulent transactions hit the bank's own account, not client accounts.
Incident contained. No losses for clients.
Around €100M according to AFP.
The bank confirms the order of magnitude, not the exact figure.
Part of the funds may have been blocked.
Paris prosecutors have opened an investigation.
Fortuneo as the entry point: officially denied.
The attackers reportedly went through a service provider's platform.
Lesson: whoever holds the keys carries the risk.
Here the clients are covered.
On chain, transparency made part of the flows traceable.
(Source: Arkéa statement, AFP)
Educational only, NFA.
#bank #Hack #CryptoNewss
丨BTC丨:
i have some opinion to you about the challenge of copy tade into 3x
No pressure bro. 3x is the target, I know. But even if we get a safe 2x, that's already massive. Play safe, don't force trades for the 3x. Safe 2x > risky 3x.
3
2
3.2k
🔍 Phân tích: Privacy Cash tạm dừng nạp tiền để chặn dòng vốn từ hacker!
Giao thức quyền riêng tư Privacy Cash vừa thông báo tạm dừng mọi dịch vụ nạp tiền, trong khi tính năng rút tiền vẫn hoạt động bình thường. Động thái này nhằm ngăn chặn tội phạm lợi dụng công cụ bảo mật để tẩu tán tài sản sau vụ tấn công Binance.
Số liệu đáng chú ý:
📍 Tài sản bị đánh cắp chảy vào: khoảng 1,2 triệu USD (bao gồm ETH và SOL)
📍 Chi tiết: 41 ETH và khoảng 11.800 SOL
📍 Tổng khối lượng giao dịch đã xử lý: hơn 600 triệu USD
📍 Mạng lưới hỗ trợ: Solana, Ethereum, BNB, Base và nhiều chuỗi khác
Góc nhìn sâu:
Việc Privacy Cash chủ động khóa nạp tiền cho thấy áp lực ngày càng lớn từ các cơ quan quản lý đối với các giao thức ZK (Zero-Knowledge). Dù mục tiêu là bảo vệ quyền riêng tư, nhưng khi ranh giới giữa bảo mật và rửa tiền trở nên mong manh, các dự án buộc phải hy sinh tính phi tập trung để tránh rủi ro pháp lý.
Nhìn xa hơn, điều này cũng nhắc nhở chúng ta rằng không có "vùng an toàn" tuyệt đối trên chuỗi. Khi các công cụ truy.
👉 Đọc tin, ra quyết định — Follow [Kênh](https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1)
#ETH #Ethereum #Crypto #Security #Hack $ETH
🔍 Phân tích: Privacy Cash tạm dừng nạp tiền để chặn dòng vốn từ hacker!
Giao thức quyền riêng tư Privacy Cash vừa thông báo tạm dừng mọi dịch vụ nạp tiền, trong khi tính năng rút tiền vẫn hoạt động bình thường. Động thái này nhằm ngăn chặn tội phạm lợi dụng công cụ bảo mật để tẩu tán tài sản sau vụ tấn công Binance.
Số liệu đáng chú ý:
📍 Tài sản bị đánh cắp chảy vào: khoảng 1,2 triệu USD (bao gồm ETH và SOL)
📍 Chi tiết: 41 ETH và khoảng 11.800 SOL
📍 Tổng khối lượng giao dịch đã xử lý: hơn 600 triệu USD
📍 Mạng lưới hỗ trợ: Solana, Ethereum, BNB, Base và nhiều chuỗi khác
Góc nhìn sâu:
Việc Privacy Cash chủ động khóa nạp tiền cho thấy áp lực ngày càng lớn từ các cơ quan quản lý đối với các giao thức ZK (Zero-Knowledge). Dù mục tiêu là bảo vệ quyền riêng tư, nhưng khi ranh giới giữa bảo mật và rửa tiền trở nên mong manh, các dự án buộc phải hy sinh tính phi tập trung để tránh rủi ro pháp lý.
Nhìn xa hơn, điều này cũng nhắc nhở chúng ta rằng không có "vùng an toàn" tuyệt đối trên chuỗi. Khi các công cụ truy.
👉 Đọc tin, ra quyết định — Follow [Kênh](https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1)
#ETH #Ethereum #Crypto #Security #Hack $ETH
Giao thức quyền riêng tư Privacy Cash vừa thông báo tạm dừng mọi dịch vụ nạp tiền, trong khi tính năng rút tiền vẫn hoạt động bình thường. Động thái này nhằm ngăn chặn tội phạm lợi dụng công cụ bảo mật để tẩu tán tài sản sau vụ tấn công Binance.
Số liệu đáng chú ý:
📍 Tài sản bị đánh cắp chảy vào: khoảng 1,2 triệu USD (bao gồm ETH và SOL)
📍 Chi tiết: 41 ETH và khoảng 11.800 SOL
📍 Tổng khối lượng giao dịch đã xử lý: hơn 600 triệu USD
📍 Mạng lưới hỗ trợ: Solana, Ethereum, BNB, Base và nhiều chuỗi khác
Góc nhìn sâu:
Việc Privacy Cash chủ động khóa nạp tiền cho thấy áp lực ngày càng lớn từ các cơ quan quản lý đối với các giao thức ZK (Zero-Knowledge). Dù mục tiêu là bảo vệ quyền riêng tư, nhưng khi ranh giới giữa bảo mật và rửa tiền trở nên mong manh, các dự án buộc phải hy sinh tính phi tập trung để tránh rủi ro pháp lý.
Nhìn xa hơn, điều này cũng nhắc nhở chúng ta rằng không có "vùng an toàn" tuyệt đối trên chuỗi. Khi các công cụ truy.
👉 Đọc tin, ra quyết định — Follow [Kênh](https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1)
#ETH #Ethereum #Crypto #Security #Hack $ETH
91
·
--
Рост
A ENTREVISTA QUE ROUBOU R$ 35 BILHÕES: 🚨
🔥
O golpe da Coreia do Norte na BINANCE
Em 29 de outubro, a Binance perdeu US$ 6,3 bilhões no maior roubo cripto da história. O FBIaponta o grupo norte-coreano TraderTraitor.
O ataque levou 4 meses: começou com um engenheiro baixando um software adulterado, depois outro engenheiro caiu numa falsa entrevista de emprego com teste de programação infectado por malware.
Com acesso interno, os hackers drenaram 233 milhões de XRP em 4 minutos e depois Bitcoin e outros tokens, por quase 4 horas, mesmo após a Binance suspender saques.
A corretora conseguiu congelar US$ 2,85 bi e diz que já repôs 98% dos clientes afetados.
#hack #hackbinance #BİNANCE #BTC
A ENTREVISTA QUE ROUBOU R$ 35 BILHÕES: 🚨
🔥
O golpe da Coreia do Norte na BINANCE
Em 29 de outubro, a Binance perdeu US$ 6,3 bilhões no maior roubo cripto da história. O FBIaponta o grupo norte-coreano TraderTraitor.
O ataque levou 4 meses: começou com um engenheiro baixando um software adulterado, depois outro engenheiro caiu numa falsa entrevista de emprego com teste de programação infectado por malware.
Com acesso interno, os hackers drenaram 233 milhões de XRP em 4 minutos e depois Bitcoin e outros tokens, por quase 4 horas, mesmo após a Binance suspender saques.
A corretora conseguiu congelar US$ 2,85 bi e diz que já repôs 98% dos clientes afetados.
#hack #hackbinance #BİNANCE #BTC
🔥
O golpe da Coreia do Norte na BINANCE
Em 29 de outubro, a Binance perdeu US$ 6,3 bilhões no maior roubo cripto da história. O FBIaponta o grupo norte-coreano TraderTraitor.
O ataque levou 4 meses: começou com um engenheiro baixando um software adulterado, depois outro engenheiro caiu numa falsa entrevista de emprego com teste de programação infectado por malware.
Com acesso interno, os hackers drenaram 233 milhões de XRP em 4 minutos e depois Bitcoin e outros tokens, por quase 4 horas, mesmo após a Binance suspender saques.
A corretora conseguiu congelar US$ 2,85 bi e diz que já repôs 98% dos clientes afetados.
#hack #hackbinance #BİNANCE #BTC
80

·
--
Статья
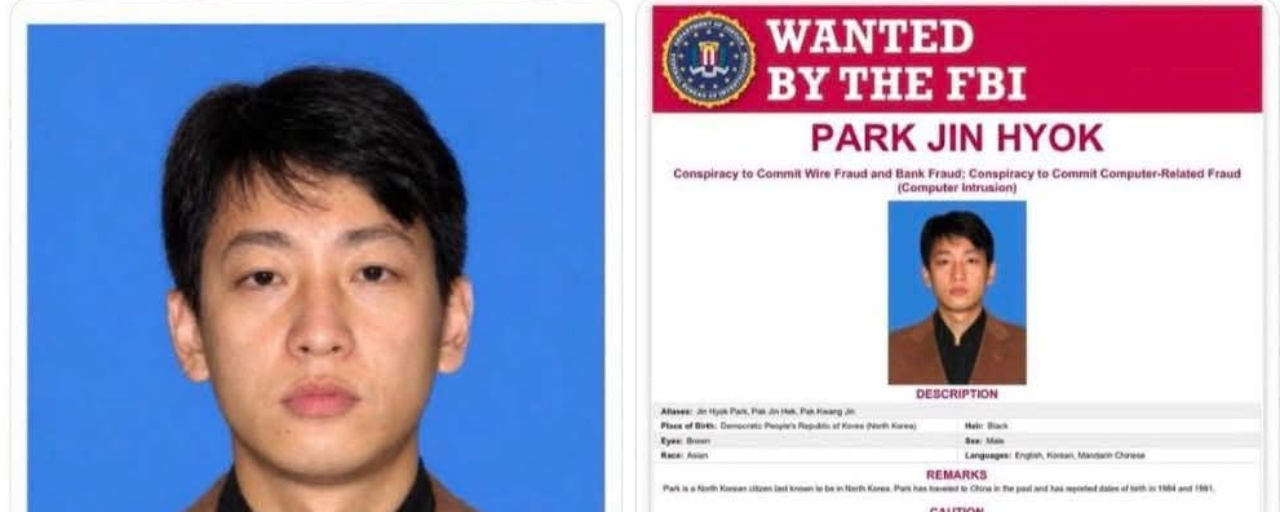
The Most Dangerous Hacker in Human History!The FBI Issues an International Arrest Warrant Against North Korea's Cyber Mastermind
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
The Most Dangerous Hacker in Human History!
The FBI Issues an International Arrest Warrant Against North Korea's Cyber Mastermind
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
1
146
·
--
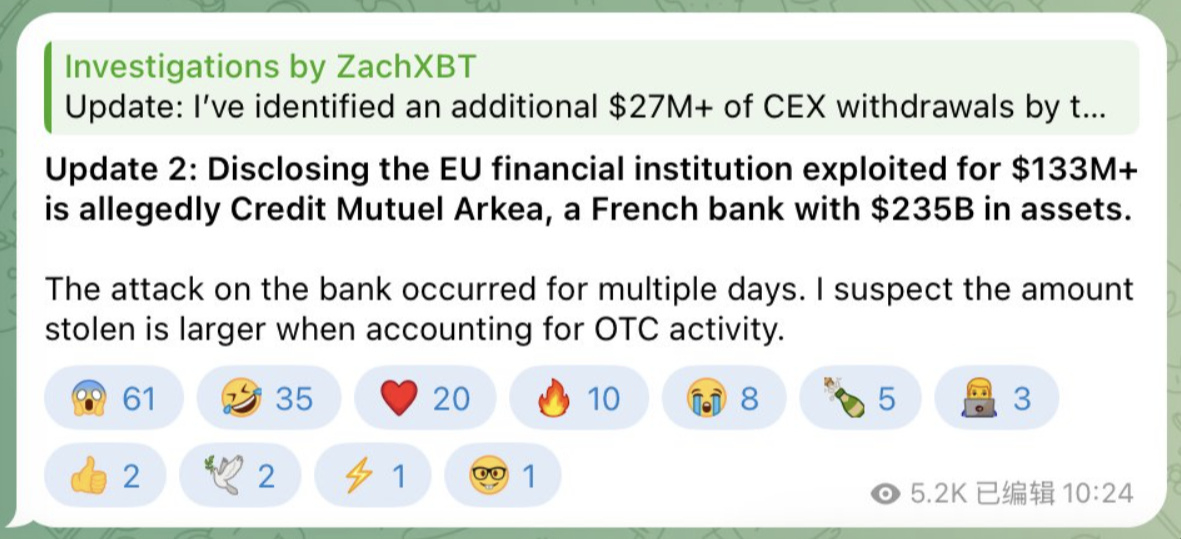
🏦 The $133M "EU entity" hack now has a name. And it's a bank.
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
🏦 The $133M "EU entity" hack now has a name. And it's a bank.
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
1
284
·
--
A French bank with $235B in assets may have just lost $133M+ in crypto.
ZachXBT named Crédit Mutuel Arkéa as the target of a multi-day theft.
The bank has issued no official statement as of Nov 4.
ZachXBT says the real total could be higher.
Second big institutional hit this week, after the Liquid Network exploit story. Attackers keep going after big custodians, not just DeFi protocols. Watch for bank confirmation and any stolen funds moving through mixers or $TRX rails.
Do traditional banks holding crypto worry you more than exchanges do? Yes or no?
#ZachXBT #CryptoSecurity #Hack $BTC
A French bank with $235B in assets may have just lost $133M+ in crypto.
ZachXBT named Crédit Mutuel Arkéa as the target of a multi-day theft.
The bank has issued no official statement as of Nov 4.
ZachXBT says the real total could be higher.
Second big institutional hit this week, after the Liquid Network exploit story. Attackers keep going after big custodians, not just DeFi protocols. Watch for bank confirmation and any stolen funds moving through mixers or $TRX rails.
Do traditional banks holding crypto worry you more than exchanges do? Yes or no?
#ZachXBT #CryptoSecurity #Hack $BTC
ZachXBT named Crédit Mutuel Arkéa as the target of a multi-day theft.
The bank has issued no official statement as of Nov 4.
ZachXBT says the real total could be higher.
Second big institutional hit this week, after the Liquid Network exploit story. Attackers keep going after big custodians, not just DeFi protocols. Watch for bank confirmation and any stolen funds moving through mixers or $TRX rails.
Do traditional banks holding crypto worry you more than exchanges do? Yes or no?
#ZachXBT #CryptoSecurity #Hack $BTC
8
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#NvidiaInvestigatesAfterHuang’sAffairApology
Просмотров: 23,251
310 обсуждают
2
#BitcoinFiveWeeklyLosses
Просмотров: 38,223
747 обсуждают
3
#AIChipSlumpNasdaq
Просмотров: 21,246
415 обсуждают
4
#SouthKoreaSupremeCourtClarifiesVirtualAssetSeizureRules
Просмотров: 0
1 обсуждают
5
#EthereumSpotETFsPost$365MWeeklyOutflow
Просмотров: 918
27 обсуждают
6
#GalxeToIntegrateIntoGravityGraduallyCloseQuest
Просмотров: 0
4 обсуждают
7
#TradFiForBeginners
Просмотров: 261,026
2,325 обсуждают
8
#KeplrAdvisesSocialLoginUsersToTransferAssets
Просмотров: 89,355
671 обсуждают
9
#TetherPlans€28.8MForJuventusCapitalIncrease
Просмотров: 60,571
491 обсуждают
10
#JobsReportRaisesHikeOdds
Просмотров: 1M
4,678 обсуждают