
#coldcardexploitattackerscontrol1366btc
coldcardexploitattackerscontrol1366btc
43,061 views
295 ກຳລັງສົນທະນາ
ມາແຮງ
ຫຼ້າສຸດ

·
--
Ukulahlekelwa Okubangelwe I-Coldcard Hack Kudlula $75MIwel sethi yokuqala yokuhlaselwa exhunywe engozini yesikhwama se-Coldcard esibikiwe iye yaphusha ukulahlekelwa okuphelele kwe-Bitcoin ngaphezu kuka-1,158 BTC, okulinganiselwa cishe ku-$75 million, ngokocwaningo oluvela kwaGalaxy Research. Amaza amabili okuhlasela kuthiwa athinte amakheli ezikhwama angu-2,673 phakathi kukaJulayi 30 noJulayi 31, okwenza kube esinye sezigameko ezinkulu zakamuva zokuphepha kwezikhwama ezizibambele zona.
I-Galaxy Research ibike ukuthi ukuhlasela kokuqala kukhiphe ngaphezu kuka-1,082 BTC kumakheli angu-1,195 ngaphansi kwehora elilodwa, kanti enye imikhankaso yesibili yahlasela amanye amakheli angu-1,478, yebeza amanye ama-76 BTC emahoreni ambalwa. Nakuba ukuhlasela kwesibili kuthinte izikhwama eziningi, ibhalansi evamile eyebiwe kumuntu ngamunye eyayihlukunyeziwe yayingaphansi kakhulu kunasemzuliswaneni wokuqala.
Ukulahlekelwa Okubangelwe I-Coldcard Hack Kudlula $75M
Iwel sethi yokuqala yokuhlaselwa exhunywe engozini yesikhwama se-Coldcard esibikiwe iye yaphusha ukulahlekelwa okuphelele kwe-Bitcoin ngaphezu kuka-1,158 BTC, okulinganiselwa cishe ku-$75 million, ngokocwaningo oluvela kwaGalaxy Research. Amaza amabili okuhlasela kuthiwa athinte amakheli ezikhwama angu-2,673 phakathi kukaJulayi 30 noJulayi 31, okwenza kube esinye sezigameko ezinkulu zakamuva zokuphepha kwezikhwama ezizibambele zona.
I-Galaxy Research ibike ukuthi ukuhlasela kokuqala kukhiphe ngaphezu kuka-1,082 BTC kumakheli angu-1,195 ngaphansi kwehora elilodwa, kanti enye imikhankaso yesibili yahlasela amanye amakheli angu-1,478, yebeza amanye ama-76 BTC emahoreni ambalwa. Nakuba ukuhlasela kwesibili kuthinte izikhwama eziningi, ibhalansi evamile eyebiwe kumuntu ngamunye eyayihlukunyeziwe yayingaphansi kakhulu kunasemzuliswaneni wokuqala.
I-Galaxy Research ibike ukuthi ukuhlasela kokuqala kukhiphe ngaphezu kuka-1,082 BTC kumakheli angu-1,195 ngaphansi kwehora elilodwa, kanti enye imikhankaso yesibili yahlasela amanye amakheli angu-1,478, yebeza amanye ama-76 BTC emahoreni ambalwa. Nakuba ukuhlasela kwesibili kuthinte izikhwama eziningi, ibhalansi evamile eyebiwe kumuntu ngamunye eyayihlukunyeziwe yayingaphansi kakhulu kunasemzuliswaneni wokuqala.
107
·
--
ເບິ່ງການແປ
Coldcard Hack Funds Deposited ⚠️‼️
A Coldcard wallet hack victim reported 229.72 ETH worth $445,000 deposited into Duel.comcasino after 17 BTC were swapped via THORChain. Victim requested fund freeze but platform requires police contact; legal action threatened if funds not frozen.$ETH $BTC
{future}(BTCUSDT)
{future}(ETHUSDT)
$EPIC
{future}(EPICUSDT)
#ColdcardExploitAttackersControl1366BTC
Coldcard Hack Funds Deposited ⚠️‼️
A Coldcard wallet hack victim reported 229.72 ETH worth $445,000 deposited into Duel.comcasino after 17 BTC were swapped via THORChain. Victim requested fund freeze but platform requires police contact; legal action threatened if funds not frozen.$ETH $BTC
$EPIC
#ColdcardExploitAttackersControl1366BTC
A Coldcard wallet hack victim reported 229.72 ETH worth $445,000 deposited into Duel.comcasino after 17 BTC were swapped via THORChain. Victim requested fund freeze but platform requires police contact; legal action threatened if funds not frozen.$ETH $BTC
$EPIC
#ColdcardExploitAttackersControl1366BTC
2
674
#coldcardexploitattackerscontrol1366btc
🚨 ການແຈ້ງເຕືອນຄວາມປອດໄພຂັ້ນຮຸນແຮງ: ກຳລັງຂະຫຍາຍການໂຈມຕີກັບຜູ້ໃຊ້ COLCARD 🚨
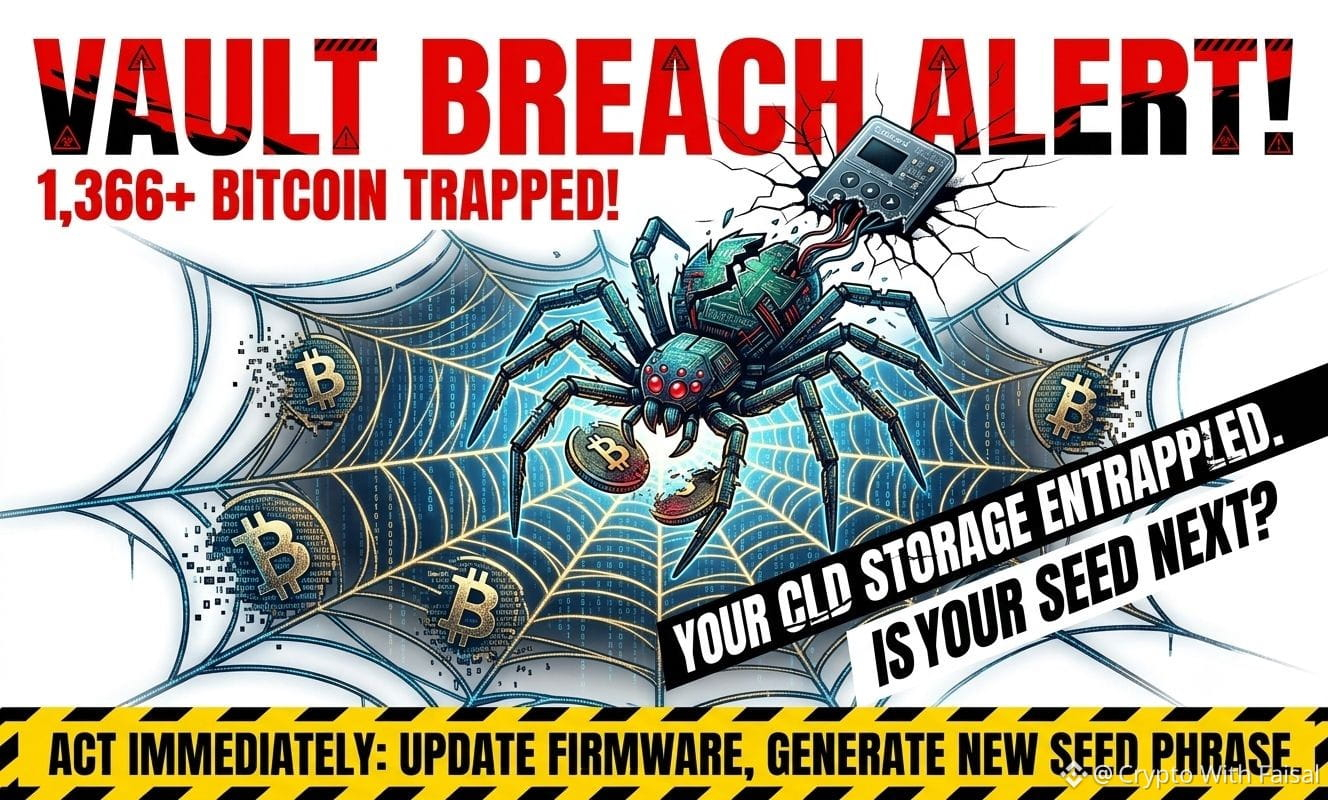
ເລືອດບໍ່ໄດ້ຢຸດ. ສິ່ງທີ່ເລີ່ມຕົ້ນດ້ວຍ 594 BTC ທີ່ຖືກລະບາຍອອກໃນເວລາບໍ່ເຖິງ 30 ນາທີມື້ວານນີ້ ຕອນນີ້ໄດ້ທະວີ—ຜູ້ໂຈມຕີພວມຄອບຄອງຫຼາຍກວ່າ 1,366.38 BTC ຢູ່ໃນການຄວບຄຸມຂອງພວກເຂົາ!
ການວິເຄາະຈາກ Galaxy Research ຢືນຢັນວ່າມີການໂຈມຕີ 3 ຄື້ນແຍກກັນທີ່ເກີດຂຶ້ນແລ້ວ. ຄຳຖາມທີ່ຈະໃຊ້ທັນທີທີ່ຜູ້ຖືຫຼຽນທຸກຄົນກຳລັງຖາມວ່າ: ການໂຈມຕີນີ້ຈົບແລ້ວ ຫຼື ຈະມີການລະເມີດເພີ່ມອີກ? ບໍ່ວ່ານີ້ແມ່ນແຮກເກີຄົນດຽວທີ່ນຳ vectors ການໂຈມຕີທີ່ອັບເກຣດມາໃຊ້ ຫຼື ຫຼາຍຜູ້ໂຈມຕີທີ່ອາໄສຊ່ອງໂຫວທີ່ເກົ່າຈາກມີນາ 2021, ຄວາມອັນຕະລາຍແມ່ນມີຈິງ.
🛡️ ແຜນປະຕິບັດດ່ວນ (ປົກປ້ອງຊັບສິນຂອງທ່ານ):
Patch ທັນທີ: ອັບເດດ firmware ຂອງອຸປະກອນເປັນຮຸ່ນລ້າສຸດທາງການທັນທີ.
ສ້າງ Seed ໃໝ່: ໂອນກອງທຶນຂອງທ່ານໄປຫາ seed phrase ໃໝ່ທີ່ສົມບູນ ແລະບໍ່ຖືກບຸກລຸກທັງສິ້ນ.
ຄອງແຄວລ່ວງໜ້າ: Cold storage ຈະປອດໄພໄດ້ພຽງແຕ່ເທົ່າກັບວິໄນຄວາມປອດໄພ—ຢ່າລໍຖ້າຈົນກະເປົ໋າຖືກລະບາຍໝົດ ເພື່ອເອົາມາປະຕິບັດ!
ຈົ່ງສົງໄສໄວ້, ຈົ່ງປອດໄພ, ແລະ ປົກປ້ອງການຖືຄອງຂອງທ່ານ! 🔒⚡
ຂໍ້ກ່າວແຈ້ງ: ບໍ່ແມ່ນຄຳແນະນຳດ້ານການເງິນ. ດຳເນີນການຄົ້ນຄວ້າຂອງທ່ານເອງສະເໝີ (DYOR).
#BTC #Coldcard #HackerAlert
$VELVET
{future}(VELVETUSDT)
$BEAT
{future}(BEATUSDT)
$BTC
{future}(BTCUSDT)
#coldcardexploitattackerscontrol1366btc
🚨 ການແຈ້ງເຕືອນຄວາມປອດໄພຂັ້ນຮຸນແຮງ: ກຳລັງຂະຫຍາຍການໂຈມຕີກັບຜູ້ໃຊ້ COLCARD 🚨
ເລືອດບໍ່ໄດ້ຢຸດ. ສິ່ງທີ່ເລີ່ມຕົ້ນດ້ວຍ 594 BTC ທີ່ຖືກລະບາຍອອກໃນເວລາບໍ່ເຖິງ 30 ນາທີມື້ວານນີ້ ຕອນນີ້ໄດ້ທະວີ—ຜູ້ໂຈມຕີພວມຄອບຄອງຫຼາຍກວ່າ 1,366.38 BTC ຢູ່ໃນການຄວບຄຸມຂອງພວກເຂົາ!
ການວິເຄາະຈາກ Galaxy Research ຢືນຢັນວ່າມີການໂຈມຕີ 3 ຄື້ນແຍກກັນທີ່ເກີດຂຶ້ນແລ້ວ. ຄຳຖາມທີ່ຈະໃຊ້ທັນທີທີ່ຜູ້ຖືຫຼຽນທຸກຄົນກຳລັງຖາມວ່າ: ການໂຈມຕີນີ້ຈົບແລ້ວ ຫຼື ຈະມີການລະເມີດເພີ່ມອີກ? ບໍ່ວ່ານີ້ແມ່ນແຮກເກີຄົນດຽວທີ່ນຳ vectors ການໂຈມຕີທີ່ອັບເກຣດມາໃຊ້ ຫຼື ຫຼາຍຜູ້ໂຈມຕີທີ່ອາໄສຊ່ອງໂຫວທີ່ເກົ່າຈາກມີນາ 2021, ຄວາມອັນຕະລາຍແມ່ນມີຈິງ.
🛡️ ແຜນປະຕິບັດດ່ວນ (ປົກປ້ອງຊັບສິນຂອງທ່ານ):
Patch ທັນທີ: ອັບເດດ firmware ຂອງອຸປະກອນເປັນຮຸ່ນລ້າສຸດທາງການທັນທີ.
ສ້າງ Seed ໃໝ່: ໂອນກອງທຶນຂອງທ່ານໄປຫາ seed phrase ໃໝ່ທີ່ສົມບູນ ແລະບໍ່ຖືກບຸກລຸກທັງສິ້ນ.
ຄອງແຄວລ່ວງໜ້າ: Cold storage ຈະປອດໄພໄດ້ພຽງແຕ່ເທົ່າກັບວິໄນຄວາມປອດໄພ—ຢ່າລໍຖ້າຈົນກະເປົ໋າຖືກລະບາຍໝົດ ເພື່ອເອົາມາປະຕິບັດ!
ຈົ່ງສົງໄສໄວ້, ຈົ່ງປອດໄພ, ແລະ ປົກປ້ອງການຖືຄອງຂອງທ່ານ! 🔒⚡
ຂໍ້ກ່າວແຈ້ງ: ບໍ່ແມ່ນຄຳແນະນຳດ້ານການເງິນ. ດຳເນີນການຄົ້ນຄວ້າຂອງທ່ານເອງສະເໝີ (DYOR).
#BTC #Coldcard #HackerAlert
$VELVET
$BEAT
$BTC
🚨 ການແຈ້ງເຕືອນຄວາມປອດໄພຂັ້ນຮຸນແຮງ: ກຳລັງຂະຫຍາຍການໂຈມຕີກັບຜູ້ໃຊ້ COLCARD 🚨
ເລືອດບໍ່ໄດ້ຢຸດ. ສິ່ງທີ່ເລີ່ມຕົ້ນດ້ວຍ 594 BTC ທີ່ຖືກລະບາຍອອກໃນເວລາບໍ່ເຖິງ 30 ນາທີມື້ວານນີ້ ຕອນນີ້ໄດ້ທະວີ—ຜູ້ໂຈມຕີພວມຄອບຄອງຫຼາຍກວ່າ 1,366.38 BTC ຢູ່ໃນການຄວບຄຸມຂອງພວກເຂົາ!
ການວິເຄາະຈາກ Galaxy Research ຢືນຢັນວ່າມີການໂຈມຕີ 3 ຄື້ນແຍກກັນທີ່ເກີດຂຶ້ນແລ້ວ. ຄຳຖາມທີ່ຈະໃຊ້ທັນທີທີ່ຜູ້ຖືຫຼຽນທຸກຄົນກຳລັງຖາມວ່າ: ການໂຈມຕີນີ້ຈົບແລ້ວ ຫຼື ຈະມີການລະເມີດເພີ່ມອີກ? ບໍ່ວ່ານີ້ແມ່ນແຮກເກີຄົນດຽວທີ່ນຳ vectors ການໂຈມຕີທີ່ອັບເກຣດມາໃຊ້ ຫຼື ຫຼາຍຜູ້ໂຈມຕີທີ່ອາໄສຊ່ອງໂຫວທີ່ເກົ່າຈາກມີນາ 2021, ຄວາມອັນຕະລາຍແມ່ນມີຈິງ.
🛡️ ແຜນປະຕິບັດດ່ວນ (ປົກປ້ອງຊັບສິນຂອງທ່ານ):
Patch ທັນທີ: ອັບເດດ firmware ຂອງອຸປະກອນເປັນຮຸ່ນລ້າສຸດທາງການທັນທີ.
ສ້າງ Seed ໃໝ່: ໂອນກອງທຶນຂອງທ່ານໄປຫາ seed phrase ໃໝ່ທີ່ສົມບູນ ແລະບໍ່ຖືກບຸກລຸກທັງສິ້ນ.
ຄອງແຄວລ່ວງໜ້າ: Cold storage ຈະປອດໄພໄດ້ພຽງແຕ່ເທົ່າກັບວິໄນຄວາມປອດໄພ—ຢ່າລໍຖ້າຈົນກະເປົ໋າຖືກລະບາຍໝົດ ເພື່ອເອົາມາປະຕິບັດ!
ຈົ່ງສົງໄສໄວ້, ຈົ່ງປອດໄພ, ແລະ ປົກປ້ອງການຖືຄອງຂອງທ່ານ! 🔒⚡
ຂໍ້ກ່າວແຈ້ງ: ບໍ່ແມ່ນຄຳແນະນຳດ້ານການເງິນ. ດຳເນີນການຄົ້ນຄວ້າຂອງທ່ານເອງສະເໝີ (DYOR).
#BTC #Coldcard #HackerAlert
$VELVET
$BEAT
$BTC
2
4
4.7k

ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC 🐋 WHALE WATCH : A third wave of suspected Coldcard wallet drains hit pulling another 207.7 BTC.
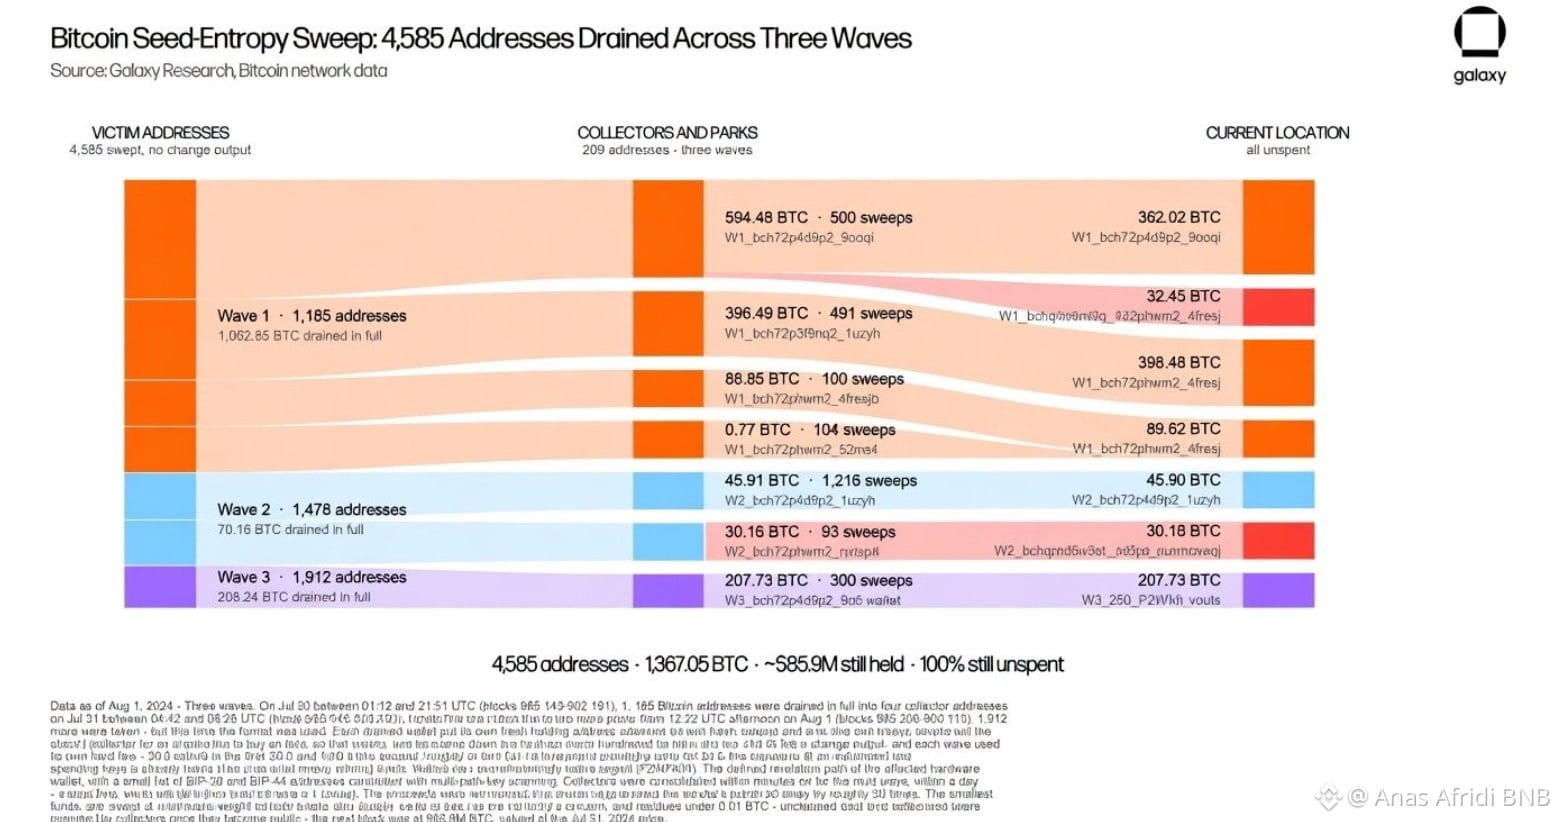
Running total: 1367 $BTC ($88.6M) across 4,585 addresses.
If you generated a seed phrase on affected firmware without a passphrase move your funds now. Fresh seed patched firmware.
Cold storage is only as secure as the entropy that created it.$BTC
{future}(BTCUSDT)
$STBL
{future}(STBLUSDT)
#ColdcardExploitAttackersControl1366BTC 🐋 WHALE WATCH : A third wave of suspected Coldcard wallet drains hit pulling another 207.7 BTC.
Running total: 1367 $BTC ($88.6M) across 4,585 addresses.
If you generated a seed phrase on affected firmware without a passphrase move your funds now. Fresh seed patched firmware.
Cold storage is only as secure as the entropy that created it.$BTC
$STBL
Running total: 1367 $BTC ($88.6M) across 4,585 addresses.
If you generated a seed phrase on affected firmware without a passphrase move your funds now. Fresh seed patched firmware.
Cold storage is only as secure as the entropy that created it.$BTC
$STBL
1
176

#coldcardexploitattackerscontrol1366btc
ཀမི་ལྷོ། ཐེངས་ 25 སྐར་ཆའི་ནང་ལུ་ 594 BTC མི་སྤོང་བྱུང་། 😱
ད་ལྟ། ཇོ་བའི་མཁས་ཚུས་ 1,366.38 BTC ལ་ཚད་འཛིན་བྱེད་ཀྱི་ཡོད་པ། 📉📉📉
«Galaxy Research» གིས་འདི་དང་དེ་ལྟར་ཕེབས་ཡོད་བཞིན་པས་ཆ་འཇོག་ཧྲིལ་པོ་ 3 ཕུང་(waves) གི་ཛྷྲས་འགོག་ཡིན་ཟེར། མཐའ་མ་ནས་བསྐྱར་འཇོག་མ་ཚར་བར་ཡོད་དམ? 🕵️♂️ ཡང་ན་སྒྲིག་ཆས་ལེགས་པ་ཡོད་པའི་ hacker གཅིག་གིས་ཡིན་པ་དང་། ཡང་ན་གཞན་དག་མང་པོ་འདུག་ནས་སྟོང་སྒྲིབ་ནང་འཛུལ་ཡོད་པ་ཡིན་སྲིད! བདེན་མེད་ཁྱད་པར་ཆེན་པོ—Coldcard ལ་ལག་བསྟར་བྱེད་མཁན་ཚུའི་བགོ་གཞི་ལ་ཧ་ཅང་མི་བཟོད་པ། 2021 ཟླ་ 3 ནས་སྟོང་གནས་མི་ཚར་པ། 💸
ག་རེ་བྱེད? ད་ལྟ་ཕམ་བརྡ (firmware) དང་བསྐྱར་འདྲིན་གྱིས་ཤིག། seed phrase གསར་པར་སྤོ་ཡོད་པ་དང་། ཡང་ན BTC ཁྱེར་ནས་ཁྱིམ་གྱི་སྟེང་གི་འོག་ལ་བཞག་པ་ཙམ་ཡིན་ནམ? (བཀའ་སློབ—ཧ་ཅང་སྨྲ་བ།) 😂 འཁྲུལ་མ་བྱེད!
དངུལ་གྱི་གཏམ་བརྗོད་མ་ཡིན།
ཞུ་འདེགས་/འཕྲིན་ལེན་ཞུ།
#BTC #Coldcard #HackerAlert
$BTC
{future}(BTCUSDT)
#coldcardexploitattackerscontrol1366btc
ཀမི་ལྷོ། ཐེངས་ 25 སྐར་ཆའི་ནང་ལུ་ 594 BTC མི་སྤོང་བྱུང་། 😱
ད་ལྟ། ཇོ་བའི་མཁས་ཚུས་ 1,366.38 BTC ལ་ཚད་འཛིན་བྱེད་ཀྱི་ཡོད་པ། 📉📉📉
«Galaxy Research» གིས་འདི་དང་དེ་ལྟར་ཕེབས་ཡོད་བཞིན་པས་ཆ་འཇོག་ཧྲིལ་པོ་ 3 ཕུང་(waves) གི་ཛྷྲས་འགོག་ཡིན་ཟེར། མཐའ་མ་ནས་བསྐྱར་འཇོག་མ་ཚར་བར་ཡོད་དམ? 🕵️♂️ ཡང་ན་སྒྲིག་ཆས་ལེགས་པ་ཡོད་པའི་ hacker གཅིག་གིས་ཡིན་པ་དང་། ཡང་ན་གཞན་དག་མང་པོ་འདུག་ནས་སྟོང་སྒྲིབ་ནང་འཛུལ་ཡོད་པ་ཡིན་སྲིད! བདེན་མེད་ཁྱད་པར་ཆེན་པོ—Coldcard ལ་ལག་བསྟར་བྱེད་མཁན་ཚུའི་བགོ་གཞི་ལ་ཧ་ཅང་མི་བཟོད་པ། 2021 ཟླ་ 3 ནས་སྟོང་གནས་མི་ཚར་པ། 💸
ག་རེ་བྱེད? ད་ལྟ་ཕམ་བརྡ (firmware) དང་བསྐྱར་འདྲིན་གྱིས་ཤིག། seed phrase གསར་པར་སྤོ་ཡོད་པ་དང་། ཡང་ན BTC ཁྱེར་ནས་ཁྱིམ་གྱི་སྟེང་གི་འོག་ལ་བཞག་པ་ཙམ་ཡིན་ནམ? (བཀའ་སློབ—ཧ་ཅང་སྨྲ་བ།) 😂 འཁྲུལ་མ་བྱེད!
དངུལ་གྱི་གཏམ་བརྗོད་མ་ཡིན།
ཞུ་འདེགས་/འཕྲིན་ལེན་ཞུ།
#BTC #Coldcard #HackerAlert
$BTC
ཀမི་ལྷོ། ཐེངས་ 25 སྐར་ཆའི་ནང་ལུ་ 594 BTC མི་སྤོང་བྱུང་། 😱
ད་ལྟ། ཇོ་བའི་མཁས་ཚུས་ 1,366.38 BTC ལ་ཚད་འཛིན་བྱེད་ཀྱི་ཡོད་པ། 📉📉📉
«Galaxy Research» གིས་འདི་དང་དེ་ལྟར་ཕེབས་ཡོད་བཞིན་པས་ཆ་འཇོག་ཧྲིལ་པོ་ 3 ཕུང་(waves) གི་ཛྷྲས་འགོག་ཡིན་ཟེར། མཐའ་མ་ནས་བསྐྱར་འཇོག་མ་ཚར་བར་ཡོད་དམ? 🕵️♂️ ཡང་ན་སྒྲིག་ཆས་ལེགས་པ་ཡོད་པའི་ hacker གཅིག་གིས་ཡིན་པ་དང་། ཡང་ན་གཞན་དག་མང་པོ་འདུག་ནས་སྟོང་སྒྲིབ་ནང་འཛུལ་ཡོད་པ་ཡིན་སྲིད! བདེན་མེད་ཁྱད་པར་ཆེན་པོ—Coldcard ལ་ལག་བསྟར་བྱེད་མཁན་ཚུའི་བགོ་གཞི་ལ་ཧ་ཅང་མི་བཟོད་པ། 2021 ཟླ་ 3 ནས་སྟོང་གནས་མི་ཚར་པ། 💸
ག་རེ་བྱེད? ད་ལྟ་ཕམ་བརྡ (firmware) དང་བསྐྱར་འདྲིན་གྱིས་ཤིག། seed phrase གསར་པར་སྤོ་ཡོད་པ་དང་། ཡང་ན BTC ཁྱེར་ནས་ཁྱིམ་གྱི་སྟེང་གི་འོག་ལ་བཞག་པ་ཙམ་ཡིན་ནམ? (བཀའ་སློབ—ཧ་ཅང་སྨྲ་བ།) 😂 འཁྲུལ་མ་བྱེད!
དངུལ་གྱི་གཏམ་བརྗོད་མ་ཡིན།
ཞུ་འདེགས་/འཕྲིན་ལེན་ཞུ།
#BTC #Coldcard #HackerAlert
$BTC
1
3
1.8k

·
--
ບົດຄວາມ
ເບິ່ງການແປ
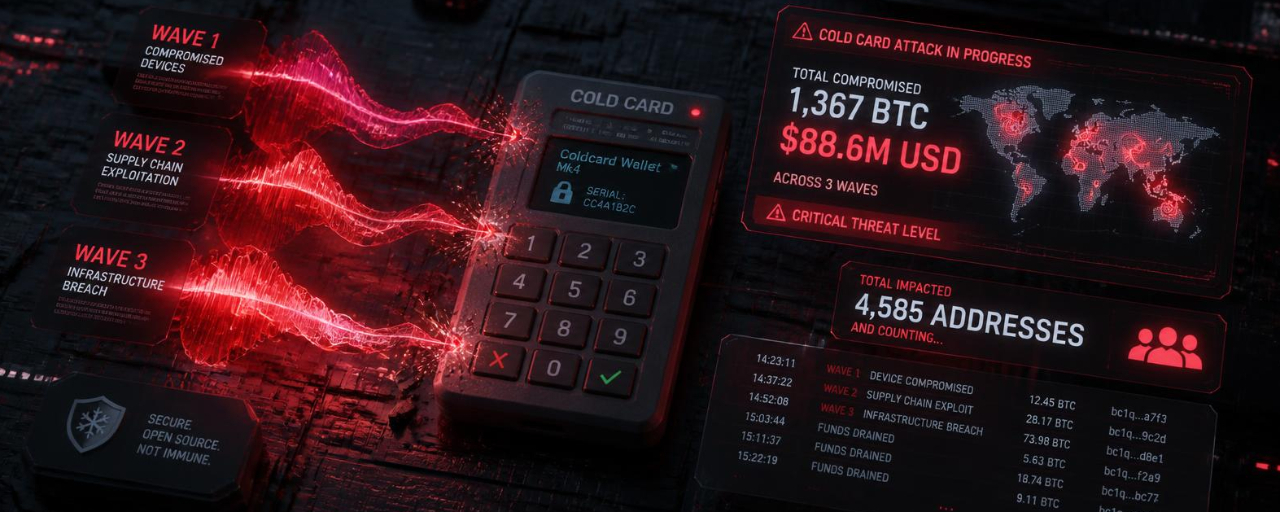
Coldcard Attack Losses Rise to $88.6M—Third Wave ConfirmedGalaxy Research has revised the Coldcard attack losses upward. Three waves have now drained 1,367 BTC from 4,585 addresses.
📊 The Numbers
Total drained: 1,367.05 $BTC (~$88.6M)
Addresses affected: 4,585
Attack waves: 3
Wave 1 (July 30):
1,082.65 BTC1,196 addresses41 minutes
Wave 2 (July 31):
76.16 BTC1,478 addresses
Wave 3 (Aug 1):
207.73 BTC1,912 addresses
🔍 How Each Wave Was Different
Wave 1: Same fee, no change outputs, one victim per transaction
Wave 2: Similar pattern to wave 1
Wave 3:
Different transaction patternIndividual destinations (not shared collector addresses)Batching multiple victims per sweepOnly checking the default derivation path
Galaxy said it is confident each wave is one operator. But they can't confirm if the same attacker is behind all three.
⚙️ Technical Details
Affected devices:
Mk2 and Mk3: firmware 4.0.1 through 4.1.9Mk4 and Mk5: before standard version 5.6.0Q: before version 1.5.0Q
The flaw: Software randomiser instead of hardware one
Effective search space:
Mk2/Mk3: ~40 bitsMk4/Q/Mk5: ~72 bits (vs intended 128)
🛡️ What Coldcard Users Should Do
Install the fixed firmwareGenerate a completely new seedVerify the backup and receiving addressSend a test transaction firstMove the remaining balanceKeep the previous backup until migration is confirmed
Important: Installing new firmware only fixes future seed generation. It cannot add entropy to an existing seed.
$ETH $BNB
#coldcardexploitattackerscontrol1366btc
Coldcard Attack Losses Rise to $88.6M—Third Wave Confirmed
Galaxy Research has revised the Coldcard attack losses upward. Three waves have now drained 1,367 BTC from 4,585 addresses.
📊 The Numbers
Total drained: 1,367.05 $BTC (~$88.6M)
Addresses affected: 4,585
Attack waves: 3
Wave 1 (July 30):
1,082.65 BTC1,196 addresses41 minutes
Wave 2 (July 31):
76.16 BTC1,478 addresses
Wave 3 (Aug 1):
207.73 BTC1,912 addresses
🔍 How Each Wave Was Different
Wave 1: Same fee, no change outputs, one victim per transaction
Wave 2: Similar pattern to wave 1
Wave 3:
Different transaction patternIndividual destinations (not shared collector addresses)Batching multiple victims per sweepOnly checking the default derivation path
Galaxy said it is confident each wave is one operator. But they can't confirm if the same attacker is behind all three.
⚙️ Technical Details
Affected devices:
Mk2 and Mk3: firmware 4.0.1 through 4.1.9Mk4 and Mk5: before standard version 5.6.0Q: before version 1.5.0Q
The flaw: Software randomiser instead of hardware one
Effective search space:
Mk2/Mk3: ~40 bitsMk4/Q/Mk5: ~72 bits (vs intended 128)
🛡️ What Coldcard Users Should Do
Install the fixed firmwareGenerate a completely new seedVerify the backup and receiving addressSend a test transaction firstMove the remaining balanceKeep the previous backup until migration is confirmed
Important: Installing new firmware only fixes future seed generation. It cannot add entropy to an existing seed.
$ETH $BNB
#coldcardexploitattackerscontrol1366btc
📊 The Numbers
Total drained: 1,367.05 $BTC (~$88.6M)
Addresses affected: 4,585
Attack waves: 3
Wave 1 (July 30):
1,082.65 BTC1,196 addresses41 minutes
Wave 2 (July 31):
76.16 BTC1,478 addresses
Wave 3 (Aug 1):
207.73 BTC1,912 addresses
🔍 How Each Wave Was Different
Wave 1: Same fee, no change outputs, one victim per transaction
Wave 2: Similar pattern to wave 1
Wave 3:
Different transaction patternIndividual destinations (not shared collector addresses)Batching multiple victims per sweepOnly checking the default derivation path
Galaxy said it is confident each wave is one operator. But they can't confirm if the same attacker is behind all three.
⚙️ Technical Details
Affected devices:
Mk2 and Mk3: firmware 4.0.1 through 4.1.9Mk4 and Mk5: before standard version 5.6.0Q: before version 1.5.0Q
The flaw: Software randomiser instead of hardware one
Effective search space:
Mk2/Mk3: ~40 bitsMk4/Q/Mk5: ~72 bits (vs intended 128)
🛡️ What Coldcard Users Should Do
Install the fixed firmwareGenerate a completely new seedVerify the backup and receiving addressSend a test transaction firstMove the remaining balanceKeep the previous backup until migration is confirmed
Important: Installing new firmware only fixes future seed generation. It cannot add entropy to an existing seed.
$ETH $BNB
#coldcardexploitattackerscontrol1366btc
4
447
·
--
ສັນຍານກະທິງ
ເບິ່ງການແປ
#coldcardexploitattackerscontrol1366btc
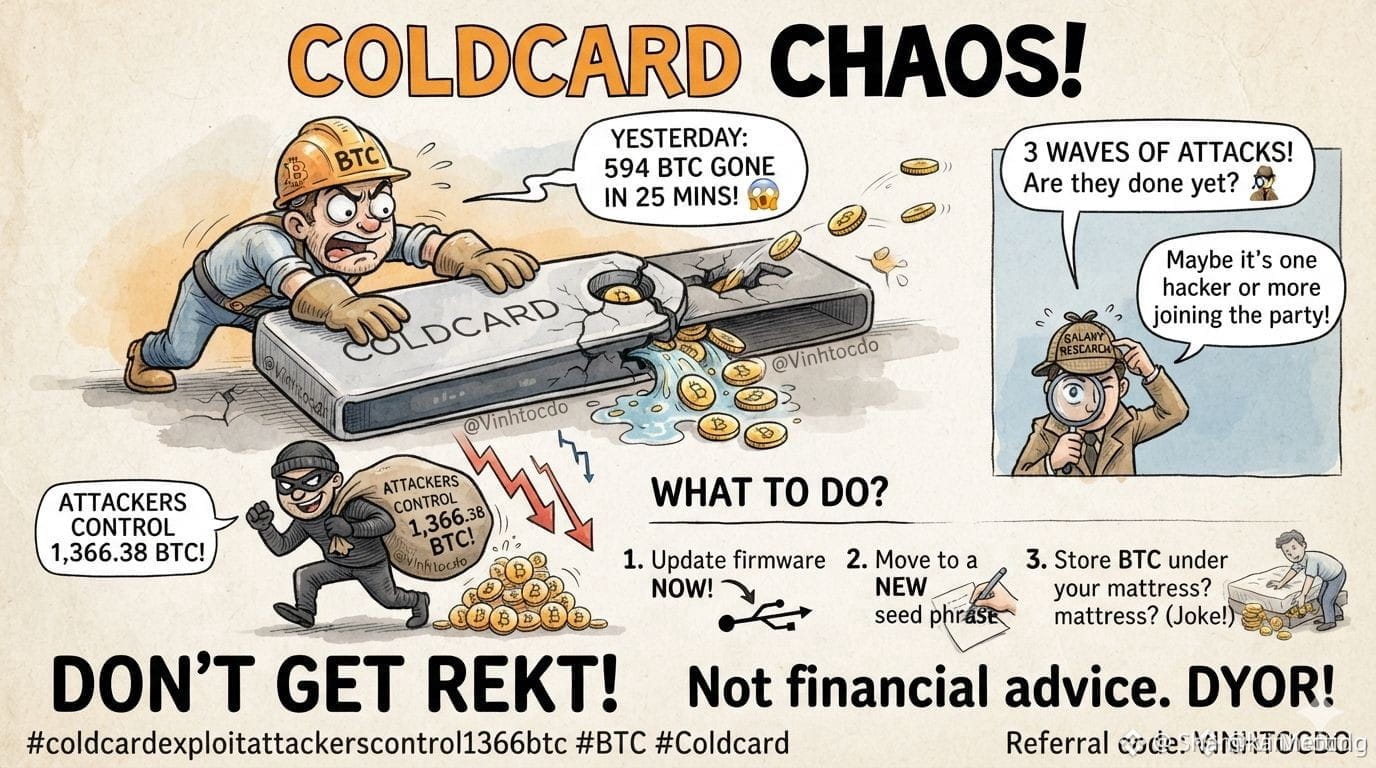
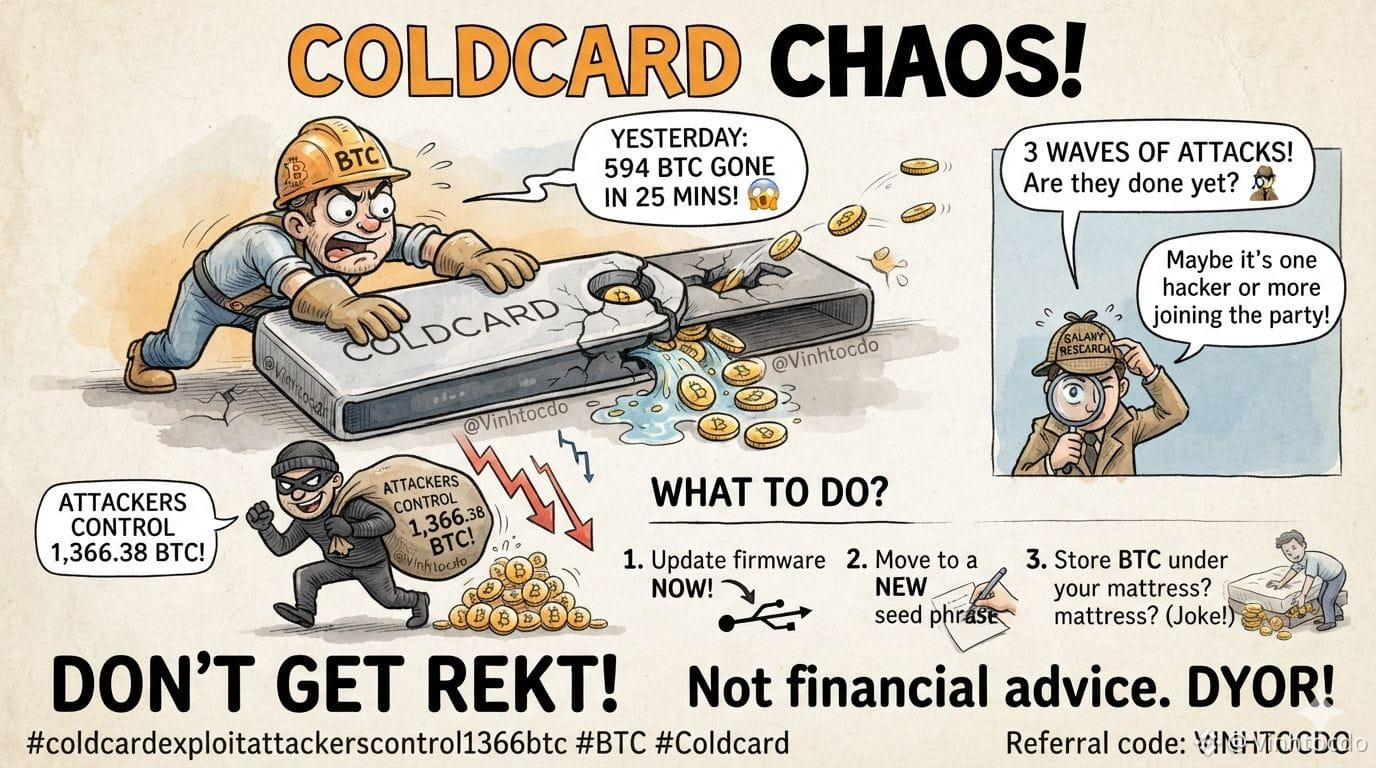
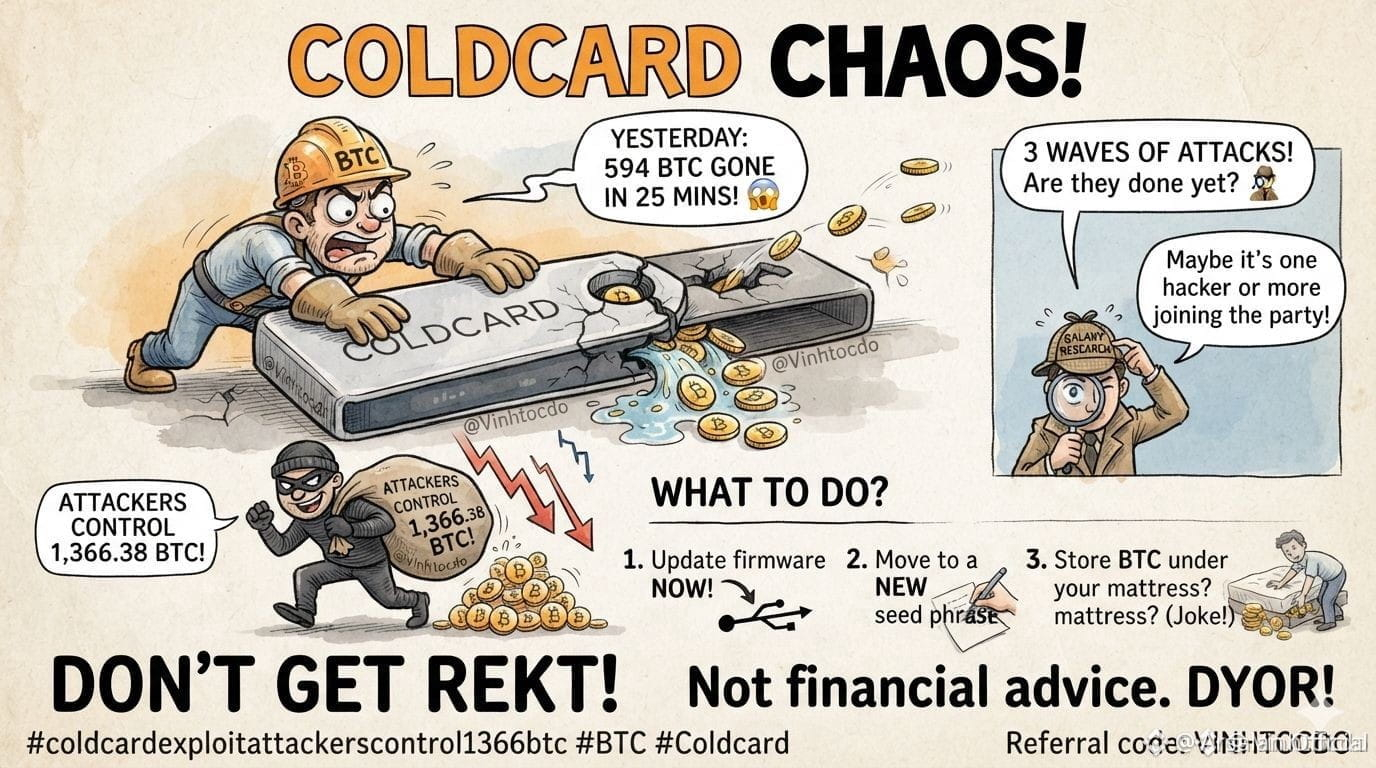
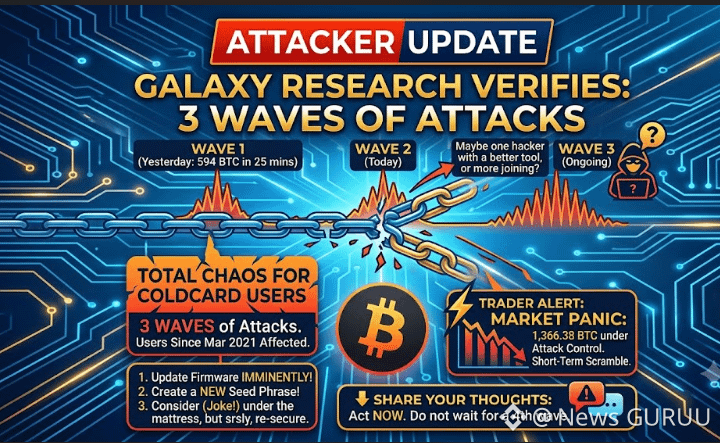
Yesterday: 594 BTC gone in 25 mins. 😱
Today: Attackers control 1,366.38 BTC! 📉📉📉
Galaxy Research says it’s officially 3 waves of attacks. Are they done yet? 🕵️♂️ Maybe it's one hacker with a better tool, or more joining the party! Total chaos for Coldcard users since March 2021. 💸
What to do? Update firmware NOW, move to a NEW seed phrase, or maybe just store your BTC under your mattress? (Joke!) 😂 Don’t get rekt!
Not financial advice. DYOR!
Referral code: VINHTOCDO
#BTC #Coldcard #HackerAlert #VINHTOCDO
$BTC
{future}(BTCUSDT)
$SAHARA
{future}(SAHARAUSDT)
$GRASS
{future}(GRASSUSDT)
#coldcardexploitattackerscontrol1366btc
Yesterday: 594 BTC gone in 25 mins. 😱
Today: Attackers control 1,366.38 BTC! 📉📉📉
Galaxy Research says it’s officially 3 waves of attacks. Are they done yet? 🕵️♂️ Maybe it's one hacker with a better tool, or more joining the party! Total chaos for Coldcard users since March 2021. 💸
What to do? Update firmware NOW, move to a NEW seed phrase, or maybe just store your BTC under your mattress? (Joke!) 😂 Don’t get rekt!
Not financial advice. DYOR!
Referral code: VINHTOCDO
#BTC #Coldcard #HackerAlert #VINHTOCDO
$BTC
$SAHARA
$GRASS
Yesterday: 594 BTC gone in 25 mins. 😱
Today: Attackers control 1,366.38 BTC! 📉📉📉
Galaxy Research says it’s officially 3 waves of attacks. Are they done yet? 🕵️♂️ Maybe it's one hacker with a better tool, or more joining the party! Total chaos for Coldcard users since March 2021. 💸
What to do? Update firmware NOW, move to a NEW seed phrase, or maybe just store your BTC under your mattress? (Joke!) 😂 Don’t get rekt!
Not financial advice. DYOR!
Referral code: VINHTOCDO
#BTC #Coldcard #HackerAlert #VINHTOCDO
$BTC
$SAHARA
$GRASS
18
1
29
41.1k
·
--
ເບິ່ງການແປ
Coldcard Hack Renews Self-Custody DebateA major security incident involving Coldcard-linked wallets has reignited the debate over self-custody after reported Bitcoin thefts exceeded 1,158 $BTC , valued at more than $75 million. Security researchers say the attack unfolded in multiple waves, prompting urgent warnings for potentially affected users.
One notable trend following the incident has been a surge in smaller Bitcoin transfers, a pattern that researchers say resembles wallet movements seen after the FTX collapse. The increase suggests many users are proactively moving funds to reduce risk rather than waiting for further developments.
According to Galaxy Research, a second wave of thefts expanded the number of affected addresses while adding to the total losses. Researchers also reported that the stolen funds remain largely untouched, allowing investigators to continue monitoring the attacker-controlled wallets for any future movement.
Security experts continue to warn that the situation may not be over. Users with potentially affected single-signature Coldcard wallets are being advised to transfer their $BTC to newly generated wallets as a precaution, while multisignature users are believed to face lower risk due to additional authorization requirements.
The incident has also revived the long-running discussion around self-custody. Some critics argue that the attack highlights the risks of managing private keys independently, while supporters maintain that self-custody remains the safest option when proper security practices and wallet management procedures are followed.
#USToCancelIranAttackSubjectToDeal #BitcoinMiningDifficultyFalls14%FromYearHigh #ColdcardExploitAttackersControl1366BTC
Coldcard Hack Renews Self-Custody Debate
A major security incident involving Coldcard-linked wallets has reignited the debate over self-custody after reported Bitcoin thefts exceeded 1,158 $BTC , valued at more than $75 million. Security researchers say the attack unfolded in multiple waves, prompting urgent warnings for potentially affected users.
One notable trend following the incident has been a surge in smaller Bitcoin transfers, a pattern that researchers say resembles wallet movements seen after the FTX collapse. The increase suggests many users are proactively moving funds to reduce risk rather than waiting for further developments.
According to Galaxy Research, a second wave of thefts expanded the number of affected addresses while adding to the total losses. Researchers also reported that the stolen funds remain largely untouched, allowing investigators to continue monitoring the attacker-controlled wallets for any future movement.
Security experts continue to warn that the situation may not be over. Users with potentially affected single-signature Coldcard wallets are being advised to transfer their $BTC to newly generated wallets as a precaution, while multisignature users are believed to face lower risk due to additional authorization requirements.
The incident has also revived the long-running discussion around self-custody. Some critics argue that the attack highlights the risks of managing private keys independently, while supporters maintain that self-custody remains the safest option when proper security practices and wallet management procedures are followed.
#USToCancelIranAttackSubjectToDeal #BitcoinMiningDifficultyFalls14%FromYearHigh #ColdcardExploitAttackersControl1366BTC
One notable trend following the incident has been a surge in smaller Bitcoin transfers, a pattern that researchers say resembles wallet movements seen after the FTX collapse. The increase suggests many users are proactively moving funds to reduce risk rather than waiting for further developments.
According to Galaxy Research, a second wave of thefts expanded the number of affected addresses while adding to the total losses. Researchers also reported that the stolen funds remain largely untouched, allowing investigators to continue monitoring the attacker-controlled wallets for any future movement.
Security experts continue to warn that the situation may not be over. Users with potentially affected single-signature Coldcard wallets are being advised to transfer their $BTC to newly generated wallets as a precaution, while multisignature users are believed to face lower risk due to additional authorization requirements.
The incident has also revived the long-running discussion around self-custody. Some critics argue that the attack highlights the risks of managing private keys independently, while supporters maintain that self-custody remains the safest option when proper security practices and wallet management procedures are followed.
#USToCancelIranAttackSubjectToDeal #BitcoinMiningDifficultyFalls14%FromYearHigh #ColdcardExploitAttackersControl1366BTC
31
ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC ‼️ WARNING: A 41-minute sweep drained 1,196 Bitcoin addresses of 1,082.65 BTC, worth about $70 million.
Researchers linked the incident to a Coldcard firmware vulnerability that weakened wallet seed generation.
Installing the patch is not enough.
Here's what Coldcard users need to know$BTC
{future}(BTCUSDT)
$Q
{future}(QUSDT)
$AKT
{future}(AKTUSDT)
#ColdcardExploitAttackersControl1366BTC ‼️ WARNING: A 41-minute sweep drained 1,196 Bitcoin addresses of 1,082.65 BTC, worth about $70 million.
Researchers linked the incident to a Coldcard firmware vulnerability that weakened wallet seed generation.
Installing the patch is not enough.
Here's what Coldcard users need to know$BTC
$Q
$AKT
Researchers linked the incident to a Coldcard firmware vulnerability that weakened wallet seed generation.
Installing the patch is not enough.
Here's what Coldcard users need to know$BTC
$Q
$AKT
1
131
ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC #BREAKING 🚨 BOOOOM 💥💥
ANOTHER COLD CARD HACK ALERT: 207.7294 BTC STOLEN! 😳 That makes a whopping 1,367.05 BTC taken from 4,585 addresses! Time to REVISIT that security guidance, folks!
STAY SAFE OUT THERE, BITCOINERS! 🔒$BTC
{future}(BTCUSDT)
$COLLECT
{future}(COLLECTUSDT)
$NIGHT
{future}(NIGHTUSDT)
#ColdcardExploitAttackersControl1366BTC #BREAKING 🚨 BOOOOM 💥💥
ANOTHER COLD CARD HACK ALERT: 207.7294 BTC STOLEN! 😳 That makes a whopping 1,367.05 BTC taken from 4,585 addresses! Time to REVISIT that security guidance, folks!
STAY SAFE OUT THERE, BITCOINERS! 🔒$BTC
$COLLECT
$NIGHT
ANOTHER COLD CARD HACK ALERT: 207.7294 BTC STOLEN! 😳 That makes a whopping 1,367.05 BTC taken from 4,585 addresses! Time to REVISIT that security guidance, folks!
STAY SAFE OUT THERE, BITCOINERS! 🔒$BTC
$COLLECT
$NIGHT
1
239
ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC That headline appears to be referring to a real, current Coldcard incident, but the wording matters.
What reliable reporting indicates:
Coinkite published a security advisory on July 30, 2026, warning that seeds generated on affected Coldcard firmware can be at risk if they were created without enough independent dice entropy and without a strong BIP-39 passphrase. (blog.coinkite.com)
The advisory says Mk2/Mk3 firmware 4.0.1 through 4.1.9 are affected, and that some Mk4, Q, and Mk5 devices before fixed firmware releases were also impacted with reduced entropy. (blog.coinkite.com)
Multiple recent reports say attackers have stolen about 1,367 BTC in total across several attack waves. One report cites 1,367.05 BTC across 4,585 addresses, and another cites Galaxy Research confirming the same scale. (cryptotimes.io)
So the core claim is plausibly true, but I’d phrase it more carefully as:
“Recent reporting says attackers exploited a Coldcard seed-generation flaw and have stolen roughly 1,367 BTC so far.” (cryptotimes.io)
A few important nuances:
“Attackers control 1366 BTC” is slightly imprecise; the latest figures I found are closer to 1,367 BTC, not exactly 1,366. (cryptotimes.io)
This does not mean all Coldcard users are affected. The risk depends on which device/firmware was used, how the seed was generated, and whether the wallet had a strong unique passphrase. (blog.coinkite.com)
Coinkite’s own guidance is to treat funds from affected seeds as at risk and migrate to a newly generated wallet on fixed firmware. (blog.coinkite.com)
If you use Coldcard, the safest immediate takeaway is:
Do not generate a new seed on affected/unpatched firmware.
Check whether your wallet seed was created on impacted firmware.
If exposed, move funds to a new wallet generated after updating to fixed firmware, ideally with strong entropy and a unique BIP-39 passphrase. (blog.coinkite.com)col$COLD.US
{stock_us}(COLD.US)
$BTC
{future}(BTCUSDT)
$COIN.US
{stock_us}(COIN.US)
#ColdcardExploitAttackersControl1366BTC That headline appears to be referring to a real, current Coldcard incident, but the wording matters.
What reliable reporting indicates:
Coinkite published a security advisory on July 30, 2026, warning that seeds generated on affected Coldcard firmware can be at risk if they were created without enough independent dice entropy and without a strong BIP-39 passphrase. (blog.coinkite.com)
The advisory says Mk2/Mk3 firmware 4.0.1 through 4.1.9 are affected, and that some Mk4, Q, and Mk5 devices before fixed firmware releases were also impacted with reduced entropy. (blog.coinkite.com)
Multiple recent reports say attackers have stolen about 1,367 BTC in total across several attack waves. One report cites 1,367.05 BTC across 4,585 addresses, and another cites Galaxy Research confirming the same scale. (cryptotimes.io)
So the core claim is plausibly true, but I’d phrase it more carefully as:
“Recent reporting says attackers exploited a Coldcard seed-generation flaw and have stolen roughly 1,367 BTC so far.” (cryptotimes.io)
A few important nuances:
“Attackers control 1366 BTC” is slightly imprecise; the latest figures I found are closer to 1,367 BTC, not exactly 1,366. (cryptotimes.io)
This does not mean all Coldcard users are affected. The risk depends on which device/firmware was used, how the seed was generated, and whether the wallet had a strong unique passphrase. (blog.coinkite.com)
Coinkite’s own guidance is to treat funds from affected seeds as at risk and migrate to a newly generated wallet on fixed firmware. (blog.coinkite.com)
If you use Coldcard, the safest immediate takeaway is:
Do not generate a new seed on affected/unpatched firmware.
Check whether your wallet seed was created on impacted firmware.
If exposed, move funds to a new wallet generated after updating to fixed firmware, ideally with strong entropy and a unique BIP-39 passphrase. (blog.coinkite.com)col$COLD.US
$BTC
$COIN.US
What reliable reporting indicates:
Coinkite published a security advisory on July 30, 2026, warning that seeds generated on affected Coldcard firmware can be at risk if they were created without enough independent dice entropy and without a strong BIP-39 passphrase. (blog.coinkite.com)
The advisory says Mk2/Mk3 firmware 4.0.1 through 4.1.9 are affected, and that some Mk4, Q, and Mk5 devices before fixed firmware releases were also impacted with reduced entropy. (blog.coinkite.com)
Multiple recent reports say attackers have stolen about 1,367 BTC in total across several attack waves. One report cites 1,367.05 BTC across 4,585 addresses, and another cites Galaxy Research confirming the same scale. (cryptotimes.io)
So the core claim is plausibly true, but I’d phrase it more carefully as:
“Recent reporting says attackers exploited a Coldcard seed-generation flaw and have stolen roughly 1,367 BTC so far.” (cryptotimes.io)
A few important nuances:
“Attackers control 1366 BTC” is slightly imprecise; the latest figures I found are closer to 1,367 BTC, not exactly 1,366. (cryptotimes.io)
This does not mean all Coldcard users are affected. The risk depends on which device/firmware was used, how the seed was generated, and whether the wallet had a strong unique passphrase. (blog.coinkite.com)
Coinkite’s own guidance is to treat funds from affected seeds as at risk and migrate to a newly generated wallet on fixed firmware. (blog.coinkite.com)
If you use Coldcard, the safest immediate takeaway is:
Do not generate a new seed on affected/unpatched firmware.
Check whether your wallet seed was created on impacted firmware.
If exposed, move funds to a new wallet generated after updating to fixed firmware, ideally with strong entropy and a unique BIP-39 passphrase. (blog.coinkite.com)col$COLD.US
$BTC
$COIN.US
1
199
ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC JUST IN: ⛏ 1,367.05 BTC reportedly drained across 4,585 Coldcard-generated addresses in what Galaxy Research suspects were three coordinated attack waves. Hardware wallet users: now is a good time to verify your setup.$BTC
{future}(BTCUSDT)
$BNB
{future}(BNBUSDT)
$SOL
{future}(SOLUSDT)
#ColdcardExploitAttackersControl1366BTC JUST IN: ⛏ 1,367.05 BTC reportedly drained across 4,585 Coldcard-generated addresses in what Galaxy Research suspects were three coordinated attack waves. Hardware wallet users: now is a good time to verify your setup.$BTC
$BNB
$SOL
$BNB
$SOL
1
78
ເບິ່ງການແປ
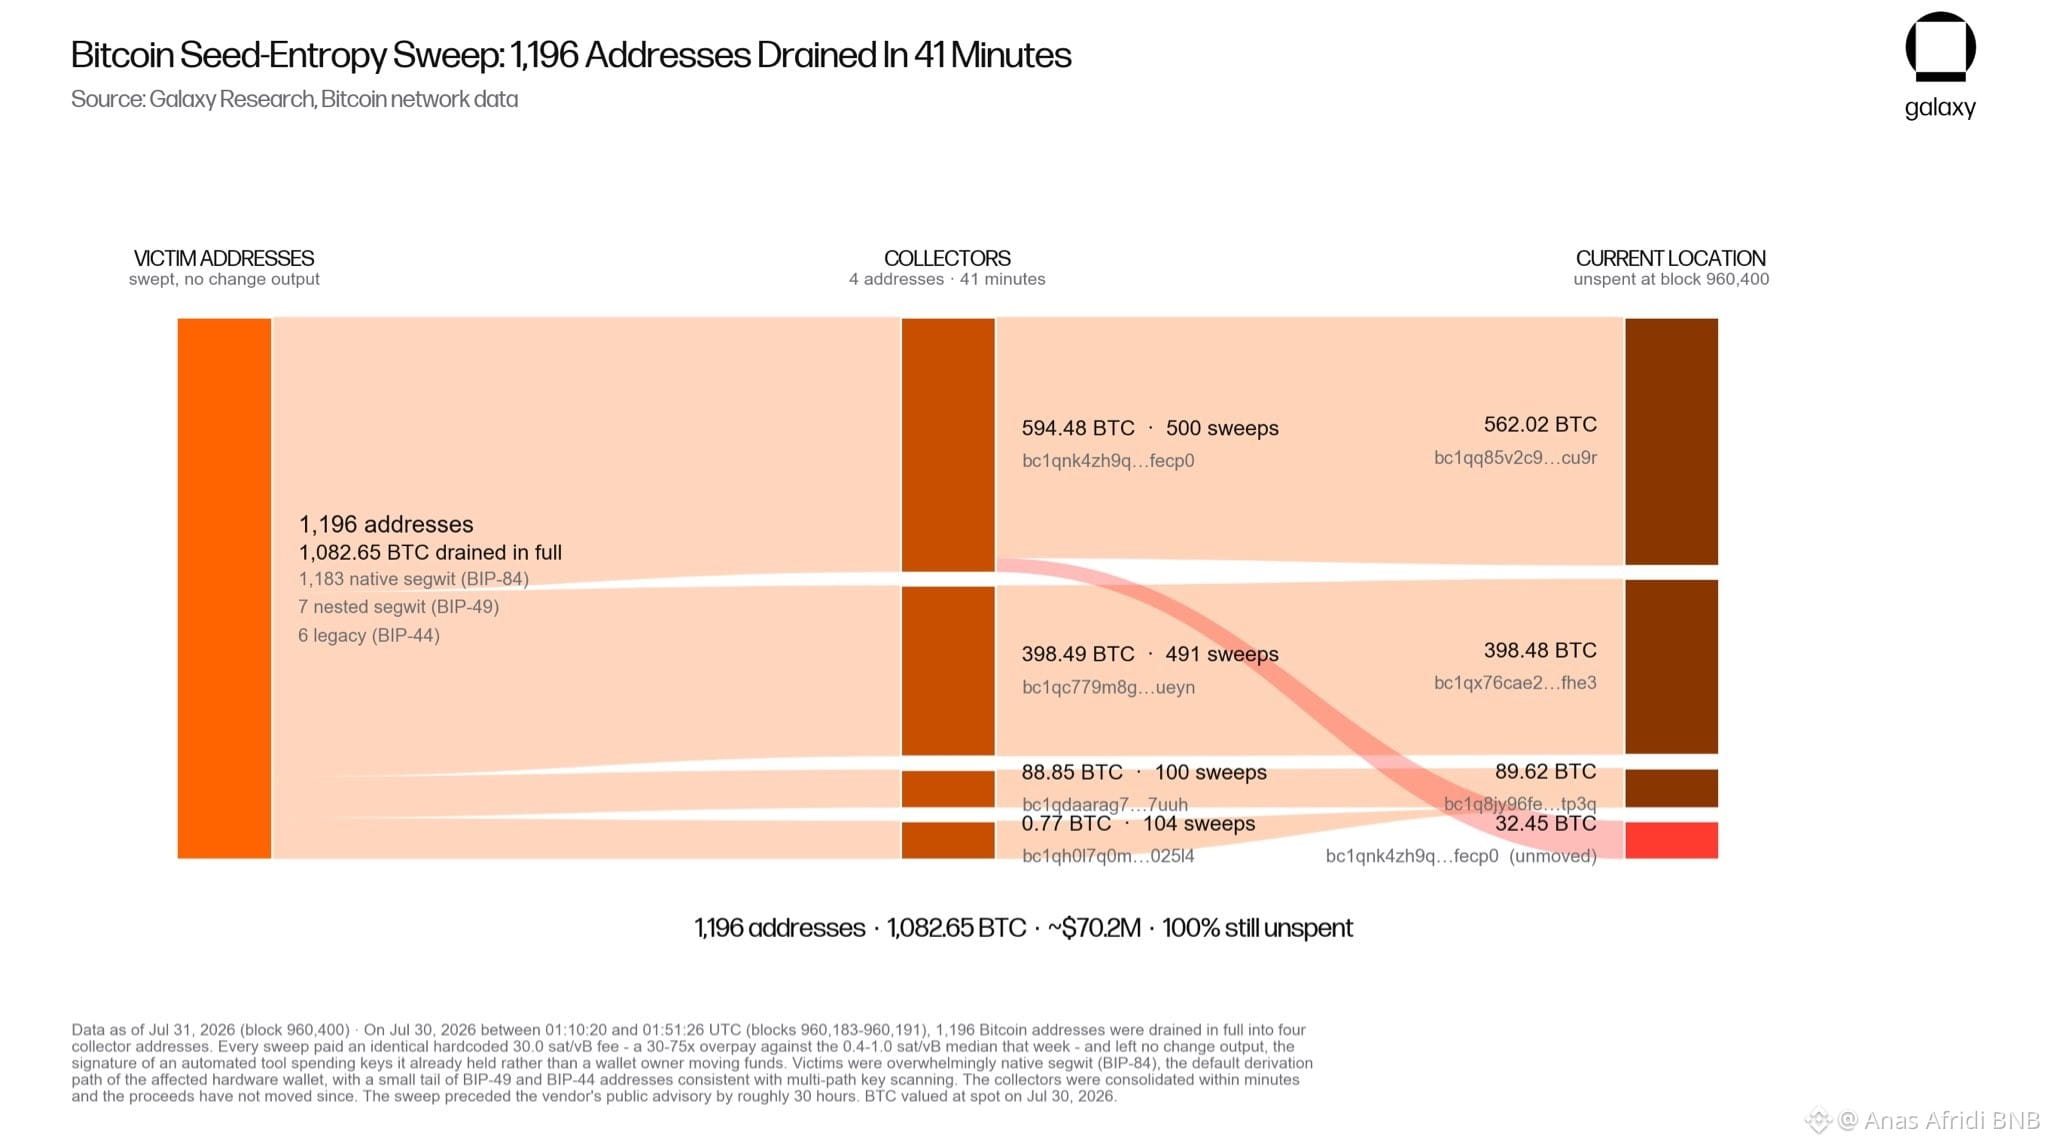
#ColdcardExploitAttackersControl1366BTC We mapped the flow of funds for the Coldcard vulnerability based on the pattern identified by engineers at Block and shared by @clay_garrett
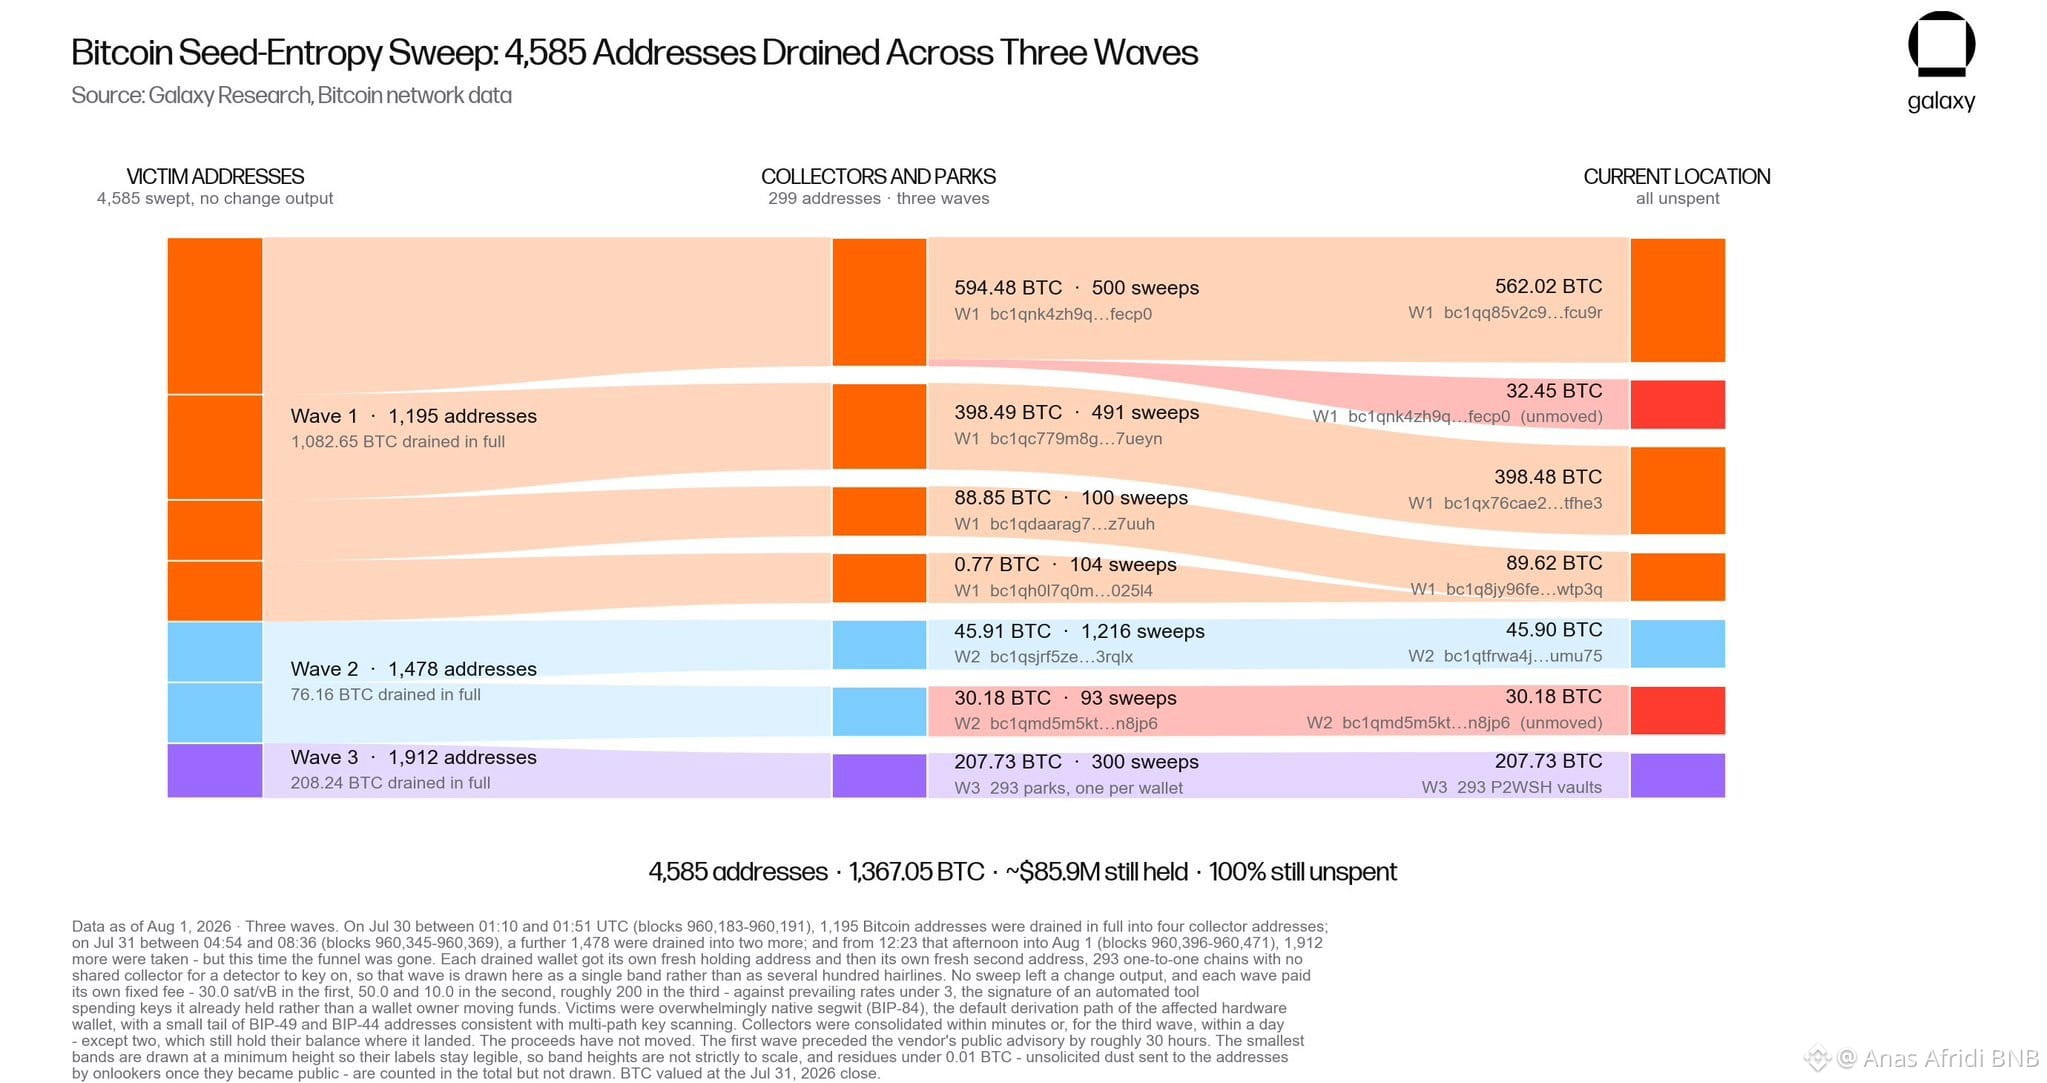
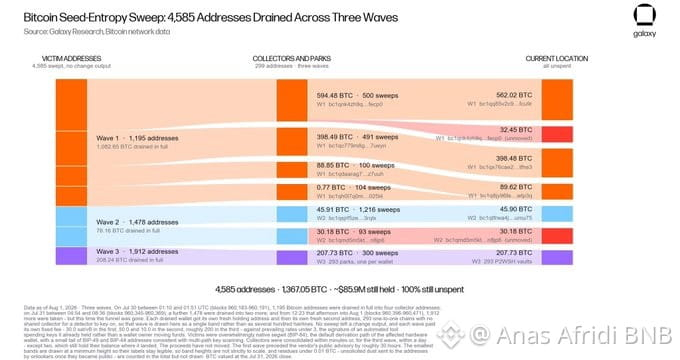
1,196 addresses drained in full for 1,082.65 BTC (~$70.2M) between 01:10:20 and 01:51:26 UTC on Jul 30 — a 41-minute window, blocks 960,183-960,191. That preceded the hardware-wallet vendor's public advisory by ~30 hours.
Signature: every sweep paid an identical hardcoded 30.0 sat/vB — a 30-75x overpay vs the 0.4-1.0 sat/vB median that week — and left no change output. That looks like an automated tool spending keys it already held, not owners moving funds. Victims: 1,183 native segwit (BIP-84), 7 BIP-49, 6 BIP-44 — consistent with multi-path key scanning.
Proceeds consolidated within minutes and have NOT moved since:
- bc1qq85v2c9...cu9r — 562.02 BTC
- bc1qx76cae2...fhe3 — 398.48 BTC
- bc1q8jy96fe...tp3q — 89.62 BTC
- bc1qnk4zh9q...fecp0 — 32.45 BTC (unmoved)$BTC
{future}(BTCUSDT)
#ColdcardExploitAttackersControl1366BTC We mapped the flow of funds for the Coldcard vulnerability based on the pattern identified by engineers at Block and shared by @clay_garrett
1,196 addresses drained in full for 1,082.65 BTC (~$70.2M) between 01:10:20 and 01:51:26 UTC on Jul 30 — a 41-minute window, blocks 960,183-960,191. That preceded the hardware-wallet vendor's public advisory by ~30 hours.
Signature: every sweep paid an identical hardcoded 30.0 sat/vB — a 30-75x overpay vs the 0.4-1.0 sat/vB median that week — and left no change output. That looks like an automated tool spending keys it already held, not owners moving funds. Victims: 1,183 native segwit (BIP-84), 7 BIP-49, 6 BIP-44 — consistent with multi-path key scanning.
Proceeds consolidated within minutes and have NOT moved since:
- bc1qq85v2c9...cu9r — 562.02 BTC
- bc1qx76cae2...fhe3 — 398.48 BTC
- bc1q8jy96fe...tp3q — 89.62 BTC
- bc1qnk4zh9q...fecp0 — 32.45 BTC (unmoved)$BTC
1,196 addresses drained in full for 1,082.65 BTC (~$70.2M) between 01:10:20 and 01:51:26 UTC on Jul 30 — a 41-minute window, blocks 960,183-960,191. That preceded the hardware-wallet vendor's public advisory by ~30 hours.
Signature: every sweep paid an identical hardcoded 30.0 sat/vB — a 30-75x overpay vs the 0.4-1.0 sat/vB median that week — and left no change output. That looks like an automated tool spending keys it already held, not owners moving funds. Victims: 1,183 native segwit (BIP-84), 7 BIP-49, 6 BIP-44 — consistent with multi-path key scanning.
Proceeds consolidated within minutes and have NOT moved since:
- bc1qq85v2c9...cu9r — 562.02 BTC
- bc1qx76cae2...fhe3 — 398.48 BTC
- bc1q8jy96fe...tp3q — 89.62 BTC
- bc1qnk4zh9q...fecp0 — 32.45 BTC (unmoved)$BTC
1
56
ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC Whoa... seriously?
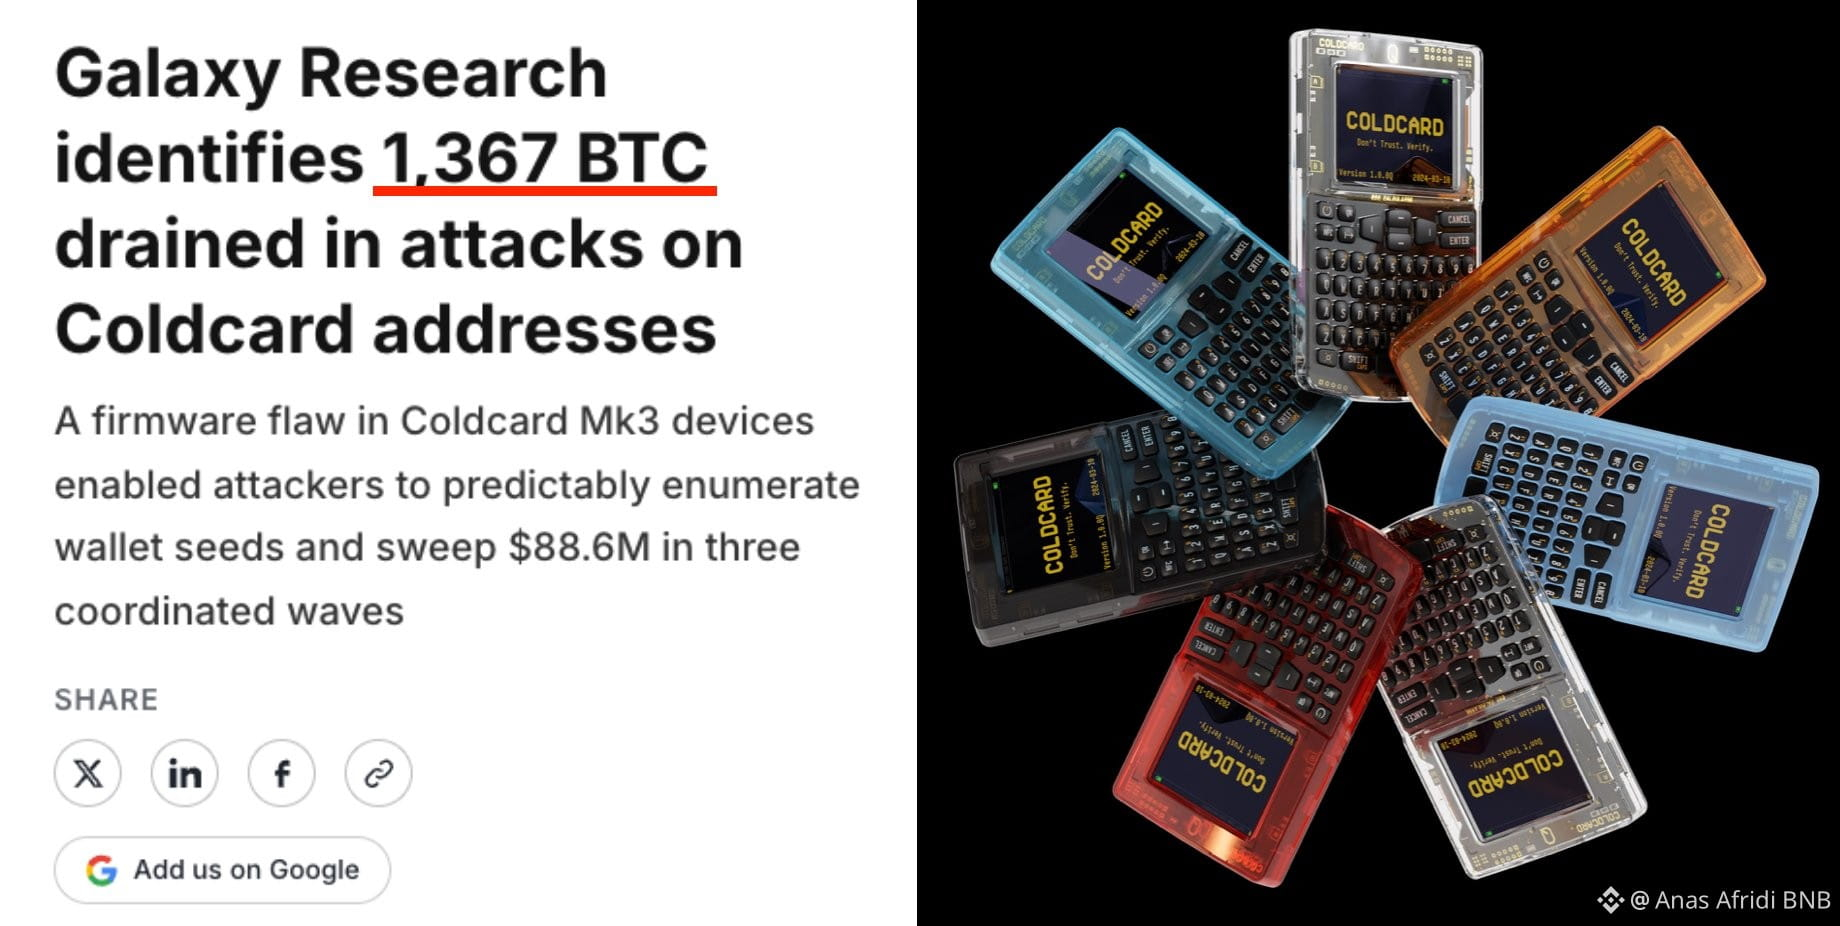
A vulnerability in Coldcard was exploited in an attack, resulting in losses exceeding $88 million.
A total of 1,367 BTC was stolen, affecting more than 4,500 victims.
At this point, even cold wallets can no longer be considered completely safe.$BTC
{future}(BTCUSDT)
#ColdcardExploitAttackersControl1366BTC Whoa... seriously?
A vulnerability in Coldcard was exploited in an attack, resulting in losses exceeding $88 million.
A total of 1,367 BTC was stolen, affecting more than 4,500 victims.
At this point, even cold wallets can no longer be considered completely safe.$BTC
A vulnerability in Coldcard was exploited in an attack, resulting in losses exceeding $88 million.
A total of 1,367 BTC was stolen, affecting more than 4,500 victims.
At this point, even cold wallets can no longer be considered completely safe.$BTC
1
62
·
--
ບົດຄວາມ
ເບິ່ງການແປ
$88.6 Million Vanishes: The Coldcard Hack Waves That Are Shaking Bitcoin's SecurityThe crypto community is on high alert as one of the most significant hardware wallet security breaches in recent memory continues to unfold. Losses have now surpassed a staggering $88.6 million, and the on-chain data is painting a complex picture of potential attackers and evolving tactics. 🚨
According to Galaxy Research, a third wave of attacks has been detected, targeting addresses linked to Coldcard devices. This fresh assault added another 207.7 $BTC to the total loot, bringing the grand total to a massive 1,367 BTC swiped from over 4,500 addresses. The sheer scale of this heist is a stark reminder that even "cold" storage isn't always impenetrable. 🥶
Here’s the breakdown of what happened:
The First Two Waves: These were eerily similar. The attacker (or group) used shared collection addresses and had a consistent transaction structure. However, a key difference in transaction fees and "replace-by-fee" signals left room for doubt about whether it was the same person pulling the strings.The Third Wave: A Shift in Strategy 🕵️♂️: This wave is a complete curveball. Instead of sending stolen funds to shared addresses, they created a new target address for every single victim. They also switched to a different address format and only scanned the default derivation path. This screams that either the same hacker re-engineered their tools to make tracking harder, or a copycat attacker has entered the chat.The Victims 👥: Most of the losses are coming from wallets with balances under 1 BTC, but the big fish (larger balances) are where the real value lies. This distribution suggests the targets are primarily individual users, not massive institutions.The Stolen Hoard 💰: The attackers are sitting on a mountain of Bitcoin, valued at nearly $89 million. Interestingly, none of these coins have been moved yet. It's a waiting game to see what happens next.
This entire exploit is tied back to vulnerable Coldcard software that was released way back in March 2021. It's a classic case of an old vulnerability coming back to haunt users.
The key takeaway?
Always keep your firmware updated and be aware of even historical vulnerabilities.
A wallet is only as secure as its code and the user's diligence. 🔐
What do you think will happen to the Bitcoin price if this 88million in BTC is eventually dumped on the market? Drop your thoughts below! 👇
$ETH $COLD.US
#coldcardexploitattackerscontrol1366btc
$88.6 Million Vanishes: The Coldcard Hack Waves That Are Shaking Bitcoin's Security
The crypto community is on high alert as one of the most significant hardware wallet security breaches in recent memory continues to unfold. Losses have now surpassed a staggering $88.6 million, and the on-chain data is painting a complex picture of potential attackers and evolving tactics. 🚨
According to Galaxy Research, a third wave of attacks has been detected, targeting addresses linked to Coldcard devices. This fresh assault added another 207.7 $BTC to the total loot, bringing the grand total to a massive 1,367 BTC swiped from over 4,500 addresses. The sheer scale of this heist is a stark reminder that even "cold" storage isn't always impenetrable. 🥶
Here’s the breakdown of what happened:
The First Two Waves: These were eerily similar. The attacker (or group) used shared collection addresses and had a consistent transaction structure. However, a key difference in transaction fees and "replace-by-fee" signals left room for doubt about whether it was the same person pulling the strings.The Third Wave: A Shift in Strategy 🕵️♂️: This wave is a complete curveball. Instead of sending stolen funds to shared addresses, they created a new target address for every single victim. They also switched to a different address format and only scanned the default derivation path. This screams that either the same hacker re-engineered their tools to make tracking harder, or a copycat attacker has entered the chat.The Victims 👥: Most of the losses are coming from wallets with balances under 1 BTC, but the big fish (larger balances) are where the real value lies. This distribution suggests the targets are primarily individual users, not massive institutions.The Stolen Hoard 💰: The attackers are sitting on a mountain of Bitcoin, valued at nearly $89 million. Interestingly, none of these coins have been moved yet. It's a waiting game to see what happens next.
This entire exploit is tied back to vulnerable Coldcard software that was released way back in March 2021. It's a classic case of an old vulnerability coming back to haunt users.
The key takeaway?
Always keep your firmware updated and be aware of even historical vulnerabilities.
A wallet is only as secure as its code and the user's diligence. 🔐
What do you think will happen to the Bitcoin price if this 88million in BTC is eventually dumped on the market? Drop your thoughts below! 👇
$ETH $COLD.US
#coldcardexploitattackerscontrol1366btc
According to Galaxy Research, a third wave of attacks has been detected, targeting addresses linked to Coldcard devices. This fresh assault added another 207.7 $BTC to the total loot, bringing the grand total to a massive 1,367 BTC swiped from over 4,500 addresses. The sheer scale of this heist is a stark reminder that even "cold" storage isn't always impenetrable. 🥶
Here’s the breakdown of what happened:
The First Two Waves: These were eerily similar. The attacker (or group) used shared collection addresses and had a consistent transaction structure. However, a key difference in transaction fees and "replace-by-fee" signals left room for doubt about whether it was the same person pulling the strings.The Third Wave: A Shift in Strategy 🕵️♂️: This wave is a complete curveball. Instead of sending stolen funds to shared addresses, they created a new target address for every single victim. They also switched to a different address format and only scanned the default derivation path. This screams that either the same hacker re-engineered their tools to make tracking harder, or a copycat attacker has entered the chat.The Victims 👥: Most of the losses are coming from wallets with balances under 1 BTC, but the big fish (larger balances) are where the real value lies. This distribution suggests the targets are primarily individual users, not massive institutions.The Stolen Hoard 💰: The attackers are sitting on a mountain of Bitcoin, valued at nearly $89 million. Interestingly, none of these coins have been moved yet. It's a waiting game to see what happens next.
This entire exploit is tied back to vulnerable Coldcard software that was released way back in March 2021. It's a classic case of an old vulnerability coming back to haunt users.
The key takeaway?
Always keep your firmware updated and be aware of even historical vulnerabilities.
A wallet is only as secure as its code and the user's diligence. 🔐
What do you think will happen to the Bitcoin price if this 88million in BTC is eventually dumped on the market? Drop your thoughts below! 👇
$ETH $COLD.US
#coldcardexploitattackerscontrol1366btc
1
27
ເບິ່ງການແປ
#ColdcardExploitAttackersControl1366BTC ⚡️UPDATE: Coldcard exploit reaches $86 MILLION with 1,367 BTC drained from 4,585 wallets across three waves.
All stolen funds remain unspent across attacker addresses.
The third wave alone hit 1,912 new addresses.$MVLL
{future}(MVLLUSDT)
$H
{future}(HUSDT)
$KAITO
{future}(KAITOUSDT)
#ColdcardExploitAttackersControl1366BTC ⚡️UPDATE: Coldcard exploit reaches $86 MILLION with 1,367 BTC drained from 4,585 wallets across three waves.
All stolen funds remain unspent across attacker addresses.
The third wave alone hit 1,912 new addresses.$MVLL
$H
$KAITO
All stolen funds remain unspent across attacker addresses.
The third wave alone hit 1,912 new addresses.$MVLL
$H
$KAITO
1
221
·
--
ສັນຍານໝີ
ເບິ່ງການແປ
#coldcardexploitattackerscontrol1366btc #sahara
🚨 COLDcard ATTACKS: BTC HOLDERS ON ALERT!
⚠️ Attackers reportedly controlled 1,366 BTC, following multiple attack waves.
✅ Security risk is still active
✅ Coldcard users should update firmware
✅ Move funds to a new seed if potentially exposed
📊 Trading View: SELL/AVOID risky exposure for now. Security concerns can trigger further panic; wait for the situation to stabilize before buying.
❓ Would you buy BTC during this security scare, or stay out until the attacks are over?
"CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"👇👇👇👇
$BTC $SAHARA $GRASS
{future}(GRASSUSDT)
{spot}(SAHARAUSDT)
{spot}(BTCUSDT)
#BTC
#coldcardexploitattackerscontrol1366btc #sahara
🚨 COLDcard ATTACKS: BTC HOLDERS ON ALERT!
⚠️ Attackers reportedly controlled 1,366 BTC, following multiple attack waves.
✅ Security risk is still active
✅ Coldcard users should update firmware
✅ Move funds to a new seed if potentially exposed
📊 Trading View: SELL/AVOID risky exposure for now. Security concerns can trigger further panic; wait for the situation to stabilize before buying.
❓ Would you buy BTC during this security scare, or stay out until the attacks are over?
"CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"👇👇👇👇
$BTC $SAHARA $GRASS
#BTC
🚨 COLDcard ATTACKS: BTC HOLDERS ON ALERT!
⚠️ Attackers reportedly controlled 1,366 BTC, following multiple attack waves.
✅ Security risk is still active
✅ Coldcard users should update firmware
✅ Move funds to a new seed if potentially exposed
📊 Trading View: SELL/AVOID risky exposure for now. Security concerns can trigger further panic; wait for the situation to stabilize before buying.
❓ Would you buy BTC during this security scare, or stay out until the attacks are over?
"CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"👇👇👇👇
$BTC $SAHARA $GRASS
#BTC
2
3.7k
·
--
ເບິ່ງການແປ
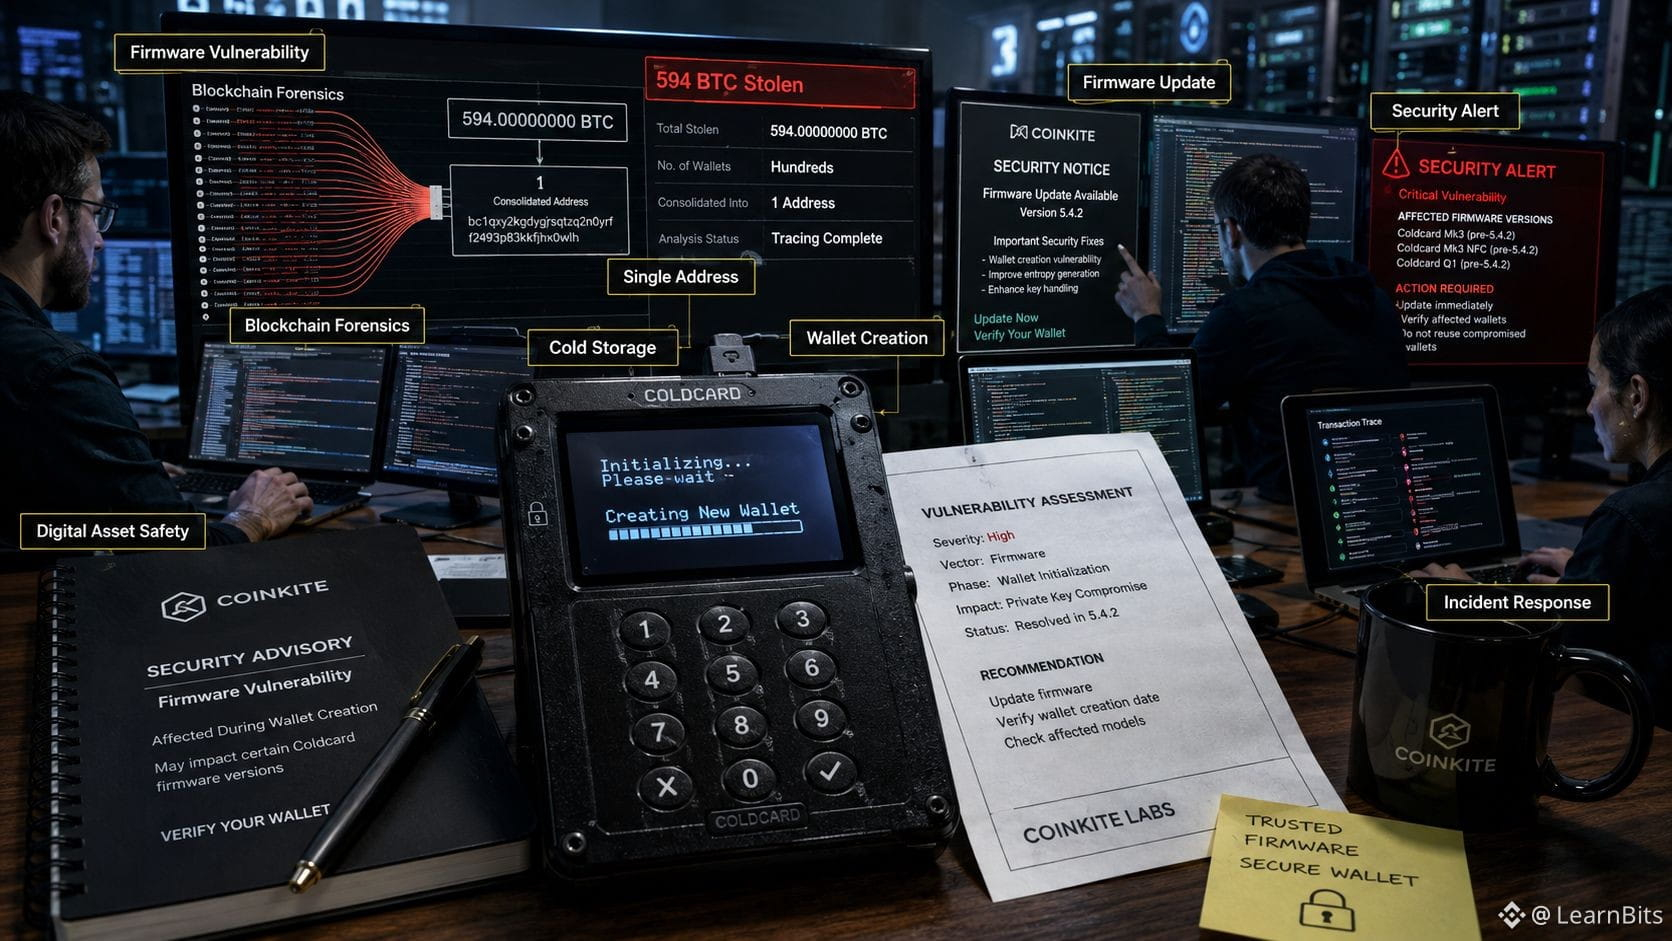
🔐 A Hardware Wallet Bug Led to a Massive Bitcoin Theft
Hundreds of $BTC wallets were drained after attackers exploited a flaw affecting certain Coldcard hardware wallet firmware versions used during wallet creation. Around 594 Bitcoin was stolen, with blockchain data showing the funds later consolidated into a single address. 😬 Coinkite has acknowledged the issue and warned affected users to check whether their wallets were created with vulnerable firmware. It's a strong reminder that even offline storage depends on secure software from day one.
#BitcoinMiningDifficultyFalls14%FromYearHigh #ColdcardExploitAttackersControl1366BTC
🔐 A Hardware Wallet Bug Led to a Massive Bitcoin Theft
Hundreds of $BTC wallets were drained after attackers exploited a flaw affecting certain Coldcard hardware wallet firmware versions used during wallet creation. Around 594 Bitcoin was stolen, with blockchain data showing the funds later consolidated into a single address. 😬 Coinkite has acknowledged the issue and warned affected users to check whether their wallets were created with vulnerable firmware. It's a strong reminder that even offline storage depends on secure software from day one.
#BitcoinMiningDifficultyFalls14%FromYearHigh #ColdcardExploitAttackersControl1366BTC
Hundreds of $BTC wallets were drained after attackers exploited a flaw affecting certain Coldcard hardware wallet firmware versions used during wallet creation. Around 594 Bitcoin was stolen, with blockchain data showing the funds later consolidated into a single address. 😬 Coinkite has acknowledged the issue and warned affected users to check whether their wallets were created with vulnerable firmware. It's a strong reminder that even offline storage depends on secure software from day one.
#BitcoinMiningDifficultyFalls14%FromYearHigh #ColdcardExploitAttackersControl1366BTC
184
ເບິ່ງການແປ
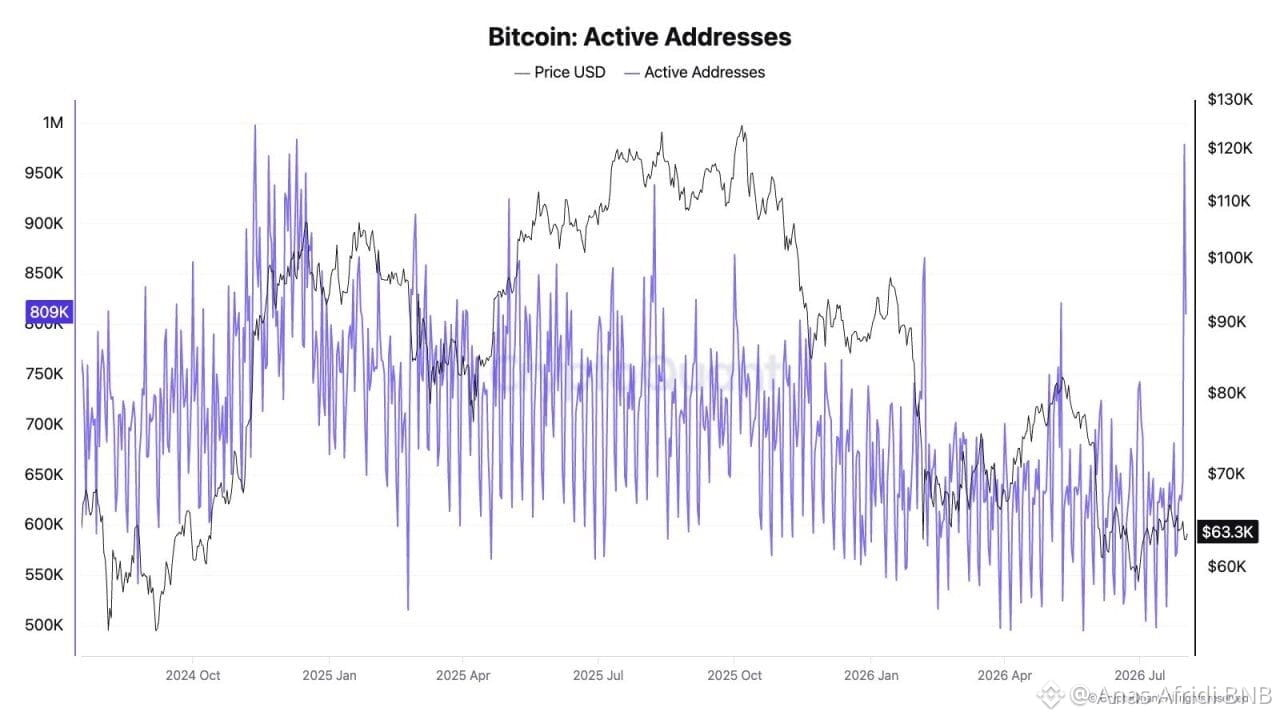
#ColdcardExploitAttackersControl1366BTC ⚡ TODAY: Bitcoin Active Addresses spike from 645K to almost 1M after the Coldcard hack.$BTC
{future}(BTCUSDT)
#ColdcardExploitAttackersControl1366BTC ⚡ TODAY: Bitcoin Active Addresses spike from 645K to almost 1M after the Coldcard hack.$BTC
1
45
·
--
ບົດຄວາມ
ເບິ່ງການແປ
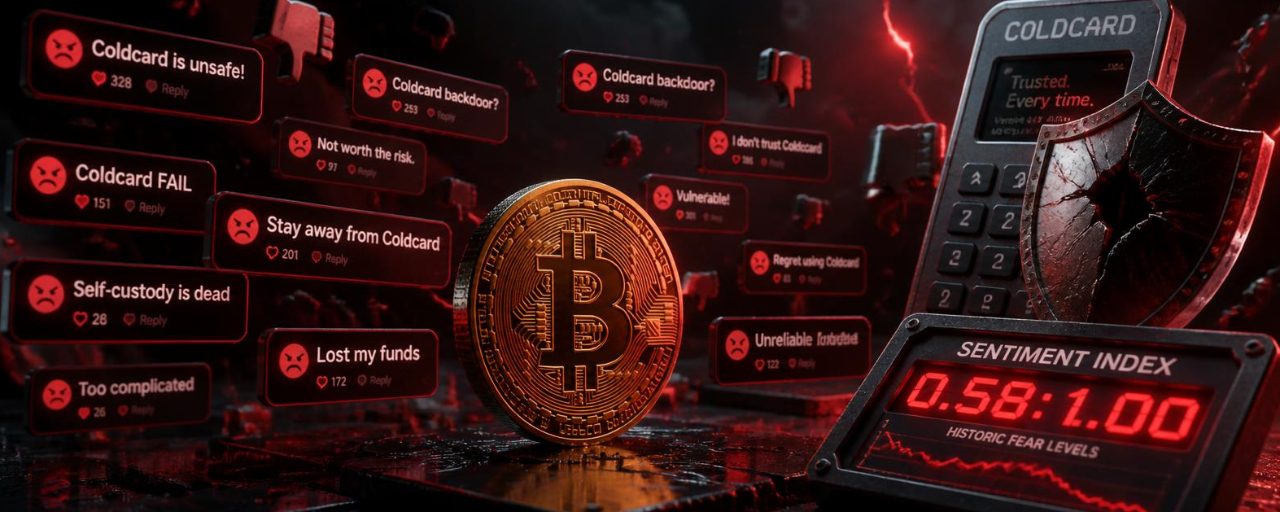
Bitcoin Sentiment Hits Historic Low—Coldcard Exploit Sparks Self-Custody FearFor every 1 positive Bitcoin comment, there are only 0.58 positive ones. The fear is deeper than FTX, Mt. Gox, or COVID-19.
📊 The Data
Santiment reports Bitcoin's positive-to-negative commentary ratio has hit the lowest level since modern tracking began.
0.58 positive : 1.00 negativeFear has surpassed greed by a margin not seen during FTX, Mt. Gox, or COVID-19 Black Thursday
🔍 Why This Time Is Different
This isn't an exchange hack. It's not a bridge exploit. It's not a smart contract bug.
It's a Coldcard hardware wallet firmware flaw.
The one thing that was supposed to be impenetrable—cold storage—has a wound.
The difference:
Exchange hacks = anger at centralized entitiesBridge exploits = questions about cross-chain architectureSmart contract bugs = debates about auditingColdcard exploit = the self-custody mental model is broken
🧠 What This Means
The panic exceeds war fears from earlier this yearThe attack is on self-sovereignty, not just dollarsThe trust bar for hardware solutions just rose
⚠️ What to Watch
On-chain flows: Exchange deposits could signal a flight to custodial convenienceHardware wallet trust: Will users move away from self-custody?Regulatory impact: Could this tilt policy toward stricter hardware certification?
📉 Bottom Line
The Coldcard exploit is a crisis of confidence deeper than its $89 million financial impact. The crowd has spoken: self-custody just got less comfortable.
$BTC $ETH $BNB
#coldcardexploitattackerscontrol1366btc
Bitcoin Sentiment Hits Historic Low—Coldcard Exploit Sparks Self-Custody Fear
For every 1 positive Bitcoin comment, there are only 0.58 positive ones. The fear is deeper than FTX, Mt. Gox, or COVID-19.
📊 The Data
Santiment reports Bitcoin's positive-to-negative commentary ratio has hit the lowest level since modern tracking began.
0.58 positive : 1.00 negativeFear has surpassed greed by a margin not seen during FTX, Mt. Gox, or COVID-19 Black Thursday
🔍 Why This Time Is Different
This isn't an exchange hack. It's not a bridge exploit. It's not a smart contract bug.
It's a Coldcard hardware wallet firmware flaw.
The one thing that was supposed to be impenetrable—cold storage—has a wound.
The difference:
Exchange hacks = anger at centralized entitiesBridge exploits = questions about cross-chain architectureSmart contract bugs = debates about auditingColdcard exploit = the self-custody mental model is broken
🧠 What This Means
The panic exceeds war fears from earlier this yearThe attack is on self-sovereignty, not just dollarsThe trust bar for hardware solutions just rose
⚠️ What to Watch
On-chain flows: Exchange deposits could signal a flight to custodial convenienceHardware wallet trust: Will users move away from self-custody?Regulatory impact: Could this tilt policy toward stricter hardware certification?
📉 Bottom Line
The Coldcard exploit is a crisis of confidence deeper than its $89 million financial impact. The crowd has spoken: self-custody just got less comfortable.
$BTC $ETH $BNB
#coldcardexploitattackerscontrol1366btc
📊 The Data
Santiment reports Bitcoin's positive-to-negative commentary ratio has hit the lowest level since modern tracking began.
0.58 positive : 1.00 negativeFear has surpassed greed by a margin not seen during FTX, Mt. Gox, or COVID-19 Black Thursday
🔍 Why This Time Is Different
This isn't an exchange hack. It's not a bridge exploit. It's not a smart contract bug.
It's a Coldcard hardware wallet firmware flaw.
The one thing that was supposed to be impenetrable—cold storage—has a wound.
The difference:
Exchange hacks = anger at centralized entitiesBridge exploits = questions about cross-chain architectureSmart contract bugs = debates about auditingColdcard exploit = the self-custody mental model is broken
🧠 What This Means
The panic exceeds war fears from earlier this yearThe attack is on self-sovereignty, not just dollarsThe trust bar for hardware solutions just rose
⚠️ What to Watch
On-chain flows: Exchange deposits could signal a flight to custodial convenienceHardware wallet trust: Will users move away from self-custody?Regulatory impact: Could this tilt policy toward stricter hardware certification?
📉 Bottom Line
The Coldcard exploit is a crisis of confidence deeper than its $89 million financial impact. The crowd has spoken: self-custody just got less comfortable.
$BTC $ETH $BNB
#coldcardexploitattackerscontrol1366btc
35
ເຂົ້າສູ່ລະບົບເພື່ອສຳຫຼວດເນື້ອຫາເພີ່ມເຕີມ
ເຂົ້າຮ່ວມກຸ່ມຜູ້ໃຊ້ຄຣິບໂຕທົ່ວໂລກໃນ Binance Square.
⚡️ ໄດ້ຮັບຂໍ້ມູນຫຼ້າສຸດ ແລະ ທີ່ມີປະໂຫຍດກ່ຽວກັບຄຣິບໂຕ.
💬 ໄດ້ຮັບຄວາມໄວ້ວາງໃຈຈາກຕະຫຼາດແລກປ່ຽນຄຣິບໂຕທີ່ໃຫຍ່ທີ່ສຸດໃນໂລກ.
👍 ຄົ້ນຫາຂໍ້ມູນເຊີງເລິກທີ່ແທ້ຈາກນັກສ້າງທີ່ໄດ້ຮັບການຢືນຢັນ.
ອີເມວ / ເບີໂທລະສັບ
ຫົວຂໍ້ທີ່ກໍາລັງນິຍົມ
1
#MemeLaunchpads82%OfArcDayOneVolume
0 views
5 ກຳລັງສົນທະນາ
2
#OstiumLoanDisputeHearingSetInNYFederalCourt
914 views
59 ກຳລັງສົນທະນາ
3
#SKPoliceRefer18PolymarketUsersToProsecutors
2,091 views
121 ກຳລັງສົນທະນາ
4
#FedSEPProjects2026RateAt4.1%
6,026 views
197 ກຳລັງສົນທະນາ
5
#USHouseAdvancesBitcoinReserveBill
4,028 views
154 ກຳລັງສົນທະນາ
6
#AmazonGetsWarrantsToBuyGeneracStock
4,748 views
174 ກຳລັງສົນທະນາ
7
#DotPlotSignalsOneMoreHikeIn2026
25,498 views
542 ກຳລັງສົນທະນາ
8
#RobinhoodToSupportCircleArcNetwork
8,047 views
194 ກຳລັງສົນທະນາ
9
#FedHikes25BpsUSStocksClose
37,239 views
449 ກຳລັງສົນທະນາ
10
#AaveToLaunchRWAMarketOnAvalanche
8,737 views
196 ກຳລັງສົນທະນາ