

XSense Crypto
7 投稿
XSense Crypto
報告
ユーザーをブロック
取引を発注
低高頻度トレーダー
3.3か月
0 フォロー
0 フォロワー
6 いいね
投稿
ポートフォリオ
すべて
引用
·
--
ブリッシュ
翻訳参照
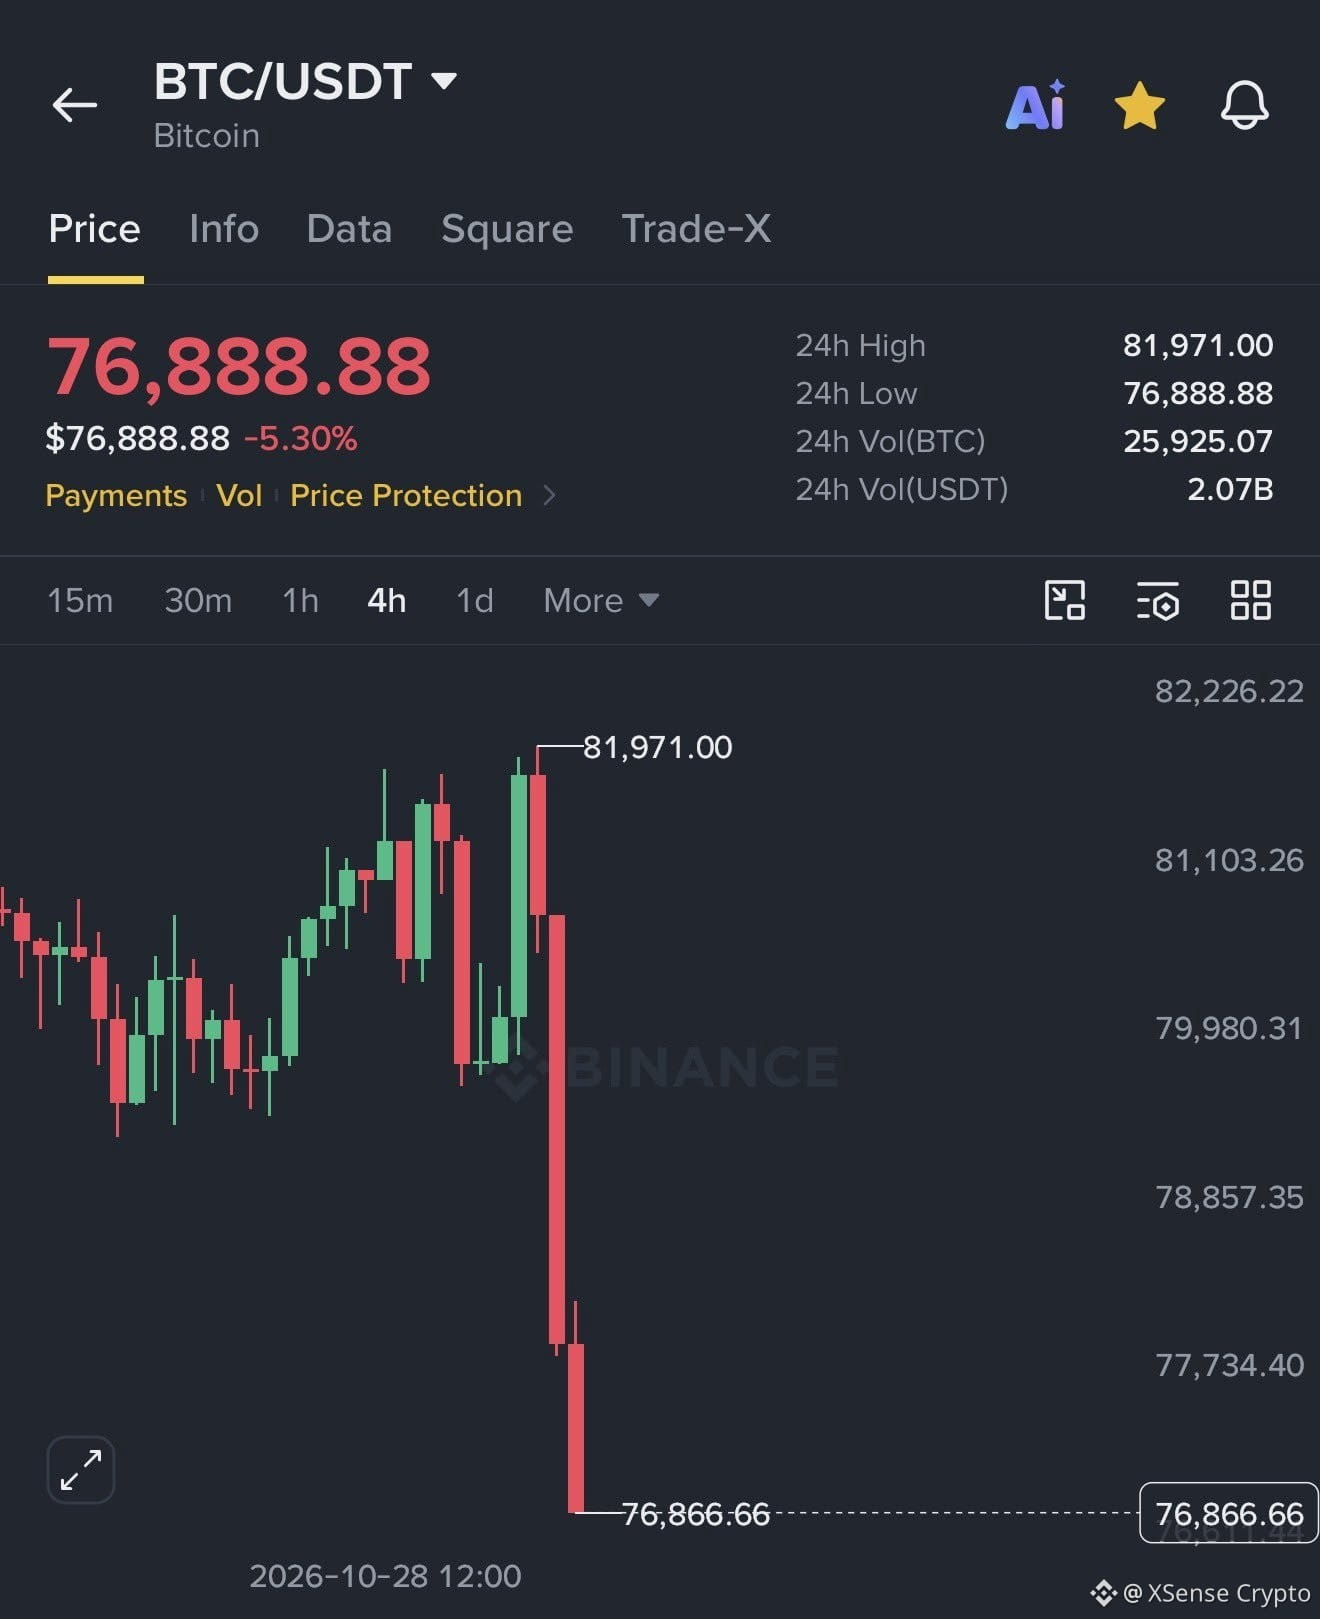
After Malone Lam, this might be the biggest crypto heist we've ever witnessed. 💀
$6.3 BILLION stolen from Binance in one of the largest crypto thefts in history.
The scale is absolutely insane.
#BinanceSquareTalks #Binancehacked #CryptoHeist $BTC #btc70k #financialpandemic
After Malone Lam, this might be the biggest crypto heist we've ever witnessed. 💀
$6.3 BILLION stolen from Binance in one of the largest crypto thefts in history.
The scale is absolutely insane.
#BinanceSquareTalks #Binancehacked #CryptoHeist $BTC #btc70k #financialpandemic
$6.3 BILLION stolen from Binance in one of the largest crypto thefts in history.
The scale is absolutely insane.
#BinanceSquareTalks #Binancehacked #CryptoHeist $BTC #btc70k #financialpandemic
7
翻訳参照
🎁 PREDICTION CONTEST: Win $10 in $BTC ! 🚀
Predict the exact time Binance will fully reactivate withdrawal options!
How to Enter:
Follow my profile & Like this post.
Comment below with your prediction (Date & UTC Time) when Binance will officially resume full withdrawal services.
Example: "Nov 1 at 18:00 UTC"
🏆 Prize: 5x $10 in $BTC to the person whose prediction is closest to the exact official announcement timestamp!
👇 Drop your predictions in the comments below!
#BinanceSAFUFundTransferCompleted7499BTC #YiHe:ProofOfReserves:10TokensAt100%Backing #GIVEAWAY🎁 #Giveawaycontest #GiveawayAlert
XSense Crypto
·
--
ブリッシュ🚨 BINANCE RECOVERY UPDATE & $10 $BTC GIVEAWAY! 🎁
*Quick Update*:
Binance has officially replenished 90% of affected assets following the recent security incident!
Major tokens (BTC, ETH, USDT, BNB, SOL, USDC, XRP) are 100% fully backed.
SAFU & Corporate Treasury are absorbing all direct user losses.
Withdrawals are expected to reopen soon!
🎁 PREDICTION CONTEST: Win $10 in $BTC ! 🚀
Predict the exact time Binance will fully reactivate withdrawal options!
How to Enter:
Follow my profile & Like this post.
Comment below with your prediction (Date & UTC Time) when Binance will officially resume full withdrawal services.
Example: "Nov 1 at 18:00 UTC"
🏆 Prize: $10 in BTC to the person whose prediction is closest to the exact official announcement timestamp!
👇 Drop your predictions in the comments below!
#BinanceSAFUFundTransferCompleted7499BTC #YiHe:ProofOfReserves:10TokensAt100%Backing #BinanceRecovery #BTCGiveaway #GIVEAWAY🎁
1
24
·
--
弱気相場
翻訳参照
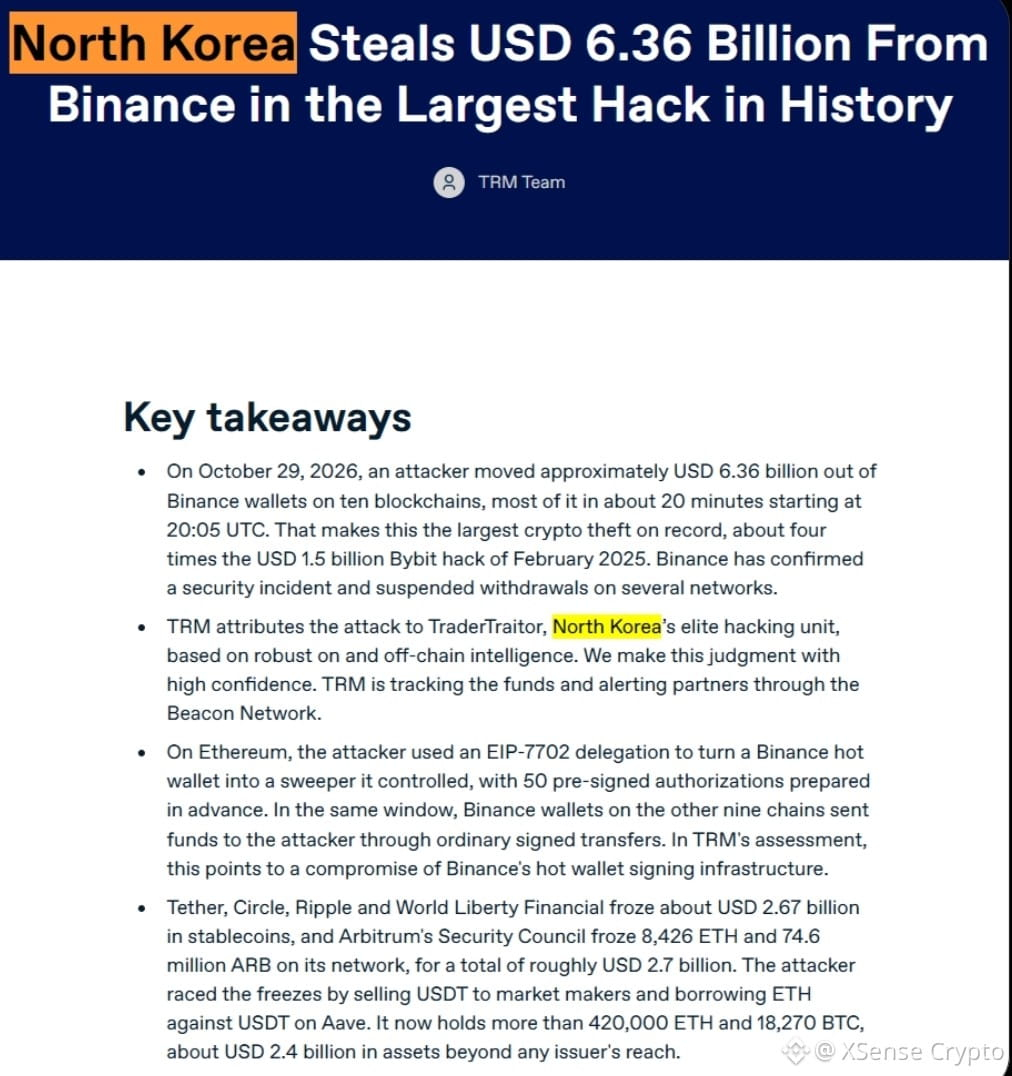
🚨 BREAKING: Elite North Korean Hacking Group "TraderTraitor" Linked to Massive $6.3 Billion Binance Hack $BTC $BNB
A major cybersecurity breakthrough has officially attributed one of the largest cyber-heists in cryptocurrency history directly to North Korean state-sponsored threat actors.
According to a recent report published by blockchain intelligence firm TRM Labs, the elite North Korean cybercrime unit known as TraderTraitor has been identified as the mastermind behind the catastrophic $6.3 billion Binance exploit.
Who is TraderTraitor?
TraderTraitor (also tracked under cyber intelligence umbrellas alongside the Lazarus Group) is a sophisticated, state-backed threat actor known for targeting Web3 infrastructure, crypto exchanges, and decentralized finance (DeFi) protocols.
The group primarily relies on targeted spear-phishing campaigns, malicious trading applications, and complex social engineering tactics to gain initial network access and compromise administrative credentials.
Key Highlights of the Investigation:
Attribution: On-chain analytics and forensic tracking by TRM Labs tied the movement of stolen funds back to wallet addresses linked to TraderTraitor infrastructure.
Modus Operandi: The attackers utilized advanced obfuscation techniques, cross-chain bridges, and mixing services to launder the proceeds before intelligence firms successfully traced the flow.
Geopolitical Impact: Experts suggest funds stolen by TraderTraitor are systematically funneled into North Korea's state-sponsored weapons programs and cyber operations.
What This Means for the Crypto Ecosystem
This incident underscores the rising sophistication of nation-state actors in the Web3 domain. Security analysts strongly advise projects and centralized entities to enforce strict multi-party computation (MPC) controls, rigorous employee security awareness training, and real-time transaction monitoring to guard against state-backed exploitation.
Stay tuned as further updates and official statements from security researchers continue to unfold.
1
67
🚨速報:北朝鮮の精鋭ハッカー集団「TraderTraitor」、Binanceでの63億ドル規模の大規模事件に関与サイバーセキュリティにおける大きな進展により、暗号資産の歴史上最大級のサイバー窃盗事件の一つが、北朝鮮政府が支援する脅威アクターによるものだと正式に特定されました。
ブロックチェーン情報分析企業TRM Labsが発表した最近の報告書によると、TraderTraitorとして知られる北朝鮮の精鋭サイバー犯罪部隊が、壊滅的な63億ドル相当のBinanceへの攻撃の首謀者として特定されました。$BTC $BNB
TraderTraitorとは?
TraderTraitorは、Lazarus Groupとともにサイバーインテリジェンス関連の枠組みで追跡されていることもあり、Web3インフラ、暗号資産取引所、分散型金融(DeFi)プロトコルを標的とすることで知られる、高度な国家支援型の脅威アクターです。
🚨速報:北朝鮮の精鋭ハッカー集団「TraderTraitor」、Binanceでの63億ドル規模の大規模事件に関与
サイバーセキュリティにおける大きな進展により、暗号資産の歴史上最大級のサイバー窃盗事件の一つが、北朝鮮政府が支援する脅威アクターによるものだと正式に特定されました。
ブロックチェーン情報分析企業TRM Labsが発表した最近の報告書によると、TraderTraitorとして知られる北朝鮮の精鋭サイバー犯罪部隊が、壊滅的な63億ドル相当のBinanceへの攻撃の首謀者として特定されました。$BTC $BNB
TraderTraitorとは?
TraderTraitorは、Lazarus Groupとともにサイバーインテリジェンス関連の枠組みで追跡されていることもあり、Web3インフラ、暗号資産取引所、分散型金融(DeFi)プロトコルを標的とすることで知られる、高度な国家支援型の脅威アクターです。
ブロックチェーン情報分析企業TRM Labsが発表した最近の報告書によると、TraderTraitorとして知られる北朝鮮の精鋭サイバー犯罪部隊が、壊滅的な63億ドル相当のBinanceへの攻撃の首謀者として特定されました。$BTC $BNB
TraderTraitorとは?
TraderTraitorは、Lazarus Groupとともにサイバーインテリジェンス関連の枠組みで追跡されていることもあり、Web3インフラ、暗号資産取引所、分散型金融(DeFi)プロトコルを標的とすることで知られる、高度な国家支援型の脅威アクターです。
1
266
ログインして、さらにコンテンツを読む
厳選トピックで世界の暗号資産トレーダーの仲間入り
⚡️ 暗号資産に関する最新かつ有益な情報が見つかります。
💬 世界最大の暗号資産取引所から信頼されています。
👍 認証を受けたクリエイターから、有益なインサイトを得られます。
メール / 電話番号