*TITLE: Crypto Security After the $6.3B Binance Hack: 7 Steps Every User Must Take in 2026*
*Introduction:*
The $6.3 billion Binance hack on Oct 29, 2026 is the largest exploit in crypto history. FBI has linked it to North Korea. While Binance covered 95% of funds via SAFU, this incident is a wake-up call for every crypto user. Your security is in YOUR hands, not just the exchange.
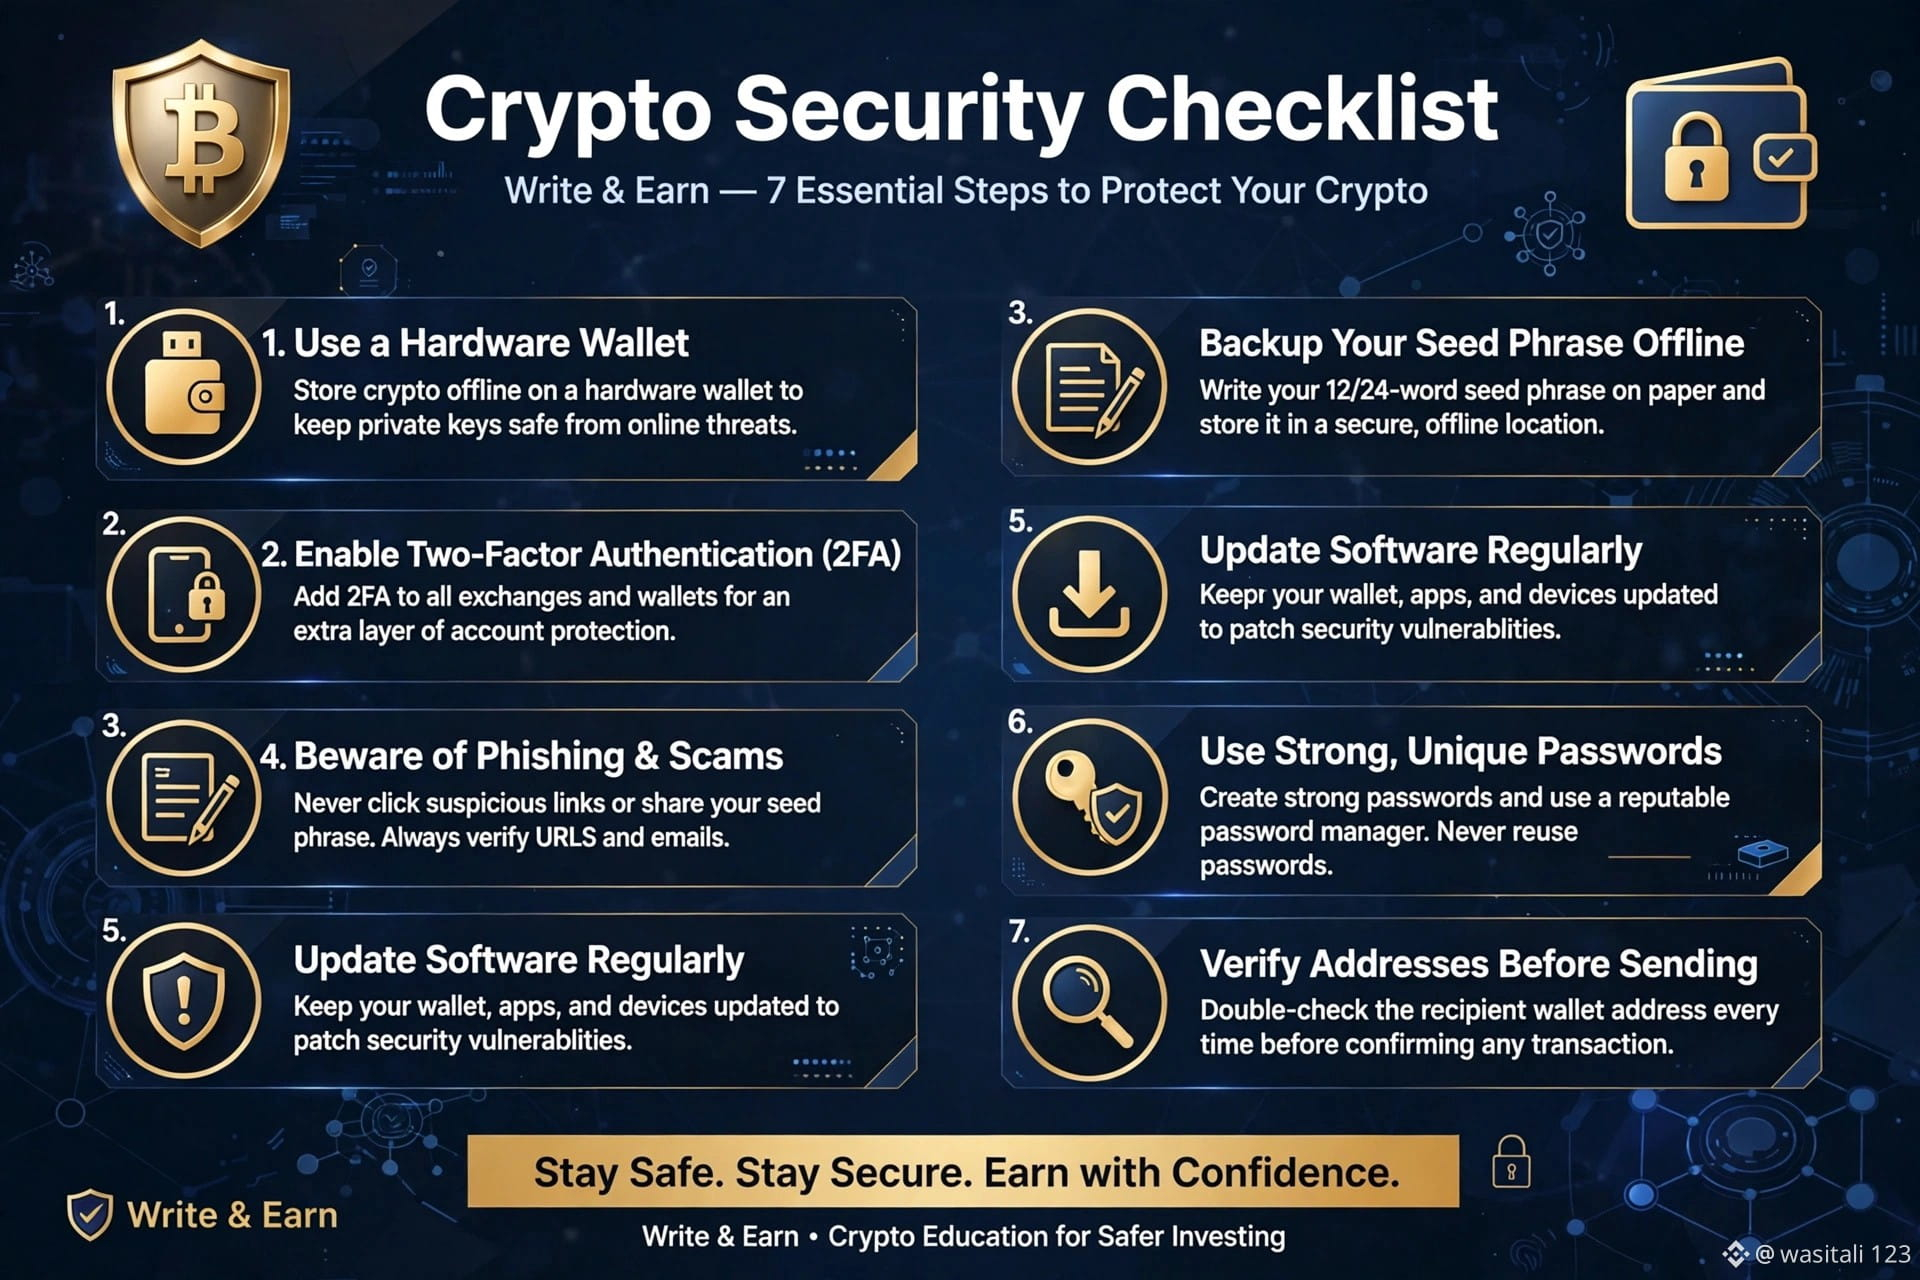
Here are 7 steps I personally follow, and you should too:
*1. Enable Withdrawal Whitelist*
Go to Binance > Security > Withdrawal Whitelist. Turn it ON. Only your personal wallet addresses can withdraw. Even if hacker gets your password, he can't withdraw to his wallet.
*2. Use Passkey + Authenticator, Not Just SMS*
SMS can be SIM-swapped. Use Binance Authenticator App + Passkey + Email code. 3 layers = almost impossible to hack.
*3. Anti-Phishing Code*
Set your anti-phishing code in Binance security. Every real Binance email will show YOUR code. If email doesn't have it, it's fake. Hackers are sending fake Binance emails right now.
*4. 80/20 Rule: Exchange vs Cold Wallet*
Never keep all funds on any exchange. I keep 20% on Binance for trading, 80% in cold wallet (Ledger/Trezor). Not your keys, not your coins.
*5. Don't Click Links from Twitter/Telegram*
After the hack, thousands of fake "Binance refund" links are circulating. Binance will NEVER DM you for refund. Check official Binance Square account only.
*6. Check API Keys & Third-Party Apps*
If you connected any bot, trading app to Binance via API, delete unused APIs now. Many hacks happen via leaked API keys.
*7. Learn On-Chain Hygiene*
Use a separate wallet for airdrops/meme coins. Don't connect your main wallet to every random website. One bad approval can drain your wallet.
*Conclusion:*
Exchanges can be hacked, that's reality of technology. But if you follow these 7 steps, even in worst case, you will be safe. This $6.3B hack taught us one lesson: In crypto, security is profit.
Stay safe. Stay SAFU.
Share this with a
#WriteAndEarn #BinanceSecurity #CryptoSafety #BinanceHack #SAFU #Write2Earn #BTC #CryptoEducation
-
*Introduction:*
The $6.3 billion Binance hack on Oct 29, 2026 is the largest exploit in crypto history. FBI has linked it to North Korea. While Binance covered 95% of funds via SAFU, this incident is a wake-up call for every crypto user. Your security is in YOUR hands, not just the exchange.
Here are 7 steps I personally follow, and you should too:
*1. Enable Withdrawal Whitelist*
Go to Binance > Security > Withdrawal Whitelist. Turn it ON. Only your personal wallet addresses can withdraw. Even if hacker gets your password, he can't withdraw to his wallet.
*2. Use Passkey + Authenticator, Not Just SMS*
SMS can be SIM-swapped. Use Binance Authenticator App + Passkey + Email code. 3 layers = almost impossible to hack.
*3. Anti-Phishing Code*
Set your anti-phishing code in Binance security. Every real Binance email will show YOUR code. If email doesn't have it, it's fake. Hackers are sending fake Binance emails right now.
*4. 80/20 Rule: Exchange vs Cold Wallet*
Never keep all funds on any exchange. I keep 20% on Binance for trading, 80% in cold wallet (Ledger/Trezor). Not your keys, not your coins.
*5. Don't Click Links from Twitter/Telegram*
After the hack, thousands of fake "Binance refund" links are circulating. Binance will NEVER DM you for refund. Check official Binance Square account only.
*6. Check API Keys & Third-Party Apps*
If you connected any bot, trading app to Binance via API, delete unused APIs now. Many hacks happen via leaked API keys.
*7. Learn On-Chain Hygiene*
Use a separate wallet for airdrops/meme coins. Don't connect your main wallet to every random website. One bad approval can drain your wallet.
*Conclusion:*
Exchanges can be hacked, that's reality of technology. But if you follow these 7 steps, even in worst case, you will be safe. This $6.3B hack taught us one lesson: In crypto, security is profit.
Stay safe. Stay SAFU.
Share this with a
#WriteAndEarn #BinanceSecurity #CryptoSafety #BinanceHack #SAFU #Write2Earn #BTC #CryptoEducation
-