



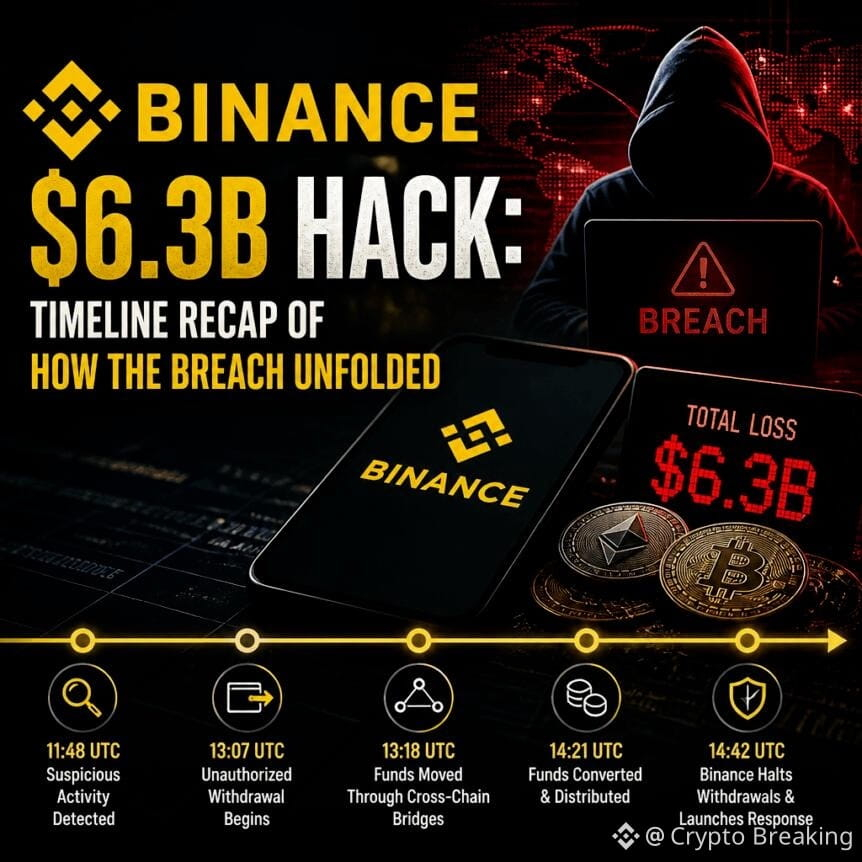
Binance says it has reserved more than $6.34 billion in company funds to cover losses after hackers stole roughly $6.3 billion from the exchange on Thursday, in what TRM Labs has described as the largest cryptocurrency theft on record. Industry partners have frozen about $3 billion in assets believed to be tied to the incident, but customers are still waiting for the exchange to reopen withdrawals.
The exchange’s investigation remains ongoing, and Binance has not publicly confirmed who carried out the attack. Still, blockchain forensics from TRM Labs linked the first unauthorized transfers to North Korea’s TraderTraitor group, which the US FBI previously associated with a $1.5 billion Bybit theft in February 2025.
Key takeaways
TRM Labs traced early unauthorized movements from Binance wallets starting around 8:05 pm UTC Thursday, spanning multiple blockchains.
Binance reserved over $6.34 billion to cover losses, including $5 billion already held in affected tokens, while the remaining coverage relies on purchases via exchanges and over-the-counter deals.
Frozen funds are not the same as recovered funds, and Binance has not disclosed how much of the stolen crypto is already back under its control.
Ethereum’s EIP-7702 is at the center of scrutiny after Binance-linked wallets were drained using an EIP-7702 delegation.
Withdrawals remain suspended; Binance says it plans to reopen them in stages on Sunday, Nov. 1, after security checks.
Forensics point to TraderTraitor as Binance wallets emptied
According to TRM Labs, the first unauthorized transfers were detected around 8:05 pm UTC Thursday. Its tracing indicates that Binance wallets were drained across multiple networks rather than being contained to a single blockchain. TRM characterizes the incident as targeting hot wallets—systems exchanges keep online to process withdrawals—which can increase operational efficiency but also broaden the attack surface if signing systems or access controls are compromised.
TRM Labs attributed the attack to North Korea’s TraderTraitor group. That attribution aligns with the US Federal Bureau of Investigation’s earlier public framing of TraderTraitor in connection with the $1.5 billion Bybit theft in February 2025. Binance has not independently confirmed the attackers’ identity, and its co-CEO Richard Teng emphasized that the company has not assigned responsibility to any individual.
Binance also addressed how the breach unfolded, saying it was not the result of a simple “one-click” permission misuse by a single engineer. In Teng’s words, investigators are still working to understand the broader scope of the intrusion, and the exchange has not attributed responsibility to any individual.
Binance sets aside $6.34B, but recovery remains unclear
Binance stated that it reserved more than $6.34 billion in company funds to cover losses. The exchange said $5 billion of that amount was already held in the affected tokens, with the rest covering the shortfall through token purchases conducted via exchanges and over-the-counter arrangements.
A Binance spokesperson told Cointelegraph that the $5 billion was held in the company’s custody, but declined to provide wallet addresses due to security concerns. CertiK, in turn, said it needed additional information to independently verify the holdings. This distinction matters for market participants: without independent visibility into custody and token balances, even well-intentioned proof-of-reserves narratives can be difficult for third parties to validate quickly during an active incident.
Binance’s communication also highlights an important nuance for customers and counterparties. Frozen funds are not necessarily recovered funds. While roughly $3 billion worth of assets were frozen by industry partners, Binance has not yet detailed how much of the stolen crypto has returned to its control.
Ethereum’s EIP-7702 in the spotlight after the delegation drain
While the theft centered on Binance wallets, technical attention has shifted to Ethereum’s EIP-7702. Cointelegraph reported earlier that the upgrade came under scrutiny after attackers used it to drain a Binance wallet. EIP-7702 enables a wallet to authorize software to act on its behalf, and that has raised questions about how delegations interact with exchange-specific approval and safety procedures.
Blockaid CEO Ido Ben-Natan told Cointelegraph that compromised signing systems likely played a central role in enabling the theft. He added that the attackers could potentially have stolen funds without EIP-7702, but the mechanism may have helped bypass certain safeguards and execute the theft in a more coordinated manner.
Binance co-CEO Richard Teng said investigators found that the attacker used an EIP-7702 delegation to gain execution authority over a hot wallet without going through Binance’s normal approval controls. Teng also pointed to a “self-destruct mechanism” that destroyed tools and traces, which he said complicated the investigation.
Binance further stated that investigators discovered additional breaches beyond the initially suspected compromised laptop. The exchange reported no evidence that wallet private keys had leaked and said it expects to share further technical findings within about 48 hours.
Separately, Chainalysis observed thousands of transactions in quick succession that could indicate automated laundering behavior. The pattern—funds moving between addresses and sometimes returning to wallets previously used—has often been seen in attempts to obfuscate provenance during large-scale hacks, though the precise classification of intent and the full route of funds may only become clearer as tracing continues.
Withdrawals and liquidity actions: Aave reopens, Binance schedules a phased return
The hack has spilled into broader market plumbing. Following the theft, precautionary measures included a freeze on new deposits and borrowing activity at decentralized lender Aave. Cointelegraph reported that Aave reopened its markets Friday afternoon, while Binance withdrawals remained suspended.
In a Friday update posted on social media, Binance said it intended to begin reopening withdrawals in stages on Sunday, Nov. 1, subject to completing security checks. The exchange also indicated that deposits and other services believed to be unaffected would continue operating.
Alongside the withdrawal plan, Binance said it would take an initial proof-of-reserves snapshot within 12 hours of the announcement, with results scheduled to be ready by Monday. The goal of the report is to demonstrate which assets Binance holds and how they back customer balances.
For users and traders, the immediate question is not only whether withdrawals return on schedule, but also whether the exchange can provide credible, verifiable transparency quickly enough to restore confidence. Given the scale of the theft, even incremental updates about custody, recovery progress, and the technical lessons tied to hot-wallet controls and delegated execution will likely drive how fast market confidence recovers.
As Binance completes its security checks and publishes further technical findings, readers should watch for three things: confirmation of the withdrawal reopening timeline, independent validation of the company’s reserve disclosures, and updated details on how much of the stolen crypto has actually been recovered or is still moving through the system.
This article was originally published as Binance $6.3B Hack: Timeline Recap of How the Breach Unfolded on Crypto Breaking News – your trusted source for crypto news, Bitcoin news, and blockchain updates.