

🚨 Aave V3 Module Exploit Drains Around 114 ETH 👀
Another DeFi security incident is getting attention on-chain.
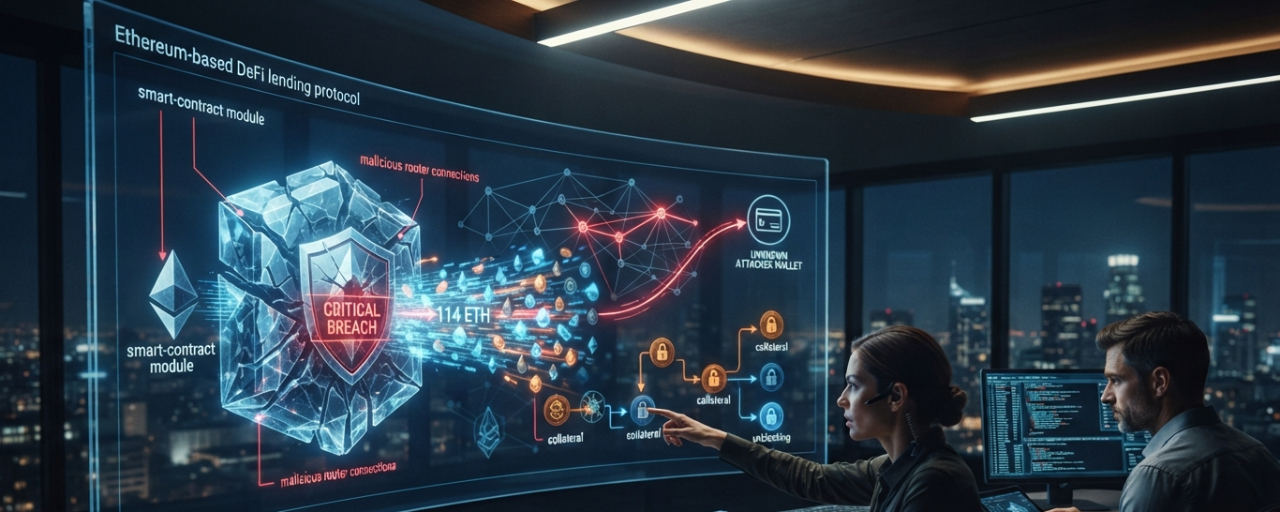
A security alert linked the incident to an Aave V3 Loop Safe Module, where an attacker reportedly bypassed an authentication check and gained the ability to execute a malicious transaction.
The wallets involved reportedly lost around 114.09 ETH, along with other collateral connected to the positions.
What makes the transaction interesting is the way the attacker handled the debt.
Instead of simply taking the collateral immediately, the attacker reportedly repaid roughly 1,300 WETH of outstanding debt first. That allowed the locked collateral to become withdrawable.
So the key part of this incident isn't only the amount stolen. It's the attack path:
• Authentication validation was bypassed
• An attacker-controlled router was used
• Debt was repaid to unlock collateral
• The newly movable assets were then targeted
This is a good reminder that in DeFi, the visible position isn't always the real target. The underlying transaction flow and permission system can matter just as much.
For $AAVE and the wider DeFi sector, incidents like this highlight why smart-contract permissions, module design and transaction validation remain critical.
Worth watching how the affected contracts and protocols respond from here.
Security commentary only, not financial advice. Always verify contract and wallet activity independently.

