Most systems still treat verification like a one time event.
But in reality, trust is something you carry not something you redo.
That’s what makes Sign interesting to me. It turns verification into something reusable, almost like a personal layer you build over time. One attestation can unlock multiple actions without exposing everything again.
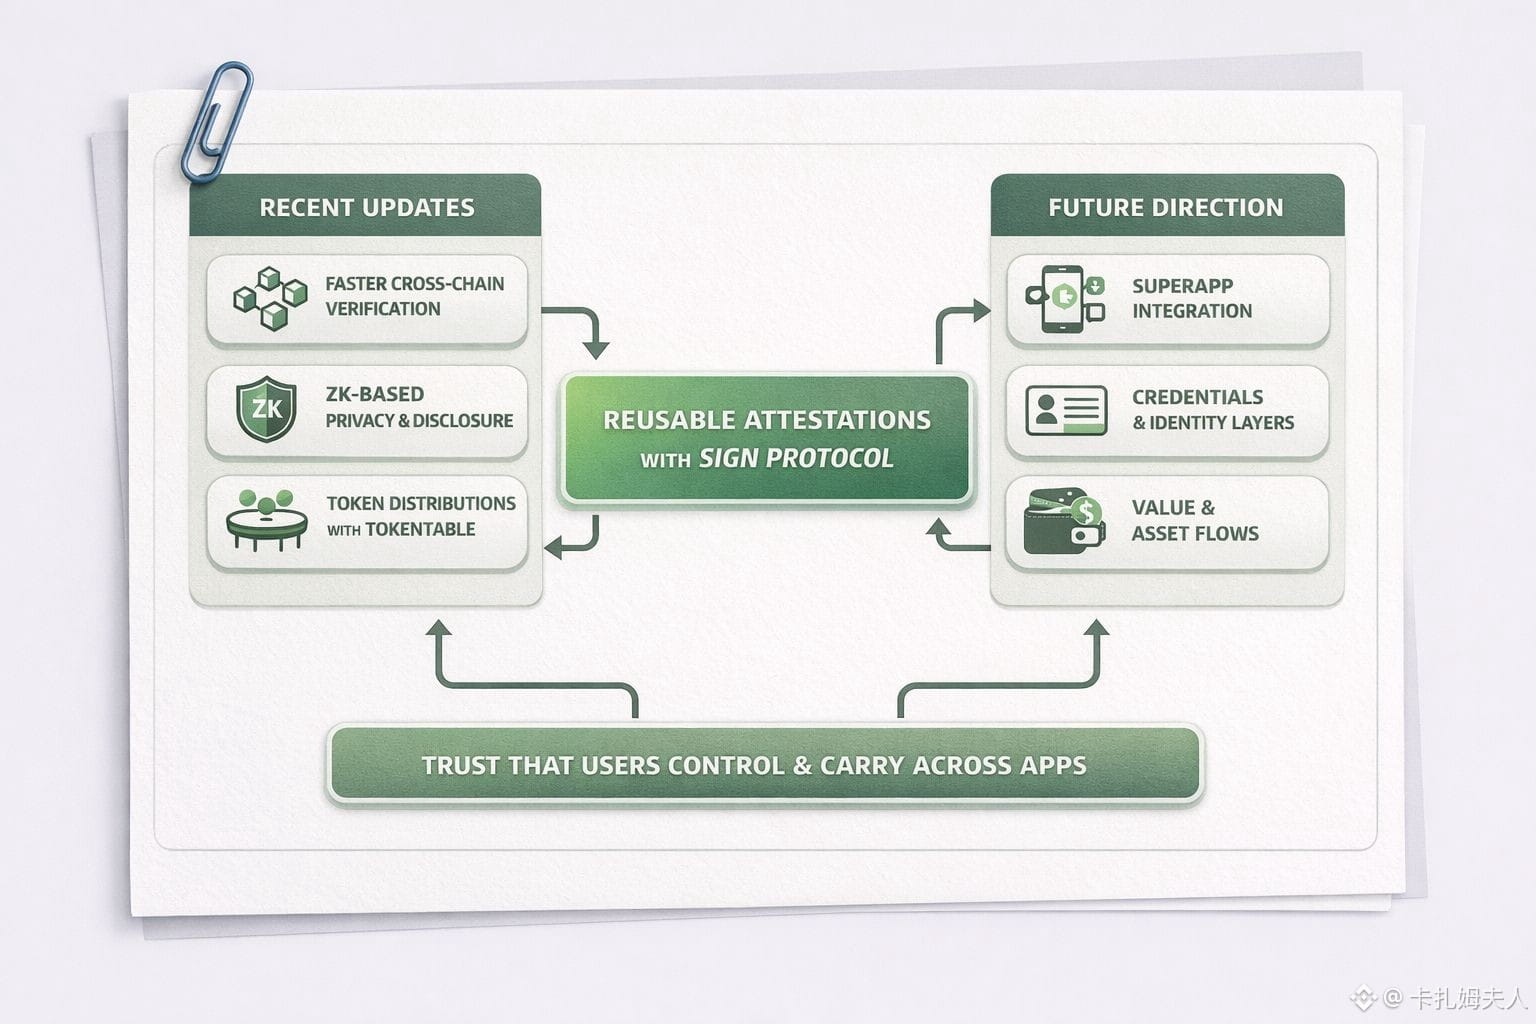
What stands out recently is how this idea is becoming more practical. With updates improving cross chain speed and privacy (especially with ZK-based selective disclosure), and tools like TokenTable already handling large scale, rule-based distributions, it’s moving beyond theory into actual usage.
The upcoming SuperApp direction also feels important not because it adds features, but because it might finally connect identity, credentials, and value flows in one place.
For me, the exciting part isn’t just verification.
It’s the idea that trust becomes composable something apps can build on, and users can carry with control.
Are you curious how others see it is reusable trust the missing piece in Web3 UX?
@SignOfficial $SIGN #SignDigitalSovereignInfra
But in reality, trust is something you carry not something you redo.
That’s what makes Sign interesting to me. It turns verification into something reusable, almost like a personal layer you build over time. One attestation can unlock multiple actions without exposing everything again.
What stands out recently is how this idea is becoming more practical. With updates improving cross chain speed and privacy (especially with ZK-based selective disclosure), and tools like TokenTable already handling large scale, rule-based distributions, it’s moving beyond theory into actual usage.
The upcoming SuperApp direction also feels important not because it adds features, but because it might finally connect identity, credentials, and value flows in one place.
For me, the exciting part isn’t just verification.
It’s the idea that trust becomes composable something apps can build on, and users can carry with control.
Are you curious how others see it is reusable trust the missing piece in Web3 UX?
@SignOfficial $SIGN #SignDigitalSovereignInfra