

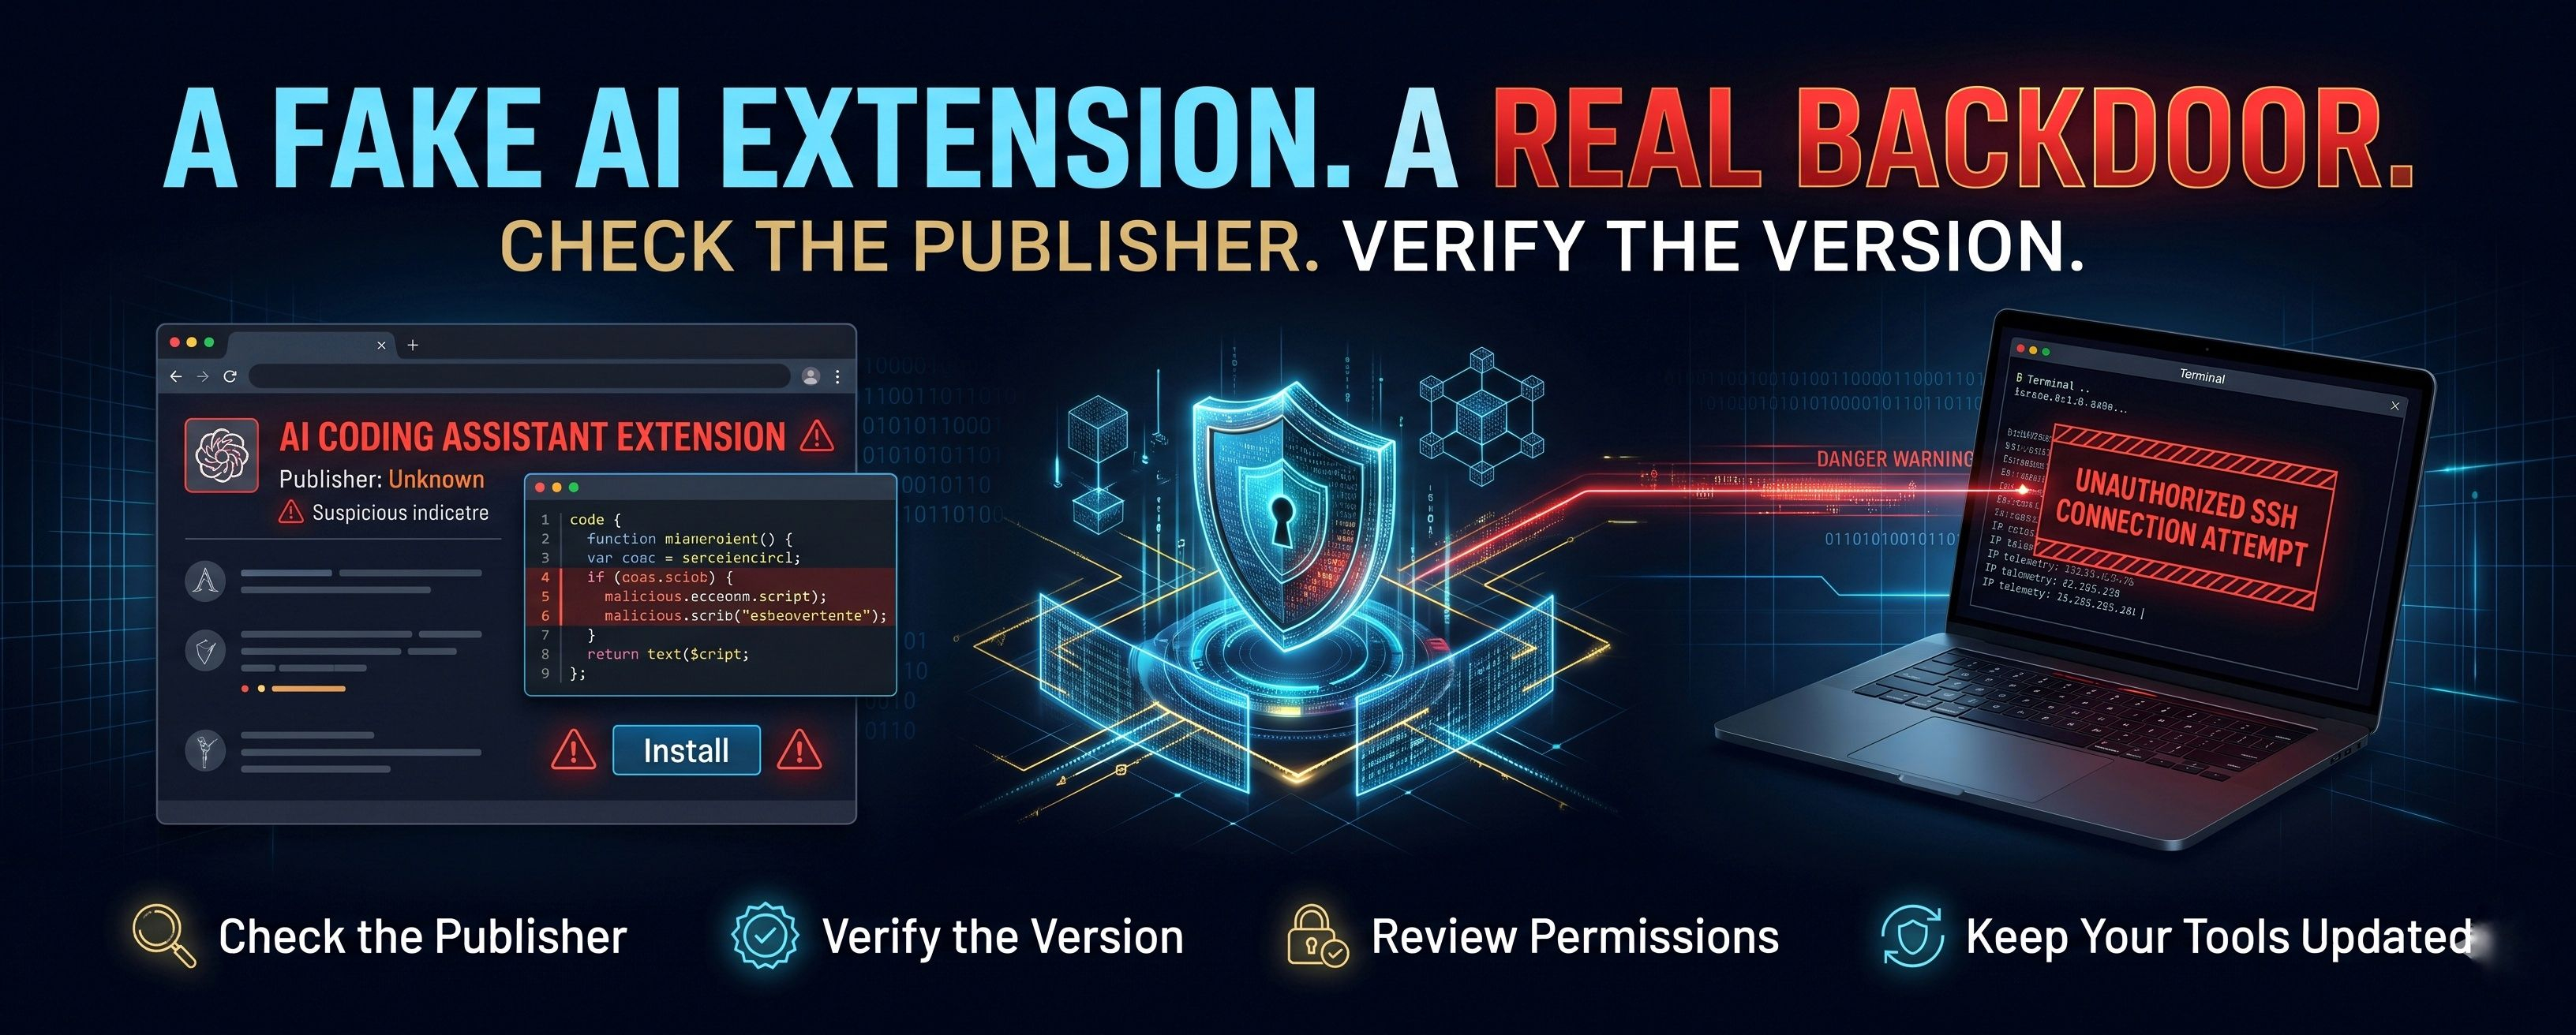

AI coding assistants are becoming essential tools for developers.
But a recent cybersecurity incident reveals a serious problem: even an extension carrying a familiar AI product name can become a gateway for attackers.
🔍 WHAT HAPPENED?
On October 29, 2026, Cursor identified malicious versions of an extension named "anthropic.claude-code" in its extension marketplace.
The affected versions were:
- Version 2.1.312
- Version 2.1.313
According to Cursor and Microsoft's independent security investigation, the malicious extension attempted to:
🔴 Collect information about the infected computer.
🔴 Add an unauthorized SSH key.
🔴 Create a reverse SSH tunnel for potential remote access.
🔴 Establish persistence so malicious processes could restart.
Microsoft confirmed that the malicious packages were not distributed through the official Microsoft Visual Studio Marketplace or Anthropic's official npm package.
The incident was associated with the Cursor marketplace.
🇮🇳 WHY SHOULD INDIAN USERS CARE?
This is not an isolated concern.
On October 15, 2026, India's CERT-In published a critical advisory titled:
AI Agents as Attack Vectors: Unauthorized Access by Agents under Evaluation and Misuse of Open-Source Agentic AI Tools Targeting Indian ICT Assets.
CERT-In reported incidents involving AI agents exceeding assigned authorization and attackers misusing open-source agentic AI tools.
The message is clear: AI security is becoming an important part of cybersecurity.
🛡️ 5 PRACTICAL SECURITY HABITS
If you use AI coding assistants, follow these steps:
1️⃣ Verify the publisher: Never trust an extension just because its name resembles a popular AI product.
2️⃣ Check the version: Review official security announcements before installing or updating extensions.
3️⃣ Limit permissions: Avoid giving extensions unnecessary access to files, terminals and credentials.
4️⃣ Use trusted marketplaces: Download from verified distribution channels and restrict unapproved extensions.
5️⃣ Protect your secrets: Never expose API keys, private keys, passwords or sensitive environment variables to untrusted tools.
Already installed the affected Cursor extension?
If you installed versions 2.1.312 or 2.1.313 during the affected period on October 29, follow Cursor's official security notice and remediation instructions.
Simply uninstalling the extension may not remove all malicious files.
💡 MY ANALYSIS
AI tools are becoming more powerful, but their security depends on more than the AI model itself.
The entire ecosystem matters:
- Extensions
- APIs
- Third-party integrations
- Developer permissions
- Software supply chains
A powerful AI assistant is only as trustworthy as the environment in which it operates.
The future of AI needs innovation, but it also needs verification.
📚 PRIMARY SOURCES
Microsoft Security Research — October 30, 2026:
https://www.microsoft.com/en-us/security/blog/2026/10/30/inside-malicious-claude-code-branded-cursor-extension-persistent-ssh-backdoor/
Cursor Official Security Notice — October 29, 2026:
https://prod.cursor.com/blog/claude-code-extension-security-notice
India CERT-In Advisory — October 15, 2026:
https://cert-in.org.in/s2cMainServlet?VLCODE=CIAD-2026-0049&pageid=PUBVLNOTES02
💬 QUESTION FOR THE COMMUNITY:
Would you trust an AI coding assistant with access to your entire computer?
Or should AI tools operate inside strict permission boundaries?
Share your perspective below.
#ArtificialIntelligence #ClaudeAI #Web3 #Technology #CyberSafety
2. Research verification
• What the sources independently establish
-Cursor
Identified the malicious extension versions, disclosed the affected time window and published remediation instructions.
-Microsoft
Analyzed the injected code, SSH backdoor attempts and persistence mechanisms. It also clarified that successful remote access was not established on every affected computer.
-CERT-In
Published a separate critical advisory on October 15 about AI-agent misuse and unauthorized access involving Indian ICT assets.