
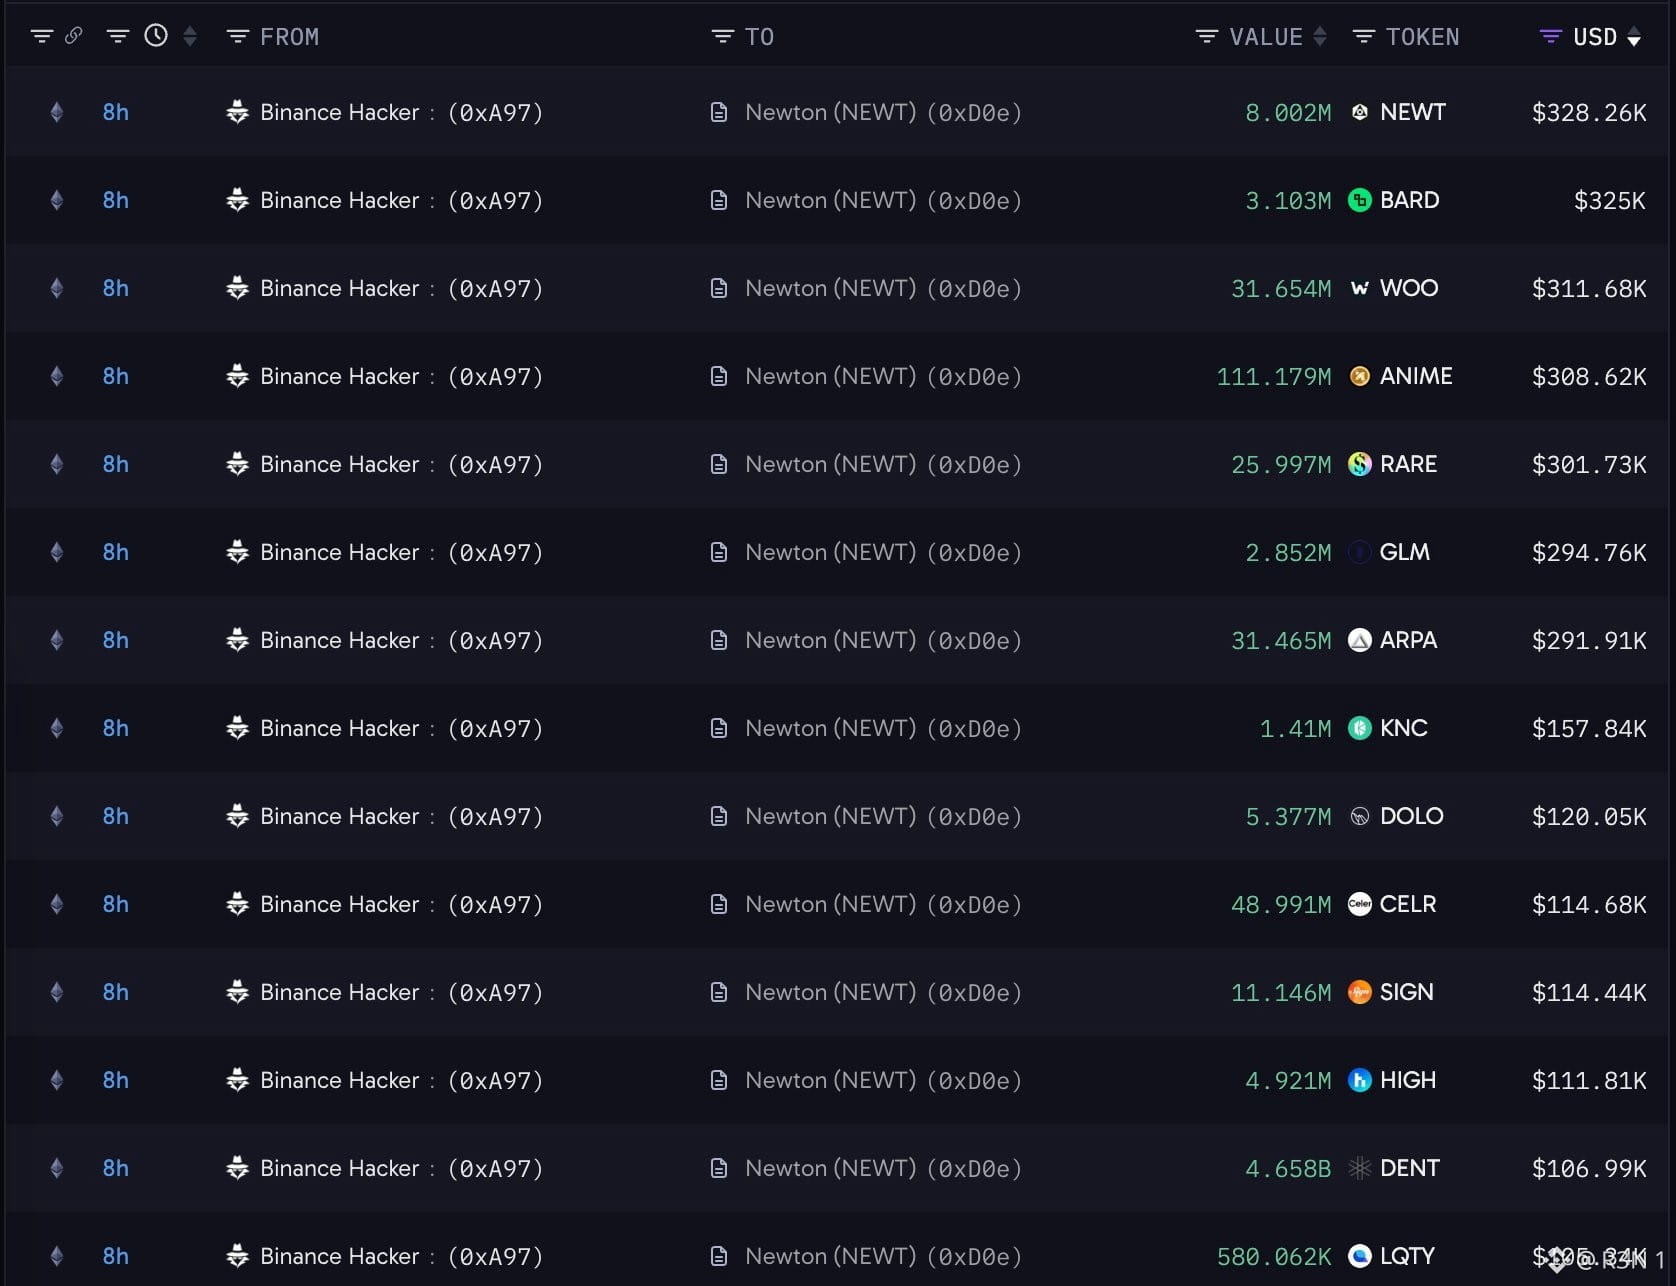
The Binance hacker made a $3.5M mistake, and nobody can undo it. The Newton Foundation says the attacker behind the Binance theft appears to have sent roughly 8 million NEWT plus 17 other tokens directly to the NEWT token contract address, worth about $3.5 million at current prices. The contract itself wasn't compromised. It's immutable, with no owner or administrator, and all management rights were relinquished on-chain in 2025, so no one, including the foundation, can retrieve the tokens. The same design that protects holders from an admin rug is what makes these funds gone for good. In crypto, "no one can touch it" cuts both ways. It also fits the pattern of a thief in a hurry. The attacker dumped altcoins including UNI, ENA, PEPE, LINK, AAVE, ONDO and WLD for about $158M worth of ETH, with Tether and Circle already freezing large stablecoin balances. Fast, stressed operations are where wrong-address mistakes happen. Keep the scale in mind, though. $3.5M against an estimated $6.3B impact, with about $3B frozen on-chain, is a rounding error. Crypto timelines love poetic justice, and a clumsy thief feels like the plot turning. It isn't. The real story is still custody, trust, and how Binance covers the loss. The risk is reading too much into it. The foundation says the attacker "appears" to have erred, which is an on-chain reading, not a final finding. The bullish angle is small but real: these tokens are effectively locked, and the contract's design held up under unusual pressure. Even the most planned heist can end in a dead-end address. Crypto has no undo button, for victims or thieves. $SOL #BTC Price Analysis# #Altcoin Season# $BNB

Bergabunglah dengan pengguna kripto global di Binance Square
⚡️ Dapatkan informasi terbaru dan berguna tentang kripto.
💬 Dipercayai oleh bursa kripto terbesar di dunia.
👍 Temukan wawasan nyata dari kreator terverifikasi.
Email/Nomor Ponsel