🚨 KREMLIN Malware hitting Brazil hard — 1,515+ infected hosts, 98.75% Brazilian IPs
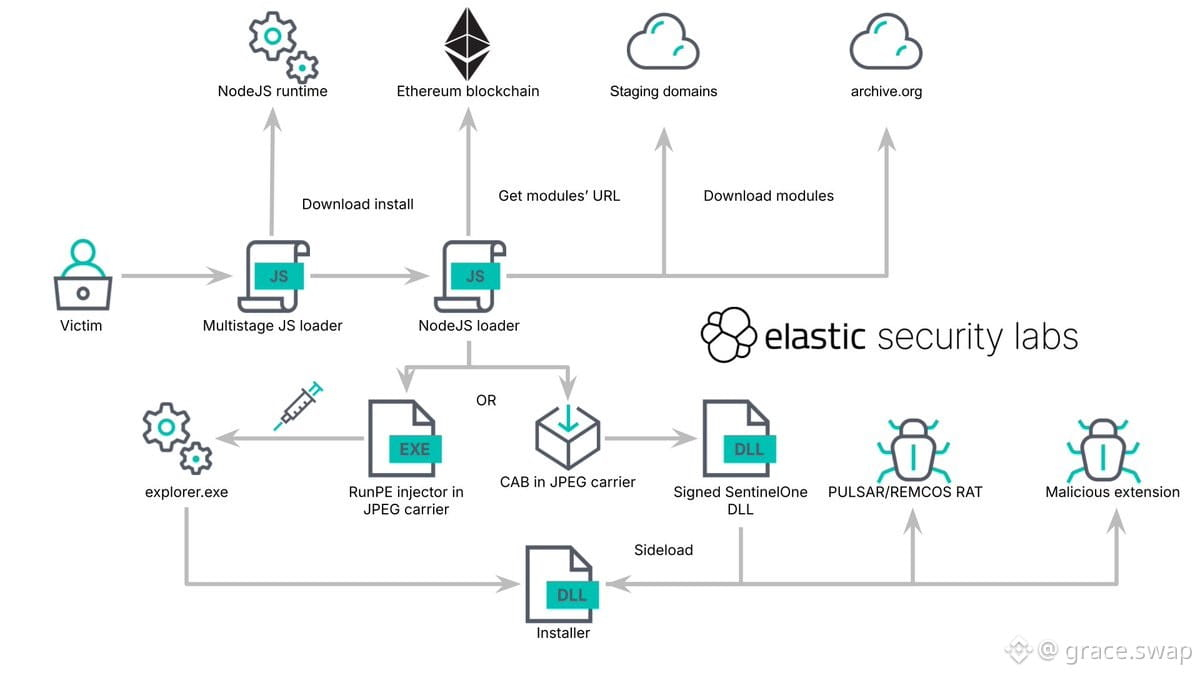
Brazilian banking op REF9334 running since May 2025. Multi-stage loaders + malicious browser extensions stealing creds, session tokens, sensitive data.
The scary part: Extensions auto-install on Chrome/Edge WITHOUT user approval by bypassing Chromium integrity (Secure Preferences, HMACs, App-Bound encryption)
They're using $ETH smart contracts as dead-drop resolvers to rotate C2 endpoints and payload hosts — makes takedowns way harder
Active contract:
0xCD7360A83E5cdbBbbbcEB0e78748babA6740d07b
Admin wallet:
0x5C32A09873be70a92fd8bB5A9fED7967dE06BdE6
If you're in Brazil or running security ops, watch for suspicious browser extension activity and monitor these on-chain addresses. This is next-level infra abuse.
Stay paranoid. Check your extensions.
Brazilian banking op REF9334 running since May 2025. Multi-stage loaders + malicious browser extensions stealing creds, session tokens, sensitive data.
The scary part: Extensions auto-install on Chrome/Edge WITHOUT user approval by bypassing Chromium integrity (Secure Preferences, HMACs, App-Bound encryption)
They're using $ETH smart contracts as dead-drop resolvers to rotate C2 endpoints and payload hosts — makes takedowns way harder
Active contract:
0xCD7360A83E5cdbBbbbcEB0e78748babA6740d07b
Admin wallet:
0x5C32A09873be70a92fd8bB5A9fED7967dE06BdE6
If you're in Brazil or running security ops, watch for suspicious browser extension activity and monitor these on-chain addresses. This is next-level infra abuse.
Stay paranoid. Check your extensions.