🚨 $7.73M $rsETH DRAINED FROM SAFE WALLET ON ETH
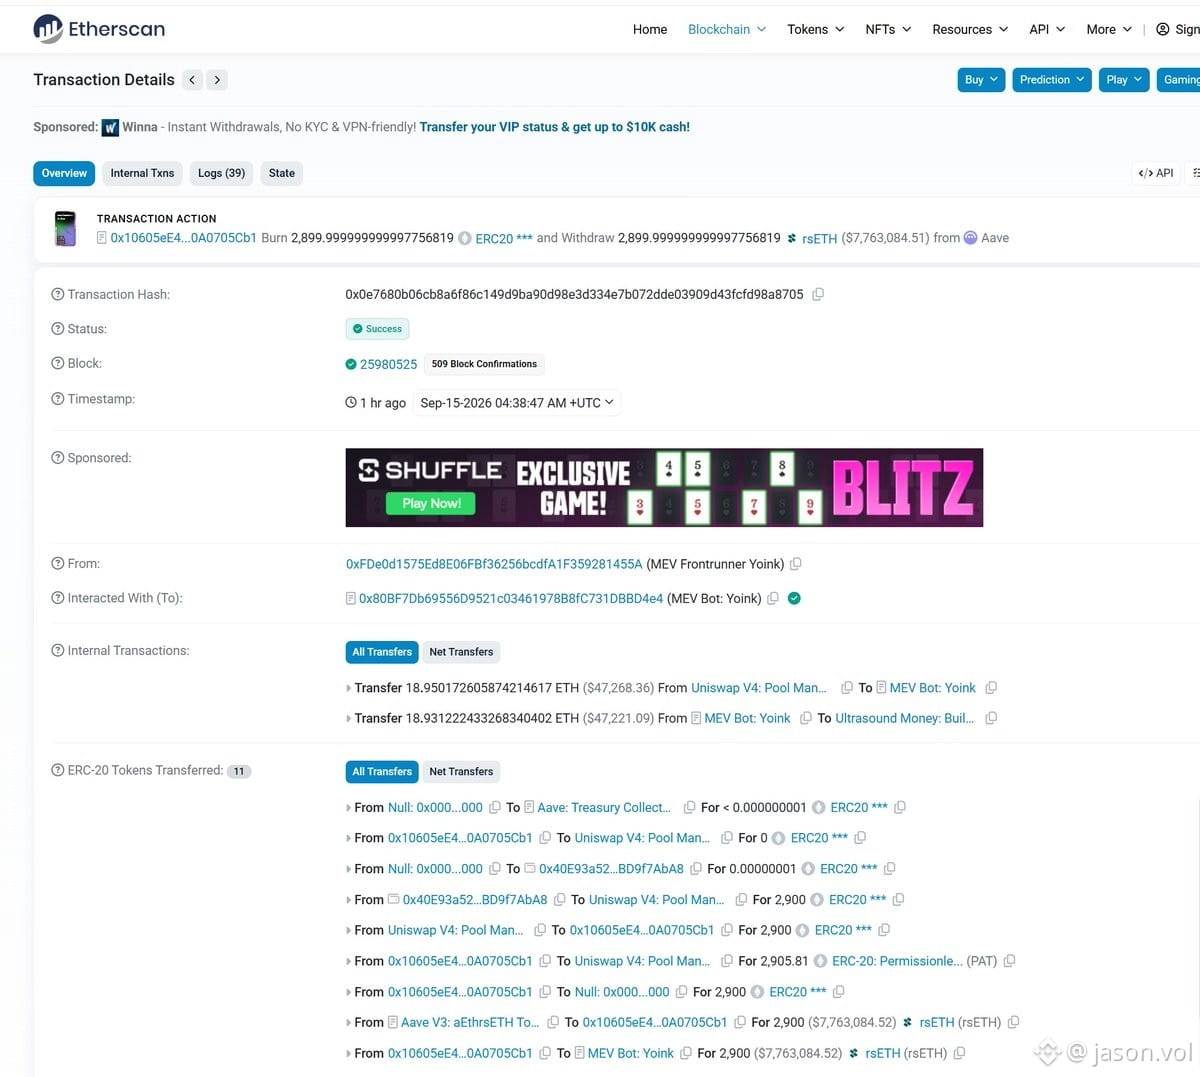
Blockaid detected a sophisticated attack on an unknown user's Safe wallet - attacker exploited a public keeper multicall to redirect a custom Uniswap V4 LP Safe module to a malicious Hook pool.
The Hook unwrapped aEthrsETH → $rsETH, then got Yoinked by MEV bot in the same block. Clean heist.
Kelp DAO responded fast:
→ Flagged suspicious activity on the affected address
→ Implemented 24hr emergency pause (no $rsETH transfers in/out)
→ Core contracts safe, collateral intact
→ Minting/withdrawals/integrations still operational
No user action needed. But this is a reminder: Safe multisigs aren't bulletproof if you're running custom modules with exposed keepers. Always audit your execution paths.
Blockaid detected a sophisticated attack on an unknown user's Safe wallet - attacker exploited a public keeper multicall to redirect a custom Uniswap V4 LP Safe module to a malicious Hook pool.
The Hook unwrapped aEthrsETH → $rsETH, then got Yoinked by MEV bot in the same block. Clean heist.
Kelp DAO responded fast:
→ Flagged suspicious activity on the affected address
→ Implemented 24hr emergency pause (no $rsETH transfers in/out)
→ Core contracts safe, collateral intact
→ Minting/withdrawals/integrations still operational
No user action needed. But this is a reminder: Safe multisigs aren't bulletproof if you're running custom modules with exposed keepers. Always audit your execution paths.