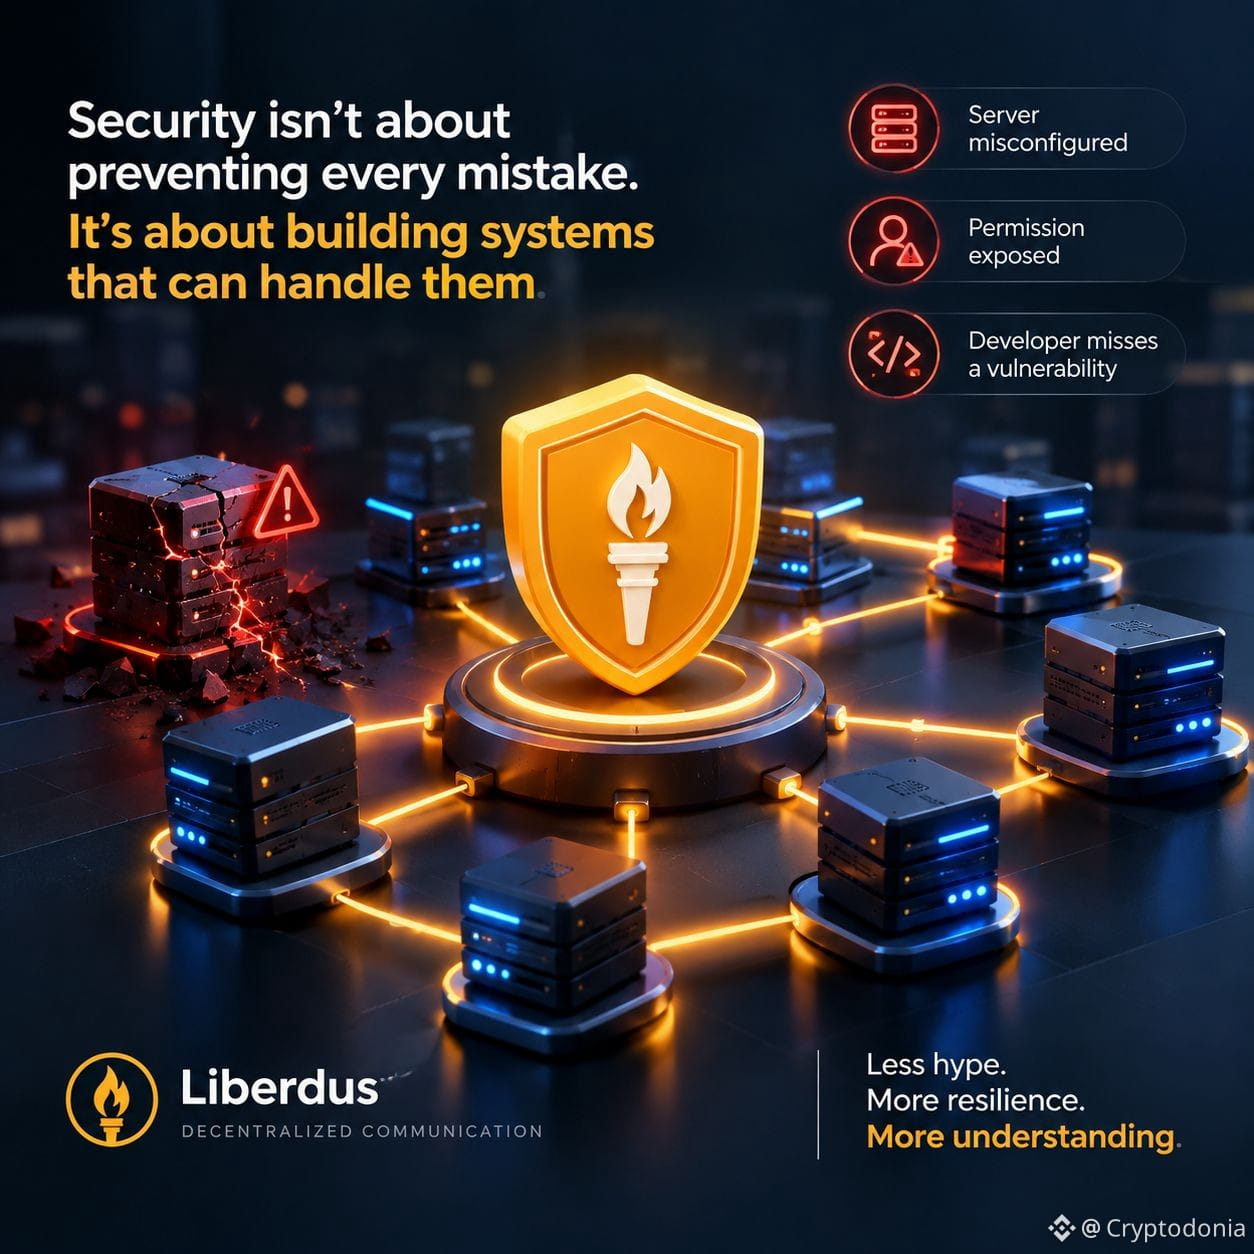
What if the real test of security isn't preventing every mistake, but making sure one mistake doesn't bring down the entire system? A server gets misconfigured. A permission gets exposed. A developer misses a vulnerability. Sometimes, it takes just one mistake to create a problem affecting thousands of users. That's why I believe security isn't just about stopping hackers. It's also about how a system is designed to handle failure. Because mistakes are inevitable. Catastrophic failure shouldn't be the default. This is where decentralization becomes an interesting conversation. Distributing infrastructure can reduce certain points of concentration, but it doesn't make a system invulnerable. Bugs, compromised nodes, and human errors can still happen. That's one reason @Liberdus interests me. Decentralized communication raises an important question: how do we build systems that give people more control while remaining resilient when things go wrong? I don't believe in selling perfection. I believe in understanding the architecture, acknowledging the trade-offs, and asking the right questions. Because real trust isn't built on promises of perfect security. It's built on systems designed with failure in mind. Less hype. More resilience. More understanding. #Security $KII #Privacy $QNT


Publier
Avertissement : ce contenu inclut des opinions de tiers. Il ne constitue pas un conseil. Binance Ai peut être utilisée, sans garantie de résultat. Consultez les CG.