

#walletsecurity
walletsecurity
168,933 vues
366 mentions
Populaire
Récents

Binance is sounding the alarm on address poisoning scams. Scammers are mimicking your past transaction history to bait you into sending funds to their fake addresses. Double check every single character before hitting send.
#AddressPoisoning #WalletSecurity
Binance is sounding the alarm on address poisoning scams. Scammers are mimicking your past transaction history to bait you into sending funds to their fake addresses. Double check every single character before hitting send.
#AddressPoisoning #WalletSecurity
#AddressPoisoning #WalletSecurity
2

·
--
Read Wallet Security BadgesAn EAL5+ or EAL6+ label can be a useful security signal, but it should start a due-diligence question rather than end one.
First identify the target of the evaluation. A wallet may use a secure element with a Common Criteria rating. That tells you something about the assessed chip and its resistance under a defined scope. It does not automatically certify the entire device, firmware, bootloader, companion app, transaction parser, recovery process, manufacturing controls and every future update.
Use four questions for every badge: who issued it, what exact component was evaluated, which model and version were covered, and when the evaluation happened? Look for a certificate identifier, security target, evaluation report or audit scope. If a vendor cites an independent audit, check whether the report is available, whether findings were fixed and whether remediation was verified.
Then review the layers outside the badge. Examine firmware transparency, signed-update controls, vulnerability disclosure, bug-bounty coverage, trusted-screen clarity, recovery architecture and official purchase channels. A strong physical security component cannot stop a user from approving a malicious request or exposing recovery material.
TokenToolHub’s guide shows how to separate useful assurance evidence from vague security marketing:
https://tokentoolhub.com/wallet-security-certifications/
#WalletSecurity #HardwareWallets #CryptoSecurity #SelfCustody #CyberSecurity
Read Wallet Security Badges
An EAL5+ or EAL6+ label can be a useful security signal, but it should start a due-diligence question rather than end one.
First identify the target of the evaluation. A wallet may use a secure element with a Common Criteria rating. That tells you something about the assessed chip and its resistance under a defined scope. It does not automatically certify the entire device, firmware, bootloader, companion app, transaction parser, recovery process, manufacturing controls and every future update.
Use four questions for every badge: who issued it, what exact component was evaluated, which model and version were covered, and when the evaluation happened? Look for a certificate identifier, security target, evaluation report or audit scope. If a vendor cites an independent audit, check whether the report is available, whether findings were fixed and whether remediation was verified.
Then review the layers outside the badge. Examine firmware transparency, signed-update controls, vulnerability disclosure, bug-bounty coverage, trusted-screen clarity, recovery architecture and official purchase channels. A strong physical security component cannot stop a user from approving a malicious request or exposing recovery material.
TokenToolHub’s guide shows how to separate useful assurance evidence from vague security marketing:
https://tokentoolhub.com/wallet-security-certifications/
#WalletSecurity #HardwareWallets #CryptoSecurity #SelfCustody #CyberSecurity
25
Duelbits crypto casino has gone offline following a $7 million hot wallet exploit. This massive security breach underscores the significant risks centralized crypto platforms face from targeted hacks.
#DuelbitsHack #WalletSecurity
Duelbits crypto casino has gone offline following a $7 million hot wallet exploit. This massive security breach underscores the significant risks centralized crypto platforms face from targeted hacks.
#DuelbitsHack #WalletSecurity
#DuelbitsHack #WalletSecurity
8
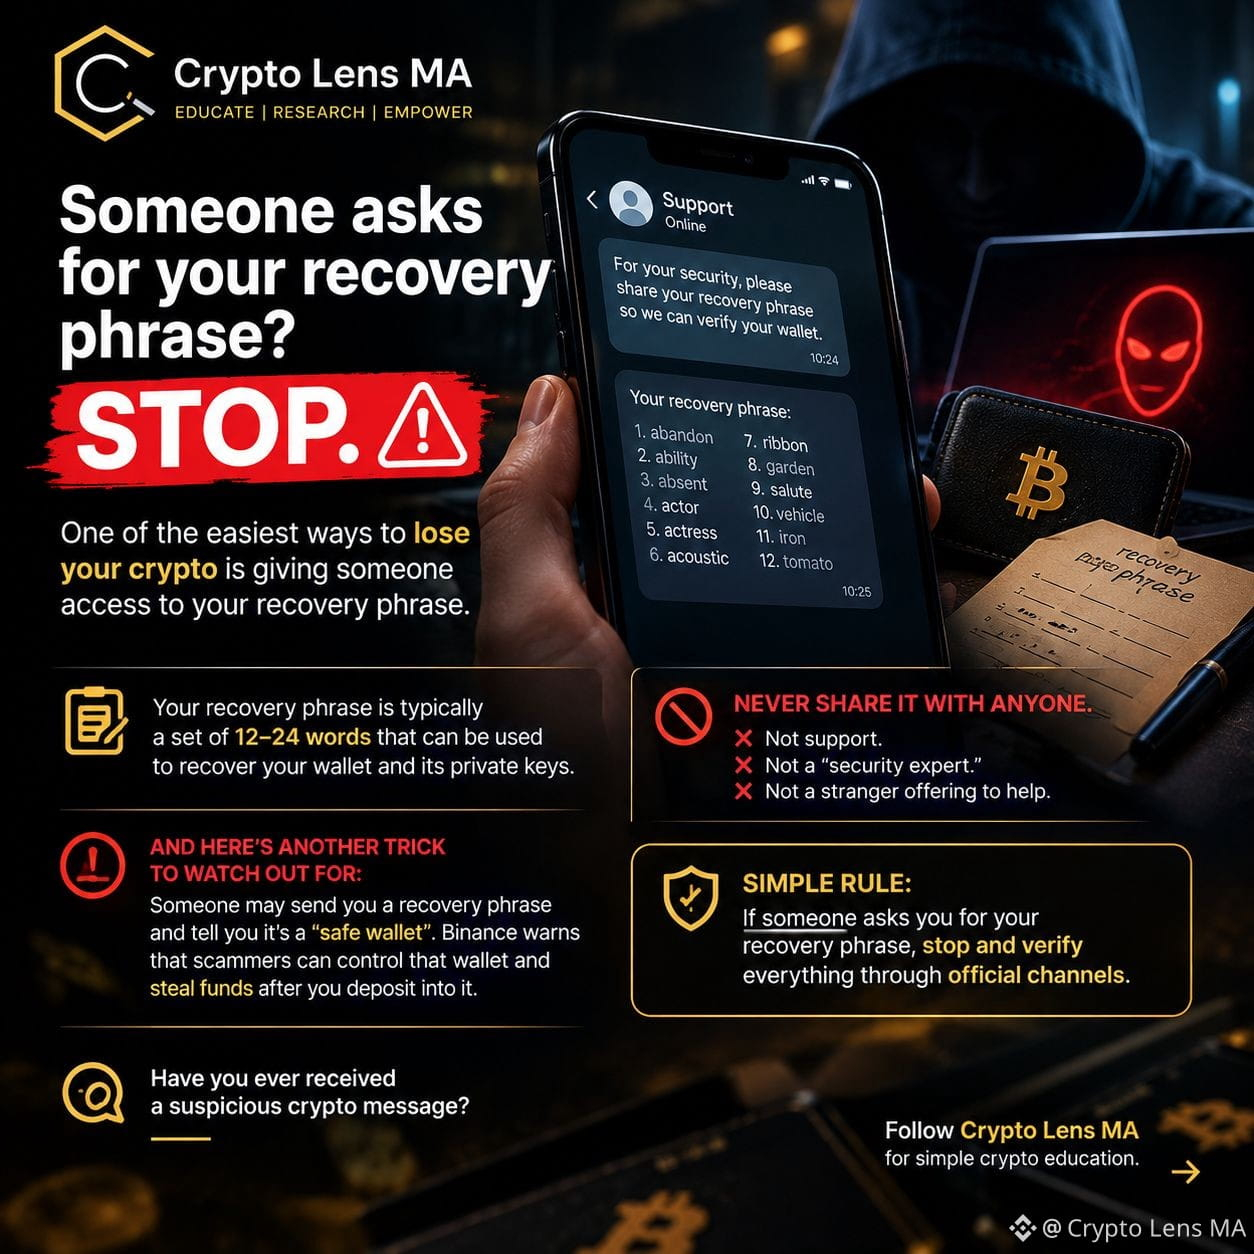
Someone asks for your recovery phrase? STOP. 🚨
One of the easiest ways to lose your crypto is giving someone access to your recovery phrase.
Your recovery phrase is typically a set of 12–24 words that can be used to recover your wallet and its private keys.
🔴 Never share it with anyone.
Not support.
Not a “security expert.”
Not a stranger offering to help.
And here's another trick to watch out for:
Someone may send you a recovery phrase and tell you it's a “safe wallet”. Binance warns that scammers can control that wallet and steal funds after you deposit into it.
Simple rule: If someone asks you for your recovery phrase, stop and verify everything through official channels. 🔐
Have you ever received a suspicious crypto message?
#CryptoSecurity #Cryptoscam #crypto #blockchain #WalletSecurity
136
A Web3 wallet provider reported a security breach, warning the XRP community to move assets immediately. This exploit puts user funds at significant risk if they do not act quickly.
#XRP #WalletSecurity
A Web3 wallet provider reported a security breach, warning the XRP community to move assets immediately. This exploit puts user funds at significant risk if they do not act quickly.
#XRP #WalletSecurity
#XRP #WalletSecurity
16
A simple coding error allowed a hacker to drain $7.8 million from a crypto wallet. This catastrophic exploit highlights the extreme risks of even minor security oversights in digital asset management.
#SecurityVulnerability #WalletSecurity
A simple coding error allowed a hacker to drain $7.8 million from a crypto wallet. This catastrophic exploit highlights the extreme risks of even minor security oversights in digital asset management.
#SecurityVulnerability #WalletSecurity
#SecurityVulnerability #WalletSecurity
5
🚨 ¿SABÍAS QUE UNA APROBACIÓN PUEDE REPRESENTAR UN RIESGO?
Cuando interactuás con determinados protocolos, podés otorgar permiso a un contrato para gastar determinados tokens de tu wallet.
El problema aparece cuando:
❌ Otorgás permisos ilimitados.
❌ Dejás aprobaciones antiguas que ya no utilizás.
❌ Interactuás con contratos comprometidos.
Por eso, una buena práctica es revisar periódicamente las aprobaciones de tus wallets y revocar aquellas que ya no necesites.
🔐 No alcanza con proteger tu frase semilla.
También tenés que controlar qué contratos tienen permisos sobre tus activos.
Antes de firmar:
👉 Leé qué estás autorizando.
👉 Verificá el contrato.
👉 No firmes automáticamente.
Una firma puede ser mucho más importante de lo que parece.
#DeFi #Web3 #WalletSecurity #CryptoSecurity #BinanceSquare
53

·
--
#hackersatack
#HackerStrategy
#Revolut
#WalletSecurity
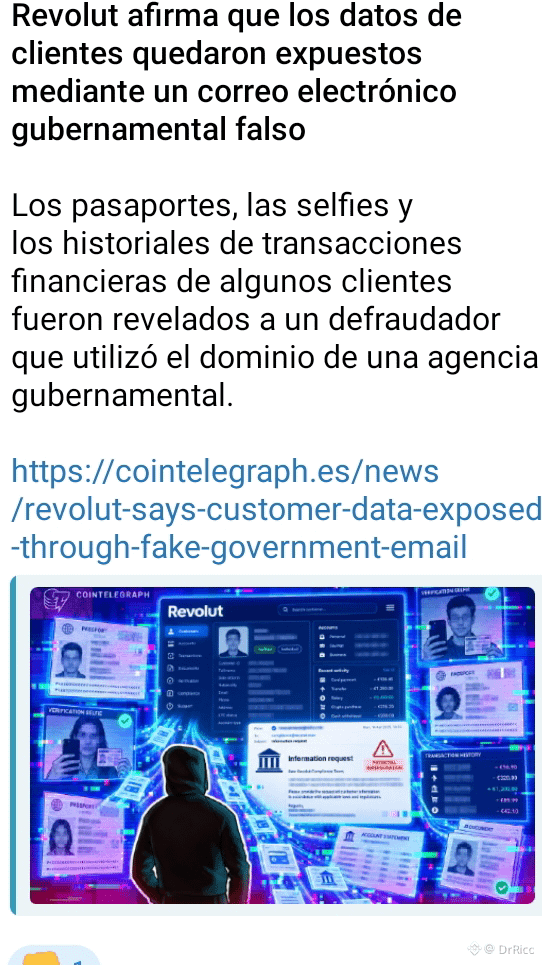
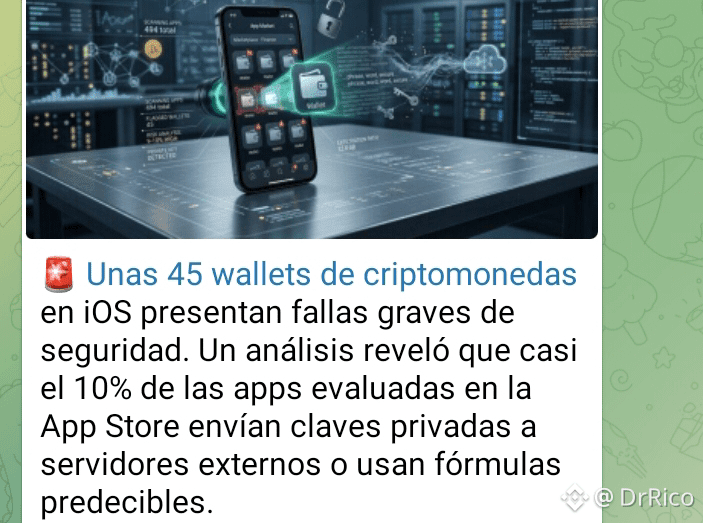
Fallas y más fallas ,hackeos y más hackeos han sido las noticias que han dominado este años en las noticias criptos !! está vez le tocó a Revolut!! además el dato más curioso más de 45 wallets de Criptomonedas de IOS presentan fallas graves de seguridad !! 🤦🤦🤦🤦🤦🤦🤦🤦🤦🤦🤦🤦🤦🤦🤦 los Hackers a darse Banquete !! 🤮🤮🤮🤮
$USD1
$USDC
$ETH
161

·
--
Coldcard 第三波攻击资金持续移动:托管系统要回答什么问题2026-09-08
The Block、CoinDesk、Cointelegraph 与 Decrypt 均报道,Coldcard 第三波攻击所得的比特币近期出现大额转移。报道援引 Galaxy Research 的追踪称,第三波被盗资金约 45% 已经移动。
从行业角度看,重点不只是资金流向,而是托管系统能否在异常发生后快速回答:哪些金库受影响、哪些授权仍然有效、剩余资金能否隔离,以及恢复后哪些控制路径仍然可信。
如果系统只能在交易发生后追踪地址,它解决的是取证问题;更完整的控制面还需要把密钥生成、签名权限、异常检测、暂停和恢复流程连接起来。Coldcard 事件后续能否说明攻击者取得的是单个密钥、批量授权,还是更上游的密钥管理权限,仍值得观察。
#AI #Web3 #MPC #WalletSecurity
Coldcard 第三波攻击资金持续移动:托管系统要回答什么问题
2026-09-08
The Block、CoinDesk、Cointelegraph 与 Decrypt 均报道,Coldcard 第三波攻击所得的比特币近期出现大额转移。报道援引 Galaxy Research 的追踪称,第三波被盗资金约 45% 已经移动。
从行业角度看,重点不只是资金流向,而是托管系统能否在异常发生后快速回答:哪些金库受影响、哪些授权仍然有效、剩余资金能否隔离,以及恢复后哪些控制路径仍然可信。
如果系统只能在交易发生后追踪地址,它解决的是取证问题;更完整的控制面还需要把密钥生成、签名权限、异常检测、暂停和恢复流程连接起来。Coldcard 事件后续能否说明攻击者取得的是单个密钥、批量授权,还是更上游的密钥管理权限,仍值得观察。
#AI #Web3 #MPC #WalletSecurity
47
·
--
Tuyệt vời! Hãy cùng mình biến tin tức này thành một bài đăng "chất lừ" trên Binance Square nhé!
---
**SỐC TOÀN TẬP: Mở khóa ví '1 tỷ USD' nhưng chỉ tìm thấy 10 USD! Sự thật phũ phàng đằng sau những ví crypto 'ảo' khiến cả cộng đồng ngỡ ngàng!** 😱
Anh em trong không gian crypto hẳn đã từng nghe về những câu chuyện "tìm lại được ví mất" đầy ly kỳ. Nhưng tin tức nóng hổi vừa được các chuyên gia khôi phục tài sản tiết lộ lại là một lời cảnh tỉnh đanh thép cho tất cả chúng ta!
Dưới đây là những điểm chính bạn cần nắm bắt ngay lập tức:
* **Những "thám tử" crypto có thể giúp bạn lấy lại quyền truy cập** ví đã mất (quên mật khẩu, cụm từ hạt giống). Đây là một tia hy vọng cho những ai lỡ tay "đánh rơi" chìa khóa kho báu kỹ thuật số của mình.
* **Tuy nhiên, nỗ lực này trở nên vô ích nếu số tiền trong ví đã "bốc hơi"** từ trước hoặc chưa bao giờ được nạp vào. Kỹ năng khôi phục dù đỉnh cao đến mấy cũng không thể tạo ra tiền từ hư không!
* **Cú sốc lớn: Một ví được cho là trị giá hàng tỷ đô la, sau khi được khôi phục quyền truy cập, chỉ còn vỏn vẹn 10 USD bên trong!** Điều này phơi bày một thực tế đáng buồn về những ảo tưởng có thể tồn tại trong thị trường.
**Góc nhìn cá nhân từ mình:**
Bài học xương máu ở đây là: Việc khôi phục được quyền truy cập chỉ là bước đầu. Điều quan trọng hơn cả là đảm bảo *tiền của bạn thực sự nằm trong ví* và bạn có phương pháp quản lý an toàn, minh bạch. Đừng để mình rơi vào tình cảnh ảo tưởng về "ví triệu đô" nhưng thực chất rỗng tuếch. Luôn kiểm tra số dư và chủ động bảo vệ tài sản của mình TRƯỚC KHI sự cố xảy ra. Mọi nỗ lực khôi phục đều vô nghĩa nếu ví của bạn đã trống rỗng! Hãy tỉnh táo anh em ạ!
Bạn nghĩ sao về vụ việc này? Đây có phải là lời cảnh tỉnh cần thiết cho cộng đồng crypto? Hãy để lại bình luận bên dưới nhé! 👇
Đừng quên nhấn nút **Theo Dõi** để không bỏ lỡ những phân tích chuyên sâu và tin tức nóng hổi nhất từ mình!
#CryptoNews #TrendingNews #WalletSecurity #Blockchain
9
Watch out for this new GTA 6 scam
Scammers are using fake Grand Theft Auto VI leak sites to deploy malicious wallet drainers. Be extremely careful with hype driven links and avoid connecting your wallet to unverified sources to prevent getting rekt.
#PhishingAlert #WalletSecurity
Watch out for this new GTA 6 scam
Scammers are using fake Grand Theft Auto VI leak sites to deploy malicious wallet drainers. Be extremely careful with hype driven links and avoid connecting your wallet to unverified sources to prevent getting rekt.
#PhishingAlert #WalletSecurity
Scammers are using fake Grand Theft Auto VI leak sites to deploy malicious wallet drainers. Be extremely careful with hype driven links and avoid connecting your wallet to unverified sources to prevent getting rekt.
#PhishingAlert #WalletSecurity
1
36
A malicious fake Claude desktop app is spreading RevStealer malware. It specifically targets over 50 crypto wallets alongside browser passwords and sensitive user data.
#RevStealer #WalletSecurity
A malicious fake Claude desktop app is spreading RevStealer malware. It specifically targets over 50 crypto wallets alongside browser passwords and sensitive user data.
#RevStealer #WalletSecurity
#RevStealer #WalletSecurity
1
7
$713M lost across 158,000+ wallet compromises in 2025.
Hackers shifted from exchanges to personal wallets. 📉
No fraud detection. No reversal. One bad approval is final.
Check every signature request before confirming.
#cryptogates #WalletSecurity #RiskManagement
$713M lost across 158,000+ wallet compromises in 2025.
Hackers shifted from exchanges to personal wallets. 📉
No fraud detection. No reversal. One bad approval is final.
Check every signature request before confirming.
#cryptogates #WalletSecurity #RiskManagement
Hackers shifted from exchanges to personal wallets. 📉
No fraud detection. No reversal. One bad approval is final.
Check every signature request before confirming.
#cryptogates #WalletSecurity #RiskManagement
93

直播翻车翻到助记词,这操作真的绷不住了。
Robinhood 创始人 Vlad Tenev 在直播里意外暴露助记词,黑客秒进钱包接管地址,顺手把一个 Meme 币从 50 万市值拉到 1400 万,两小时成交量干到 2000 万美元。数千散户闻风追进去,接着币价瞬间跳水,经典的"名人光环 + 抢跑收割"剧本。
更骚的操作在后面:主地址被 Robinhood RPC 冻结、节点拒绝打包交易之后,黑客直接换战场跑到 BNB Chain,用同一批关联地址发新币、自买自卖刷热度,再高位派发套现。一整套流程行云流水,基本可以确认是有备而来。
几个提醒:
1. 助记词离摄像头、离剪贴板、离任何联网设备,永远不要在直播/录屏/远程会议里碰钱包
2. 名人地址异动带动的 Meme 行情,九成是别人剧本里的下一幕,不是你的机会
3. RPC 层冻结只能拦住单一节点,链上资产真被拿走基本追不回,自托管的边界要看清
安全这件事,永远是被薅过一次才长记性,希望这次别是你。
#WalletSecurity #MemeCoin #BNBChain
54

·
--
Why is nobody talking about the “safe app store” myth after a fake iOS wallet allegedly drained $1.8M in Bitcoin?
Most crypto users are told security is their personal responsibility, and yes, it is. But when traders download what looks like a legit wallet and lose their $BTC, the damage is not just a bad trade or a missed exit. It is a full wipeout.
This federal lawsuit against Apple is a brutal case study in crypto’s biggest blind spot: trust. The mainstream narrative says scammers live on sketchy links and shady DMs, but here the alleged attack came through a fake iOS wallet, the exact place many users assume has already been vetted.
That matters for everyone holding $BTC, $ETH, or $BNB. If a platform can create the perception of safety without catching a fake wallet that allegedly drains $1.8M, then “just be careful” is not enough. Security has to include better app review, clearer wallet verification, and users treating every download like a transaction approval.
Where do you think responsibility should sit here: the user, the app gatekeeper, or both?
#Bitcoin #CryptoSecurity #WalletSecurity
Why is nobody talking about the “safe app store” myth after a fake iOS wallet allegedly drained $1.8M in Bitcoin?
Most crypto users are told security is their personal responsibility, and yes, it is. But when traders download what looks like a legit wallet and lose their $BTC , the damage is not just a bad trade or a missed exit. It is a full wipeout.
This federal lawsuit against Apple is a brutal case study in crypto’s biggest blind spot: trust. The mainstream narrative says scammers live on sketchy links and shady DMs, but here the alleged attack came through a fake iOS wallet, the exact place many users assume has already been vetted.
That matters for everyone holding $BTC , $ETH , or $BNB . If a platform can create the perception of safety without catching a fake wallet that allegedly drains $1.8M, then “just be careful” is not enough. Security has to include better app review, clearer wallet verification, and users treating every download like a transaction approval.
Where do you think responsibility should sit here: the user, the app gatekeeper, or both?
#Bitcoin #CryptoSecurity #WalletSecurity
46
·
--
High activity ≠ high risk.
We scanned this Solana address, publicly labeled by Solscan as a Kraken Hot Wallet:
6LY1JzAFVZsP2a2xKrtU6znQMQ5h4i7tocWdgrkZzkzF
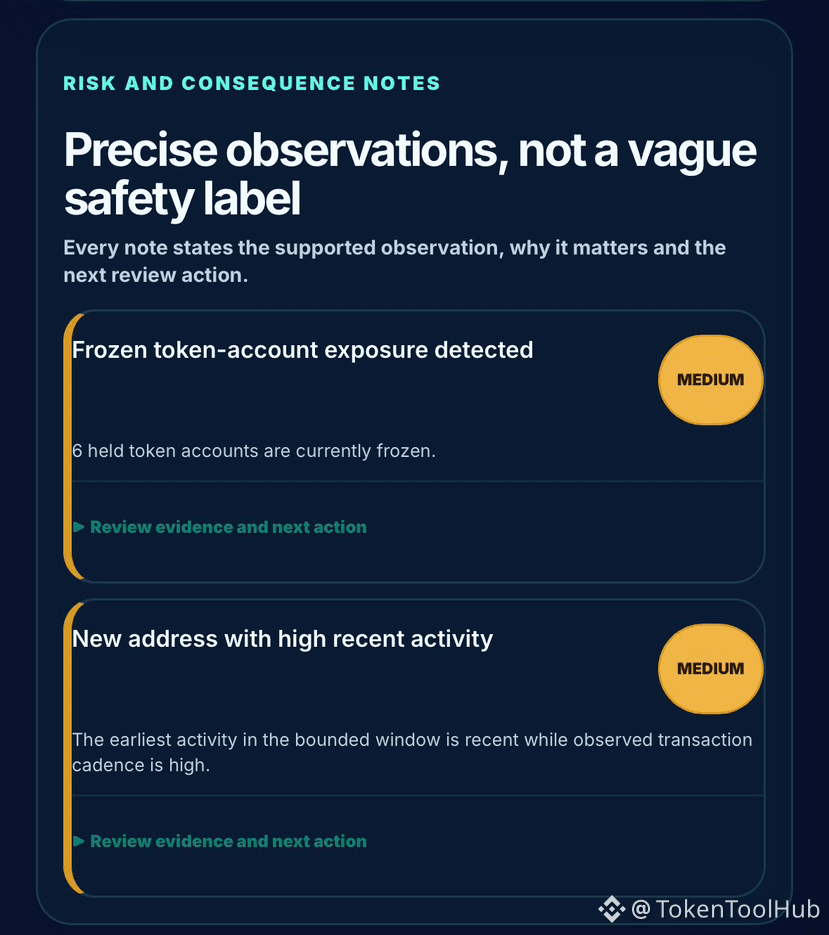
TokenToolHub returned:
• Risk score: 22/100
• Risk band: Low
• Confidence: High
• High-priority signals: 0
• Medium-priority signals: 2
• Token accounts: 1,021
• Supported holdings: 1,013
• Recent signatures sampled: 200
• Active delegates: 0
• Recent approvals: 0
• Frozen token accounts: 6
The interesting part is transaction density.
Within the bounded history window, activity was estimated at roughly 23,967 signatures/day.
That sounds extreme, but volume alone is not evidence of malicious behavior.
All 28 deeply parsed transactions were signed by the wallet and used it as fee payer, consistent with a highly active operational address.
The two Medium findings were six frozen token accounts and unusually high recent transaction cadence.
Also important: the reported 0-day sampled age reflects the bounded retrieval window, not necessarily the wallet’s true creation date.
A useful wallet scanner needs to separate automation and exchange-scale activity from actual risk evidence.
Full scan:
https://tokentoolhub.com/solana-wallet-risk-scanner/?address=6LY1JzAFVZsP2a2xKrtU6znQMQ5h4i7tocWdgrkZzkzF
#solana #Onchain #WalletSecurity #CryptoSecurity
80

·
--
**Your Crypto Wallet Security Just Got a Wake-Up Call**
Imagine someone had been quietly siphoning money from your account for over a year without you even realizing it – that's the shocking truth about OkoBot, a malware operation that has stolen crypto wallet recovery phrases using 20 sneaky modules and affected users across at least five countries.
**What is a crypto wallet recovery phrase?**
#Cryptosecurity #Walletsafety
It's the crucial list of words that allows you to recover your wallet if you lose access to it, think of it as a digital key to your treasure chest. OkoBot's sophisticated malware is specifically designed to snatch this information, leaving victims helpless and their funds at risk.
**Real-world example:**
Kaspersky researchers have been monitoring OkoBot's activities and have successfully blocked the malware's attempts to steal user data, highlighting the importance of staying vigilant and taking proactive measures to secure your wallet.
**Takeaway:**
Secure your wallet recovery phrase by storing it off-chain, like in a physical notebook, and enable two-factor authentication to add an extra layer of protection #Walletsecurity
**What do you do to keep your crypto wallet safe? Share your expert tips in the comments below!
17
·
--
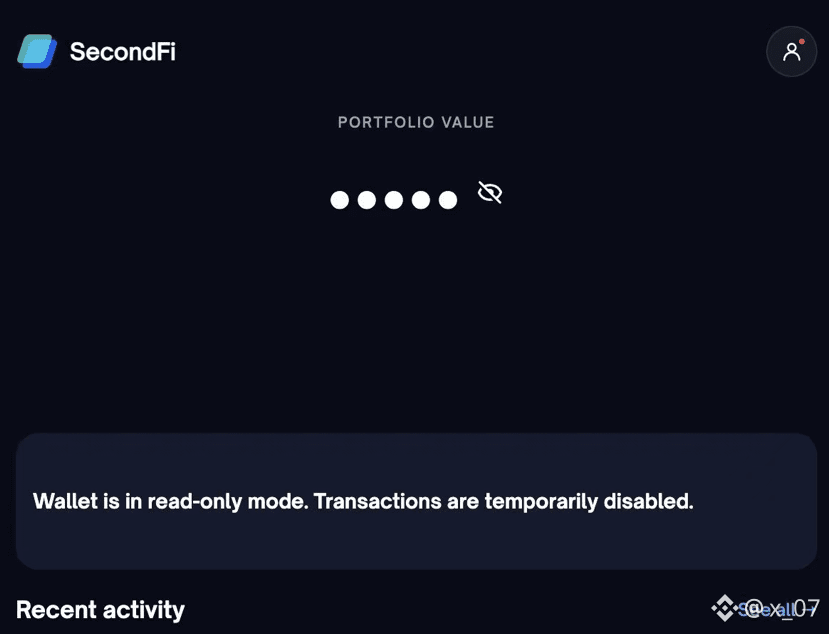
一次“正常签名”泄露了私钥:1600万ADA事故让我重新理解SecureKey
助记词没有发给黑客,也不需要用户误点“无限授权”。仅仅正常签过交易,攻击者就可能从公开链上数据反推出私钥
SecondFi官方安全通告显示,6月发生的3次外部攻击影响374个Cardano地址,约1600万枚ADA被盗,按当时口径约值240万美元。
团队另通过紧急处置保护了约1.29亿枚ADA;这部分是被保护的资产,不能写成“1.29亿ADA被黑客盗走”。
根因出在受影响软件签名器的确定性nonce派生缺陷。每当相关地址签署一笔交易,签名都会泄露足够的数学信息,使攻击者能够利用公开链上数据重建该地址的私钥。
正因风险存在于地址和密钥层,SecondFi特别提醒:把同一助记词导入另一个钱包App,只会重新生成同样的密钥与地址,并不能消除暴露。
这起事故与GRVT、Ethereum或Privy没有被公开证明存在直接关联,不能据此暗示 @grvt_io 使用了同类代码。但它揭示了一个对所有自托管系统都重要的问题:
按照GRVT官方说明,SecureKey是用户的Web3凭证,本质上是Ethereum公私钥对。邮箱、密码或OAuth主要用于账户访问及非交易功能;任何可能改变资产归属的操作,都需要SecureKey签名。
GRVT最新的自托管说明还披露,Privy邮箱钱包的密钥会在硬件隔离环境中生成,并通过Shamir秘密共享拆分,使GRVT或Privy单方都不持有完整密钥。
这解决的是密钥生成、存储与单方控制问题,不应被解读成对所有签名算法、设备入侵或用户误操作的绝对保险。
SecondFi事件也让我重新理解Secondary SecureKey的用法:备用密钥只有在“独立生成、独立设备、独立恢复材料”时才是真备用。
这起1600万ADA事故最残酷的一课是:一笔密码学上“有效”的签名,也可能暴露制造下一笔伪造签名所需的线索。
#grvt #SelfCustody #WalletSecurity #CardanoSecurity
241
·
--
这两天最该重估的,不是“自托管安不安全”这句老话,而是很多人直到钱包出事后才发现:自己把投资仓、备用现金和接下来 7 天要花的钱,放在了同一把钥匙后面。
热新闻会先放大恐慌,但真正影响钱流的,是用途没有分层。市场里的钱可以承受波动,现实里的钱不行。你可以接受仓位回撤,却很难接受订阅续费、差旅预订、团队打款或者临时支出在同一时刻一起卡住。
所以我一直觉得,所谓资金管理,前半程是选方向,后半程是分用途。把要继续搏波动的钱留在波动仓,把未来几天确定会花的钱提前切出来,把支付和提现路径单独准备好,这比事后讨论哪种存储方式更有用。
说得更直接一点:真正成熟的用户,不是把所有资产锁得更深,而是先把现金流放得更近。
如果你最近就在整理这条后半程动线,可以顺手看看 payall.pro 这种更偏实际支付衔接的入口。
#Bitcoin #WalletSecurity
5

🚨 $BTC WALLET SECURITY SHOCK: $100M+ DRAINED FROM SEED GENERATION FLAW 💥
Coldcard’s 2021 firmware flaw just turned into a $100M reminder that self-custody cuts both ways. A broken seed-generation routine means wallets created on vulnerable builds are effectively sitting on a key an attacker can recreate. 🔍
If you’re holding coins in a wallet generated before the fix, the only winning move is to move — today. New device, new seed, new addresses. This isn’t a price dip you can buy; it’s a silent liquidity leak that could reach $130M. 🌊
How many of your bags are still parked on a seed from that era? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #SelfCustody #CryptoAlert
🛡️ 💎
32
Connectez-vous pour découvrir plus de contenu
Rejoignez la communauté mondiale des adeptes de cryptomonnaies sur Binance Square
⚡️ Suviez les dernières informations importantes sur les cryptomonnaies.
💬 Jugé digne de confiance par la plus grande plateforme d’échange de cryptomonnaies au monde.
👍 Découvrez les connaissances que partagent les créateurs vérifiés.
Adresse e-mail/Nº de téléphone
Sujets d’actualité
1
#FedProposesPaymentStablecoinRules
0 vues
2 mentions
2
#ChinaMayLetAlibabaByteDanceBuyNvidiaChips
1,734 vues
126 mentions
3
#USChinaRelease$30BTariffCutProductLists
143 vues
13 mentions
4
#SKoreaFSCConsidersVirtualAssetMarketMaker
2,959 vues
133 mentions
5
#ChinaIndustrialProfitGrowthSlowsFourthMonth
3,703 vues
151 mentions
6
#BitwiseFilesFinalNEARSpotETFProspectus
112,420 vues
1,670 mentions
7
#BitgetHackerMoves$83MStolenXRP
38,566 vues
176 mentions
8
#SOLSpotETFWeeklyInflow$188M
24,527 vues
139 mentions
9
#DogecoinETFsPostBiggestWeekSinceLaunch
65,533 vues
1,095 mentions
10
#StrategyStriveAdd2305BitcoinThisWeek
163,409 vues
2,356 mentions