

#wallethack
wallethack
9,406 vues
20 mentions
Populaire
Récents

·
--
#hackersdrainover12.4mxrpfromdcentwallets
A Wallet Breach Kept Bleeding Even After the Warnings Went Out
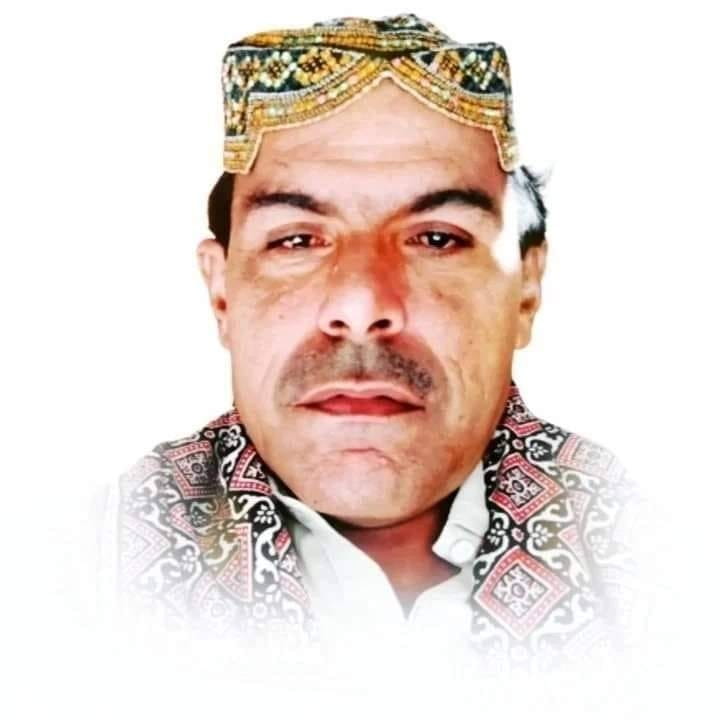
Over 7,300 crypto wallets just lost more than 12.4 million XRP — and the strangest part is how long the theft continued even after users were told to move their funds.
Here's the timeline: South Korean wallet provider D'CENT confirmed a security breach affecting its App Wallet on September 16, after attackers began exploiting compromised private keys the day before. The first wave was brutal — roughly 3.6 million XRP drained from 1,682 wallets in under three hours, mixing manual theft of large balances with automated scripts sweeping smaller ones. Despite public warnings, more than 640,000 additional XRP disappeared after September 21, and by September 25, total losses reached approximately 12.4 million XRP, worth roughly $18-20 million. No exploit hit the XRP Ledger itself — every transfer used valid signatures from already-compromised keys. Roughly half the stolen funds have since moved to Ethereum via THORChain, a cross-chain swap protocol that doesn't require identity verification, complicating recovery efforts. D'CENT says it's working with law enforcement and has urged all App Wallet users to generate new recovery phrases immediately.
Why does this matter? This wasn't a protocol-level flaw — it was compromised key material, a reminder that wallet security often hinges on implementation details users never see. The continued draining after public alerts also raises a real question about how effectively warnings reach affected users in time, and cross-chain laundering tools make recovery meaningfully harder once funds start moving.
Whether D'CENT fully identifies the breach's root cause, or whether affected users see any reimbursement, remains unresolved.
Does the industry need faster, more forceful ways to warn users mid-breach — or is user vigilance always the last line of defense? 🤔
#xrp #CryptoSecurity #WalletHack #DCENT
AngelOfCrypto_-:
nice
9
1
22
19.5k
·
--
Haussier
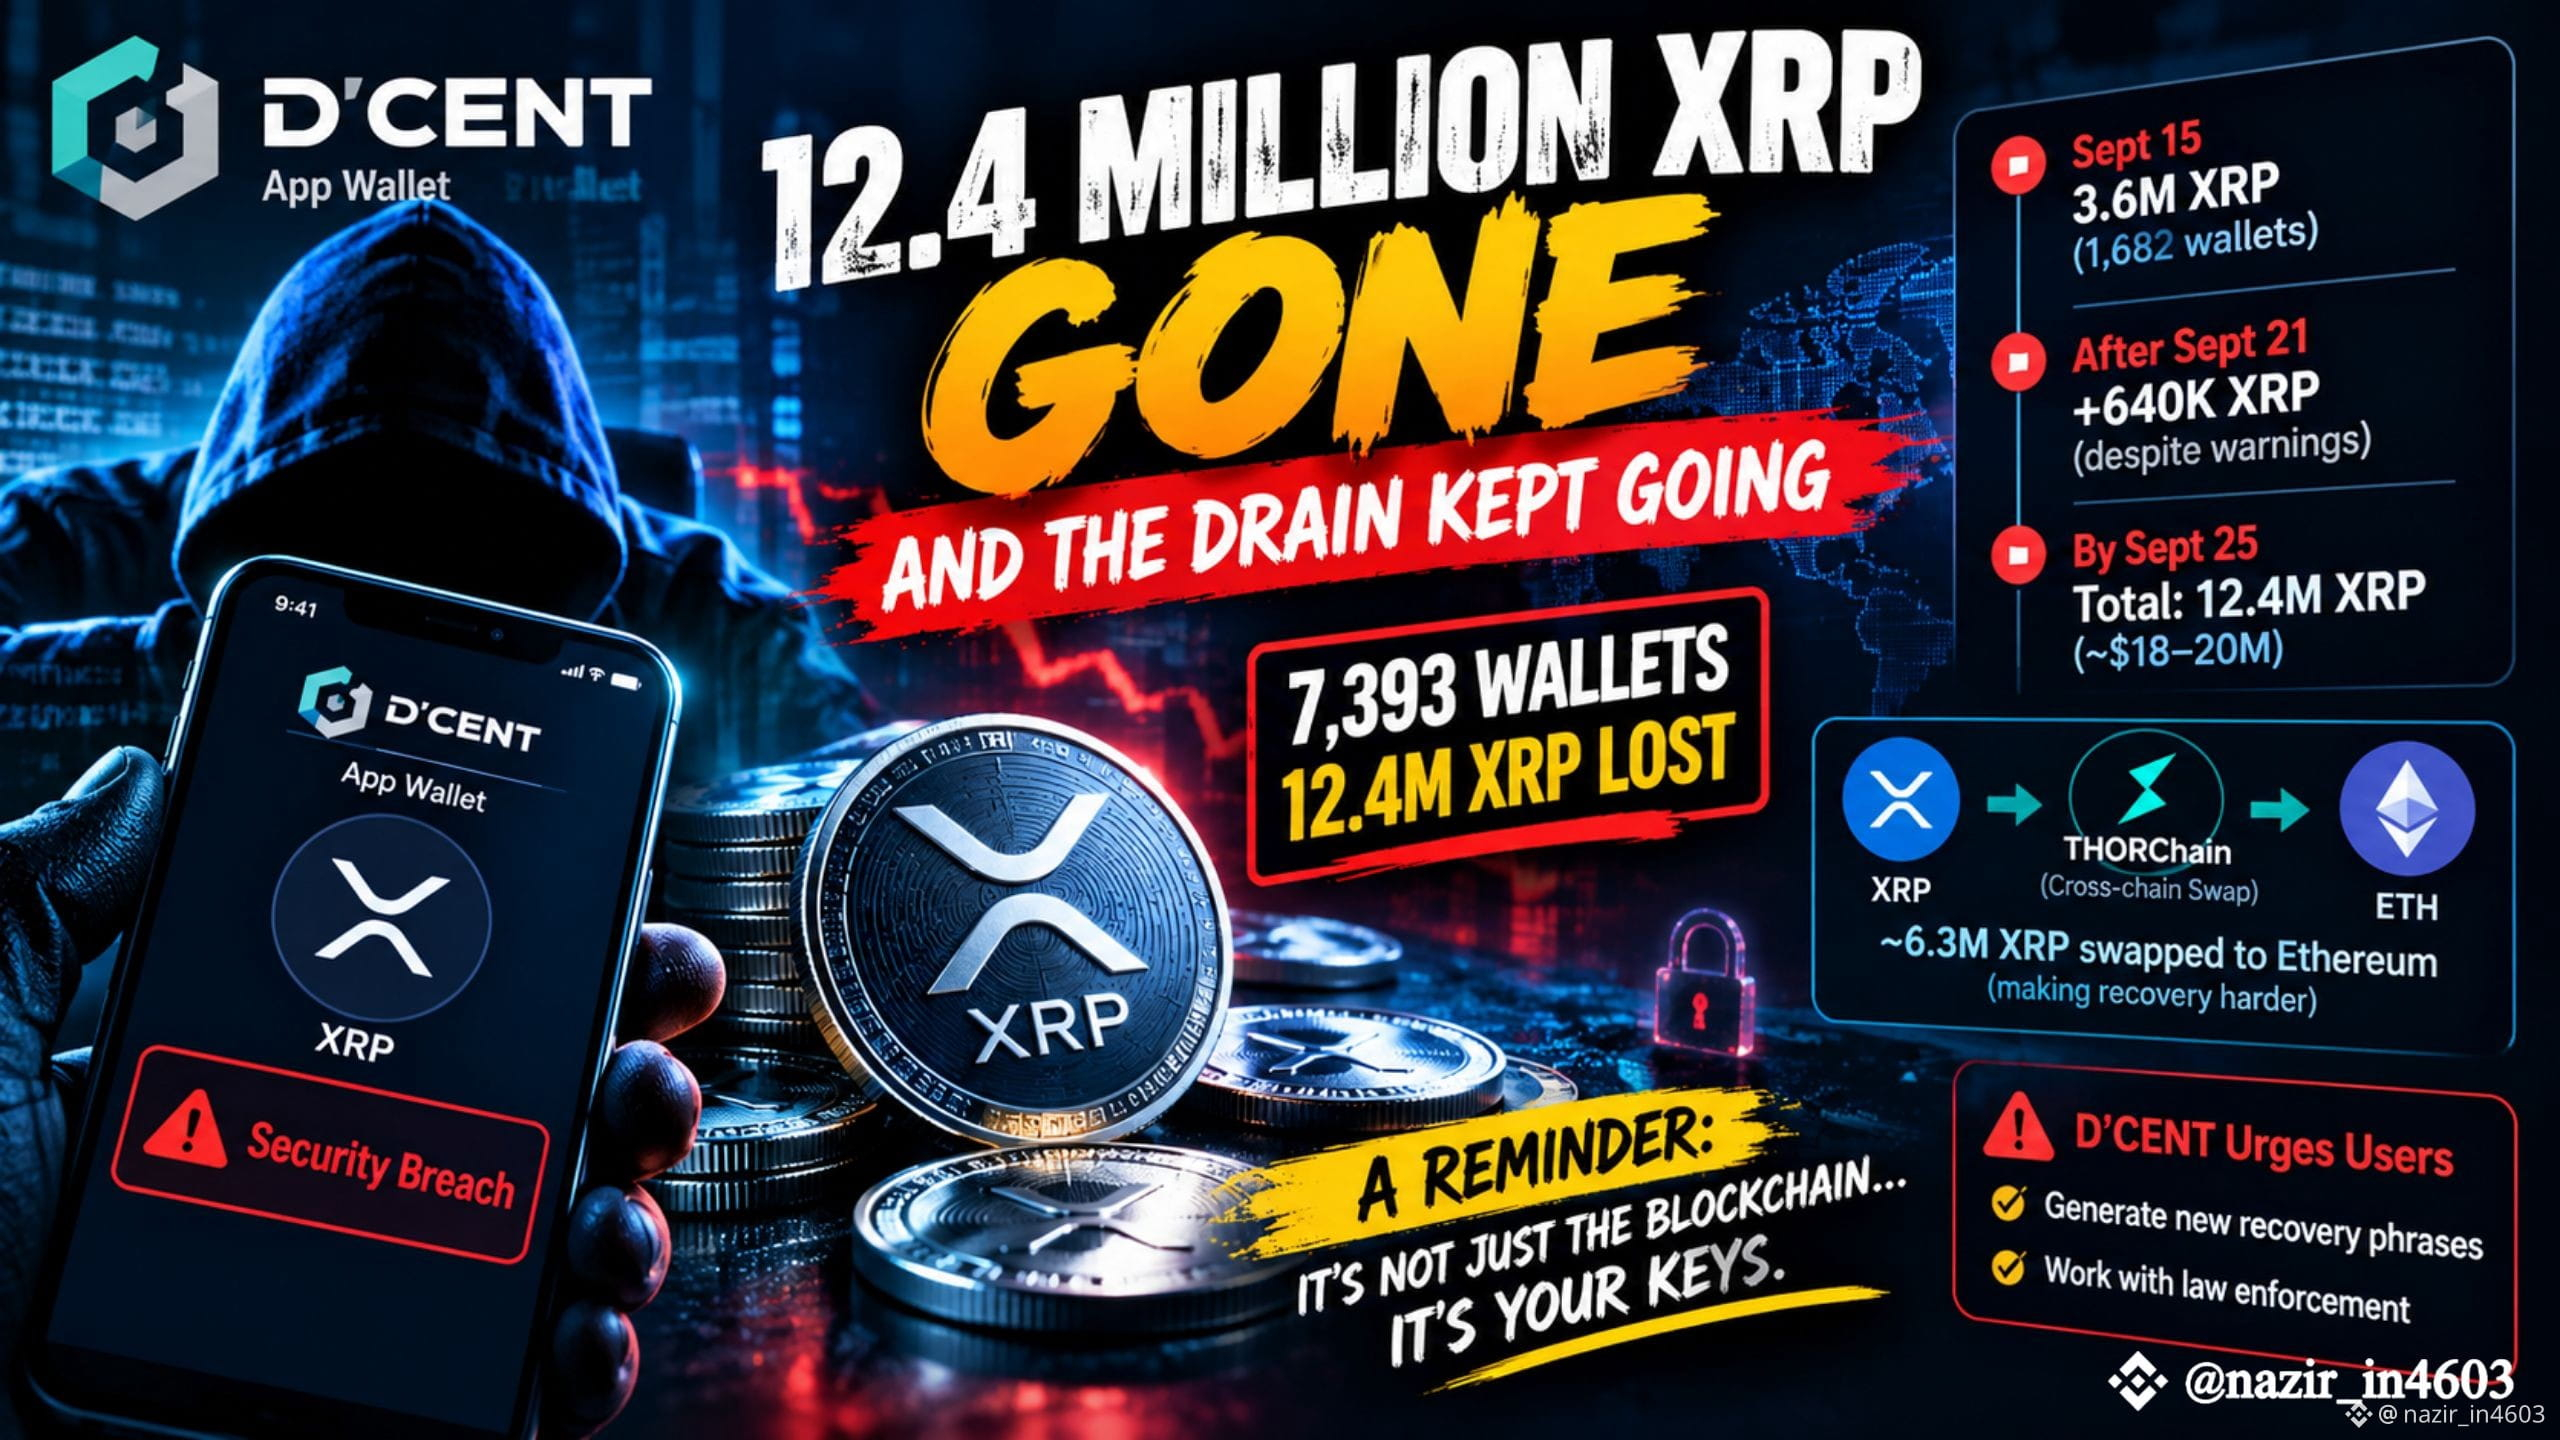
🚨 12.4 MILLION $XRP GONE — AND THE DRAIN KEPT GOING
This is the kind of crypto security story that makes you stop and look twice.
The D’CENT App Wallet incident has now been linked to roughly 12.4 million XRP drained from 7,393 wallets. But the most disturbing part isn’t just the amount.
It’s what happened after the warnings started going out.
The first major wave hit on September 15, when around 3.6 million XRP was drained from 1,682 wallets in just a few hours. The attackers weren’t breaking the XRP Ledger itself — the transfers were signed using private keys that had already been compromised.
Then came the part that really raises questions.
Even after users were being warned to move their funds, the same compromised keys were still being used. More than 640,000 XRP was taken after September 21, pushing the overall losses to around 12.4 million XRP. Some wallets were even drained again after being refilled.
And the money started moving across chains. On-chain analysis indicates that roughly 6.3 million XRP was swapped toward Ethereum through THORChain, making recovery and tracking even more complicated.
That’s the real lesson here:
🔐 A blockchain can remain secure while the keys controlling individual wallets are compromised.
For crypto users, the phrase “not your keys, not your coins” suddenly feels a lot less like a slogan.
The big question now isn’t only how the keys were compromised.
It’s also this:
When a wallet breach is actively happening, how quickly can affected users actually be warned — and how much time do they have to react? 🤔
#XRP #CryptoSecurity #WalletHack #DCENT #XRPL #CryptoNews
{future}(XRPUSDT)
🚨 12.4 MILLION $XRP GONE — AND THE DRAIN KEPT GOING
This is the kind of crypto security story that makes you stop and look twice.
The D’CENT App Wallet incident has now been linked to roughly 12.4 million XRP drained from 7,393 wallets. But the most disturbing part isn’t just the amount.
It’s what happened after the warnings started going out.
The first major wave hit on September 15, when around 3.6 million XRP was drained from 1,682 wallets in just a few hours. The attackers weren’t breaking the XRP Ledger itself — the transfers were signed using private keys that had already been compromised.
Then came the part that really raises questions.
Even after users were being warned to move their funds, the same compromised keys were still being used. More than 640,000 XRP was taken after September 21, pushing the overall losses to around 12.4 million XRP. Some wallets were even drained again after being refilled.
And the money started moving across chains. On-chain analysis indicates that roughly 6.3 million XRP was swapped toward Ethereum through THORChain, making recovery and tracking even more complicated.
That’s the real lesson here:
🔐 A blockchain can remain secure while the keys controlling individual wallets are compromised.
For crypto users, the phrase “not your keys, not your coins” suddenly feels a lot less like a slogan.
The big question now isn’t only how the keys were compromised.
It’s also this:
When a wallet breach is actively happening, how quickly can affected users actually be warned — and how much time do they have to react? 🤔
#XRP #CryptoSecurity #WalletHack #DCENT #XRPL #CryptoNews
105

$2.3M crypto heist as wallet keys were compromised.
private keys linked to two wallets were leaked, enabling attackers to steal around $2.3 million in USDT. The incident highlights persistent security risks in crypto and the critical need for stronger key protection.
#CryptoNews #WalletHack #cryptofirst21 #Write2Earn #crypto
private keys linked to two wallets were leaked, enabling attackers to steal around $2.3 million in USDT. The incident highlights persistent security risks in crypto and the critical need for stronger key protection.
#CryptoNews #WalletHack #cryptofirst21 #Write2Earn #crypto
16
834

🚨 تحذير: برمجيات خبيثة تستهدف محافظ الكريبتو على macOS عبر تيليجرام!
كشفت شركة SlowMist عن برمجيات خبيثة جديدة تستهدف مستخدمي macOS، قادرة على سرقة بيانات اعتماد جلسات تيليجرام واختراق محافظ العملات المشفرة. كما يمكنها خداع المستخدمين للحصول على عبارات استعادة محافظهم عبر تطبيقات مزيفة، مما يشكل تهديداً خطيراً للأصول الرقمية.
يجب على مستخدمي ماك توخي الحذر الشديد.
━━━━━━━━━━━━━━
📊 التأثير: 🔥 مرتفع جداً
🏷️ OTHER
#macOS #Malware #CryptoSecurity #Telegram #WalletHack
🔗 المصدر: https://cointelegraph.com/news/macos-malware-crypto-investors-slowmist
1
12
Connectez-vous pour découvrir plus de contenu
Rejoignez la communauté mondiale des adeptes de cryptomonnaies sur Binance Square
⚡️ Suviez les dernières informations importantes sur les cryptomonnaies.
💬 Jugé digne de confiance par la plus grande plateforme d’échange de cryptomonnaies au monde.
👍 Découvrez les connaissances que partagent les créateurs vérifiés.
Adresse e-mail/Nº de téléphone
Sujets d’actualité
1
#BitcoinClears$85200
15,195 vues
235 mentions
2
#AltcoinSeasonIndexHoldsAbove60For5Days
73,110 vues
1,263 mentions
3
#USADPAdds90000JobsInSeptember
33,167 vues
701 mentions
4
#USCorePCEEasesTo3%InAugust
23,765 vues
527 mentions
5
#KospiPostsWorstQuarterSince2020
16,276 vues
504 mentions
6
#SECToClarifyOnChainFundraisingRules
41,411 vues
680 mentions
7
#UKFCAOpensCryptoFirmAuthorization
39,554 vues
571 mentions
8
#JapanMOFStudyGroupOnTokenizedGovtBonds
22,503 vues
431 mentions
9
#QNTRises287%
110,398 vues
933 mentions
10
#TrumpRejectsAIRulesForVoluntaryAudits
63,115 vues
807 mentions