

#infosec
infosec
8,271 vues
33 mentions
Populaire
Récents

·
--
New Head of Security implements aggressive IT protocols
• Department internet feed isolated to restrict external access
• Equipment departures now require mandatory recording
• IT department raised concerns over data security and machine sanitization
#CryptoSecurity #CryptoNews #BinanceSquare #InfoSec #SecurityAlert
• Department internet feed isolated to restrict external access
• Equipment departures now require mandatory recording
• IT department raised concerns over data security and machine sanitization
#CryptoSecurity #CryptoNews #BinanceSquare #InfoSec #SecurityAlert
18
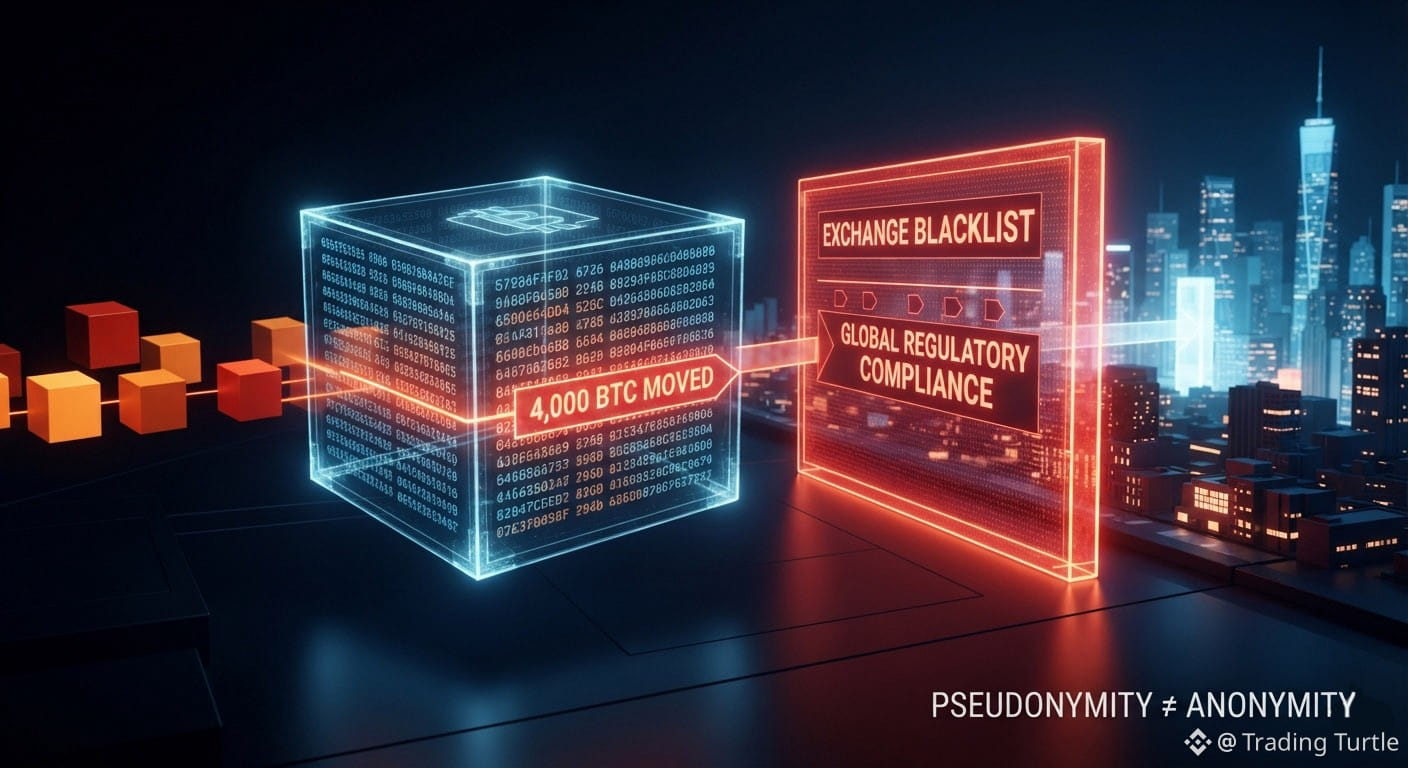
💡 Why "Tracking the Wallet" Isn't Enough: The Mechanics Behind the Recent 4,000 BTC Exploit
The crypto community was recently rocked by a vulnerability in the Liquid Network federation wallet, resulting in the withdrawal of roughly 4,000 Bitcoin (valued at over $320M).
While the incident concluded with the "white hat" returning the majority of the funds after securing a hefty $47M bounty, it highlights a persistent point of confusion in blockchain security: If blockchain transactions are entirely public, why can't we just stop or unmask the hacker using their wallet address?
As cybersecurity and blockchain professionals, it’s critical to understand the distinction between tracking a ledger and enforcing real-world accountability. Here is why wallet tracking alone doesn't prevent a heist:
➡️ Pseudonymity ≠ Anonymity: The blockchain exposes every single transaction from Point A to Point B, but addresses are just strings of code, not identities. Tracking the wallet is instant; linking that wallet to a physical person requires a break in operational security (OpSec) or a connection to a regulated endpoint.
➡️ Decentralization Means No "Undo" Button: Unlike traditional banking rails where a fraudulent wire transfer can be frozen or reversed by a central authority, decentralized ledgers are immutable. If the exploiter holds the private keys, they hold absolute control over the funds.
➡️ The Laundering Gauntlet: Sophisticated actors don't simply send stolen funds to a retail exchange. They leverage privacy coins, decentralized protocols, and mixers to break the public deterministic trail, making forensic auditing incredibly complex.
The Silver Lining? Public tracking does work as a deterrent. Because the 4,000 BTC wallet address was immediately blacklisted globally by exchanges, the exploiter's exit liquidity was virtually choked off. This transparency is ultimately what drives attackers—even malicious ones—to negotiate returns under the guise of "white hat" bounties.
#Cybersecurity #BlockchainSecurity #Cryptocurrency #Web3 #Infosec
51
·
--

Article
The Silent Drift: Uncovering the Cyber Trail to North Korean HackersThe digital battlefield is shifting—and the latest wave of #DriftInvestigationLinksRecentAttackToNorthKoreanHackers is a chilling reminder of just how sophisticated cyber warfare has become.
What makes this case especially alarming isn’t just the scale of the breach, but the precision. The “Drift” trail suggests a slow, calculated infiltration—one that quietly maps vulnerabilities before striking with intent. This wasn’t random. It was strategic.
Security experts are now pointing toward patterns long associated with North Korean-linked groups: stealthy entry points, long dwell times, and coordinated data extraction. If confirmed, this adds another chapter to an already complex narrative of state-backed cyber operations that blur the line between espionage and economic disruption.
The real question is: how many more “drift” attacks are already in motion—undetected?
As businesses and governments scramble to reinforce their defenses, one thing is clear: cybersecurity is no longer just an IT issue. It’s national security.
Stay alert. Stay informed. Because in this era, silence in the system doesn’t mean safety—it might just mean someone is watching.
#CyberSecurity #databreach #DigitalWarfare #InfoSec
The Silent Drift: Uncovering the Cyber Trail to North Korean Hackers
The digital battlefield is shifting—and the latest wave of #DriftInvestigationLinksRecentAttackToNorthKoreanHackers is a chilling reminder of just how sophisticated cyber warfare has become.
What makes this case especially alarming isn’t just the scale of the breach, but the precision. The “Drift” trail suggests a slow, calculated infiltration—one that quietly maps vulnerabilities before striking with intent. This wasn’t random. It was strategic.
Security experts are now pointing toward patterns long associated with North Korean-linked groups: stealthy entry points, long dwell times, and coordinated data extraction. If confirmed, this adds another chapter to an already complex narrative of state-backed cyber operations that blur the line between espionage and economic disruption.
The real question is: how many more “drift” attacks are already in motion—undetected?
As businesses and governments scramble to reinforce their defenses, one thing is clear: cybersecurity is no longer just an IT issue. It’s national security.
Stay alert. Stay informed. Because in this era, silence in the system doesn’t mean safety—it might just mean someone is watching.
#CyberSecurity #databreach #DigitalWarfare #InfoSec
2
174
·
--
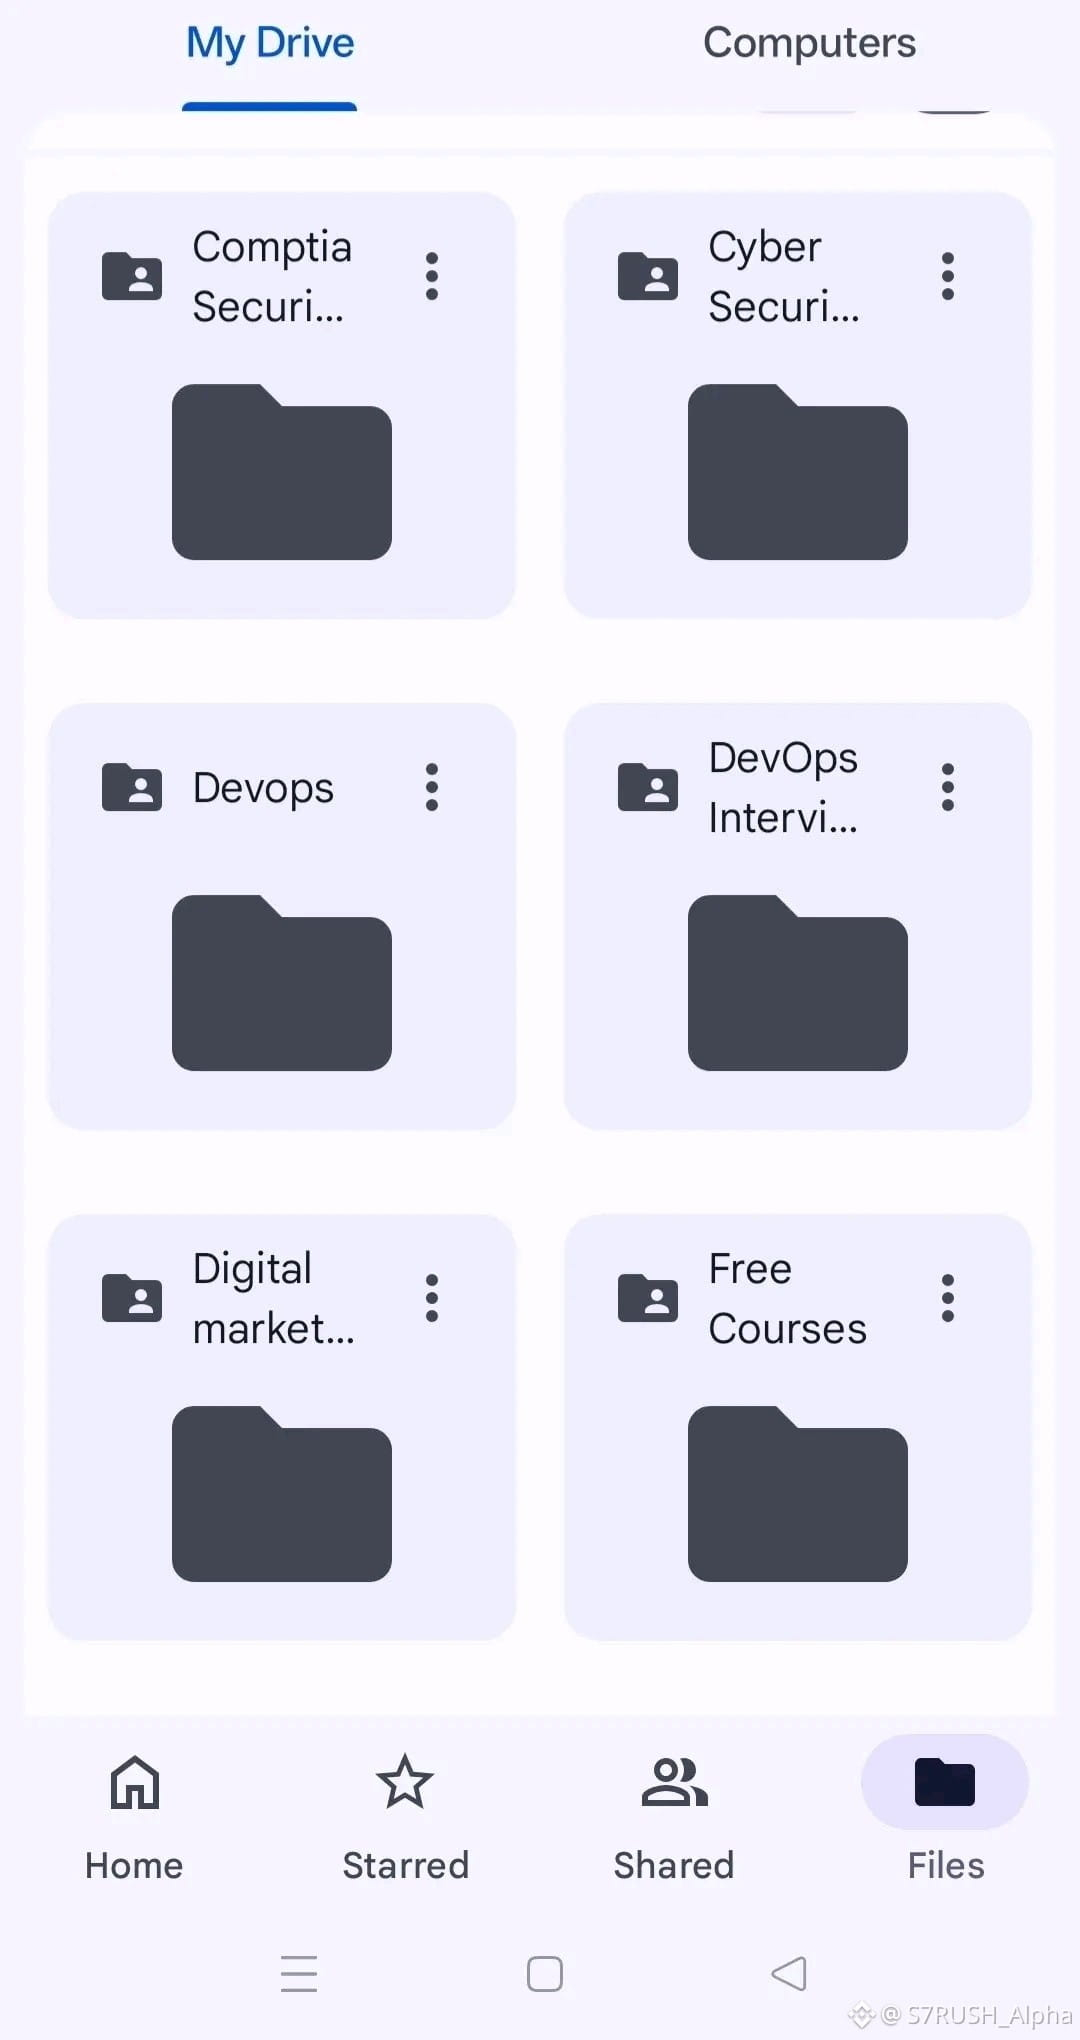
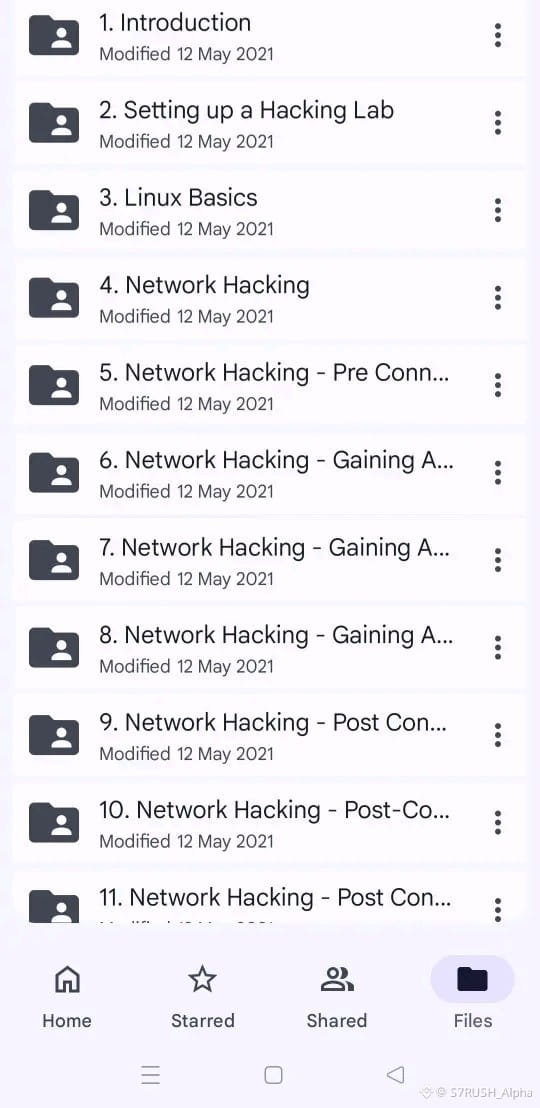
50+ GB Cybersecurity Learning Bundle 🚀
A massive collection of resources covering networking, Linux, web security, OSINT, and defensive security workflows.
Perfect for anyone serious about building real cybersecurity skills from beginner to advanced.
Share and Comment "BUNDLE" 🚀👇
#cybersecurity #infosec #learning #linux #NetworkSecurity
A massive collection of resources covering networking, Linux, web security, OSINT, and defensive security workflows.
Perfect for anyone serious about building real cybersecurity skills from beginner to advanced.
Share and Comment "BUNDLE" 🚀👇
#cybersecurity #infosec #learning #linux #NetworkSecurity
26

Vercel’s breach looks bigger than one account ⚡
The team says it reviewed nearly 1 PB of logs and found activity that stretched beyond the original Context.ai incident, with the attacker distributing malware and hunting for platform keys. That turns this from a single-victim event into an ecosystem trust issue, where credential rotation, vendor coordination, and fast containment matter more than headlines. Microsoft, AWS, and Wiz are now in the loop, which suggests the blast radius may be wider than first believed.
Not financial advice. Manage your risk and protect your capital.
#CyberSecurity #Infosec #CloudSecurity #DataBreach #RiskManagementMastery
⚡
11

🚨 كاسبرسكي تحذر: برمجيات خبيثة تستهدف مستثمري العملات المشفرة عبر تطبيقات GitHub مزيفة!
أعلنت شركة الأمن السيبراني كاسبرسكي عن اكتشاف إطار عمل جديد لبرمجيات خبيثة يستغل التكتيكات الهندسية الاجتماعية وتطبيقات GitHub المخترقة لاستهداف مستثمري العملات المشفرة، محذرة من مخاطر سرقة الأصول الرقمية.
━━━━━━━━━━━━━━
📊 التأثير: 🔥 مرتفع جداً
🏷️ OTHER
#Kaspersky #Cybersecurity #CryptoScam #Malware #Infosec
🔗 المصدر: https://cointelegraph.com/news/kaspersky-malware-framework-crypto-investors
22
⚽️ هجوم إلكتروني ضخم يستهدف 12 مليون حساب بث خلال كأس العالم ويستهدف محافظ العملات المشفرة
كشف تقرير لشركة HUMAN Security عن سرقة 12 مليون حساب بث مباشر، منها 802 ألف حساب في يونيو 2026، وذلك بالتزامن مع كأس العالم. يشير التقرير إلى تصاعد الجرائم الإلكترونية التي تستهدف حاملي محافظ العملات المشفرة باستخدام برمجيات طروادة المصرفية.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #WorldCup #CryptoCrime #HUMANSafety #InfoSec
🔗 المصدر: https://cryptobriefing.com/human-security-stolen-streaming-accounts-world-cup/
28
🚨 تقرير يكشف عن أساليب جديدة لبرمجيات خبيثة تستهدف المستخدمين
كشف تقرير أمني عن استخدام خدمة تحميل برمجيات خبيثة روسية جديدة تُعرف باسم DOUBLECUP، تقنيات مبتكرة لتضمين برمجيات ضارة. تعتمد هذه الخدمة على خداع المستخدمين من خلال ClickFix لتخزين صور PNG ملغومة بالبرمجيات الخبيثة في ذاكرة التخزين المؤقت للمتصفح، ومن ثم توزيع برمجيات CountLoader وحصان طروادة للتحكم عن بعد DeviceManager.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #Malware #Trojans #Cybercrime #Infosec
📰 المصدر: thehackernews.com
11

·
--
Anthropic breach rumor keeps $A on the radar 🔍
The ShinyHunters claim matters less for the screenshots and more for the signal: internal model dashboards, user controls, and cost/performance data are now prime targets. If this is confirmed, institutions will likely treat AI infrastructure as a widening attack surface, with spillover risk for vendors and crypto-adjacent companies built on the stack.
Not financial advice. Manage your risk and protect your capital.
#Aİ #CyberSecurity #Anthropic #Infosec #Crypto
✦
{future}(AIXBTUSDT)
Anthropic breach rumor keeps $A on the radar 🔍
The ShinyHunters claim matters less for the screenshots and more for the signal: internal model dashboards, user controls, and cost/performance data are now prime targets. If this is confirmed, institutions will likely treat AI infrastructure as a widening attack surface, with spillover risk for vendors and crypto-adjacent companies built on the stack.
Not financial advice. Manage your risk and protect your capital.
#Aİ #CyberSecurity #Anthropic #Infosec #Crypto
✦
30
🚨 هجوم ChainDrop البرمجي يستهدف حزم npm ويصيب 1300 منها
كشف تقرير أمني عن اتساع نطاق هجوم ChainDrop البرمجي، حيث استهدف أكثر من 1300 حزمة في مستودعات npm الشهيرة. يستخدم المهاجمون تدفقات عمل GitHub Actions شرعية لنشر التعليمات البرمجية الضارة، مما يؤثر على مشاريع برمجية تعتمد على هذه الحزم.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 المصدر: 4sysops.com
12
Connectez-vous pour découvrir plus de contenu
Rejoignez la communauté mondiale des adeptes de cryptomonnaies sur Binance Square
⚡️ Suviez les dernières informations importantes sur les cryptomonnaies.
💬 Jugé digne de confiance par la plus grande plateforme d’échange de cryptomonnaies au monde.
👍 Découvrez les connaissances que partagent les créateurs vérifiés.
Adresse e-mail/Nº de téléphone
Sujets d’actualité
1
#UKFCAWinsCourtOrderToRecover851400Pounds
9,749 vues
520 mentions
2
#ChainlinkLaunchesCCIP2WithEnterpriseVerification
23,563 vues
739 mentions
3
#GoldFallsTo$4144
9,422 vues
122 mentions
4
#QNTFallsOver40%FromMorningHigh
59,846 vues
1,148 mentions
5
#USDTAdds845900HoldersInPast7Days
7,859 vues
301 mentions
6
#KospiFalls2.7%SamsungSKHynixDropOver5%
16,271 vues
492 mentions
7
#BitgetCEOConfirms$388MStolenInHack
4,275 vues
39 mentions
8
#BTCFallsBelow$83000
24,583 vues
154 mentions
9
#BitgetDetailsSecurityIncidentTimeline
32,561 vues
628 mentions
10
#BitcoinSpotETFs$2.39BWeeklyNetInflow
10,746 vues
43 mentions