
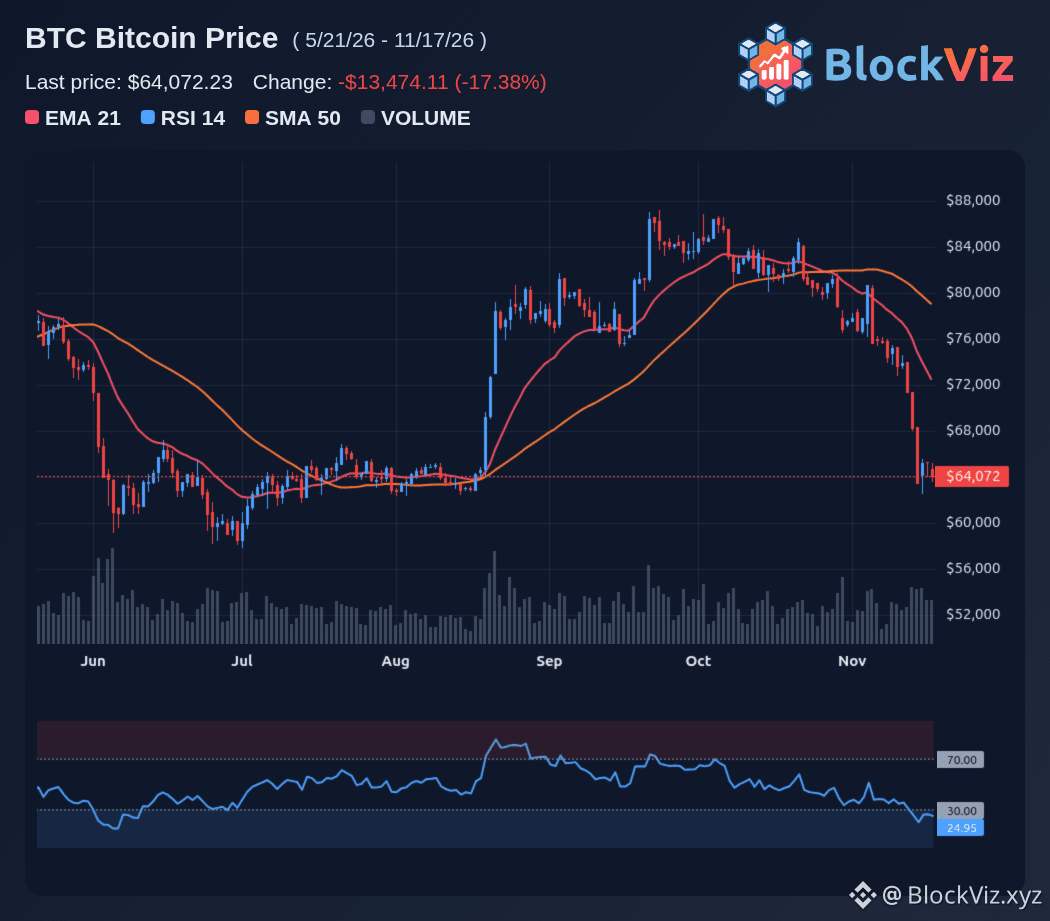
One compromised script can turn a single security failure into a problem across 178 trusted websites, including names such as HSBC, the BBC, and Ledger. That changes the question from “Which company was hacked?” to “Who controlled the dependency that failed?” A third-party script, tag manager, or shared web component can make an otherwise secure domain serve hostile content without its core systems being breached. For crypto users, the immediate risk may sit in the browser session rather than the wallet itself. A modified page can present a fake support prompt, request a recovery phrase, or trick someone into approving a transaction. The trusted domain becomes the delivery mechanism. Responsibility should follow that failure point. If a supplier was compromised, the affected sites still need to isolate the integration, revoke access, and prove the injection is gone. If their own infrastructure introduced the code, the accountability is more direct. The deeper lesson is that brand security now depends on every external component a site trusts. One poisoned integration can make hundreds of unrelated domains appear compromised at once. $BTC
Únete a usuarios de criptomonedas de todo el mundo en Binance Square
⚡️ Obtén la información más reciente y útil sobre criptomonedas.
💬 Confía en el mayor exchange de criptomonedas del mundo.
👍 Descubre opiniones reales de creadores verificados.
Correo electrónico/número de teléfono