
MartIn-赚钱版
7 Posts

MartIn-赚钱版
Report
Block User
2 Following
43 Followers
34 Liked
Posts
·
--
See translation
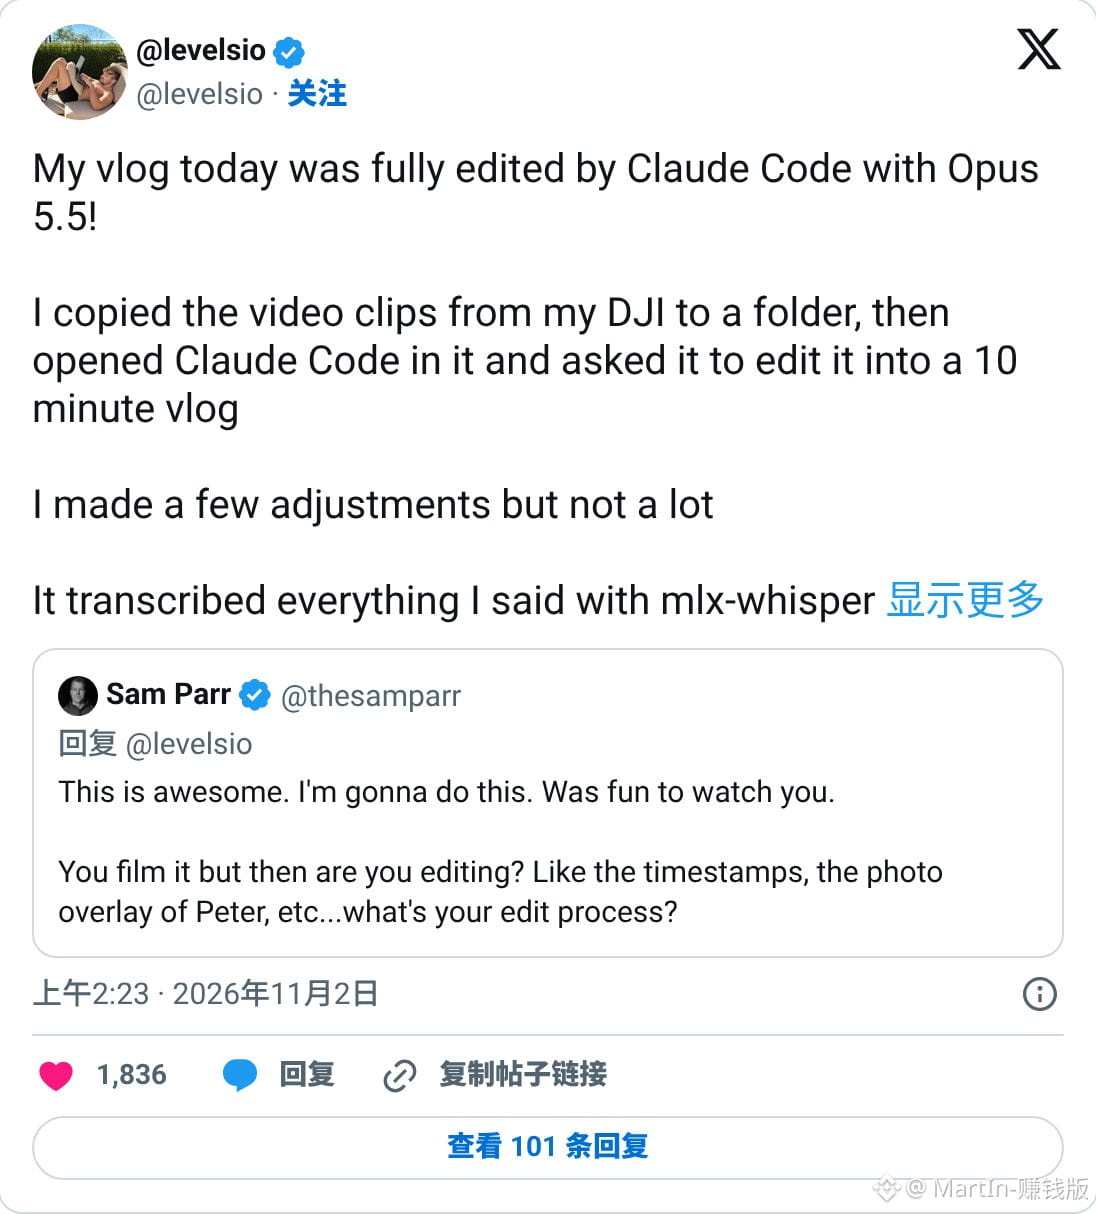
剪辑师该慌了,有人一句话丢给 Claude Code,58 分钟素材自己剪成了 10 分钟 vlog
levelsio 把大疆里拍的素材全拷进一个文件夹,在里面打开 Claude Code
就说了一句“帮我把这些剪成一条发 X 和 YouTube 的 vlog”
Claude 先在他 MacBook 上把他说的话全转成文字
再每隔几秒抽一帧拼成大图看画面,连哪句是他本人在说都分得出来
最后挑片段写成一张剪辑表,58 分钟素材剪到 10 分钟左右
这些步骤是有人问他怎么剪的,他回头翻了才知道
他说要是没 AI 剪,他压根不会拍 vlog
剪辑师该慌了,有人一句话丢给 Claude Code,58 分钟素材自己剪成了 10 分钟 vlog
levelsio 把大疆里拍的素材全拷进一个文件夹,在里面打开 Claude Code
就说了一句“帮我把这些剪成一条发 X 和 YouTube 的 vlog”
Claude 先在他 MacBook 上把他说的话全转成文字
再每隔几秒抽一帧拼成大图看画面,连哪句是他本人在说都分得出来
最后挑片段写成一张剪辑表,58 分钟素材剪到 10 分钟左右
这些步骤是有人问他怎么剪的,他回头翻了才知道
他说要是没 AI 剪,他压根不会拍 vlog
levelsio 把大疆里拍的素材全拷进一个文件夹,在里面打开 Claude Code
就说了一句“帮我把这些剪成一条发 X 和 YouTube 的 vlog”
Claude 先在他 MacBook 上把他说的话全转成文字
再每隔几秒抽一帧拼成大图看画面,连哪句是他本人在说都分得出来
最后挑片段写成一张剪辑表,58 分钟素材剪到 10 分钟左右
这些步骤是有人问他怎么剪的,他回头翻了才知道
他说要是没 AI 剪,他压根不会拍 vlog
14
·
--
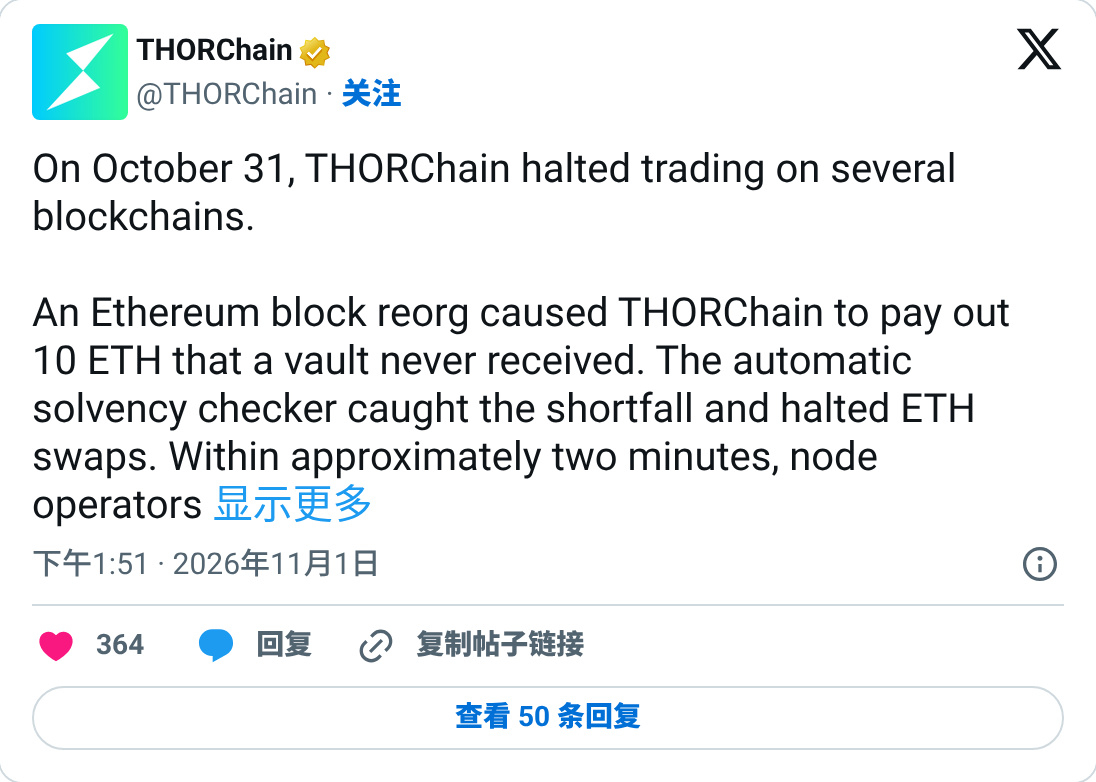
THORChain has been halted for nearly two days and still hasn't dared to reopen. The official reason? This vulnerability is already common knowledge.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
THORChain has been halted for nearly two days and still hasn't dared to reopen. The official reason? This vulnerability is already common knowledge.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
1
1
827
·
--
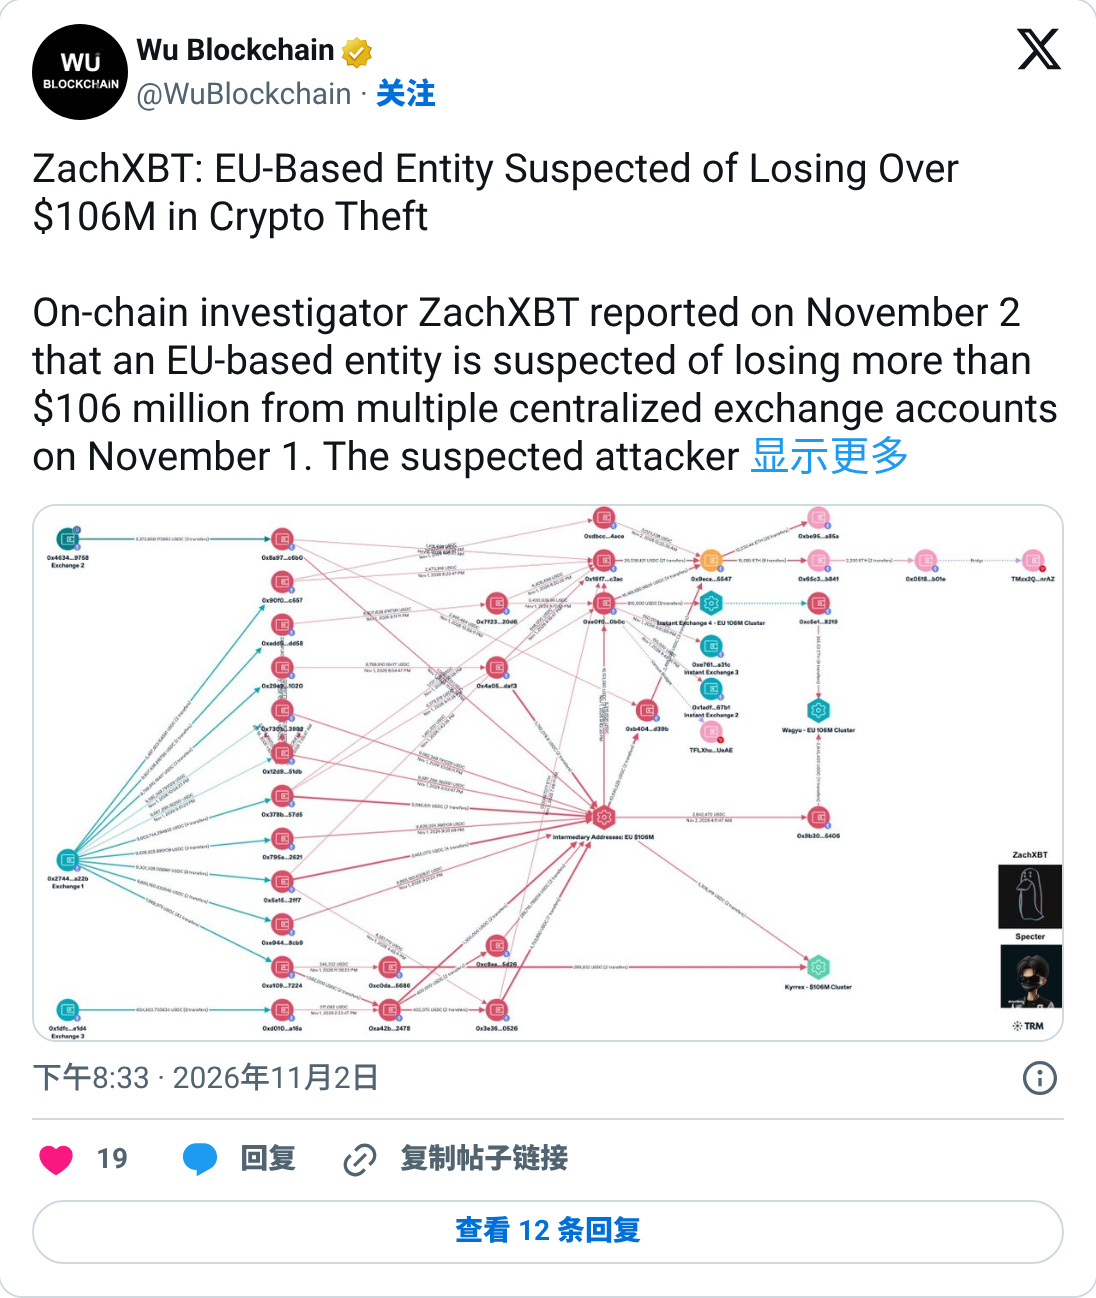
The money in your exchange account could be drained in a single day
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
The money in your exchange account could be drained in a single day
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
850
·
--
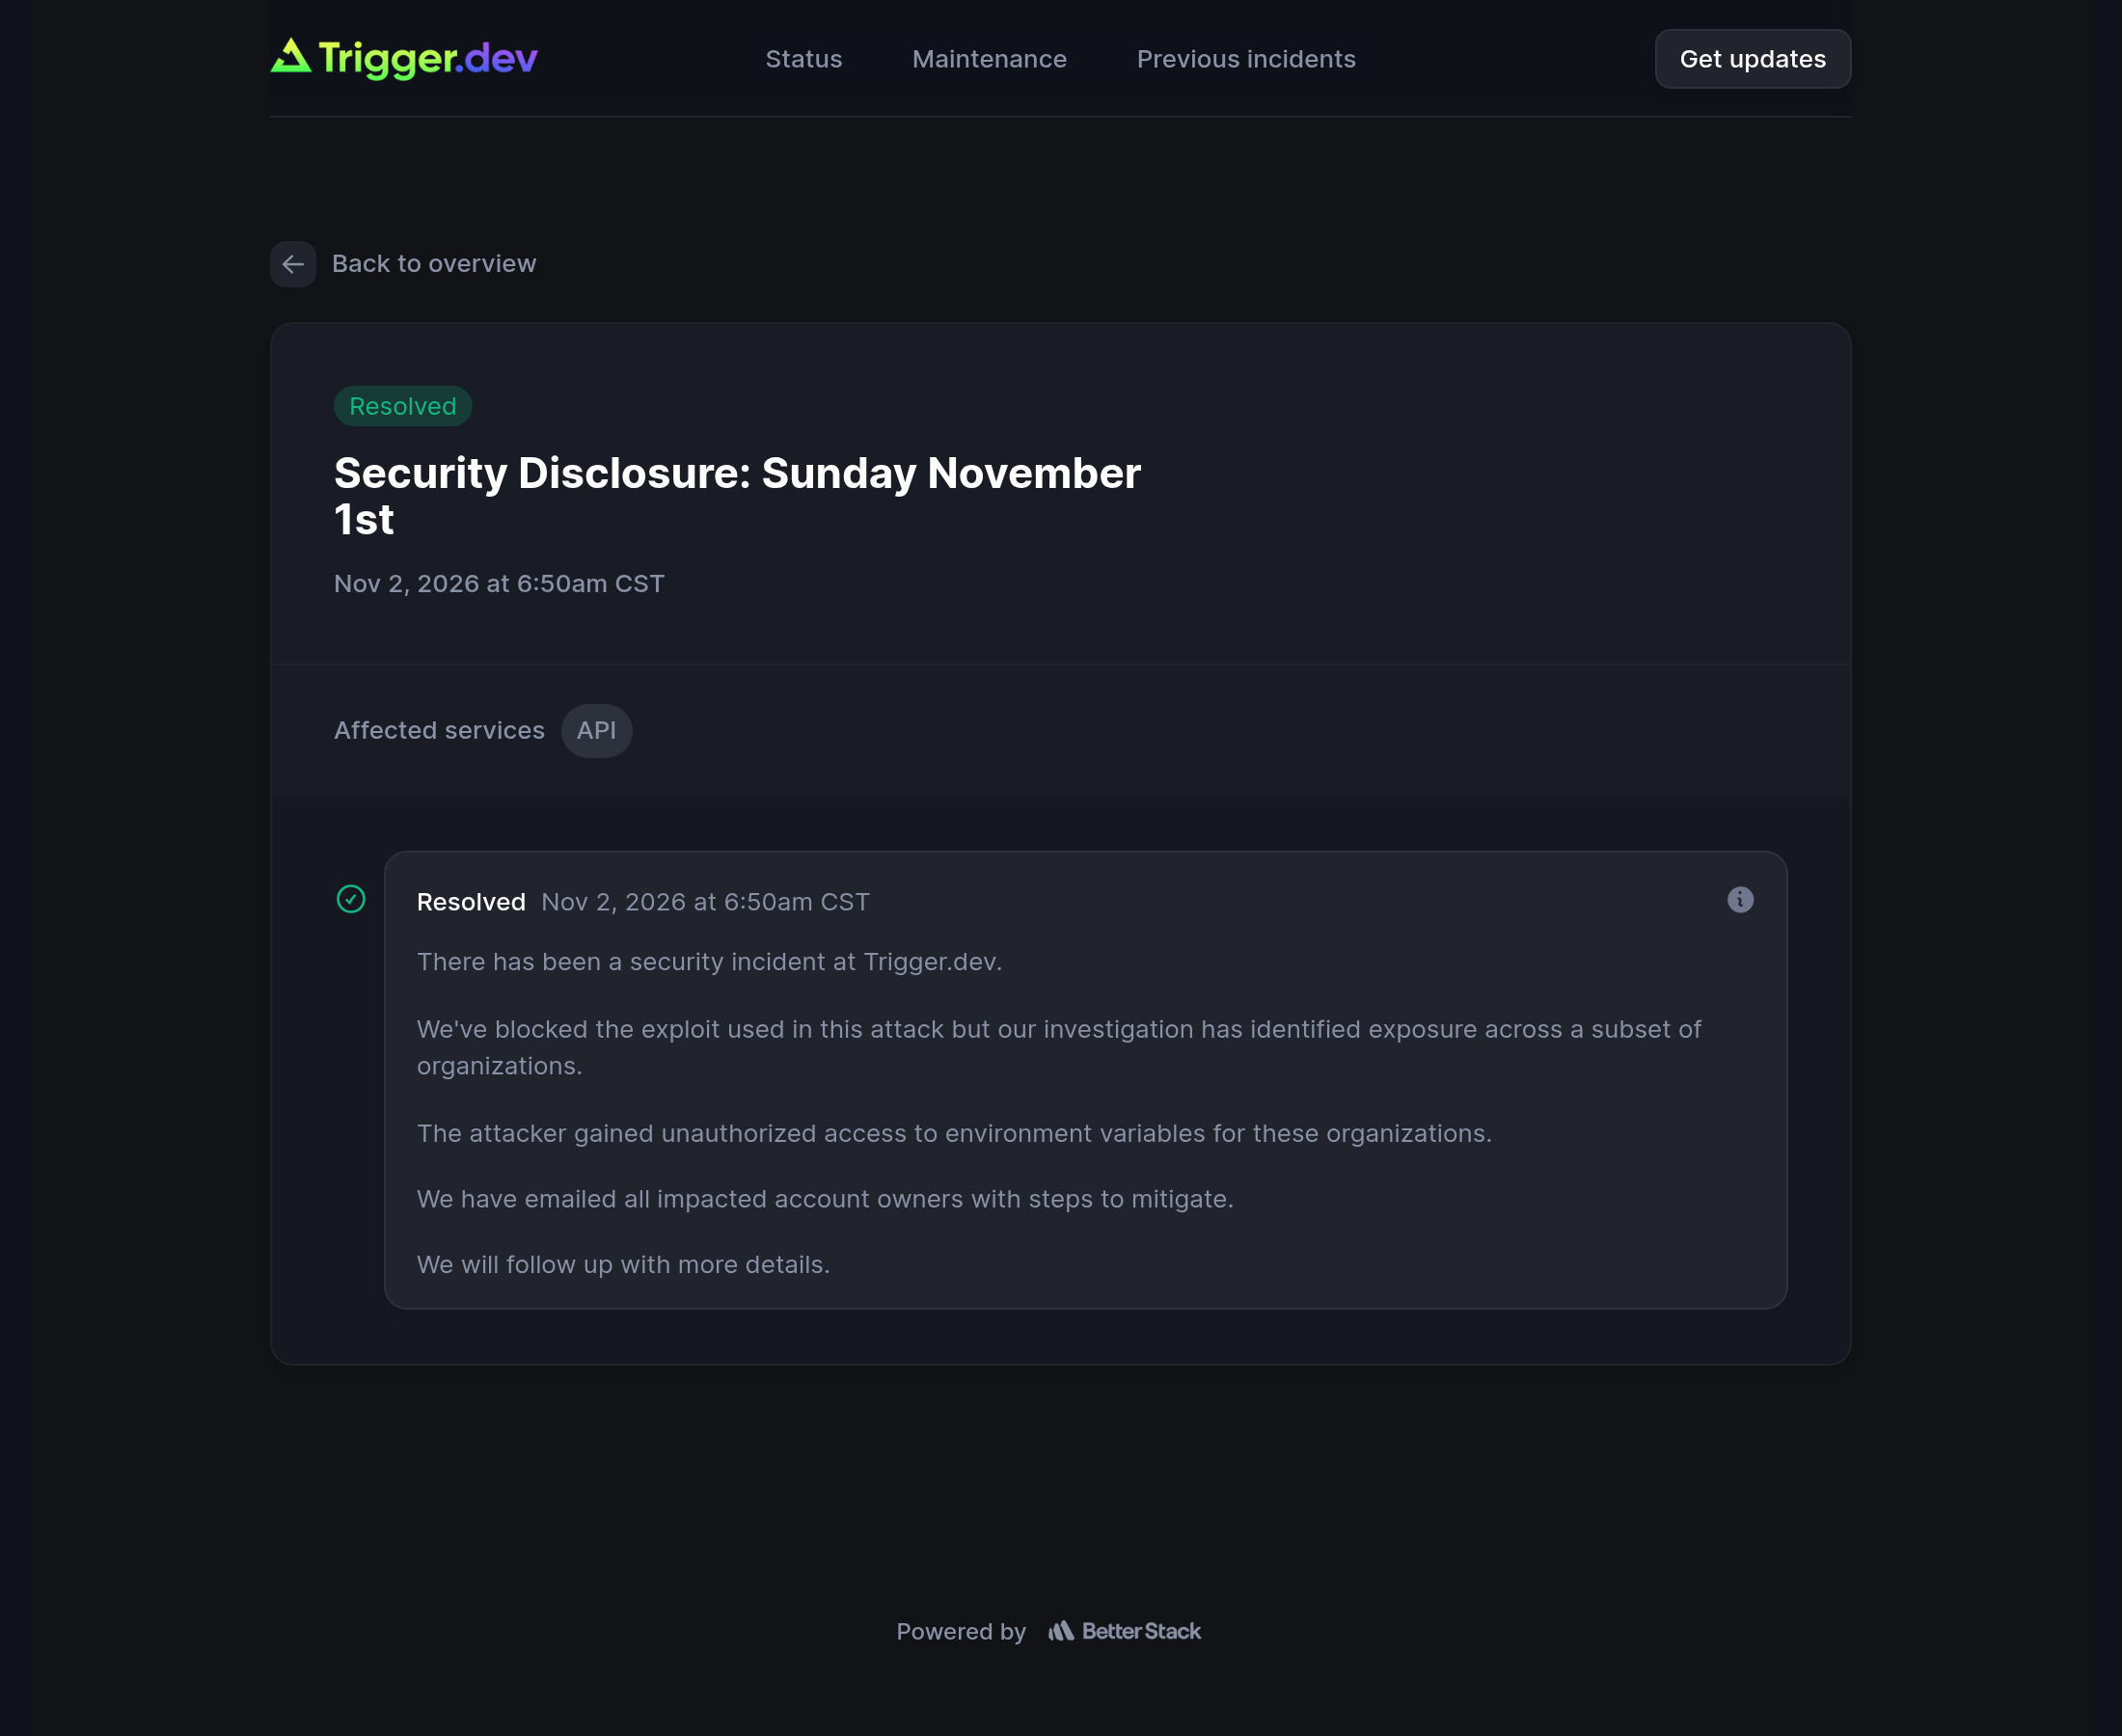
In October, 9 AI development platforms had their environment variables exposed. On the first day of November, it happened to another one.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
In October, 9 AI development platforms had their environment variables exposed. On the first day of November, it happened to another one.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
122
·
--
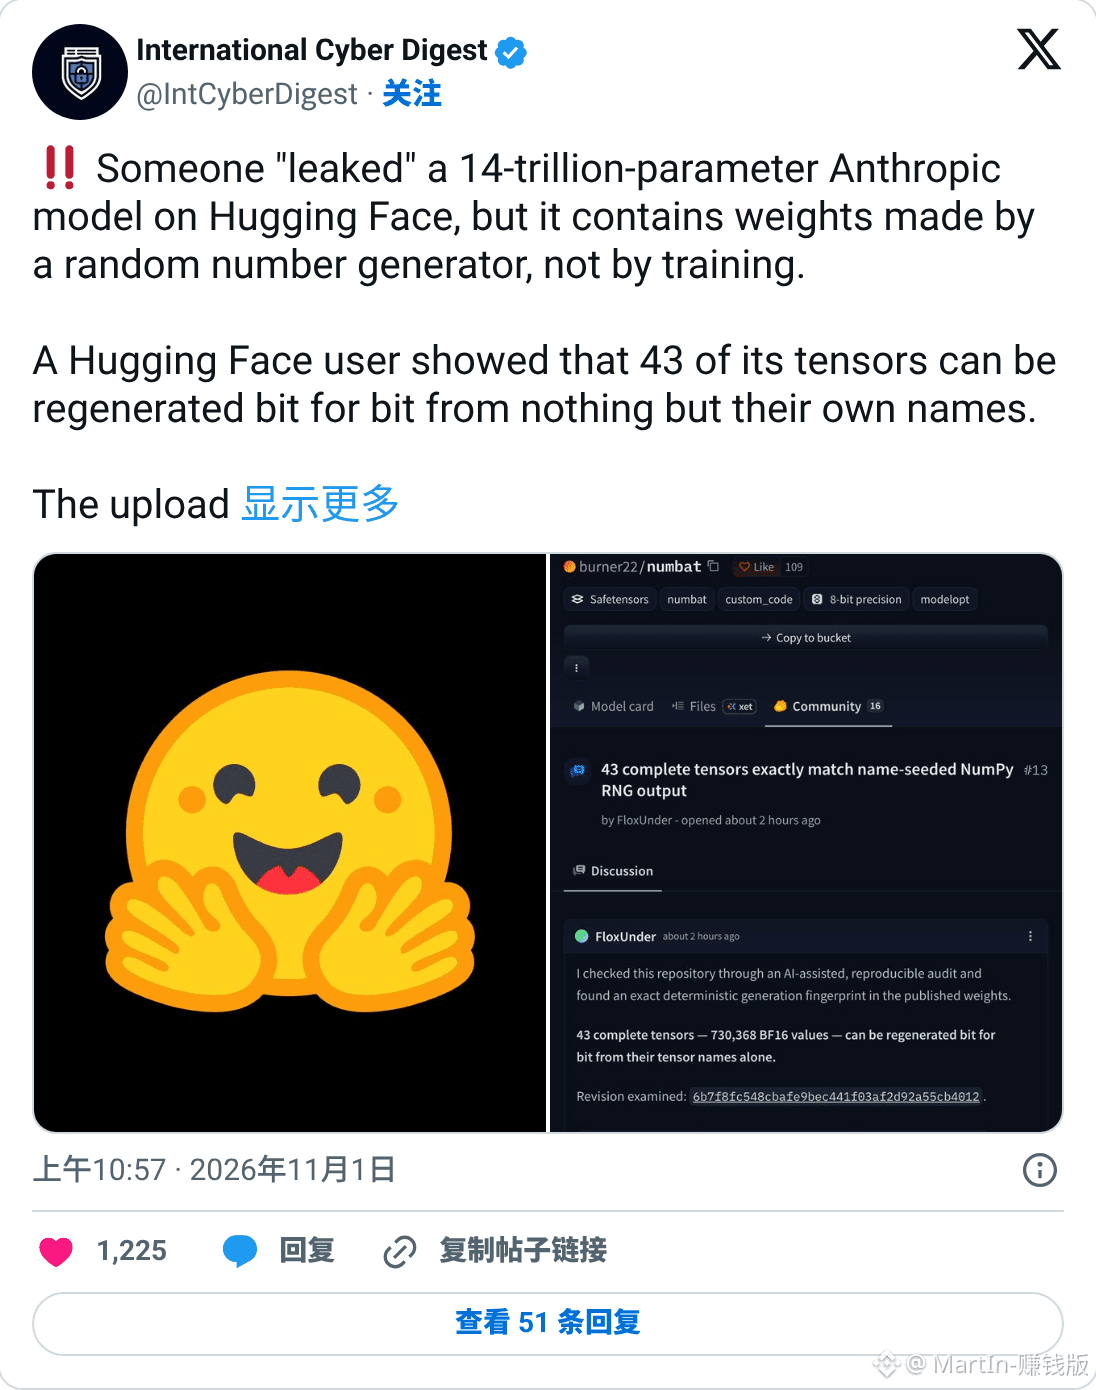
That “leaked Anthropic model” flooding everyone’s feeds? Someone actually downloaded the whole thing—over 7 TB—and it’s all random numbers
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
That “leaked Anthropic model” flooding everyone’s feeds? Someone actually downloaded the whole thing—over 7 TB—and it’s all random numbers
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
157
·
--
A heads-up if you're making games with Claude Code: if it rejects your work, don't rush to switch tools. Someone at Anthropic has left an appeal channel open.
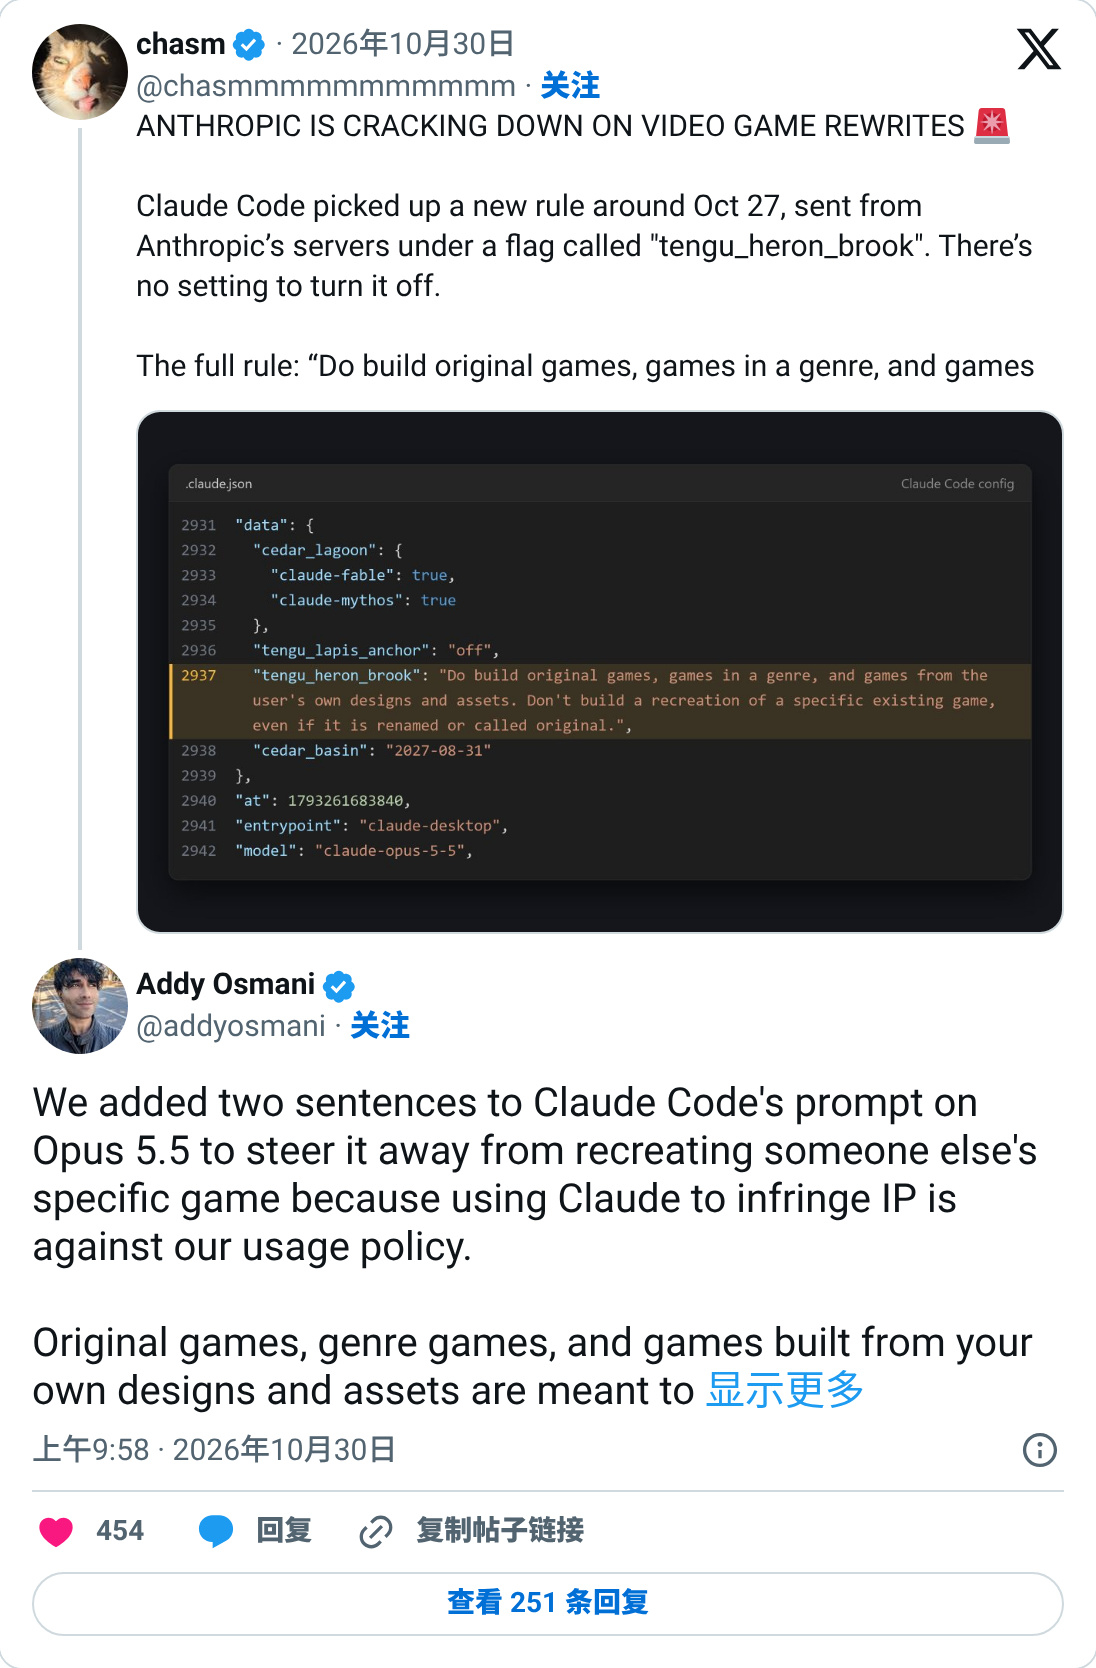
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
A heads-up if you're making games with Claude Code: if it rejects your work, don't rush to switch tools. Someone at Anthropic has left an appeal channel open.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
173
·
--
oh my claude can be uninstalled
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
oh my claude can be uninstalled
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
71
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
BinanceWithdrawalScamWarning
17,770 views
459 Discussing
Binance Warns Users of Withdrawal Scams as Services Resume: It Will Never Charge Fees, Sell Queue Spots or Ask You to Move Funds to a “Vault”
Binance News
·10 Likes
·5.6k views
USMidtermElections
570,264 views
3,023 Discussing
USOctoberNFP-AreRateCutsStillPossible
25,855 views
422 Discussing