

Cryptopolitan
58.4k Posts

Cryptopolitan
 Square Verified+
Report
Block User
Crypto news that doesn't waste your time. Breaking updates, market analysis, on-chain insights. Building the smartest crypto community.

Creator of the Year
1 Following
161.5K+ Followers
573.5K+ Liked
1 Badges
Posts
PINNED
At Cryptopolitan, we research, analyze, and deliver news—daily.
From breaking updates to in-depth analysis, educational guides, and market insights, we’re here to keep you informed with neutral and authentic news.
Thank you for trusting us to be your go-to source!
At Cryptopolitan, we research, analyze, and deliver news—daily.
From breaking updates to in-depth analysis, educational guides, and market insights, we’re here to keep you informed with neutral and authentic news.
Thank you for trusting us to be your go-to source!
From breaking updates to in-depth analysis, educational guides, and market insights, we’re here to keep you informed with neutral and authentic news.
Thank you for trusting us to be your go-to source!
120
68
343
1.8k
Texas brothers get 366 months combined for $8M crypto kidnapping in MinnesotaTwo brothers from Waller, Texas, have been sentenced to a combined 366 months in federal prison.
The pair have been found guilty of holding a Minnesota family at gunpoint and forcing the theft of more than $8 million in cryptocurrency.
Have Raymond and Isiah Garcia been sentenced?
The U.S. Attorney’s Office for the District of Minnesota announced on Friday that Raymond Christian Garcia and his brother Isiah Angelo Garcia have been sentenced to 180 and 186 months in prison, respectively, for their role in the attack on a Minnesota family.
U.S. District Judge Donovan W. Frank handed down the sentences on Thursday after both men had pleaded guilty on June 18 to one count each of interference with commerce by robbery.
The brothers drove from Texas to a home in Grant, Minnesota, on September 19, 2025, planning to steal a family’s cryptocurrency. Court documents cited by the Justice Department say they bound the family with zip ties and held them at gunpoint for over nine hours.
Raymond Garcia reportedly stood guard over the man’s wife and adult son, armed with an AR-15-style rifle, while Isiah Garcia made the father, who was called Victim 1 in the filings, log into his accounts and send his funds to a wallet the brothers controlled.
When the first transfers fell short of what the brothers expected, Isiah Garcia drove Victim 1 roughly three hours to the family’s cabin in northern Minnesota to retrieve a hardware wallet and move the rest. The total stolen amount was more than $8 million.
The brothers agreed to pay more than $8 million in restitution as part of their pleas.
How were the Garcia brothers caught?
The brothers fled after the victim’s son called 911. A September 2025 DOJ account says that deputies found a suitcase in the tree line behind the home holding a disassembled AR-15-style rifle, ammunition, and a Wendy’s receipt. That receipt helped investigators trace a rental car to the Houston area, where law enforcement arrested the two near their home in Waller.
The Washington County complaint initially pegged the stolen crypto at about $72,000, which was far below the more than $8 million figure the U.S. Attorney’s Office later revealed.
The victim believed some of his account information had leaked in a data breach, and filings say the brothers were repeatedly on the phone with an unidentified third party who fed them details about the accounts.
Cryptopolitan has previously covered the documented rise in physical attacks on crypto holders, known as wrench attacks. Chainalysis counted 46 such incidents worldwide in the first half of 2026, with reported home invasions jumping from one case in 2025 to 20.
The Web3 security firm CertiK documented 34 attacks in the first four months of 2026 and said the attacks have led to $101 million in losses. Notably, 82% of these wrench attacks happened in France.
If you're reading this, you’re already ahead. Stay there with our newsletter.
Texas brothers get 366 months combined for $8M crypto kidnapping in Minnesota
Two brothers from Waller, Texas, have been sentenced to a combined 366 months in federal prison.
The pair have been found guilty of holding a Minnesota family at gunpoint and forcing the theft of more than $8 million in cryptocurrency.
Have Raymond and Isiah Garcia been sentenced?
The U.S. Attorney’s Office for the District of Minnesota announced on Friday that Raymond Christian Garcia and his brother Isiah Angelo Garcia have been sentenced to 180 and 186 months in prison, respectively, for their role in the attack on a Minnesota family.
U.S. District Judge Donovan W. Frank handed down the sentences on Thursday after both men had pleaded guilty on June 18 to one count each of interference with commerce by robbery.
The brothers drove from Texas to a home in Grant, Minnesota, on September 19, 2025, planning to steal a family’s cryptocurrency. Court documents cited by the Justice Department say they bound the family with zip ties and held them at gunpoint for over nine hours.
Raymond Garcia reportedly stood guard over the man’s wife and adult son, armed with an AR-15-style rifle, while Isiah Garcia made the father, who was called Victim 1 in the filings, log into his accounts and send his funds to a wallet the brothers controlled.
When the first transfers fell short of what the brothers expected, Isiah Garcia drove Victim 1 roughly three hours to the family’s cabin in northern Minnesota to retrieve a hardware wallet and move the rest. The total stolen amount was more than $8 million.
The brothers agreed to pay more than $8 million in restitution as part of their pleas.
How were the Garcia brothers caught?
The brothers fled after the victim’s son called 911. A September 2025 DOJ account says that deputies found a suitcase in the tree line behind the home holding a disassembled AR-15-style rifle, ammunition, and a Wendy’s receipt. That receipt helped investigators trace a rental car to the Houston area, where law enforcement arrested the two near their home in Waller.
The Washington County complaint initially pegged the stolen crypto at about $72,000, which was far below the more than $8 million figure the U.S. Attorney’s Office later revealed.
The victim believed some of his account information had leaked in a data breach, and filings say the brothers were repeatedly on the phone with an unidentified third party who fed them details about the accounts.
Cryptopolitan has previously covered the documented rise in physical attacks on crypto holders, known as wrench attacks. Chainalysis counted 46 such incidents worldwide in the first half of 2026, with reported home invasions jumping from one case in 2025 to 20.
The Web3 security firm CertiK documented 34 attacks in the first four months of 2026 and said the attacks have led to $101 million in losses. Notably, 82% of these wrench attacks happened in France.
If you're reading this, you’re already ahead. Stay there with our newsletter.
243
Israel extradites Nomad exploit suspect after rejecting 'code is law' defenseIsrael handed Alexander Block to U.S. prosecutors on Thursday to face charges over a $2.8 million exploit of the Nomad crypto bridge.
The extradition was processed after Israel’s Supreme Court ruled that taking advantage of a software flaw can be criminal even when the code permits it and blocked any further appeals on the case.
Why was Alexander Block extradited to the U.S.?
Alexander Block, an Israeli-Russian citizen who previously went by Alexander Gurevich, has been handed over to U.S. prosecutors to face charges regarding a $2.8 million exploit of the Nomad crypto bridge.
Block argued before Israeli judges that despite the fact that he exploited a flaw, everything he did used functions Nomad’s automated system allowed. He also argued that the public blockchain record of his transfers cancels out any money-laundering charge.
The Supreme Court disagreed and ruled that deliberately exploiting a bug to take funds counts as criminal computer intrusion, and that the contract permitting his actions does not work as a defense. It also said that a wallet’s transactions being publicly visible doesn’t reveal who controls it, and doesn’t rule out an attempt to hide where the money came from.
Supreme Court President Isaac Amit then denied Block’s request for another hearing, and with no appeals left, the prosecution’s international department, the Israel Police, and Interpol coordinated his extradition.
How did the Nomad drain start?
Nomad was a bridge built by Illusory Systems that allowed users to move value between blockchains. It worked by locking assets on one chain before releasing matching tokens on another.
Prosecutors in the Northern District of California say a June 2022 update to Nomad’s smart contracts created a flaw in that system that was then exploited by bad actors.
The extradition request cited in the Israeli ruling says that a user named “Bitlik” was behind the first thefts. He allegedly made six test transfers to probe the bug, then four real ones worth more than $2.8 million on or around August 1, 2022.
To hide where the money came from, Block allegedly moved it between wallets and converted it into other cryptocurrencies.
His transfers also exposed the bug to everyone else. Other users rushed in and emptied a Nomad wallet that held more than $186 million, in a free-for-all that wiped out nearly all of the bridge’s funds.
In August 2023, a federal grand jury indicted Block on eight counts, covering computer fraud, transporting stolen property, and money laundering.
The U.S. asked for his extradition in December 2024, and Israeli police arrested him at Ben-Gurion Airport in May 2025 as he prepared to board a flight to Russia, days after he swapped the surname Gurevich for Block and picked up a passport in the new name.
Do U.S. juries agree with “code is law”?
Unlike the Israeli Supreme Court’s rejection of Block’s “code is law” argument, the U.S. verdicts have been inconsistent.
For example, in May 2025, U.S. District Judge Arun Subramanian threw out the fraud convictions of Avraham Eisenberg, who had exploited the Mango Markets platform. His reasons were that New York was the wrong place to try the case, and that Mango Markets had no rule against what Eisenberg did.
“Code is law” is the argument that if a smart contract allows an action, the action can’t be a crime.
A Manhattan jury was locked in a stalemate in November 2025 over brothers Anton and James Peraire-Bueno, who were accused of a $25 million Ethereum scheme. The judge eventually declared a mistrial and prosecutors asked to retry them in early 2026.
Then on October 7, another Manhattan jury needed only about two hours to find Uranium Finance hacker Jonathan Spalletta guilty on computer-fraud and money-laundering counts tied to a pair of 2021 attacks that cost the exchange more than $50 million.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Israel extradites Nomad exploit suspect after rejecting 'code is law' defense
Israel handed Alexander Block to U.S. prosecutors on Thursday to face charges over a $2.8 million exploit of the Nomad crypto bridge.
The extradition was processed after Israel’s Supreme Court ruled that taking advantage of a software flaw can be criminal even when the code permits it and blocked any further appeals on the case.
Why was Alexander Block extradited to the U.S.?
Alexander Block, an Israeli-Russian citizen who previously went by Alexander Gurevich, has been handed over to U.S. prosecutors to face charges regarding a $2.8 million exploit of the Nomad crypto bridge.
Block argued before Israeli judges that despite the fact that he exploited a flaw, everything he did used functions Nomad’s automated system allowed. He also argued that the public blockchain record of his transfers cancels out any money-laundering charge.
The Supreme Court disagreed and ruled that deliberately exploiting a bug to take funds counts as criminal computer intrusion, and that the contract permitting his actions does not work as a defense. It also said that a wallet’s transactions being publicly visible doesn’t reveal who controls it, and doesn’t rule out an attempt to hide where the money came from.
Supreme Court President Isaac Amit then denied Block’s request for another hearing, and with no appeals left, the prosecution’s international department, the Israel Police, and Interpol coordinated his extradition.
How did the Nomad drain start?
Nomad was a bridge built by Illusory Systems that allowed users to move value between blockchains. It worked by locking assets on one chain before releasing matching tokens on another.
Prosecutors in the Northern District of California say a June 2022 update to Nomad’s smart contracts created a flaw in that system that was then exploited by bad actors.
The extradition request cited in the Israeli ruling says that a user named “Bitlik” was behind the first thefts. He allegedly made six test transfers to probe the bug, then four real ones worth more than $2.8 million on or around August 1, 2022.
To hide where the money came from, Block allegedly moved it between wallets and converted it into other cryptocurrencies.
His transfers also exposed the bug to everyone else. Other users rushed in and emptied a Nomad wallet that held more than $186 million, in a free-for-all that wiped out nearly all of the bridge’s funds.
In August 2023, a federal grand jury indicted Block on eight counts, covering computer fraud, transporting stolen property, and money laundering.
The U.S. asked for his extradition in December 2024, and Israeli police arrested him at Ben-Gurion Airport in May 2025 as he prepared to board a flight to Russia, days after he swapped the surname Gurevich for Block and picked up a passport in the new name.
Do U.S. juries agree with “code is law”?
Unlike the Israeli Supreme Court’s rejection of Block’s “code is law” argument, the U.S. verdicts have been inconsistent.
For example, in May 2025, U.S. District Judge Arun Subramanian threw out the fraud convictions of Avraham Eisenberg, who had exploited the Mango Markets platform. His reasons were that New York was the wrong place to try the case, and that Mango Markets had no rule against what Eisenberg did.
“Code is law” is the argument that if a smart contract allows an action, the action can’t be a crime.
A Manhattan jury was locked in a stalemate in November 2025 over brothers Anton and James Peraire-Bueno, who were accused of a $25 million Ethereum scheme. The judge eventually declared a mistrial and prosecutors asked to retry them in early 2026.
Then on October 7, another Manhattan jury needed only about two hours to find Uranium Finance hacker Jonathan Spalletta guilty on computer-fraud and money-laundering counts tied to a pair of 2021 attacks that cost the exchange more than $50 million.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
1.2k
Verified
ChangeNOW moves from simple swap tool toward crypto super app as it courts wallet builders at Tok...ChangeNOW is expanding beyond cryptocurrency swaps as it seeks to build a platform combining digital asset management, payments and infrastructure for businesses, according to Pauline Shangett, the company’s chief strategy officer.
The company, which began operating in 2017, has added a crypto wallet, loans and trading features to its original exchange service.
In an interview with Cryptopolitan at the Token2049 event, Shangett said that payment cards are also planned, as ChangeNOW works toward becoming a one-stop platform for people who want to acquire, hold and spend digital assets.
How is ChangeNOW moving beyond cryptocurrency swaps?
Shangett said that they are morphing into a super app. While she said that what they are doing does have neobank functionalities, the super app rings better, as they have been bringing multiple services into a single platform.
Shangett cited the growth of real-world assets (RWAs) as one factor contributing to crypto’s potential to reach mainstream users. She said, “What we’re doing right now is like trying to become like truly a one-stop shop for anybody who wants to interact with crypto, who wants to own crypto, and most importantly, who wants to pay in crypto.”
The company is also investing more in public relations, events and brand recognition. Shangett said ChangeNOW had relied largely on search engine optimization and social media for much of its history, but it has now expanded its marketing efforts in recent years.
It plans to continue that work through more industry events, speaking engagements and media appearances, she said.
How is ChangeNOW building its business around crypto infrastructure and payments?
Beyond its consumer platform, ChangeNOW provides infrastructure for companies building cryptocurrency products. Shangett said, “Right now, we have more than 5,000 infrastructure partners who use our API as a way for them to either monetize their business or just expand and grow.”
ChangeNOW also has B2B offerings and they include swaps, custody, liquidity, loans, payment services, and wallet infrastructure, which Shangett called “wallet as a service.”
The company has also introduced private transfers, which route payments through the company’s infrastructure so recipients do not directly see the sender’s wallet address in the final transaction path.
One of the possible use cases of that feature, according to Shangett, is paying employees for businesses that do that over the blockchain, where publicly visible wallet balances and transaction histories may create privacy concerns.
Early-stage wallet companies can also access ChangeNOW’s functionality without charge under the firm’s Fast-Track program. ChangeNOW also gives support in other capacities such as marketing and public relations.
Shangett said the program is intended to help founders generate revenue while covering development, infrastructure and customer acquisition costs.
ChangeNOW is also working with hardware wallet providers, including Ledger and Trezor. It has partnered with CoolWallet on a co-branded product.
Licensing requirements shaping ChangeNOW’s expansion
As ChangeNOW adds services, licensing has become one of its main strategic challenges, Shangett said.
“When you’re adding on new features, more and more of them are restricted to certain markets,” Shangett said, adding that they are “working on obtaining all the necessary paperwork to expand ourselves into the markets that we’re not available in.”
She said ChangeNOW limits access in sanctioned jurisdictions, markets where using its services could be unsafe, and countries where it has not obtained the necessary licenses or permissions.
She said that the company refunds transactions that come from restricted markets and blocks the originating IP addresses. The company is still working towards obtaining the permissions needed to enter other markets.
As ChangeNOW expands its product offering, Shangett said, the challenge will be to make more crypto services available while maintaining the standards the company expects from its partners.
ChangeNOW moves from simple swap tool toward crypto super app as it courts wallet builders at Tok...
ChangeNOW is expanding beyond cryptocurrency swaps as it seeks to build a platform combining digital asset management, payments and infrastructure for businesses, according to Pauline Shangett, the company’s chief strategy officer.
The company, which began operating in 2017, has added a crypto wallet, loans and trading features to its original exchange service.
In an interview with Cryptopolitan at the Token2049 event, Shangett said that payment cards are also planned, as ChangeNOW works toward becoming a one-stop platform for people who want to acquire, hold and spend digital assets.
How is ChangeNOW moving beyond cryptocurrency swaps?
Shangett said that they are morphing into a super app. While she said that what they are doing does have neobank functionalities, the super app rings better, as they have been bringing multiple services into a single platform.
Shangett cited the growth of real-world assets (RWAs) as one factor contributing to crypto’s potential to reach mainstream users. She said, “What we’re doing right now is like trying to become like truly a one-stop shop for anybody who wants to interact with crypto, who wants to own crypto, and most importantly, who wants to pay in crypto.”
The company is also investing more in public relations, events and brand recognition. Shangett said ChangeNOW had relied largely on search engine optimization and social media for much of its history, but it has now expanded its marketing efforts in recent years.
It plans to continue that work through more industry events, speaking engagements and media appearances, she said.
How is ChangeNOW building its business around crypto infrastructure and payments?
Beyond its consumer platform, ChangeNOW provides infrastructure for companies building cryptocurrency products. Shangett said, “Right now, we have more than 5,000 infrastructure partners who use our API as a way for them to either monetize their business or just expand and grow.”
ChangeNOW also has B2B offerings and they include swaps, custody, liquidity, loans, payment services, and wallet infrastructure, which Shangett called “wallet as a service.”
The company has also introduced private transfers, which route payments through the company’s infrastructure so recipients do not directly see the sender’s wallet address in the final transaction path.
One of the possible use cases of that feature, according to Shangett, is paying employees for businesses that do that over the blockchain, where publicly visible wallet balances and transaction histories may create privacy concerns.
Early-stage wallet companies can also access ChangeNOW’s functionality without charge under the firm’s Fast-Track program. ChangeNOW also gives support in other capacities such as marketing and public relations.
Shangett said the program is intended to help founders generate revenue while covering development, infrastructure and customer acquisition costs.
ChangeNOW is also working with hardware wallet providers, including Ledger and Trezor. It has partnered with CoolWallet on a co-branded product.
Licensing requirements shaping ChangeNOW’s expansion
As ChangeNOW adds services, licensing has become one of its main strategic challenges, Shangett said.
“When you’re adding on new features, more and more of them are restricted to certain markets,” Shangett said, adding that they are “working on obtaining all the necessary paperwork to expand ourselves into the markets that we’re not available in.”
She said ChangeNOW limits access in sanctioned jurisdictions, markets where using its services could be unsafe, and countries where it has not obtained the necessary licenses or permissions.
She said that the company refunds transactions that come from restricted markets and blocks the originating IP addresses. The company is still working towards obtaining the permissions needed to enter other markets.
As ChangeNOW expands its product offering, Shangett said, the challenge will be to make more crypto services available while maintaining the standards the company expects from its partners.
1.7k
North Korea's top hacking units have operationalized AI, Microsoft saysMicrosoft says three North Korean hacking groups now use AI in their daily attacks, the highest level on its scale.
Microsoft (NASDAQ: MSFT) rates North Korea’s overall use of AI in hacking as high. The report came out as North Korea is blamed for the biggest crypto theft ever, the $6.36 billion Binance hack.
How are North Korean hackers using AI?
In a report published Thursday, Microsoft Threat Intelligence ranked eight of North Korea’s most active hacking groups on a four-step scale. The steps are emerging, expanding, accelerating and operationalized. “Operationalized” is the top step and means that AI is part of the group’s whole operation.
Microsoft ranks North Korean hacking groups by AI adoption. Source: Microsoft
Jade Sleet, Coral Sleet and Jasper Sleet are at the top step while Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet are in the accelerating step. Emerald Sleet is in the expanding step and currently no group is in the emerging step.
Microsoft linked the rankings to specific activity.
Jade Sleet ran campaigns through three fake companies in a single week.
Coral Sleet found a way to plant malware in private code storage.
Onyx Sleet created dozens of custom phishing messages within minutes.
Diamond Sleet used AI to build fake people and front companies to trick its targets.
One group reportedly made over 100 custom PDF lures aimed at South Korean users in August and September. Work like this once took days for each target.
The groups also used AI coding tools. Microsoft said operators used tools such as Cursor to write code, fix errors and build ways to avoid detection.
Onyx Sleet and Pearl Sleet used ARTEX, an open-source tool that tests systems for weaknesses. It can be linked to an AI model and told to scout targets on its own. A China-linked group, Storm-0940, reportedly used ARTEX against ConnectWise.
Microsoft’s analysts believe humans are still mainly in charge of North Korea’s hacking operations and simply use AI to speed up work the groups already did, such as scouting targets, making phishing content and keeping fake identities going.
Microsoft said crypto exchanges and financial firms are among the most common targets for North Korea’s cyber operations because the aim is mainly to raise money for the regime and gather intelligence.
Did AI play a part in the Binance hack?
So far, there is no evidence yet that the attackers involved in the Binance hack used AI, and Microsoft’s report does not link the Binance theft to any AI technique.
The Binance hack, which has been described as the largest crypto theft on record, happened on October 29. Blockchain research firm TRM Labs said an attacker moved about $6.36 billion out of Binance wallets across ten blockchains, most of it in about 20 minutes.
TRM blamed TraderTraitor, which it calls North Korea’s elite hacking unit, and said it is highly confident in this finding. Jonathan Levin, co-founder of Chainalysis, reached the same conclusion on X.
Cryptopolitan reported that Binance’s own account of the incident outlines how the attackers got in, but not what tools they used. The exchange first said a hacked engineer’s laptop looked like the entry point, but a later probe found more “points of breach.”
Binance has frozen about $3 billion of the stolen funds, paused withdrawals and promised to cover user losses.
The smartest crypto minds already read our newsletter. Want in? Join them.
North Korea's top hacking units have operationalized AI, Microsoft says
Microsoft says three North Korean hacking groups now use AI in their daily attacks, the highest level on its scale.
Microsoft (NASDAQ: MSFT) rates North Korea’s overall use of AI in hacking as high. The report came out as North Korea is blamed for the biggest crypto theft ever, the $6.36 billion Binance hack.
How are North Korean hackers using AI?
In a report published Thursday, Microsoft Threat Intelligence ranked eight of North Korea’s most active hacking groups on a four-step scale. The steps are emerging, expanding, accelerating and operationalized. “Operationalized” is the top step and means that AI is part of the group’s whole operation.
Microsoft ranks North Korean hacking groups by AI adoption. Source: Microsoft
Jade Sleet, Coral Sleet and Jasper Sleet are at the top step while Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet are in the accelerating step. Emerald Sleet is in the expanding step and currently no group is in the emerging step.
Microsoft linked the rankings to specific activity.
Jade Sleet ran campaigns through three fake companies in a single week.
Coral Sleet found a way to plant malware in private code storage.
Onyx Sleet created dozens of custom phishing messages within minutes.
Diamond Sleet used AI to build fake people and front companies to trick its targets.
One group reportedly made over 100 custom PDF lures aimed at South Korean users in August and September. Work like this once took days for each target.
The groups also used AI coding tools. Microsoft said operators used tools such as Cursor to write code, fix errors and build ways to avoid detection.
Onyx Sleet and Pearl Sleet used ARTEX, an open-source tool that tests systems for weaknesses. It can be linked to an AI model and told to scout targets on its own. A China-linked group, Storm-0940, reportedly used ARTEX against ConnectWise.
Microsoft’s analysts believe humans are still mainly in charge of North Korea’s hacking operations and simply use AI to speed up work the groups already did, such as scouting targets, making phishing content and keeping fake identities going.
Microsoft said crypto exchanges and financial firms are among the most common targets for North Korea’s cyber operations because the aim is mainly to raise money for the regime and gather intelligence.
Did AI play a part in the Binance hack?
So far, there is no evidence yet that the attackers involved in the Binance hack used AI, and Microsoft’s report does not link the Binance theft to any AI technique.
The Binance hack, which has been described as the largest crypto theft on record, happened on October 29. Blockchain research firm TRM Labs said an attacker moved about $6.36 billion out of Binance wallets across ten blockchains, most of it in about 20 minutes.
TRM blamed TraderTraitor, which it calls North Korea’s elite hacking unit, and said it is highly confident in this finding. Jonathan Levin, co-founder of Chainalysis, reached the same conclusion on X.
Cryptopolitan reported that Binance’s own account of the incident outlines how the attackers got in, but not what tools they used. The exchange first said a hacked engineer’s laptop looked like the entry point, but a later probe found more “points of breach.”
Binance has frozen about $3 billion of the stolen funds, paused withdrawals and promised to cover user losses.
The smartest crypto minds already read our newsletter. Want in? Join them.
1.2k
Verified
Zcash’s $125M grants fight: ZCG offers $46M back as Winklevoss pushes coinholder ruleThe five-person Zcash Community Grants (ZCG) committee has drawn criticism from people calling out the $46 million it wants to return of the roughly $125 million in its treasury as too small.
The 8% allocation of block rewards flowing into the treasury became worth fighting over after the recent 48-fold explosion in ZEC’s price over the last three years caused the funds to balloon in value.
Notably, the Zcash community has still not reached consensus on the best path to reroute the funds into. One of the more popular proposals to hand over control to coinholders has its detractors, who note that the people pushing the idea also stand to gain the most from concentrating power in the hands of the largest ZEC holders.
What solution did the ZCG propose?
The ZCG committee proposed moving 36,200 ZEC (worth about $46 million) from its roughly 91,500-ZEC treasury into the Network Sustainability Mechanism (NSM) in a Zcash community forum post, where it also conceded that the current 8% allocation it receives is more than it needs.
The Financial Privacy Foundation reported that ZCG spent only $1.53 million in Q1 2026.
The Network Sustainability Mechanism, as Cryptopolitan reported, is a protocol reserve that temporarily removes ZEC tokens from circulation and pays them to miners later over decades.
Another 62,000 ZEC ($78.5 million) in future funding was committed by the ZCG crew, with ongoing plans to continue to taper the remaining funds until the 2032 Zcash halving event. The current 8% allocation to the ZCG treasury runs until at least 2028.
Over time, the ZCG’s proposal to send ZEC to the NSM would amount to 98,000 ZEC (about $124 million) in future rewards for miners.
Why the Zcash community is fighting over $125 million
Under present rules, ZCG receives 8% of block rewards while the Coinholder-Controlled Fund receives 12%. The ZCG is controlled by the five-person committee, while token holders vote on the latter every quarter.
Block subsidy allocation for non-direct development funding. Source: Zcash
The allocation dispute centers on the nearly $125 million figure that Zcash co-founder Sean Bowe cited, quoting the ZCG’s public dashboard, which lists 91,452.98 ZEC and about $8.8 million in dollar-denominated assets against $2.4 million in outstanding grant commitments.
With all that money at stake, the Zcash community is facing competing proposals, pushing to send the ZCG’s funds in different directions.
Helius co-founder Mert Mumtaz dismissed ZCG’s refund plan as “nowhere near good enough” on X, calling the treasury “gargantuan” and arguing spending should answer to ZEC holders rather than a committee they had no hand in picking.
Gemini co-founder Tyler Winklevoss backed Mumtaz on Friday, saying that anyone who “can’t even take a little scrutiny” was “not qualified to run 110 million dollars with no accountability.” The response came after the Helius co-founder posted that a committee member had unfollowed him.
Direct holder control has skeptics inside the industry too. A token-weighted vote favors the largest wallets, and several of the people demanding the change are among the biggest stakeholders.
Dragonfly managing partner Haseeb Qureshi, who in September called for winding down the dev fund after it expires in 2028, argued against letting ZEC holders vote directly on allocations. Paradigm co-founder Matt Huang argued the same position. Both favored some form of elected council over a raw coin vote.
Maxime Desalle, an investor at Winklevoss Capital who has disclosed he is “actively involved with Cypherpunk, the world’s largest Zcash miner,” wants ZCG abolished outright.
The current fight follows Bowe’s narrower October 26 proposal to switch off the 8% stream and divert it to the NSM while leaving ZCG’s treasury untouched, which split Zcash’s own co-founders.
The smartest crypto minds already read our newsletter. Want in? Join them.
Zcash’s $125M grants fight: ZCG offers $46M back as Winklevoss pushes coinholder rule
The five-person Zcash Community Grants (ZCG) committee has drawn criticism from people calling out the $46 million it wants to return of the roughly $125 million in its treasury as too small.
The 8% allocation of block rewards flowing into the treasury became worth fighting over after the recent 48-fold explosion in ZEC’s price over the last three years caused the funds to balloon in value.
Notably, the Zcash community has still not reached consensus on the best path to reroute the funds into. One of the more popular proposals to hand over control to coinholders has its detractors, who note that the people pushing the idea also stand to gain the most from concentrating power in the hands of the largest ZEC holders.
What solution did the ZCG propose?
The ZCG committee proposed moving 36,200 ZEC (worth about $46 million) from its roughly 91,500-ZEC treasury into the Network Sustainability Mechanism (NSM) in a Zcash community forum post, where it also conceded that the current 8% allocation it receives is more than it needs.
The Financial Privacy Foundation reported that ZCG spent only $1.53 million in Q1 2026.
The Network Sustainability Mechanism, as Cryptopolitan reported, is a protocol reserve that temporarily removes ZEC tokens from circulation and pays them to miners later over decades.
Another 62,000 ZEC ($78.5 million) in future funding was committed by the ZCG crew, with ongoing plans to continue to taper the remaining funds until the 2032 Zcash halving event. The current 8% allocation to the ZCG treasury runs until at least 2028.
Over time, the ZCG’s proposal to send ZEC to the NSM would amount to 98,000 ZEC (about $124 million) in future rewards for miners.
Why the Zcash community is fighting over $125 million
Under present rules, ZCG receives 8% of block rewards while the Coinholder-Controlled Fund receives 12%. The ZCG is controlled by the five-person committee, while token holders vote on the latter every quarter.
Block subsidy allocation for non-direct development funding. Source: Zcash
The allocation dispute centers on the nearly $125 million figure that Zcash co-founder Sean Bowe cited, quoting the ZCG’s public dashboard, which lists 91,452.98 ZEC and about $8.8 million in dollar-denominated assets against $2.4 million in outstanding grant commitments.
With all that money at stake, the Zcash community is facing competing proposals, pushing to send the ZCG’s funds in different directions.
Helius co-founder Mert Mumtaz dismissed ZCG’s refund plan as “nowhere near good enough” on X, calling the treasury “gargantuan” and arguing spending should answer to ZEC holders rather than a committee they had no hand in picking.
Gemini co-founder Tyler Winklevoss backed Mumtaz on Friday, saying that anyone who “can’t even take a little scrutiny” was “not qualified to run 110 million dollars with no accountability.” The response came after the Helius co-founder posted that a committee member had unfollowed him.
Direct holder control has skeptics inside the industry too. A token-weighted vote favors the largest wallets, and several of the people demanding the change are among the biggest stakeholders.
Dragonfly managing partner Haseeb Qureshi, who in September called for winding down the dev fund after it expires in 2028, argued against letting ZEC holders vote directly on allocations. Paradigm co-founder Matt Huang argued the same position. Both favored some form of elected council over a raw coin vote.
Maxime Desalle, an investor at Winklevoss Capital who has disclosed he is “actively involved with Cypherpunk, the world’s largest Zcash miner,” wants ZCG abolished outright.
The current fight follows Bowe’s narrower October 26 proposal to switch off the 8% stream and divert it to the NSM while leaving ZCG’s treasury untouched, which split Zcash’s own co-founders.
The smartest crypto minds already read our newsletter. Want in? Join them.
1.4k
Russia’s feared FSB to gain access to private keys of crypto walletsThe Federal Security Service of the Russian Federation (FSB) will have full access to the private keys of crypto wallets hosted by licensed custodians.
The news comes despite opposition from Russian banks, which will be among the key participants in the country’s recently regulated market for digital assets.
FSB to have round-the-clock reach to the keys of Russians’ crypto wallets
FSB, the successor of the Soviet Union’s notorious KGB, will be given immediate access to the private keys of custodial wallets held by Russian citizens and firms.
The Central Bank of Russia (CBR), which oversees the newly legalized industry, made the announcement following discussions with representatives of the banking sector.
The Association of Banks of Russia (ABR) had proposed denying the three-letter agency the option to reach both keys and signing tools, Bits.media noted in a report on Thursday.
However, the monetary authority in Moscow did not support their initiative, the crypto news outlet revealed. The CBR also rejected a request to push back implementation until 2028.
Major players from the traditional financial market, including Russia’s big majority state-owned lenders and private commercial banks – Sber, VTB, T-Bank, and Alfa-Bank – took part in the talks.
Granting security services access to the crypto keys stems from the deployment of SORM, the government-implemented “system of technical means for ensuring operational-search activities.”
The latter, a framework comprising physical equipment and regulatory protocols, is installed on the networks of internet service providers across the country and enables instant data access for state agencies.
Using it, the FSB will be able to obtain information from cryptocurrency exchanges, brokers and “digital depositories,” or crypto custodial platforms as defined by the new “digital currency” law.
Starting March 1, 2027, all these entities will be required to provide the FSB with remote 24/7 access to the data they are storing, including text and voice messages, images, videos, and other client records.
Meanwhile, it also became clear that the Russian central bank intends to oblige crypto exchanges and custodians to reject any transfers of funds that lack details identifying their senders and recipients.
Moscow creates domestic crypto market under state control
Pressed by western fiat sanctions over its invasion of Ukraine, Russia has been increasingly relying on cryptocurrencies as a means to circumvent financial restrictions in foreign trade.
This year, the Putin administration took steps to legalize the growing market and place it under its strict control. A law “On digital currencies and digital rights” was adopted and signed this past summer.
The comprehensive legislation, which entered into force on September 1, allows both retail investors and companies to acquire and trade assets like Bitcoin (BTC), Ethereum (ETH) and Tether (USDT).
However, this can be done only through authorized intermediaries. The Bank of Russia has licensed two dozen coin trading and custodial platforms. Among them, Russia’s largest banks and stock exchanges.
This week, the CBR designated the National Association of Securities Market Participants, a body with close ties to the government, as a “self-regulatory” organization for Russian cryptocurrency firms.
Already registered crypto exchanges and digital depositories are required to become its members by January 27, 2027, and newcomers will have to secure membership within 90 days of their licensing.
To be legally owned and used domestically, Russian crypto holdings must be kept in digital wallets hosted by these state-approved service providers.
The use of self-hosted wallets is effectively prohibited, although owners are allowed to transfer their balances to custodial wallets or spend them in cross-border payments.
On Thursday, CBR Deputy Governor Vladimir Chistyukhin confirmed that the restrictions on personal wallets within the domestic market will not apply to international settlements, as reported by RBC.
During the negotiations with the monetary policy regulator, Russian bankers attempted to secure more relaxed rules for crypto exposure and the use of coins as collateral, but their proposals were rejected by the central bank.
If you're reading this, you’re already ahead. Stay there with our newsletter.
Russia’s feared FSB to gain access to private keys of crypto wallets
The Federal Security Service of the Russian Federation (FSB) will have full access to the private keys of crypto wallets hosted by licensed custodians.
The news comes despite opposition from Russian banks, which will be among the key participants in the country’s recently regulated market for digital assets.
FSB to have round-the-clock reach to the keys of Russians’ crypto wallets
FSB, the successor of the Soviet Union’s notorious KGB, will be given immediate access to the private keys of custodial wallets held by Russian citizens and firms.
The Central Bank of Russia (CBR), which oversees the newly legalized industry, made the announcement following discussions with representatives of the banking sector.
The Association of Banks of Russia (ABR) had proposed denying the three-letter agency the option to reach both keys and signing tools, Bits.media noted in a report on Thursday.
However, the monetary authority in Moscow did not support their initiative, the crypto news outlet revealed. The CBR also rejected a request to push back implementation until 2028.
Major players from the traditional financial market, including Russia’s big majority state-owned lenders and private commercial banks – Sber, VTB, T-Bank, and Alfa-Bank – took part in the talks.
Granting security services access to the crypto keys stems from the deployment of SORM, the government-implemented “system of technical means for ensuring operational-search activities.”
The latter, a framework comprising physical equipment and regulatory protocols, is installed on the networks of internet service providers across the country and enables instant data access for state agencies.
Using it, the FSB will be able to obtain information from cryptocurrency exchanges, brokers and “digital depositories,” or crypto custodial platforms as defined by the new “digital currency” law.
Starting March 1, 2027, all these entities will be required to provide the FSB with remote 24/7 access to the data they are storing, including text and voice messages, images, videos, and other client records.
Meanwhile, it also became clear that the Russian central bank intends to oblige crypto exchanges and custodians to reject any transfers of funds that lack details identifying their senders and recipients.
Moscow creates domestic crypto market under state control
Pressed by western fiat sanctions over its invasion of Ukraine, Russia has been increasingly relying on cryptocurrencies as a means to circumvent financial restrictions in foreign trade.
This year, the Putin administration took steps to legalize the growing market and place it under its strict control. A law “On digital currencies and digital rights” was adopted and signed this past summer.
The comprehensive legislation, which entered into force on September 1, allows both retail investors and companies to acquire and trade assets like Bitcoin (BTC), Ethereum (ETH) and Tether (USDT).
However, this can be done only through authorized intermediaries. The Bank of Russia has licensed two dozen coin trading and custodial platforms. Among them, Russia’s largest banks and stock exchanges.
This week, the CBR designated the National Association of Securities Market Participants, a body with close ties to the government, as a “self-regulatory” organization for Russian cryptocurrency firms.
Already registered crypto exchanges and digital depositories are required to become its members by January 27, 2027, and newcomers will have to secure membership within 90 days of their licensing.
To be legally owned and used domestically, Russian crypto holdings must be kept in digital wallets hosted by these state-approved service providers.
The use of self-hosted wallets is effectively prohibited, although owners are allowed to transfer their balances to custodial wallets or spend them in cross-border payments.
On Thursday, CBR Deputy Governor Vladimir Chistyukhin confirmed that the restrictions on personal wallets within the domestic market will not apply to international settlements, as reported by RBC.
During the negotiations with the monetary policy regulator, Russian bankers attempted to secure more relaxed rules for crypto exposure and the use of coins as collateral, but their proposals were rejected by the central bank.
If you're reading this, you’re already ahead. Stay there with our newsletter.
1
693
CZ tells Musk 'bad time to troll' amid $6.3 billion Binance hackElon Musk’s keyboard warrior persona has drawn a public response from Binance co-founder Changpeng Zhao (CZ), who called out unhelpful comments from the Tesla founder and X owner as crypto’s largest exchange deals with the industry’s largest security breach.
CZ’s response came within hours of Binance’s $6.3 billion hack, with the exchange’s former CEO reminding Musk of an earlier $500 million Binance cash injection into the 2022 deal to buy Twitter.
Elon, have a lot of respect for you, but bad time to troll. Please stop.
Our SPCX shares (from our $500m investment in your Twitter takeover) are worth more than a billion.
Would appreciate if you show a little support. Thanks!
— CZ 🔶 BNB (@cz_binance) October 30, 2026
That stake has since doubled and is now worth over $1 billion.
CZ responds to Musk’s public trolling
CZ asked Elon to “Please stop” and “show a little support” earlier today, after multiple posts from the billionaire appeared to be poking fun at Binance’s situation as the exchange deals with the fallout of its $6.3 billion hack.
Even in his response, CZ noted that he holds Musk in high regard, writing: “Elon, I have a lot of respect for you, but bad time to troll.”
CZ reminded Musk of past business dealings with Binance, when the exchange committed about $500 million to Musk’s 2022 bid to acquire Twitter for $44 billion.
The request was in response to a loaded post from Musk, who shared a grimacing emoji to a thread about the Binance hack.
CZ responded to another attempt by Musk to draw humor from an earlier post where Zhao was sharing cybersecurity advice, writing that the breach “is more complex than that, but all hacks generally have a compromised device (or algorithm) at some point.”
CZ’s mention of Binance’s shareholdings drew a reply from co-founder Yi He, who played along in public. “Reporting to the major shareholder: Our company’s revenue for the year is sufficient to cover the losses, so we do not yet need to sell the SpaceX shares you are bullish on,” she wrote, tagging CZ and Musk.
@cz_binance @elonmusk @HuaweiMate6 Reporting to the major shareholder: Our company’s revenue for the year is sufficient to cover the losses, so we do not yet need to sell the SpaceX shares you are bullish on.💁♀️
— Yi He (@heyibinance) October 30, 2026
CZ clarified that he was not floating a sale. He said he was only pointing to funds Musk “might know” about so that the Tesla and SpaceX chief would “be less worried.”
Both men have engaged in terse interactions publicly before. During a 2021 episode, Musk called out stalled Dogecoin withdrawals on Binance as “shady.” CZ fired back by linking to a Tesla vehicle recall.
In December 2024, Musk replied with a short “Thanks!” when CZ brought up the $500 million contribution to his 2022 Twitter acquisition, as Cryptopolitan reported at the time.
What Binance says went wrong
The exchange estimates the security incident, which began Thursday, cost around $6.3 billion, making it the largest hack in crypto history. Binance first blamed a compromised laptop belonging to a DevOps engineer, which it said may have let an attacker reach a service container and push through unauthorized withdrawals.
That account has since widened. In its latest update, Binance said its investigation “uncovered additional points of breach.”
CEO Richard Teng wrote on Friday that the attacker “did not simply use one engineer’s permissions, and this was not a single ‘one-click’ action,” describing a more involved attack process. The firm said it has found no evidence of a wallet private key leak and has not pinned responsibility on any individual.
Binance has frozen about $3 billion of the stolen funds on-chain. It says it will absorb every loss through its SAFU emergency fund and company reserves. Deposits have reopened, withdrawals remain paused, and the exchange says it is on track to turn them back on in 45 hours.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
CZ tells Musk 'bad time to troll' amid $6.3 billion Binance hack
Elon Musk’s keyboard warrior persona has drawn a public response from Binance co-founder Changpeng Zhao (CZ), who called out unhelpful comments from the Tesla founder and X owner as crypto’s largest exchange deals with the industry’s largest security breach.
CZ’s response came within hours of Binance’s $6.3 billion hack, with the exchange’s former CEO reminding Musk of an earlier $500 million Binance cash injection into the 2022 deal to buy Twitter.
Elon, have a lot of respect for you, but bad time to troll. Please stop.
Our SPCX shares (from our $500m investment in your Twitter takeover) are worth more than a billion.
Would appreciate if you show a little support. Thanks!
— CZ 🔶 BNB (@cz_binance) October 30, 2026
That stake has since doubled and is now worth over $1 billion.
CZ responds to Musk’s public trolling
CZ asked Elon to “Please stop” and “show a little support” earlier today, after multiple posts from the billionaire appeared to be poking fun at Binance’s situation as the exchange deals with the fallout of its $6.3 billion hack.
Even in his response, CZ noted that he holds Musk in high regard, writing: “Elon, I have a lot of respect for you, but bad time to troll.”
CZ reminded Musk of past business dealings with Binance, when the exchange committed about $500 million to Musk’s 2022 bid to acquire Twitter for $44 billion.
The request was in response to a loaded post from Musk, who shared a grimacing emoji to a thread about the Binance hack.
CZ responded to another attempt by Musk to draw humor from an earlier post where Zhao was sharing cybersecurity advice, writing that the breach “is more complex than that, but all hacks generally have a compromised device (or algorithm) at some point.”
CZ’s mention of Binance’s shareholdings drew a reply from co-founder Yi He, who played along in public. “Reporting to the major shareholder: Our company’s revenue for the year is sufficient to cover the losses, so we do not yet need to sell the SpaceX shares you are bullish on,” she wrote, tagging CZ and Musk.
@cz_binance @elonmusk @HuaweiMate6 Reporting to the major shareholder: Our company’s revenue for the year is sufficient to cover the losses, so we do not yet need to sell the SpaceX shares you are bullish on.💁♀️
— Yi He (@heyibinance) October 30, 2026
CZ clarified that he was not floating a sale. He said he was only pointing to funds Musk “might know” about so that the Tesla and SpaceX chief would “be less worried.”
Both men have engaged in terse interactions publicly before. During a 2021 episode, Musk called out stalled Dogecoin withdrawals on Binance as “shady.” CZ fired back by linking to a Tesla vehicle recall.
In December 2024, Musk replied with a short “Thanks!” when CZ brought up the $500 million contribution to his 2022 Twitter acquisition, as Cryptopolitan reported at the time.
What Binance says went wrong
The exchange estimates the security incident, which began Thursday, cost around $6.3 billion, making it the largest hack in crypto history. Binance first blamed a compromised laptop belonging to a DevOps engineer, which it said may have let an attacker reach a service container and push through unauthorized withdrawals.
That account has since widened. In its latest update, Binance said its investigation “uncovered additional points of breach.”
CEO Richard Teng wrote on Friday that the attacker “did not simply use one engineer’s permissions, and this was not a single ‘one-click’ action,” describing a more involved attack process. The firm said it has found no evidence of a wallet private key leak and has not pinned responsibility on any individual.
Binance has frozen about $3 billion of the stolen funds on-chain. It says it will absorb every loss through its SAFU emergency fund and company reserves. Deposits have reopened, withdrawals remain paused, and the exchange says it is on track to turn them back on in 45 hours.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
1
970
Jameson Lopp warns of Google phishing sent from Google's own serversCasa’s Jameson Lopp warned on Thursday about a new phishing scam that sends fake emails through Google’s own systems.
Crypto holders face the biggest risk from this scam due to the use of fake login pages to steal passwords and other sensitive data.
How can a scam email come from Google itself?
Casa’s Jameson Lopp has warned on X that there’s a new version of an old scam currently running. He posted a screenshot of the scam email, which is sent through Google’s actual servers in order to make it look real.
New flavor of Google phishing that abuses Google's own infrastructure to send you this email. If you click the https://t.co/H9sDdmX0PF link you end up at a phishing login page. pic.twitter.com/dfkvfibo33
— Jameson Lopp (@lopp) October 29, 2026
The post explains that when a user clicks the link in the email, they will be sent to a fake login page.
In May, Lopp shared another scam that used Google’s account recovery form. The attacker wrote a very long message in the form, keeping a notice that looked real at the top and the scam link far below it, after a lot of empty space. The alert in this incident came through Google’s real account systems.
Check Point (NASDAQ: CHKP) found a campaign that misused the “Send Email” feature in Google Cloud’s Application Integration tool. Over a period of two weeks in December 2025, attackers sent 9,394 emails to about 3,200 organizations and the emails came from a real Google address, noreply-application-integration@google.com, so they passed DMARC and SPF checks.
People who clicked the links in the emails were first sent through several trusted Google web addresses. Next, they saw a fake CAPTCHA page that stopped automatic security scanners. After that, they landed on a fake Microsoft (NASDAQ: MSFT) login page that was not hosted by Microsoft.
Google (NASDAQ: GOOGL) told the researchers it had blocked the campaigns. It said the problem came from the misuse of an automation tool, not from a break-in to its systems.
Similar scams have reportedly been carried out through Google Meet, DoubleClick, Google Analytics and other services.
Why are crypto holders targeted so often?
Crypto exchange users and wallet holders are especially at risk because fake login pages can be used to steal passwords, session data or two-factor codes.
Cryptopolitan reported just this week that scammers used leaked API keys from Cloudflare (NYSE: NET) to send emails from Foundation’s own domains. Some recipients said the scam emails they received had legitimate details like their names, addresses and past Passport purchases.
Foundation has since revoked the keys and said the funds on its devices are safe.
Notably, Binance said it blocked 22.9 million scam and phishing attempts in the first quarter of 2026, 54% more than the quarter before. It also said it protected about $1.98 billion in user funds.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Jameson Lopp warns of Google phishing sent from Google's own servers
Casa’s Jameson Lopp warned on Thursday about a new phishing scam that sends fake emails through Google’s own systems.
Crypto holders face the biggest risk from this scam due to the use of fake login pages to steal passwords and other sensitive data.
How can a scam email come from Google itself?
Casa’s Jameson Lopp has warned on X that there’s a new version of an old scam currently running. He posted a screenshot of the scam email, which is sent through Google’s actual servers in order to make it look real.
New flavor of Google phishing that abuses Google's own infrastructure to send you this email. If you click the https://t.co/H9sDdmX0PF link you end up at a phishing login page. pic.twitter.com/dfkvfibo33
— Jameson Lopp (@lopp) October 29, 2026
The post explains that when a user clicks the link in the email, they will be sent to a fake login page.
In May, Lopp shared another scam that used Google’s account recovery form. The attacker wrote a very long message in the form, keeping a notice that looked real at the top and the scam link far below it, after a lot of empty space. The alert in this incident came through Google’s real account systems.
Check Point (NASDAQ: CHKP) found a campaign that misused the “Send Email” feature in Google Cloud’s Application Integration tool. Over a period of two weeks in December 2025, attackers sent 9,394 emails to about 3,200 organizations and the emails came from a real Google address, noreply-application-integration@google.com, so they passed DMARC and SPF checks.
People who clicked the links in the emails were first sent through several trusted Google web addresses. Next, they saw a fake CAPTCHA page that stopped automatic security scanners. After that, they landed on a fake Microsoft (NASDAQ: MSFT) login page that was not hosted by Microsoft.
Google (NASDAQ: GOOGL) told the researchers it had blocked the campaigns. It said the problem came from the misuse of an automation tool, not from a break-in to its systems.
Similar scams have reportedly been carried out through Google Meet, DoubleClick, Google Analytics and other services.
Why are crypto holders targeted so often?
Crypto exchange users and wallet holders are especially at risk because fake login pages can be used to steal passwords, session data or two-factor codes.
Cryptopolitan reported just this week that scammers used leaked API keys from Cloudflare (NYSE: NET) to send emails from Foundation’s own domains. Some recipients said the scam emails they received had legitimate details like their names, addresses and past Passport purchases.
Foundation has since revoked the keys and said the funds on its devices are safe.
Notably, Binance said it blocked 22.9 million scam and phishing attempts in the first quarter of 2026, 54% more than the quarter before. It also said it protected about $1.98 billion in user funds.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
1
1.7k
Article
DEX swaps and arbitrage drive Ethereum fees above $56M on the day after Binance hackEthereum fees spiked to the highest levels since April, showing a sudden burst of activity in the ecosystem in the aftermath of the Binance hack. Decentralized trading and MEV bot fees were the main drivers of the performance spike on the chain.
Ethereum block builders had a field day after the $6.3B Binance hack, the biggest theft event in the history of crypto. The event showed decentralized platforms were extremely resilient and even benefited from the increased activity.
The initial movement of funds from the Binance wallet was one source of fees, but the hack also opened new trading opportunities, decentralized liquidations, and other on-chain transfers.
Most of the block builder fees came from activities in stablecoins, as well as Ethereum’s leading apps and protocols. The hacker also had to swap some of the stolen assets for ETH, demanding the services of block builders to forge priority transactions.
MEV bots moved in, pushing those transactions with high fees to block builders. Block builders then pay validators a share of the fee, keeping the rest as revenue, explained X analyst @0xnairoff.
Ethereum breaks above $56M in daily fees
The recent inflow of activity led to over $44.25M in daily fees on the day of the hack, and $56.4M in the next 24 hours. As of October 30, activity was still elevated, with over $10M in fees as of this report.
Activity from MEV bots, block builders, and validators led to the highest daily fees on Ethereum since April. | Source: DeFi Llama
The biggest effect of the recent fees affected Titan Builder, the leading block builder in the past months. In the past 24 hours, the block builder absorbed $24.65M in fees, meaning validators would also receive a large portion of the additional income.
The Ethereum chain alone had over $10M in daily fees, while Uniswap turned into the main trading venue, also logging over $10M in fees, based on DeFi Llama data.
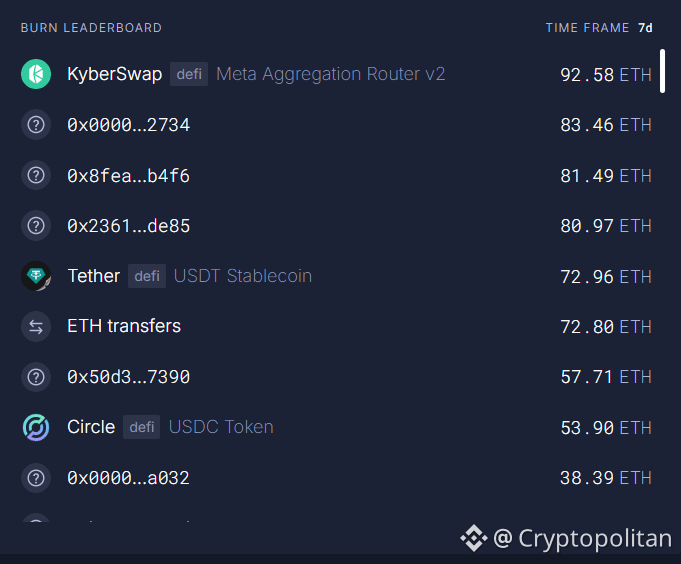
As of October 30, the mix of smart contracts and apps on Ethereum also shifted. KyberSwap emerged as a leading aggregation router, burning 92.58 ETH in fees. Several unknown smart contracts also displaced USDT and USDC as the leading gas burners. ETH transfers alone burned 72.8 ETH in the past day.
Ethereum activity showed a prevalence of DEX trading, raising demand for routers, MEV bots, and general ETH and stablecoin transfers. | Source: Ultrasound Money
At the same time, ETH gas fees are still under $0.01, as only specialized traders and whales rushed to perform transactions and swaps.
Additionally, the increased activity led to a one-month peak in blob fees, after weeks of almost zero demand for blob space. The usage of L2 chains, especially Arbitrum, was linked to some of the stolen assets and attempts to bridge them to Ethereum.
Binance hack led to ETH arbitrage
Following the Binance hack, ETH was used as an exit asset, similar to other large-scale exploits. As a result, ETH prices showed significant disparity. On decentralized markets like Uniswap, ETH traded as high as $2,700. Other data points to anomalous on-chain pricing as high as $3,300, though not offered at all on centralized markets.
On other markets, the price settled at around $2,223.25, causing additional pressure on derivative markets. The ETH decentralized price was mostly driven by attempts to swap tokens. At the same time, the ETH crash is causing liquidation risk for whales that positioned themselves while ETH was still more bullish.
ETH is down by 17.2% in October to date following its recent crash, and on track to close the worst October since its inception in 2016.
The ETH crash brought down the fear and greed index to 28 points, solidly in fear territory. ETH is closely watched for preserving $2,200 as a support level. Losing that level is seen as a signal for sinking below $2,000.
If you're reading this, you’re already ahead. Stay there with our newsletter.
DEX swaps and arbitrage drive Ethereum fees above $56M on the day after Binance hack
Ethereum fees spiked to the highest levels since April, showing a sudden burst of activity in the ecosystem in the aftermath of the Binance hack. Decentralized trading and MEV bot fees were the main drivers of the performance spike on the chain.
Ethereum block builders had a field day after the $6.3B Binance hack, the biggest theft event in the history of crypto. The event showed decentralized platforms were extremely resilient and even benefited from the increased activity.
The initial movement of funds from the Binance wallet was one source of fees, but the hack also opened new trading opportunities, decentralized liquidations, and other on-chain transfers.
Most of the block builder fees came from activities in stablecoins, as well as Ethereum’s leading apps and protocols. The hacker also had to swap some of the stolen assets for ETH, demanding the services of block builders to forge priority transactions.
MEV bots moved in, pushing those transactions with high fees to block builders. Block builders then pay validators a share of the fee, keeping the rest as revenue, explained X analyst @0xnairoff.
Ethereum breaks above $56M in daily fees
The recent inflow of activity led to over $44.25M in daily fees on the day of the hack, and $56.4M in the next 24 hours. As of October 30, activity was still elevated, with over $10M in fees as of this report.
Activity from MEV bots, block builders, and validators led to the highest daily fees on Ethereum since April. | Source: DeFi Llama
The biggest effect of the recent fees affected Titan Builder, the leading block builder in the past months. In the past 24 hours, the block builder absorbed $24.65M in fees, meaning validators would also receive a large portion of the additional income.
The Ethereum chain alone had over $10M in daily fees, while Uniswap turned into the main trading venue, also logging over $10M in fees, based on DeFi Llama data.
As of October 30, the mix of smart contracts and apps on Ethereum also shifted. KyberSwap emerged as a leading aggregation router, burning 92.58 ETH in fees. Several unknown smart contracts also displaced USDT and USDC as the leading gas burners. ETH transfers alone burned 72.8 ETH in the past day.
Ethereum activity showed a prevalence of DEX trading, raising demand for routers, MEV bots, and general ETH and stablecoin transfers. | Source: Ultrasound Money
At the same time, ETH gas fees are still under $0.01, as only specialized traders and whales rushed to perform transactions and swaps.
Additionally, the increased activity led to a one-month peak in blob fees, after weeks of almost zero demand for blob space. The usage of L2 chains, especially Arbitrum, was linked to some of the stolen assets and attempts to bridge them to Ethereum.
Binance hack led to ETH arbitrage
Following the Binance hack, ETH was used as an exit asset, similar to other large-scale exploits. As a result, ETH prices showed significant disparity. On decentralized markets like Uniswap, ETH traded as high as $2,700. Other data points to anomalous on-chain pricing as high as $3,300, though not offered at all on centralized markets.
On other markets, the price settled at around $2,223.25, causing additional pressure on derivative markets. The ETH decentralized price was mostly driven by attempts to swap tokens. At the same time, the ETH crash is causing liquidation risk for whales that positioned themselves while ETH was still more bullish.
ETH is down by 17.2% in October to date following its recent crash, and on track to close the worst October since its inception in 2016.
The ETH crash brought down the fear and greed index to 28 points, solidly in fear territory. ETH is closely watched for preserving $2,200 as a support level. Losing that level is seen as a signal for sinking below $2,000.
If you're reading this, you’re already ahead. Stay there with our newsletter.
1.6k
Binance hack splits crypto into funds that freeze and funds that don'tThe attackers in the $6.3 billion Binance theft have started to split their haul along the lines of assets that can be frozen or potentially clawed back and assets beyond freeze controls.
On one hand, stablecoin issuers are already pulling blacklist and freeze levers, while the hackers are racing to cross over to ETH, BTC and other tokens with no issuers or off switches.
The scramble to wall off tokens before they cross into unrecoverable territory follows what has been described as the biggest theft in crypto history, which, ironically, hit the world’s largest crypto exchange.
Binance’s initial report of the incident has blamed the exploit on a compromised DevOps engineer’s laptop.
What has been frozen from the Binance hack?
The Binance attackers, whom TRM Labs and Chainalysis have, with high confidence, fingered as North Korea’s TraderTraitor unit, have lost nearly $3 billion of the tokens they moved from the exchange.
The issuers of the largest stablecoins by market cap, Tether and Circle, have both blacklisted about 1.77 billion USDT and 825 million USDC, respectively, according to TRM Labs.
Of the stolen 88.5 million RLUSD stablecoin, Ripple has frozen 40.5 million, while Trump-linked World Liberty Financial has locked 27.8 million of its USD1 token.
Arbitrum’s Security Council also pulled a lever that helped it stop $30.5 million.
However, the North Korea-linked attackers still have almost $3 billion that no entity can touch, per Arkham and Lookonchain tracking: roughly $1.09 billion in ETH, $1.41 billion in BTC and 682.9 million TRX.
Binance attacker now holds about $2.86 billion in assets that cannot be frozen or recovered.
The attacker raised $158.25 million from selling altcoins like AAVE, ENA, LINK, PEPE and UNI. All of that money has since been converted into Ethereum, a non-freezable asset.
Who can intervene and who can’t?
DEX aggregator 1inch and the Reserve protocol present a side-by-side comparison of the intervention bridge that the hackers are looking to cross.
1inch said exploit-linked addresses have already been blocked from accessing its dApp, wallet and API. It also said it has reached out to Binance to offer help and is coordinating with ZeroShadow, SEAL 911 and TRM Labs.
Reserve, on the other hand, could not do anything to stop the attackers when they swept up about 3.4 billion of its RSR token. The team wrote on X that “no one, including us, can freeze” the tokens because RSR is immutable and has no admin keys.
Arbitrum’s Security Council temporarily modified the network’s inbox contract on Ethereum, added a function to reproduce a cross-chain transaction while impersonating the exploit address, and moved 8,425 ETH and 74,559,805 ARB into a holding wallet ending in 0DA0, according to the Arbitrum governance forum.
The council then restored the contract. The funds can only move after an ArbitrumDAO vote.
The council used the same emergency powers in April, when it froze about 30,766 ETH, worth roughly $71 million, tied to the KelpDAO exploit.
What the Bitget hack already showed
Frozen is not recovered, and the industry has fresh proof of how little freezing can catch once an attacker converts. In the September Bitget breach, Cryptopolitan reported that Circle and Tether locked just $318,000 out of $387.5 million stolen, because the thief had already swapped the rest into Ether.
Bitquery data cited by Cryptopolitan shows wallets frozen within a week keep 59% of their USDT after a week but only 12% after six months.
Binance has suspended deposits and withdrawals, pledged to cover user losses from its SAFU reserve and company funds, and expects withdrawals to resume within 48 hours.
Co-CEO Richard Teng wrote on X, “Your money is safe and we’re covering every loss.” The exchange has not said how much of the frozen $3 billion it can actually reclaim, or what will happen to the remaining $3.3 billion.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Binance hack splits crypto into funds that freeze and funds that don't
The attackers in the $6.3 billion Binance theft have started to split their haul along the lines of assets that can be frozen or potentially clawed back and assets beyond freeze controls.
On one hand, stablecoin issuers are already pulling blacklist and freeze levers, while the hackers are racing to cross over to ETH, BTC and other tokens with no issuers or off switches.
The scramble to wall off tokens before they cross into unrecoverable territory follows what has been described as the biggest theft in crypto history, which, ironically, hit the world’s largest crypto exchange.
Binance’s initial report of the incident has blamed the exploit on a compromised DevOps engineer’s laptop.
What has been frozen from the Binance hack?
The Binance attackers, whom TRM Labs and Chainalysis have, with high confidence, fingered as North Korea’s TraderTraitor unit, have lost nearly $3 billion of the tokens they moved from the exchange.
The issuers of the largest stablecoins by market cap, Tether and Circle, have both blacklisted about 1.77 billion USDT and 825 million USDC, respectively, according to TRM Labs.
Of the stolen 88.5 million RLUSD stablecoin, Ripple has frozen 40.5 million, while Trump-linked World Liberty Financial has locked 27.8 million of its USD1 token.
Arbitrum’s Security Council also pulled a lever that helped it stop $30.5 million.
However, the North Korea-linked attackers still have almost $3 billion that no entity can touch, per Arkham and Lookonchain tracking: roughly $1.09 billion in ETH, $1.41 billion in BTC and 682.9 million TRX.
Binance attacker now holds about $2.86 billion in assets that cannot be frozen or recovered.
The attacker raised $158.25 million from selling altcoins like AAVE, ENA, LINK, PEPE and UNI. All of that money has since been converted into Ethereum, a non-freezable asset.
Who can intervene and who can’t?
DEX aggregator 1inch and the Reserve protocol present a side-by-side comparison of the intervention bridge that the hackers are looking to cross.
1inch said exploit-linked addresses have already been blocked from accessing its dApp, wallet and API. It also said it has reached out to Binance to offer help and is coordinating with ZeroShadow, SEAL 911 and TRM Labs.
Reserve, on the other hand, could not do anything to stop the attackers when they swept up about 3.4 billion of its RSR token. The team wrote on X that “no one, including us, can freeze” the tokens because RSR is immutable and has no admin keys.
Arbitrum’s Security Council temporarily modified the network’s inbox contract on Ethereum, added a function to reproduce a cross-chain transaction while impersonating the exploit address, and moved 8,425 ETH and 74,559,805 ARB into a holding wallet ending in 0DA0, according to the Arbitrum governance forum.
The council then restored the contract. The funds can only move after an ArbitrumDAO vote.
The council used the same emergency powers in April, when it froze about 30,766 ETH, worth roughly $71 million, tied to the KelpDAO exploit.
What the Bitget hack already showed
Frozen is not recovered, and the industry has fresh proof of how little freezing can catch once an attacker converts. In the September Bitget breach, Cryptopolitan reported that Circle and Tether locked just $318,000 out of $387.5 million stolen, because the thief had already swapped the rest into Ether.
Bitquery data cited by Cryptopolitan shows wallets frozen within a week keep 59% of their USDT after a week but only 12% after six months.
Binance has suspended deposits and withdrawals, pledged to cover user losses from its SAFU reserve and company funds, and expects withdrawals to resume within 48 hours.
Co-CEO Richard Teng wrote on X, “Your money is safe and we’re covering every loss.” The exchange has not said how much of the frozen $3 billion it can actually reclaim, or what will happen to the remaining $3.3 billion.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
2
1
269
Verified
Article
Circle starts winding down CCTP V1 ahead of the December 1 USDC bridge pauseCircle will start throttling the legacy Cross-Chain Transfer Protocol (CCTP V1) on Saturday, October 31.
The wind-down will end Dec. 1, 2026, at which point V1 contracts stop.
Apps still using USDC in the old system have about a month to change over to CCTP V2. Otherwise, their crosschain transfers will end.
Burn limits drop from October 31 until a December 1 pause
CCTP links USDC across blockchains. On one chain, it burns the stablecoin and mints that much on another chain. To clear the mint, Circle needs to sign off on it, which is called an attestation.
There is a burn limit that tells the process how much USDC it can take in at any given time. In a blog post on August 27, Circle said that these limits would start to be lowered on October 31. Performance would get worse over the course of one month in order to get rid of all legacy use.
Circle’s CCTP V1 wind-down schedule, from its August 27, 2026 migration post.
The V1 contracts will stop on December 1. Integrations still linked to them then can’t move USDC between chains.
Circle first warned about the move away from V1 on November 14, 2025.
Since Noble won’t get CCTP V2, it’s on a different schedule. New USDC minting there was set to close on October 13.
The Noble USDC contract and all its CCTP routes will stop working on January 12, 2027. Manual redemptions open a day later.
Circle now lists Sui on V2, and all V1 chains except Noble already use V2.
CCTP V2 adds three parameters to depositForBurn
Plain CCTP, which used to be called CCTP V2, has its own contracts and APIs and can’t work with V1.
TokenMessengerV2 and MessageTransmitterV2 are two of the new interfaces that developers will need to change the code to point to. There are three extra parameters in V2’s depositForBurn function: a destination caller, a maximum fee, and a minimum finality threshold.
Instead of getting message bytes from an onchain transaction and hashing them, integrations ask for them at a V2 messages API with the transaction hash.
It is no longer possible in V2 to use replaceDepositForBurn or some other old functions. Developers no longer have to worry about contract addresses and attestation polling when they use Circle’s Arc App Kits.
V2 adds Standard and Fast Transfer modes and supports 31 blockchains. When USDC comes, programmable hooks let an app start an automatic action on the destination chain.
How much Fast Transfer costs is based on the source chain. There was no fee for transfers on V1.
Circle says that there will be more minter allowances than pending attestations so that in-flight transfers can be settled before the pause on December 1.
CCTP has come under legal fire before. A Drift Protocol investor filed suit against Circle in a Massachusetts district court in April in connection with the $280 million Drift exploit, Cryptopolitan reported.
The class action claims that Circle didn’t freeze around $230 million of USDC that North Korean hackers channeled through CCTP. CEO Jeremy Allaire said Circle freezes wallets at the direction of law enforcement or courts and should not be a digital vigilante.
Circle launched its Arc layer-1 blockchain on mainnet in September with validators including BlackRock, Visa, Mastercard and DTCC.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Circle starts winding down CCTP V1 ahead of the December 1 USDC bridge pause
Circle will start throttling the legacy Cross-Chain Transfer Protocol (CCTP V1) on Saturday, October 31.
The wind-down will end Dec. 1, 2026, at which point V1 contracts stop.
Apps still using USDC in the old system have about a month to change over to CCTP V2. Otherwise, their crosschain transfers will end.
Burn limits drop from October 31 until a December 1 pause
CCTP links USDC across blockchains. On one chain, it burns the stablecoin and mints that much on another chain. To clear the mint, Circle needs to sign off on it, which is called an attestation.
There is a burn limit that tells the process how much USDC it can take in at any given time. In a blog post on August 27, Circle said that these limits would start to be lowered on October 31. Performance would get worse over the course of one month in order to get rid of all legacy use.
Circle’s CCTP V1 wind-down schedule, from its August 27, 2026 migration post.
The V1 contracts will stop on December 1. Integrations still linked to them then can’t move USDC between chains.
Circle first warned about the move away from V1 on November 14, 2025.
Since Noble won’t get CCTP V2, it’s on a different schedule. New USDC minting there was set to close on October 13.
The Noble USDC contract and all its CCTP routes will stop working on January 12, 2027. Manual redemptions open a day later.
Circle now lists Sui on V2, and all V1 chains except Noble already use V2.
CCTP V2 adds three parameters to depositForBurn
Plain CCTP, which used to be called CCTP V2, has its own contracts and APIs and can’t work with V1.
TokenMessengerV2 and MessageTransmitterV2 are two of the new interfaces that developers will need to change the code to point to. There are three extra parameters in V2’s depositForBurn function: a destination caller, a maximum fee, and a minimum finality threshold.
Instead of getting message bytes from an onchain transaction and hashing them, integrations ask for them at a V2 messages API with the transaction hash.
It is no longer possible in V2 to use replaceDepositForBurn or some other old functions. Developers no longer have to worry about contract addresses and attestation polling when they use Circle’s Arc App Kits.
V2 adds Standard and Fast Transfer modes and supports 31 blockchains. When USDC comes, programmable hooks let an app start an automatic action on the destination chain.
How much Fast Transfer costs is based on the source chain. There was no fee for transfers on V1.
Circle says that there will be more minter allowances than pending attestations so that in-flight transfers can be settled before the pause on December 1.
CCTP has come under legal fire before. A Drift Protocol investor filed suit against Circle in a Massachusetts district court in April in connection with the $280 million Drift exploit, Cryptopolitan reported.
The class action claims that Circle didn’t freeze around $230 million of USDC that North Korean hackers channeled through CCTP. CEO Jeremy Allaire said Circle freezes wallets at the direction of law enforcement or courts and should not be a digital vigilante.
Circle launched its Arc layer-1 blockchain on mainnet in September with validators including BlackRock, Visa, Mastercard and DTCC.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
1
1.6k
Verified
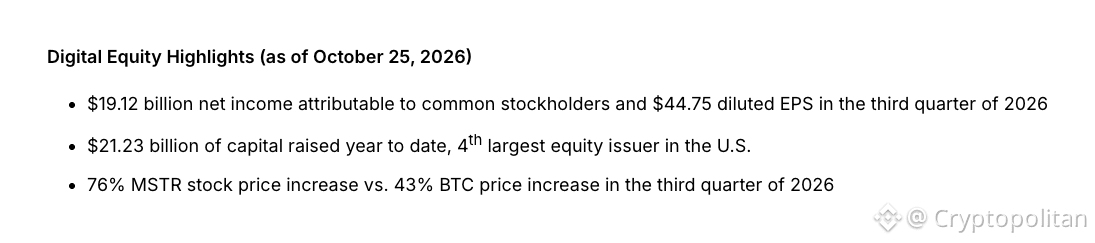
Article
Strategy books record $20.9B Q3 operating income as finance chief Kang leavesStrategy reported an operating income of $20.91 billion, a record, in the third quarter and announced that Chief Financial Officer Andrew Kang will step down on November 5.
Almost all of the quarter’s profit was a paper gain on its Bitcoin.
Reza Virasteh takes over finance on January 1, 2027
Kang is leaving as CFO after four and a half years and will be an advisor until December 31. Reza Virasteh, the company’s executive vice president of operations, will become CFO on Jan. 1, 2027.
In the meantime, the finance team is run by CEO Phong Le. Le will lead the finances for the bitcoin strategy starting in January and will share principal financial officer duties with Virasteh, according to the Oct. 29 earnings release.
“Q3 operating income of $21 billion was the largest ever in Strategy’s history,” Kang said in the release. He called serving as CFO “an honor and privilege.”
Operating income a year earlier was $3.89 billion. Digital assets alone added $20.91 billion in gains this quarter.
Net income was $19.53 billion, or $44.75 a diluted share, compared with $2.79 billion and $8.42 in the third quarter of 2025. Preferred dividends of $419.6 million diminished the common shareholders’ share to $19.12 billion.
Software revenue declined to $125.4 million, down 3% from $128.7 million a year earlier. Gross margin was 71%.
Bitcoin-led losses hit $12.54 billion in the first quarter and $8.22 billion in the next, meaning the first nine months were $1.23 billion in the red, or $6.27 a diluted share.
Even Strategy’s own yardsticks look backwards. Year to date, it posted a BTC Yield of -3.7%, a BTC Gain of -24,947 bitcoin and a BTC $ Gain of -$2.03 billion, so each share now carries less bitcoin than in January.
Holdings were at 848,517 bitcoin on October 25, a leap of 26% this year. Cost basis was $64.02 billion, about $75,446 per coin.
The market value on October 23 was $68.90 billion and the Bitcoin price was $81,200.
The company said Bitcoin was up 43% and MSTR was up 76% in the quarter. Sales of stock under its at-the-market program raised $5.41 billion net in the quarter and $21.23 billion raised in 2026 makes Strategy the fourth-largest U.S. equity issuer this year.
Strategy’s Digital Equity Highlights as of October 25, 2026, from its third-quarter earnings release.
“We’re at the beginning of the next bitcoin bull market,” Executive Chairman Michael Saylor said in the release. He cites banks getting on board with bitcoin and a price 21% above its 200-week moving average.
MSTR was off about 3.5% in after-hours trading on Oct. 29. Bitcoin dropped below $77,000 on the same day.
Shareholders back daily preferred dividends with 99.3% of votes
Strategy has sold about $431.8 million of bitcoin this year to pay for some of its preferred dividends and STRC buybacks. Cryptopolitan reported it sold 1,638 bitcoin in the week to August 2 for about $104.7 million.
Strategy’s common stockholders voted on October 28 to permit STRC, STRF, STRK and STRD dividends to accumulate on a calendar day basis. The measure got 99.3% of the votes cast, according to Strategy’s October 28 filing.
STRC changes November 1. STRF, STRK and STRD follow on January 1, 2027.
This year STRC buybacks were approximately $2.04 billion at an average price of $97.39 per share, ~2.6% below its stated amount of $100. Strategy maintains STRC dividend rate at 12.00%.
USD Assets are at $5.07 billion, which the company says would cover about 3.4 years of preferred dividends and interest. The USD Reserve alone stands at $4.83 billion, up from $3.225 billion on July 20.
If you're reading this, you’re already ahead. Stay there with our newsletter.
Strategy books record $20.9B Q3 operating income as finance chief Kang leaves
Strategy reported an operating income of $20.91 billion, a record, in the third quarter and announced that Chief Financial Officer Andrew Kang will step down on November 5.
Almost all of the quarter’s profit was a paper gain on its Bitcoin.
Reza Virasteh takes over finance on January 1, 2027
Kang is leaving as CFO after four and a half years and will be an advisor until December 31. Reza Virasteh, the company’s executive vice president of operations, will become CFO on Jan. 1, 2027.
In the meantime, the finance team is run by CEO Phong Le. Le will lead the finances for the bitcoin strategy starting in January and will share principal financial officer duties with Virasteh, according to the Oct. 29 earnings release.
“Q3 operating income of $21 billion was the largest ever in Strategy’s history,” Kang said in the release. He called serving as CFO “an honor and privilege.”
Operating income a year earlier was $3.89 billion. Digital assets alone added $20.91 billion in gains this quarter.
Net income was $19.53 billion, or $44.75 a diluted share, compared with $2.79 billion and $8.42 in the third quarter of 2025. Preferred dividends of $419.6 million diminished the common shareholders’ share to $19.12 billion.
Software revenue declined to $125.4 million, down 3% from $128.7 million a year earlier. Gross margin was 71%.
Bitcoin-led losses hit $12.54 billion in the first quarter and $8.22 billion in the next, meaning the first nine months were $1.23 billion in the red, or $6.27 a diluted share.
Even Strategy’s own yardsticks look backwards. Year to date, it posted a BTC Yield of -3.7%, a BTC Gain of -24,947 bitcoin and a BTC $ Gain of -$2.03 billion, so each share now carries less bitcoin than in January.
Holdings were at 848,517 bitcoin on October 25, a leap of 26% this year. Cost basis was $64.02 billion, about $75,446 per coin.
The market value on October 23 was $68.90 billion and the Bitcoin price was $81,200.
The company said Bitcoin was up 43% and MSTR was up 76% in the quarter. Sales of stock under its at-the-market program raised $5.41 billion net in the quarter and $21.23 billion raised in 2026 makes Strategy the fourth-largest U.S. equity issuer this year.
Strategy’s Digital Equity Highlights as of October 25, 2026, from its third-quarter earnings release.
“We’re at the beginning of the next bitcoin bull market,” Executive Chairman Michael Saylor said in the release. He cites banks getting on board with bitcoin and a price 21% above its 200-week moving average.
MSTR was off about 3.5% in after-hours trading on Oct. 29. Bitcoin dropped below $77,000 on the same day.
Shareholders back daily preferred dividends with 99.3% of votes
Strategy has sold about $431.8 million of bitcoin this year to pay for some of its preferred dividends and STRC buybacks. Cryptopolitan reported it sold 1,638 bitcoin in the week to August 2 for about $104.7 million.
Strategy’s common stockholders voted on October 28 to permit STRC, STRF, STRK and STRD dividends to accumulate on a calendar day basis. The measure got 99.3% of the votes cast, according to Strategy’s October 28 filing.
STRC changes November 1. STRF, STRK and STRD follow on January 1, 2027.
This year STRC buybacks were approximately $2.04 billion at an average price of $97.39 per share, ~2.6% below its stated amount of $100. Strategy maintains STRC dividend rate at 12.00%.
USD Assets are at $5.07 billion, which the company says would cover about 3.4 years of preferred dividends and interest. The USD Reserve alone stands at $4.83 billion, up from $3.225 billion on July 20.
If you're reading this, you’re already ahead. Stay there with our newsletter.
2
1.9k
Verified
OpenTrade appoints former SWIFT CEO Lázaro Campos as Chair to scale stablecoin yieldOpenTrade, the stablecoin yield infrastructure platform, has appointed former SWIFT CEO Lázaro Campos as Chair of its Board of Directors.
Lázaro has spent 35 years building and governing the infrastructure global finance runs on. As CEO, he led SWIFT through a full strategic and financial transformation (€600M revenue, 10,000 financial_institutions, 210 countries), including a 2008 crisis-driven restructuring that cut costs by 30% without sacrificing growth.
He has also sat on the Bank of England’s RTGS/CHAPS Board, served on Starling Bank’s board, and chairs Payoneer Europe today.
He now brings that experience to stablecoins. He joins as OpenTrade moves from early growth to scale, with more than $1B in transaction volume over the past 12 months, $300M in total value locked and $32M raised to date.
Campos’s track record across SWIFT and global payments
Seven weeks into his tenure as CEO, Lázaro set in motion a €150M redesign of SWIFT’s network so that payment data between European banks would stay in Europe. Under Lázaro’s leadership, SWIFT’s network volumes nearly doubled.
He also launched Innotribe, SWIFT’s innovation program. Earlier in his career there, he led SWIFT’s work on market infrastructure projects including CLS, CHAPS Euro, EBA Clearing and TARGET.
Since leaving SWIFT, he has held board roles across payments and digital banking. He is Chairman of Payoneer Europe, Chairman of PPRO’s Advisory Board and Senior Independent Director of International Workplace Group plc.
He was previously a Non-Executive Director of Starling Bank, an independent member of the Bank of England’s RTGS/CHAPS Board, a member of Standard Chartered’s Board Financial Crime Risk Committee and Chairman of The ID Co (Atto). He also co-founded FinTechStage.
“I’ve spent most of my career on the infrastructure the world uses to move money. Stablecoins are the next chapter, and yield is what makes them useful to businesses and the people they serve. OpenTrade has built the infrastructure this market needs, and I’m delighted to support Dave, Jeff and the team for what comes next,” said Lázaro Campos, Chair of the Board, OpenTrade.
OpenTrade powers real-world-asset yield for fintechs
OpenTrade exists to make every balance count. Fintechs and digital asset platforms use it to offer dollar- and euro-denominated yield backed by real-world assets. Clients use OpenTrade to earn yield on their own treasury, or to power earn products on their users’ balances, without building any investment infrastructure themselves.
“Stablecoins are becoming one of the rails global finance runs on, and the businesses building on them expect the same resilience and trust they get from the traditional system. Lázaro spent his career setting that standard. He ran infrastructure the world’s banks depend on every day, and having him as Chair as we scale says a lot about what this team has built,” said David Sutter, Co-founder and CEO of OpenTrade.
Appointment follows $17M strategic raise
Lázaro’s appointment follows OpenTrade’s $17M strategic raise in May 2026, led by Mercury Fund and Notion Capital with participation from a16z crypto, AlbionVC and CMCC Global. The funding is expanding OpenTrade’s product suite, including curated vaults, and taking it into new markets.
“This fundraise reflects the clear market demand for yield curation and orchestration across TradFi, CeFi and DeFi,” said Jay Wilson, Partner at AlbionVC, at the time of the raise.
As Chair, Lázaro will guide OpenTrade through its next phase: scaling stablecoin yield for fintechs and digital asset platforms worldwide.
OpenTrade appoints former SWIFT CEO Lázaro Campos as Chair to scale stablecoin yield
OpenTrade, the stablecoin yield infrastructure platform, has appointed former SWIFT CEO Lázaro Campos as Chair of its Board of Directors.
Lázaro has spent 35 years building and governing the infrastructure global finance runs on. As CEO, he led SWIFT through a full strategic and financial transformation (€600M revenue, 10,000 financial_institutions, 210 countries), including a 2008 crisis-driven restructuring that cut costs by 30% without sacrificing growth.
He has also sat on the Bank of England’s RTGS/CHAPS Board, served on Starling Bank’s board, and chairs Payoneer Europe today.
He now brings that experience to stablecoins. He joins as OpenTrade moves from early growth to scale, with more than $1B in transaction volume over the past 12 months, $300M in total value locked and $32M raised to date.
Campos’s track record across SWIFT and global payments
Seven weeks into his tenure as CEO, Lázaro set in motion a €150M redesign of SWIFT’s network so that payment data between European banks would stay in Europe. Under Lázaro’s leadership, SWIFT’s network volumes nearly doubled.
He also launched Innotribe, SWIFT’s innovation program. Earlier in his career there, he led SWIFT’s work on market infrastructure projects including CLS, CHAPS Euro, EBA Clearing and TARGET.
Since leaving SWIFT, he has held board roles across payments and digital banking. He is Chairman of Payoneer Europe, Chairman of PPRO’s Advisory Board and Senior Independent Director of International Workplace Group plc.
He was previously a Non-Executive Director of Starling Bank, an independent member of the Bank of England’s RTGS/CHAPS Board, a member of Standard Chartered’s Board Financial Crime Risk Committee and Chairman of The ID Co (Atto). He also co-founded FinTechStage.
“I’ve spent most of my career on the infrastructure the world uses to move money. Stablecoins are the next chapter, and yield is what makes them useful to businesses and the people they serve. OpenTrade has built the infrastructure this market needs, and I’m delighted to support Dave, Jeff and the team for what comes next,” said Lázaro Campos, Chair of the Board, OpenTrade.
OpenTrade powers real-world-asset yield for fintechs
OpenTrade exists to make every balance count. Fintechs and digital asset platforms use it to offer dollar- and euro-denominated yield backed by real-world assets. Clients use OpenTrade to earn yield on their own treasury, or to power earn products on their users’ balances, without building any investment infrastructure themselves.
“Stablecoins are becoming one of the rails global finance runs on, and the businesses building on them expect the same resilience and trust they get from the traditional system. Lázaro spent his career setting that standard. He ran infrastructure the world’s banks depend on every day, and having him as Chair as we scale says a lot about what this team has built,” said David Sutter, Co-founder and CEO of OpenTrade.
Appointment follows $17M strategic raise
Lázaro’s appointment follows OpenTrade’s $17M strategic raise in May 2026, led by Mercury Fund and Notion Capital with participation from a16z crypto, AlbionVC and CMCC Global. The funding is expanding OpenTrade’s product suite, including curated vaults, and taking it into new markets.
“This fundraise reflects the clear market demand for yield curation and orchestration across TradFi, CeFi and DeFi,” said Jay Wilson, Partner at AlbionVC, at the time of the raise.
As Chair, Lázaro will guide OpenTrade through its next phase: scaling stablecoin yield for fintechs and digital asset platforms worldwide.
1
2
3.4k
Verified
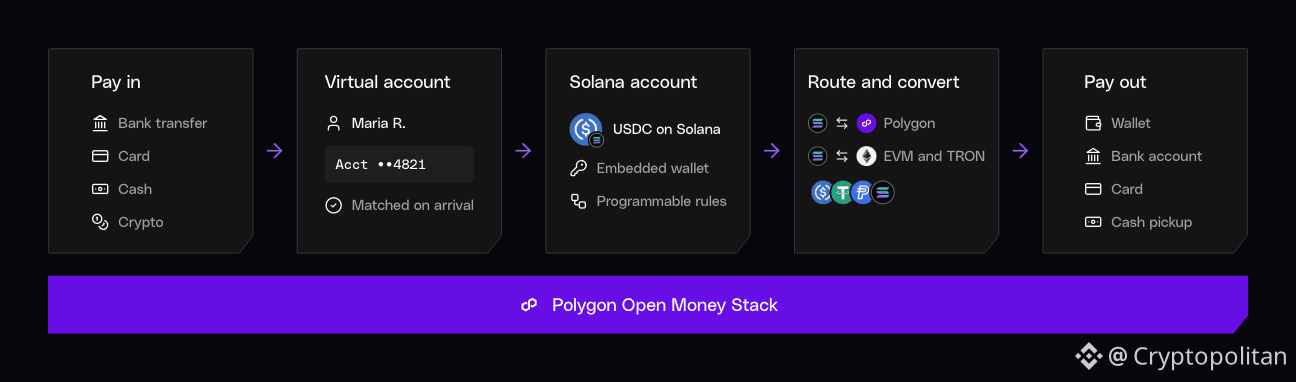
Article
Polygon opens US bank payouts to Solana stablecoin businessesNow, with one integration, Solana businesses can take a bank deposit, hold it in stablecoins and pay it out to a US bank account.
With licenses in 48 US states behind the dollar leg, Polygon Labs on Thursday added Solana to its Open Money Stack.
USDC, USDT and PYUSD route across TRON and EVM chains
The stack converts fiat into stablecoins on Solana, retains funds in embedded or custodial wallets, and pays out to bank accounts, cards, cash or wallets. Every client is given a virtual account so that incoming bank transfers have an address to go to.
In a blog post released by Polygon, the stack is said to move USDC, USDT, PYUSD, SOL and wrapped SOL across Solana, TRON and EVM chains in one transaction.
How a payment moves through Polygon’s Open Money Stack on Solana, from bank pay-in to payout, shown in its blog post of October 29, 2026.
The app can take USDC from an Ethereum wallet and settle it in SOL to a Solana user. TRON entered the stack earlier in October. Licenses are from the Coinme buy.
The closed deal gave Polygon 37 state money-transmitter licenses and 11 exemptions in a total of 48 US states, Cryptopolitan reported on October 14. It also brought Polygon a money services business registration with the Financial Crimes Enforcement Network.
Kira is among the first firms to plug in
Kira is among the first companies to use the Solana integration. The company moves clients between dollars and stablecoins, transmits payments via banking rails and pays suppliers overseas.
“We already use Solana to move stablecoins, and working with Polygon helps us turn those transfers into dollars in our clients’ bank accounts when they need to pay suppliers,” said Kira CEO Edrizio De La Cruz.
In 2026, the network processed over $5.5 trillion of stablecoin volume, said Vibhu Norby, chief product officer at the Solana Foundation. Polygon’s stack is another path for businesses, along with payment tools already on Solana, he said.
Per Polygon, Solana processes over $2 trillion in stablecoin volume every quarter.
The launch came about a week after Solana switched on its Alpenglow consensus upgrade. Finality went from around 12.8 seconds to 150 milliseconds.
Solana is Polygon’s newest move in a pivot that played out across 2026. In January, a spokesperson said, “Polygon Labs is no longer a scaling company, but a blockchain-based payments company.”
Polymarket, which accounted for more than half of Polygon’s transactions in March 2026, has been developing its own layer-2 network.
Polygon said in January it would buy smart-wallet provider Sequence and Coinme in deals worth more than $250 million combined. Together, the two constitute the Open Money Stack, which aggregates on- and off-ramps, wallets, cross-chain routing and settlement under a single API.
Co-founder Sandeep Nailwal branded the strategy a “reverse Stripe.”
Stablecoins now total about $300 billion in supply. Tether’s USDT leads the pack, with more than $180 billion, while Circle’s USDC sits at almost $72 billion.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Polygon opens US bank payouts to Solana stablecoin businesses
Now, with one integration, Solana businesses can take a bank deposit, hold it in stablecoins and pay it out to a US bank account.
With licenses in 48 US states behind the dollar leg, Polygon Labs on Thursday added Solana to its Open Money Stack.
USDC, USDT and PYUSD route across TRON and EVM chains
The stack converts fiat into stablecoins on Solana, retains funds in embedded or custodial wallets, and pays out to bank accounts, cards, cash or wallets. Every client is given a virtual account so that incoming bank transfers have an address to go to.
In a blog post released by Polygon, the stack is said to move USDC, USDT, PYUSD, SOL and wrapped SOL across Solana, TRON and EVM chains in one transaction.
How a payment moves through Polygon’s Open Money Stack on Solana, from bank pay-in to payout, shown in its blog post of October 29, 2026.
The app can take USDC from an Ethereum wallet and settle it in SOL to a Solana user. TRON entered the stack earlier in October. Licenses are from the Coinme buy.
The closed deal gave Polygon 37 state money-transmitter licenses and 11 exemptions in a total of 48 US states, Cryptopolitan reported on October 14. It also brought Polygon a money services business registration with the Financial Crimes Enforcement Network.
Kira is among the first firms to plug in
Kira is among the first companies to use the Solana integration. The company moves clients between dollars and stablecoins, transmits payments via banking rails and pays suppliers overseas.
“We already use Solana to move stablecoins, and working with Polygon helps us turn those transfers into dollars in our clients’ bank accounts when they need to pay suppliers,” said Kira CEO Edrizio De La Cruz.
In 2026, the network processed over $5.5 trillion of stablecoin volume, said Vibhu Norby, chief product officer at the Solana Foundation. Polygon’s stack is another path for businesses, along with payment tools already on Solana, he said.
Per Polygon, Solana processes over $2 trillion in stablecoin volume every quarter.
The launch came about a week after Solana switched on its Alpenglow consensus upgrade. Finality went from around 12.8 seconds to 150 milliseconds.
Solana is Polygon’s newest move in a pivot that played out across 2026. In January, a spokesperson said, “Polygon Labs is no longer a scaling company, but a blockchain-based payments company.”
Polymarket, which accounted for more than half of Polygon’s transactions in March 2026, has been developing its own layer-2 network.
Polygon said in January it would buy smart-wallet provider Sequence and Coinme in deals worth more than $250 million combined. Together, the two constitute the Open Money Stack, which aggregates on- and off-ramps, wallets, cross-chain routing and settlement under a single API.
Co-founder Sandeep Nailwal branded the strategy a “reverse Stripe.”
Stablecoins now total about $300 billion in supply. Tether’s USDT leads the pack, with more than $180 billion, while Circle’s USDC sits at almost $72 billion.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
899
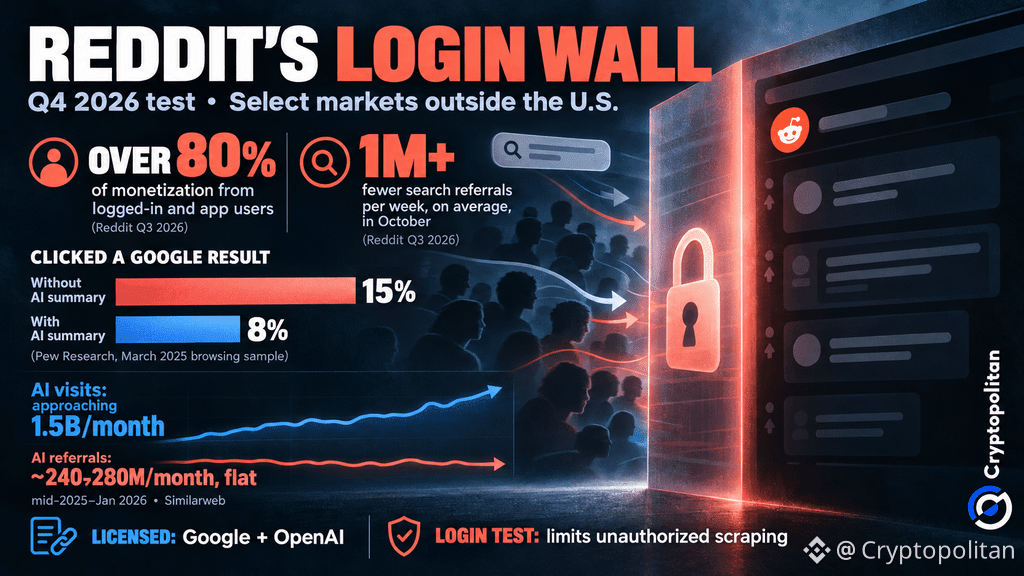
Article
Will Reddit lose casual readers by forcing users to sign in?Reddit wants more people to sign in before browsing its content online. The company will test the requirement in select markets outside the US during Q4 2026. There is no schedule yet for the introduction of this strategy to other markets. No information was given by Reddit on what users will see if they stay logged out.
Why Reddit wants you signed in
Reddit’s shareholder letter shows why. Logged-in and app users account for over 80% of monetization and most engagement. Huffman told The Verge that requiring accounts could improve personalization, advertising, and protection against unauthorized scraping.
The app’s incognito mode is also returning. Users won’t have to reveal their real-world identities, only sign in.
But there’s a trade-off. As Madison and Wall’s Luke Stillman told Reuters:
“Requiring users to log in creates another barrier to engagement, particularly for casual users.”
The numbers behind the decision
Reddit continued to have an increase in revenue, although traffic has decreased. In the third quarter, revenues rose 53% reaching $895 million, better than the estimation of analysts of $878.4 million. The average number of daily active unique users worldwide on Reddit was 130.3 million, including 79.6 million users outside the United States. However, the number of daily US users fell by 2% to 50.7 million.
In October, search traffic declined further. The search referrals for Reddit fell by an average of over 1 million every week, with logged-out users suffering the most. If the trend continues, Reddit warned that its daily users may decline by a low double-digit percentage in Q4. This will translate into a low double-digit drop from its current base of about 130 million users. It remains a forecast as of now.
The warning has made investors anxious. The shares of Reddit dropped by 18% during evening trading, according to Reuters.
What the AI search data actually shows
Huffman blamed Google’s AI Mode, saying it doesn’t send visitors to Reddit or other sites. Yet Google says AI Mode had surpassed one billion monthly users by May. More usage doesn’t necessarily mean more outbound clicks.
Pew Research found that Google users clicked a traditional result in 8% of visits with AI summaries, against 15% without them. Just 1% clicked links inside summaries.
Similarweb also found that monthly referrals from generative AI platforms stayed around 240 million–280 million through January 2026, even as monthly AI visits neared 1.5 billion.
Still, the effect on Reddit isn’t entirely negative. An Emory–Washington University study linked AI Overviews to 12% more daily comments in safe-for-work communities. Those gains largely disappeared from opinion and advice discussions after AI Mode arrived. Cryptopolitan flagged the search-referral risk in May 2025.
Reddit’s Login Wall by the Numbers: 80% Monetization, Falling Referrals and AI Search Trends
Licensed data versus lost casual readers
Reddit licenses content to Google and OpenAI while suing companies accused of unauthorized scraping. Google’s 2024 partnership gives it structured access through Reddit’s Data API, although Google says its use of publicly crawlable material is unchanged.
Selected overseas markets face the first tests, even as Reddit’s international daily audience grew 24% year over year. Accounts could improve engagement and ad targeting. But if casual visitors leave, Reddit’s reach could suffer.
Reddit expects $1.00 billion–$1.03 billion in Q4 revenue and $480 million–$510 million in adjusted EBITDA.
If you're reading this, you’re already ahead. Stay there with our newsletter.
Will Reddit lose casual readers by forcing users to sign in?
Reddit wants more people to sign in before browsing its content online. The company will test the requirement in select markets outside the US during Q4 2026. There is no schedule yet for the introduction of this strategy to other markets. No information was given by Reddit on what users will see if they stay logged out.
Why Reddit wants you signed in
Reddit’s shareholder letter shows why. Logged-in and app users account for over 80% of monetization and most engagement. Huffman told The Verge that requiring accounts could improve personalization, advertising, and protection against unauthorized scraping.
The app’s incognito mode is also returning. Users won’t have to reveal their real-world identities, only sign in.
But there’s a trade-off. As Madison and Wall’s Luke Stillman told Reuters:
“Requiring users to log in creates another barrier to engagement, particularly for casual users.”
The numbers behind the decision
Reddit continued to have an increase in revenue, although traffic has decreased. In the third quarter, revenues rose 53% reaching $895 million, better than the estimation of analysts of $878.4 million. The average number of daily active unique users worldwide on Reddit was 130.3 million, including 79.6 million users outside the United States. However, the number of daily US users fell by 2% to 50.7 million.
In October, search traffic declined further. The search referrals for Reddit fell by an average of over 1 million every week, with logged-out users suffering the most. If the trend continues, Reddit warned that its daily users may decline by a low double-digit percentage in Q4. This will translate into a low double-digit drop from its current base of about 130 million users. It remains a forecast as of now.
The warning has made investors anxious. The shares of Reddit dropped by 18% during evening trading, according to Reuters.
What the AI search data actually shows
Huffman blamed Google’s AI Mode, saying it doesn’t send visitors to Reddit or other sites. Yet Google says AI Mode had surpassed one billion monthly users by May. More usage doesn’t necessarily mean more outbound clicks.
Pew Research found that Google users clicked a traditional result in 8% of visits with AI summaries, against 15% without them. Just 1% clicked links inside summaries.
Similarweb also found that monthly referrals from generative AI platforms stayed around 240 million–280 million through January 2026, even as monthly AI visits neared 1.5 billion.
Still, the effect on Reddit isn’t entirely negative. An Emory–Washington University study linked AI Overviews to 12% more daily comments in safe-for-work communities. Those gains largely disappeared from opinion and advice discussions after AI Mode arrived. Cryptopolitan flagged the search-referral risk in May 2025.
Reddit’s Login Wall by the Numbers: 80% Monetization, Falling Referrals and AI Search Trends
Licensed data versus lost casual readers
Reddit licenses content to Google and OpenAI while suing companies accused of unauthorized scraping. Google’s 2024 partnership gives it structured access through Reddit’s Data API, although Google says its use of publicly crawlable material is unchanged.
Selected overseas markets face the first tests, even as Reddit’s international daily audience grew 24% year over year. Accounts could improve engagement and ad targeting. But if casual visitors leave, Reddit’s reach could suffer.
Reddit expects $1.00 billion–$1.03 billion in Q4 revenue and $480 million–$510 million in adjusted EBITDA.
If you're reading this, you’re already ahead. Stay there with our newsletter.
OPENAI-2.34%
GOOGUS-1.76%
3
1.8k
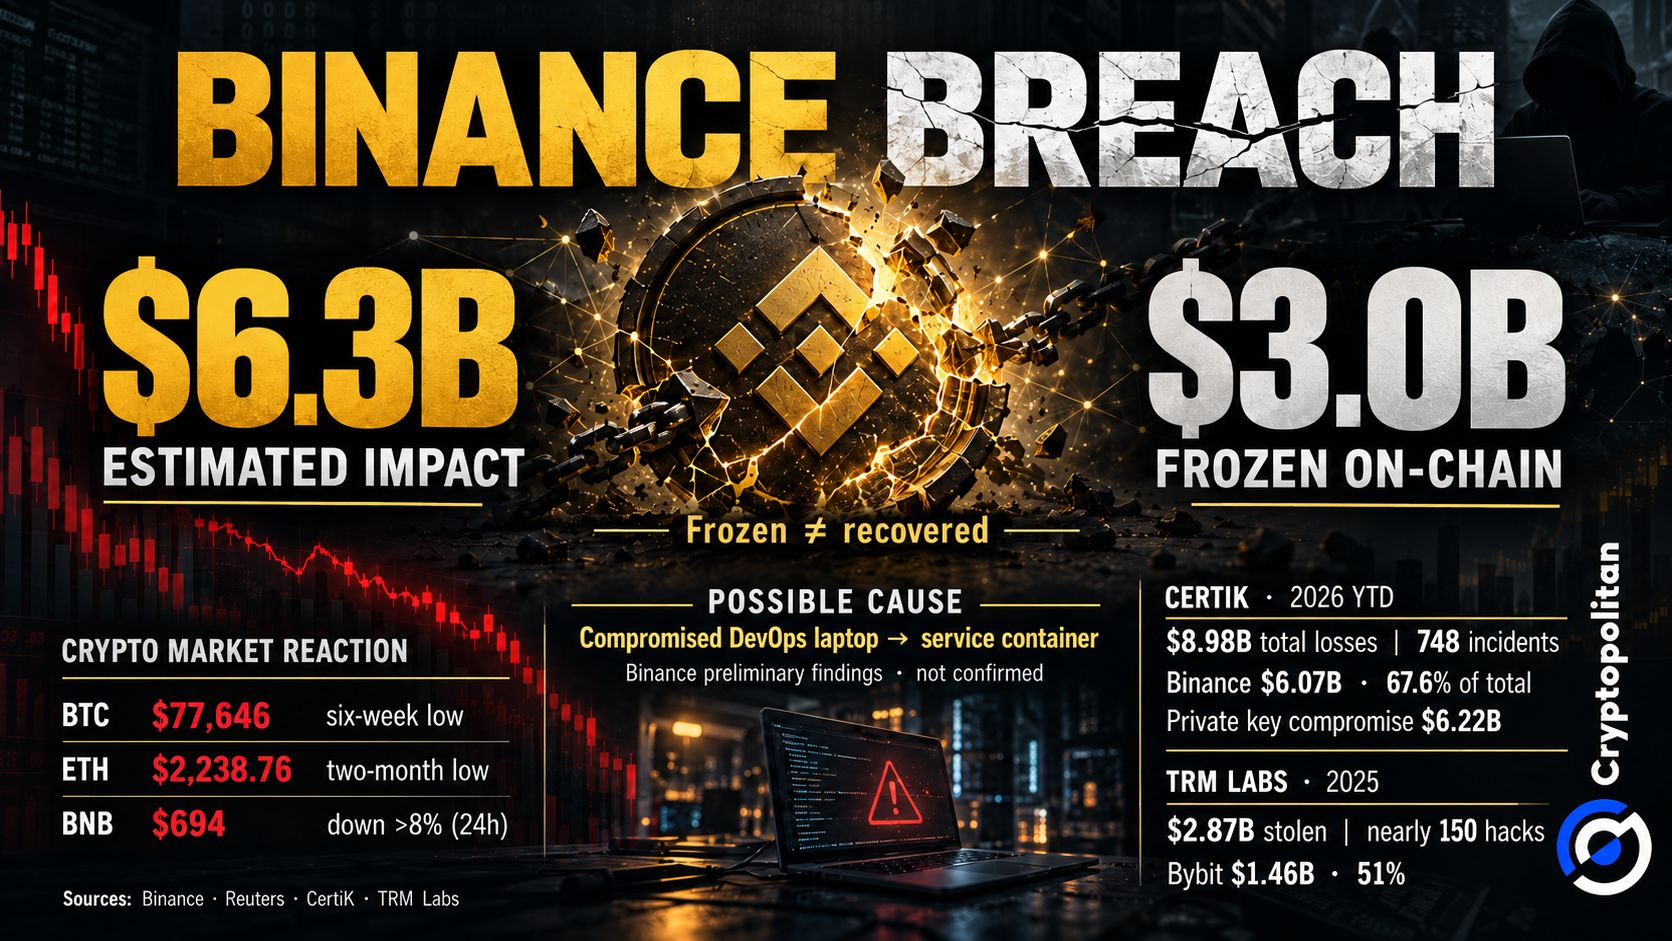
Article
Could Binance’s $6.3B hack trigger a wider crypto sell-off?Binance is looking into a security breach that is estimated to have caused losses of $6.3 billion. It has frozen around $3 billion in assets and has stopped its users from making deposits and withdrawals. But the exchange has not yet determined how much money is lost forever.
What Binance says it found
According to Binance’s statement on October 30, a laptop of a DevOps engineer has been compromised. The attacker may have made use of it to get access to the service container and initiate unauthorized withdrawals. So far, Binance says it has found no evidence that wallet private keys were exposed.
It is not yet clear how much damage has occurred. Binance has estimated the damage from the event at $6.3 billion. However, this does not mean that all this money is gone forever.
After issuing the initial warning, Binance cancelled authorization for the affected address. It also contacted the police and blockchain investigators to help track down the stolen funds.
According to the exchange, any losses will be compensated from their SAFU reserves as well as from the company funds. The exchange will also issue a technical report once the investigation has finished. An updated proof of reserves will also be published once the security issues have been cleared.
Frozen is not recovered
The roughly $3 billion Binance has frozen is not the same as money recovered.
Tether CEO Paolo Ardoino reported freezing more than 1.567 billion USDT. Circle’s Jeremy Allaire confirmed freezing over 800 million USDC alongside law enforcement. Both amounts are included in Binance’s total.
Circle is closely tracking reports of a potential exploit involving Binance. In coordination with law enforcement, we have frozen more than 800M USDC associated with the incident and will continue supporting the investigation.
— Jeremy Allaire (@jerallaire) October 29, 2026
However, freezing stolen assets only prevents further transfers. It does not automatically return the money.
The timing of the asset freezes was critical. Bitquery showed that Ethereum wallets that had assets frozen within a week kept 59% of their USDT. After half a year, only 12% of the USDT is left.
The limits of asset freezes were clearly exposed during the Bitget hack in September. Cryptopolitan pointed out that Circle and Tether managed to freeze only $318,000 from $387.5 million that had been stolen. By that time, the money was already converted into other cryptocurrencies.
The clues investigators will weigh
Investigators have two questions to answer: first, how the hacker was able to allow the withdrawals, and secondly, what happened to the rest of the money.
The suspicion that a Binance laptop was compromised to open the door for the hacker gives investigators a place to start. But they still have to prove how the hacker managed to gain access to the laptop.
Another option worth looking into relates to EIP-7702. This Ethereum feature gives regular accounts the right to assign transactions to smart contracts.
As Binance Academy points out, hackers can take advantage of these permissions to empty wallets. However, Binance hasn’t connected EIP-7702 to the hack and has not confirmed whether or not it was used.
Prices slid as the news broke
The uncertainty quickly spread to cryptocurrency markets.
Reuters reported that Bitcoin fell to a six-week low of $77,646. Ether dropped to $2,238.76, its lowest level in two months. BNB also lost more than 8% over 24 hours, falling to $694.
Binance $6.3B Breach by the Numbers: $3B Frozen as Crypto Prices Fall
The breach has also pushed this year’s security losses sharply higher.
According to CertiK’s dashboard, cryptocurrency losses reached $8.98 billion across 748 incidents in 2026. Binance alone accounted for $6.07 billion, or 67.6% of the total.
Private key compromise remained the costliest attack category at $6.22 billion, although other exploits occurred more frequently.
The figures show how a single major breach can dominate annual losses. TRM Labs recorded $2.87 billion stolen across nearly 150 hacks in 2025. The $1.46 billion Bybit breach alone accounted for 51% of that total.
Will SAFU and Proof of Reserves reassure?
Binance insists that user funds remain safe and promises to cover losses through its SAFU reserve and company funds.
But restoring confidence will take more than that assurance. Customers will be looking for answers in the promised technical report and updated Proof of Reserves. They will also want to know how much of the frozen $3 billion Binance can actually recover.
The hacker who perpetrated the alleged theft of $1.5 billion from Binance spread out over 18,270 BTC that were taken in the hack over 19 wallets within a matter of minutes, after which he did not move the cryptocurrency. It has been found on the blockchain that 17 of these wallets currently have precisely 1,000 BTC in them, while the other two have 832.5 BTC and 437.7 BTC, respectively.
It was done through the use of a peel chain, where parts of the stolen cryptocurrency were moved via new addresses. No wallet among the 19 had made an outbound transaction by 04:23 UTC on Friday.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Could Binance’s $6.3B hack trigger a wider crypto sell-off?
Binance is looking into a security breach that is estimated to have caused losses of $6.3 billion. It has frozen around $3 billion in assets and has stopped its users from making deposits and withdrawals. But the exchange has not yet determined how much money is lost forever.
What Binance says it found
According to Binance’s statement on October 30, a laptop of a DevOps engineer has been compromised. The attacker may have made use of it to get access to the service container and initiate unauthorized withdrawals. So far, Binance says it has found no evidence that wallet private keys were exposed.
It is not yet clear how much damage has occurred. Binance has estimated the damage from the event at $6.3 billion. However, this does not mean that all this money is gone forever.
After issuing the initial warning, Binance cancelled authorization for the affected address. It also contacted the police and blockchain investigators to help track down the stolen funds.
According to the exchange, any losses will be compensated from their SAFU reserves as well as from the company funds. The exchange will also issue a technical report once the investigation has finished. An updated proof of reserves will also be published once the security issues have been cleared.
Frozen is not recovered
The roughly $3 billion Binance has frozen is not the same as money recovered.
Tether CEO Paolo Ardoino reported freezing more than 1.567 billion USDT. Circle’s Jeremy Allaire confirmed freezing over 800 million USDC alongside law enforcement. Both amounts are included in Binance’s total.
Circle is closely tracking reports of a potential exploit involving Binance. In coordination with law enforcement, we have frozen more than 800M USDC associated with the incident and will continue supporting the investigation.
— Jeremy Allaire (@jerallaire) October 29, 2026
However, freezing stolen assets only prevents further transfers. It does not automatically return the money.
The timing of the asset freezes was critical. Bitquery showed that Ethereum wallets that had assets frozen within a week kept 59% of their USDT. After half a year, only 12% of the USDT is left.
The limits of asset freezes were clearly exposed during the Bitget hack in September. Cryptopolitan pointed out that Circle and Tether managed to freeze only $318,000 from $387.5 million that had been stolen. By that time, the money was already converted into other cryptocurrencies.
The clues investigators will weigh
Investigators have two questions to answer: first, how the hacker was able to allow the withdrawals, and secondly, what happened to the rest of the money.
The suspicion that a Binance laptop was compromised to open the door for the hacker gives investigators a place to start. But they still have to prove how the hacker managed to gain access to the laptop.
Another option worth looking into relates to EIP-7702. This Ethereum feature gives regular accounts the right to assign transactions to smart contracts.
As Binance Academy points out, hackers can take advantage of these permissions to empty wallets. However, Binance hasn’t connected EIP-7702 to the hack and has not confirmed whether or not it was used.
Prices slid as the news broke
The uncertainty quickly spread to cryptocurrency markets.
Reuters reported that Bitcoin fell to a six-week low of $77,646. Ether dropped to $2,238.76, its lowest level in two months. BNB also lost more than 8% over 24 hours, falling to $694.
Binance $6.3B Breach by the Numbers: $3B Frozen as Crypto Prices Fall
The breach has also pushed this year’s security losses sharply higher.
According to CertiK’s dashboard, cryptocurrency losses reached $8.98 billion across 748 incidents in 2026. Binance alone accounted for $6.07 billion, or 67.6% of the total.
Private key compromise remained the costliest attack category at $6.22 billion, although other exploits occurred more frequently.
The figures show how a single major breach can dominate annual losses. TRM Labs recorded $2.87 billion stolen across nearly 150 hacks in 2025. The $1.46 billion Bybit breach alone accounted for 51% of that total.
Will SAFU and Proof of Reserves reassure?
Binance insists that user funds remain safe and promises to cover losses through its SAFU reserve and company funds.
But restoring confidence will take more than that assurance. Customers will be looking for answers in the promised technical report and updated Proof of Reserves. They will also want to know how much of the frozen $3 billion Binance can actually recover.
The hacker who perpetrated the alleged theft of $1.5 billion from Binance spread out over 18,270 BTC that were taken in the hack over 19 wallets within a matter of minutes, after which he did not move the cryptocurrency. It has been found on the blockchain that 17 of these wallets currently have precisely 1,000 BTC in them, while the other two have 832.5 BTC and 437.7 BTC, respectively.
It was done through the use of a peel chain, where parts of the stolen cryptocurrency were moved via new addresses. No wallet among the 19 had made an outbound transaction by 04:23 UTC on Friday.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
2
1.1k
Coinbase ends three-quarter losing streak with $719M profitCoinbase managed to snap its three-quarter losing streak and pull in a profit. The exchange clocked $1.22 billion in Q3 revenue—a 35% drop from the same period last year—but still a massive win, as net income climbed 66% to $719 million.
For the past three quarters, Coinbase has struggled with losses amid continued volatility in crypto markets. Nonetheless, trading activity picked up in September, seeing as crypto prices recovered. Still, analysts remain divided over how much the price rebound actually helped the exchange and whether the momentum will last.
Coinbase’s newer businesses are doing well
Under CEO Brian Armstrong’s direction, Coinbase has been aggressively pushing into alternative financial products to shield itself from sudden token crashes. Some of these products delivered strong results in Q3. For instance, subscriptions and non-trading services brought in 49% of overall net revenue.
The number of paying Coinbase One subscribers particularly climbed 24% year over year to a new record in Q3 2026. The group represents some of the platform’s most valuable customers, with average revenue per user 3.5 times higher, balances 4.2 times larger and long-term trading retention more than 50% higher.
Furthermore, the firm’s prediction markets platform has scaled remarkably quickly, with an annualised revenue run rate exceeding $200 million. Since its launch, the prediction markets platform has seen 82% quarterly compound growth and a daily trader count growth of 60%+ quarter over quarter.
Speaking about the Q3 revenue performance, Alesia Haas, CFO, said, “Subscription services and prediction markets have made Coinbase more diversified and resilient across market cycles.” But Coinbase still gets a lot of its revenue from crypto transactions. Even as it diversifies, analysts say the exchange remains highly exposed to fluctuations in crypto trading activity.
USDC revenue provides another boost to Coinbase
Coinbase is also benefiting from the increasing demand for USDC (a dollar-pegged stablecoin issued by Circle). The exchange said average USDC held across products was a record $22 billion in Q3 2026 (+49% YoY).
The growth resulted in $307 million in stablecoin revenue during the quarter (up from $292M Q2). The exchange said it was driven by higher average USDC balances and interest rates, but some of the growth was offset by balances held outside its platform.
The stablecoin business is particularly important to Coinbase’s diversification strategy because it provides revenue beyond traditional cryptocurrency trading. But it still has some sensitivity to interest rates and to the amount of USDC customers hold on Coinbase products.
Cumulatively, in Q3, Coinbase’s share of global trading volume reached 10.7%. The exchange also strengthened its position in spot and derivatives trading, with crypto derivatives trading volume increasing at a compound annual growth rate (CAGR) of 179% over the past two years.
Coinbase lowered trading fees in September, raising concerns
Coinbase has been facing growing pressure from cheaper rivals, including Robinhood Markets Inc. More recently, the exchange responded with reduced fees for many active traders. However, some experts worry that, given current market dynamics, trading fees across the crypto exchange industry could eventually fall to zero.
“Everyone wants to know if it’s going to be the beginning of a take-rate decline,” said Dan Dolev, an analyst at Mizuho Securities USA.
Up until September, Coinbase had enough pricing power to protect itself against any market downturn by adjusting fees. The company managed to protect its revenue from transaction fees by raising fees for casual buyers and offering discounts to high-frequency trading users.
Matthew Sigel, the head of digital assets at VanEck, like many analysts, agrees that the weak link for exchanges is pricing. He said that if platforms are unable to convert active trading into revenue due to fee reductions, the entire ecosystem suffers.
In addition, he stated that Coinbase is particularly vulnerable to this pricing problem because of its track record of generating revenue through high fees charged to retail clients, which breaks down once fee compression becomes the norm.
Looking ahead, analysts remain divided over Coinbase’s diversification strategy. JPMorgan sees significant upside potential in tokenization, payments and Base, while Barclays is more sceptical that these businesses will sufficiently offset the exchange’s dependence on retail trading revenue and USDC.
All told, Coinbase’s latest results suggest that its diversification strategy is gaining traction. However, the exchange has yet to prove that its newer businesses can generate enough revenue to offset weaker retail trading activity. Its ability to expand stablecoin adoption, prediction markets, and blockchain infrastructure could determine whether it can sustain profitability through another prolonged crypto market downturn.
If you're reading this, you’re already ahead. Stay there with our newsletter.
Coinbase ends three-quarter losing streak with $719M profit
Coinbase managed to snap its three-quarter losing streak and pull in a profit. The exchange clocked $1.22 billion in Q3 revenue—a 35% drop from the same period last year—but still a massive win, as net income climbed 66% to $719 million.
For the past three quarters, Coinbase has struggled with losses amid continued volatility in crypto markets. Nonetheless, trading activity picked up in September, seeing as crypto prices recovered. Still, analysts remain divided over how much the price rebound actually helped the exchange and whether the momentum will last.
Coinbase’s newer businesses are doing well
Under CEO Brian Armstrong’s direction, Coinbase has been aggressively pushing into alternative financial products to shield itself from sudden token crashes. Some of these products delivered strong results in Q3. For instance, subscriptions and non-trading services brought in 49% of overall net revenue.
The number of paying Coinbase One subscribers particularly climbed 24% year over year to a new record in Q3 2026. The group represents some of the platform’s most valuable customers, with average revenue per user 3.5 times higher, balances 4.2 times larger and long-term trading retention more than 50% higher.
Furthermore, the firm’s prediction markets platform has scaled remarkably quickly, with an annualised revenue run rate exceeding $200 million. Since its launch, the prediction markets platform has seen 82% quarterly compound growth and a daily trader count growth of 60%+ quarter over quarter.
Speaking about the Q3 revenue performance, Alesia Haas, CFO, said, “Subscription services and prediction markets have made Coinbase more diversified and resilient across market cycles.” But Coinbase still gets a lot of its revenue from crypto transactions. Even as it diversifies, analysts say the exchange remains highly exposed to fluctuations in crypto trading activity.
USDC revenue provides another boost to Coinbase
Coinbase is also benefiting from the increasing demand for USDC (a dollar-pegged stablecoin issued by Circle). The exchange said average USDC held across products was a record $22 billion in Q3 2026 (+49% YoY).
The growth resulted in $307 million in stablecoin revenue during the quarter (up from $292M Q2). The exchange said it was driven by higher average USDC balances and interest rates, but some of the growth was offset by balances held outside its platform.
The stablecoin business is particularly important to Coinbase’s diversification strategy because it provides revenue beyond traditional cryptocurrency trading. But it still has some sensitivity to interest rates and to the amount of USDC customers hold on Coinbase products.
Cumulatively, in Q3, Coinbase’s share of global trading volume reached 10.7%. The exchange also strengthened its position in spot and derivatives trading, with crypto derivatives trading volume increasing at a compound annual growth rate (CAGR) of 179% over the past two years.
Coinbase lowered trading fees in September, raising concerns
Coinbase has been facing growing pressure from cheaper rivals, including Robinhood Markets Inc. More recently, the exchange responded with reduced fees for many active traders. However, some experts worry that, given current market dynamics, trading fees across the crypto exchange industry could eventually fall to zero.
“Everyone wants to know if it’s going to be the beginning of a take-rate decline,” said Dan Dolev, an analyst at Mizuho Securities USA.
Up until September, Coinbase had enough pricing power to protect itself against any market downturn by adjusting fees. The company managed to protect its revenue from transaction fees by raising fees for casual buyers and offering discounts to high-frequency trading users.
Matthew Sigel, the head of digital assets at VanEck, like many analysts, agrees that the weak link for exchanges is pricing. He said that if platforms are unable to convert active trading into revenue due to fee reductions, the entire ecosystem suffers.
In addition, he stated that Coinbase is particularly vulnerable to this pricing problem because of its track record of generating revenue through high fees charged to retail clients, which breaks down once fee compression becomes the norm.
Looking ahead, analysts remain divided over Coinbase’s diversification strategy. JPMorgan sees significant upside potential in tokenization, payments and Base, while Barclays is more sceptical that these businesses will sufficiently offset the exchange’s dependence on retail trading revenue and USDC.
All told, Coinbase’s latest results suggest that its diversification strategy is gaining traction. However, the exchange has yet to prove that its newer businesses can generate enough revenue to offset weaker retail trading activity. Its ability to expand stablecoin adoption, prediction markets, and blockchain infrastructure could determine whether it can sustain profitability through another prolonged crypto market downturn.
If you're reading this, you’re already ahead. Stay there with our newsletter.
234
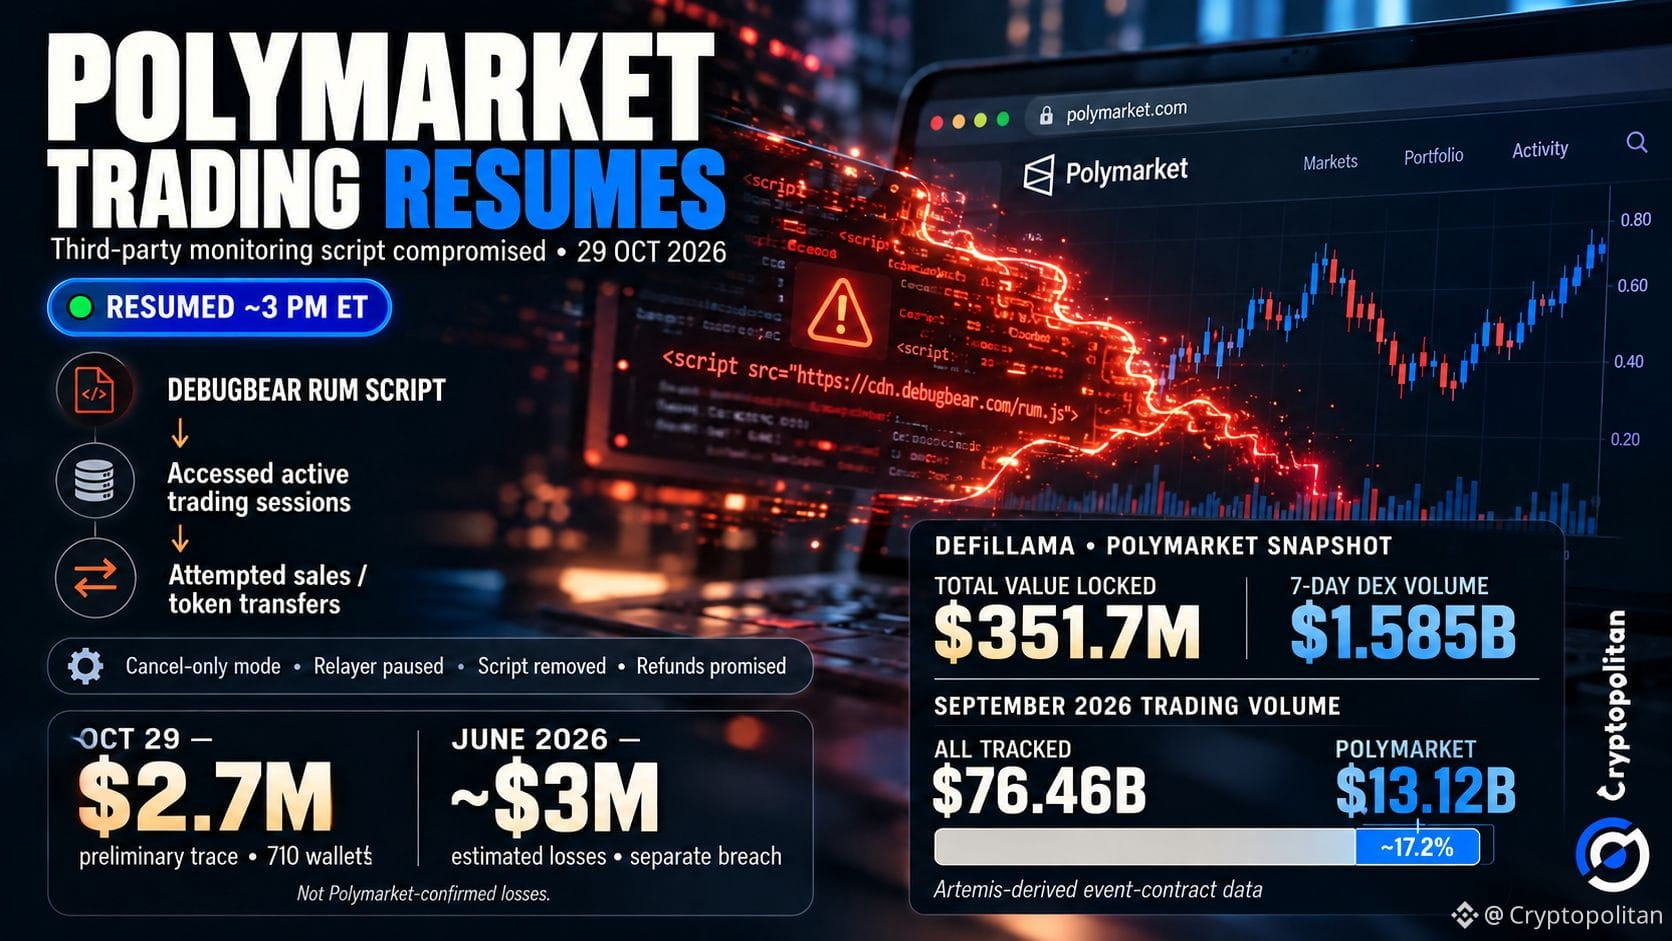
Article
Polymarket’s security troubles may be far from overPolymarket opened trading again on its international exchange on October 29, 2026, after being forced to shut down for a short time due to a compromised monitoring script. The exchange stopped orders, halted relayer activities, and promised customers their money back. The separate US platform was unaffected.
A monitoring script that reached into live trading sessions
Hudson Rock discovered a 15,187-byte malicious payload in DebugBear’s Real User Monitoring script. It was able to gain access to saved account information, find out about authorized clients of traders, and attempt the selling of positions as well as the transfer of tokens.
Polymarket’s website code also showed that the DebugBear script had been removed. The attack appears to have exploited code running on the website, rather than a flaw in its smart contracts.
Cancel-only mode, then a fix by 3 p.m. ET
Polymarket put the international exchange in cancel-only mode on October 29, 2026. Its status account said a provider was compromised and the case had been referred to U.K. law enforcement.
On October 29, 2026, around 3 p.m. ET, trading began again at Polymarket. The company announced its refund policy. As per CNBC’s report, customers who lost below $10,000 are expected to receive their refunds by October 30, 2026. In contrast, the company’s customers who lost over that amount need to sign a release form first. Even though the company communicated its refund plans, it does not confirm that any refunds have been issued.
DebugBear told customers to pull its code
DebugBear also acknowledged a security problem. On October 29, 2026, the company urged customers to remove its monitoring code while specialist responders investigated.
We’re impacted by an ongoing security incident. If you use our RUM product, please remove the embed code from your website.
— DebugBear (@DebugBear) October 29, 2026
The warning highlighted a wider concern. Third-party scripts can run inside legitimate websites. If compromised, they may gain access to users’ active browser sessions.
Preliminary loss estimates versus confirmed losses
For now, the financial damage remains unclear. Betting Intelligence and Polysights traced at least $2.7 million in withdrawals involving 710 wallets on October 29, 2026, CNBC reported.
Meanwhile, Hudson Rock identified about $2.19 million at a fallback recipient address. However, that balance does not establish how much was stolen. Polymarket has yet to confirm the total losses.
Polymarket DebugBear Breach: Trading Status, $2.7M Loss Estimate and Market Data
Two earlier vendor failures, no shared cause
This wasn’t Polymarket’s first vendor-related security problem. In June 2026, Halborn and TechCrunch reported a malicious-script attack. It reportedly drained around $3 million from at least 11 wallets. Polymarket promised refunds then, too.
Earlier, in December 2025, a separate authentication-provider breach affected users’ accounts. Both Cryptopolitan and CertiK documented the incident.
All three cases involved outside providers. However, there is no evidence linking them to the same attacker or underlying cause.
What repeated vendor exposure means for a $78 billion sector
These repeated incidents come as prediction markets attract more trading activity. An Artemis-derived report recorded $76.46 billion in trading volume across tracked markets in September 2026. Polymarket accounted for $13.12 billion. These figures represent trading activity, not assets held.
That growth brings security concerns into sharper focus. CertiK warns that platforms combining traditional web services with blockchain technology can still have centralized vulnerabilities.
Such risks could also discourage institutional investors. According to Jefferies, hedge funds are showing interest but remain cautious. Liquidity, compliance and reputational concerns continue to hold them back.
Meanwhile, KPMG highlights the different responsibilities of vendors, brokers, exchanges and clearinghouses. U.S.-regulated exchanges must meet surveillance, system-safeguard and participant-protection requirements. However, those rules do not automatically apply to Polymarket International.
For Polymarket, restoring trading is only part of the challenge. The bigger test is whether it can manage risks from outside providers and regain users’ confidence.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Polymarket’s security troubles may be far from over
Polymarket opened trading again on its international exchange on October 29, 2026, after being forced to shut down for a short time due to a compromised monitoring script. The exchange stopped orders, halted relayer activities, and promised customers their money back. The separate US platform was unaffected.
A monitoring script that reached into live trading sessions
Hudson Rock discovered a 15,187-byte malicious payload in DebugBear’s Real User Monitoring script. It was able to gain access to saved account information, find out about authorized clients of traders, and attempt the selling of positions as well as the transfer of tokens.
Polymarket’s website code also showed that the DebugBear script had been removed. The attack appears to have exploited code running on the website, rather than a flaw in its smart contracts.
Cancel-only mode, then a fix by 3 p.m. ET
Polymarket put the international exchange in cancel-only mode on October 29, 2026. Its status account said a provider was compromised and the case had been referred to U.K. law enforcement.
On October 29, 2026, around 3 p.m. ET, trading began again at Polymarket. The company announced its refund policy. As per CNBC’s report, customers who lost below $10,000 are expected to receive their refunds by October 30, 2026. In contrast, the company’s customers who lost over that amount need to sign a release form first. Even though the company communicated its refund plans, it does not confirm that any refunds have been issued.
DebugBear told customers to pull its code
DebugBear also acknowledged a security problem. On October 29, 2026, the company urged customers to remove its monitoring code while specialist responders investigated.
We’re impacted by an ongoing security incident. If you use our RUM product, please remove the embed code from your website.
— DebugBear (@DebugBear) October 29, 2026
The warning highlighted a wider concern. Third-party scripts can run inside legitimate websites. If compromised, they may gain access to users’ active browser sessions.
Preliminary loss estimates versus confirmed losses
For now, the financial damage remains unclear. Betting Intelligence and Polysights traced at least $2.7 million in withdrawals involving 710 wallets on October 29, 2026, CNBC reported.
Meanwhile, Hudson Rock identified about $2.19 million at a fallback recipient address. However, that balance does not establish how much was stolen. Polymarket has yet to confirm the total losses.
Polymarket DebugBear Breach: Trading Status, $2.7M Loss Estimate and Market Data
Two earlier vendor failures, no shared cause
This wasn’t Polymarket’s first vendor-related security problem. In June 2026, Halborn and TechCrunch reported a malicious-script attack. It reportedly drained around $3 million from at least 11 wallets. Polymarket promised refunds then, too.
Earlier, in December 2025, a separate authentication-provider breach affected users’ accounts. Both Cryptopolitan and CertiK documented the incident.
All three cases involved outside providers. However, there is no evidence linking them to the same attacker or underlying cause.
What repeated vendor exposure means for a $78 billion sector
These repeated incidents come as prediction markets attract more trading activity. An Artemis-derived report recorded $76.46 billion in trading volume across tracked markets in September 2026. Polymarket accounted for $13.12 billion. These figures represent trading activity, not assets held.
That growth brings security concerns into sharper focus. CertiK warns that platforms combining traditional web services with blockchain technology can still have centralized vulnerabilities.
Such risks could also discourage institutional investors. According to Jefferies, hedge funds are showing interest but remain cautious. Liquidity, compliance and reputational concerns continue to hold them back.
Meanwhile, KPMG highlights the different responsibilities of vendors, brokers, exchanges and clearinghouses. U.S.-regulated exchanges must meet surveillance, system-safeguard and participant-protection requirements. However, those rules do not automatically apply to Polymarket International.
For Polymarket, restoring trading is only part of the challenge. The bigger test is whether it can manage risks from outside providers and regain users’ confidence.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
334
Binance Hit by $6.3 Billion Hack, Largest in Crypto HistoryThe biggest crypto hack in history just transpired on the largest crypto exchange. Binance has put a number on the security incident that rocked the exchange on Thursday, October 29. In an update posted today, the exchange confirms nearly $6.3 billion was affected. This is a developing story and the figures could change as Binance and its partners keep tracing the funds.
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private… pic.twitter.com/5REncAI77y
— Binance (@binance) October 30, 2026
The industry came together to freeze approximately $3 billion onchain, which leaves around $3.3 billion out of reach at the time of writing. DeFillama states that the unrecovered portion alone is more than was stolen across all of crypto last year. It is also equivalent to how much was lost in 2023 and 2024 combined.
A Compromised Laptop Gave the Attacker a Way In
Binance’s initial findings point to a compromised DevOps engineers laptop. The exchange said that the attacker used the machine to reach an internal service container and push unauthorized withdrawal transactions from there. As of now, Binance states that it has found no signs that any wallet private keys were leaked, and it plans to put out a full technical post-mortem report once the facts are verified.
What is verified now is that the attack began around 4:30 P.M. ET, according to onchain data from Arkham. Data from Arkham shows that the attacker siphoned large amounts of Bitcoin, Ethereum, Tron and Solana among other assets. Tether CEO Paolo Ardoino confirmed on X that they froze $1.567 billion in USDT and Circle CEO Jeremy Allaire also confirmed that they froze over $800 million in USDC. Ripple, World Liberty, BitGo and Paxos also froze stolen assets, and Arbitrum’s Security Council froze around $30.5 million. The largest DeFi lending protocol, Aave, also froze its lending markets as precautionary measure, after the attacker borrowed Ethereum against stolen USDT.
Tether froze more than 1.567B USDT related to a potential Binance exchange hack.
Protecting the industry and our partners is our main priority.
Stay safe everyone.
— Paolo Ardoino 🤖 (@paoloardoino) October 29, 2026
Circle is closely tracking reports of a potential exploit involving Binance. In coordination with law enforcement, we have frozen more than 800M USDC associated with the incident and will continue supporting the investigation.
— Jeremy Allaire (@jerallaire) October 29, 2026
We’re aware of reports of a potential incident affecting Binance-affiliated wallets.
Aave’s contracts are unaffected, and positions remain overcollateralized. As a precaution, all DAO-operated markets across V3 and V4 have been frozen.
The freeze pauses new deposits and…
— Aave (@aave) October 29, 2026
Binance have also paused deposits and withdrawals as security checks are ongoing. Binance has also revoked authorization for the affected address and is working with law enforcement and blockchain intelligence firms to recover the funds. The exchange says its SAFU emergency fund and company reserves will cover every dollar of user losses, and an updated Proof of Reserves will follow after remediation.
Blockaid Traces the Drain Back to One Hot Wallet
Blockchain security firm Blockaid has published one of the most detailed onchain breakdowns of the attack so far. Its report centers on Binance 14, one of the exchange’s largest and busiest Ethereum hot wallets.
According to Blockaid, the attacker funded an operator address through Tornado Cash starting Oct. 28 and rehearsed the whole sequence on its own wallets with test runs of $2 to $6. At 20:20 UTC on Oct. 29, it sent a single transaction carrying 50 EIP-7702 authorizations signed with the Binance 14 key. The wallet was still processing withdrawals, so the attacker had no way of knowing which nonce would be live and signed a whole range instead. One matched. That handed control of the wallet to an unverified sweeper contract only the attacker could operate.
About three minutes later, the sweeper emptied Binance 14 of 167,464 ETH, 1.615 billion USDT and around 60 other tokens, worth roughly $2.5 billion at the time. The wallet was left holding 1 ETH. Within 12 minutes, 10 more Binance hot wallets on Ethereum, Arbitrum, Avalanche and Optimism sent funds to the same collection address. The delegation stayed active, so the attacker returned at 21:44 UTC and took another 200 million USDT in fresh deposits without a new signature.
Blockaid CEO Ido Ben-Natan said that the evidence points to compromised signing infrastructure, and he does not think a key was leaked. That fits with Binance’s account of a breached laptop and service container. Ben-Natan also drew parallels with the $1.5 billion Bybit hack of February 2025, which this incident now dwarfs several times over.
Onchain investigator ZachXBT suspects North Korea’s Lazarus Group, though neither Binance nor any authority has confirmed the attribution. Binance has asked users to rely only on its official channels for updates.
The smartest crypto minds already read our newsletter. Want in? Join them.
Binance Hit by $6.3 Billion Hack, Largest in Crypto History
The biggest crypto hack in history just transpired on the largest crypto exchange. Binance has put a number on the security incident that rocked the exchange on Thursday, October 29. In an update posted today, the exchange confirms nearly $6.3 billion was affected. This is a developing story and the figures could change as Binance and its partners keep tracing the funds.
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private… pic.twitter.com/5REncAI77y
— Binance (@binance) October 30, 2026
The industry came together to freeze approximately $3 billion onchain, which leaves around $3.3 billion out of reach at the time of writing. DeFillama states that the unrecovered portion alone is more than was stolen across all of crypto last year. It is also equivalent to how much was lost in 2023 and 2024 combined.
A Compromised Laptop Gave the Attacker a Way In
Binance’s initial findings point to a compromised DevOps engineers laptop. The exchange said that the attacker used the machine to reach an internal service container and push unauthorized withdrawal transactions from there. As of now, Binance states that it has found no signs that any wallet private keys were leaked, and it plans to put out a full technical post-mortem report once the facts are verified.
What is verified now is that the attack began around 4:30 P.M. ET, according to onchain data from Arkham. Data from Arkham shows that the attacker siphoned large amounts of Bitcoin, Ethereum, Tron and Solana among other assets. Tether CEO Paolo Ardoino confirmed on X that they froze $1.567 billion in USDT and Circle CEO Jeremy Allaire also confirmed that they froze over $800 million in USDC. Ripple, World Liberty, BitGo and Paxos also froze stolen assets, and Arbitrum’s Security Council froze around $30.5 million. The largest DeFi lending protocol, Aave, also froze its lending markets as precautionary measure, after the attacker borrowed Ethereum against stolen USDT.
Tether froze more than 1.567B USDT related to a potential Binance exchange hack.
Protecting the industry and our partners is our main priority.
Stay safe everyone.
— Paolo Ardoino 🤖 (@paoloardoino) October 29, 2026
Circle is closely tracking reports of a potential exploit involving Binance. In coordination with law enforcement, we have frozen more than 800M USDC associated with the incident and will continue supporting the investigation.
— Jeremy Allaire (@jerallaire) October 29, 2026
We’re aware of reports of a potential incident affecting Binance-affiliated wallets.
Aave’s contracts are unaffected, and positions remain overcollateralized. As a precaution, all DAO-operated markets across V3 and V4 have been frozen.
The freeze pauses new deposits and…
— Aave (@aave) October 29, 2026
Binance have also paused deposits and withdrawals as security checks are ongoing. Binance has also revoked authorization for the affected address and is working with law enforcement and blockchain intelligence firms to recover the funds. The exchange says its SAFU emergency fund and company reserves will cover every dollar of user losses, and an updated Proof of Reserves will follow after remediation.
Blockaid Traces the Drain Back to One Hot Wallet
Blockchain security firm Blockaid has published one of the most detailed onchain breakdowns of the attack so far. Its report centers on Binance 14, one of the exchange’s largest and busiest Ethereum hot wallets.
According to Blockaid, the attacker funded an operator address through Tornado Cash starting Oct. 28 and rehearsed the whole sequence on its own wallets with test runs of $2 to $6. At 20:20 UTC on Oct. 29, it sent a single transaction carrying 50 EIP-7702 authorizations signed with the Binance 14 key. The wallet was still processing withdrawals, so the attacker had no way of knowing which nonce would be live and signed a whole range instead. One matched. That handed control of the wallet to an unverified sweeper contract only the attacker could operate.
About three minutes later, the sweeper emptied Binance 14 of 167,464 ETH, 1.615 billion USDT and around 60 other tokens, worth roughly $2.5 billion at the time. The wallet was left holding 1 ETH. Within 12 minutes, 10 more Binance hot wallets on Ethereum, Arbitrum, Avalanche and Optimism sent funds to the same collection address. The delegation stayed active, so the attacker returned at 21:44 UTC and took another 200 million USDT in fresh deposits without a new signature.
Blockaid CEO Ido Ben-Natan said that the evidence points to compromised signing infrastructure, and he does not think a key was leaked. That fits with Binance’s account of a breached laptop and service container. Ben-Natan also drew parallels with the $1.5 billion Bybit hack of February 2025, which this incident now dwarfs several times over.
Onchain investigator ZachXBT suspects North Korea’s Lazarus Group, though neither Binance nor any authority has confirmed the attribution. Binance has asked users to rely only on its official channels for updates.
The smartest crypto minds already read our newsletter. Want in? Join them.
2
513
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
UniswapA16zSeekDeFiExemptionFromIllinoisCryptoTax
8,684 views
425 Discussing
UNISWAP & a16z PUSH BACK AGAINST CRYPTO TAX RULES — IS DeFi AT A TURNING POINT?
Crypto Pulse Hub
·3 Likes
·480 views
HKDollarStablecoinHKDAPToLaunchOnSolana
5,022 views
242 Discussing
$1.5BInLeveragedCryptoBetsLiquidated
19,764 views
197 Discussing