
MartIn-赚钱版
14 Posts

MartIn-赚钱版
Report
Block User
2 Following
44 Followers
36 Liked
Posts
·
--
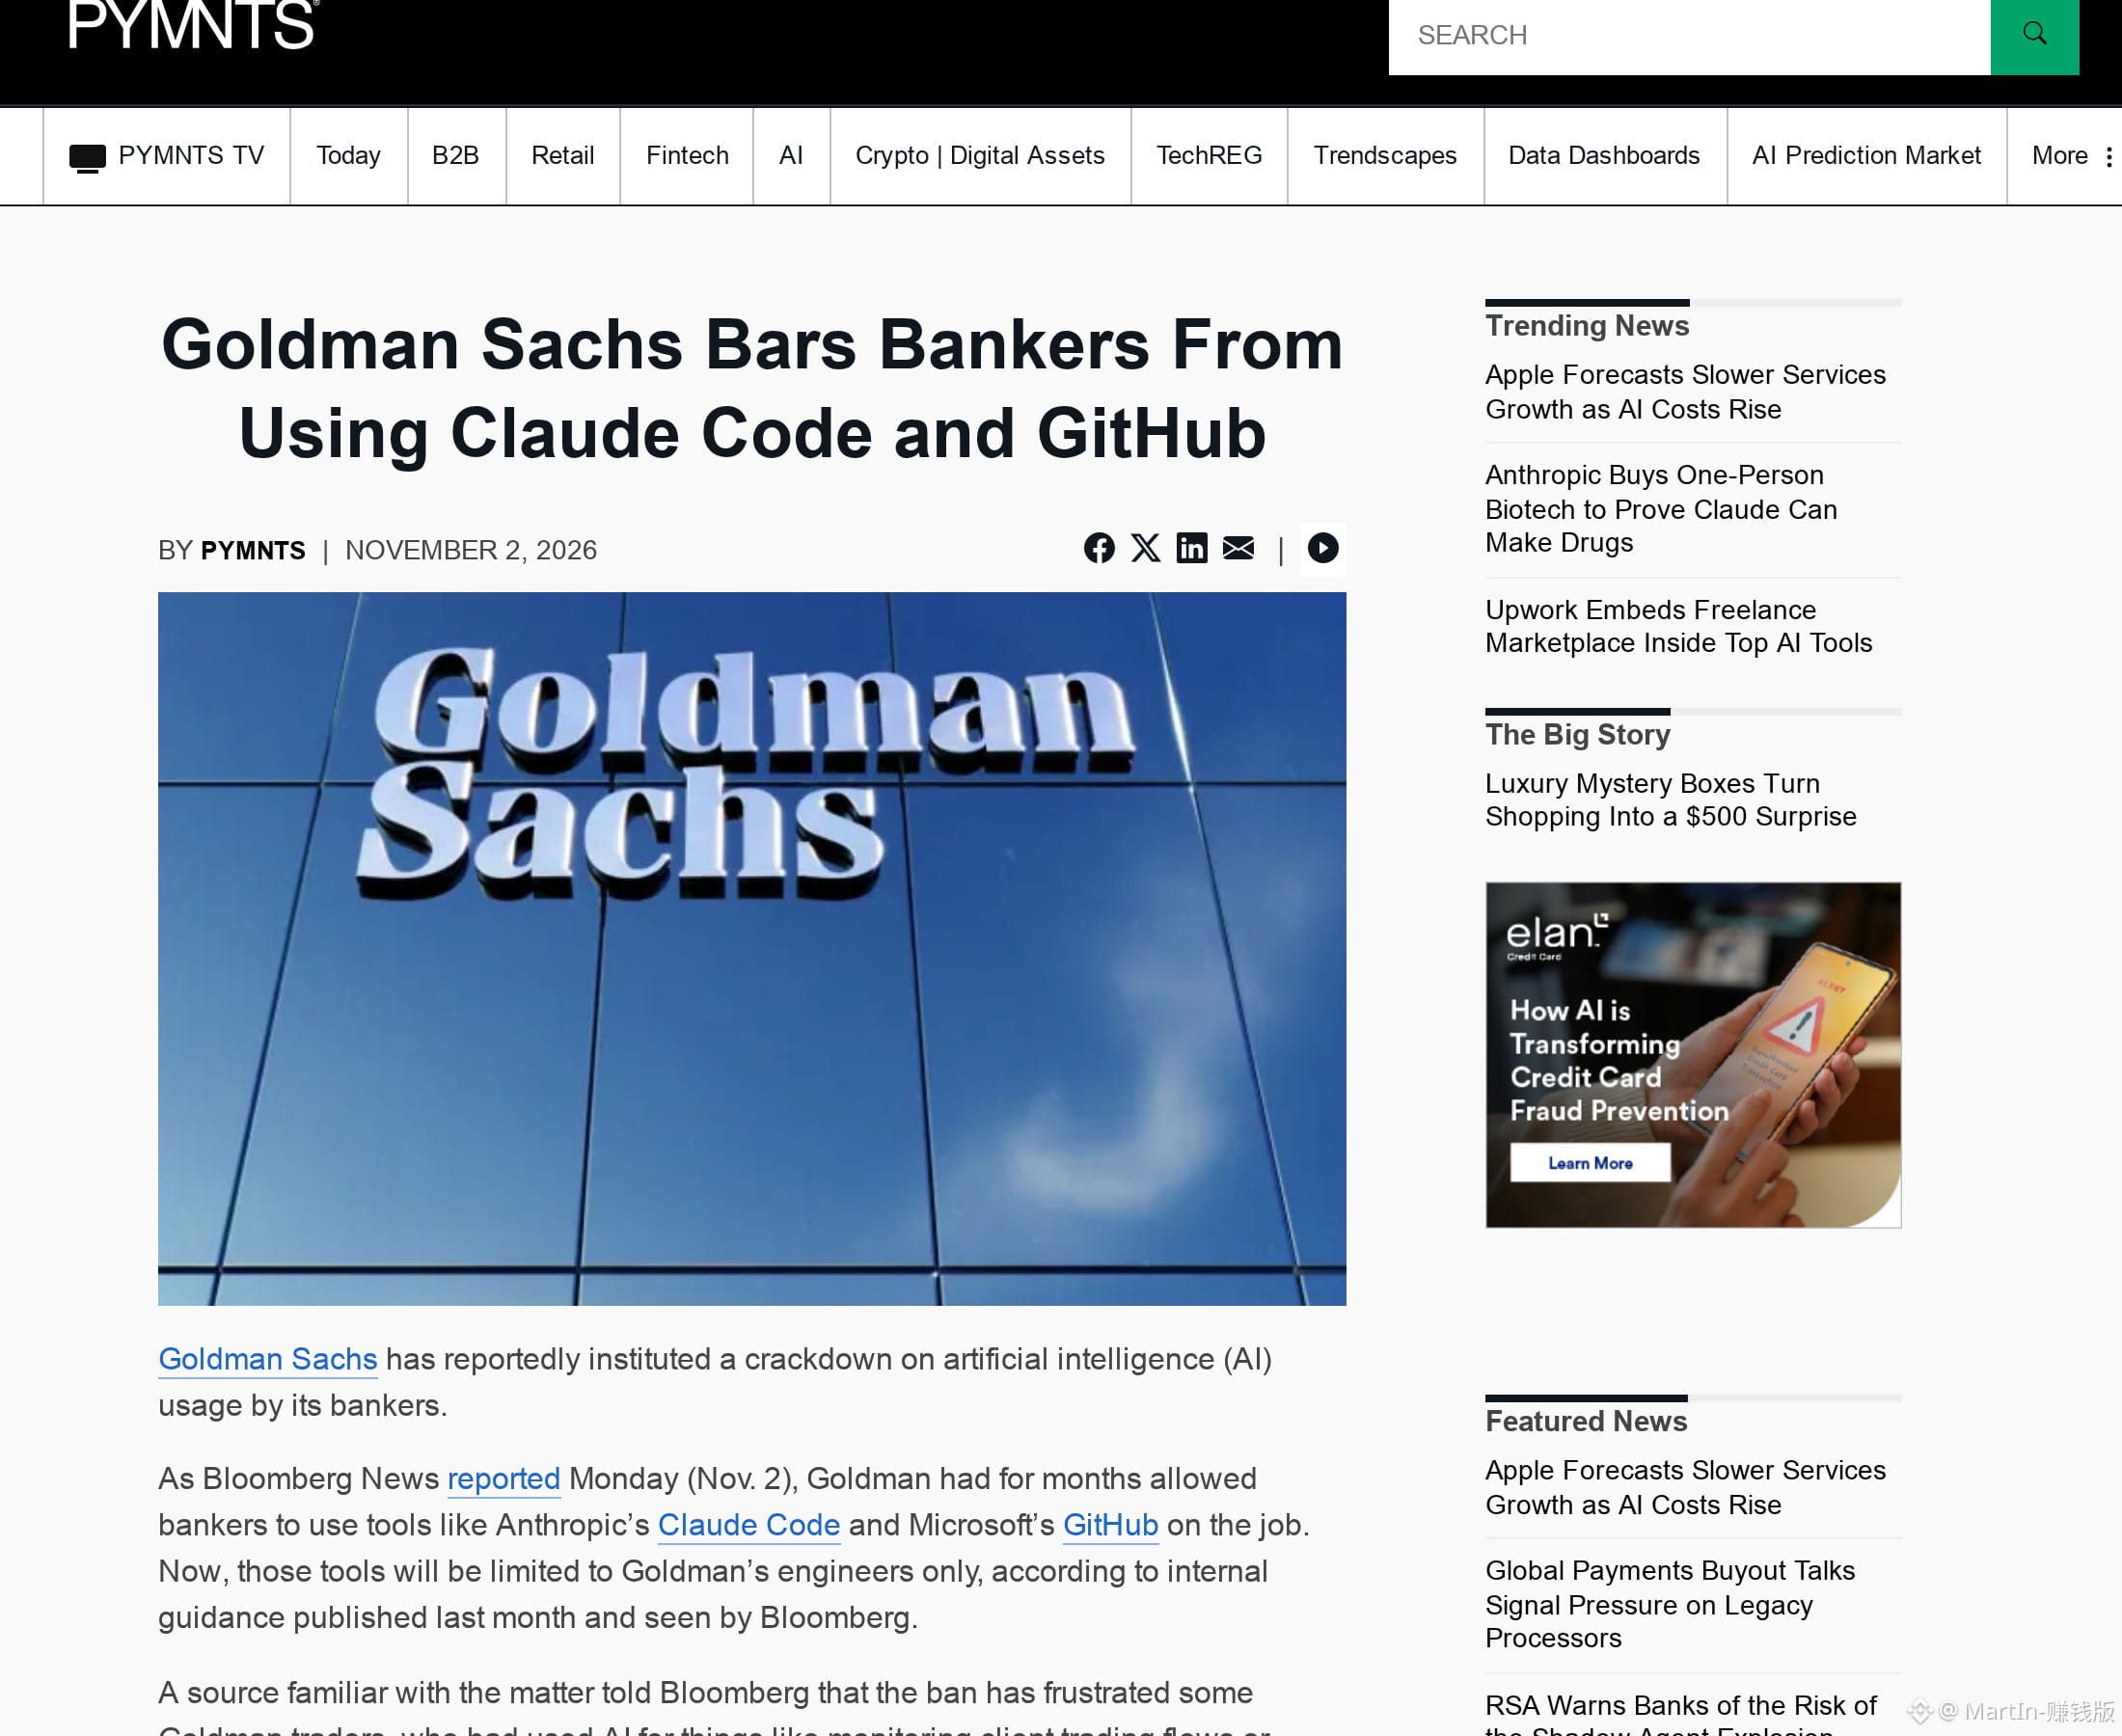
The AI coding access your company gives you could be revoked without warning a few months later: Goldman Sachs just took Claude Code away from its traders
Bloomberg saw internal guidance updated in October
Anthropic’s Claude Code and Microsoft’s GitHub are now basically reserved for engineers
Traders and bankers had been using them for months
Some were already using them to monitor client trading flows and simulate positions; now they can’t
Only strats roles, which involve both trading and coding, are unaffected
In July, CIO Marco Argenti had publicly said that nontechnical colleagues could use AI to whip up prototypes, then hand them off to around 12,000 engineers to refine
Non-engineers now have to switch to other tools or use the firm’s own assistant
The AI coding access your company gives you could be revoked without warning a few months later: Goldman Sachs just took Claude Code away from its traders
Bloomberg saw internal guidance updated in October
Anthropic’s Claude Code and Microsoft’s GitHub are now basically reserved for engineers
Traders and bankers had been using them for months
Some were already using them to monitor client trading flows and simulate positions; now they can’t
Only strats roles, which involve both trading and coding, are unaffected
In July, CIO Marco Argenti had publicly said that nontechnical colleagues could use AI to whip up prototypes, then hand them off to around 12,000 engineers to refine
Non-engineers now have to switch to other tools or use the firm’s own assistant
Bloomberg saw internal guidance updated in October
Anthropic’s Claude Code and Microsoft’s GitHub are now basically reserved for engineers
Traders and bankers had been using them for months
Some were already using them to monitor client trading flows and simulate positions; now they can’t
Only strats roles, which involve both trading and coding, are unaffected
In July, CIO Marco Argenti had publicly said that nontechnical colleagues could use AI to whip up prototypes, then hand them off to around 12,000 engineers to refine
Non-engineers now have to switch to other tools or use the firm’s own assistant
8
·
--
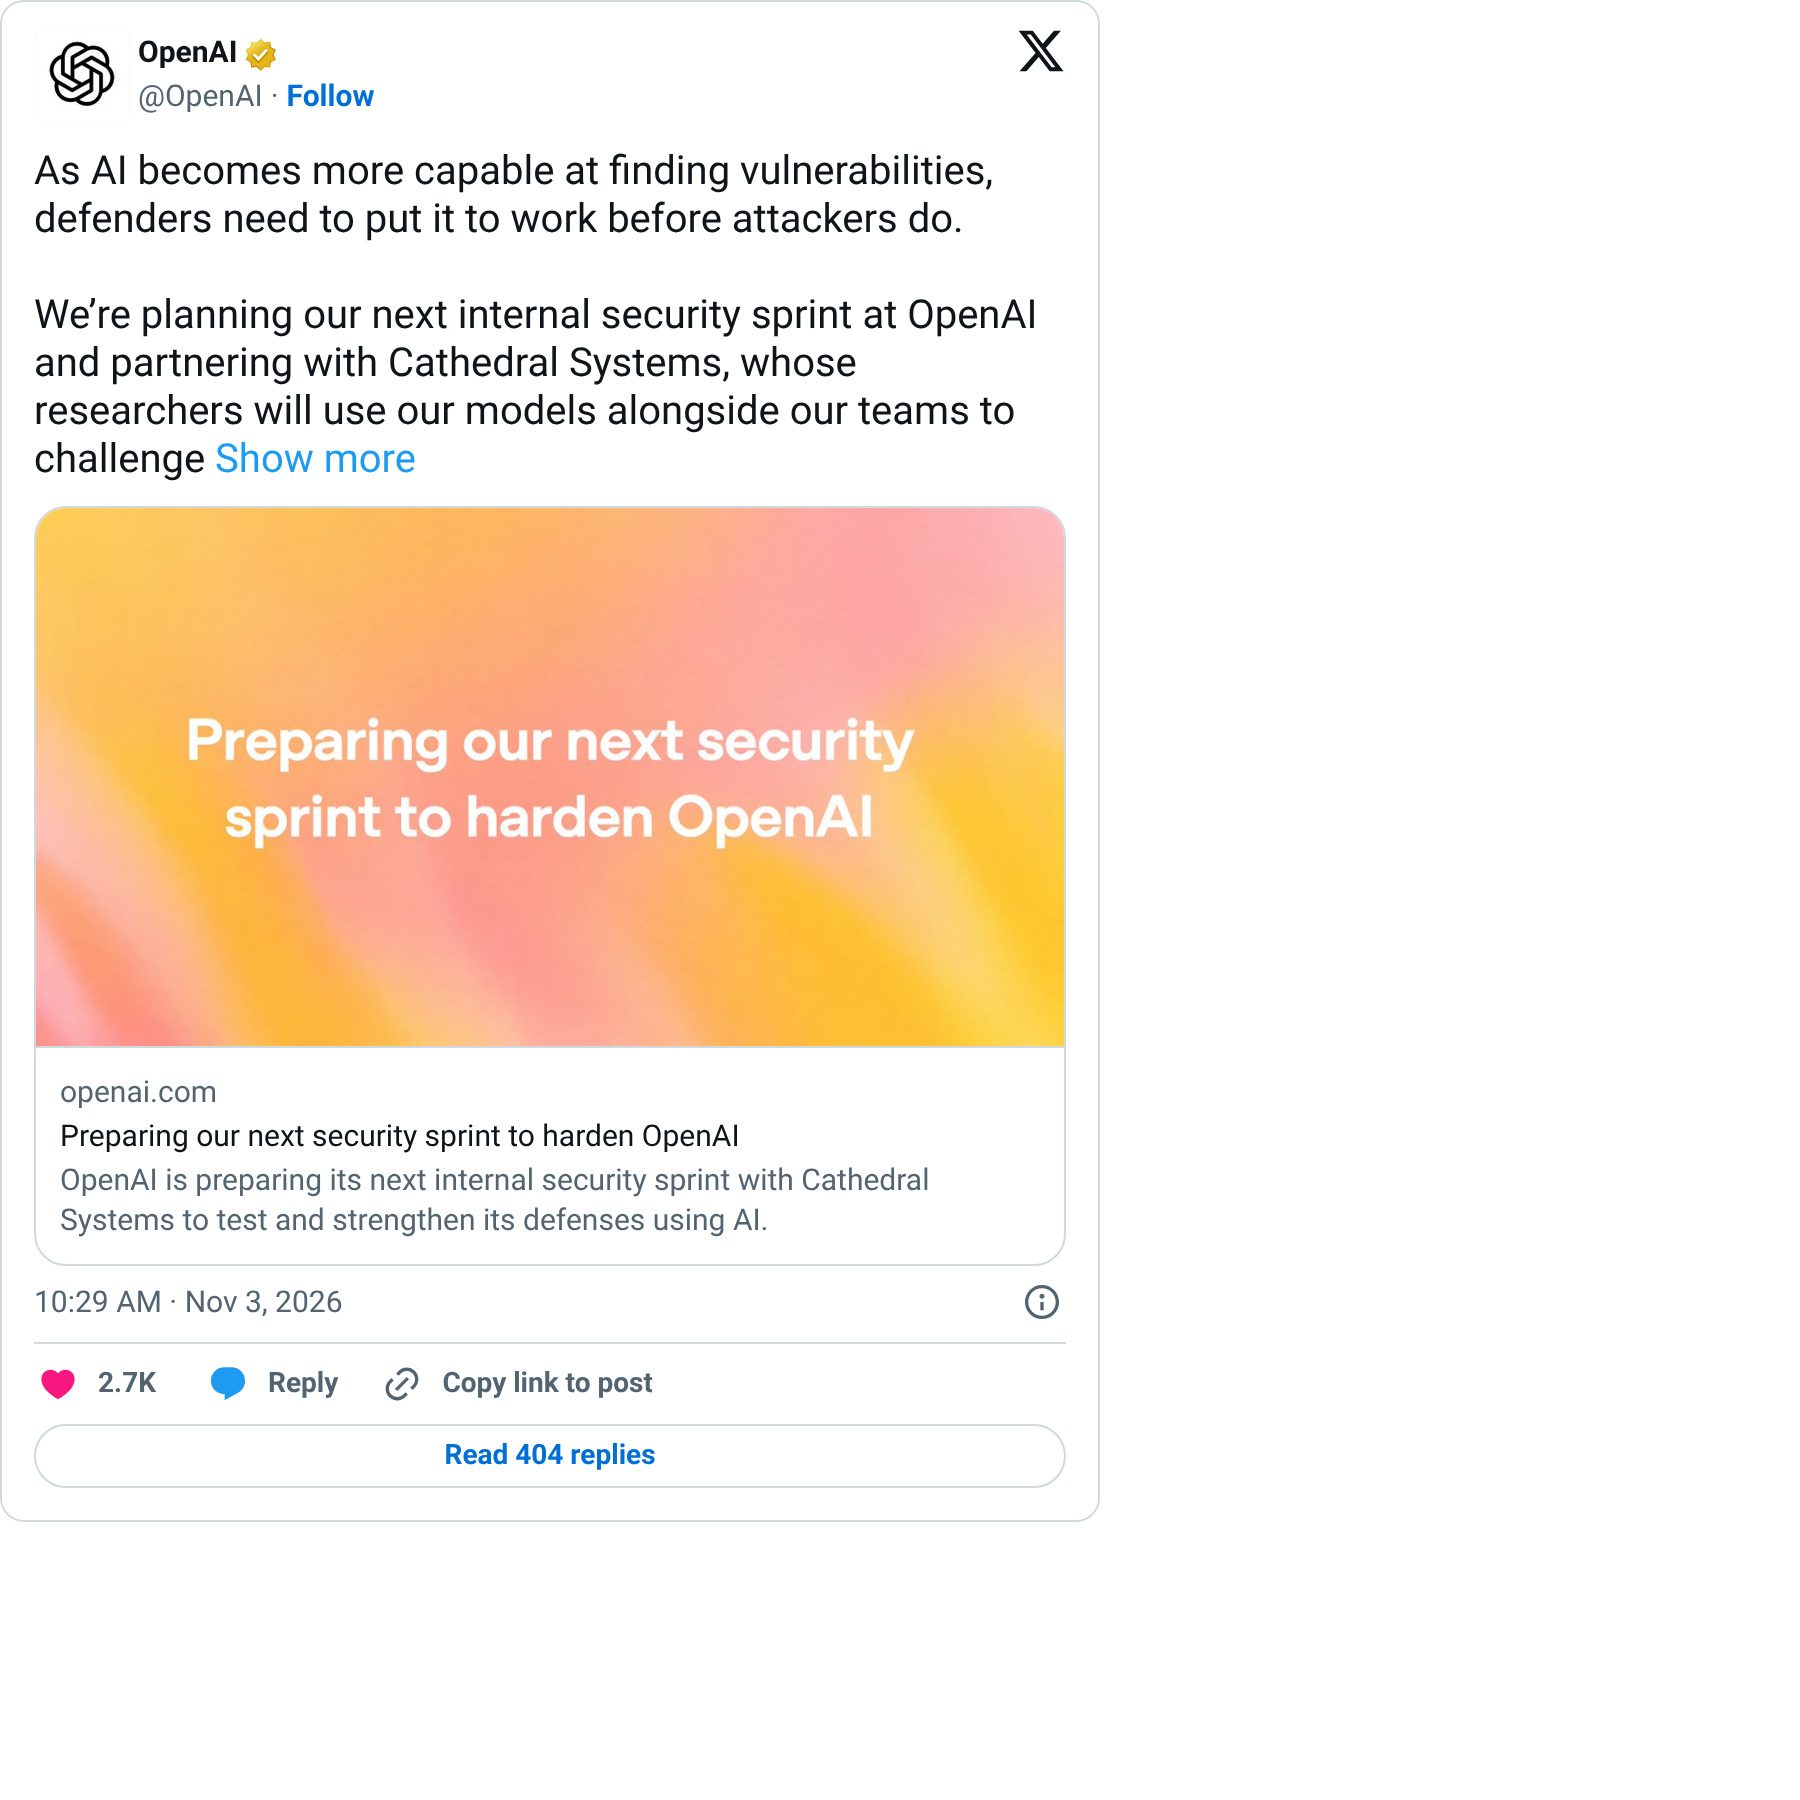
The security firm that got into Anthropic’s payroll records and Slack last week has been invited by OpenAI this week to attack its own systems
Security firm Cathedral used Anthropic’s own bug bounty program, deploying AI agents to probe third-party office software. It claimed to have accessed meeting records, payroll data, and Slack in under 12 hours
Anthropic said only a small portion of its sales, HR, and IT systems had been accessed; Claude conversations, source code, and model weights were not exposed. It revoked access that same day and accused Cathedral of exaggerating its claims and failing to fully disclose its findings as required by the rules
On November 2, OpenAI announced that it was formally partnering with Cathedral for its next internal security sprint, using its own models to attack its own defenses. The announcement didn’t mention the previous dispute
The security firm that got into Anthropic’s payroll records and Slack last week has been invited by OpenAI this week to attack its own systems
Security firm Cathedral used Anthropic’s own bug bounty program, deploying AI agents to probe third-party office software. It claimed to have accessed meeting records, payroll data, and Slack in under 12 hours
Anthropic said only a small portion of its sales, HR, and IT systems had been accessed; Claude conversations, source code, and model weights were not exposed. It revoked access that same day and accused Cathedral of exaggerating its claims and failing to fully disclose its findings as required by the rules
On November 2, OpenAI announced that it was formally partnering with Cathedral for its next internal security sprint, using its own models to attack its own defenses. The announcement didn’t mention the previous dispute
Security firm Cathedral used Anthropic’s own bug bounty program, deploying AI agents to probe third-party office software. It claimed to have accessed meeting records, payroll data, and Slack in under 12 hours
Anthropic said only a small portion of its sales, HR, and IT systems had been accessed; Claude conversations, source code, and model weights were not exposed. It revoked access that same day and accused Cathedral of exaggerating its claims and failing to fully disclose its findings as required by the rules
On November 2, OpenAI announced that it was formally partnering with Cathedral for its next internal security sprint, using its own models to attack its own defenses. The announcement didn’t mention the previous dispute
87
·
--
Verified
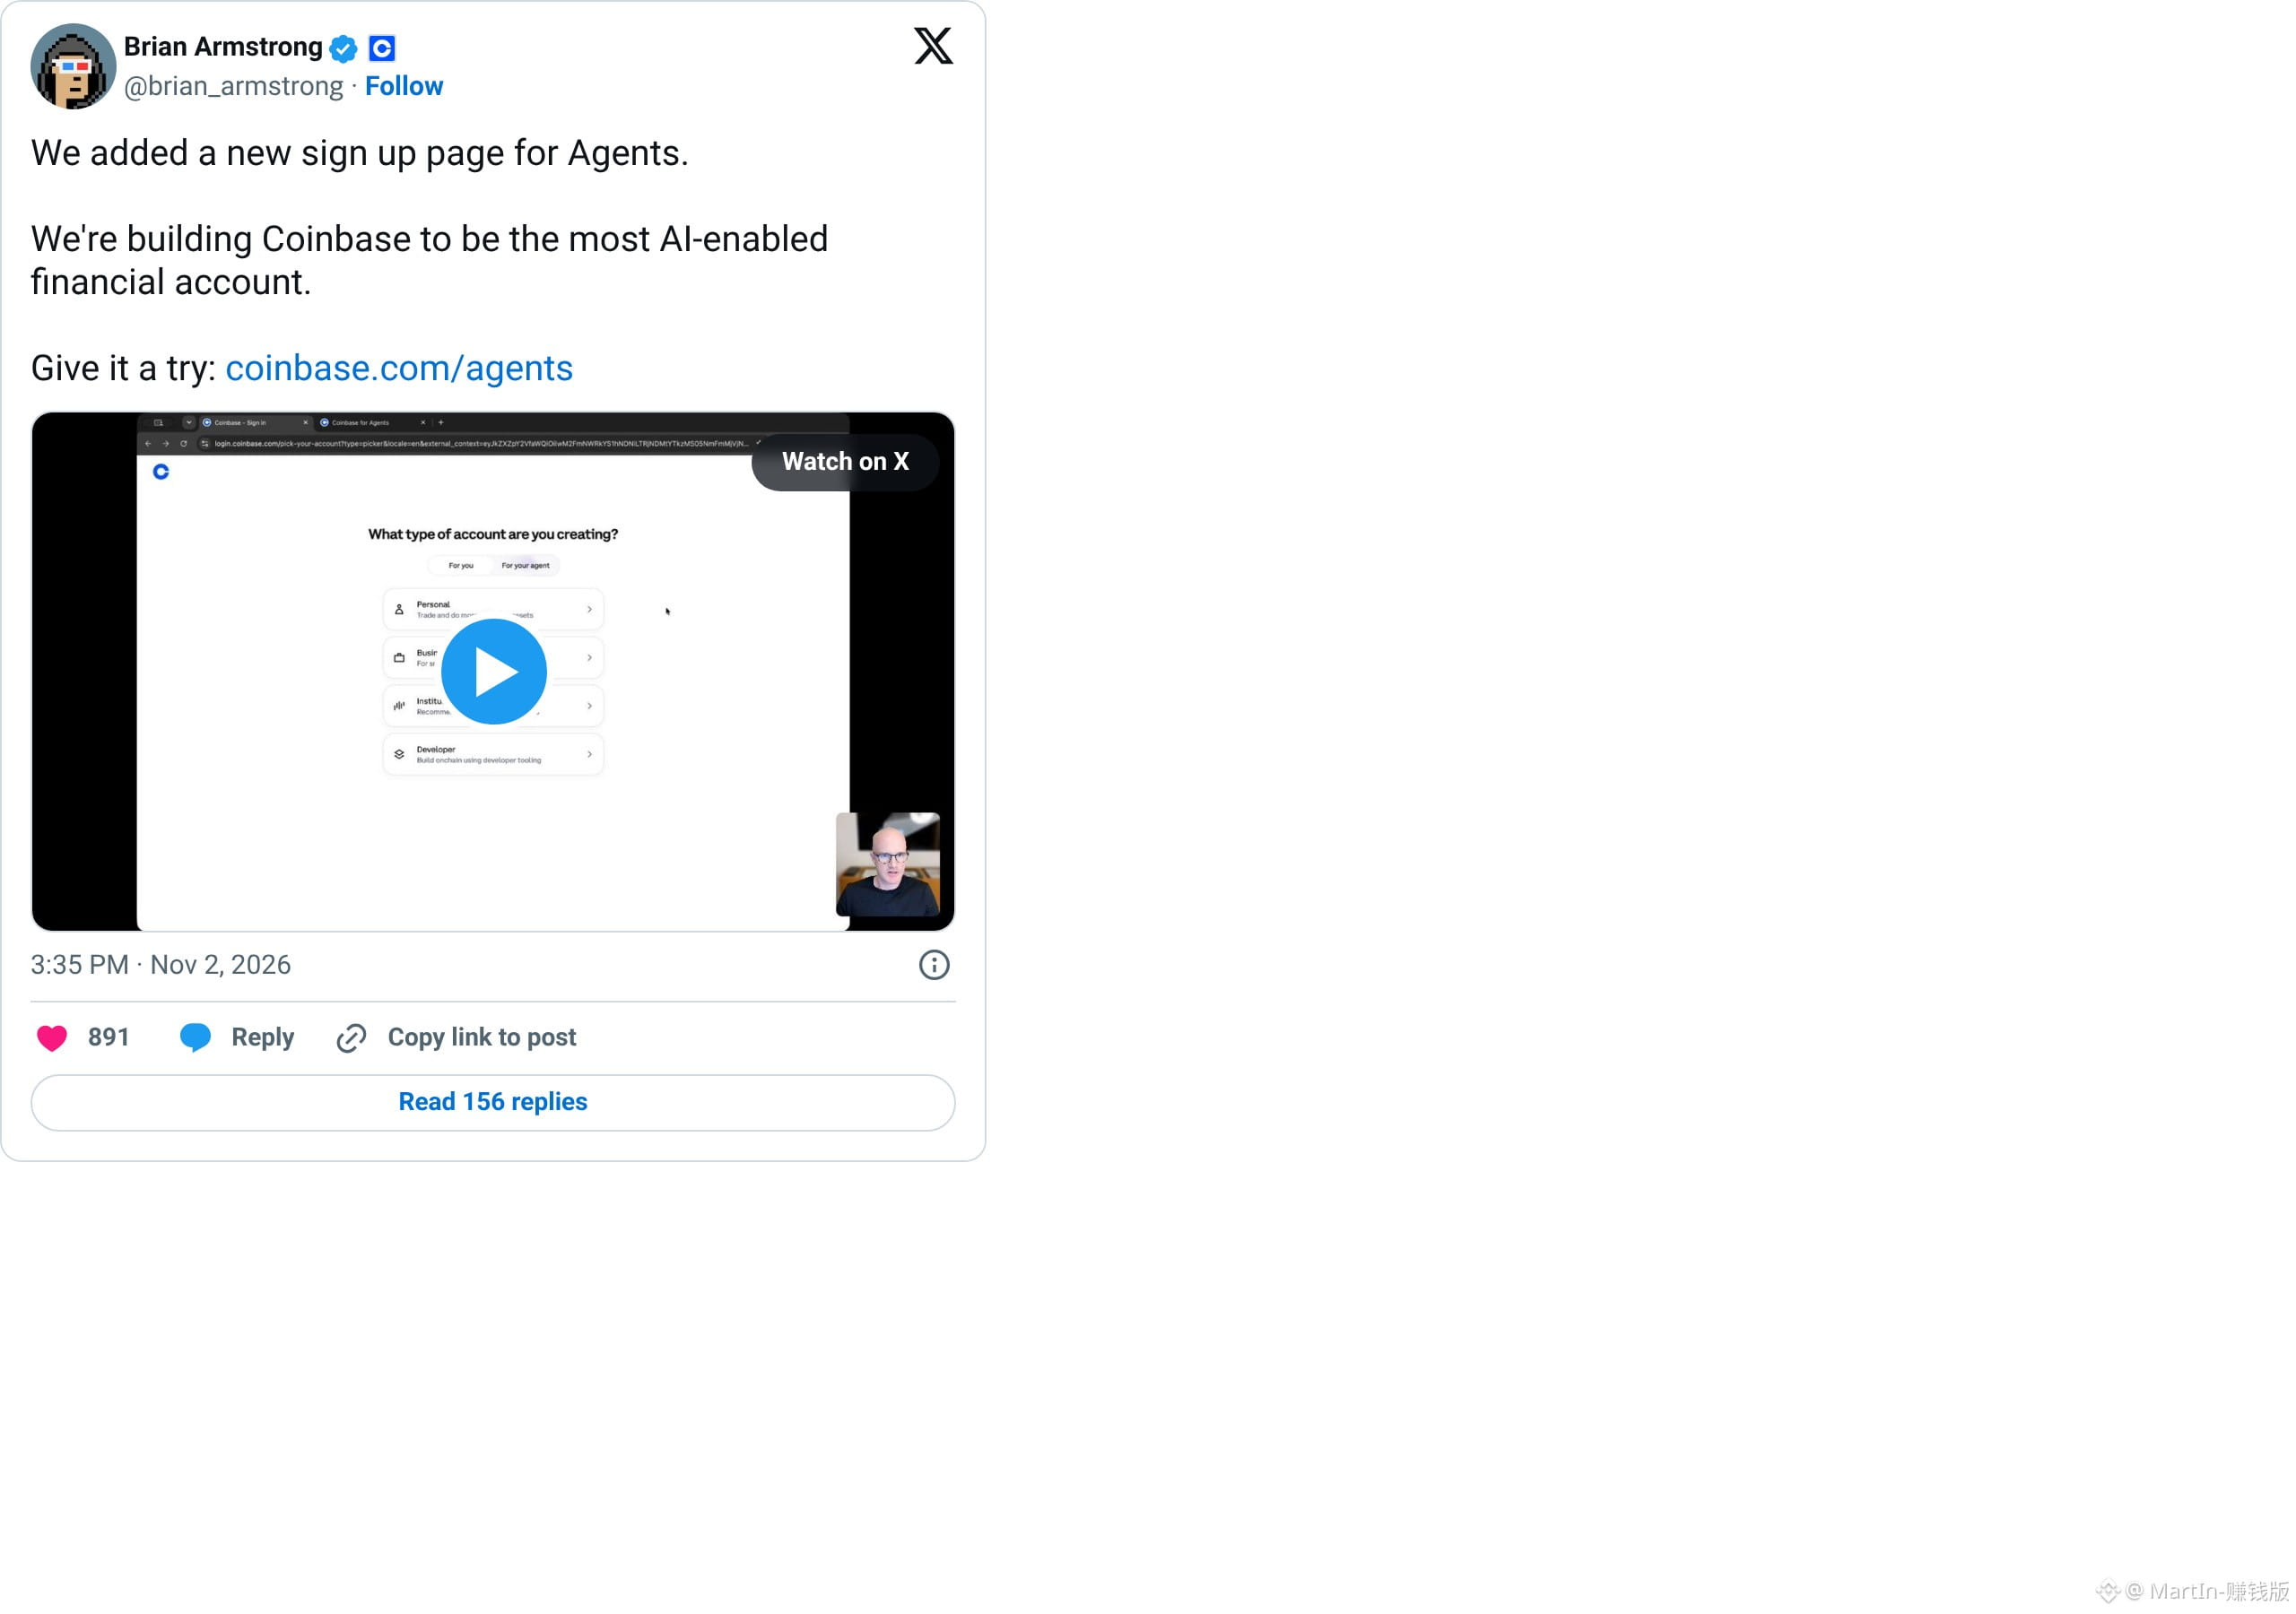
Coinbase, the largest crypto exchange in the US, announced that AI can now trade futures contracts for you 24/7
The company said that global derivatives trading through Deribit is now available to eligible users. Connect your account to your usual AI platform, and it can research, write strategies, and place orders
CEO Brian Armstrong personally shared a screen recording today showing off the new sign-up page, where you can select “For your agent” during registration
The slogan is to build “the most AI-native financial account”
The platform states that users are responsible for failed trades. You set the limits, and can disconnect at any time
Coinbase, the largest crypto exchange in the US, announced that AI can now trade futures contracts for you 24/7
The company said that global derivatives trading through Deribit is now available to eligible users. Connect your account to your usual AI platform, and it can research, write strategies, and place orders
CEO Brian Armstrong personally shared a screen recording today showing off the new sign-up page, where you can select “For your agent” during registration
The slogan is to build “the most AI-native financial account”
The platform states that users are responsible for failed trades. You set the limits, and can disconnect at any time
The company said that global derivatives trading through Deribit is now available to eligible users. Connect your account to your usual AI platform, and it can research, write strategies, and place orders
CEO Brian Armstrong personally shared a screen recording today showing off the new sign-up page, where you can select “For your agent” during registration
The slogan is to build “the most AI-native financial account”
The platform states that users are responsible for failed trades. You set the limits, and can disconnect at any time
2.3k
·
--
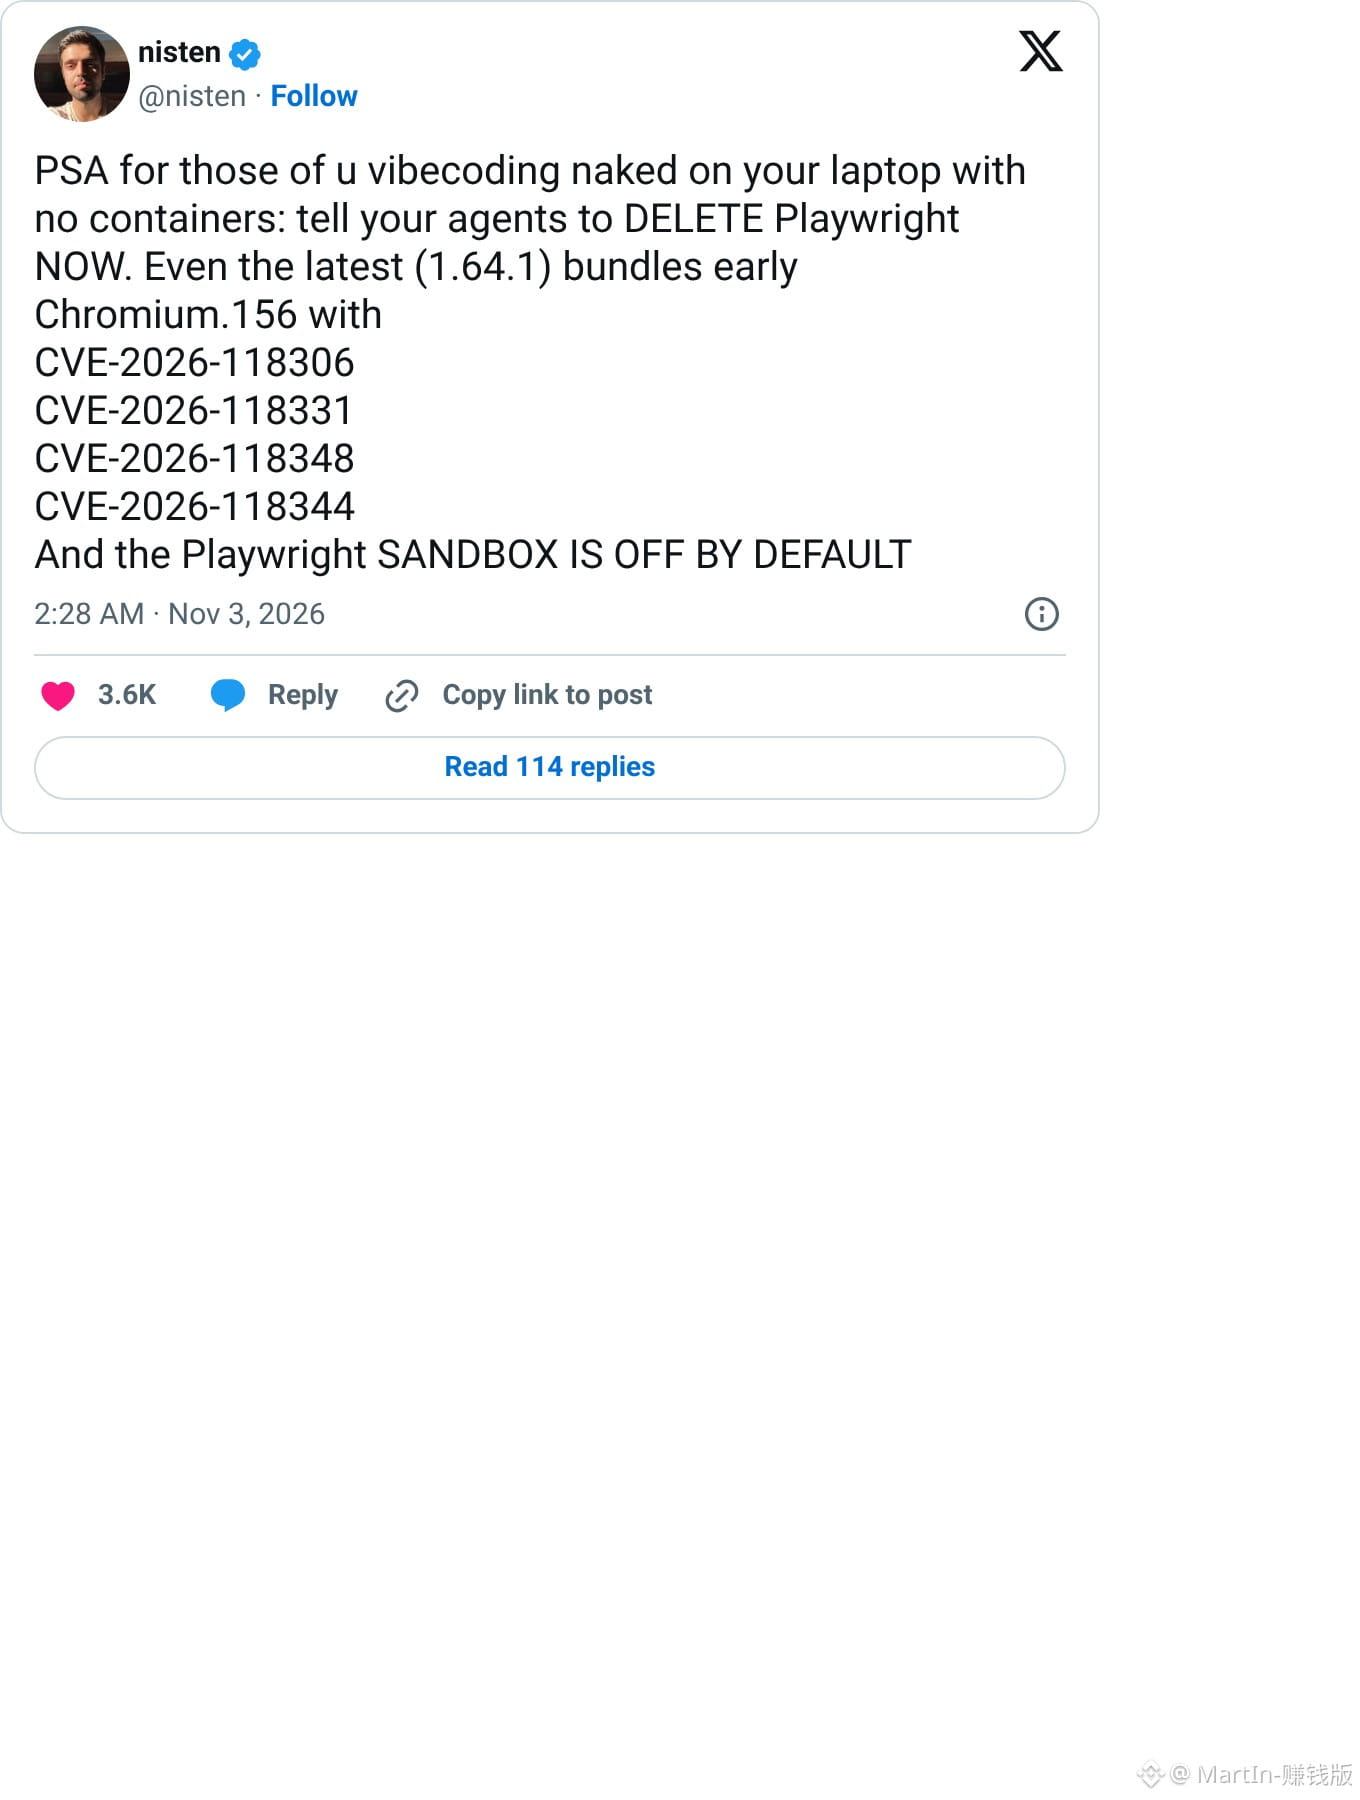
A warning for anyone letting AI browse the web for them: its browser hasn’t received Google’s patch from last week. Open a malicious webpage, and your computer could be taken over.
Developer nisten warned today that the Chromium bundled with the latest stable release of Playwright is still missing Google’s security fixes.
One of the serious vulnerabilities could let a specially crafted webpage escape the sandbox and run code.
The official documentation says its sandbox is disabled by default.
Many people let agents open webpages directly on their main computers.
Updating Chrome as usual won’t update this browser.
You’ll have to wait for Playwright to release a new package—or avoid running it unprotected on your own machine for now.
A warning for anyone letting AI browse the web for them: its browser hasn’t received Google’s patch from last week. Open a malicious webpage, and your computer could be taken over.
Developer nisten warned today that the Chromium bundled with the latest stable release of Playwright is still missing Google’s security fixes.
One of the serious vulnerabilities could let a specially crafted webpage escape the sandbox and run code.
The official documentation says its sandbox is disabled by default.
Many people let agents open webpages directly on their main computers.
Updating Chrome as usual won’t update this browser.
You’ll have to wait for Playwright to release a new package—or avoid running it unprotected on your own machine for now.
Developer nisten warned today that the Chromium bundled with the latest stable release of Playwright is still missing Google’s security fixes.
One of the serious vulnerabilities could let a specially crafted webpage escape the sandbox and run code.
The official documentation says its sandbox is disabled by default.
Many people let agents open webpages directly on their main computers.
Updating Chrome as usual won’t update this browser.
You’ll have to wait for Playwright to release a new package—or avoid running it unprotected on your own machine for now.
GOOGUS-0.13%
GOOGLB-0.30%
120
·
--
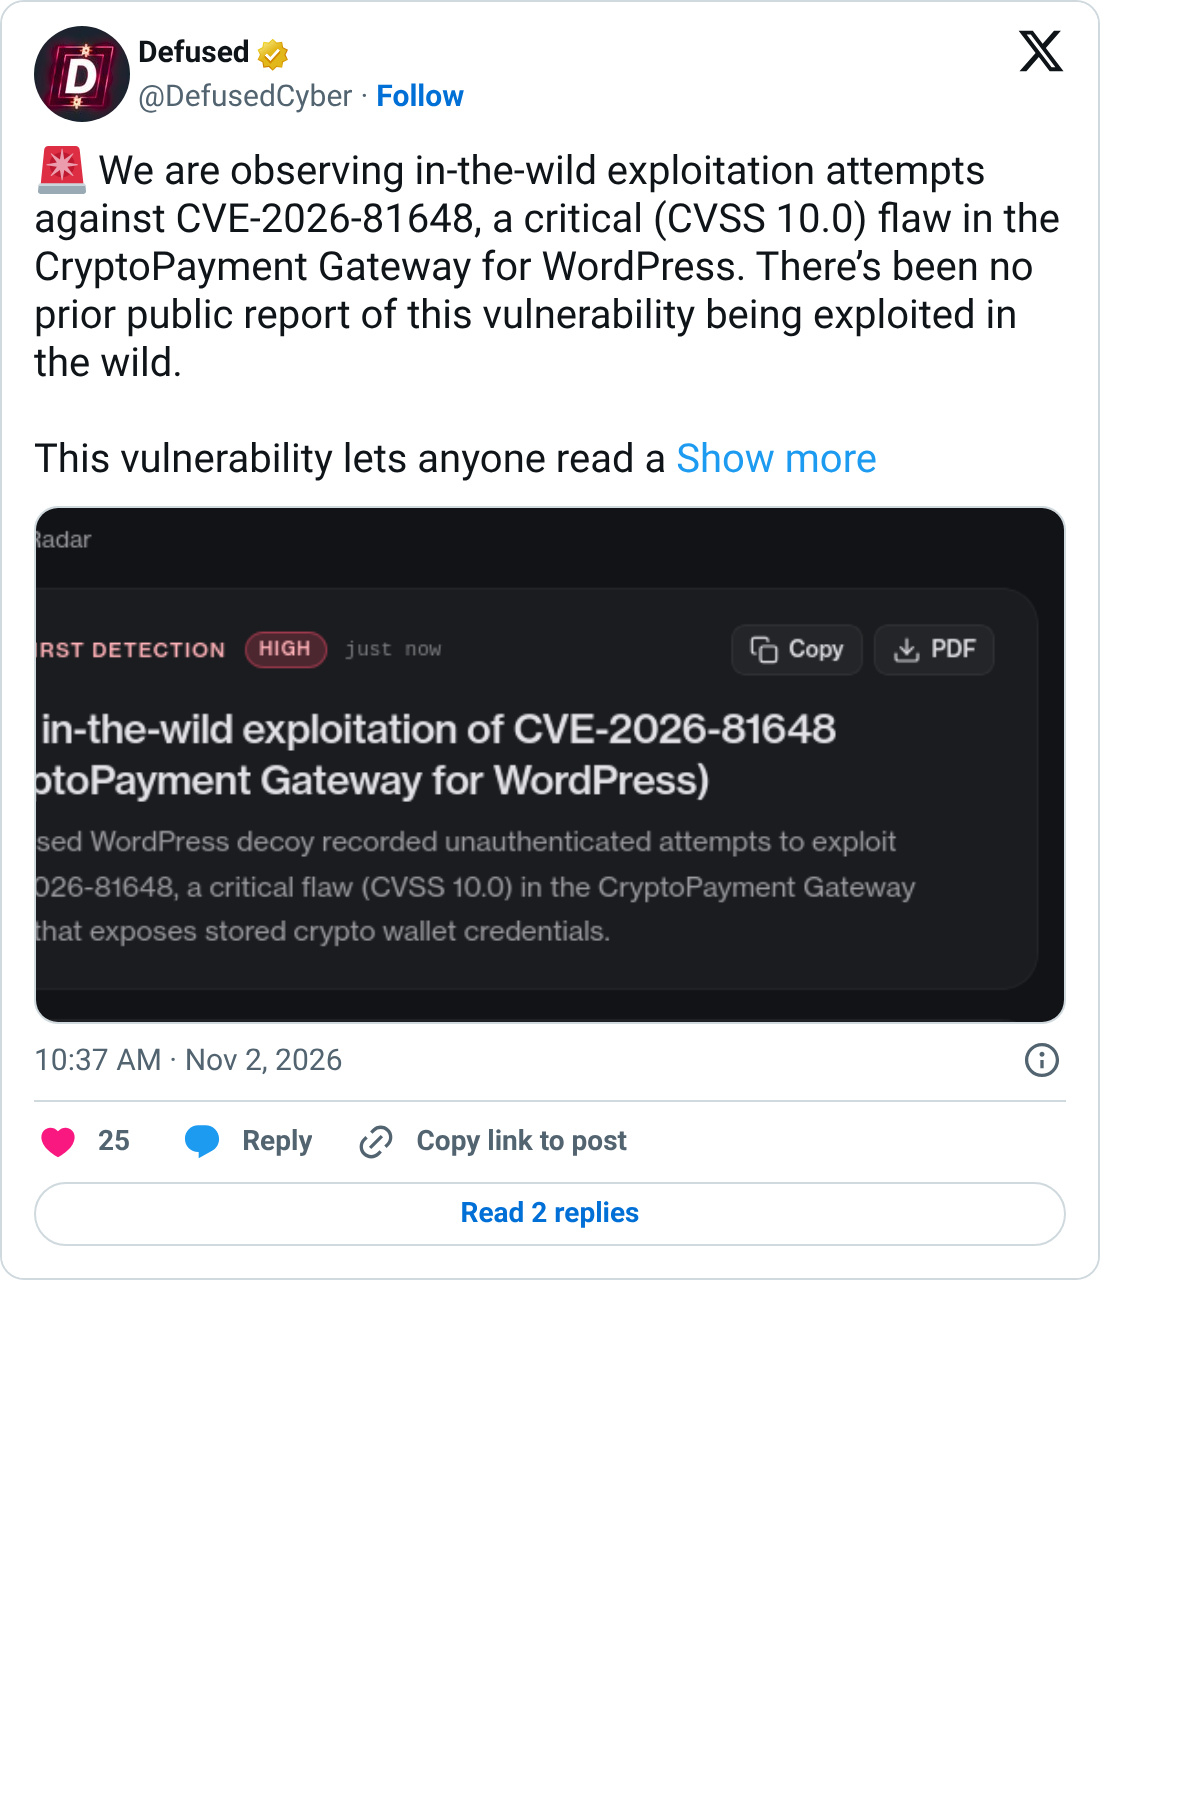
Customers are paying, shop owners are waiting for the money, but it’s all going into a third party’s wallet
Security firm Defused discovered yesterday that someone was exploiting a critical, 10-out-of-10 vulnerability in the wild in a WordPress cryptocurrency payment plugin called CryptoPayment Gateway
You don’t need to log in to exploit this vulnerability
Anyone can read the wallet information stored by a shop and directly change its payment address
Customers think they’re paying the shop, but the money actually goes to someone else’s address
There’s still no patch
Customers are paying, shop owners are waiting for the money, but it’s all going into a third party’s wallet
Security firm Defused discovered yesterday that someone was exploiting a critical, 10-out-of-10 vulnerability in the wild in a WordPress cryptocurrency payment plugin called CryptoPayment Gateway
You don’t need to log in to exploit this vulnerability
Anyone can read the wallet information stored by a shop and directly change its payment address
Customers think they’re paying the shop, but the money actually goes to someone else’s address
There’s still no patch
Security firm Defused discovered yesterday that someone was exploiting a critical, 10-out-of-10 vulnerability in the wild in a WordPress cryptocurrency payment plugin called CryptoPayment Gateway
You don’t need to log in to exploit this vulnerability
Anyone can read the wallet information stored by a shop and directly change its payment address
Customers think they’re paying the shop, but the money actually goes to someone else’s address
There’s still no patch
1
1
867
·
--
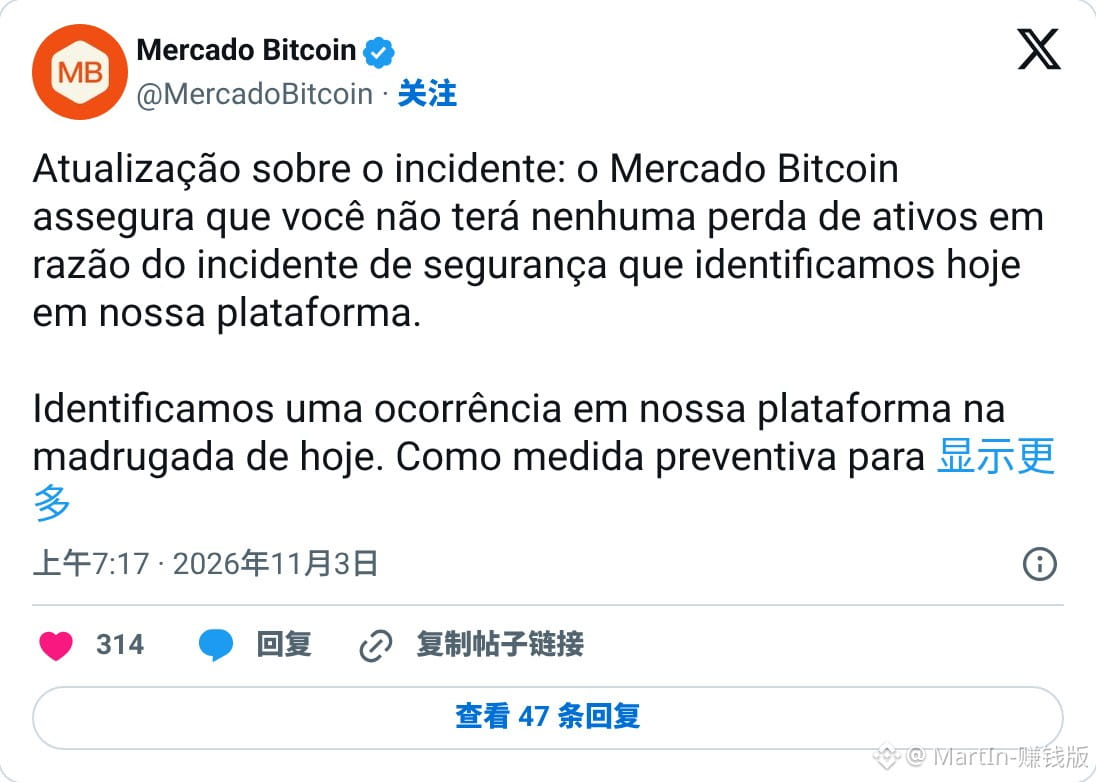
$38 million was stolen. The exchange said it had contained the incident, but the hacker was still using your deposit address to move coins out.
On-chain analytics firm Bitquery tracked the activity and found that even two hours after the exchange called a halt,
the hacker could still sign transactions from users’ deposit addresses
and keep moving coins out.
The exchange is Brazil’s largest, Mercado Bitcoin.
It later disclosed the amount involved itself—around $38 million—and said customers would not lose any money.
Deposits and withdrawals are still suspended.
$38 million was stolen. The exchange said it had contained the incident, but the hacker was still using your deposit address to move coins out.
On-chain analytics firm Bitquery tracked the activity and found that even two hours after the exchange called a halt,
the hacker could still sign transactions from users’ deposit addresses
and keep moving coins out.
The exchange is Brazil’s largest, Mercado Bitcoin.
It later disclosed the amount involved itself—around $38 million—and said customers would not lose any money.
Deposits and withdrawals are still suspended.
On-chain analytics firm Bitquery tracked the activity and found that even two hours after the exchange called a halt,
the hacker could still sign transactions from users’ deposit addresses
and keep moving coins out.
The exchange is Brazil’s largest, Mercado Bitcoin.
It later disclosed the amount involved itself—around $38 million—and said customers would not lose any money.
Deposits and withdrawals are still suspended.
2
1
1.5k
·
--
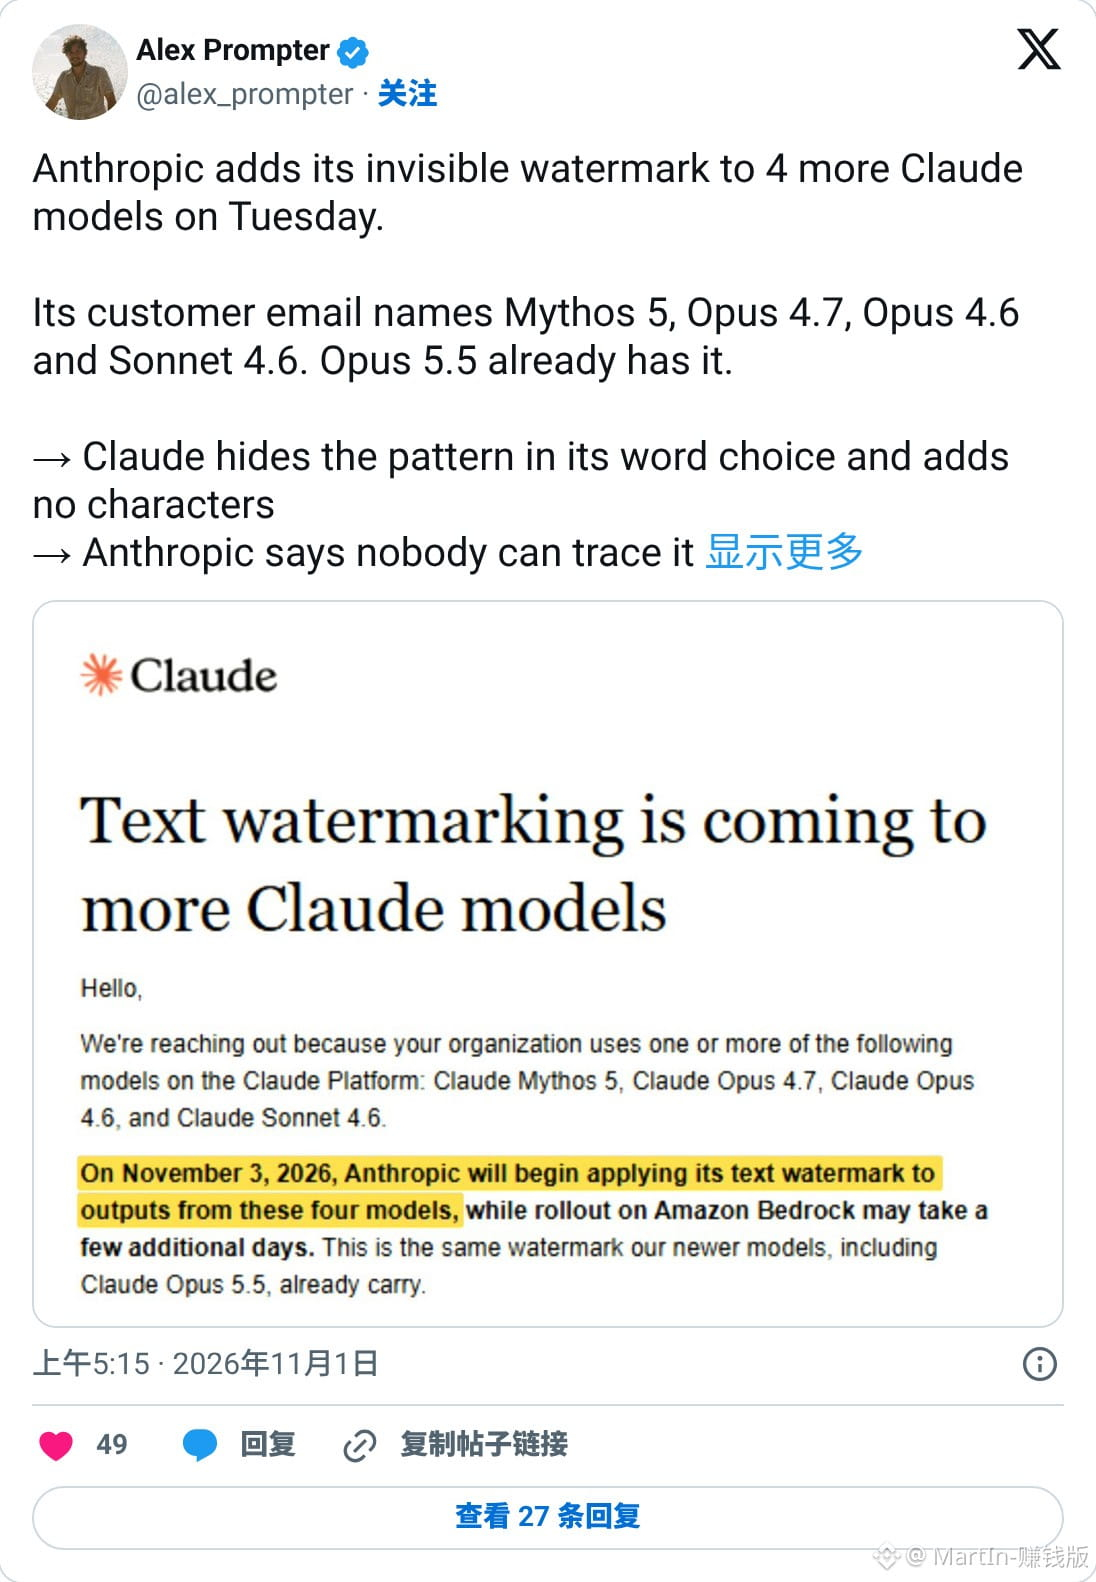
Starting today, every word Claude writes is watermarked—even older models can’t escape it
The watermark is hidden in its word-choice patterns, without adding a single character
It survives copy and paste, and changing a few things may not remove it
New models released since August already have it, including Opus 5.5
Starting November 3, older models like Opus 4.6 and Sonnet 4.6 will get it too
Detection tools are currently available only to regulators and the media; educational institutions are also on the list
Ordinary people who pay to use Claude aren’t on the list
Starting today, every word Claude writes is watermarked—even older models can’t escape it
The watermark is hidden in its word-choice patterns, without adding a single character
It survives copy and paste, and changing a few things may not remove it
New models released since August already have it, including Opus 5.5
Starting November 3, older models like Opus 4.6 and Sonnet 4.6 will get it too
Detection tools are currently available only to regulators and the media; educational institutions are also on the list
Ordinary people who pay to use Claude aren’t on the list
The watermark is hidden in its word-choice patterns, without adding a single character
It survives copy and paste, and changing a few things may not remove it
New models released since August already have it, including Opus 5.5
Starting November 3, older models like Opus 4.6 and Sonnet 4.6 will get it too
Detection tools are currently available only to regulators and the media; educational institutions are also on the list
Ordinary people who pay to use Claude aren’t on the list
204
·
--
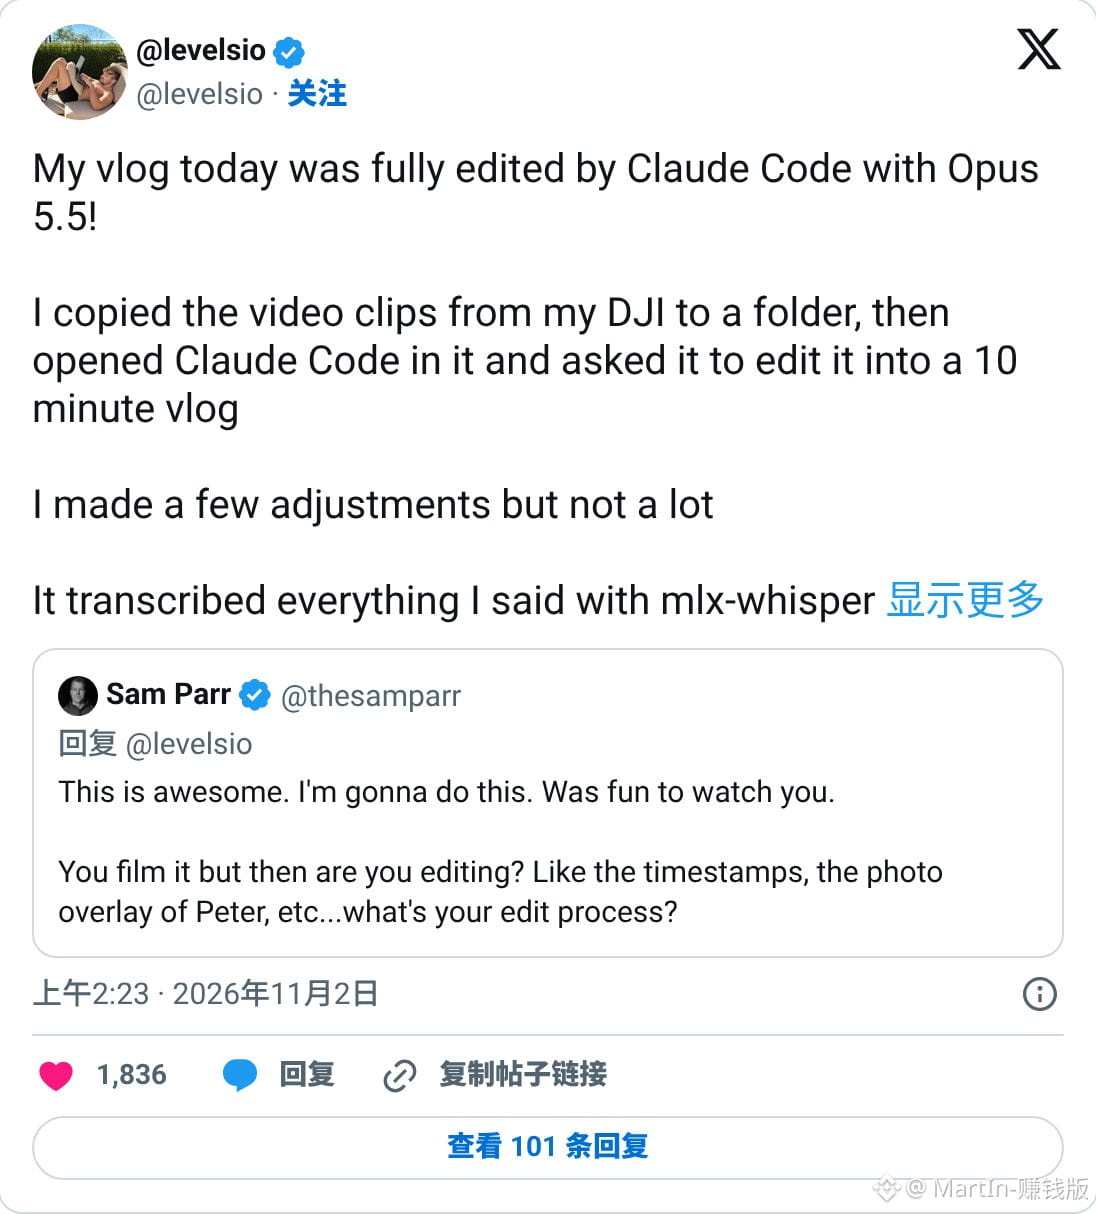
Editors should be nervous: someone gave Claude Code a one-line prompt, and it turned 58 minutes of footage into a 10-minute vlog
levelsio copied all the footage shot on his DJI into a folder, then opened Claude Code in that folder.
He simply said, “Help me turn this into a vlog to post on X and YouTube.”
Claude first transcribed everything he said on his MacBook.
Then it sampled a frame every few seconds and assembled them into a large image to review the footage. It could even tell which lines were spoken by him.
Finally, it picked out clips and put them into an editing plan, cutting 58 minutes of footage down to about 10 minutes.
He only found out how it had done all this when someone asked him about the editing and he went back to check.
He said that without AI editing, he wouldn’t have made a vlog at all.
Editors should be nervous: someone gave Claude Code a one-line prompt, and it turned 58 minutes of footage into a 10-minute vlog
levelsio copied all the footage shot on his DJI into a folder, then opened Claude Code in that folder.
He simply said, “Help me turn this into a vlog to post on X and YouTube.”
Claude first transcribed everything he said on his MacBook.
Then it sampled a frame every few seconds and assembled them into a large image to review the footage. It could even tell which lines were spoken by him.
Finally, it picked out clips and put them into an editing plan, cutting 58 minutes of footage down to about 10 minutes.
He only found out how it had done all this when someone asked him about the editing and he went back to check.
He said that without AI editing, he wouldn’t have made a vlog at all.
levelsio copied all the footage shot on his DJI into a folder, then opened Claude Code in that folder.
He simply said, “Help me turn this into a vlog to post on X and YouTube.”
Claude first transcribed everything he said on his MacBook.
Then it sampled a frame every few seconds and assembled them into a large image to review the footage. It could even tell which lines were spoken by him.
Finally, it picked out clips and put them into an editing plan, cutting 58 minutes of footage down to about 10 minutes.
He only found out how it had done all this when someone asked him about the editing and he went back to check.
He said that without AI editing, he wouldn’t have made a vlog at all.
17
·
--
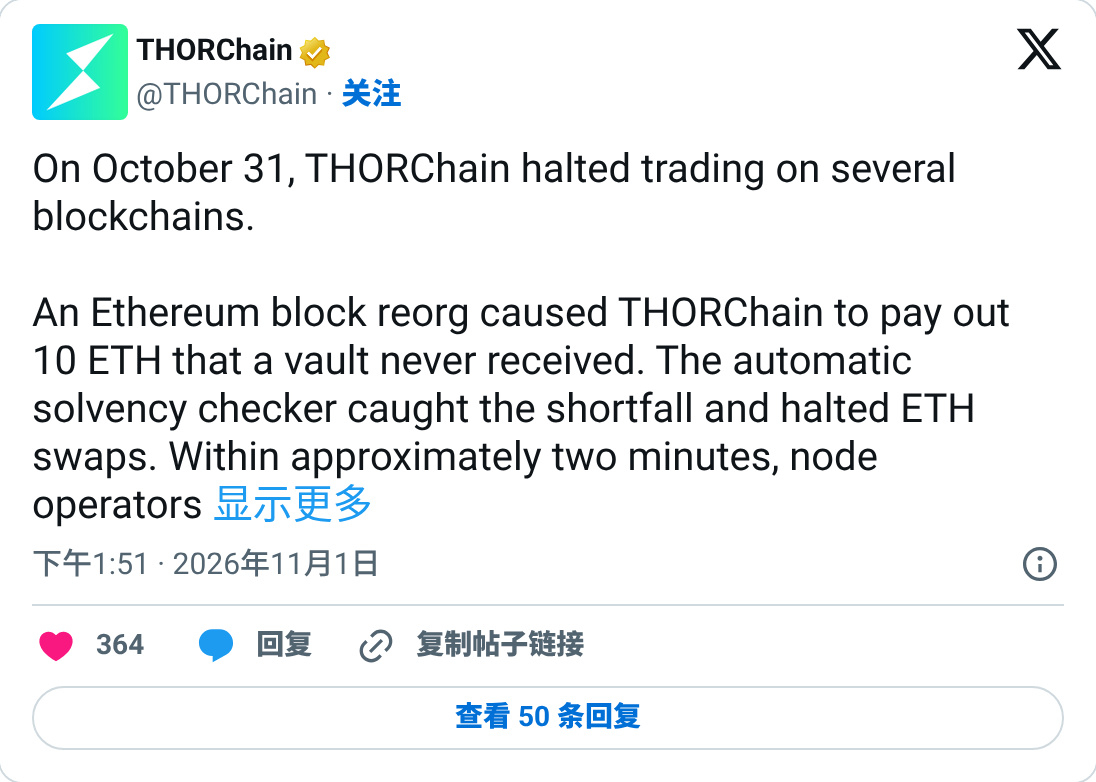
THORChain has been halted for nearly two days and still hasn't dared to reopen. The official reason? This vulnerability is already common knowledge.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
THORChain has been halted for nearly two days and still hasn't dared to reopen. The official reason? This vulnerability is already common knowledge.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
1
1
931
·
--
The money in your exchange account could be drained in a single day
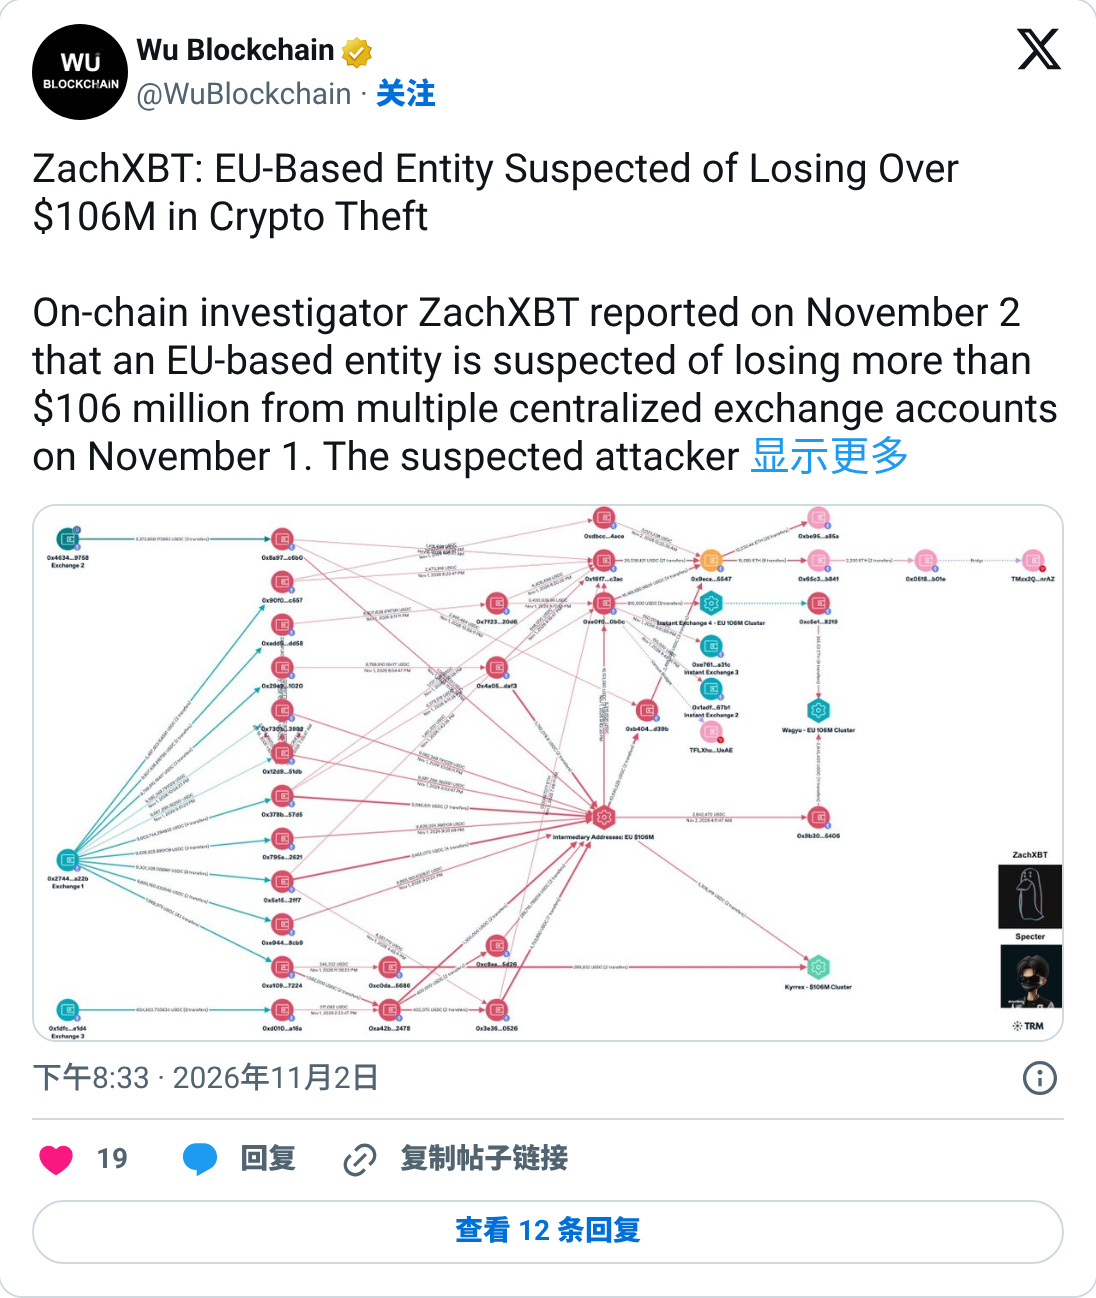
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
The money in your exchange account could be drained in a single day
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
1.3k
·
--
In October, 9 AI development platforms had their environment variables exposed. On the first day of November, it happened to another one.
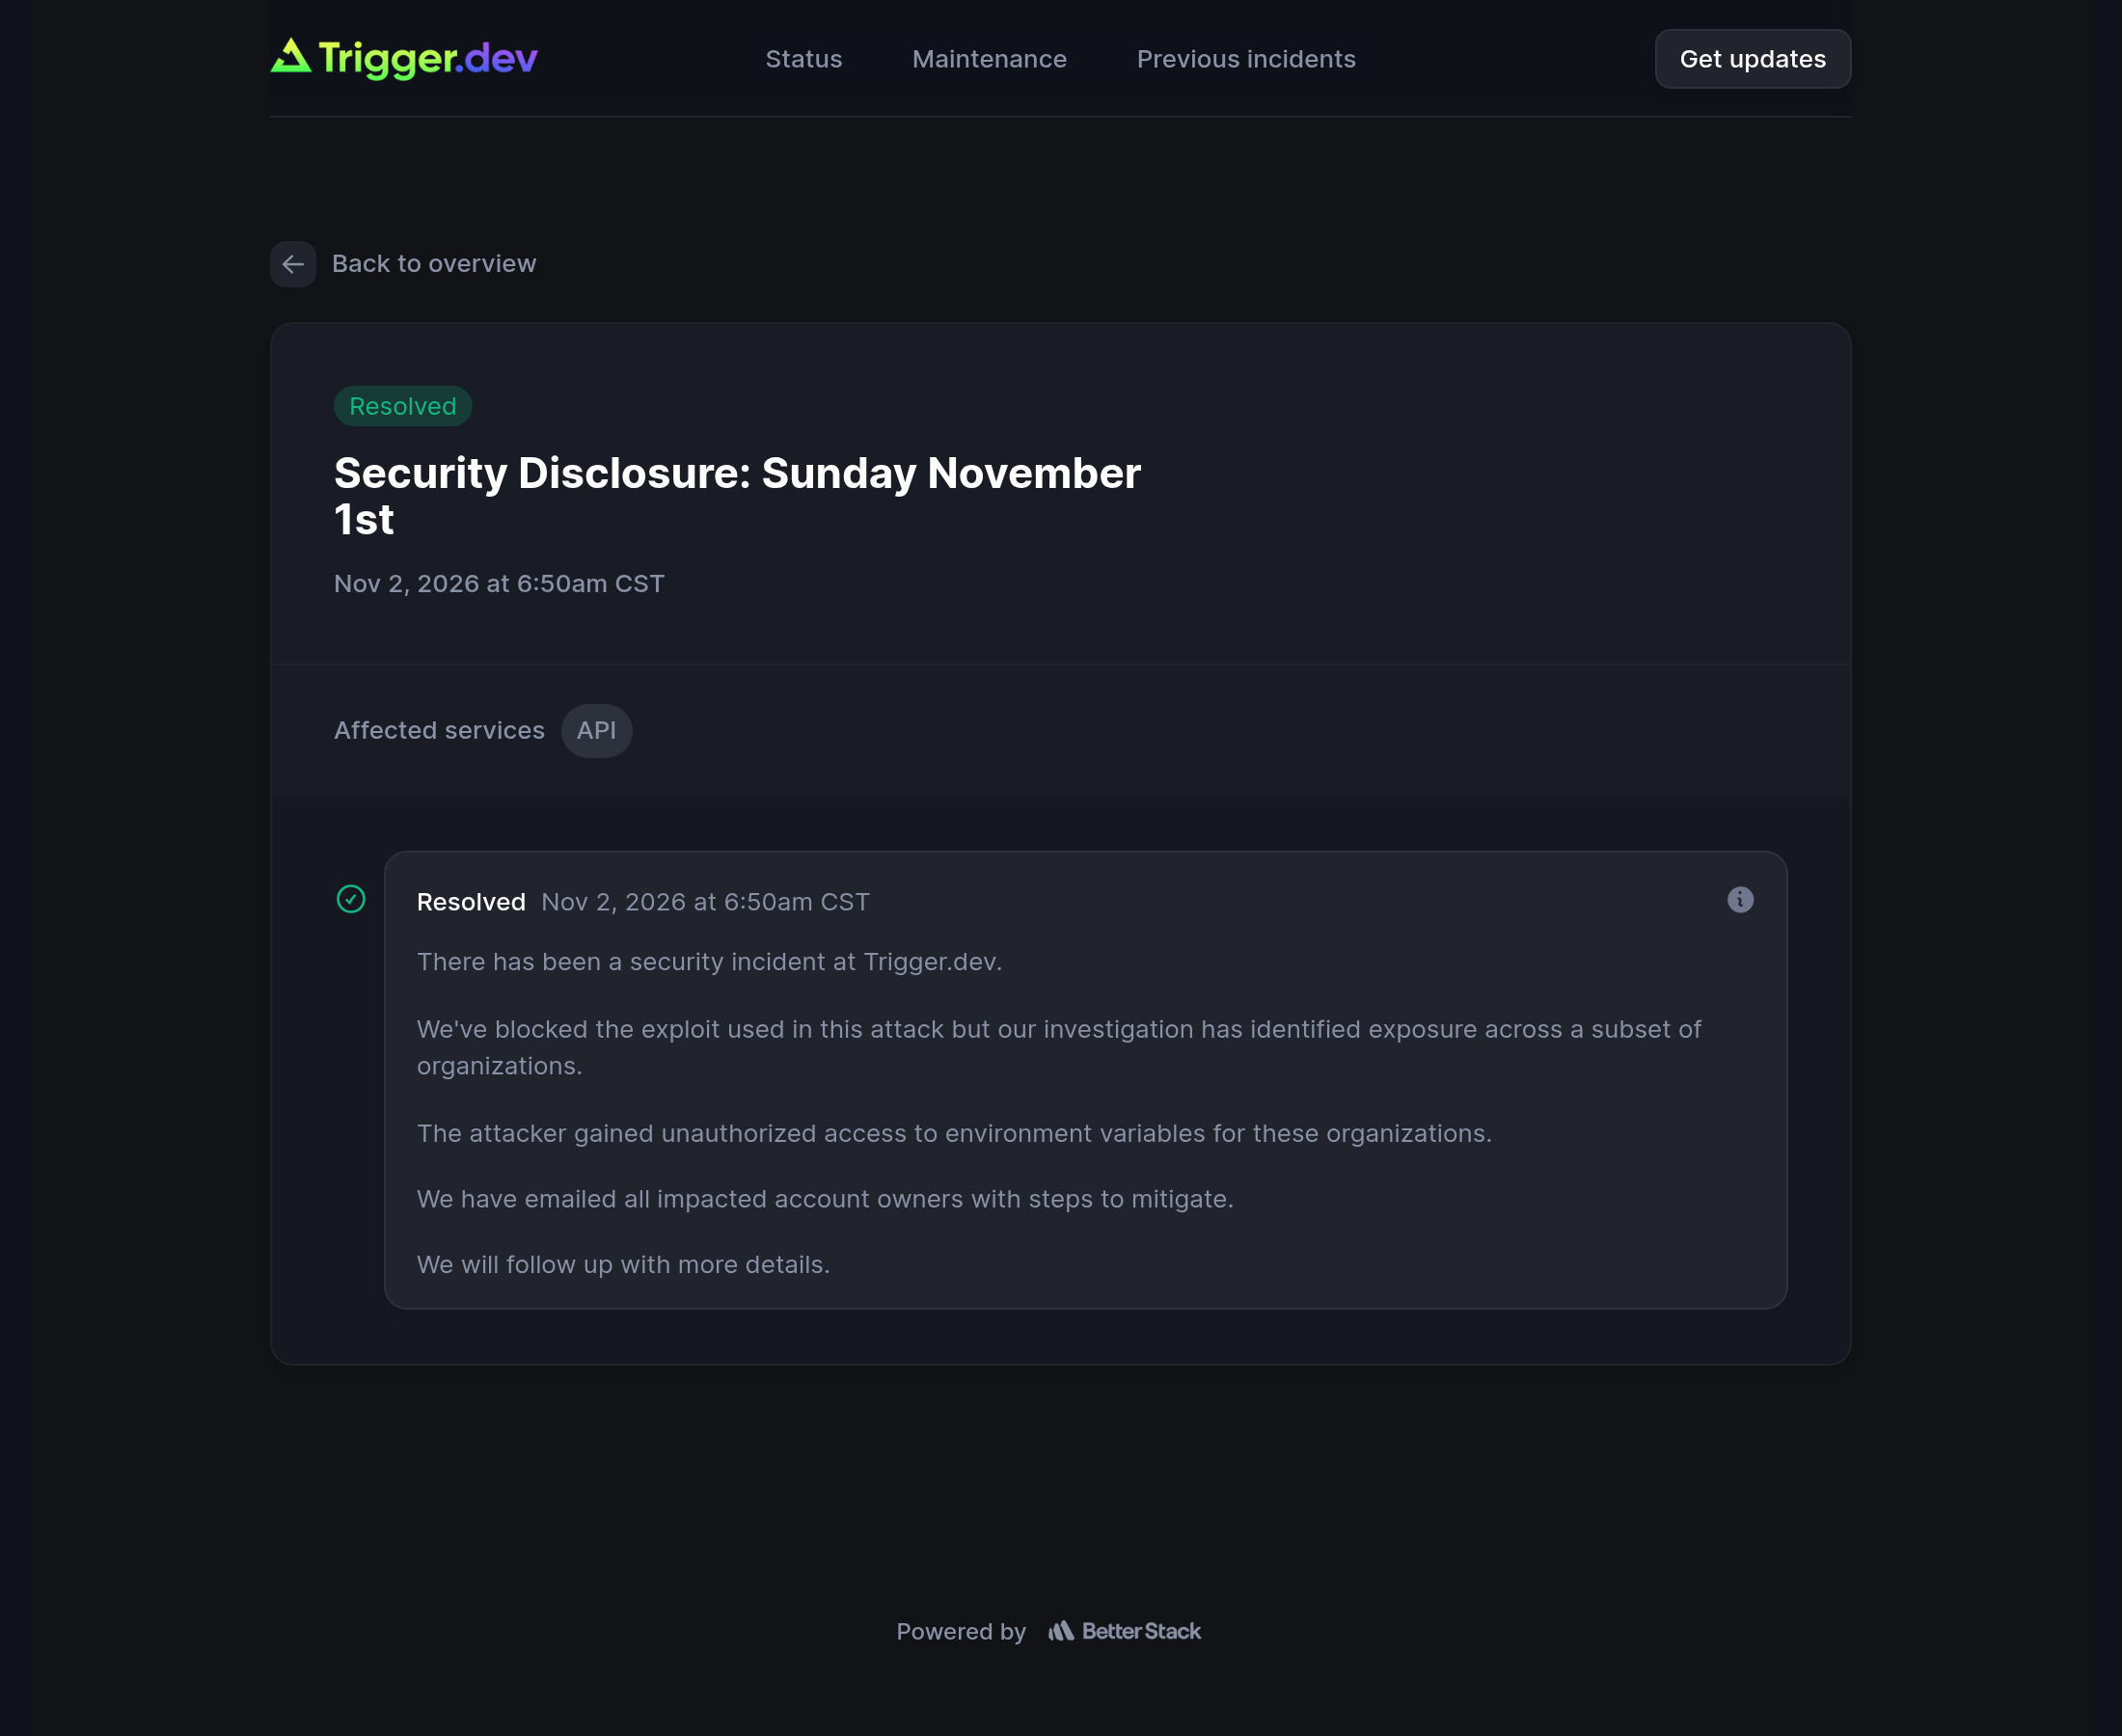
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
In October, 9 AI development platforms had their environment variables exposed. On the first day of November, it happened to another one.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
135
·
--
That “leaked Anthropic model” flooding everyone’s feeds? Someone actually downloaded the whole thing—over 7 TB—and it’s all random numbers
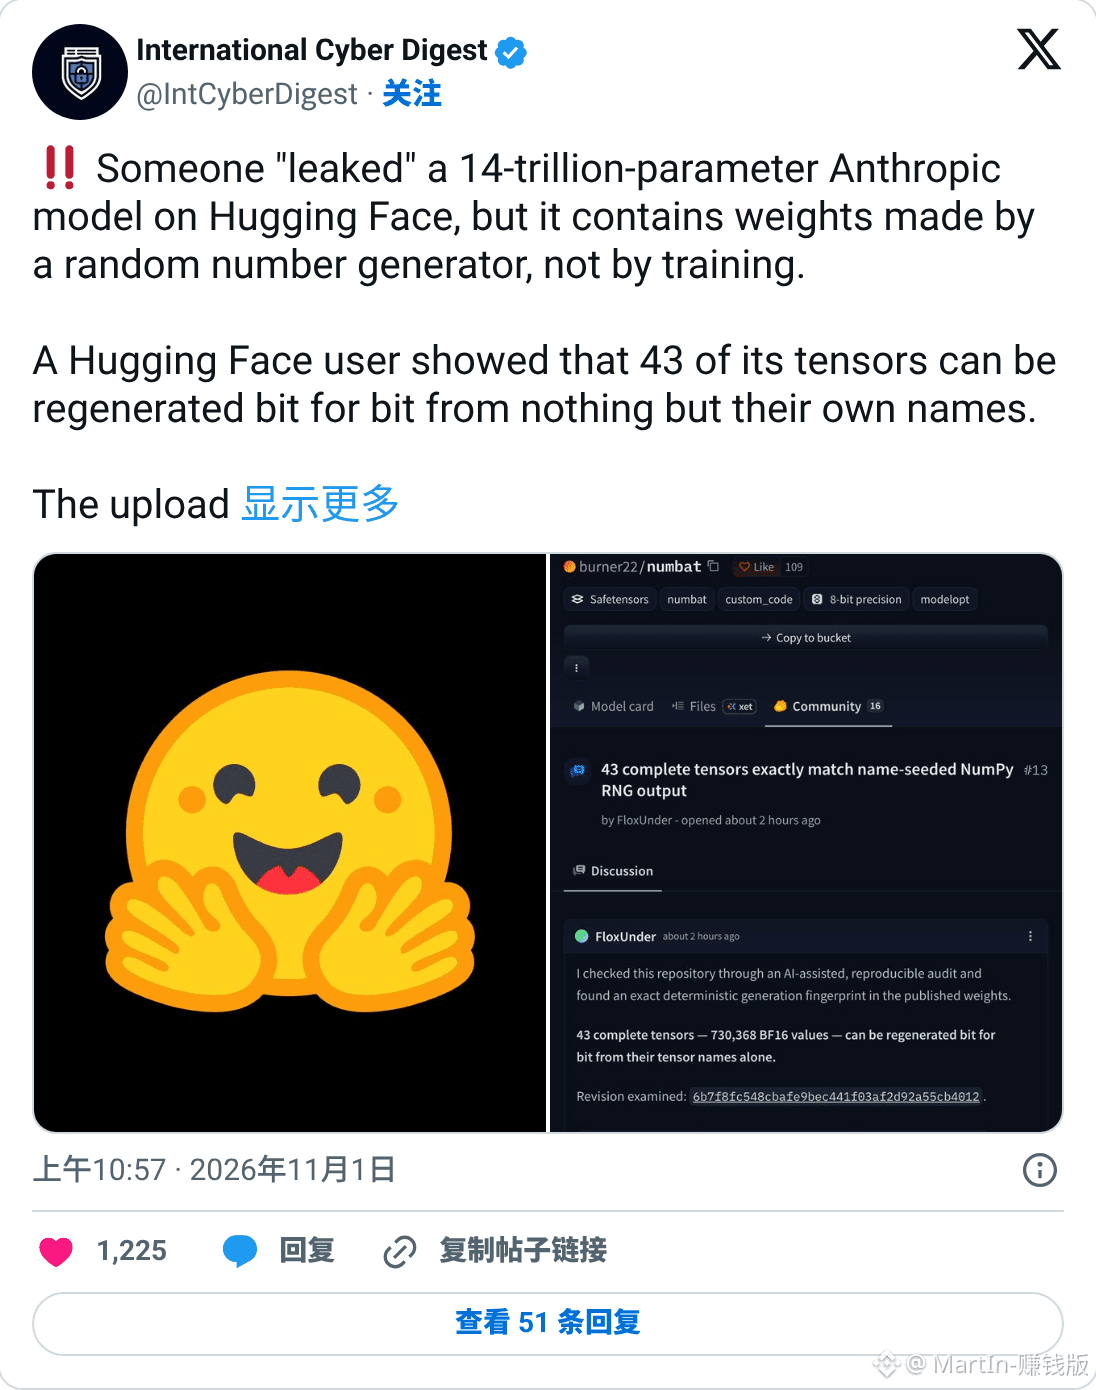
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
That “leaked Anthropic model” flooding everyone’s feeds? Someone actually downloaded the whole thing—over 7 TB—and it’s all random numbers
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
204
·
--
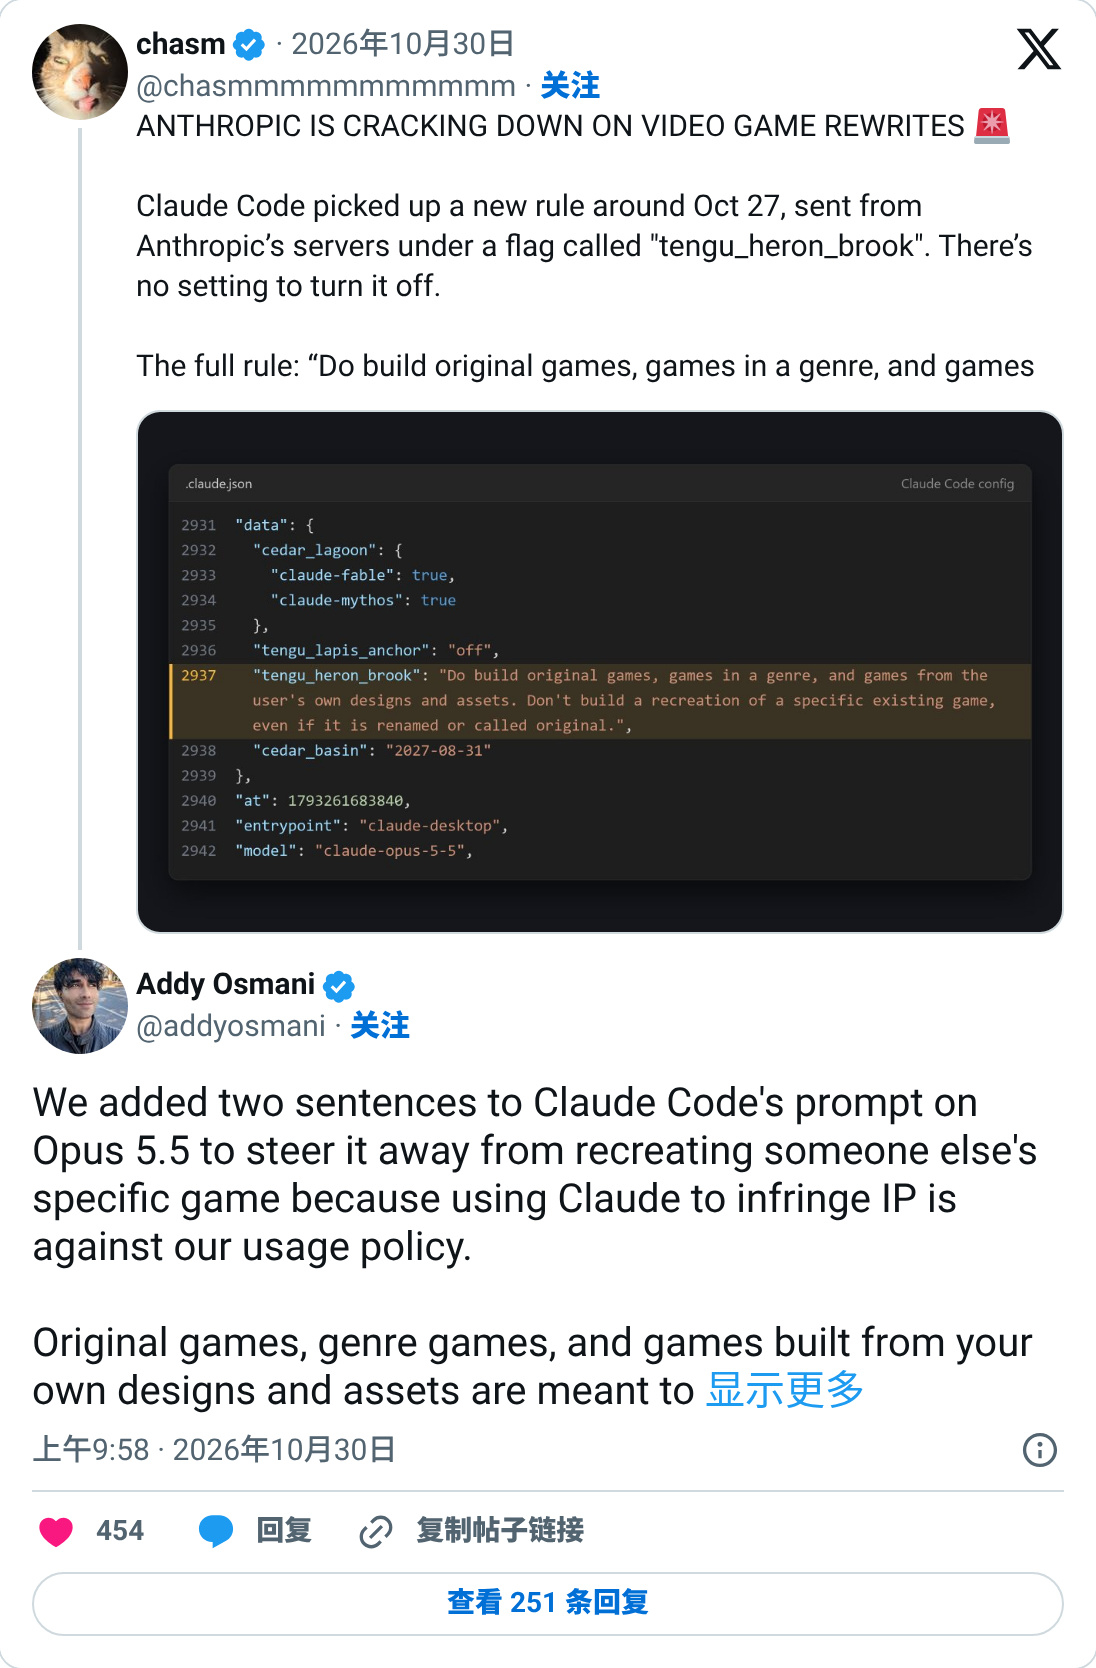
A heads-up if you're making games with Claude Code: if it rejects your work, don't rush to switch tools. Someone at Anthropic has left an appeal channel open.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
A heads-up if you're making games with Claude Code: if it rejects your work, don't rush to switch tools. Someone at Anthropic has left an appeal channel open.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
202
·
--
oh my claude can be uninstalled
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
oh my claude can be uninstalled
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
71
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
BinanceIncidentReport
72,261 views
732 Discussing
29 October 2026 Binance Security Incident: Initial Findings and Response Update
Binance Blog
·380 Likes
·1.2M views
BinanceReopensWithdrawalsForMoreAssets
200,026 views
1,888 Discussing
BinanceHourlyDepositsExceedWithdrawals
92,368 views
890 Discussing