Affected by a security incident at a third-party service provider, Ledger’s official website and several other sites were hit by a cyberattack
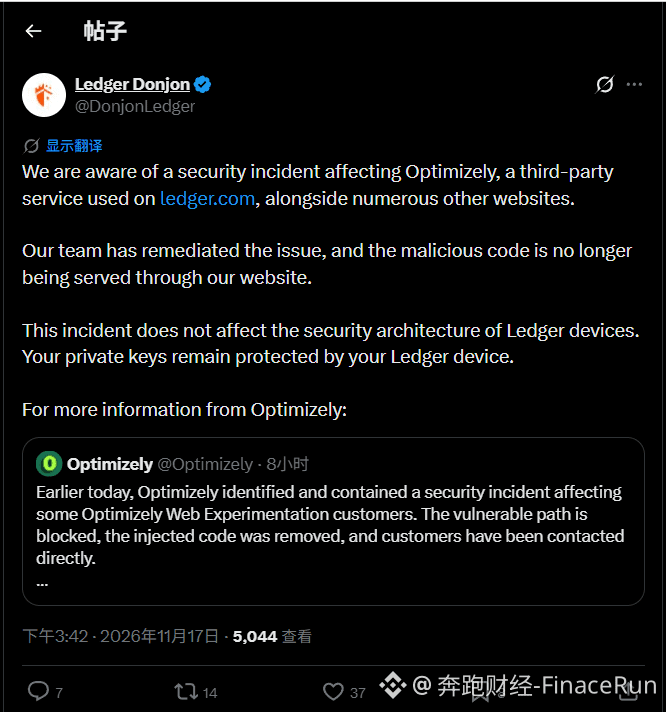
On November 17, Ledger’s security team, Ledger Donjon, announced on X that a security incident at third-party service provider Optimizely had affected Ledger’s official website and several other sites that use the service.
According to the announcement, the Ledger team has completed the necessary security fixes, and the malicious code has been removed from its official website, which no longer poses a threat to visitors. The incident originated from a third-party service used by the website and was limited to the web interface.
Ledger emphasized that the incident did not affect the security architecture of its hardware wallet devices. Users’ private keys remain protected by the devices themselves, and their assets were not affected.
As of publication, Ledger has not disclosed the specific attack method, the number of users affected, or whether any assets were actually lost.
In summary, news of a security incident involving Ledger can easily make people nervous. However, this time the risk came from a third-party script on the official website, and private keys stored in hardware wallets were not affected.
What do you think? When using a hardware wallet, do you pay attention to potential risks in associated services on the official website? Feel free to share your thoughts in the comments.
#Ledger安全事件
On November 17, Ledger’s security team, Ledger Donjon, announced on X that a security incident at third-party service provider Optimizely had affected Ledger’s official website and several other sites that use the service.
According to the announcement, the Ledger team has completed the necessary security fixes, and the malicious code has been removed from its official website, which no longer poses a threat to visitors. The incident originated from a third-party service used by the website and was limited to the web interface.
Ledger emphasized that the incident did not affect the security architecture of its hardware wallet devices. Users’ private keys remain protected by the devices themselves, and their assets were not affected.
As of publication, Ledger has not disclosed the specific attack method, the number of users affected, or whether any assets were actually lost.
In summary, news of a security incident involving Ledger can easily make people nervous. However, this time the risk came from a third-party script on the official website, and private keys stored in hardware wallets were not affected.
What do you think? When using a hardware wallet, do you pay attention to potential risks in associated services on the official website? Feel free to share your thoughts in the comments.
#Ledger安全事件