🚨 Keplr Wallet Security Breach! More Than 44,000 Wallets Affected? USDT and ATOM Holders, Take Note! 🔐💥
📅 2026/11/08|Crypto Wallet Security Alert!
🔴 ① What happened?
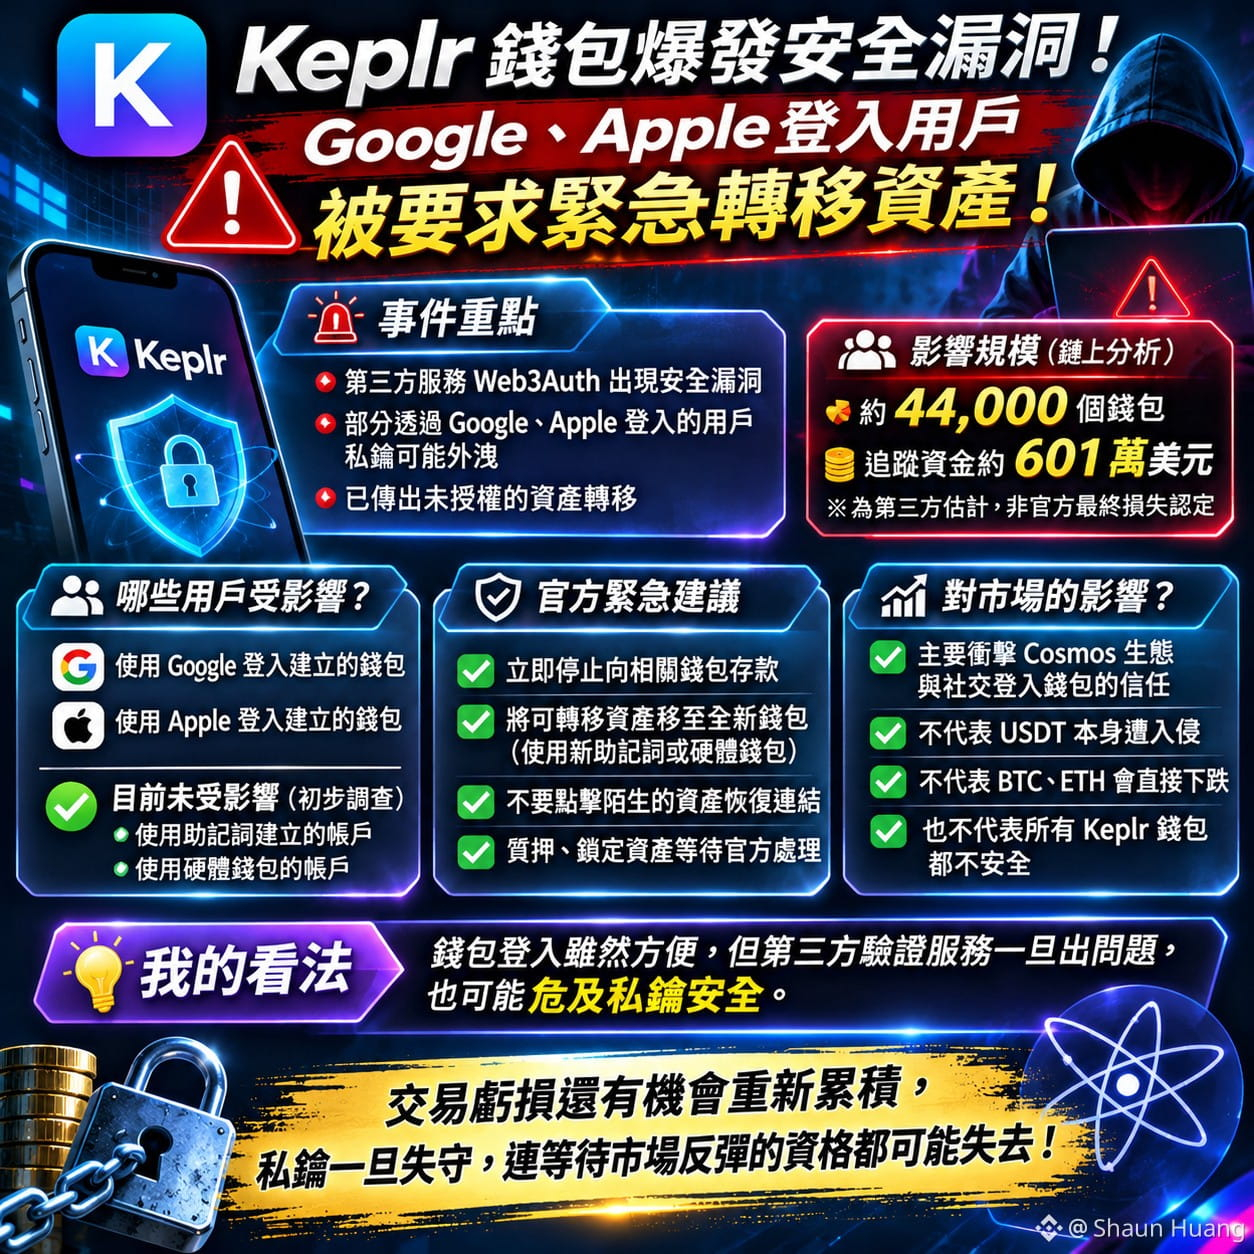
Keplr said a security vulnerability in third-party service Web3Auth exposed the private keys of some users who signed in with Google or Apple. Unauthorized asset transfers have also been reported.
💰 ② How serious are the losses?
Blockchain analytics firm Bitquery estimates:
🔴 More than 44,000 wallets involved
🔴 Approximately $6.01 million in funds tracked
⚠️ This is a third-party on-chain analysis, not an official final loss assessment.
🛡️ ③ Which users are affected?
⚠️ Wallets created using Google sign-in
⚠️ Wallets created using Apple sign-in
✅ Accounts created with a recovery phrase or hardware wallet are not affected, according to the current preliminary investigation.
🚨 ④ Urgent official recommendations
✅ Stop depositing funds into wallets linked to social sign-ins
✅ Move transferable assets to a new recovery phrase or hardware wallet
✅ Don’t click unfamiliar asset recovery links
✅ Stake or lock assets while awaiting official guidance
Reduced balances in some accounts may also be related to official protective transfers.
₿ ⑤ Impact on the crypto market?
The incident primarily affects the Cosmos ecosystem and trust in social sign-in wallets.
⚠️ This does not mean USDT itself has been compromised.
⚠️ This does not mean BTC or ETH will directly decline.
⚠️ And it certainly does not mean all Keplr wallets are unsafe.
🔍 Latest fact check
Keplr has issued an asset transfer warning. The Web3Auth vulnerability and the extent of its impact are still under investigation, and the actual losses have yet to be confirmed.
💡 My take
Convenient wallet sign-in doesn’t mean asset management is risk-free. If a third-party authentication service runs into trouble, private key security could also be at risk.
🎯 Trading losses can still be made back over time, but once your private keys are compromised, you may lose even the chance to wait for a market rebound!
$BTC
$ETH
#keplr建议社交登录用户转移资产
📅 2026/11/08|Crypto Wallet Security Alert!
🔴 ① What happened?
Keplr said a security vulnerability in third-party service Web3Auth exposed the private keys of some users who signed in with Google or Apple. Unauthorized asset transfers have also been reported.
💰 ② How serious are the losses?
Blockchain analytics firm Bitquery estimates:
🔴 More than 44,000 wallets involved
🔴 Approximately $6.01 million in funds tracked
⚠️ This is a third-party on-chain analysis, not an official final loss assessment.
🛡️ ③ Which users are affected?
⚠️ Wallets created using Google sign-in
⚠️ Wallets created using Apple sign-in
✅ Accounts created with a recovery phrase or hardware wallet are not affected, according to the current preliminary investigation.
🚨 ④ Urgent official recommendations
✅ Stop depositing funds into wallets linked to social sign-ins
✅ Move transferable assets to a new recovery phrase or hardware wallet
✅ Don’t click unfamiliar asset recovery links
✅ Stake or lock assets while awaiting official guidance
Reduced balances in some accounts may also be related to official protective transfers.
₿ ⑤ Impact on the crypto market?
The incident primarily affects the Cosmos ecosystem and trust in social sign-in wallets.
⚠️ This does not mean USDT itself has been compromised.
⚠️ This does not mean BTC or ETH will directly decline.
⚠️ And it certainly does not mean all Keplr wallets are unsafe.
🔍 Latest fact check
Keplr has issued an asset transfer warning. The Web3Auth vulnerability and the extent of its impact are still under investigation, and the actual losses have yet to be confirmed.
💡 My take
Convenient wallet sign-in doesn’t mean asset management is risk-free. If a third-party authentication service runs into trouble, private key security could also be at risk.
🎯 Trading losses can still be made back over time, but once your private keys are compromised, you may lose even the chance to wait for a market rebound!
$BTC
$ETH
#keplr建议社交登录用户转移资产