Gnosis Pay breach exposes card details and personal information
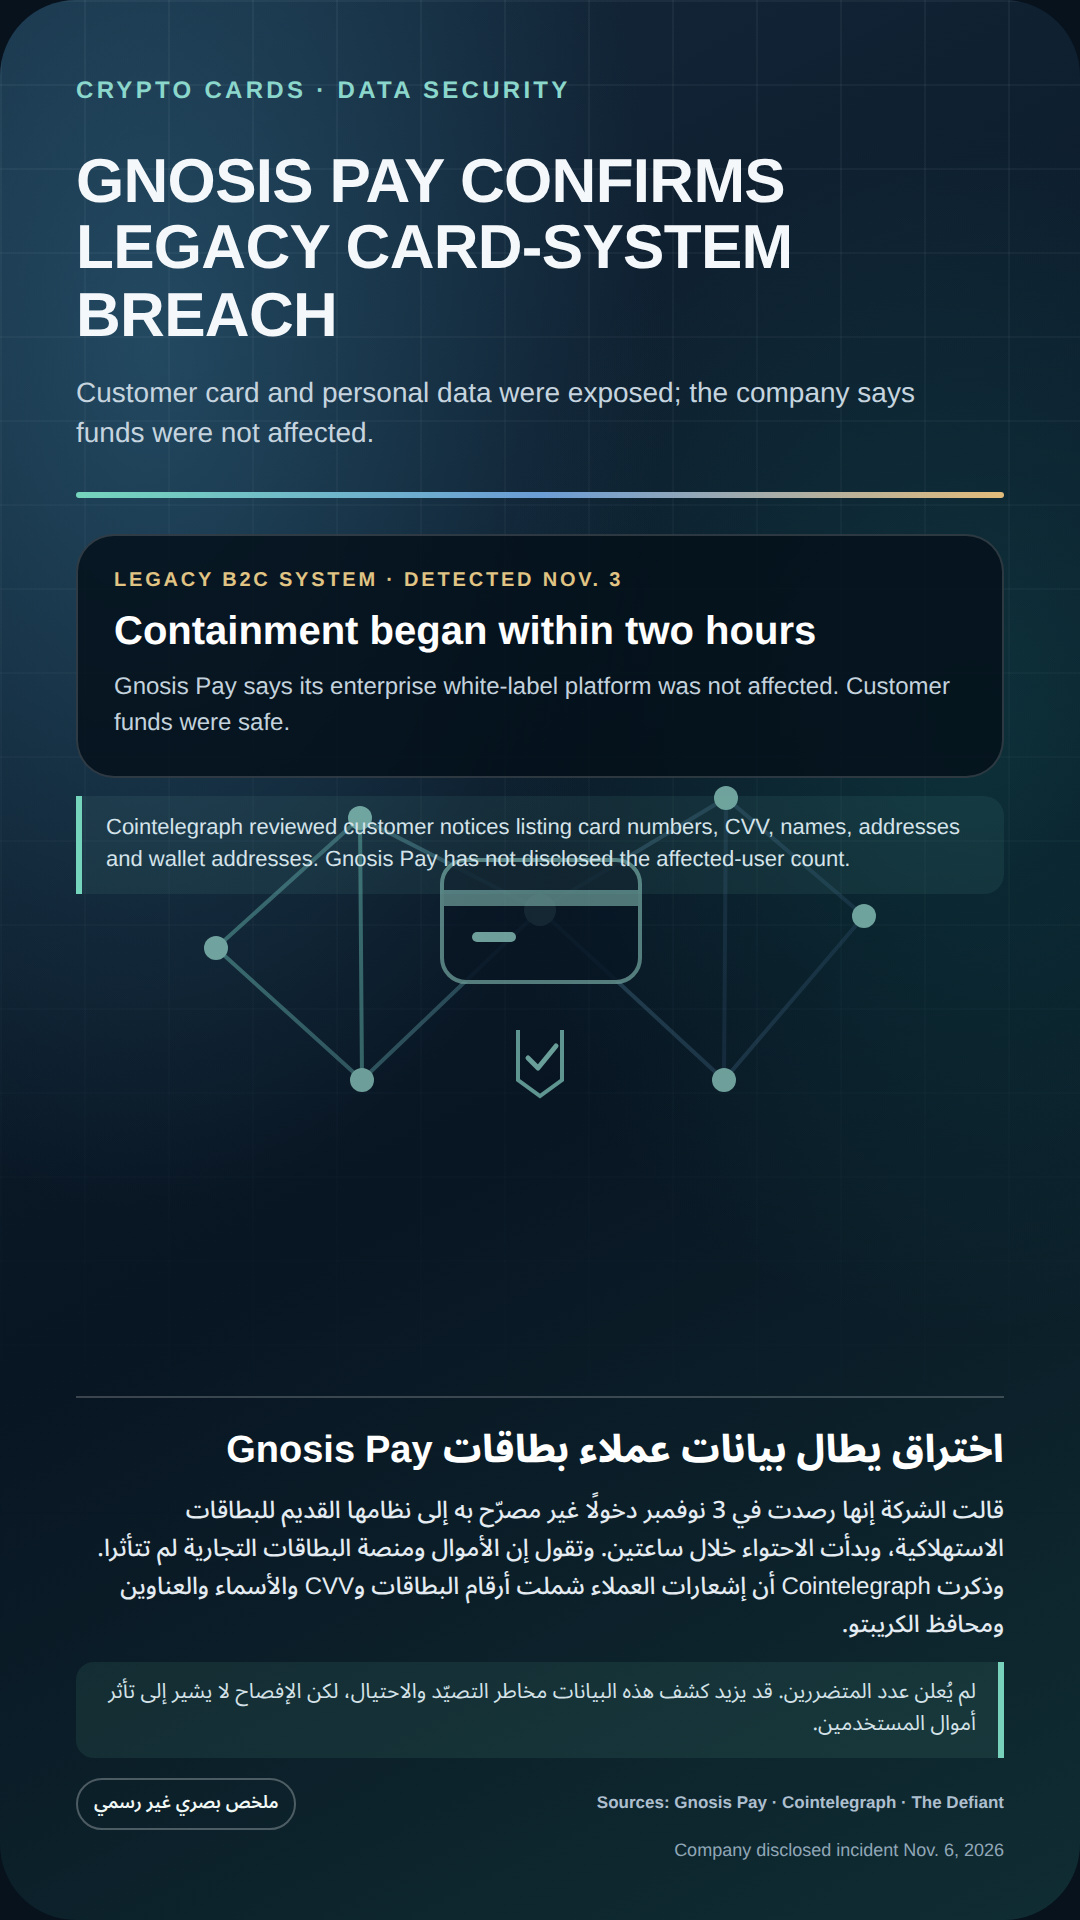
The facts: Gnosis Pay said monitoring systems detected unauthorized access to its legacy consumer card system on November 3, and containment began within two hours. It said customer funds and its business card platform were unaffected, and that it fixed the vulnerability and required additional 3D Secure verification for online payments until the system is retired on December 20. It did not disclose how many customers were affected.
Data details: According to customer notifications reviewed by Cointelegraph, the data included full card numbers, expiration dates, CVV codes, names, addresses, and wallet addresses; in some cases, it also included banking information. These details are attributed to the notifications reviewed by the report and are not a list publicly released by the company.
Context: The exposed data could increase the risk of phishing, identity theft, or card misuse. This does not mean that wallet funds were stolen; the company said users’ funds were unaffected.
Sources:
Gnosis Pay — https://gnosispay.com/blog/data-breach-legacy-system-gnosis-pay-branded-cards
Cointelegraph — https://cointelegraph.com/news/gnosis-pay-breach-exposes-card-details-personal-data-crypto-wallet-information
The Defiant — https://thedefiant.io/news/security/gnosis-pay-confirms-breach-of-consumer-card-system
The facts: Gnosis Pay said monitoring systems detected unauthorized access to its legacy consumer card system on November 3, and containment began within two hours. It said customer funds and its business card platform were unaffected, and that it fixed the vulnerability and required additional 3D Secure verification for online payments until the system is retired on December 20. It did not disclose how many customers were affected.
Data details: According to customer notifications reviewed by Cointelegraph, the data included full card numbers, expiration dates, CVV codes, names, addresses, and wallet addresses; in some cases, it also included banking information. These details are attributed to the notifications reviewed by the report and are not a list publicly released by the company.
Context: The exposed data could increase the risk of phishing, identity theft, or card misuse. This does not mean that wallet funds were stolen; the company said users’ funds were unaffected.
Sources:
Gnosis Pay — https://gnosispay.com/blog/data-breach-legacy-system-gnosis-pay-branded-cards
Cointelegraph — https://cointelegraph.com/news/gnosis-pay-breach-exposes-card-details-personal-data-crypto-wallet-information
The Defiant — https://thedefiant.io/news/security/gnosis-pay-confirms-breach-of-consumer-card-system