A few Ethereum projects would become vulnerable under Glamsterdam's proposed rules, the Ethereum Foundation said in its November 6 update. ChainSecurity found the issues during testnet testing of the upgrade.
The Foundation is engaging ChainSecurity and Dedaub alongside internal audits, and asking developers and auditors across Ethereum to check their projects. Its own review cannot cover every application, including the off-chain code those applications depend on.
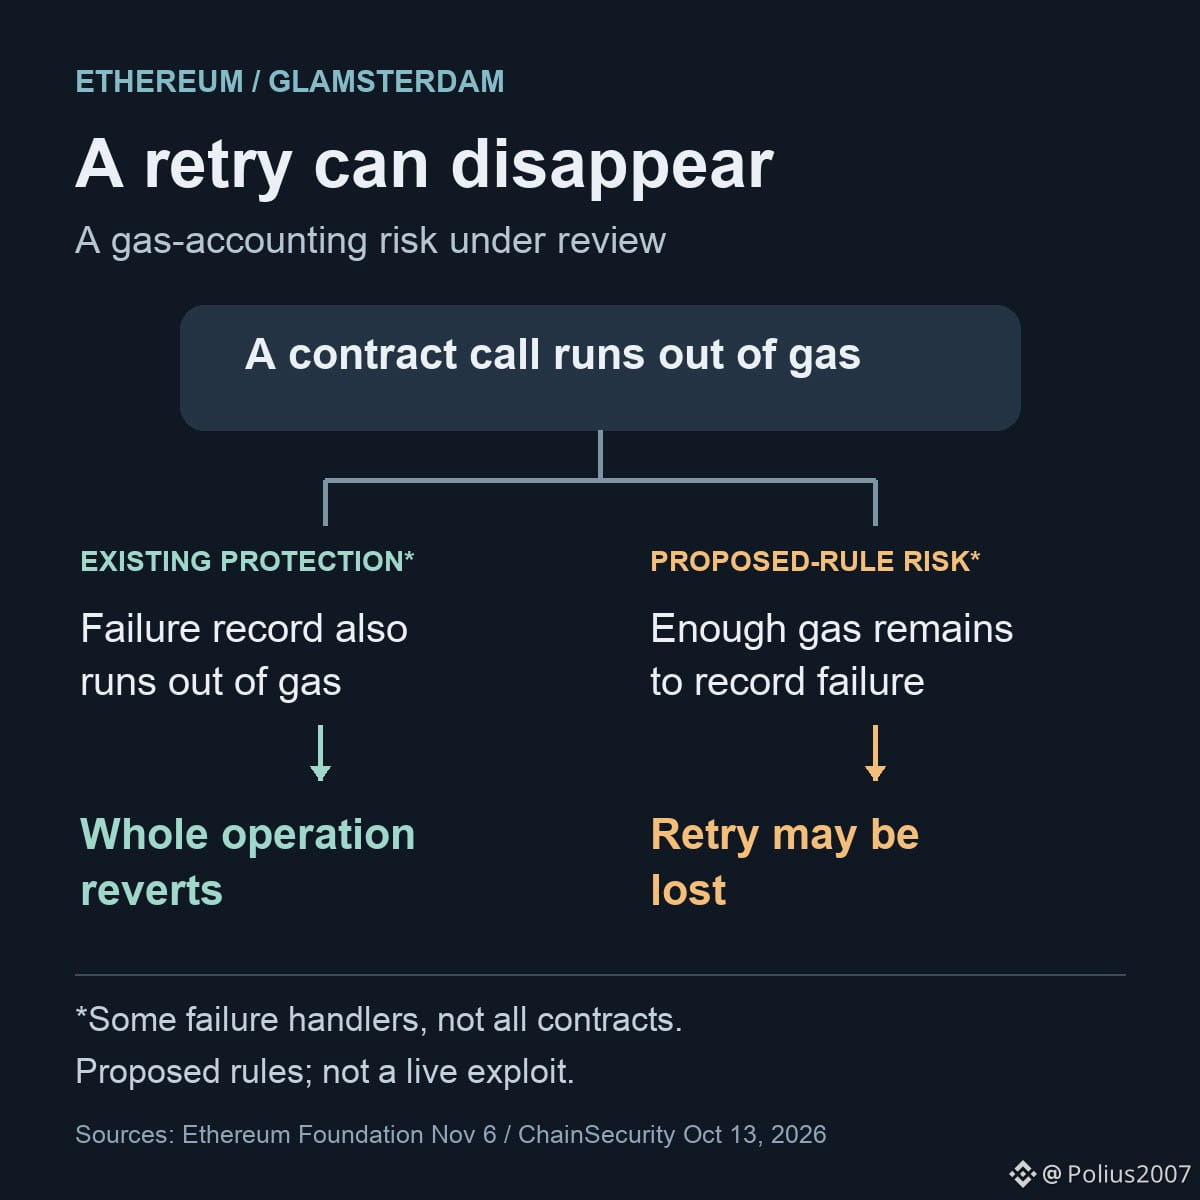
One risk shows how a change in gas accounting can affect what users can recover from. ChainSecurity describes contracts where an unsuccessful operation can currently be tried again because the whole attempt rolls back. Under the proposed rules, some of those contracts could instead record a permanent failure, closing that retry path even though their code has not changed. This concerns how applications handle failed contract calls, not every failed wallet transaction.
The November 6 update names no affected projects and reports no live exploit. Hoodi's testnet upgrade remains on hold until the issues are resolved.
The open question is how widely existing applications depend on assumptions the upgrade would break. The Foundation wants that evidence for upcoming AllCoreDev discussions, including whether changes to the upgrade specifications could prevent the problems.
Sources: Ethereum Foundation, November 6; ChainSecurity's analysis of the October 13 specifications.
https://blog.ethereum.org/2026/11/06/glamsterdam-8037-8038
https://www.chainsecurity.com/blog/glamsterdam-gas/index.html
#Ethereum #ETH
The Foundation is engaging ChainSecurity and Dedaub alongside internal audits, and asking developers and auditors across Ethereum to check their projects. Its own review cannot cover every application, including the off-chain code those applications depend on.
One risk shows how a change in gas accounting can affect what users can recover from. ChainSecurity describes contracts where an unsuccessful operation can currently be tried again because the whole attempt rolls back. Under the proposed rules, some of those contracts could instead record a permanent failure, closing that retry path even though their code has not changed. This concerns how applications handle failed contract calls, not every failed wallet transaction.
The November 6 update names no affected projects and reports no live exploit. Hoodi's testnet upgrade remains on hold until the issues are resolved.
The open question is how widely existing applications depend on assumptions the upgrade would break. The Foundation wants that evidence for upcoming AllCoreDev discussions, including whether changes to the upgrade specifications could prevent the problems.
Sources: Ethereum Foundation, November 6; ChainSecurity's analysis of the October 13 specifications.
https://blog.ethereum.org/2026/11/06/glamsterdam-8037-8038
https://www.chainsecurity.com/blog/glamsterdam-gas/index.html
#Ethereum #ETH