Consensys has just announced a major upgrade: the slowest step in elliptic-curve security checks has been accelerated, running 10.8 times faster on the FourQ curve.
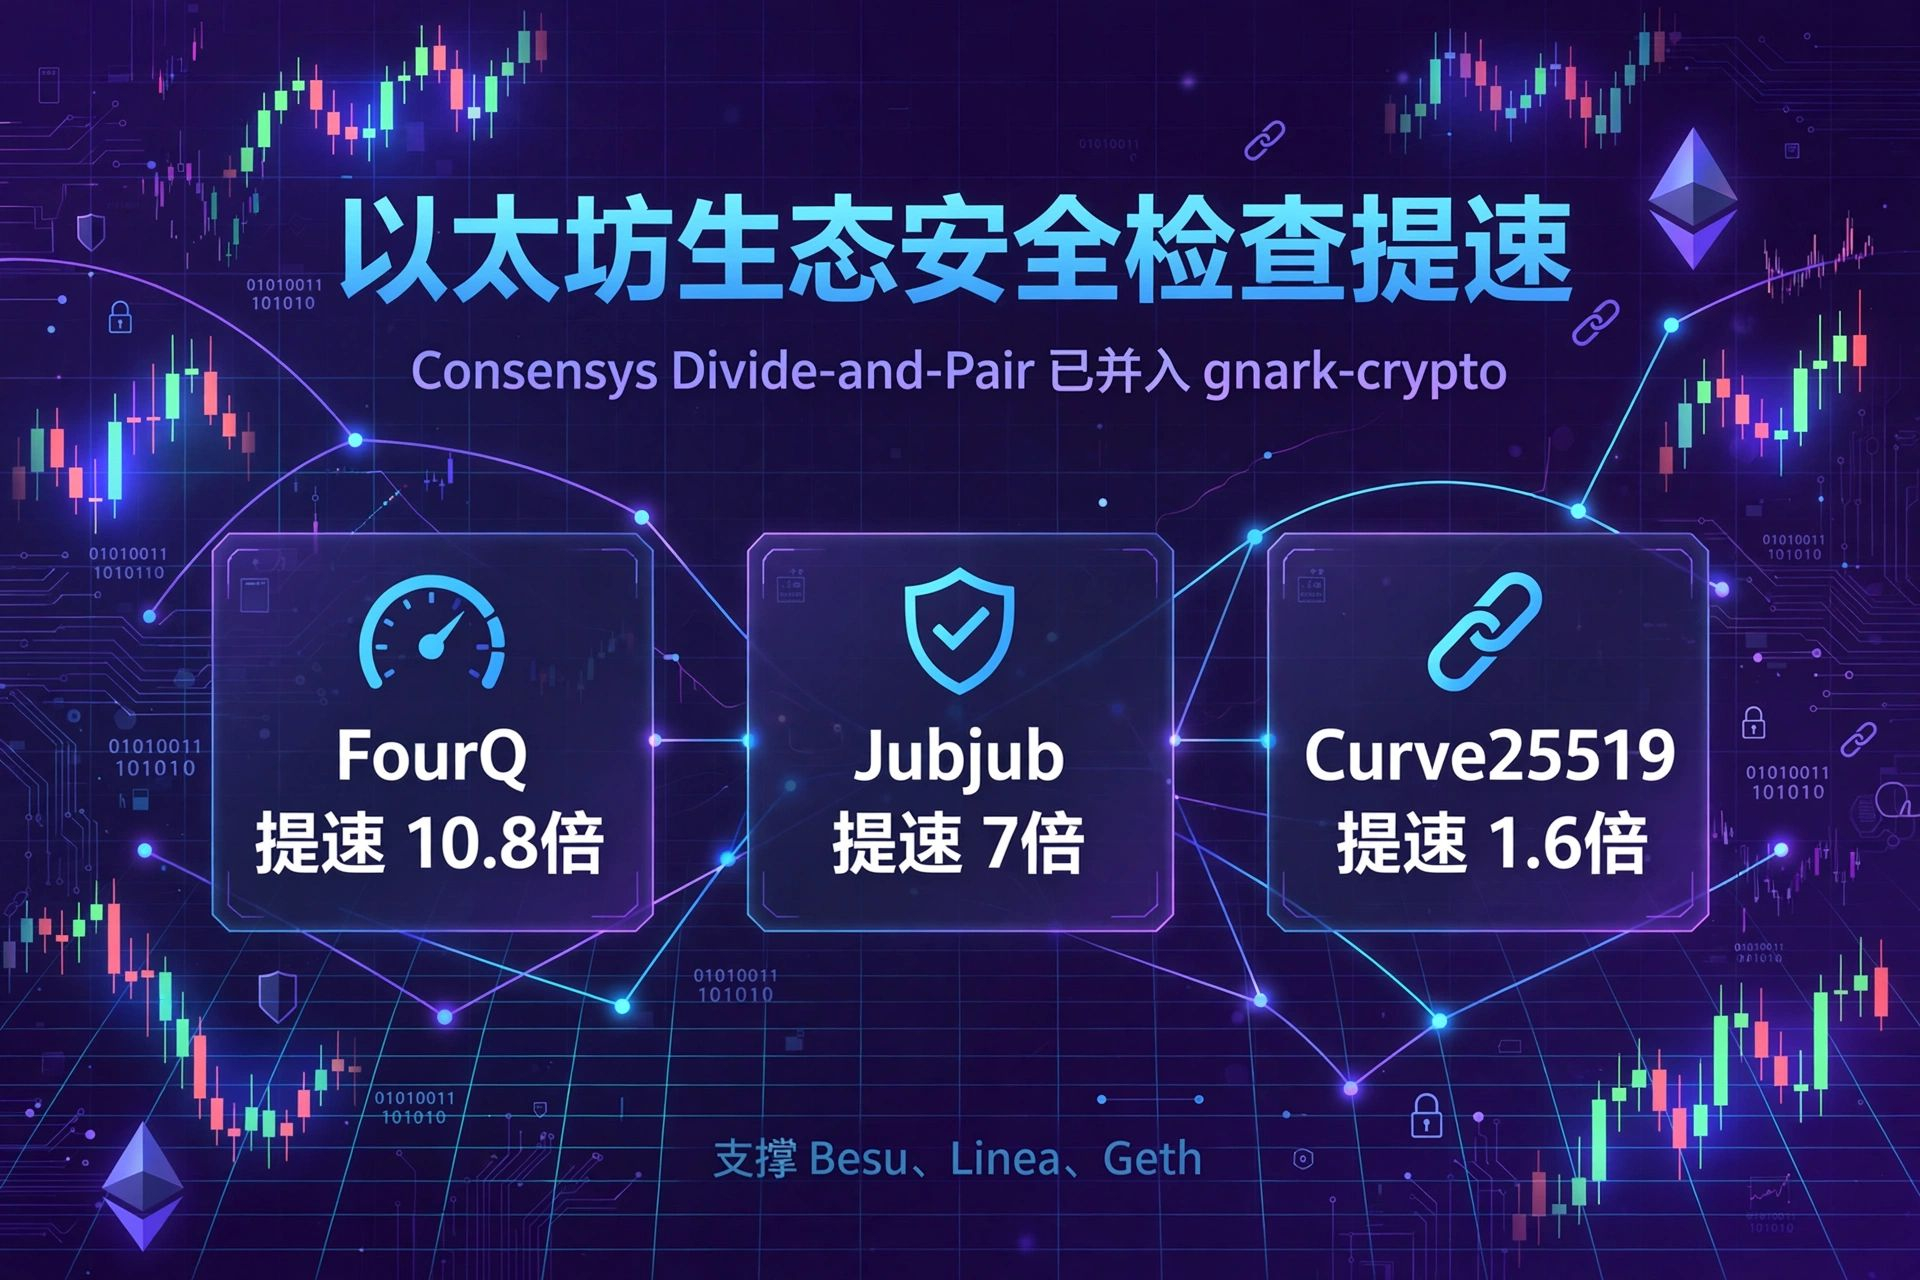
The new method is called Divide-and-Pair and targets subgroup membership checks. It delivers speedups of about 1.6× on Curve25519, 1.3× on Curve448, 1.4× on GC256A, 10.8× on FourQ, and 7× on Jubjub. It has been integrated into the open-source library gnark-crypto, which powers systems including Besu, Linea, Geth, Succinct, and Lighter. The related paper has been accepted by the IACR Transactions on Cryptographic Hardware and Embedded Systems and will be presented at CHES 2027.
I think the real value of this speedup is that it isn’t tied to a particular curve: the same method is no slower than the old one across all five curves. Developers don’t have to switch approaches for each curve individually, making it possible to leave security checks enabled by default instead of turning them off for speed.
If you could roll out this new check in only one of Besu, Linea, and Geth first, which would you choose?
Follow me. When this paper is presented at CHES 2027, I’ll help you check whether its measured speedups in Besu and Linea hold up.
$ETH
The new method is called Divide-and-Pair and targets subgroup membership checks. It delivers speedups of about 1.6× on Curve25519, 1.3× on Curve448, 1.4× on GC256A, 10.8× on FourQ, and 7× on Jubjub. It has been integrated into the open-source library gnark-crypto, which powers systems including Besu, Linea, Geth, Succinct, and Lighter. The related paper has been accepted by the IACR Transactions on Cryptographic Hardware and Embedded Systems and will be presented at CHES 2027.
I think the real value of this speedup is that it isn’t tied to a particular curve: the same method is no slower than the old one across all five curves. Developers don’t have to switch approaches for each curve individually, making it possible to leave security checks enabled by default instead of turning them off for speed.
If you could roll out this new check in only one of Besu, Linea, and Geth first, which would you choose?
Follow me. When this paper is presented at CHES 2027, I’ll help you check whether its measured speedups in Besu and Linea hold up.
$ETH