📰 The Miners’ Shield Has Been Breached: Nearly $1 Million Stolen from a Solana Bot—What Does It Mean?
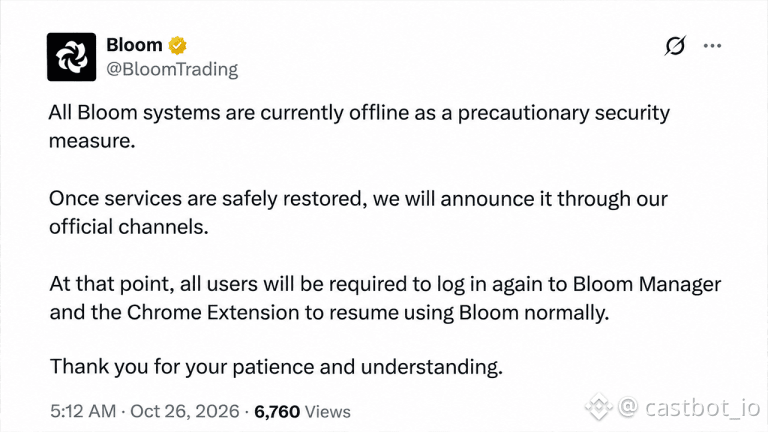
Bloom, an automated trading bot on Solana, was hacked, resulting in losses of nearly $1 million. The hacker stole 49 wallets belonging to 9 users, but the company says no keys were stolen and it will fully reimburse users. So how did the hacker pull it off? Through a vulnerability in a third-party tool.
Why does this news matter?
This attack didn’t directly target Bloom’s code. Instead, it exploited a vulnerability in a third-party tool used in its system. This exposes the fragility of the DeFi bot ecosystem: if one link fails, the whole chain could collapse. Why is this important? Because it shows that:
- It’s not just major projects that get hacked—even bots, the supposed “security guards,” can get caught in the crossfire.
- DeFi’s “untrusted-on-untrusted” problem (untrusted code plus untrusted third parties) means bots can end up making things worse.
Market impact
For Solana, although the company claims no keys were lost, this incident has made the market question the security of bot systems. The short-term sentiment impact is negative because:
- SOL at $101.37 may face more scrutiny.
- This could trigger a domino effect of concerns about the security of the entire Solana DeFi ecosystem.
- Funds may temporarily flow out of automated pools such as bots.
Similar incidents in the past? SmartBee on Binance Smart Chain had a similar vulnerability in 2019, but on a much smaller scale. This incident is larger and took place on a popular chain like Solana, so its impact is broader.
Trading approach
💡 For SOL, below $95 is a relatively safe zone—but that thesis is invalidated if it later turns out that Bloom’s private keys really were lost. Put simply: the bot tool is starting to fail.
This article is not sponsored by any project. The author does not hold any of the assets mentioned.
⚠️ This is not investment advice. Predictions are for reference only.
$SOL #SecurityIncident