#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Hack 🚨
The world of crypto is in uproar, but let’s cut through the noise with hard, verified evidence about a $351.6 million Bitget hack.
Warning: It’s not what you think.
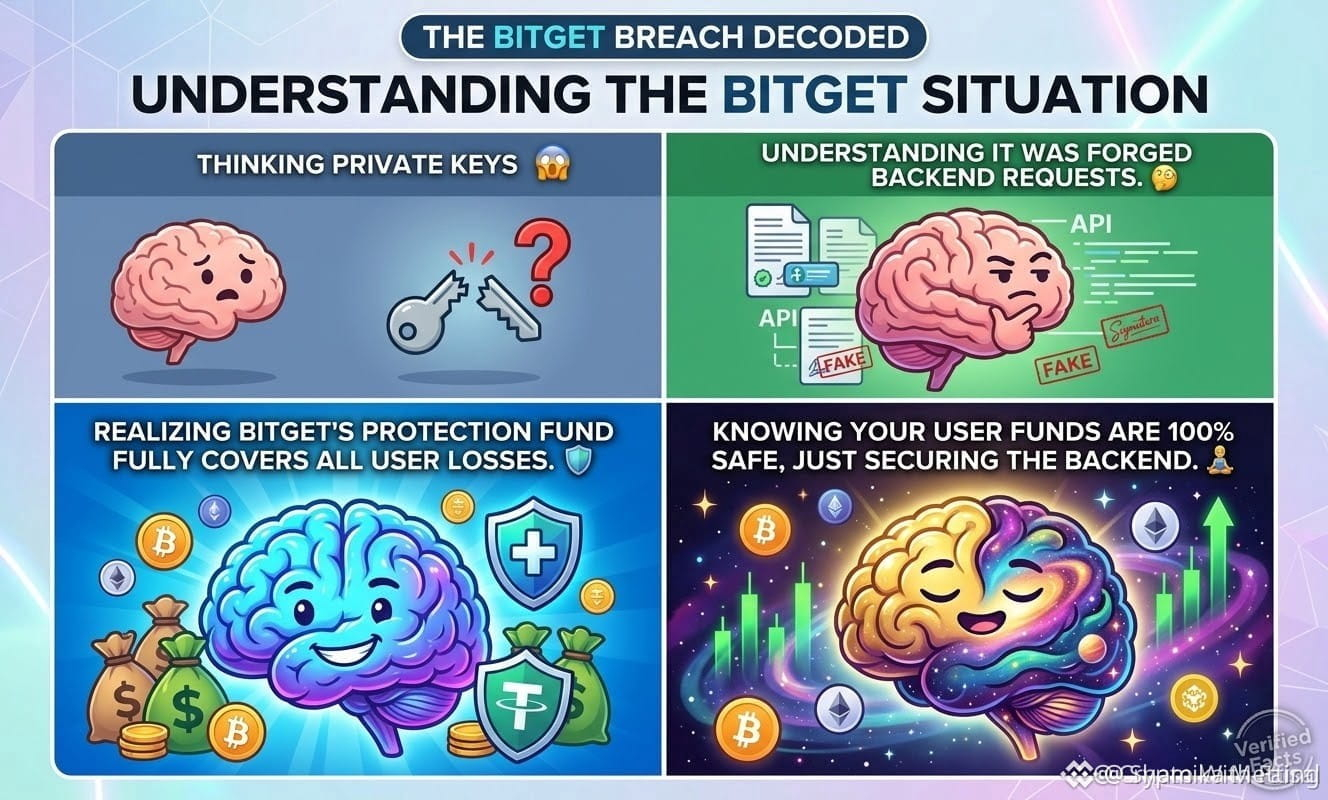
The attackers didn’t steal wallet vault keys. Instead, they compromised a back-end system, tampered with transaction documents, and sent fake withdrawal requests through Bitget’s own approval process.
Why does this technical detail matter?
Because key theft means endless bleeding. 🩸
Fake requests = plug the loophole and stop the bleeding. 🛑
Good news:
✅ Keys are safe: The private keys never left their place.
✅ Vaults secured: Only the hot and semi-warm wallets were targeted. Cold storage remains 100% safe.
✅ Users are okay: Bitget’s protection fund of $464 million fully covers the $351.6 million loss.
Withdrawals were temporarily paused for a comprehensive security review, but CEO Gracy Chen confirmed that users’ assets are safe.
This incident proves that back-end infrastructure has become the new battleground in Web3. Stay alert and stay safe! 🛡️
Please follow up
$AVAX
🚨 The Real Story Behind the Bitget Hack 🚨
The world of crypto is in uproar, but let’s cut through the noise with hard, verified evidence about a $351.6 million Bitget hack.
Warning: It’s not what you think.
The attackers didn’t steal wallet vault keys. Instead, they compromised a back-end system, tampered with transaction documents, and sent fake withdrawal requests through Bitget’s own approval process.
Why does this technical detail matter?
Because key theft means endless bleeding. 🩸
Fake requests = plug the loophole and stop the bleeding. 🛑
Good news:
✅ Keys are safe: The private keys never left their place.
✅ Vaults secured: Only the hot and semi-warm wallets were targeted. Cold storage remains 100% safe.
✅ Users are okay: Bitget’s protection fund of $464 million fully covers the $351.6 million loss.
Withdrawals were temporarily paused for a comprehensive security review, but CEO Gracy Chen confirmed that users’ assets are safe.
This incident proves that back-end infrastructure has become the new battleground in Web3. Stay alert and stay safe! 🛡️
Please follow up
$AVAX