EU Wallet Vulnerability: Must Report in 24 Hours, Main Obligation Still Goes Until Next Year
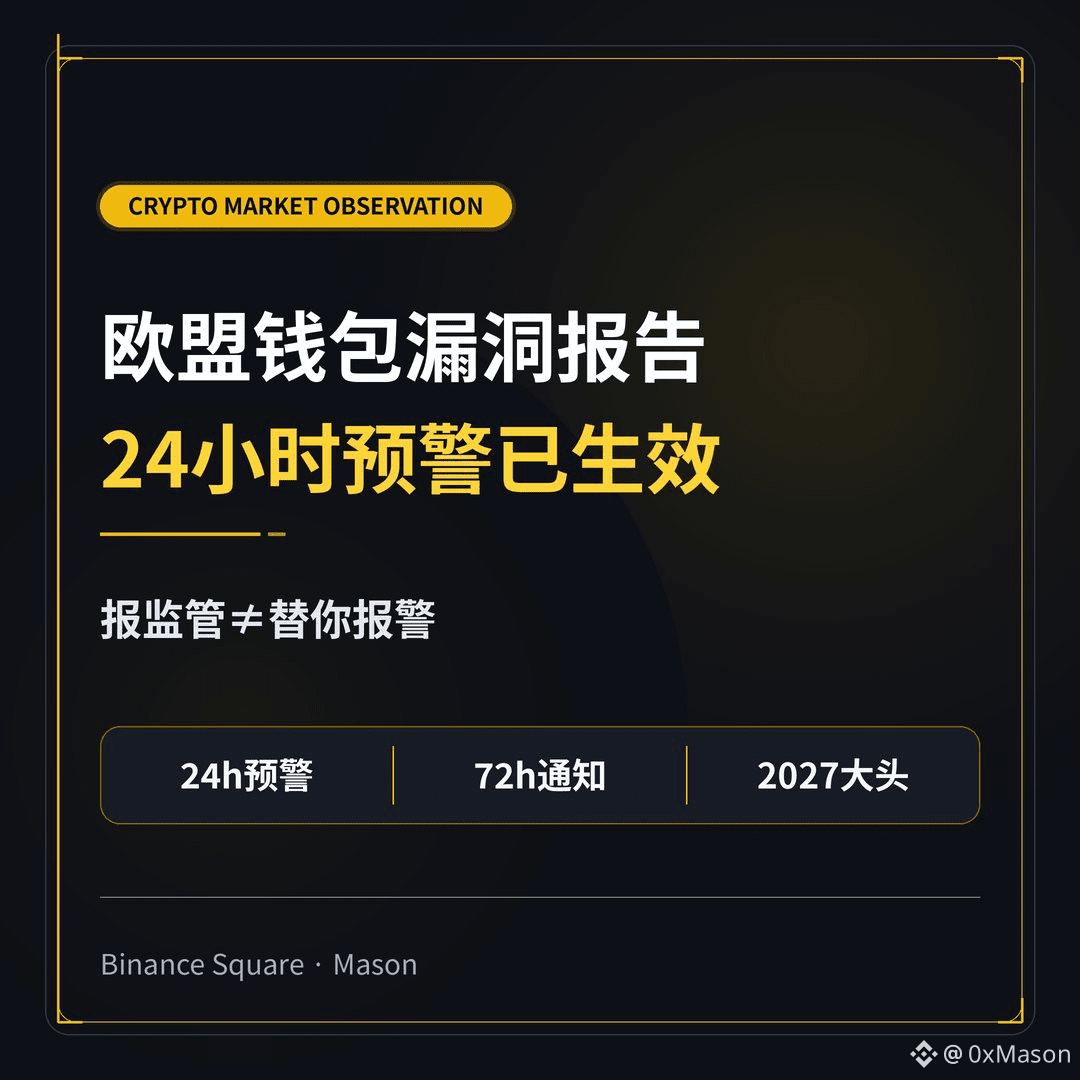
Starting September 11, providers of in-scope commercially networked hardware wallets and wallet software that discover vulnerabilities or serious security incidents that are “actively exploited” must issue an early warning to the EU’s cybersecurity authority within 24 hours.
Within 72 hours, they must submit the complete notification; the final vulnerability report must be delivered within 14 days after the patch becomes available. For serious incidents, an additional month is allowed after the 72-hour notification. File through ENISA’s unified reporting platform, and you also need to notify affected users. For older products, as long as they were introduced to the EU market during the same year, they follow the same clock.
Don’t read this as “your wallet app will automatically report for you.” Individual open-source contributors generally aren’t considered manufacturers; open-source stewards and the major product security obligations only take effect on December 11, 2027. Scope depends on how the product is sold—there’s no official brand whitelist.
Starting September 11, providers of in-scope commercially networked hardware wallets and wallet software that discover vulnerabilities or serious security incidents that are “actively exploited” must issue an early warning to the EU’s cybersecurity authority within 24 hours.
Within 72 hours, they must submit the complete notification; the final vulnerability report must be delivered within 14 days after the patch becomes available. For serious incidents, an additional month is allowed after the 72-hour notification. File through ENISA’s unified reporting platform, and you also need to notify affected users. For older products, as long as they were introduced to the EU market during the same year, they follow the same clock.
Don’t read this as “your wallet app will automatically report for you.” Individual open-source contributors generally aren’t considered manufacturers; open-source stewards and the major product security obligations only take effect on December 11, 2027. Scope depends on how the product is sold—there’s no official brand whitelist.