Bitcoin’s mainnet script language has always been “dumb” and can’t handle complex computations. That’s both its security foundation and its functional ceiling.
Babylon’s Trustless Bitcoin Vaults (TBV) aims to resolve a key contradiction: how can the Bitcoin mainnet verify a complex off-chain operation without changing a single line of code in the mainnet?
The answer lies in a “garbled circuit.”
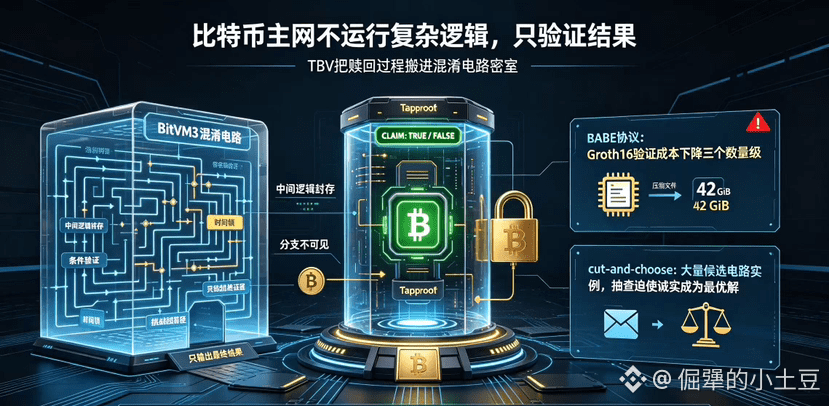
In simple terms, your withdrawal logic is packaged into a garbled circuit via the BitVM3 framework. The circuit outputs a result—whether the claim is “true” or “false.” The mainnet only needs to verify this final outcome; as for how many conditional checks occurred in between, which branches were triggered, and so on, the outside world knows nothing.
Let’s use an imperfect analogy: traditional on-chain operations are like shouting “I’m withdrawing money” in an open public square—everyone can see your path and timing, and frontrunning robots are already waiting at the finish line to steal your spot. A garbled circuit moves the entire process into a locked room—while the verdict is public, the case file is permanently sealed. You know the result, but not the reasoning process.
There are two key technical supports here.
The first is the BABE protocol. In January 2026, Babylon co-founder and Stanford professor David Tse released BABE, reducing the verification cost of Groth16 zero-knowledge proofs by three orders of magnitude. In BitVM3’s early方案, a single garbled-circuit file could be as large as 42 GiB, making large-scale real-world use impossible. BABE compresses off-chain storage and setup costs by an entire three orders of magnitude, moving this from the lab to the edge of practical engineering.
The second is the cut-and-choose protocol.
At present, the generation and verification of garbled circuits depend on specific prover nodes. If the prover is attacked or colludes, the integrity of the circuit may be compromised. The centralization of the prover is itself a single point of failure.
As of May 2026, more than 56,000 BTC (about $5.6 billion) have already been put to work for yield through this mechanism. But between “it can run” and “it can run reliably at scale,” there are still two hurdles: gas costs in a real mainnet environment and the fault-recovery rate.
I’m on board with the direction—but before the data comes out, let’s wait and see, and not change anything.
#baby $BABY @BabylonLabs_io
Babylon’s Trustless Bitcoin Vaults (TBV) aims to resolve a key contradiction: how can the Bitcoin mainnet verify a complex off-chain operation without changing a single line of code in the mainnet?
The answer lies in a “garbled circuit.”
In simple terms, your withdrawal logic is packaged into a garbled circuit via the BitVM3 framework. The circuit outputs a result—whether the claim is “true” or “false.” The mainnet only needs to verify this final outcome; as for how many conditional checks occurred in between, which branches were triggered, and so on, the outside world knows nothing.
Let’s use an imperfect analogy: traditional on-chain operations are like shouting “I’m withdrawing money” in an open public square—everyone can see your path and timing, and frontrunning robots are already waiting at the finish line to steal your spot. A garbled circuit moves the entire process into a locked room—while the verdict is public, the case file is permanently sealed. You know the result, but not the reasoning process.
There are two key technical supports here.
The first is the BABE protocol. In January 2026, Babylon co-founder and Stanford professor David Tse released BABE, reducing the verification cost of Groth16 zero-knowledge proofs by three orders of magnitude. In BitVM3’s early方案, a single garbled-circuit file could be as large as 42 GiB, making large-scale real-world use impossible. BABE compresses off-chain storage and setup costs by an entire three orders of magnitude, moving this from the lab to the edge of practical engineering.
The second is the cut-and-choose protocol.
At present, the generation and verification of garbled circuits depend on specific prover nodes. If the prover is attacked or colludes, the integrity of the circuit may be compromised. The centralization of the prover is itself a single point of failure.
As of May 2026, more than 56,000 BTC (about $5.6 billion) have already been put to work for yield through this mechanism. But between “it can run” and “it can run reliably at scale,” there are still two hurdles: gas costs in a real mainnet environment and the fault-recovery rate.
I’m on board with the direction—but before the data comes out, let’s wait and see, and not change anything.
#baby $BABY @BabylonLabs_io