


A hairdryer, an unattended weather sensor, and two meticulously calculated trades.
On April 6 and April 15, 2026, the French meteorological probe at Charles de Gaulle Airport in Paris was heated using a portable heating device, causing temperature readings to spike unusually in a short time. The actual temperature at Charles de Gaulle Airport did not experience such fluctuations, but the prediction market for 'Paris daily maximum temperature' on Polymarket settled as usual. Two operations netted a total of $34,000, transferred from the platform to an anonymous account that was only opened two days before the incident.
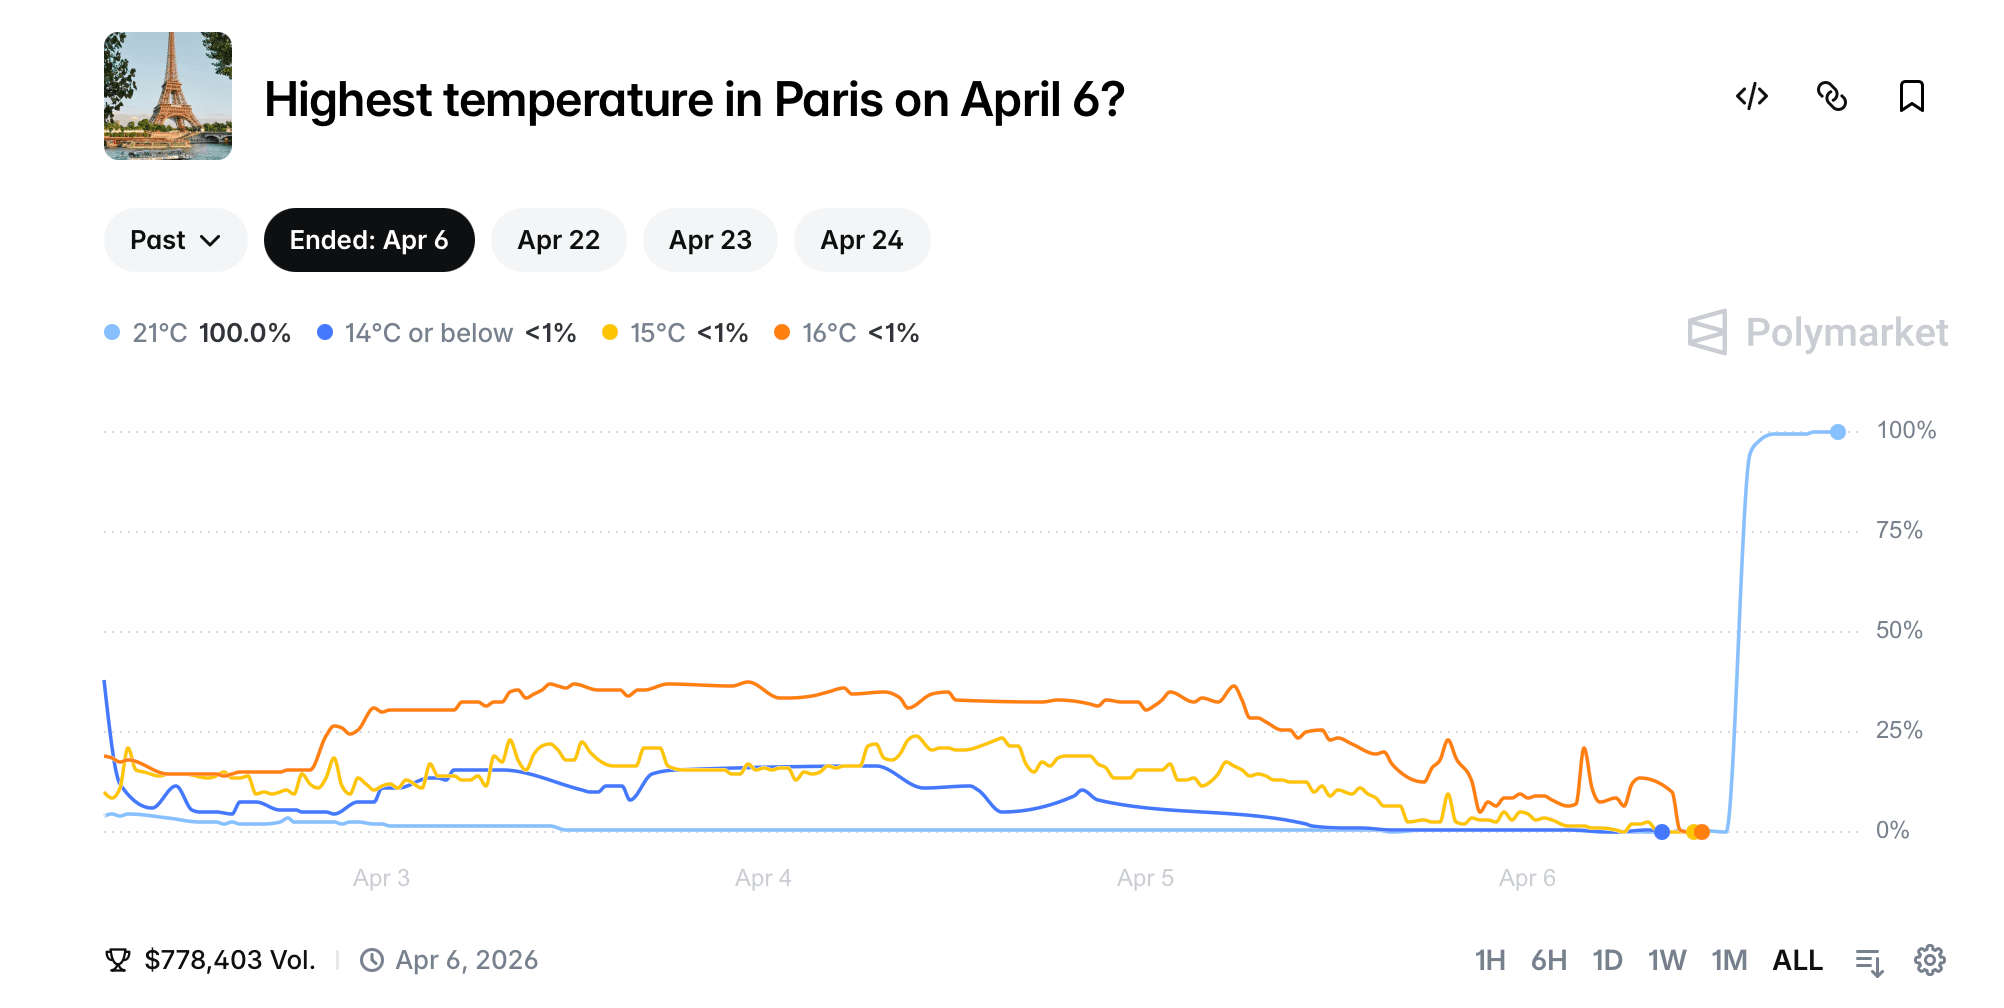
This is not a typical crypto attack. It did not exploit any smart contract vulnerabilities nor target any decentralized governance processes. The entire toolkit for the attack was just a hairdryer.
How did a temperature spike of 4°C in just 12 minutes fool the global prediction market?
Between 6:30 PM and 6:42 PM on April 6, the temperature reading at Charles de Gaulle Airport surged by 4°C in just 12 minutes, peaking at 22.5°C before rapidly dropping in 5 minutes. The actual temperature in Paris did not exhibit such drastic fluctuations that day, and nearby weather stations did not record any similar anomalies.
The weather station (code: LFPG) is located at the edge of the runway at Charles de Gaulle Airport, close to a public area next to the road. Its relatively open physical location allows suspects to approach the sensor and make physical interventions.
This brief 'high temperature' coincidentally hit the '21°C' option on Polymarket, a result that had previously gone almost unnoticed. After the anomalous data was accepted as the day's highest temperature by the platform, it settled as Yes. A certain account took home about $14,000.
Nine days later, around 9:30 PM on April 15, a nearly identical script unfolded again: a cloudy, windless night saw the temperature readings at Charles de Gaulle Airport bizarrely rise to 22°C. The probability of the '22°C' option on Polymarket skyrocketed from 0.1% to 95% in just 30 minutes. The second payout exceeded $20,000, still funneled into the same account.
Paul Marquis, founder of the French E-Meteo Service and meteorologist, provided a technically irrefutable judgment: 'There was no change in wind direction or relative humidity at the time, and other nearby weather stations did not record any anomalies. Physical interference is the most reasonable explanation, such as placing a heating device near the sensor probe.'
The French national meteorological agency (Météo-France) subsequently conducted a physical inspection of the sensor and found traces of tampering, officially filing a criminal complaint with the Roissy Air Transport Gendarmerie. The charge is 'destruction of an automated data processing system.' Under French law, this offense can carry a maximum sentence of 7 years in prison and a €300,000 fine.
The profile of the account involved is similarly unconvincing. It was created only 48 hours before the first incident on April 4, 2026. The initial funds were only a few dozen dollars, transferred from a crypto exchange. It participated almost exclusively in 'Paris Weather' markets, specifically buying extremely low probability 'high temperature' options. After two successful hits, the funds were quickly moved through mixers and decentralized exchanges, making on-chain tracking significantly more difficult.
On one side is a common household hairdryer costing less than €30, and on the other is a global climate prediction market with daily trading volumes exceeding $2 million; the extreme imbalance between attack cost and potential rewards is striking.
The anomalous data was first discovered by local weather enthusiasts on the Infoclimat forum. The incident was then spread to the English-speaking world by the crypto community, with reports subsequently followed up by Le Monde, Le Figaro, and BFMTV. Polymarket has not issued any public statements on the matter and has not revoked the already paid $34,000 reward.
Rule vulnerability: why should a single sensor reading determine a six-figure prize?
The real protagonist of this incident, rather than the hairdryer, is the settlement rules of the Polymarket weather market.
Polymarket's weather markets have seen explosive growth in recent years, now boasting 173 active markets covering temperature, precipitation, hurricanes, tornadoes, earthquakes, volcanoes, and even pandemics. The mechanism used for the 'Daily Maximum Temperature in Paris' market is extremely simple, locking data sources to specific weather station readings hosted on the Wunderground website.
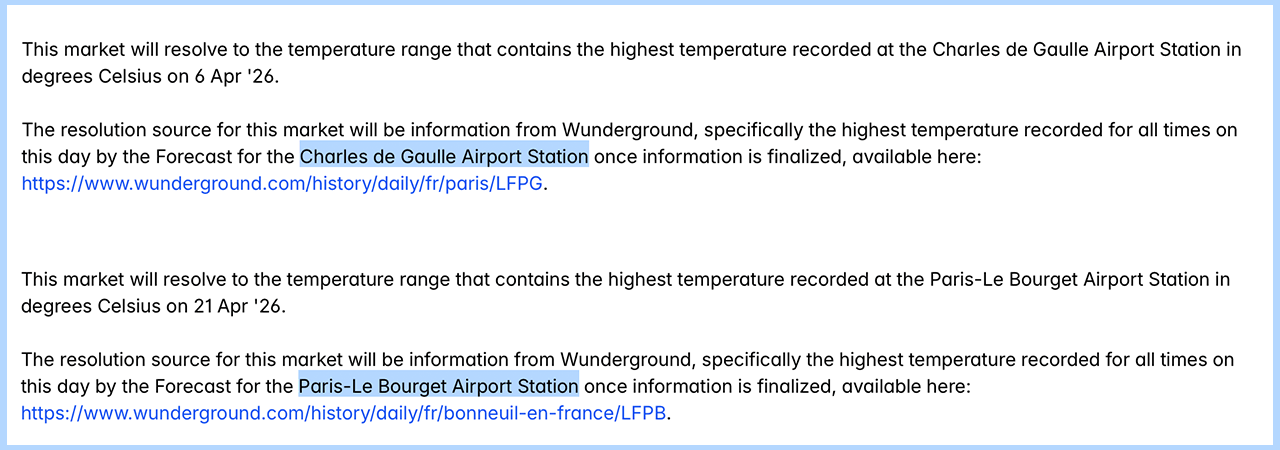
Before this incident, the site was the Charles de Gaulle Airport weather station (code LFPG), with temperatures accurate to whole degrees Celsius. Most crucially, the market settled immediately after the data was finalized and 'did not consider any subsequent data revisions.'
This last point means that even if the French meteorological agency later discovered anomalies in the data and revised the historical records, Polymarket would still pay out rewards based on the tainted original readings. The rules are clear, and the execution is unambiguous.
The vulnerabilities are clearly presented in three points:
Firstly, it's a single point of failure. The entire six-figure prize pool settlement relies entirely on a single sensor's reading. Polymarket did not design a multi-station weighting, redundancy checks, or anomaly shutdown mechanisms; the so-called 'data source' is just that metal probe by the runway at Charles de Gaulle Airport.
Secondly, there is the issue of physical accessibility. The weather station at Charles de Gaulle Airport is located near the edge of the runway, adjacent to a public area next to the road, allowing any ordinary person to approach within a few meters of the probe. This geographical detail turns the theoretical possibility of 'physical interference' into a nearly zero-cost reality.
Thirdly, the rigidity of the settlement mechanism. Post-event revisions are ineffective, meaning once an attack is successful, there is no possibility of 'reversal.' The rules guarantee the certainty of settlements while also ensuring that once manipulation is successful, it cannot be undone.
Victor, an analyst at Fibo Crypto, coined a term with technical elegance for this type of tactic: 'physical oracle attack.' Unlike past attacks targeting UMA governance votes, manipulating oracle results through large-scale token voting—known as 'digital oracle attacks'—the physical oracle attack bypasses the entire on-chain logic, directly affecting the first mile of the data pipeline—the metal probe in the real world.
On April 17, two days after the incident was exposed, Polymarket quietly made a rule change, switching the settlement data source for the Paris weather market from Charles de Gaulle Airport (LFPG) to Paris-Le Bourget Airport (LFPB). This switch came without any official announcement, no public technical explanation, and no response to the two previous manipulations that had already occurred.
Swapping out a probe is much easier than publicly admitting a vulnerability. Polymarket's weather market was initially designed to be a mirror reflecting the collective judgment of the market about the future. But when the image in the mirror is worth enough, the odds are steep enough, and the probe is easily accessible, someone will always walk by with a €30 hairdryer and blow in the desired outcome.