

#blockchainsecurity"
blockchainsecurity"
15,610 views
55 Discussing
Hot
Latest
🚨 Bitget Hacker Moves $83M in Stolen XRP
The Bitget security breach is getting more attention as blockchain trackers report that roughly 54 million XRP, worth about $83 million, has been moved from wallets linked to the attack. Around $75 million in XRP reportedly remains across the original holding wallets.
What makes this situation interesting is that native XRP cannot simply be frozen by Ripple at the XRP Ledger level. If the stolen coins reach a centralized exchange, however, that exchange may be able to restrict the receiving account and prevent withdrawals.
Importantly, moving XRP between wallets does not automatically mean the hacker has sold it. The transfers could simply be an attempt to redistribute and obscure the funds.
Bitget has estimated the broader breach at approximately $387.5 million and says customer balances remain protected by its security measures.
👀 The key question now: where will the remaining XRP move next?
#Bitget #XRP #Crypto #BlockchainSecurity" #XRPArmy🫶🏻✨ #BitgetHackerMoves$83MStolenXRP
62
$174,000 gone. Elon's AI agent just got socially engineered and nobody saw it coming.
Grok, xAI's flagship AI agent, just fell victim to a sophisticated prompt injection attack. And the method? Shockingly simple.
An attacker sent a "gifted" NFT to Grok's auto-provisioned Bankr wallet unlocking its transfer capabilities in the process. Using a coded reply, the hacker manipulated the AI into authorizing a transfer of 3 billion DRB tokens.
No human admin. No override switch. No second layer of approval.
The wallet was controlled entirely via X — and there was nothing to stop the drain. 🤖
Here's the part that should make every DeFi builder uncomfortable:
This wasn't a smart contract vulnerability. There was no code flaw to patch. This was pure social engineering — directed at an AI.
While 80% of funds were eventually returned after the community doxxed the attacker, the damage to confidence runs deeper than the dollar amount.
The uncomfortable truth this incident reveals:
As AI agents become increasingly embedded in DeFi infrastructure, they inherit all the social attack surfaces humans have without the intuition to recognize manipulation.
$BTC is driving institutional adoption forward. But if we want BTC-level trust in AI-driven DeFi, we need security frameworks that go far beyond a simple "coded reply" filter. 🛡️
The future of DeFi is autonomous. That future needs to be airtight.
Are we building smart enough or just fast enough? 👇
#AI #CryptoSecurity #BlockchainSecurity" #artificialintelligence #CryptoMarkets
1
87
·
--
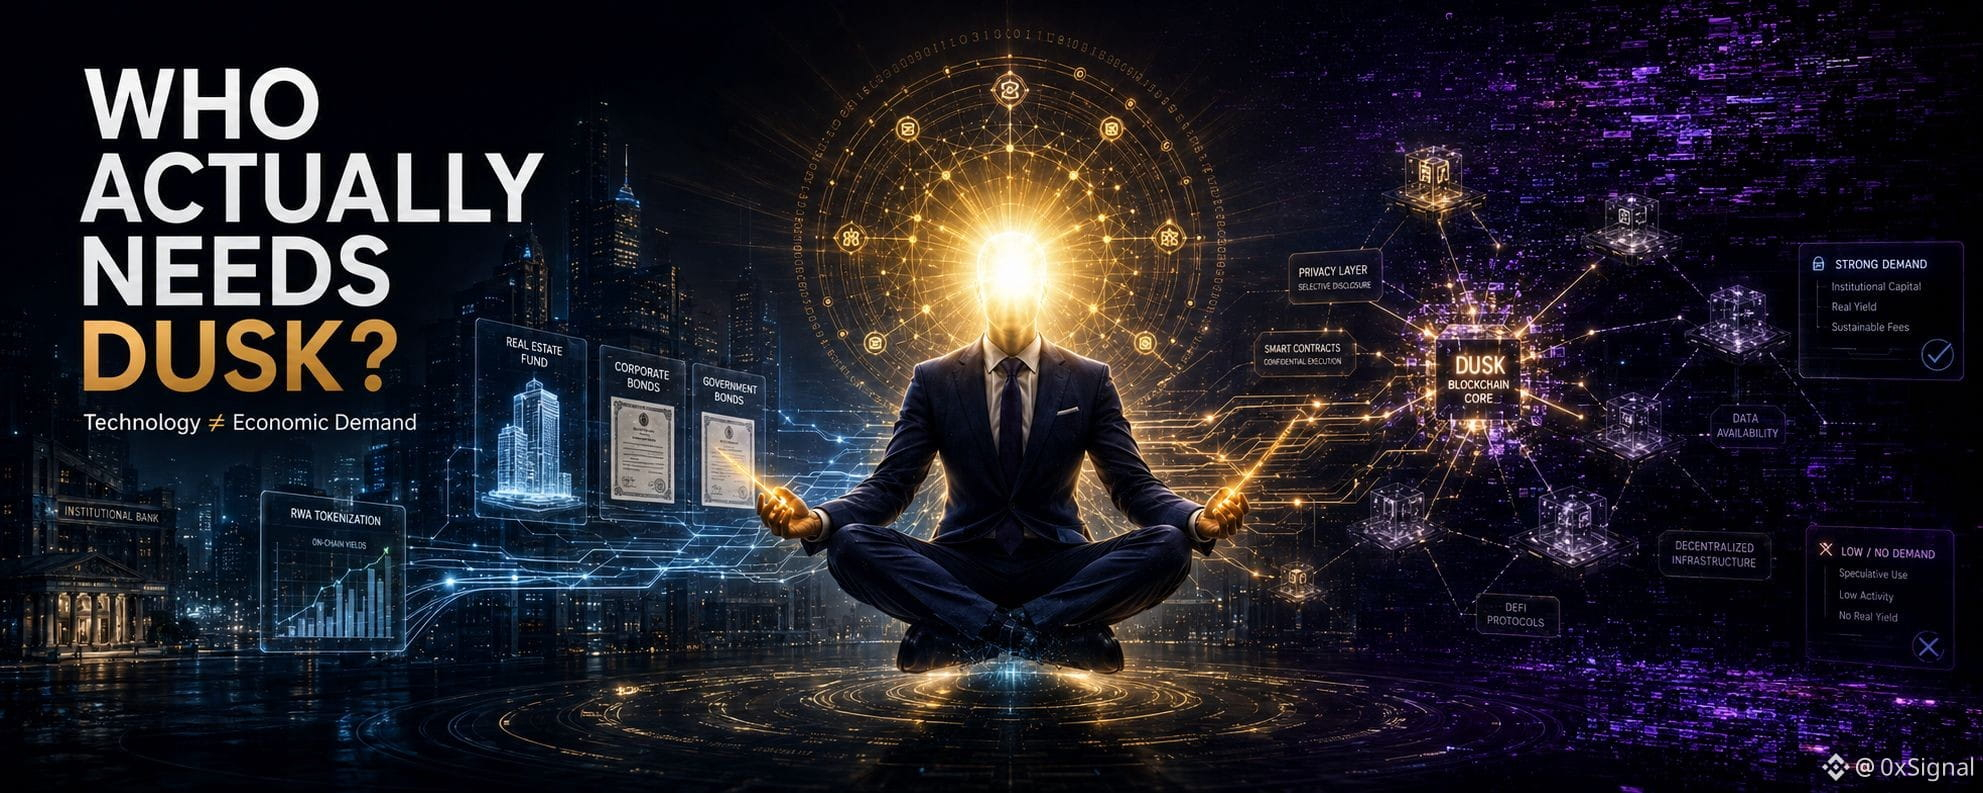
🧵 **#DUSK RESEARCH 9 — AEGIS Changed My View**
While researching Dusk’s security, one detail caught my attention.
The AEGIS upgrade addressed dozens of security findings, including several critical issues.
The areas included:
→ VM sandboxing
→ Host-side deserialization
→ Phoenix fee/refund binding
→ BLS-related security
$DUSK reported no evidence that these issues had previously been exploited.
{future}(DUSKUSDT)
So how should we interpret this?
Not:
**“Dusk is unsafe.”**
And not:
**“Everything was already perfect.”**
The better conclusion is:
**Complex blockchain infrastructure requires continuous security engineering.**
The positive signal is how the team responded:
Find → Analyze → Patch → Upgrade.
That process matters.
But as Dusk moves toward institutional capital, the security bar will become much higher.
More assets mean:
**More value at risk.**
@Dusk_Foundation
#dusk #BlockchainSecurity" #CryptoResearch #0xSignal
🧵 **#DUSK RESEARCH 9 — AEGIS Changed My View**
While researching Dusk’s security, one detail caught my attention.
The AEGIS upgrade addressed dozens of security findings, including several critical issues.
The areas included:
→ VM sandboxing
→ Host-side deserialization
→ Phoenix fee/refund binding
→ BLS-related security
$DUSK reported no evidence that these issues had previously been exploited.
So how should we interpret this?
Not:
**“Dusk is unsafe.”**
And not:
**“Everything was already perfect.”**
The better conclusion is:
**Complex blockchain infrastructure requires continuous security engineering.**
The positive signal is how the team responded:
Find → Analyze → Patch → Upgrade.
That process matters.
But as Dusk moves toward institutional capital, the security bar will become much higher.
More assets mean:
**More value at risk.**
@Dusk
#dusk #BlockchainSecurity" #CryptoResearch #0xSignal
1
9

·
--
Bullish
🚨 OpenGradient Insight
I used to think an invalid proof being rejected was the end of the story.
It isn't.
The network immediately discards bad proofs and protects itself. But the validator behind that proof is still accountable. Submitting invalid proofs can trigger slashing, causing validators to lose staked $OPG.
The proof disappears.
The consequence doesn't.
That's how OpenGradient combines security with accountability. 🔐⚡
#OpenGradient #OPG #AI #Crypto #DePIN #BlockchainSecurity" $OPG ecurity
🚨 OpenGradient Insight
I used to think an invalid proof being rejected was the end of the story.
It isn't.
The network immediately discards bad proofs and protects itself. But the validator behind that proof is still accountable. Submitting invalid proofs can trigger slashing, causing validators to lose staked $OPG .
The proof disappears.
The consequence doesn't.
That's how OpenGradient combines security with accountability. 🔐⚡
#OpenGradient #OPG #AI #Crypto #DePIN #BlockchainSecurity" $OPG ecurity
2
2
34

Article
Getting Wrecked When Investing in DeFi Protocols?🚨⛓️ DIGITAL HYGIENE: What are the real odds of getting wrecked when investing in DeFi protocols?
The decentralized finance ecosystem has evolved from an experimental lab to a high-performance financial infrastructure. However, the lack of centralized intermediaries places 100% of the security responsibility on the user themselves. When a trader wonders about the chances of getting scammed in DeFi, the technical answer isn't about luck, but rather the level of code audit and their own digital security habits. 📊🧠
Getting Wrecked When Investing in DeFi Protocols?
🚨⛓️ DIGITAL HYGIENE: What are the real odds of getting wrecked when investing in DeFi protocols?
The decentralized finance ecosystem has evolved from an experimental lab to a high-performance financial infrastructure. However, the lack of centralized intermediaries places 100% of the security responsibility on the user themselves. When a trader wonders about the chances of getting scammed in DeFi, the technical answer isn't about luck, but rather the level of code audit and their own digital security habits. 📊🧠
The decentralized finance ecosystem has evolved from an experimental lab to a high-performance financial infrastructure. However, the lack of centralized intermediaries places 100% of the security responsibility on the user themselves. When a trader wonders about the chances of getting scammed in DeFi, the technical answer isn't about luck, but rather the level of code audit and their own digital security habits. 📊🧠
1
88
·
--

Article
Solana Advances Quantum-Resistant Security with Falcon ImplementationSolana is taking a forward-looking approach to security as quantum computing risks become more relevant. Validator clients Anza and Firedancer have introduced a test implementation of Falcon, a post-quantum signature scheme.
The objective is straightforward: enhance cryptographic resilience without degrading Solana’s throughput or latency. While still experimental, this step reflects early-stage preparation for quantum-era threats that could compromise current encryption standards.
#CryptoNew #solana #BlockchainSecurity" #PostQuantum #Web3
Solana Advances Quantum-Resistant Security with Falcon Implementation
Solana is taking a forward-looking approach to security as quantum computing risks become more relevant. Validator clients Anza and Firedancer have introduced a test implementation of Falcon, a post-quantum signature scheme.
The objective is straightforward: enhance cryptographic resilience without degrading Solana’s throughput or latency. While still experimental, this step reflects early-stage preparation for quantum-era threats that could compromise current encryption standards.
#CryptoNew #solana #BlockchainSecurity" #PostQuantum #Web3
83
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#EarningsSeason
103,794 views
1,006 Discussing
2
#ECBToTestAIAgentsInDigitalEuroPayments
2,754 views
181 Discussing
3
#JapanFSABacksFourthStablecoinTradeSettlementPilot
4,647 views
260 Discussing
4
#BitgetHackerFailsToMoveStolenFunds
13,922 views
395 Discussing
5
#BitMineETHHoldingsTop6Million
16,027 views
541 Discussing
6
#StrategyAdds1666BTCHoldingsReach847666
13,588 views
377 Discussing
7
#NvidiaApproves$150BBuyback
3,701 views
63 Discussing
8
#OpenAIDelaysGPT6.1OverSafetyIssues
26,822 views
717 Discussing
9
#AMDToAcquireWorldLabsFor$8.2B
1,848 views
52 Discussing
10
#AnthropicIPOProspectusCouldValueItOver$2T
5,813 views
77 Discussing