
#ledger
ledger
970,092 views
1,523 Discussing
Hot
Latest
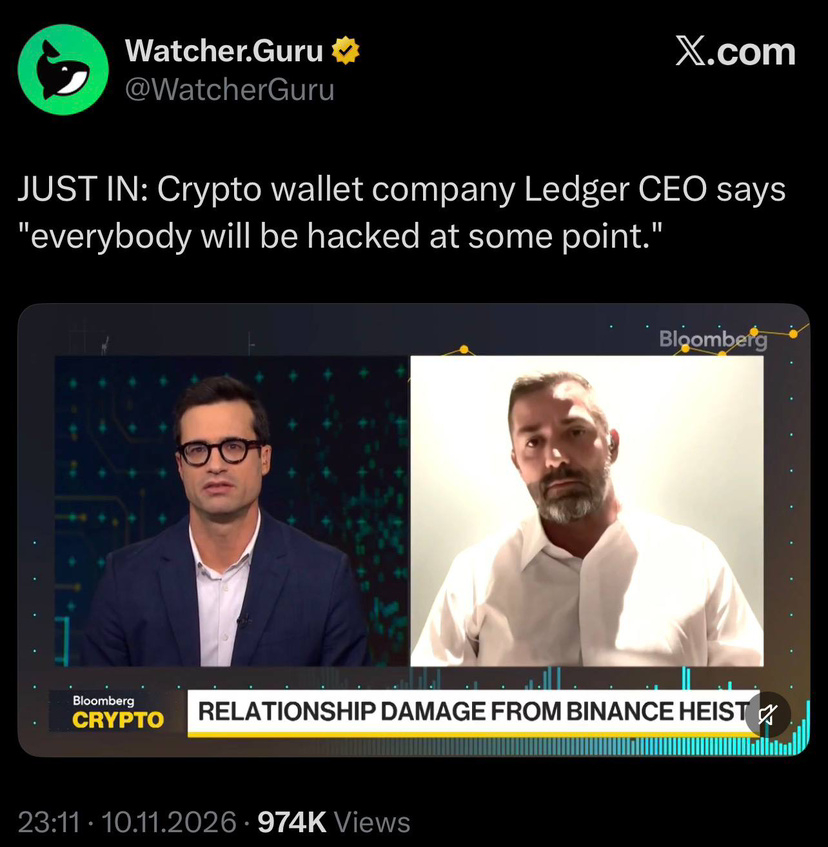
🔐 Ledger CEO: “Sooner or later, everyone will become a victim of a hack.”
A blunt reminder that in crypto, security is never something to ignore.
$BTC #Ledger #CryptoSecurity #Crypto
🔐 Ledger CEO: “Sooner or later, everyone will become a victim of a hack.”
A blunt reminder that in crypto, security is never something to ignore.
$BTC #Ledger #CryptoSecurity #Crypto
A blunt reminder that in crypto, security is never something to ignore.
$BTC #Ledger #CryptoSecurity #Crypto
2
86


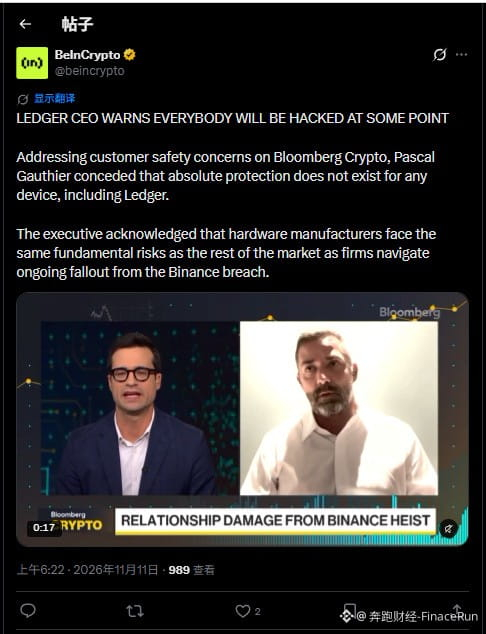
Ledger CEO: Hardware wallets cannot provide absolute security; the industry faces shared risk challenges
November 11 — According to a post by BeInCrypto, Ledger CEO Pascal Gauthier recently admitted on Bloomberg Crypto that no device, including Ledger hardware wallets, can provide absolute security.
His remarks come as the Binance hacking incident continues to reverberate across the cryptocurrency industry and users’ concerns about hardware wallet security continue to grow.
He emphasized that as the market continues to absorb the ripple effects of the Binance hack, hardware manufacturers, like other market participants, face the same fundamental security risks, and no one is immune.
As a leading global hardware wallet manufacturer, Ledger CEO’s remarks may seem candid and pragmatic, but look more like a carefully orchestrated shift in risk and attention. They also challenge some users’ ingrained belief that hardware wallets are “absolutely secure.”
In summary, Ledger CEO’s remarks not only reflect the company’s transparency in the face of a crisis, but also highlight the real gap between the hardware wallet industry’s “security promises” and its actual protective capabilities.
However, some market observers argue that Ledger has consistently made security its core selling point, yet now claims that absolute protection is impossible. In effect, they say, this lowers the company’s security obligations and user expectations while giving it an explanation to fall back on in the event of a potential security incident.
Furthermore, hardware wallet manufacturers should remain focused on improving product security, rather than instilling in users the idea that attacks are “difficult to avoid.”
#Ledger #硬件钱包
Ledger CEO: Hardware wallets cannot provide absolute security; the industry faces shared risk challenges
November 11 — According to a post by BeInCrypto, Ledger CEO Pascal Gauthier recently admitted on Bloomberg Crypto that no device, including Ledger hardware wallets, can provide absolute security.
His remarks come as the Binance hacking incident continues to reverberate across the cryptocurrency industry and users’ concerns about hardware wallet security continue to grow.
He emphasized that as the market continues to absorb the ripple effects of the Binance hack, hardware manufacturers, like other market participants, face the same fundamental security risks, and no one is immune.
As a leading global hardware wallet manufacturer, Ledger CEO’s remarks may seem candid and pragmatic, but look more like a carefully orchestrated shift in risk and attention. They also challenge some users’ ingrained belief that hardware wallets are “absolutely secure.”
In summary, Ledger CEO’s remarks not only reflect the company’s transparency in the face of a crisis, but also highlight the real gap between the hardware wallet industry’s “security promises” and its actual protective capabilities.
However, some market observers argue that Ledger has consistently made security its core selling point, yet now claims that absolute protection is impossible. In effect, they say, this lowers the company’s security obligations and user expectations while giving it an explanation to fall back on in the event of a potential security incident.
Furthermore, hardware wallet manufacturers should remain focused on improving product security, rather than instilling in users the idea that attacks are “difficult to avoid.”
#Ledger #硬件钱包
November 11 — According to a post by BeInCrypto, Ledger CEO Pascal Gauthier recently admitted on Bloomberg Crypto that no device, including Ledger hardware wallets, can provide absolute security.
His remarks come as the Binance hacking incident continues to reverberate across the cryptocurrency industry and users’ concerns about hardware wallet security continue to grow.
He emphasized that as the market continues to absorb the ripple effects of the Binance hack, hardware manufacturers, like other market participants, face the same fundamental security risks, and no one is immune.
As a leading global hardware wallet manufacturer, Ledger CEO’s remarks may seem candid and pragmatic, but look more like a carefully orchestrated shift in risk and attention. They also challenge some users’ ingrained belief that hardware wallets are “absolutely secure.”
In summary, Ledger CEO’s remarks not only reflect the company’s transparency in the face of a crisis, but also highlight the real gap between the hardware wallet industry’s “security promises” and its actual protective capabilities.
However, some market observers argue that Ledger has consistently made security its core selling point, yet now claims that absolute protection is impossible. In effect, they say, this lowers the company’s security obligations and user expectations while giving it an explanation to fall back on in the event of a potential security incident.
Furthermore, hardware wallet manufacturers should remain focused on improving product security, rather than instilling in users the idea that attacks are “difficult to avoid.”
#Ledger #硬件钱包
1
3.4k
#LedgerLeaksEverySignature
🚨 LEDGER ACCUSED OF "EAVESDROPPING" ON EVERY TRANSACTION SIGNATURE
Hardware wallet users, listen up: the Ambire wallet has just uncovered a toolkit showing that Ledger has been sending details of every signature to its servers since May, including the receiving address, device model, and software version. Ledger says this is how Clear Signing works and that the company does not store the data; SlowMist confirmed that this mechanism collects it by default. It’s even more concerning because last month, Ledger wallets purchased through Southeast Asian resellers were found to have been fitted with unusual components that drained all the funds. Bitcoin is still hovering around $74,492.
Biggest perpetual market moves today: $ZEC 998 dollars, $ICP 2,61 dollars, $ZRO 1,60 dollars
#Ledger #ViCung #Security
#LedgerLeaksEverySignature
🚨 LEDGER ACCUSED OF "EAVESDROPPING" ON EVERY TRANSACTION SIGNATURE
Hardware wallet users, listen up: the Ambire wallet has just uncovered a toolkit showing that Ledger has been sending details of every signature to its servers since May, including the receiving address, device model, and software version. Ledger says this is how Clear Signing works and that the company does not store the data; SlowMist confirmed that this mechanism collects it by default. It’s even more concerning because last month, Ledger wallets purchased through Southeast Asian resellers were found to have been fitted with unusual components that drained all the funds. Bitcoin is still hovering around $74,492.
Biggest perpetual market moves today: $ZEC 998 dollars, $ICP 2,61 dollars, $ZRO 1,60 dollars
#Ledger #ViCung #Security
🚨 LEDGER ACCUSED OF "EAVESDROPPING" ON EVERY TRANSACTION SIGNATURE
Hardware wallet users, listen up: the Ambire wallet has just uncovered a toolkit showing that Ledger has been sending details of every signature to its servers since May, including the receiving address, device model, and software version. Ledger says this is how Clear Signing works and that the company does not store the data; SlowMist confirmed that this mechanism collects it by default. It’s even more concerning because last month, Ledger wallets purchased through Southeast Asian resellers were found to have been fitted with unusual components that drained all the funds. Bitcoin is still hovering around $74,492.
Biggest perpetual market moves today: $ZEC 998 dollars, $ICP 2,61 dollars, $ZRO 1,60 dollars
#Ledger #ViCung #Security
8

·
--
【Market Update】Ledger developer kit reports every signature by default
An Ambire developer disclosed on November 10 that the Ledger developer kit reports every signature by default, including the network, destination address, device firmware, app version, and whether it was a blind signature. This is enabled by default starting with v1.16. Ledger says this is required for Clear Signing; the data is not stored, and the code is in the SDK, not the firmware. Signature reporting enabled by default—do you accept this?
$BTC $ETH $SOL
#币安广场 #Ledger #Wallet Security
(Source: Unchained)
⚠️Risk Warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risks; please exercise caution.
【Market Update】Ledger developer kit reports every signature by default
An Ambire developer disclosed on November 10 that the Ledger developer kit reports every signature by default, including the network, destination address, device firmware, app version, and whether it was a blind signature. This is enabled by default starting with v1.16. Ledger says this is required for Clear Signing; the data is not stored, and the code is in the SDK, not the firmware. Signature reporting enabled by default—do you accept this?
$BTC $ETH $SOL
#币安广场 #Ledger #Wallet Security
(Source: Unchained)
⚠️Risk Warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risks; please exercise caution.
An Ambire developer disclosed on November 10 that the Ledger developer kit reports every signature by default, including the network, destination address, device firmware, app version, and whether it was a blind signature. This is enabled by default starting with v1.16. Ledger says this is required for Clear Signing; the data is not stored, and the code is in the SDK, not the firmware. Signature reporting enabled by default—do you accept this?
$BTC $ETH $SOL
#币安广场 #Ledger #Wallet Security
(Source: Unchained)
⚠️Risk Warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risks; please exercise caution.
21

·
--
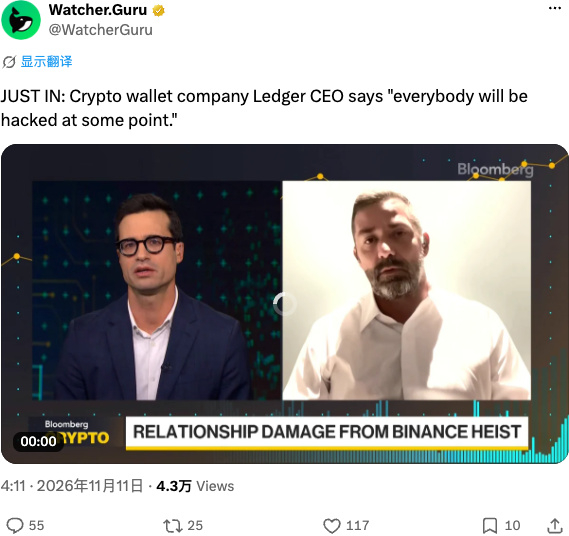
Ledger CEO bluntly warns: No one is immune to hacks. Don’t think buying a cold wallet means you’re safe—there’s no such thing as absolute security in crypto. The more secure you think you are, the more likely you are to get burned.
$BTC #Ledger
Ledger CEO bluntly warns: No one is immune to hacks. Don’t think buying a cold wallet means you’re safe—there’s no such thing as absolute security in crypto. The more secure you think you are, the more likely you are to get burned.
$BTC #Ledger
$BTC #Ledger
282

Ledger’s CEO just said, "Everyone will get hacked sooner or later."
That’s true, but it hits differently coming from someone who sells hardware wallets. Fear is already the best-selling product in this industry. First they tell you everyone will get hacked, and you can guess what comes next.
Let’s talk facts. This year, North Korean hackers were behind the bulk of on-chain thefts—over 80%, according to TRM. They rely on social engineering, phishing, and lying low for weeks before striking, not on cracking that little screen of yours. In the Binance case involving more than $6.3 billion, a big chunk of the money is still being slowly laundered through THORChain and Chainflip. Will buying a cold wallet protect you from that? To some extent—but only if you don’t sign things blindly, click random links, or take photos of your seed phrase.
And don’t forget the device-tampering scam in Singapore a while back. People had just been scared all over again, and then a bunch of accounts suddenly started pushing other wallets with the exact same talking points. Everyone wants a piece of the security-anxiety business.
My take: a cold wallet is a tool, not a talisman. Nine times out of ten, people get hacked because of human error, not the chip. The CEO’s most honest version of that quote would be: Most people will get hacked because they can’t keep their hands off things, and then they’ll come buy our products.
#钱包安全 #Ledger
Ledger’s CEO just said, "Everyone will get hacked sooner or later."
That’s true, but it hits differently coming from someone who sells hardware wallets. Fear is already the best-selling product in this industry. First they tell you everyone will get hacked, and you can guess what comes next.
Let’s talk facts. This year, North Korean hackers were behind the bulk of on-chain thefts—over 80%, according to TRM. They rely on social engineering, phishing, and lying low for weeks before striking, not on cracking that little screen of yours. In the Binance case involving more than $6.3 billion, a big chunk of the money is still being slowly laundered through THORChain and Chainflip. Will buying a cold wallet protect you from that? To some extent—but only if you don’t sign things blindly, click random links, or take photos of your seed phrase.
And don’t forget the device-tampering scam in Singapore a while back. People had just been scared all over again, and then a bunch of accounts suddenly started pushing other wallets with the exact same talking points. Everyone wants a piece of the security-anxiety business.
My take: a cold wallet is a tool, not a talisman. Nine times out of ten, people get hacked because of human error, not the chip. The CEO’s most honest version of that quote would be: Most people will get hacked because they can’t keep their hands off things, and then they’ll come buy our products.
#钱包安全 #Ledger
That’s true, but it hits differently coming from someone who sells hardware wallets. Fear is already the best-selling product in this industry. First they tell you everyone will get hacked, and you can guess what comes next.
Let’s talk facts. This year, North Korean hackers were behind the bulk of on-chain thefts—over 80%, according to TRM. They rely on social engineering, phishing, and lying low for weeks before striking, not on cracking that little screen of yours. In the Binance case involving more than $6.3 billion, a big chunk of the money is still being slowly laundered through THORChain and Chainflip. Will buying a cold wallet protect you from that? To some extent—but only if you don’t sign things blindly, click random links, or take photos of your seed phrase.
And don’t forget the device-tampering scam in Singapore a while back. People had just been scared all over again, and then a bunch of accounts suddenly started pushing other wallets with the exact same talking points. Everyone wants a piece of the security-anxiety business.
My take: a cold wallet is a tool, not a talisman. Nine times out of ten, people get hacked because of human error, not the chip. The CEO’s most honest version of that quote would be: Most people will get hacked because they can’t keep their hands off things, and then they’ll come buy our products.
#钱包安全 #Ledger
7

·
--
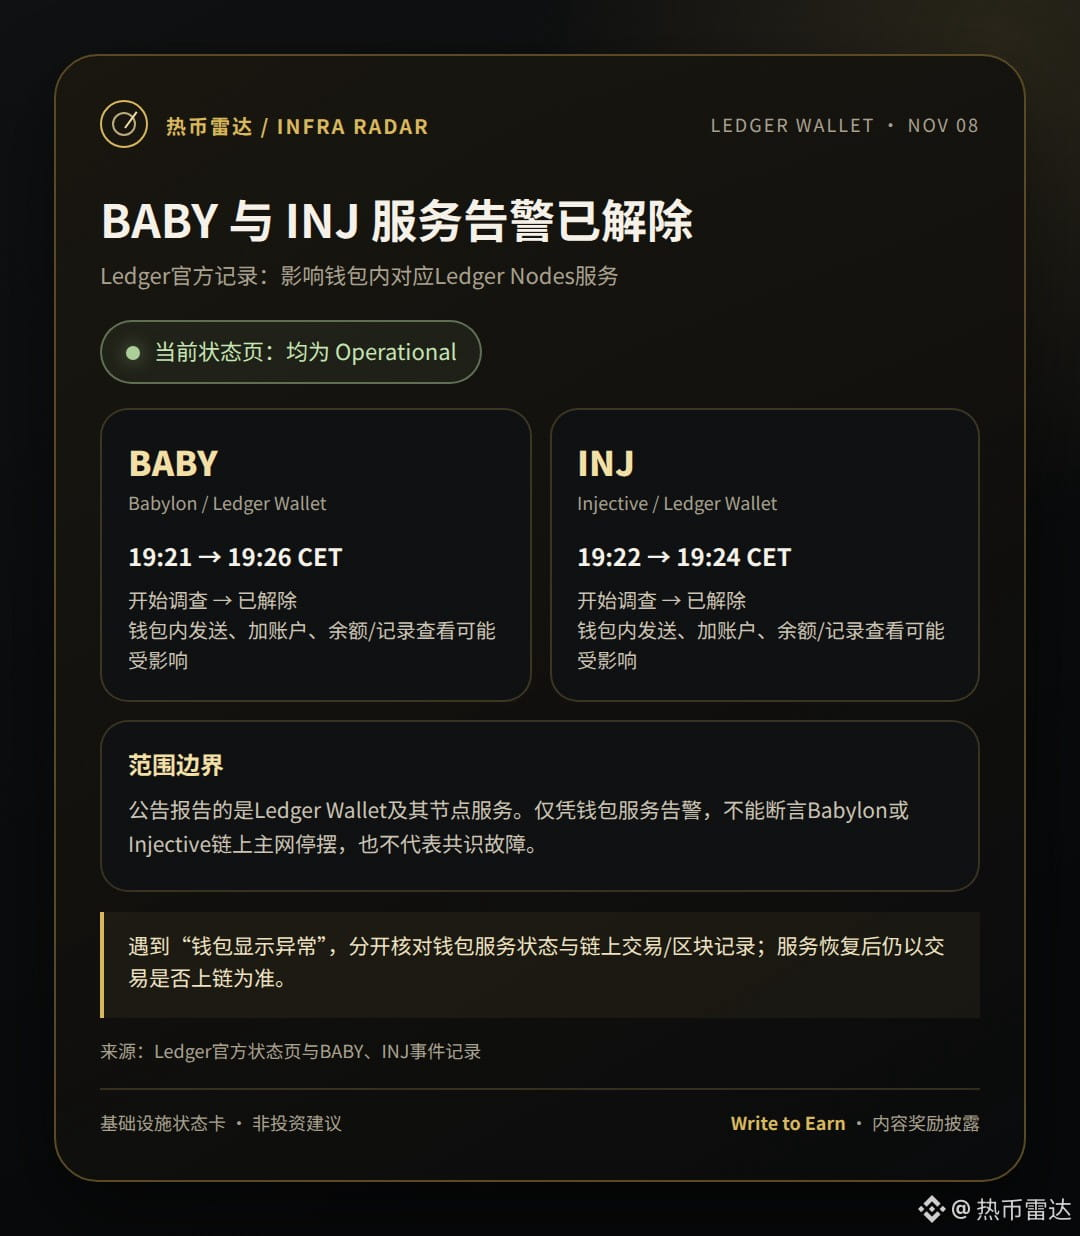
Ledger Wallet’s BABY and INJ node service alerts have both been resolved. The impact was limited to sending, adding accounts, and viewing balances/history in the wallet; this does not mean either mainnet was down.
• Babylon: investigation began at 19:21 CET on November 8; resolved at 19:26.
• Injective: investigation began at 19:22; resolved at 19:24. Both are currently listed as Operational on Ledger’s status page.
For alerts like these, distinguish wallet/node services from on-chain consensus, then check whether the transaction was confirmed on-chain. When you encounter a wallet issue, do you check service status first or look up the on-chain record?
Sources: Ledger official status page https://status.ledger.com/ |BABY incident https://status.ledger.com/incidents/xz4vbjnn02f8 |INJ incident https://status.ledger.com/incidents/krbsn5zxcx2n
Disclosure: Participating in Binance Square Write to Earn; may receive content rewards. Eligibility and amount are subject to the platform’s rules and are not guaranteed. Not investment advice.
$BABY $INJ #Ledger
Ledger Wallet’s BABY and INJ node service alerts have both been resolved. The impact was limited to sending, adding accounts, and viewing balances/history in the wallet; this does not mean either mainnet was down.
• Babylon: investigation began at 19:21 CET on November 8; resolved at 19:26.
• Injective: investigation began at 19:22; resolved at 19:24. Both are currently listed as Operational on Ledger’s status page.
For alerts like these, distinguish wallet/node services from on-chain consensus, then check whether the transaction was confirmed on-chain. When you encounter a wallet issue, do you check service status first or look up the on-chain record?
Sources: Ledger official status page https://status.ledger.com/ |BABY incident https://status.ledger.com/incidents/xz4vbjnn02f8 |INJ incident https://status.ledger.com/incidents/krbsn5zxcx2n
Disclosure: Participating in Binance Square Write to Earn; may receive content rewards. Eligibility and amount are subject to the platform’s rules and are not guaranteed. Not investment advice.
$BABY $INJ #Ledger
• Babylon: investigation began at 19:21 CET on November 8; resolved at 19:26.
• Injective: investigation began at 19:22; resolved at 19:24. Both are currently listed as Operational on Ledger’s status page.
For alerts like these, distinguish wallet/node services from on-chain consensus, then check whether the transaction was confirmed on-chain. When you encounter a wallet issue, do you check service status first or look up the on-chain record?
Sources: Ledger official status page https://status.ledger.com/ |BABY incident https://status.ledger.com/incidents/xz4vbjnn02f8 |INJ incident https://status.ledger.com/incidents/krbsn5zxcx2n
Disclosure: Participating in Binance Square Write to Earn; may receive content rewards. Eligibility and amount are subject to the platform’s rules and are not guaranteed. Not investment advice.
$BABY $INJ #Ledger
312
Article
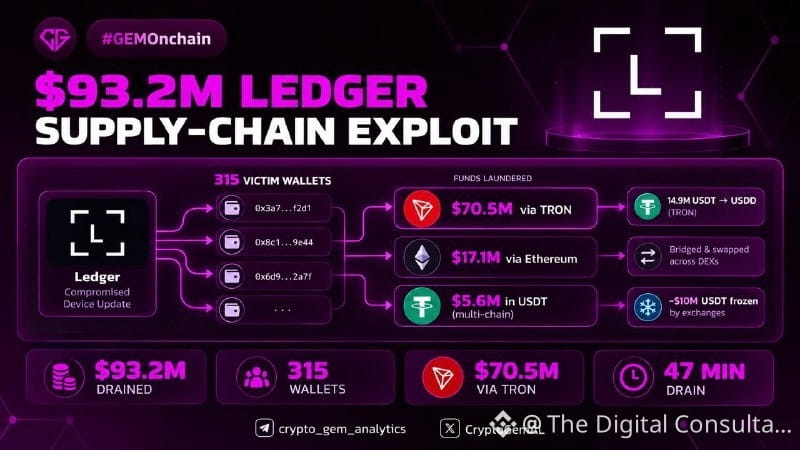
315 wallets drained in 47 minutes: Is the problem with Ledger’s manufacturing?In just 47 minutes, 315 wallets were drained across six networks, with a total of $93.2 million withdrawn, while $14.9 million in USDT was likely converted to USDD to avoid being frozen by the issuer. $ETH
Ledger is investigating Nano X devices suspected of being sold by a Southeast Asian distributor called CryptoBilis. They may have contained an additional chip that captured the recovery phrase during setup.
315 wallets drained in 47 minutes: Is the problem with Ledger’s manufacturing?
In just 47 minutes, 315 wallets were drained across six networks, with a total of $93.2 million withdrawn, while $14.9 million in USDT was likely converted to USDD to avoid being frozen by the issuer. $ETH
Ledger is investigating Nano X devices suspected of being sold by a Southeast Asian distributor called CryptoBilis. They may have contained an additional chip that captured the recovery phrase during setup.
Ledger is investigating Nano X devices suspected of being sold by a Southeast Asian distributor called CryptoBilis. They may have contained an additional chip that captured the recovery phrase during setup.
37
·
--
Verified
Ledger now lets you connect directly to #Morpho from your hardware wallet.
You no longer need a browser extension or an intermediary wallet. Connect your #Ledger via USB or Bluetooth, clearly see on the screen what you’re signing—such as deposits, loans, or vaults—and your keys stay on the device.
Morpho is the first lending protocol to join this direct access program. This really helps address the blind signing issue that’s such a pain in DeFi.
If you use Morpho or are putting money into lending with self-custody, it’s worth giving it a try.
Always DYOR and proceed at your own risk, but the experience feels much smoother.
Ledger now lets you connect directly to #Morpho from your hardware wallet.
You no longer need a browser extension or an intermediary wallet. Connect your #Ledger via USB or Bluetooth, clearly see on the screen what you’re signing—such as deposits, loans, or vaults—and your keys stay on the device.
Morpho is the first lending protocol to join this direct access program. This really helps address the blind signing issue that’s such a pain in DeFi.
If you use Morpho or are putting money into lending with self-custody, it’s worth giving it a try.
Always DYOR and proceed at your own risk, but the experience feels much smoother.
You no longer need a browser extension or an intermediary wallet. Connect your #Ledger via USB or Bluetooth, clearly see on the screen what you’re signing—such as deposits, loans, or vaults—and your keys stay on the device.
Morpho is the first lending protocol to join this direct access program. This really helps address the blind signing issue that’s such a pain in DeFi.
If you use Morpho or are putting money into lending with self-custody, it’s worth giving it a try.
Always DYOR and proceed at your own risk, but the experience feels much smoother.
1
518

·
--
A caller claiming to be a police officer, plus a genuine Ledger email—this combination made the news today
Today, CoinEdition reported on an emerging scam that takes things a step further than the usual fake links. Someone first gets a call from a person claiming to be a detective. The caller says that during an investigation they found the person’s passport, ID, passwords, or wallet recovery information. They may also ask where the person has been recently and whether they use cryptocurrency, then say they’ll have an expert check whether the person’s wallet has been compromised.
What makes the call seem credible is an automated email that arrives right afterward from Ledger’s official system. The scammer opens a support ticket in Ledger’s customer service system using your email address, and the system automatically sends you a genuine email in response. The person on the phone uses this real email as proof, saying, “See? The official company emailed you. I’m the real deal.” One person who answered the call noticed that the caller ID looked like it was from a local police station, so they called to verify independently. They were told that no officer with that name worked there. Some people then received a second call, this time from someone claiming to be with Ledger.
Let’s be clear about one thing first. So far, all of this comes from users’ accounts on forums. There has been no official confirmation of the number of victims or the amount of money lost, so we shouldn’t present it as a proven major case. But retail investors should remember the method itself, because it exploits the way we usually judge whether something is genuine: a real email combined with a genuine-looking caller ID can easily make people lower their guard.
Ledger’s position is stated clearly in the report: it does not offer phone support and will never call to ask for your 24-word recovery phrase. Those 24 words are the scammers’ real target. They may try to get you to read them aloud over the phone, or direct you to a convincing-looking diagnostic or recovery page and ask you to enter them there. Anyone who gets those 24 words can drain the wallet from any device.
There are three things retail investors can do right away. First, if an unsolicited call mentions an investigation, an exposed wallet, or an urgent security check, hang up. Don’t follow links they provide or accept a transfer to a so-called support agent. Second, if you want to verify the claim, use another device to look it up yourself. Contact Ledger through the channels listed on its official website, or find the local police station’s publicly listed contact details independently. Don’t use the numbers or links provided during the call. Third, if you’ve already entered your recovery phrase on a webpage or read it aloud to someone, assume the wallet has been compromised. Use a clean device to create a new wallet with a new recovery phrase, then move any remaining funds as soon as possible. If you suspect someone is impersonating Ledger, you can report it to phishing@ledger.fr.
A genuine email doesn’t mean the call is genuine. Scammers can borrow credible-looking evidence, and that’s even more concerning than fake links alone.
Have you ever received a call from someone claiming to be an official or a police officer who immediately started talking about your wallet? How did you handle it?
— Web3 Retail Investor Xiao Kai
This article expresses personal opinions only and does not constitute investment advice. Its factual sources are CoinEdition’s November 4 report, the user accounts cited in it, and Ledger’s official position.
#Ledger #防骗 #助记词 #PhoneScam
A caller claiming to be a police officer, plus a genuine Ledger email—this combination made the news today
Today, CoinEdition reported on an emerging scam that takes things a step further than the usual fake links. Someone first gets a call from a person claiming to be a detective. The caller says that during an investigation they found the person’s passport, ID, passwords, or wallet recovery information. They may also ask where the person has been recently and whether they use cryptocurrency, then say they’ll have an expert check whether the person’s wallet has been compromised.
What makes the call seem credible is an automated email that arrives right afterward from Ledger’s official system. The scammer opens a support ticket in Ledger’s customer service system using your email address, and the system automatically sends you a genuine email in response. The person on the phone uses this real email as proof, saying, “See? The official company emailed you. I’m the real deal.” One person who answered the call noticed that the caller ID looked like it was from a local police station, so they called to verify independently. They were told that no officer with that name worked there. Some people then received a second call, this time from someone claiming to be with Ledger.
Let’s be clear about one thing first. So far, all of this comes from users’ accounts on forums. There has been no official confirmation of the number of victims or the amount of money lost, so we shouldn’t present it as a proven major case. But retail investors should remember the method itself, because it exploits the way we usually judge whether something is genuine: a real email combined with a genuine-looking caller ID can easily make people lower their guard.
Ledger’s position is stated clearly in the report: it does not offer phone support and will never call to ask for your 24-word recovery phrase. Those 24 words are the scammers’ real target. They may try to get you to read them aloud over the phone, or direct you to a convincing-looking diagnostic or recovery page and ask you to enter them there. Anyone who gets those 24 words can drain the wallet from any device.
There are three things retail investors can do right away. First, if an unsolicited call mentions an investigation, an exposed wallet, or an urgent security check, hang up. Don’t follow links they provide or accept a transfer to a so-called support agent. Second, if you want to verify the claim, use another device to look it up yourself. Contact Ledger through the channels listed on its official website, or find the local police station’s publicly listed contact details independently. Don’t use the numbers or links provided during the call. Third, if you’ve already entered your recovery phrase on a webpage or read it aloud to someone, assume the wallet has been compromised. Use a clean device to create a new wallet with a new recovery phrase, then move any remaining funds as soon as possible. If you suspect someone is impersonating Ledger, you can report it to phishing@ledger.fr.
A genuine email doesn’t mean the call is genuine. Scammers can borrow credible-looking evidence, and that’s even more concerning than fake links alone.
Have you ever received a call from someone claiming to be an official or a police officer who immediately started talking about your wallet? How did you handle it?
— Web3 Retail Investor Xiao Kai
This article expresses personal opinions only and does not constitute investment advice. Its factual sources are CoinEdition’s November 4 report, the user accounts cited in it, and Ledger’s official position.
#Ledger #防骗 #助记词 #PhoneScam
Today, CoinEdition reported on an emerging scam that takes things a step further than the usual fake links. Someone first gets a call from a person claiming to be a detective. The caller says that during an investigation they found the person’s passport, ID, passwords, or wallet recovery information. They may also ask where the person has been recently and whether they use cryptocurrency, then say they’ll have an expert check whether the person’s wallet has been compromised.
What makes the call seem credible is an automated email that arrives right afterward from Ledger’s official system. The scammer opens a support ticket in Ledger’s customer service system using your email address, and the system automatically sends you a genuine email in response. The person on the phone uses this real email as proof, saying, “See? The official company emailed you. I’m the real deal.” One person who answered the call noticed that the caller ID looked like it was from a local police station, so they called to verify independently. They were told that no officer with that name worked there. Some people then received a second call, this time from someone claiming to be with Ledger.
Let’s be clear about one thing first. So far, all of this comes from users’ accounts on forums. There has been no official confirmation of the number of victims or the amount of money lost, so we shouldn’t present it as a proven major case. But retail investors should remember the method itself, because it exploits the way we usually judge whether something is genuine: a real email combined with a genuine-looking caller ID can easily make people lower their guard.
Ledger’s position is stated clearly in the report: it does not offer phone support and will never call to ask for your 24-word recovery phrase. Those 24 words are the scammers’ real target. They may try to get you to read them aloud over the phone, or direct you to a convincing-looking diagnostic or recovery page and ask you to enter them there. Anyone who gets those 24 words can drain the wallet from any device.
There are three things retail investors can do right away. First, if an unsolicited call mentions an investigation, an exposed wallet, or an urgent security check, hang up. Don’t follow links they provide or accept a transfer to a so-called support agent. Second, if you want to verify the claim, use another device to look it up yourself. Contact Ledger through the channels listed on its official website, or find the local police station’s publicly listed contact details independently. Don’t use the numbers or links provided during the call. Third, if you’ve already entered your recovery phrase on a webpage or read it aloud to someone, assume the wallet has been compromised. Use a clean device to create a new wallet with a new recovery phrase, then move any remaining funds as soon as possible. If you suspect someone is impersonating Ledger, you can report it to phishing@ledger.fr.
A genuine email doesn’t mean the call is genuine. Scammers can borrow credible-looking evidence, and that’s even more concerning than fake links alone.
Have you ever received a call from someone claiming to be an official or a police officer who immediately started talking about your wallet? How did you handle it?
— Web3 Retail Investor Xiao Kai
This article expresses personal opinions only and does not constitute investment advice. Its factual sources are CoinEdition’s November 4 report, the user accounts cited in it, and Ledger’s official position.
#Ledger #防骗 #助记词 #PhoneScam
60

Singapore discovers tampered Ledger devices on the market since September; South Korea delays crypto tax again
- Singapore police confirm: Tampered Ledger devices have appeared on the market since September 10.
- This information was made public only a month later.
- South Korean lawmakers are expected to delay the crypto tax law once again.
#BinanceSquare #CryptoNews #Ledger #BTC #ETH
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
Singapore discovers tampered Ledger devices on the market since September; South Korea delays crypto tax again
- Singapore police confirm: Tampered Ledger devices have appeared on the market since September 10.
- This information was made public only a month later.
- South Korean lawmakers are expected to delay the crypto tax law once again.
#BinanceSquare #CryptoNews #Ledger #BTC #ETH
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
- Singapore police confirm: Tampered Ledger devices have appeared on the market since September 10.
- This information was made public only a month later.
- South Korean lawmakers are expected to delay the crypto tax law once again.
#BinanceSquare #CryptoNews #Ledger #BTC #ETH
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
192
·
--
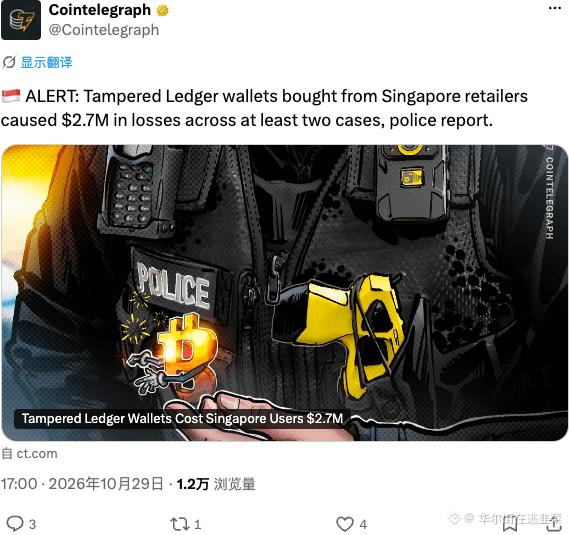
Singapore police report that tampered Ledger wallets purchased at retail stores caused two losses totaling $2.7 million. Now you have to watch out for hardware wallets being swapped out when you buy one—these days, even “air-gapping” is becoming an arms race. Offline channels are full of pitfalls; don’t cut corners. Security is what matters 🚨
#Ledger #硬件钱包 #Singapore
Singapore police report that tampered Ledger wallets purchased at retail stores caused two losses totaling $2.7 million. Now you have to watch out for hardware wallets being swapped out when you buy one—these days, even “air-gapping” is becoming an arms race. Offline channels are full of pitfalls; don’t cut corners. Security is what matters 🚨
#Ledger #硬件钱包 #Singapore
#Ledger #硬件钱包 #Singapore
20

·
--
Bullish
S$3.5 million is how much people lost on Ledger wallets bought at regular stores in Singapore
Police say there have been at least two cases since September 10. And what gets me isn’t even the amount, but the shelf:
- Retail stores in Singapore. “A new box off the shelf” doesn’t guarantee anything anymore
- The implant, as Ledger itself explains, reads 24 words from the screen during setup and sends them over LTE. You do everything right—and game over
- On October 13, Ledger halted sales through resellers in seven countries in the region. Too late for these two
And yes, S$ is Singapore dollars, not USD. Headlines miss that
The police advice is simple: don’t enter your phrase on a suspicious device, and if it might have leaked—get a new wallet, a new phrase, and use a trusted device. Basically, now you have to ask where it was bought before even opening the box
I don’t have a position here. I’m watching to see whether the amount goes above S$3.5 million; when there’s an update, I’ll break it down. Follow if you hold crypto in cold storage
#Ledger #CryptoSecurity
S$3.5 million is how much people lost on Ledger wallets bought at regular stores in Singapore
Police say there have been at least two cases since September 10. And what gets me isn’t even the amount, but the shelf:
- Retail stores in Singapore. “A new box off the shelf” doesn’t guarantee anything anymore
- The implant, as Ledger itself explains, reads 24 words from the screen during setup and sends them over LTE. You do everything right—and game over
- On October 13, Ledger halted sales through resellers in seven countries in the region. Too late for these two
And yes, S$ is Singapore dollars, not USD. Headlines miss that
The police advice is simple: don’t enter your phrase on a suspicious device, and if it might have leaked—get a new wallet, a new phrase, and use a trusted device. Basically, now you have to ask where it was bought before even opening the box
I don’t have a position here. I’m watching to see whether the amount goes above S$3.5 million; when there’s an update, I’ll break it down. Follow if you hold crypto in cold storage
#Ledger #CryptoSecurity
Police say there have been at least two cases since September 10. And what gets me isn’t even the amount, but the shelf:
- Retail stores in Singapore. “A new box off the shelf” doesn’t guarantee anything anymore
- The implant, as Ledger itself explains, reads 24 words from the screen during setup and sends them over LTE. You do everything right—and game over
- On October 13, Ledger halted sales through resellers in seven countries in the region. Too late for these two
And yes, S$ is Singapore dollars, not USD. Headlines miss that
The police advice is simple: don’t enter your phrase on a suspicious device, and if it might have leaked—get a new wallet, a new phrase, and use a trusted device. Basically, now you have to ask where it was bought before even opening the box
I don’t have a position here. I’m watching to see whether the amount goes above S$3.5 million; when there’s an update, I’ll break it down. Follow if you hold crypto in cold storage
#Ledger #CryptoSecurity
171
People treat hardware wallets like a “buy one and you’re safe” talisman. Singapore just slapped that idea down.
Singapore police say that since September 10, at least two victims bought Ledger devices from local brick-and-mortar stores. The devices had been fitted with malicious components that could capture seed phrases and private keys. Together, the victims lost about 3.5 million Singapore dollars, or roughly 2.7 million US dollars.
The point isn’t how secure Ledger’s chips are. It’s how many people handled your device before it reached you. Cold wallets protect you from online hackers, not people in the supply chain. Hunt for a bargain with a secondhand device, an “authorized store,” or discounted stock from a small online seller, and you might save a few dozen bucks while handing your entire portfolio to some stranger in the middle.
There’s another ugly detail: the first report was filed on September 10, but Ledger’s public warning came on October 9—almost a month later. Only after that did it tell Southeast Asian distributors to stop selling the devices. Who’s responsible for the people who bought them in stores during that month?
And a quick gripe about the accounts reposting this: several of them directly reported 3.5 million Singapore dollars as 3.5 million US dollars. They were quicker to post “JUST IN” than to check the facts.
Here’s what I do: buy only through official channels, inspect the packaging when you open it, and return the device if it comes with a seed phrase already set up for you. Your seed phrase should always be generated by you on the device. Anyone who hands you one ready-made is a thief. If you’ve already bought one through an unofficial channel, don’t hesitate: get a new device, generate a new seed phrase, and move your coins.
#硬件钱包 #Ledger
People treat hardware wallets like a “buy one and you’re safe” talisman. Singapore just slapped that idea down.
Singapore police say that since September 10, at least two victims bought Ledger devices from local brick-and-mortar stores. The devices had been fitted with malicious components that could capture seed phrases and private keys. Together, the victims lost about 3.5 million Singapore dollars, or roughly 2.7 million US dollars.
The point isn’t how secure Ledger’s chips are. It’s how many people handled your device before it reached you. Cold wallets protect you from online hackers, not people in the supply chain. Hunt for a bargain with a secondhand device, an “authorized store,” or discounted stock from a small online seller, and you might save a few dozen bucks while handing your entire portfolio to some stranger in the middle.
There’s another ugly detail: the first report was filed on September 10, but Ledger’s public warning came on October 9—almost a month later. Only after that did it tell Southeast Asian distributors to stop selling the devices. Who’s responsible for the people who bought them in stores during that month?
And a quick gripe about the accounts reposting this: several of them directly reported 3.5 million Singapore dollars as 3.5 million US dollars. They were quicker to post “JUST IN” than to check the facts.
Here’s what I do: buy only through official channels, inspect the packaging when you open it, and return the device if it comes with a seed phrase already set up for you. Your seed phrase should always be generated by you on the device. Anyone who hands you one ready-made is a thief. If you’ve already bought one through an unofficial channel, don’t hesitate: get a new device, generate a new seed phrase, and move your coins.
#硬件钱包 #Ledger
Singapore police say that since September 10, at least two victims bought Ledger devices from local brick-and-mortar stores. The devices had been fitted with malicious components that could capture seed phrases and private keys. Together, the victims lost about 3.5 million Singapore dollars, or roughly 2.7 million US dollars.
The point isn’t how secure Ledger’s chips are. It’s how many people handled your device before it reached you. Cold wallets protect you from online hackers, not people in the supply chain. Hunt for a bargain with a secondhand device, an “authorized store,” or discounted stock from a small online seller, and you might save a few dozen bucks while handing your entire portfolio to some stranger in the middle.
There’s another ugly detail: the first report was filed on September 10, but Ledger’s public warning came on October 9—almost a month later. Only after that did it tell Southeast Asian distributors to stop selling the devices. Who’s responsible for the people who bought them in stores during that month?
And a quick gripe about the accounts reposting this: several of them directly reported 3.5 million Singapore dollars as 3.5 million US dollars. They were quicker to post “JUST IN” than to check the facts.
Here’s what I do: buy only through official channels, inspect the packaging when you open it, and return the device if it comes with a seed phrase already set up for you. Your seed phrase should always be generated by you on the device. Anyone who hands you one ready-made is a thief. If you’ve already bought one through an unofficial channel, don’t hesitate: get a new device, generate a new seed phrase, and move your coins.
#硬件钱包 #Ledger
5
·
--
Singapore police have officially weighed in: the Ledger tampering case dates back a month before it blew up online.
On the afternoon of October 28, the Singapore Police Force issued a statement saying it had received at least two reports since September 10, with total losses of about S$3.5 million (approximately US$2.7 million).
The compromised devices were bought at some retail stores in Singapore. They contained malicious hardware capable of stealing recovery phrases and private keys, allowing crypto to be transferred without your approval.
What hits hardest for me is the timeline: someone reported it as early as September 10, but the story didn’t blow up online until October 9. How many people spent that month using compromised devices?
The Straits Times cited analysts’ estimates that total losses from the incident have exceeded US$86 million. This isn’t an isolated case.
My advice is simple: if you have a Ledger bought from a retail store, don’t enter your recovery phrase into it or use it for transactions. If you suspect it’s been tampered with, move your crypto to a wallet on a brand-new device, generated from scratch.
There’s only one way to prove this assessment wrong: the police or Ledger publishes a list of affected batches showing that your device isn’t among them.
Did you buy your hardware wallet directly from the official website, or pick one up in person at a local store for convenience?
$BTC $ETH $SOL
#硬件钱包 #Ledger
Singapore police have officially weighed in: the Ledger tampering case dates back a month before it blew up online.
On the afternoon of October 28, the Singapore Police Force issued a statement saying it had received at least two reports since September 10, with total losses of about S$3.5 million (approximately US$2.7 million).
The compromised devices were bought at some retail stores in Singapore. They contained malicious hardware capable of stealing recovery phrases and private keys, allowing crypto to be transferred without your approval.
What hits hardest for me is the timeline: someone reported it as early as September 10, but the story didn’t blow up online until October 9. How many people spent that month using compromised devices?
The Straits Times cited analysts’ estimates that total losses from the incident have exceeded US$86 million. This isn’t an isolated case.
My advice is simple: if you have a Ledger bought from a retail store, don’t enter your recovery phrase into it or use it for transactions. If you suspect it’s been tampered with, move your crypto to a wallet on a brand-new device, generated from scratch.
There’s only one way to prove this assessment wrong: the police or Ledger publishes a list of affected batches showing that your device isn’t among them.
Did you buy your hardware wallet directly from the official website, or pick one up in person at a local store for convenience?
$BTC $ETH $SOL
#硬件钱包 #Ledger
On the afternoon of October 28, the Singapore Police Force issued a statement saying it had received at least two reports since September 10, with total losses of about S$3.5 million (approximately US$2.7 million).
The compromised devices were bought at some retail stores in Singapore. They contained malicious hardware capable of stealing recovery phrases and private keys, allowing crypto to be transferred without your approval.
What hits hardest for me is the timeline: someone reported it as early as September 10, but the story didn’t blow up online until October 9. How many people spent that month using compromised devices?
The Straits Times cited analysts’ estimates that total losses from the incident have exceeded US$86 million. This isn’t an isolated case.
My advice is simple: if you have a Ledger bought from a retail store, don’t enter your recovery phrase into it or use it for transactions. If you suspect it’s been tampered with, move your crypto to a wallet on a brand-new device, generated from scratch.
There’s only one way to prove this assessment wrong: the police or Ledger publishes a list of affected batches showing that your device isn’t among them.
Did you buy your hardware wallet directly from the official website, or pick one up in person at a local store for convenience?
$BTC $ETH $SOL
#硬件钱包 #Ledger
353
·
--
Singapore police issued a warning on 10/28: since 9/10, at least two cases have been reported in which users bought tampered Ledger hardware wallets from some local retailers, losing a total of about 3.5 million Singapore dollars.
Malicious hardware had been added to the devices, allowing recovery phrases or private keys to be intercepted during setup. The assets were then secretly transferred away.
Ledger said its chips, systems, and servers had not been compromised; the issue was with its distribution channels. Sales have been suspended in seven locations across Southeast Asia and Hong Kong. On-chain analysis estimates total losses may exceed US$86 million, a figure Ledger has not confirmed.
Buy hardware wallets only through official channels, and never enter your recovery phrase on a suspicious device. If you suspect it has been exposed, generate a new recovery phrase on a new device and transfer your assets. $BTC is currently around 79,760 (24h -1.4%).
#硬件钱包安全 #Ledger #CryptoSecurity
Singapore police issued a warning on 10/28: since 9/10, at least two cases have been reported in which users bought tampered Ledger hardware wallets from some local retailers, losing a total of about 3.5 million Singapore dollars.
Malicious hardware had been added to the devices, allowing recovery phrases or private keys to be intercepted during setup. The assets were then secretly transferred away.
Ledger said its chips, systems, and servers had not been compromised; the issue was with its distribution channels. Sales have been suspended in seven locations across Southeast Asia and Hong Kong. On-chain analysis estimates total losses may exceed US$86 million, a figure Ledger has not confirmed.
Buy hardware wallets only through official channels, and never enter your recovery phrase on a suspicious device. If you suspect it has been exposed, generate a new recovery phrase on a new device and transfer your assets. $BTC is currently around 79,760 (24h -1.4%).
#硬件钱包安全 #Ledger #CryptoSecurity
Malicious hardware had been added to the devices, allowing recovery phrases or private keys to be intercepted during setup. The assets were then secretly transferred away.
Ledger said its chips, systems, and servers had not been compromised; the issue was with its distribution channels. Sales have been suspended in seven locations across Southeast Asia and Hong Kong. On-chain analysis estimates total losses may exceed US$86 million, a figure Ledger has not confirmed.
Buy hardware wallets only through official channels, and never enter your recovery phrase on a suspicious device. If you suspect it has been exposed, generate a new recovery phrase on a new device and transfer your assets. $BTC is currently around 79,760 (24h -1.4%).
#硬件钱包安全 #Ledger #CryptoSecurity
156
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#HuangExitNvidiaStrategyInFocus
73,988 views
882 Discussing
2
#AnthropicRejectsIPODelayValuationinQuestion
668,427 views
5,167 Discussing
3
#BitMineReports$6.3BNetLossForFiscal2026
9,395 views
113 Discussing
4
#ChipStocksExtendLossesAfterNvidiaCEOChange
27,452 views
381 Discussing
5
#ThailandProposes$148KDailyStablecoinDepositWithdrawalCaps
2,607 views
41 Discussing
6
#CoreWeaveJumps10%On168%RevenueGrowth
176,888 views
1,622 Discussing
7
#ZcashFallsBelow$1000ForFirstTimeSinceSeptember
84,347 views
258 Discussing
8
#MSCIRemovalMayCurbStrategy’sBitcoinBuying
48,855 views
560 Discussing
9
#TradFiForBeginners
527,070 views
3,673 Discussing
10
#USJoblessClaimsRise
19.1M views
7,782 Discussing