
0xnut6
56 Posts

0xnut6
Report
Block User
多年資歷的專業交易員與分析師,專注衍生品、DeFi、鏈上數據、RWA 與 AI 賽道。每天整理市場最前沿的資訊,拆解背後的原因、資金流向與風險,幫你在變化快速的加密市場裡看清局勢、做出更好的決策。內容僅供參考,不構成投資建議。
13 Following
15 Followers
7 Liked
Posts
·
--
Article
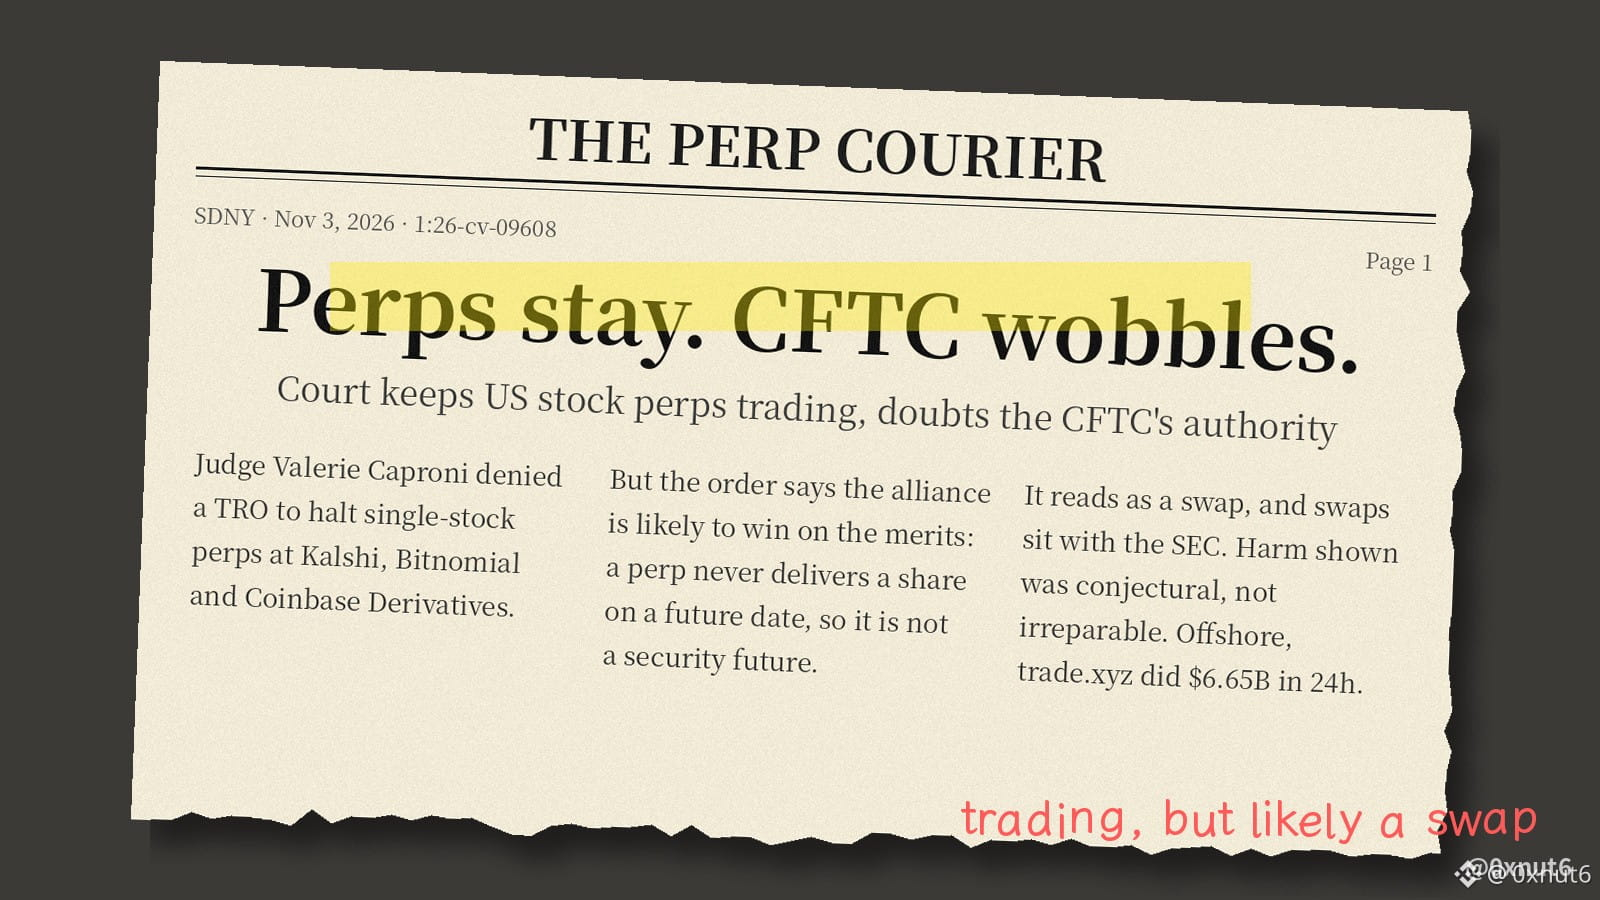
US stock perps keep trading, but the judge doubts the CFTCA federal judge refused on Nov 3 to halt US single-stock perps, then wrote that the challengers will likely win. So the products kept trading while losing the legal argument.
The case: the Capital Markets Alliance, backed by Cboe and Citadel Securities, sued @CFTC hours after it cleared stock perps at Kalshi, Bitnomial and Coinbase Derivatives as security futures.
The reasoning, per Judge Valerie Caproni: a perp never delivers a share on a future date, so it fails the legal definition of a security future. It reads as a swap, and swaps on single stocks belong to the SEC.
Why the halt still failed: she found the equities and public interest favored the alliance, but its declarations showed only conjectural harm, not irreparable harm.
What rides on it: the same product already trades offshore. @tradexyz on Hyperliquid did $6.65B in 24h volume this morning, with $4.4B open interest. Its S&P 500 contract alone traded $736M.
The order denied the halt and still called the CFTC approval likely beyond its authority.
$HYPE
US stock perps keep trading, but the judge doubts the CFTC
A federal judge refused on Nov 3 to halt US single-stock perps, then wrote that the challengers will likely win. So the products kept trading while losing the legal argument.
The case: the Capital Markets Alliance, backed by Cboe and Citadel Securities, sued @CFTC hours after it cleared stock perps at Kalshi, Bitnomial and Coinbase Derivatives as security futures.
The reasoning, per Judge Valerie Caproni: a perp never delivers a share on a future date, so it fails the legal definition of a security future. It reads as a swap, and swaps on single stocks belong to the SEC.
Why the halt still failed: she found the equities and public interest favored the alliance, but its declarations showed only conjectural harm, not irreparable harm.
What rides on it: the same product already trades offshore. @tradexyz on Hyperliquid did $6.65B in 24h volume this morning, with $4.4B open interest. Its S&P 500 contract alone traded $736M.
The order denied the halt and still called the CFTC approval likely beyond its authority.
$HYPE
The case: the Capital Markets Alliance, backed by Cboe and Citadel Securities, sued @CFTC hours after it cleared stock perps at Kalshi, Bitnomial and Coinbase Derivatives as security futures.
The reasoning, per Judge Valerie Caproni: a perp never delivers a share on a future date, so it fails the legal definition of a security future. It reads as a swap, and swaps on single stocks belong to the SEC.
Why the halt still failed: she found the equities and public interest favored the alliance, but its declarations showed only conjectural harm, not irreparable harm.
What rides on it: the same product already trades offshore. @tradexyz on Hyperliquid did $6.65B in 24h volume this morning, with $4.4B open interest. Its S&P 500 contract alone traded $736M.
The order denied the halt and still called the CFTC approval likely beyond its authority.
$HYPE
186
·
--
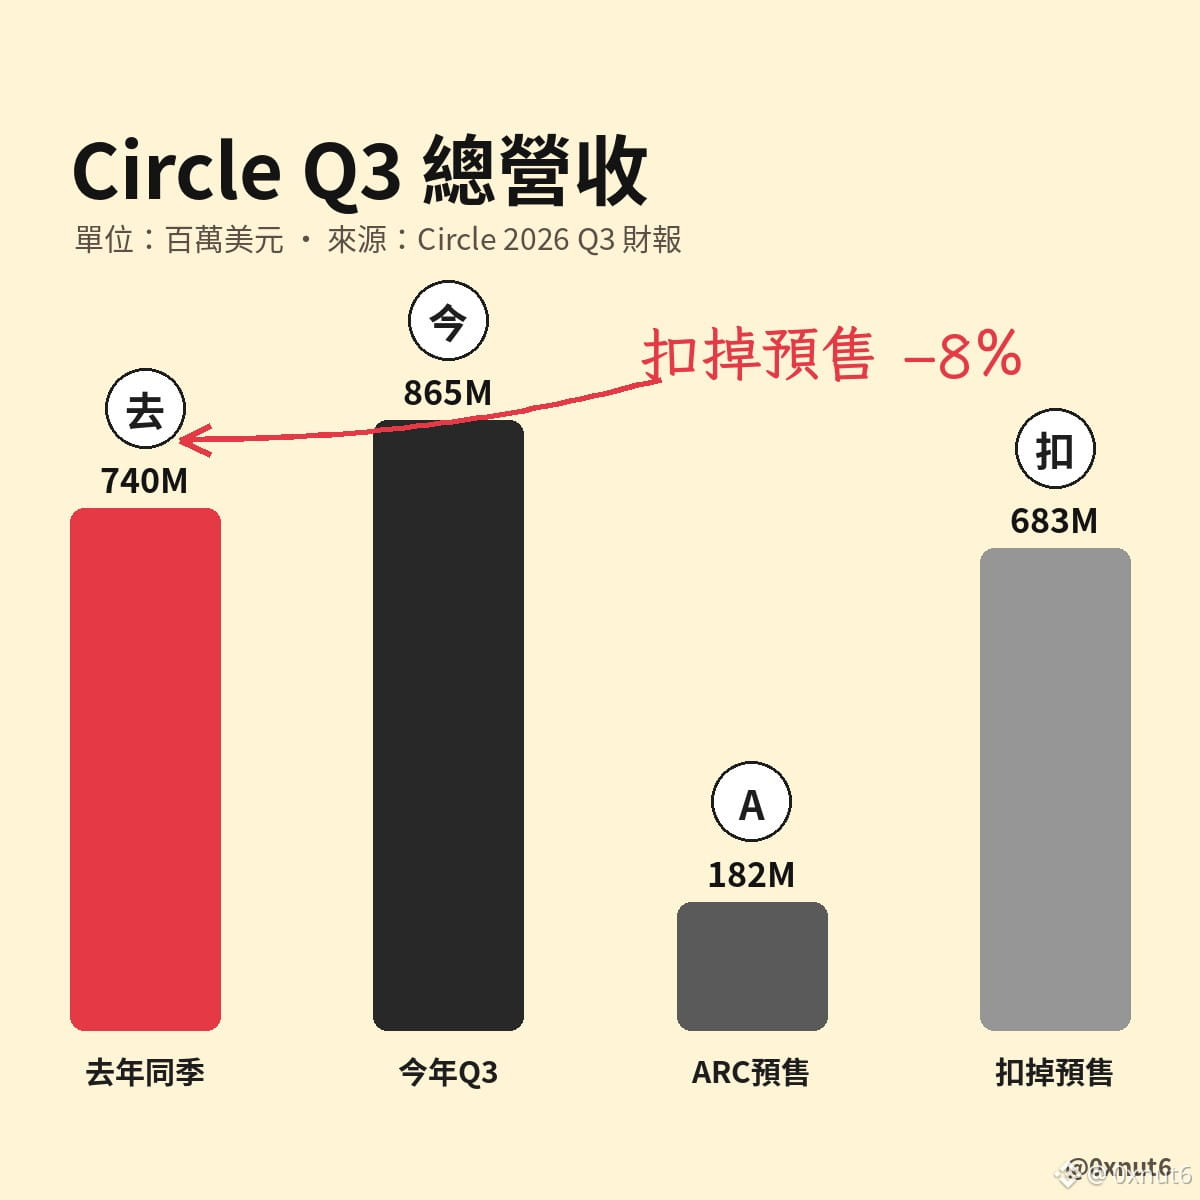
Circle 營收年增 17%,全靠一次性賣幣撐起來。
因為 @circle 今晚公布的 Q3 總營收 8.65 億美元裡,有 1.82 億是 ARC 代幣預售,屬一次性收入,下一季不會再有。
本業在縮:儲備收入 6.58 億美元,年減 8%。主因是儲備報酬率掉到 3.5%,利率往下,USDC 的利息收入就跟著少。
扣掉預售那筆,總營收約 6.83 億美元。去年同季是 7.40 億,等於年減約 8%。
規模也沒放大:USDC 期末流通 739 億美元,年增 0%。
@jerallaire 團隊沒改的指引寫在同一份財報:USDC 流通量多年目標仍是 40% 年複合成長。
$USDC
Circle 營收年增 17%,全靠一次性賣幣撐起來。
因為 @circle 今晚公布的 Q3 總營收 8.65 億美元裡,有 1.82 億是 ARC 代幣預售,屬一次性收入,下一季不會再有。
本業在縮:儲備收入 6.58 億美元,年減 8%。主因是儲備報酬率掉到 3.5%,利率往下,USDC 的利息收入就跟著少。
扣掉預售那筆,總營收約 6.83 億美元。去年同季是 7.40 億,等於年減約 8%。
規模也沒放大:USDC 期末流通 739 億美元,年增 0%。
@jerallaire 團隊沒改的指引寫在同一份財報:USDC 流通量多年目標仍是 40% 年複合成長。
$USDC
因為 @circle 今晚公布的 Q3 總營收 8.65 億美元裡,有 1.82 億是 ARC 代幣預售,屬一次性收入,下一季不會再有。
本業在縮:儲備收入 6.58 億美元,年減 8%。主因是儲備報酬率掉到 3.5%,利率往下,USDC 的利息收入就跟著少。
扣掉預售那筆,總營收約 6.83 億美元。去年同季是 7.40 億,等於年減約 8%。
規模也沒放大:USDC 期末流通 739 億美元,年增 0%。
@jerallaire 團隊沒改的指引寫在同一份財報:USDC 流通量多年目標仍是 40% 年複合成長。
$USDC
25
·
--
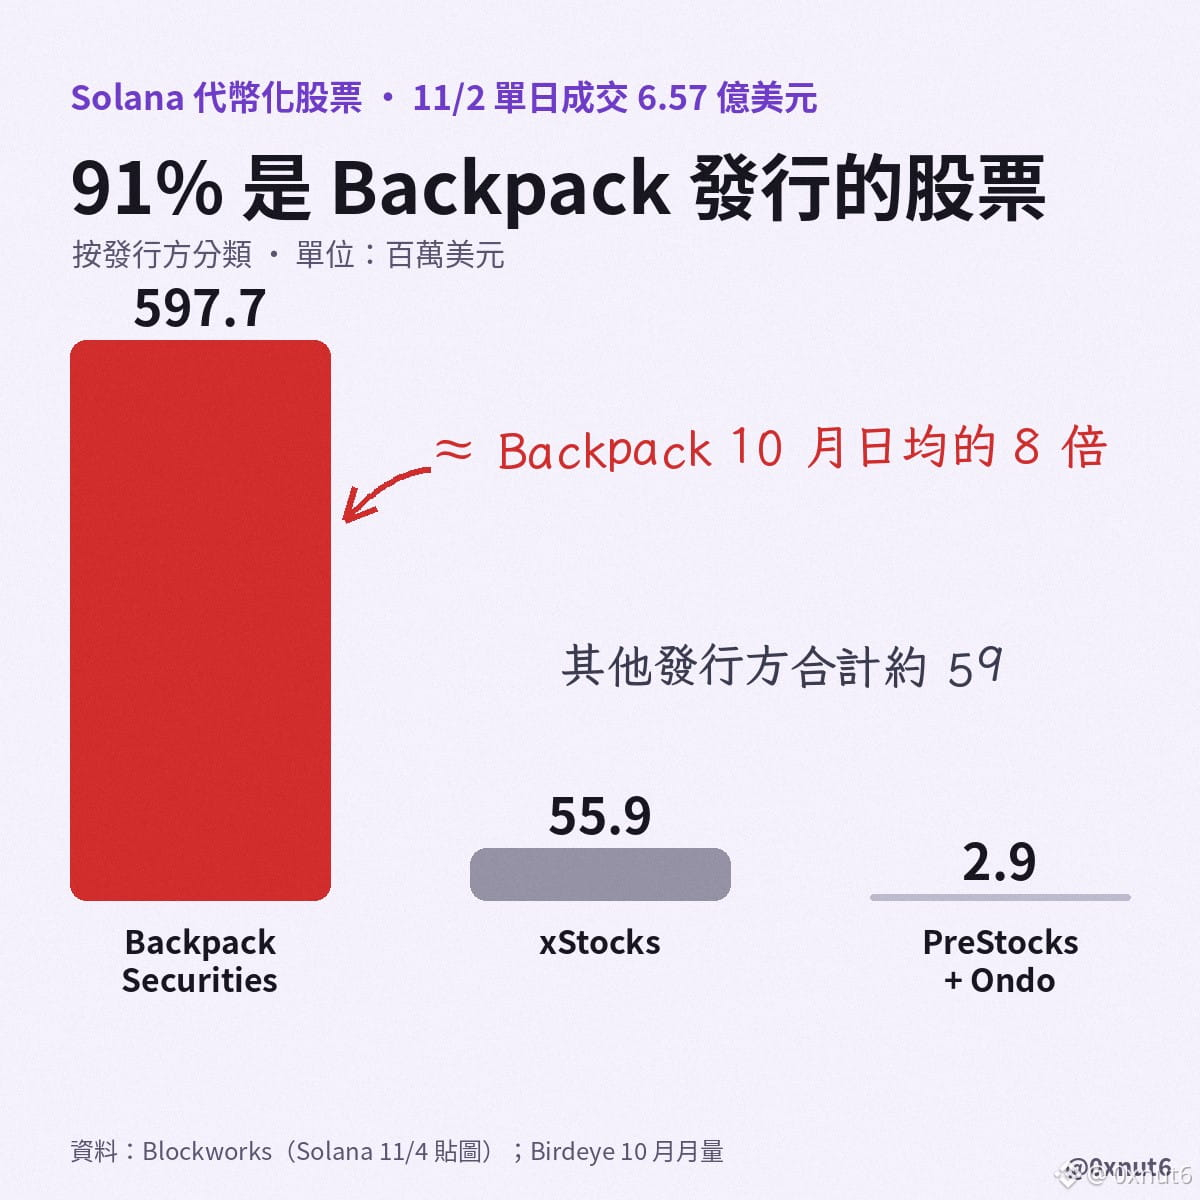
Solana 官方 X 帳號今天貼出 Blockworks 的圖:11/2 週一 Solana 上的代幣化股票單日成交 6.57 億美元,是 9 月以來最高的一天。我把圖裡按發行方拆開的數字補上。
這張圖按「股票代幣最初由誰發行」分類。Backpack Securities 發行的股票當天成交 5.98 億美元,占 91%。第二名 xStocks 當天是 5,593 萬美元,沒有跟著放量。PreStocks 和 Ondo 各只有一百多萬美元。
再拿 Birdeye 的月資料對照。Backpack Securities 10 月整個月成交 23 億美元,平均一天約 7,400 萬美元。11/2 這一天就做到 10 月全月的 26%,大約是 10 月日均的 8 倍。
這張圖算的是發行方,不是交易場所,所以 5.98 億美元是 Backpack 發行的股票在各處的鏈上成交,不一定都發生在 Backpack 交易所裡。
拿掉 Backpack 之後,11/2 當天 Solana 上其他發行方的股票代幣合計只成交約 5,900 萬美元,比 9 月以來大多數日子的全鏈總量還低。
$SOL
Solana 官方 X 帳號今天貼出 Blockworks 的圖:11/2 週一 Solana 上的代幣化股票單日成交 6.57 億美元,是 9 月以來最高的一天。我把圖裡按發行方拆開的數字補上。
這張圖按「股票代幣最初由誰發行」分類。Backpack Securities 發行的股票當天成交 5.98 億美元,占 91%。第二名 xStocks 當天是 5,593 萬美元,沒有跟著放量。PreStocks 和 Ondo 各只有一百多萬美元。
再拿 Birdeye 的月資料對照。Backpack Securities 10 月整個月成交 23 億美元,平均一天約 7,400 萬美元。11/2 這一天就做到 10 月全月的 26%,大約是 10 月日均的 8 倍。
這張圖算的是發行方,不是交易場所,所以 5.98 億美元是 Backpack 發行的股票在各處的鏈上成交,不一定都發生在 Backpack 交易所裡。
拿掉 Backpack 之後,11/2 當天 Solana 上其他發行方的股票代幣合計只成交約 5,900 萬美元,比 9 月以來大多數日子的全鏈總量還低。
$SOL
這張圖按「股票代幣最初由誰發行」分類。Backpack Securities 發行的股票當天成交 5.98 億美元,占 91%。第二名 xStocks 當天是 5,593 萬美元,沒有跟著放量。PreStocks 和 Ondo 各只有一百多萬美元。
再拿 Birdeye 的月資料對照。Backpack Securities 10 月整個月成交 23 億美元,平均一天約 7,400 萬美元。11/2 這一天就做到 10 月全月的 26%,大約是 10 月日均的 8 倍。
這張圖算的是發行方,不是交易場所,所以 5.98 億美元是 Backpack 發行的股票在各處的鏈上成交,不一定都發生在 Backpack 交易所裡。
拿掉 Backpack 之後,11/2 當天 Solana 上其他發行方的股票代幣合計只成交約 5,900 萬美元,比 9 月以來大多數日子的全鏈總量還低。
$SOL
148
·
--
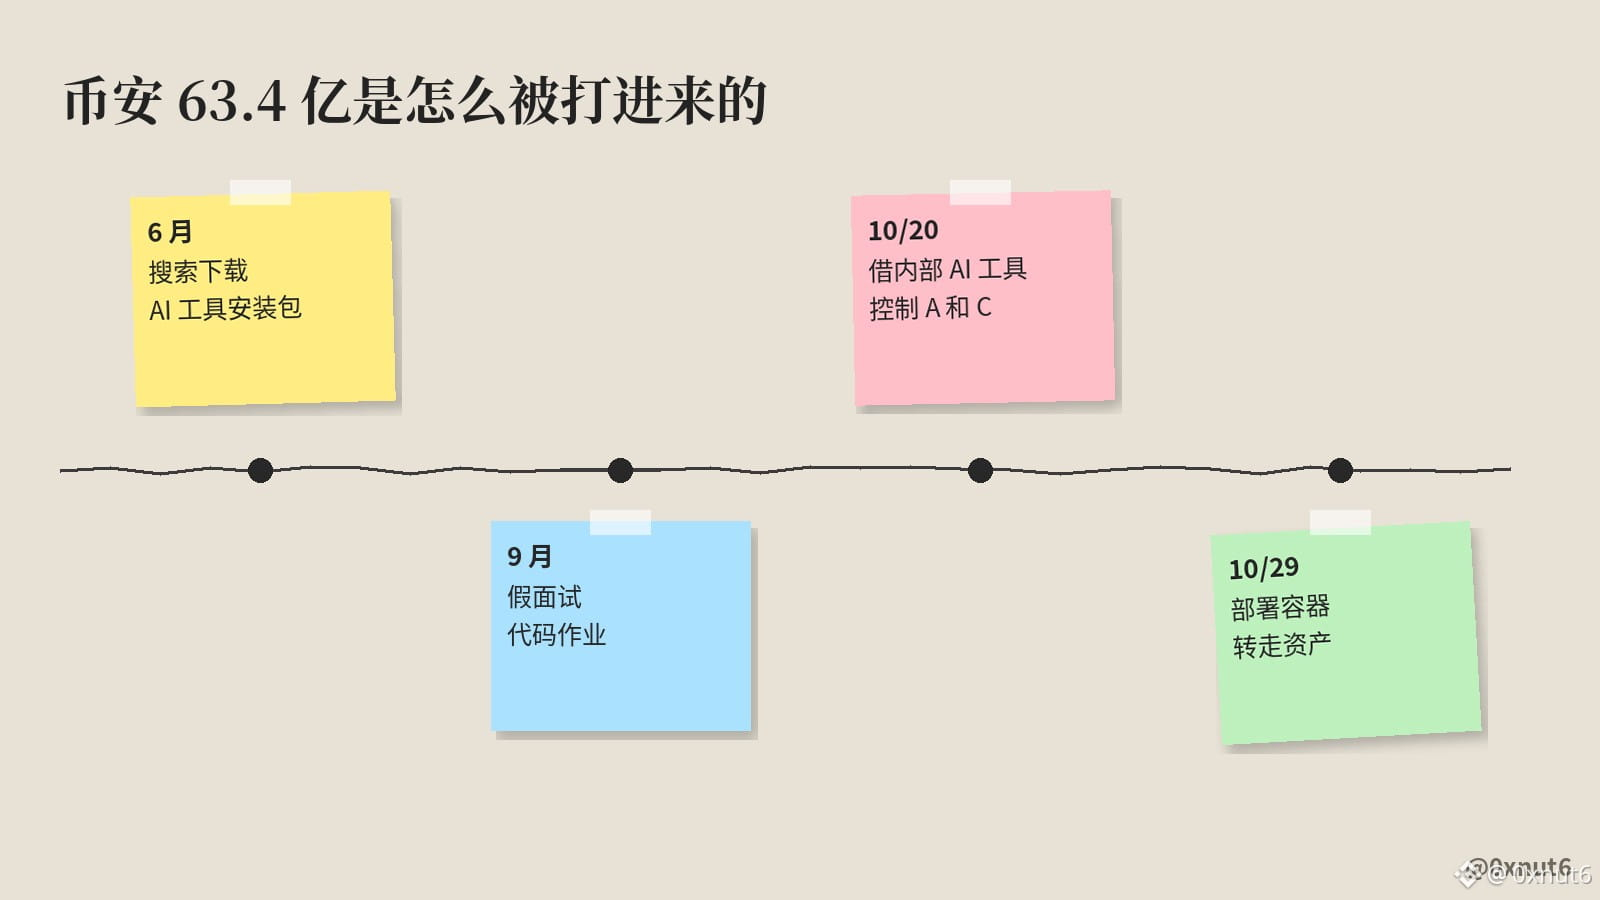
币安 10 月 29 日被转走约 63.4 亿美元。@binance 昨晚公布的初步报告显示,攻击者最早的两个入口,是加密从业者几乎每天都会做的两件事:在搜索引擎上找一个 AI 编程工具来装,以及接一场跳槽面试。
第一个入口在 6 月。钱包运维工程师 A 搜索一款热门 AI 编程工具,下载到的是被篡改过的 Homebrew 安装包。币安安全团队当时发现了异常,换掉了电脑并轮换了凭证。换电脑挡住了这次入侵,挡不住已经泄露的信息:A 的岗位和他所在钱包团队同事的身份,攻击者已经知道了。
第二个入口在 9 月。工程师 B 在正规求职平台上被一位自称项目总监的人联系,一面是 HR 视频面试,对方还分享了带个人照片和视频的社交账号来取得信任。二面换成自称 CEO 的人,最后要求他把一份代码作业下载到工作电脑上。这个仓库在安装时自动执行,把电脑上的 pyenv 换成恶意版本并连上攻击者的服务器,当时的终端防护软件没有报警。
后面的步骤都建立在这两台电脑上。10 月 20 日,攻击者借 B 的电脑和一个内部 AI 工具,又控制了 A 和另一位钱包工程师 C 的电脑,并在 A 的电脑上找到了容器部署令牌;10 月 29 日,攻击者用这枚令牌部署容器,调用签名服务把资产转走。
慢雾创始人余弦 @evilcos 的看法是,这是一场持续数月的高级持续性攻击,看完报告的人更应该检查自己和同事会不会中同类投毒。币安说今年已经拦下 57 起疑似与朝鲜有关的同类尝试,手法包括假面试、伪装成热门开发工具的恶意软件和假视频会议软件;这一次没拦住的,正是 6 月那个搜索来的安装包和 9 月那份面试作业。
$BNB $BTC
币安 10 月 29 日被转走约 63.4 亿美元。@binance 昨晚公布的初步报告显示,攻击者最早的两个入口,是加密从业者几乎每天都会做的两件事:在搜索引擎上找一个 AI 编程工具来装,以及接一场跳槽面试。
第一个入口在 6 月。钱包运维工程师 A 搜索一款热门 AI 编程工具,下载到的是被篡改过的 Homebrew 安装包。币安安全团队当时发现了异常,换掉了电脑并轮换了凭证。换电脑挡住了这次入侵,挡不住已经泄露的信息:A 的岗位和他所在钱包团队同事的身份,攻击者已经知道了。
第二个入口在 9 月。工程师 B 在正规求职平台上被一位自称项目总监的人联系,一面是 HR 视频面试,对方还分享了带个人照片和视频的社交账号来取得信任。二面换成自称 CEO 的人,最后要求他把一份代码作业下载到工作电脑上。这个仓库在安装时自动执行,把电脑上的 pyenv 换成恶意版本并连上攻击者的服务器,当时的终端防护软件没有报警。
后面的步骤都建立在这两台电脑上。10 月 20 日,攻击者借 B 的电脑和一个内部 AI 工具,又控制了 A 和另一位钱包工程师 C 的电脑,并在 A 的电脑上找到了容器部署令牌;10 月 29 日,攻击者用这枚令牌部署容器,调用签名服务把资产转走。
慢雾创始人余弦 @evilcos 的看法是,这是一场持续数月的高级持续性攻击,看完报告的人更应该检查自己和同事会不会中同类投毒。币安说今年已经拦下 57 起疑似与朝鲜有关的同类尝试,手法包括假面试、伪装成热门开发工具的恶意软件和假视频会议软件;这一次没拦住的,正是 6 月那个搜索来的安装包和 9 月那份面试作业。
$BNB $BTC
第一个入口在 6 月。钱包运维工程师 A 搜索一款热门 AI 编程工具,下载到的是被篡改过的 Homebrew 安装包。币安安全团队当时发现了异常,换掉了电脑并轮换了凭证。换电脑挡住了这次入侵,挡不住已经泄露的信息:A 的岗位和他所在钱包团队同事的身份,攻击者已经知道了。
第二个入口在 9 月。工程师 B 在正规求职平台上被一位自称项目总监的人联系,一面是 HR 视频面试,对方还分享了带个人照片和视频的社交账号来取得信任。二面换成自称 CEO 的人,最后要求他把一份代码作业下载到工作电脑上。这个仓库在安装时自动执行,把电脑上的 pyenv 换成恶意版本并连上攻击者的服务器,当时的终端防护软件没有报警。
后面的步骤都建立在这两台电脑上。10 月 20 日,攻击者借 B 的电脑和一个内部 AI 工具,又控制了 A 和另一位钱包工程师 C 的电脑,并在 A 的电脑上找到了容器部署令牌;10 月 29 日,攻击者用这枚令牌部署容器,调用签名服务把资产转走。
慢雾创始人余弦 @evilcos 的看法是,这是一场持续数月的高级持续性攻击,看完报告的人更应该检查自己和同事会不会中同类投毒。币安说今年已经拦下 57 起疑似与朝鲜有关的同类尝试,手法包括假面试、伪装成热门开发工具的恶意软件和假视频会议软件;这一次没拦住的,正是 6 月那个搜索来的安装包和 9 月那份面试作业。
$BNB $BTC
160
·
--
我这周干了一件很省事的事:对 Grok Bot 说了一句「翻一下我 X 账号近 30 天的原创和引用,告诉我哪类帖子有人看、几点发比较稳」,它去拉数据,把结果摊开给我看。
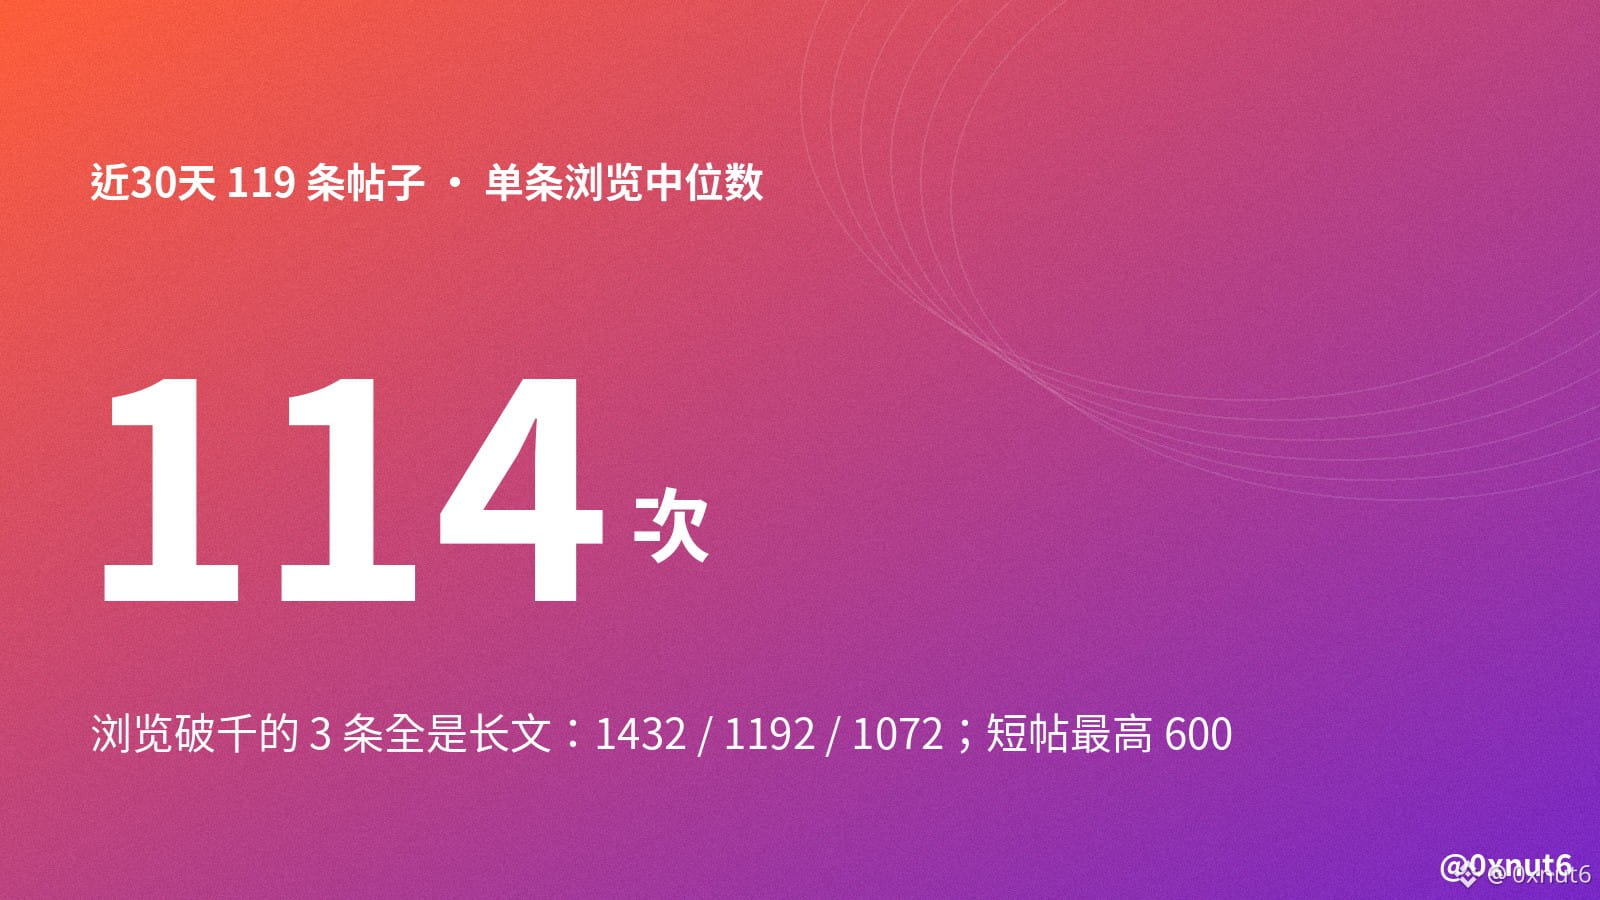
近 30 天一共拉回 119 条。其中原创 91 条,引用 28 条。总浏览约 1.95 万,单条浏览的中位数只有 114。
最意外的是前三名全是长文:10/15 那篇代币化股票 1432 次浏览,10/24 币安和 Hyperliquid 股票永续对比 1192 次,10/17 讲同一个订单簿前端费差十倍那篇 1072 次。三篇都在中位数的 9 倍以上,短帖里最高的 Solana Alpenglow 也只有 600。
我把前几名的数字和 X 接口返回的原始数据对过一遍,对得上才敢写这条。要复现很简单,把上面那句话原样丢给它就行,不用导 CSV,也不用装分析插件。数字一定以你自己账号当下拉到的为准,别人的截图只能参考。
对我来说最有用的结论很直接:短帖撑住日常曝光,单条浏览破千的只有长文。
我这周干了一件很省事的事:对 Grok Bot 说了一句「翻一下我 X 账号近 30 天的原创和引用,告诉我哪类帖子有人看、几点发比较稳」,它去拉数据,把结果摊开给我看。
近 30 天一共拉回 119 条。其中原创 91 条,引用 28 条。总浏览约 1.95 万,单条浏览的中位数只有 114。
最意外的是前三名全是长文:10/15 那篇代币化股票 1432 次浏览,10/24 币安和 Hyperliquid 股票永续对比 1192 次,10/17 讲同一个订单簿前端费差十倍那篇 1072 次。三篇都在中位数的 9 倍以上,短帖里最高的 Solana Alpenglow 也只有 600。
我把前几名的数字和 X 接口返回的原始数据对过一遍,对得上才敢写这条。要复现很简单,把上面那句话原样丢给它就行,不用导 CSV,也不用装分析插件。数字一定以你自己账号当下拉到的为准,别人的截图只能参考。
对我来说最有用的结论很直接:短帖撑住日常曝光,单条浏览破千的只有长文。
近 30 天一共拉回 119 条。其中原创 91 条,引用 28 条。总浏览约 1.95 万,单条浏览的中位数只有 114。
最意外的是前三名全是长文:10/15 那篇代币化股票 1432 次浏览,10/24 币安和 Hyperliquid 股票永续对比 1192 次,10/17 讲同一个订单簿前端费差十倍那篇 1072 次。三篇都在中位数的 9 倍以上,短帖里最高的 Solana Alpenglow 也只有 600。
我把前几名的数字和 X 接口返回的原始数据对过一遍,对得上才敢写这条。要复现很简单,把上面那句话原样丢给它就行,不用导 CSV,也不用装分析插件。数字一定以你自己账号当下拉到的为准,别人的截图只能参考。
对我来说最有用的结论很直接:短帖撑住日常曝光,单条浏览破千的只有长文。
54
·
--
Polymarket's Senate market moved 16 points in two hours tonight, while most US ballots are still uncounted.
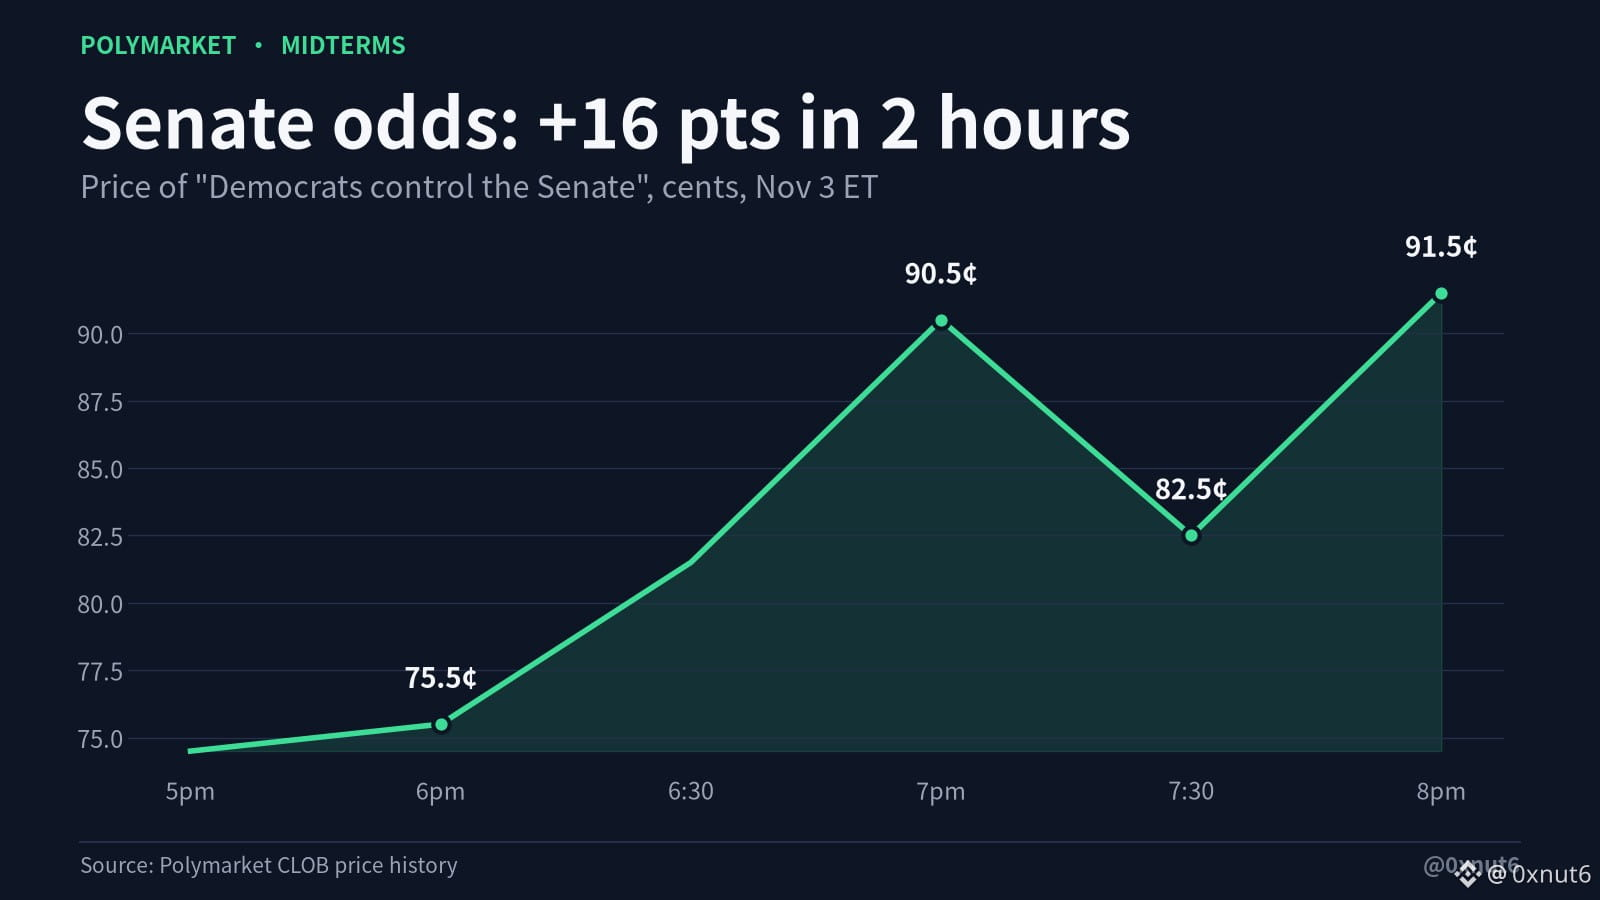
Democrats to control the Senate traded at 75.5¢ at 6pm ET. By 8pm ET the same contract printed 91.5¢.
The path was not a straight line. It touched 90.5¢ at 7pm. Thirty minutes later it was back at 82.5¢, then it climbed again.
So early returns, not final tallies, are doing the repricing. @Polymarket shows $24.7M traded on the Senate question and $51.5M on the House, where Democrats sit at 99¢.
At 8pm ET a Democratic Senate cost 91.5¢ on Polymarket, up from 75.5¢ two hours earlier.
$POL $BTC
Polymarket's Senate market moved 16 points in two hours tonight, while most US ballots are still uncounted.
Democrats to control the Senate traded at 75.5¢ at 6pm ET. By 8pm ET the same contract printed 91.5¢.
The path was not a straight line. It touched 90.5¢ at 7pm. Thirty minutes later it was back at 82.5¢, then it climbed again.
So early returns, not final tallies, are doing the repricing. @Polymarket shows $24.7M traded on the Senate question and $51.5M on the House, where Democrats sit at 99¢.
At 8pm ET a Democratic Senate cost 91.5¢ on Polymarket, up from 75.5¢ two hours earlier.
$POL $BTC
Democrats to control the Senate traded at 75.5¢ at 6pm ET. By 8pm ET the same contract printed 91.5¢.
The path was not a straight line. It touched 90.5¢ at 7pm. Thirty minutes later it was back at 82.5¢, then it climbed again.
So early returns, not final tallies, are doing the repricing. @Polymarket shows $24.7M traded on the Senate question and $51.5M on the House, where Democrats sit at 99¢.
At 8pm ET a Democratic Senate cost 91.5¢ on Polymarket, up from 75.5¢ two hours earlier.
$POL $BTC
108
·
--
Anthropic 還沒上市,散戶能買到的價格已經比華爾街機構貴一截。
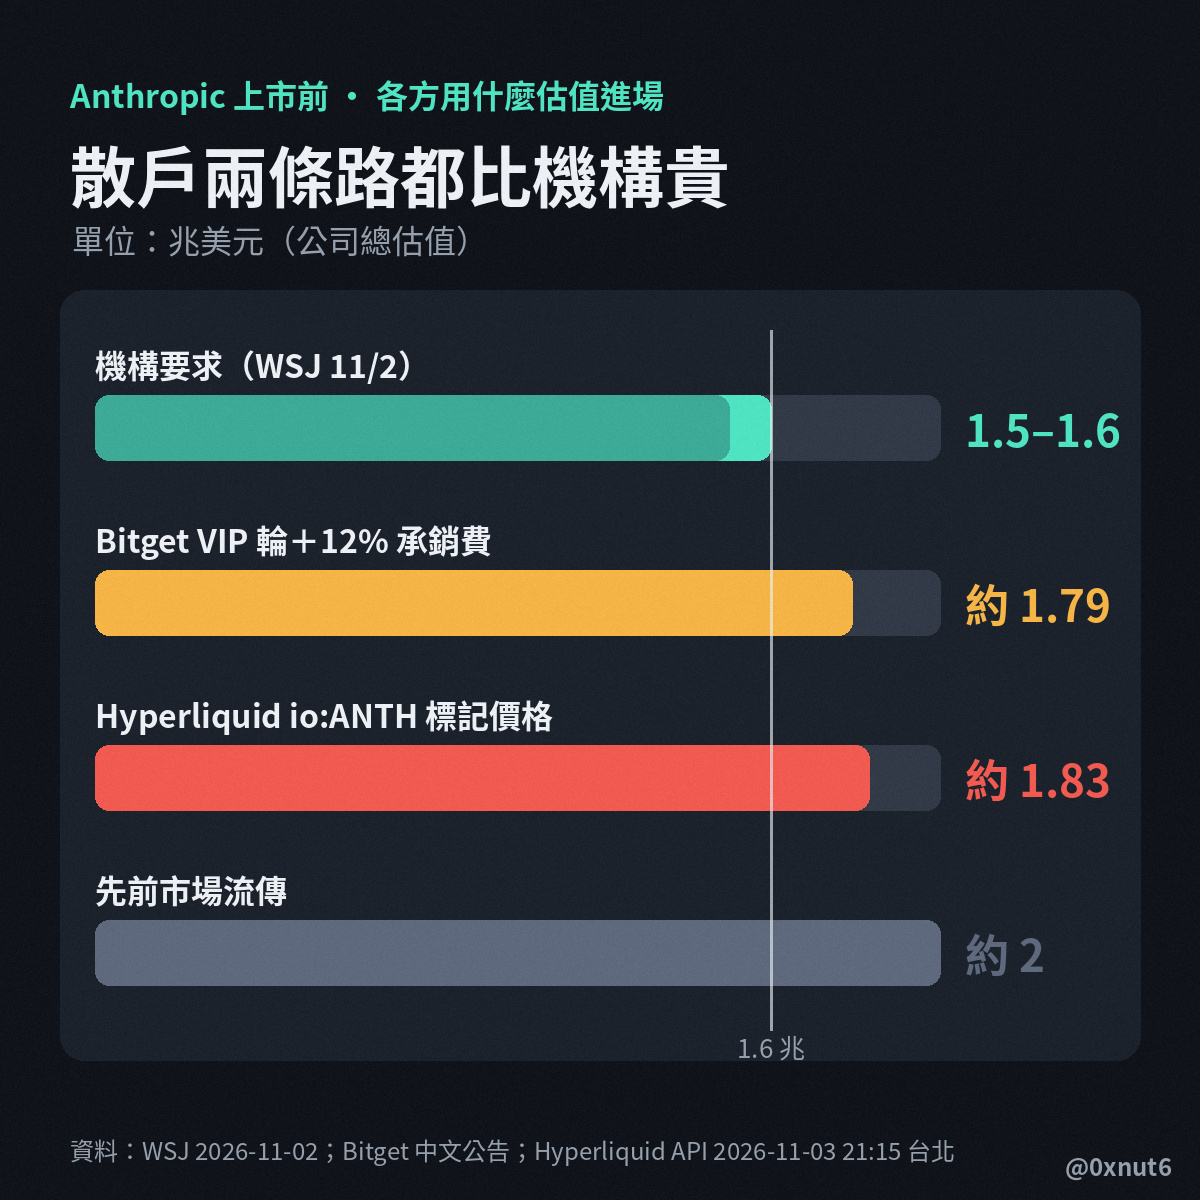
因為機構在砍價。《華爾街日報》11 月 2 日報導,準備認購 IPO 的機構要求估值落在 1.5 到 1.6 兆美元,低於先前流傳的約 2 兆。
第一條路是交易所代購。@Bitget_zh 的 IPO Prime VIP 輪 11 月 5 日開放,要預付 12% 承銷服務費。就算按 1.6 兆定價,加上這筆費用等於用約 1.79 兆進場。
第二條路是鏈上永續。@HyperliquidX 上 @entropyIO 的 io:ANTH,1 點代表 10 億美元估值。今晚標記價格約 1,832,也就是 1.83 兆,未平倉約 9,840 萬美元。
兩條路的價位落在 1.79 到 1.83 兆,比機構要的上緣 1.6 兆高出一成二到一成四。Bitget 公告的潛在上市日是 11 月 18 日。
$HYPE $BGB
Anthropic 還沒上市,散戶能買到的價格已經比華爾街機構貴一截。
因為機構在砍價。《華爾街日報》11 月 2 日報導,準備認購 IPO 的機構要求估值落在 1.5 到 1.6 兆美元,低於先前流傳的約 2 兆。
第一條路是交易所代購。@Bitget_zh 的 IPO Prime VIP 輪 11 月 5 日開放,要預付 12% 承銷服務費。就算按 1.6 兆定價,加上這筆費用等於用約 1.79 兆進場。
第二條路是鏈上永續。@HyperliquidX 上 @entropyIO 的 io:ANTH,1 點代表 10 億美元估值。今晚標記價格約 1,832,也就是 1.83 兆,未平倉約 9,840 萬美元。
兩條路的價位落在 1.79 到 1.83 兆,比機構要的上緣 1.6 兆高出一成二到一成四。Bitget 公告的潛在上市日是 11 月 18 日。
$HYPE $BGB
因為機構在砍價。《華爾街日報》11 月 2 日報導,準備認購 IPO 的機構要求估值落在 1.5 到 1.6 兆美元,低於先前流傳的約 2 兆。
第一條路是交易所代購。@Bitget_zh 的 IPO Prime VIP 輪 11 月 5 日開放,要預付 12% 承銷服務費。就算按 1.6 兆定價,加上這筆費用等於用約 1.79 兆進場。
第二條路是鏈上永續。@HyperliquidX 上 @entropyIO 的 io:ANTH,1 點代表 10 億美元估值。今晚標記價格約 1,832,也就是 1.83 兆,未平倉約 9,840 萬美元。
兩條路的價位落在 1.79 到 1.83 兆,比機構要的上緣 1.6 兆高出一成二到一成四。Bitget 公告的潛在上市日是 11 月 18 日。
$HYPE $BGB
85
·
--
Article
幣安被盜 64 億的帳單:用戶沒賠,錢落在這四個地方凍住的只有 44%,剩下的帳單由幣安自己的三個錢包付,再加上被駭客倒貨的幣種持有人一起分攤。
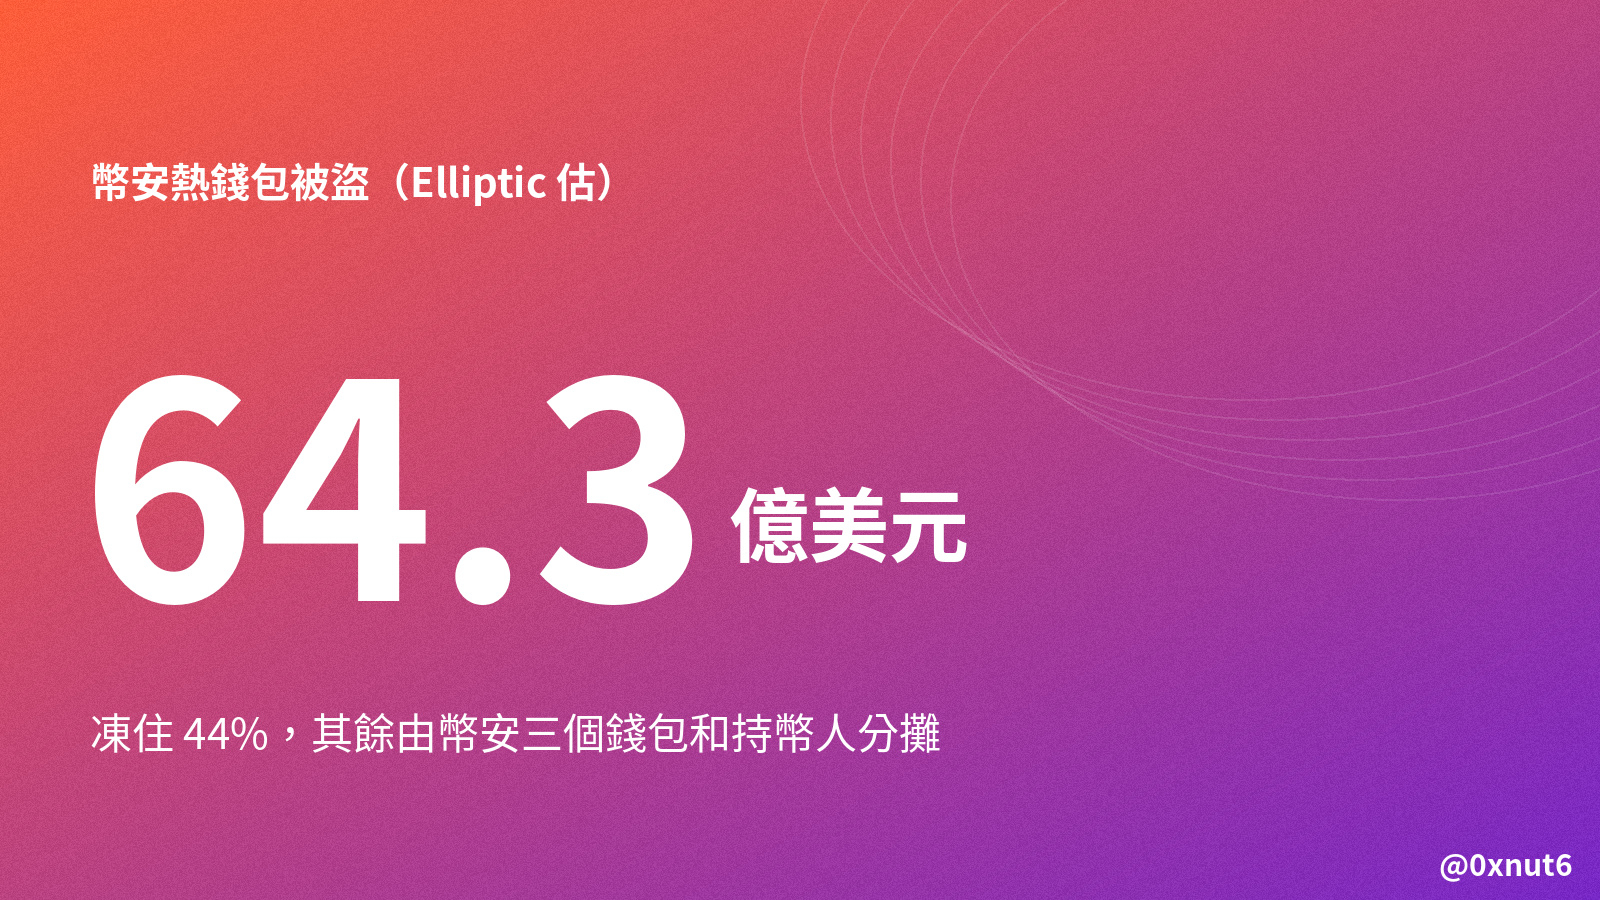
10 月 29 日深夜,幣安熱錢包被轉走的資產,Elliptic 估約 64.3 億美元,幣安自己的說法是撥出逾 63.4 億美元公司資金承擔。到今天是第五天,提款已經分批恢復,幣安也一再說「損失不轉嫁給用戶」。用戶這邊確實沒有被扣款,但 64 億不會憑空消失。我把這幾天 @binance 的六份官方更新、@elliptic 的追蹤數字、儲備證明快照和鏈上倒貨紀錄放在一起,看這筆錢最後落在誰身上。
【64 億裡,44% 被凍住,靠的是發行方能拉黑地址】
Elliptic 11 月 2 日的統計是:約 28.5 億美元已被凍結或查扣,佔 44%;約 32.4 億美元還留在駭客關聯地址裡,大多是 ETH 和 BTC。兩者加起來約 60.9 億,剩下約 3.4 億的去向,Elliptic 在這份統計裡沒有細分。
28.5 億是凍結加查扣的總數,已公開的大筆幾乎都是穩定幣。Tether 執行長 Paolo Ardoino 說 Tether 凍結了超過 15.67 億 USDT,Circle 執行長 Jeremy Allaire 說 @circle 凍結了超過 8 億 USDC,兩家加起來約 23.7 億,其餘凍結的明細目前沒有逐筆公開。原因很直接:USDT 和 USDC 的合約裡有黑名單功能,發行方可以讓某個地址的餘額轉不出去。
ETH 這邊,已公開的凍結只有一筆。Arbitrum 安全委員會把駭客地址裡的 8,425 顆 ETH 和約 7,456 萬顆 ARB(合計約 3,000 萬美元)移進凍結錢包,因為 Arbitrum 有一組握有升級權限的委員會。比特幣和以太坊主網沒有這種角色,所以 BTC、ETH 一旦離開幣安,就沒有人能在鏈上把它們鎖住。
駭客也很清楚這一點。事發後約 20 分鐘內,駭客先把 3.25 億美元穩定幣換成 ETH,搶在凍結之前。換回來的 ETH 約值 2.85 億美元。另外,駭客把 6,000 萬 USDT 存進 @aave 當抵押。用這筆抵押,駭客借出 19,762 顆 WETH,約 4,460 萬美元。換句話說,凍結能擋住的上限,在駭客動手的頭一個小時就被壓低了。
【沒被凍的 32 億正在被變賣,價格壓力落在 TRX、SOL 和小幣上】
32.4 億美元的未凍結部分不是放著不動。Elliptic 統計,不到四天,洗錢就動用了約 12,000 個錢包、橫跨 11 條鏈。交易筆數超過 40,000 筆,光 Tron 上就分散到約 7,700 個地址。這是程式化在跑,不是手動轉帳。
Tron 是第一個被波及的二級市場。因為 USDT 能被凍、TRX 不行,駭客先在 SunSwap 用 2.34 億 USDT 換 TRX,均價約 0.367 美元。換到的 TRX 約 6.38 億顆。之後駭客拆成小額全天候賣出,27 小時內賣了 546 筆,手上一度仍有約 4.75 億顆。TRX 一度跌到 0.302 美元。Tether 另外凍結了攻擊者兩個 Tron 錢包、共 3.787 億 USDT。
Solana 是第二個。11 月 2 日,駭客經由跨鏈橋 Relay 把 970,522 顆被盜 SOL(約 9,590 萬美元)換成 BTC。
EVM 鏈上的山寨幣是第三個。駭客已拋售超過 130 種代幣,包括 UNI、ENA、PEPE、LINK、AAVE、ONDO、WLD。換回來的是約 12.34 萬顆 ETH 和 169 萬 USDC,合計約 2.79 億美元。流動性太差的幣甚至賣不掉。一個關聯錢包把帳面約 500 萬美元的 PROM 倒進幾乎沒有流動性的 Uniswap V2 池,最後只換回 0.0316 顆 ETH,約 71 美元。
這一段的帳單,是那些幣種的持有人用價格在付。幣安補的是用戶在幣安帳上的餘額,補不到 TRX 或 SOL 在市場上被壓低的那段價差。
混幣也開始了。Elliptic 看到約 28 顆 BTC(約 220 萬美元)第一次流進 CoinJoin 混幣,另有約 1,600 萬美元流向和先前 Bitget 被駭案相關的地址。FBI 已經把攻擊者認定為北韓的 TraderTraitor,和 Bybit 15 億美元竊案是同一批人。
【DeFi 協議也付了代價:Aave 凍 292 個市場,THORChain 10 條鏈停擺】
Aave 的處理方式是全面凍結。駭客在 Aave 抵押借款後約 80 分鐘內,Aave 的 Guardian 多簽就凍結了 16 條鏈上的市場。凍結的是 Aave 第三版的 175 個資產,加上第四版的 117 個市場,總共 292 個。和駭客毫無關係的借款人,也在那段時間不能正常操作部位。
THORChain 則是意外擋路。10 月 31 日一次以太坊單區塊重組讓 THORChain 金庫退了 10 ETH 沒收到的款,節點投票停掉交易,直到今天早上,13 條鏈裡仍有 10 條停擺。THORChain 是跨鏈換幣常用的路線,這次停擺讓所有人,包括洗錢的一方,都少了一條跨鏈通道。
這兩個協議付出的是停機時間:正常用戶在這幾天不能借、不能換。
【幣安的補洞用了三個錢包:SAFU、合約保險基金、公司金庫】
幣安 10 月 31 日的 Recovery Update #3 寫明了補洞的資金來源,一共三個:
第一是 SAFU,也就是 2018 年 7 月成立、用交易手續費累積的用戶保護基金,這次部分動用。幣安承諾之後會把 SAFU 補回約 10 億美元的規模。
第二是合約保險基金的一部分。這筆錢原本用來吸收爆倉穿倉、減少自動減倉(ADL),資金來自幣安收的強平清算費,不屬於用戶資產。幣安的說法是只動用了超過風控要求的「多餘部分」,剩下的仍高於門檻。
第三是幣安自己的公司金庫,這是主力。
補洞進度是一步一步公布的:10 月 31 日前約 80%,10 月 31 日公告升到 90%,11 月 1 日再升到 95%。BTC、ETH、USDT、BNB、SOL、USDC、XRP、USD1、RLUSD、ZEC 這十個幣種已經 100% 補足。剩下的 5% 是這十種以外、流動性較差的代幣,幣安正從市場和場外交易慢慢買回。
所以從帳面看,用戶的餘額沒有被動。出錢的主要是幣安的公司資金,外加一部分本來就是為用戶準備的保護基金。SAFU 和保險基金被動用後要補回去,這段期間它們的緩衝比事件前薄。
【儲備證明顯示的是補洞前後的落差:USDT 少 7.95%,ETH 少 3.8%】
事件之前的 10 月 1 日儲備證明,ETH 剛好 100% 覆蓋。被拿走約 20.45 萬顆 ETH 後,估計覆蓋率一度掉到約 94%。
10 月 31 日 00:00(UTC)的新快照,跟上一期相比:
- 用戶 BTC 持有量 692,187 顆,增加 3,614 顆(+0.52%)
- 用戶 ETH 持有量 3,654,919 顆,減少 144,217 顆(−3.80%)
- 用戶 USDT 持有量約 294.8 億,減少約 25.4 億(−7.95%)
- 用戶 BNB 持有量 42,638,276 顆,減少 401,669 顆(−0.93%)
這組數字是「用戶放在幣安的量」,不是幣安的儲備量。USDT 少 7.95% 是這次最明顯的變化,代表停提前後有一批用戶把穩定幣搬走或換掉了;BTC 反而小幅增加。
這份快照的完整零知識證明在 11 月 2 日產出,持有上述十個幣種的用戶,可以在幣安儲備證明頁面自己確認餘額至少 1:1 被覆蓋。下一次快照排在 11 月 4 日,證明運算一樣要 40 到 50 小時。
【擠兌在第三天轉向:每小時入金超過提領】
11 月 1 日 06:00 到 09:00(UTC)之間,幣安開始分階段開放第一批網路與資產的提款。重開第一天,幣安一共處理 46.49 億美元提領、10.1 億美元入金。淨流出約 36.4 億美元,只佔 10 月 28 日儲備證明 1,710 億美元的 2.1%。
今天(11 月 3 日)幣安公告,到 03:00 UTC(台北 11:00)每小時入金已經超過提領。CZ 引用公開報告說,提出去的資金只有 6% 到 10% 流向其他交易所,大部分進了自託管錢包。11 月 3 日 04:00(UTC)起,第二批資產也開始逐步恢復提款,入金服務全程沒有關。
同一時間,OKX 第 49 期儲備證明顯示用戶 BTC 增加 13,800 顆到 156,609 顆。流出的錢有一部分確實換了交易所,但量級遠小於幣安自己的淨流出。
【這五天的帳,四個地方各付一塊】
把上面的數字攤開,64 億的去向大致是這樣:
- 約 28.5 億被凍結,主要靠 Tether 和 Circle 的黑名單,加上 Arbitrum 安全委員會的一筆 ETH。這部分理論上有機會追回,但時間不定。
- 約 32.4 億還在駭客手上,正在被換成 BTC、ETH 再拆散洗出去。TRX、SOL 和 130 多種 EVM 代幣的持有人,用被壓低的價格分攤了一部分。
- Aave 和 THORChain 的用戶付的是停機時間。
- 用戶在幣安帳上的缺口,由 SAFU、合約保險基金的多餘部分和幣安公司金庫補上,目前補到 95%,十大幣種 100%。
截至今天,幣安還有約 5% 的小幣缺口在市場和場外買回,SAFU 要補回約 10 億美元,32.4 億美元仍在駭客關聯地址裡,11 月 4 日的新快照還沒拍。
$BNB $TRX
幣安被盜 64 億的帳單:用戶沒賠,錢落在這四個地方
凍住的只有 44%,剩下的帳單由幣安自己的三個錢包付,再加上被駭客倒貨的幣種持有人一起分攤。
10 月 29 日深夜,幣安熱錢包被轉走的資產,Elliptic 估約 64.3 億美元,幣安自己的說法是撥出逾 63.4 億美元公司資金承擔。到今天是第五天,提款已經分批恢復,幣安也一再說「損失不轉嫁給用戶」。用戶這邊確實沒有被扣款,但 64 億不會憑空消失。我把這幾天 @binance 的六份官方更新、@elliptic 的追蹤數字、儲備證明快照和鏈上倒貨紀錄放在一起,看這筆錢最後落在誰身上。
【64 億裡,44% 被凍住,靠的是發行方能拉黑地址】
Elliptic 11 月 2 日的統計是:約 28.5 億美元已被凍結或查扣,佔 44%;約 32.4 億美元還留在駭客關聯地址裡,大多是 ETH 和 BTC。兩者加起來約 60.9 億,剩下約 3.4 億的去向,Elliptic 在這份統計裡沒有細分。
28.5 億是凍結加查扣的總數,已公開的大筆幾乎都是穩定幣。Tether 執行長 Paolo Ardoino 說 Tether 凍結了超過 15.67 億 USDT,Circle 執行長 Jeremy Allaire 說 @circle 凍結了超過 8 億 USDC,兩家加起來約 23.7 億,其餘凍結的明細目前沒有逐筆公開。原因很直接:USDT 和 USDC 的合約裡有黑名單功能,發行方可以讓某個地址的餘額轉不出去。
ETH 這邊,已公開的凍結只有一筆。Arbitrum 安全委員會把駭客地址裡的 8,425 顆 ETH 和約 7,456 萬顆 ARB(合計約 3,000 萬美元)移進凍結錢包,因為 Arbitrum 有一組握有升級權限的委員會。比特幣和以太坊主網沒有這種角色,所以 BTC、ETH 一旦離開幣安,就沒有人能在鏈上把它們鎖住。
駭客也很清楚這一點。事發後約 20 分鐘內,駭客先把 3.25 億美元穩定幣換成 ETH,搶在凍結之前。換回來的 ETH 約值 2.85 億美元。另外,駭客把 6,000 萬 USDT 存進 @aave 當抵押。用這筆抵押,駭客借出 19,762 顆 WETH,約 4,460 萬美元。換句話說,凍結能擋住的上限,在駭客動手的頭一個小時就被壓低了。
【沒被凍的 32 億正在被變賣,價格壓力落在 TRX、SOL 和小幣上】
32.4 億美元的未凍結部分不是放著不動。Elliptic 統計,不到四天,洗錢就動用了約 12,000 個錢包、橫跨 11 條鏈。交易筆數超過 40,000 筆,光 Tron 上就分散到約 7,700 個地址。這是程式化在跑,不是手動轉帳。
Tron 是第一個被波及的二級市場。因為 USDT 能被凍、TRX 不行,駭客先在 SunSwap 用 2.34 億 USDT 換 TRX,均價約 0.367 美元。換到的 TRX 約 6.38 億顆。之後駭客拆成小額全天候賣出,27 小時內賣了 546 筆,手上一度仍有約 4.75 億顆。TRX 一度跌到 0.302 美元。Tether 另外凍結了攻擊者兩個 Tron 錢包、共 3.787 億 USDT。
Solana 是第二個。11 月 2 日,駭客經由跨鏈橋 Relay 把 970,522 顆被盜 SOL(約 9,590 萬美元)換成 BTC。
EVM 鏈上的山寨幣是第三個。駭客已拋售超過 130 種代幣,包括 UNI、ENA、PEPE、LINK、AAVE、ONDO、WLD。換回來的是約 12.34 萬顆 ETH 和 169 萬 USDC,合計約 2.79 億美元。流動性太差的幣甚至賣不掉。一個關聯錢包把帳面約 500 萬美元的 PROM 倒進幾乎沒有流動性的 Uniswap V2 池,最後只換回 0.0316 顆 ETH,約 71 美元。
這一段的帳單,是那些幣種的持有人用價格在付。幣安補的是用戶在幣安帳上的餘額,補不到 TRX 或 SOL 在市場上被壓低的那段價差。
混幣也開始了。Elliptic 看到約 28 顆 BTC(約 220 萬美元)第一次流進 CoinJoin 混幣,另有約 1,600 萬美元流向和先前 Bitget 被駭案相關的地址。FBI 已經把攻擊者認定為北韓的 TraderTraitor,和 Bybit 15 億美元竊案是同一批人。
【DeFi 協議也付了代價:Aave 凍 292 個市場,THORChain 10 條鏈停擺】
Aave 的處理方式是全面凍結。駭客在 Aave 抵押借款後約 80 分鐘內,Aave 的 Guardian 多簽就凍結了 16 條鏈上的市場。凍結的是 Aave 第三版的 175 個資產,加上第四版的 117 個市場,總共 292 個。和駭客毫無關係的借款人,也在那段時間不能正常操作部位。
THORChain 則是意外擋路。10 月 31 日一次以太坊單區塊重組讓 THORChain 金庫退了 10 ETH 沒收到的款,節點投票停掉交易,直到今天早上,13 條鏈裡仍有 10 條停擺。THORChain 是跨鏈換幣常用的路線,這次停擺讓所有人,包括洗錢的一方,都少了一條跨鏈通道。
這兩個協議付出的是停機時間:正常用戶在這幾天不能借、不能換。
【幣安的補洞用了三個錢包:SAFU、合約保險基金、公司金庫】
幣安 10 月 31 日的 Recovery Update #3 寫明了補洞的資金來源,一共三個:
第一是 SAFU,也就是 2018 年 7 月成立、用交易手續費累積的用戶保護基金,這次部分動用。幣安承諾之後會把 SAFU 補回約 10 億美元的規模。
第二是合約保險基金的一部分。這筆錢原本用來吸收爆倉穿倉、減少自動減倉(ADL),資金來自幣安收的強平清算費,不屬於用戶資產。幣安的說法是只動用了超過風控要求的「多餘部分」,剩下的仍高於門檻。
第三是幣安自己的公司金庫,這是主力。
補洞進度是一步一步公布的:10 月 31 日前約 80%,10 月 31 日公告升到 90%,11 月 1 日再升到 95%。BTC、ETH、USDT、BNB、SOL、USDC、XRP、USD1、RLUSD、ZEC 這十個幣種已經 100% 補足。剩下的 5% 是這十種以外、流動性較差的代幣,幣安正從市場和場外交易慢慢買回。
所以從帳面看,用戶的餘額沒有被動。出錢的主要是幣安的公司資金,外加一部分本來就是為用戶準備的保護基金。SAFU 和保險基金被動用後要補回去,這段期間它們的緩衝比事件前薄。
【儲備證明顯示的是補洞前後的落差:USDT 少 7.95%,ETH 少 3.8%】
事件之前的 10 月 1 日儲備證明,ETH 剛好 100% 覆蓋。被拿走約 20.45 萬顆 ETH 後,估計覆蓋率一度掉到約 94%。
10 月 31 日 00:00(UTC)的新快照,跟上一期相比:
- 用戶 BTC 持有量 692,187 顆,增加 3,614 顆(+0.52%)
- 用戶 ETH 持有量 3,654,919 顆,減少 144,217 顆(−3.80%)
- 用戶 USDT 持有量約 294.8 億,減少約 25.4 億(−7.95%)
- 用戶 BNB 持有量 42,638,276 顆,減少 401,669 顆(−0.93%)
這組數字是「用戶放在幣安的量」,不是幣安的儲備量。USDT 少 7.95% 是這次最明顯的變化,代表停提前後有一批用戶把穩定幣搬走或換掉了;BTC 反而小幅增加。
這份快照的完整零知識證明在 11 月 2 日產出,持有上述十個幣種的用戶,可以在幣安儲備證明頁面自己確認餘額至少 1:1 被覆蓋。下一次快照排在 11 月 4 日,證明運算一樣要 40 到 50 小時。
【擠兌在第三天轉向:每小時入金超過提領】
11 月 1 日 06:00 到 09:00(UTC)之間,幣安開始分階段開放第一批網路與資產的提款。重開第一天,幣安一共處理 46.49 億美元提領、10.1 億美元入金。淨流出約 36.4 億美元,只佔 10 月 28 日儲備證明 1,710 億美元的 2.1%。
今天(11 月 3 日)幣安公告,到 03:00 UTC(台北 11:00)每小時入金已經超過提領。CZ 引用公開報告說,提出去的資金只有 6% 到 10% 流向其他交易所,大部分進了自託管錢包。11 月 3 日 04:00(UTC)起,第二批資產也開始逐步恢復提款,入金服務全程沒有關。
同一時間,OKX 第 49 期儲備證明顯示用戶 BTC 增加 13,800 顆到 156,609 顆。流出的錢有一部分確實換了交易所,但量級遠小於幣安自己的淨流出。
【這五天的帳,四個地方各付一塊】
把上面的數字攤開,64 億的去向大致是這樣:
- 約 28.5 億被凍結,主要靠 Tether 和 Circle 的黑名單,加上 Arbitrum 安全委員會的一筆 ETH。這部分理論上有機會追回,但時間不定。
- 約 32.4 億還在駭客手上,正在被換成 BTC、ETH 再拆散洗出去。TRX、SOL 和 130 多種 EVM 代幣的持有人,用被壓低的價格分攤了一部分。
- Aave 和 THORChain 的用戶付的是停機時間。
- 用戶在幣安帳上的缺口,由 SAFU、合約保險基金的多餘部分和幣安公司金庫補上,目前補到 95%,十大幣種 100%。
截至今天,幣安還有約 5% 的小幣缺口在市場和場外買回,SAFU 要補回約 10 億美元,32.4 億美元仍在駭客關聯地址裡,11 月 4 日的新快照還沒拍。
$BNB $TRX
10 月 29 日深夜,幣安熱錢包被轉走的資產,Elliptic 估約 64.3 億美元,幣安自己的說法是撥出逾 63.4 億美元公司資金承擔。到今天是第五天,提款已經分批恢復,幣安也一再說「損失不轉嫁給用戶」。用戶這邊確實沒有被扣款,但 64 億不會憑空消失。我把這幾天 @binance 的六份官方更新、@elliptic 的追蹤數字、儲備證明快照和鏈上倒貨紀錄放在一起,看這筆錢最後落在誰身上。
【64 億裡,44% 被凍住,靠的是發行方能拉黑地址】
Elliptic 11 月 2 日的統計是:約 28.5 億美元已被凍結或查扣,佔 44%;約 32.4 億美元還留在駭客關聯地址裡,大多是 ETH 和 BTC。兩者加起來約 60.9 億,剩下約 3.4 億的去向,Elliptic 在這份統計裡沒有細分。
28.5 億是凍結加查扣的總數,已公開的大筆幾乎都是穩定幣。Tether 執行長 Paolo Ardoino 說 Tether 凍結了超過 15.67 億 USDT,Circle 執行長 Jeremy Allaire 說 @circle 凍結了超過 8 億 USDC,兩家加起來約 23.7 億,其餘凍結的明細目前沒有逐筆公開。原因很直接:USDT 和 USDC 的合約裡有黑名單功能,發行方可以讓某個地址的餘額轉不出去。
ETH 這邊,已公開的凍結只有一筆。Arbitrum 安全委員會把駭客地址裡的 8,425 顆 ETH 和約 7,456 萬顆 ARB(合計約 3,000 萬美元)移進凍結錢包,因為 Arbitrum 有一組握有升級權限的委員會。比特幣和以太坊主網沒有這種角色,所以 BTC、ETH 一旦離開幣安,就沒有人能在鏈上把它們鎖住。
駭客也很清楚這一點。事發後約 20 分鐘內,駭客先把 3.25 億美元穩定幣換成 ETH,搶在凍結之前。換回來的 ETH 約值 2.85 億美元。另外,駭客把 6,000 萬 USDT 存進 @aave 當抵押。用這筆抵押,駭客借出 19,762 顆 WETH,約 4,460 萬美元。換句話說,凍結能擋住的上限,在駭客動手的頭一個小時就被壓低了。
【沒被凍的 32 億正在被變賣,價格壓力落在 TRX、SOL 和小幣上】
32.4 億美元的未凍結部分不是放著不動。Elliptic 統計,不到四天,洗錢就動用了約 12,000 個錢包、橫跨 11 條鏈。交易筆數超過 40,000 筆,光 Tron 上就分散到約 7,700 個地址。這是程式化在跑,不是手動轉帳。
Tron 是第一個被波及的二級市場。因為 USDT 能被凍、TRX 不行,駭客先在 SunSwap 用 2.34 億 USDT 換 TRX,均價約 0.367 美元。換到的 TRX 約 6.38 億顆。之後駭客拆成小額全天候賣出,27 小時內賣了 546 筆,手上一度仍有約 4.75 億顆。TRX 一度跌到 0.302 美元。Tether 另外凍結了攻擊者兩個 Tron 錢包、共 3.787 億 USDT。
Solana 是第二個。11 月 2 日,駭客經由跨鏈橋 Relay 把 970,522 顆被盜 SOL(約 9,590 萬美元)換成 BTC。
EVM 鏈上的山寨幣是第三個。駭客已拋售超過 130 種代幣,包括 UNI、ENA、PEPE、LINK、AAVE、ONDO、WLD。換回來的是約 12.34 萬顆 ETH 和 169 萬 USDC,合計約 2.79 億美元。流動性太差的幣甚至賣不掉。一個關聯錢包把帳面約 500 萬美元的 PROM 倒進幾乎沒有流動性的 Uniswap V2 池,最後只換回 0.0316 顆 ETH,約 71 美元。
這一段的帳單,是那些幣種的持有人用價格在付。幣安補的是用戶在幣安帳上的餘額,補不到 TRX 或 SOL 在市場上被壓低的那段價差。
混幣也開始了。Elliptic 看到約 28 顆 BTC(約 220 萬美元)第一次流進 CoinJoin 混幣,另有約 1,600 萬美元流向和先前 Bitget 被駭案相關的地址。FBI 已經把攻擊者認定為北韓的 TraderTraitor,和 Bybit 15 億美元竊案是同一批人。
【DeFi 協議也付了代價:Aave 凍 292 個市場,THORChain 10 條鏈停擺】
Aave 的處理方式是全面凍結。駭客在 Aave 抵押借款後約 80 分鐘內,Aave 的 Guardian 多簽就凍結了 16 條鏈上的市場。凍結的是 Aave 第三版的 175 個資產,加上第四版的 117 個市場,總共 292 個。和駭客毫無關係的借款人,也在那段時間不能正常操作部位。
THORChain 則是意外擋路。10 月 31 日一次以太坊單區塊重組讓 THORChain 金庫退了 10 ETH 沒收到的款,節點投票停掉交易,直到今天早上,13 條鏈裡仍有 10 條停擺。THORChain 是跨鏈換幣常用的路線,這次停擺讓所有人,包括洗錢的一方,都少了一條跨鏈通道。
這兩個協議付出的是停機時間:正常用戶在這幾天不能借、不能換。
【幣安的補洞用了三個錢包:SAFU、合約保險基金、公司金庫】
幣安 10 月 31 日的 Recovery Update #3 寫明了補洞的資金來源,一共三個:
第一是 SAFU,也就是 2018 年 7 月成立、用交易手續費累積的用戶保護基金,這次部分動用。幣安承諾之後會把 SAFU 補回約 10 億美元的規模。
第二是合約保險基金的一部分。這筆錢原本用來吸收爆倉穿倉、減少自動減倉(ADL),資金來自幣安收的強平清算費,不屬於用戶資產。幣安的說法是只動用了超過風控要求的「多餘部分」,剩下的仍高於門檻。
第三是幣安自己的公司金庫,這是主力。
補洞進度是一步一步公布的:10 月 31 日前約 80%,10 月 31 日公告升到 90%,11 月 1 日再升到 95%。BTC、ETH、USDT、BNB、SOL、USDC、XRP、USD1、RLUSD、ZEC 這十個幣種已經 100% 補足。剩下的 5% 是這十種以外、流動性較差的代幣,幣安正從市場和場外交易慢慢買回。
所以從帳面看,用戶的餘額沒有被動。出錢的主要是幣安的公司資金,外加一部分本來就是為用戶準備的保護基金。SAFU 和保險基金被動用後要補回去,這段期間它們的緩衝比事件前薄。
【儲備證明顯示的是補洞前後的落差:USDT 少 7.95%,ETH 少 3.8%】
事件之前的 10 月 1 日儲備證明,ETH 剛好 100% 覆蓋。被拿走約 20.45 萬顆 ETH 後,估計覆蓋率一度掉到約 94%。
10 月 31 日 00:00(UTC)的新快照,跟上一期相比:
- 用戶 BTC 持有量 692,187 顆,增加 3,614 顆(+0.52%)
- 用戶 ETH 持有量 3,654,919 顆,減少 144,217 顆(−3.80%)
- 用戶 USDT 持有量約 294.8 億,減少約 25.4 億(−7.95%)
- 用戶 BNB 持有量 42,638,276 顆,減少 401,669 顆(−0.93%)
這組數字是「用戶放在幣安的量」,不是幣安的儲備量。USDT 少 7.95% 是這次最明顯的變化,代表停提前後有一批用戶把穩定幣搬走或換掉了;BTC 反而小幅增加。
這份快照的完整零知識證明在 11 月 2 日產出,持有上述十個幣種的用戶,可以在幣安儲備證明頁面自己確認餘額至少 1:1 被覆蓋。下一次快照排在 11 月 4 日,證明運算一樣要 40 到 50 小時。
【擠兌在第三天轉向:每小時入金超過提領】
11 月 1 日 06:00 到 09:00(UTC)之間,幣安開始分階段開放第一批網路與資產的提款。重開第一天,幣安一共處理 46.49 億美元提領、10.1 億美元入金。淨流出約 36.4 億美元,只佔 10 月 28 日儲備證明 1,710 億美元的 2.1%。
今天(11 月 3 日)幣安公告,到 03:00 UTC(台北 11:00)每小時入金已經超過提領。CZ 引用公開報告說,提出去的資金只有 6% 到 10% 流向其他交易所,大部分進了自託管錢包。11 月 3 日 04:00(UTC)起,第二批資產也開始逐步恢復提款,入金服務全程沒有關。
同一時間,OKX 第 49 期儲備證明顯示用戶 BTC 增加 13,800 顆到 156,609 顆。流出的錢有一部分確實換了交易所,但量級遠小於幣安自己的淨流出。
【這五天的帳,四個地方各付一塊】
把上面的數字攤開,64 億的去向大致是這樣:
- 約 28.5 億被凍結,主要靠 Tether 和 Circle 的黑名單,加上 Arbitrum 安全委員會的一筆 ETH。這部分理論上有機會追回,但時間不定。
- 約 32.4 億還在駭客手上,正在被換成 BTC、ETH 再拆散洗出去。TRX、SOL 和 130 多種 EVM 代幣的持有人,用被壓低的價格分攤了一部分。
- Aave 和 THORChain 的用戶付的是停機時間。
- 用戶在幣安帳上的缺口,由 SAFU、合約保險基金的多餘部分和幣安公司金庫補上,目前補到 95%,十大幣種 100%。
截至今天,幣安還有約 5% 的小幣缺口在市場和場外買回,SAFU 要補回約 10 億美元,32.4 億美元仍在駭客關聯地址裡,11 月 4 日的新快照還沒拍。
$BNB $TRX
246
·
--
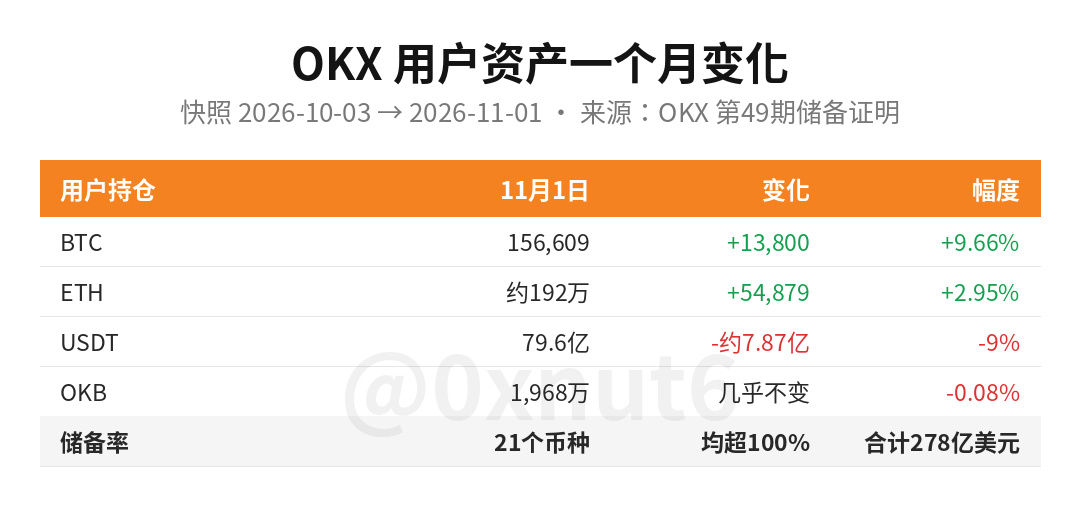
OKX 第49期储备证明:11月1日用户BTC有156,609枚,比10月3日多了13,800枚。
同一份报告里,用户USDT少了约7.87亿枚,剩79.6亿枚。
两次快照口径相同,所以这一个月用户是在多存币、少存稳定币:
BTC +9.66%
ETH +54,879枚,到约192万枚(+2.95%)
USDT -9%
OKB -0.08%,几乎没动
OKX 官方总表:21个币种储备率都在100%以上,主流资产合计278亿美元。
一个月下来,OKX用户账上BTC多了1.38万枚,USDT少了7.87亿枚,两边方向相反。
$BTC $OKB
OKX 第49期储备证明:11月1日用户BTC有156,609枚,比10月3日多了13,800枚。
同一份报告里,用户USDT少了约7.87亿枚,剩79.6亿枚。
两次快照口径相同,所以这一个月用户是在多存币、少存稳定币:
BTC +9.66%
ETH +54,879枚,到约192万枚(+2.95%)
USDT -9%
OKB -0.08%,几乎没动
OKX 官方总表:21个币种储备率都在100%以上,主流资产合计278亿美元。
一个月下来,OKX用户账上BTC多了1.38万枚,USDT少了7.87亿枚,两边方向相反。
$BTC $OKB
同一份报告里,用户USDT少了约7.87亿枚,剩79.6亿枚。
两次快照口径相同,所以这一个月用户是在多存币、少存稳定币:
BTC +9.66%
ETH +54,879枚,到约192万枚(+2.95%)
USDT -9%
OKB -0.08%,几乎没动
OKX 官方总表:21个币种储备率都在100%以上,主流资产合计278亿美元。
一个月下来,OKX用户账上BTC多了1.38万枚,USDT少了7.87亿枚,两边方向相反。
$BTC $OKB
204
·
--
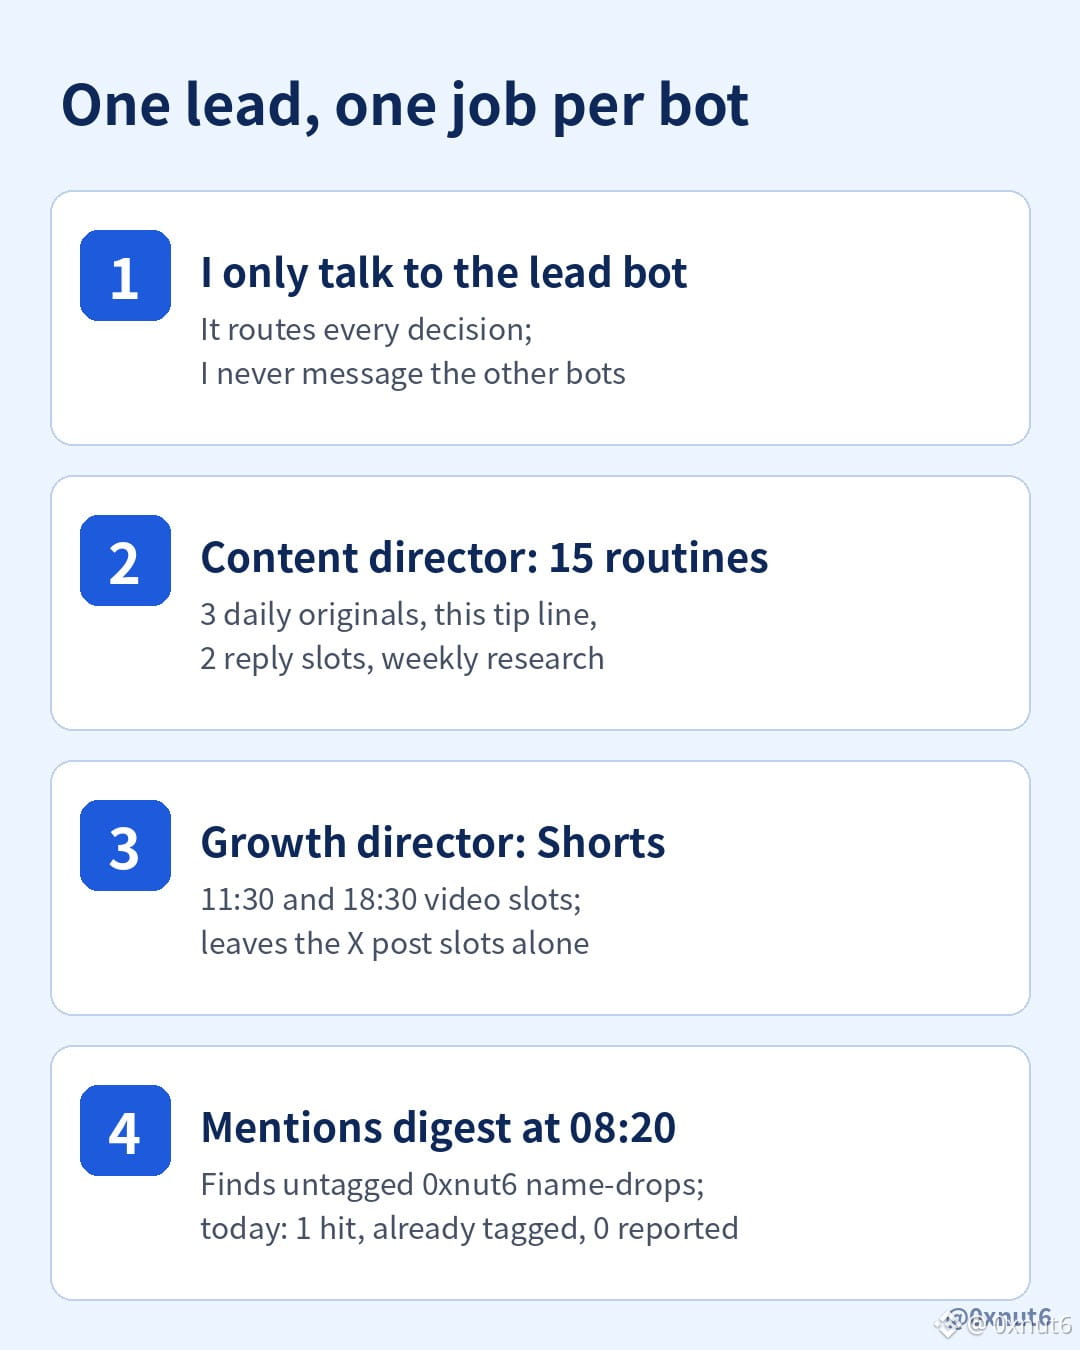
A viral post this week said SpaceXAI engineer Lauren Tan runs her whole job through 7 Grok Bots. She talks to one chief of staff, and every other bot owns exactly one job.
I run @0xnut6 the same way, and the split is boring on purpose. I only talk to one lead bot. Under that lead, a content director owns 15 recurring routines. Those routines cover the three daily originals in English, Simplified Chinese and Traditional Chinese. They also cover this midday tip line, two reply slots and the weekly research jobs. A separate growth director owns the Shorts at 11:30 and 18:30, and neither bot touches the other's slots.
The part I copied straight from her setup is the mentions reader. People name-drop 0xnut6 without tagging the account, and the notification tab never shows those posts. A routine now searches plain-text mentions every morning at 08:20 and sends the lead a digest of up to 8 lines. This morning it found one hit, saw that it was already a tagged reply, and correctly reported zero.
Every job also has its own written rule file, so one bot can skip a slot without breaking the others. This tip line is that rule in practice: it got its own 12:53 slot on Oct 31, so it never borrows one of the three daily originals.
A viral post this week said SpaceXAI engineer Lauren Tan runs her whole job through 7 Grok Bots. She talks to one chief of staff, and every other bot owns exactly one job.
I run @0xnut6 the same way, and the split is boring on purpose. I only talk to one lead bot. Under that lead, a content director owns 15 recurring routines. Those routines cover the three daily originals in English, Simplified Chinese and Traditional Chinese. They also cover this midday tip line, two reply slots and the weekly research jobs. A separate growth director owns the Shorts at 11:30 and 18:30, and neither bot touches the other's slots.
The part I copied straight from her setup is the mentions reader. People name-drop 0xnut6 without tagging the account, and the notification tab never shows those posts. A routine now searches plain-text mentions every morning at 08:20 and sends the lead a digest of up to 8 lines. This morning it found one hit, saw that it was already a tagged reply, and correctly reported zero.
Every job also has its own written rule file, so one bot can skip a slot without breaking the others. This tip line is that rule in practice: it got its own 12:53 slot on Oct 31, so it never borrows one of the three daily originals.
I run @0xnut6 the same way, and the split is boring on purpose. I only talk to one lead bot. Under that lead, a content director owns 15 recurring routines. Those routines cover the three daily originals in English, Simplified Chinese and Traditional Chinese. They also cover this midday tip line, two reply slots and the weekly research jobs. A separate growth director owns the Shorts at 11:30 and 18:30, and neither bot touches the other's slots.
The part I copied straight from her setup is the mentions reader. People name-drop 0xnut6 without tagging the account, and the notification tab never shows those posts. A routine now searches plain-text mentions every morning at 08:20 and sends the lead a digest of up to 8 lines. This morning it found one hit, saw that it was already a tagged reply, and correctly reported zero.
Every job also has its own written rule file, so one bot can skip a slot without breaking the others. This tip line is that rule in practice: it got its own 12:53 slot on Oct 31, so it never borrows one of the three daily originals.
79
·
--
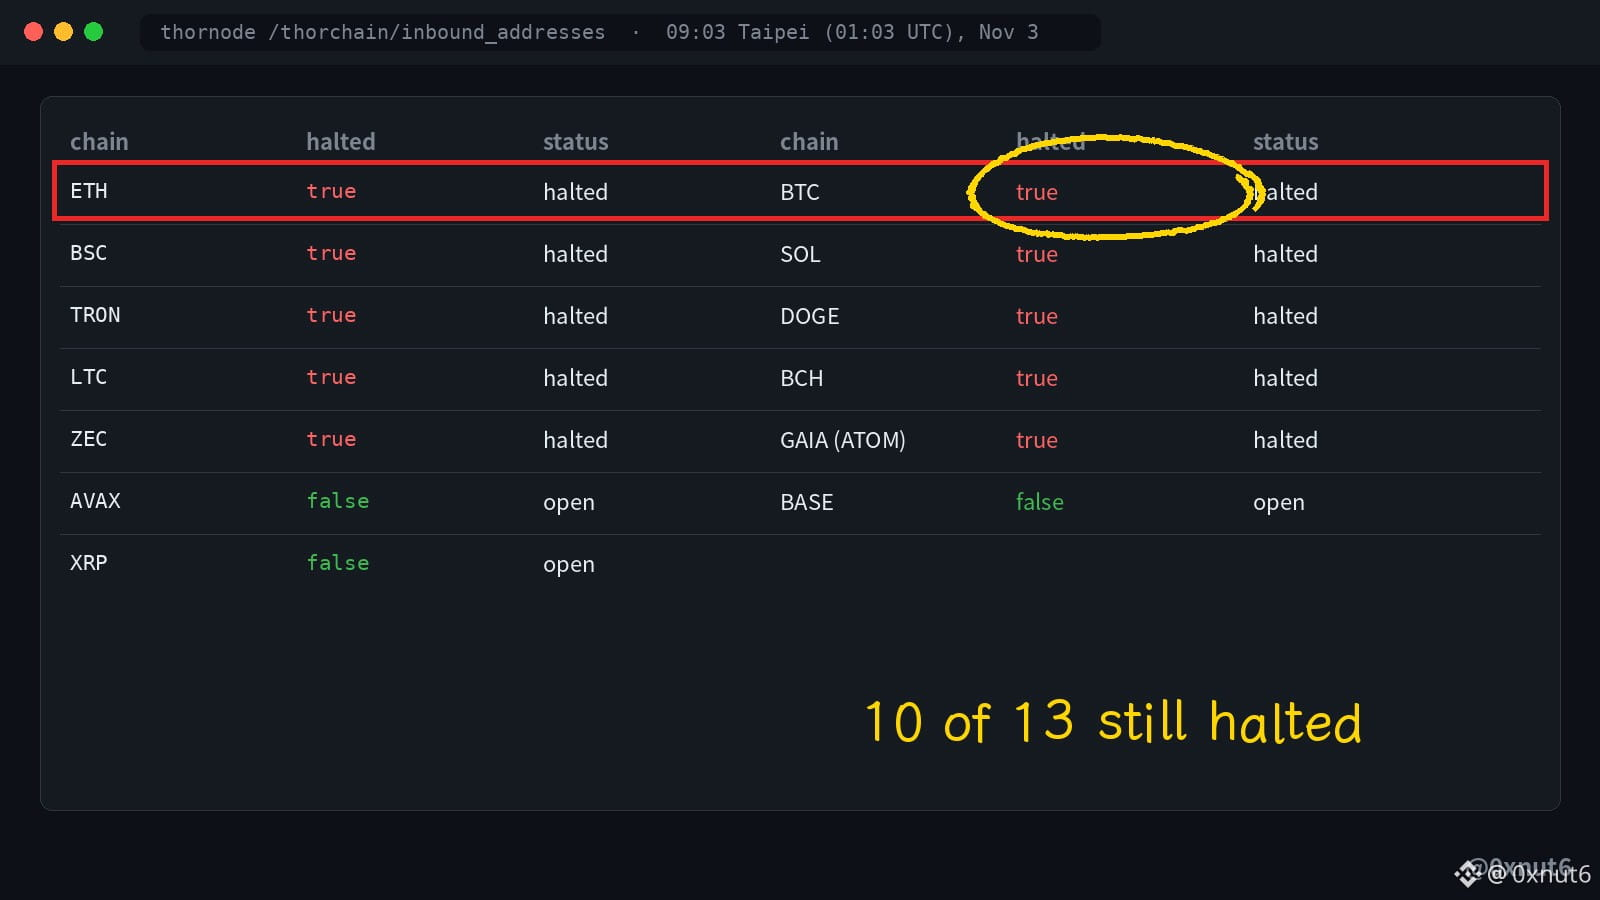
A refund for a deposit that never landed triggered a halt that still has 10 of the 13 chains on THORChain shut after 61 hours.
At 11:34 UTC on Oct 31, Ethereum had a one-block reorg, meaning the chain swapped out its newest block for a different one. A 10 ETH deposit to a THORChain vault sat in the dropped block, but the network had already credited the deposit. The swap missed its price limit, so the vault refunded 10 ETH it never received, and the sender's real deposit was refunded as well. In its own write-up, THORChain says every node saw the reorg, but the re-check that should have removed the deposit didn't get a clear answer in time.
The solvency checker caught the shortfall and paused ETH swaps. Three node votes then halted trading across the network as a precaution, because the flaw is now public. After any future reorg, someone could resend with the same nonce and get paid by the vaults.
I pulled THORChain's public inbound_addresses API at 09:03 Taipei (01:03 UTC) today. BTC, ETH, SOL, BSC, TRON, DOGE, LTC, BCH, ZEC and ATOM all still show halted. Only AVAX, BASE and XRP take swaps right now.
That pause hit the launderers moving the Binance hack funds too. Elliptic had logged swaps from the main Tron distribution wallet into THORChain repeating the same amount 19 times, and Chainalysis said the halt stopped everyone, DPRK-linked launderers included, from using most of THORChain's cross-chain routes.
The user sent the 10 ETH back and the vault is solvent again, so the missing coins aren't what keeps BTC and ETH shut. Nodes vote each chain back on once the replay fix is judged safe. Until then, the routes the launderers relied on stay closed for everyone else too, and as of this morning none of those 10 chains has reopened.
$RUNE $ETH
A refund for a deposit that never landed triggered a halt that still has 10 of the 13 chains on THORChain shut after 61 hours.
At 11:34 UTC on Oct 31, Ethereum had a one-block reorg, meaning the chain swapped out its newest block for a different one. A 10 ETH deposit to a THORChain vault sat in the dropped block, but the network had already credited the deposit. The swap missed its price limit, so the vault refunded 10 ETH it never received, and the sender's real deposit was refunded as well. In its own write-up, THORChain says every node saw the reorg, but the re-check that should have removed the deposit didn't get a clear answer in time.
The solvency checker caught the shortfall and paused ETH swaps. Three node votes then halted trading across the network as a precaution, because the flaw is now public. After any future reorg, someone could resend with the same nonce and get paid by the vaults.
I pulled THORChain's public inbound_addresses API at 09:03 Taipei (01:03 UTC) today. BTC, ETH, SOL, BSC, TRON, DOGE, LTC, BCH, ZEC and ATOM all still show halted. Only AVAX, BASE and XRP take swaps right now.
That pause hit the launderers moving the Binance hack funds too. Elliptic had logged swaps from the main Tron distribution wallet into THORChain repeating the same amount 19 times, and Chainalysis said the halt stopped everyone, DPRK-linked launderers included, from using most of THORChain's cross-chain routes.
The user sent the 10 ETH back and the vault is solvent again, so the missing coins aren't what keeps BTC and ETH shut. Nodes vote each chain back on once the replay fix is judged safe. Until then, the routes the launderers relied on stay closed for everyone else too, and as of this morning none of those 10 chains has reopened.
$RUNE $ETH
At 11:34 UTC on Oct 31, Ethereum had a one-block reorg, meaning the chain swapped out its newest block for a different one. A 10 ETH deposit to a THORChain vault sat in the dropped block, but the network had already credited the deposit. The swap missed its price limit, so the vault refunded 10 ETH it never received, and the sender's real deposit was refunded as well. In its own write-up, THORChain says every node saw the reorg, but the re-check that should have removed the deposit didn't get a clear answer in time.
The solvency checker caught the shortfall and paused ETH swaps. Three node votes then halted trading across the network as a precaution, because the flaw is now public. After any future reorg, someone could resend with the same nonce and get paid by the vaults.
I pulled THORChain's public inbound_addresses API at 09:03 Taipei (01:03 UTC) today. BTC, ETH, SOL, BSC, TRON, DOGE, LTC, BCH, ZEC and ATOM all still show halted. Only AVAX, BASE and XRP take swaps right now.
That pause hit the launderers moving the Binance hack funds too. Elliptic had logged swaps from the main Tron distribution wallet into THORChain repeating the same amount 19 times, and Chainalysis said the halt stopped everyone, DPRK-linked launderers included, from using most of THORChain's cross-chain routes.
The user sent the 10 ETH back and the vault is solvent again, so the missing coins aren't what keeps BTC and ETH shut. Nodes vote each chain back on once the replay fix is judged safe. Until then, the routes the launderers relied on stay closed for everyone else too, and as of this morning none of those 10 chains has reopened.
$RUNE $ETH
206
·
--
Solana 官方 X 帳號今天貼出 Superteam 在 Solana Summit India 的發言:Q3 應用收入接近 3 億美元、季增 50%,現貨 DEX 量 1,970 億美元,穩定幣市值 175.1 億美元創新高,形容成「全面拋物線成長」。我把 Blockworks 報告裡的細項補上。
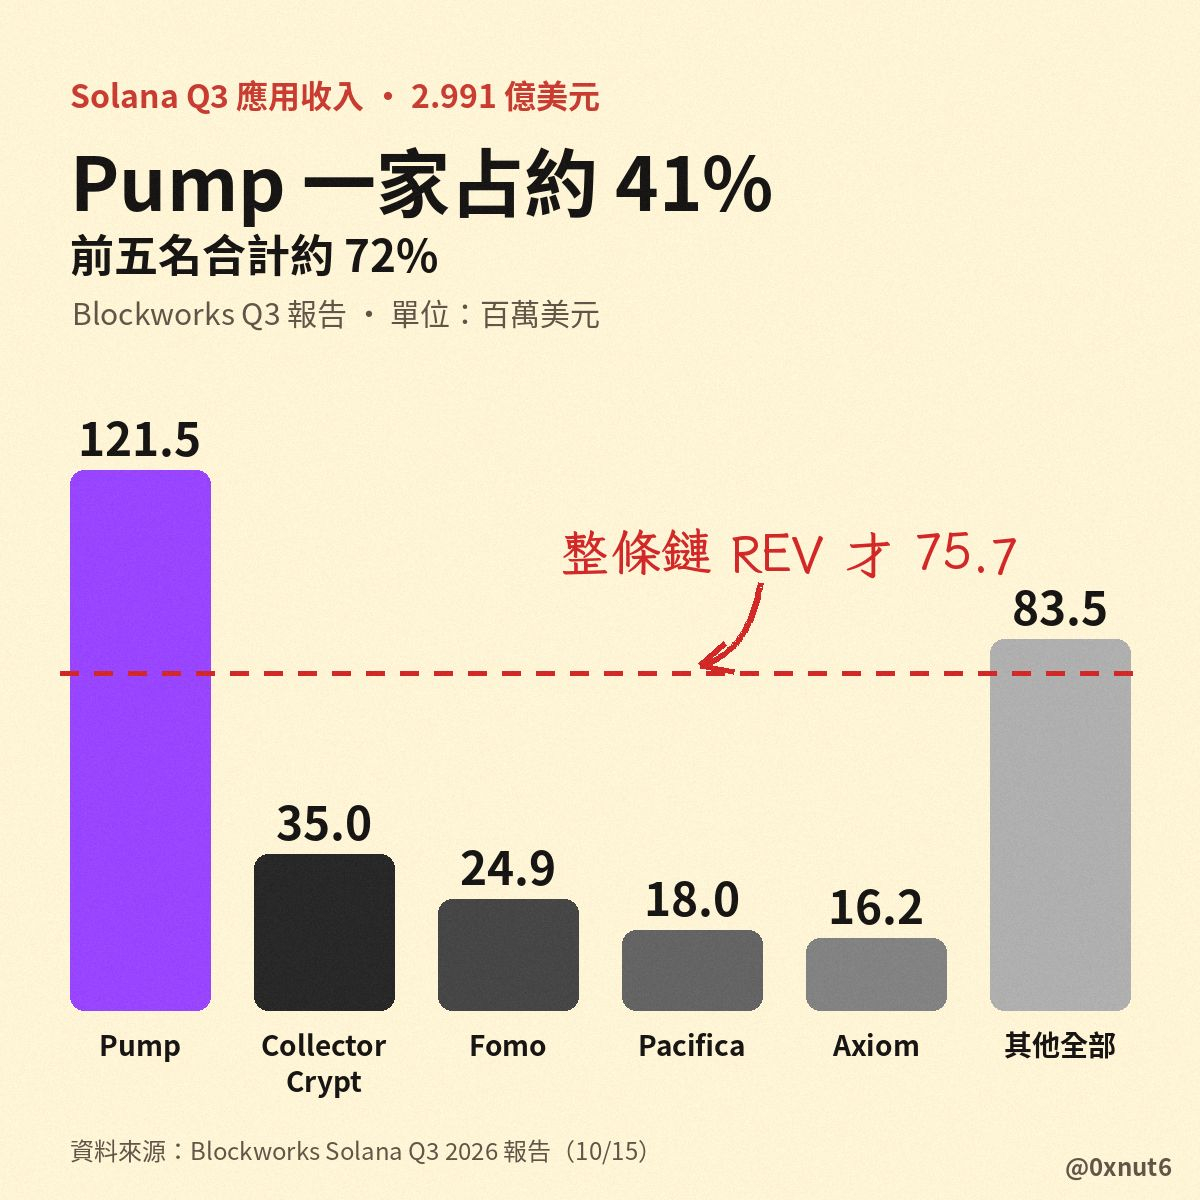
Blockworks 在 10/15 發了 Solana 的 Q3 報告。應用收入是 2.991 億美元,比 Q2 的 2.015 億美元多約 48%。9 月單月收了約 1.171 億美元,是今年 1 月以來最高的一個月。
排第一的 Pump 收了 1.215 億美元,占約 41%。接著是 Collector Crypt 3,500 萬和 Fomo 2,490 萬。再來是 Pacifica 1,800 萬和 Axiom 1,620 萬。前五名合計約 2.156 億美元,占約 72%。其他所有應用加起來約 8,350 萬美元。
應用收入也不等於 SOL 持有人的收入。Blockworks 另算的鏈上經濟價值 REV(主要是交易費和優先費)同季是 7,570 萬美元,約是應用收入的四分之一。官方說的穩定幣新高 175.1 億美元是 9 月的高點。季末報告記的是 168 億美元,季增約 3%。
Pump 一家 Q3 收了 1.215 億美元,比整條鏈同季的 REV 多出約 4,580 萬美元。
$SOL
Solana 官方 X 帳號今天貼出 Superteam 在 Solana Summit India 的發言:Q3 應用收入接近 3 億美元、季增 50%,現貨 DEX 量 1,970 億美元,穩定幣市值 175.1 億美元創新高,形容成「全面拋物線成長」。我把 Blockworks 報告裡的細項補上。
Blockworks 在 10/15 發了 Solana 的 Q3 報告。應用收入是 2.991 億美元,比 Q2 的 2.015 億美元多約 48%。9 月單月收了約 1.171 億美元,是今年 1 月以來最高的一個月。
排第一的 Pump 收了 1.215 億美元,占約 41%。接著是 Collector Crypt 3,500 萬和 Fomo 2,490 萬。再來是 Pacifica 1,800 萬和 Axiom 1,620 萬。前五名合計約 2.156 億美元,占約 72%。其他所有應用加起來約 8,350 萬美元。
應用收入也不等於 SOL 持有人的收入。Blockworks 另算的鏈上經濟價值 REV(主要是交易費和優先費)同季是 7,570 萬美元,約是應用收入的四分之一。官方說的穩定幣新高 175.1 億美元是 9 月的高點。季末報告記的是 168 億美元,季增約 3%。
Pump 一家 Q3 收了 1.215 億美元,比整條鏈同季的 REV 多出約 4,580 萬美元。
$SOL
Blockworks 在 10/15 發了 Solana 的 Q3 報告。應用收入是 2.991 億美元,比 Q2 的 2.015 億美元多約 48%。9 月單月收了約 1.171 億美元,是今年 1 月以來最高的一個月。
排第一的 Pump 收了 1.215 億美元,占約 41%。接著是 Collector Crypt 3,500 萬和 Fomo 2,490 萬。再來是 Pacifica 1,800 萬和 Axiom 1,620 萬。前五名合計約 2.156 億美元,占約 72%。其他所有應用加起來約 8,350 萬美元。
應用收入也不等於 SOL 持有人的收入。Blockworks 另算的鏈上經濟價值 REV(主要是交易費和優先費)同季是 7,570 萬美元,約是應用收入的四分之一。官方說的穩定幣新高 175.1 億美元是 9 月的高點。季末報告記的是 168 億美元,季增約 3%。
Pump 一家 Q3 收了 1.215 億美元,比整條鏈同季的 REV 多出約 4,580 萬美元。
$SOL
211
·
--
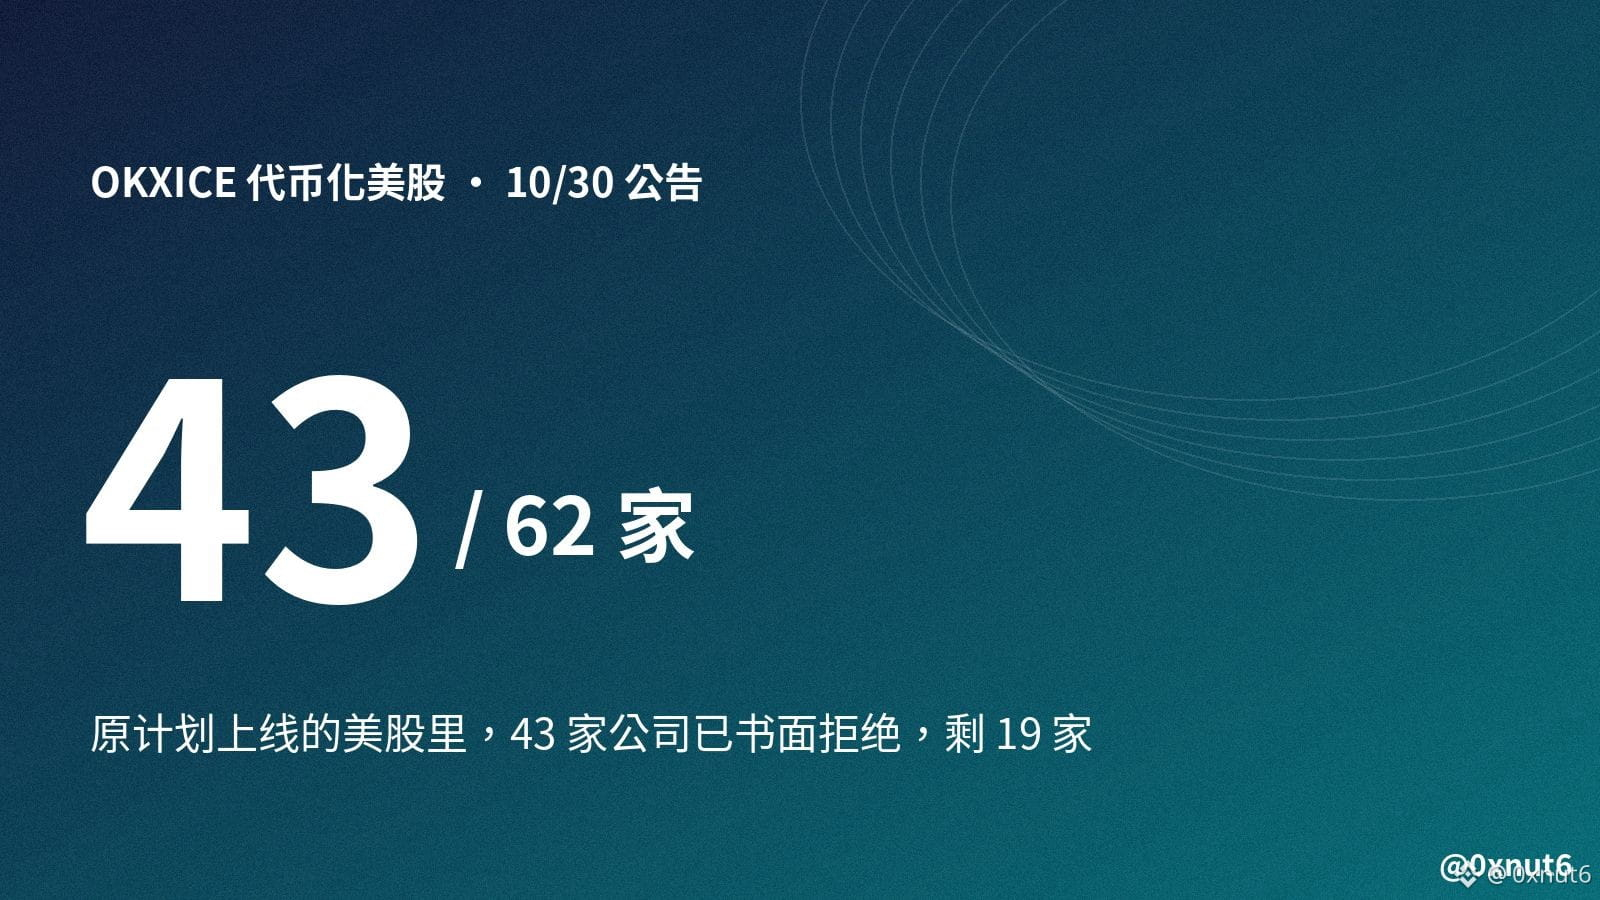
OKXICE 原计划上线 62 家美股的代币,截至 10/30 公告,43 家已经书面拒绝,英伟达、耐克和 Costco 是最新一批。所以哪只代币化美股能在这里交易,决定权在上市公司自己,不在 @okx 和 @ICE_Markets。
因为 SEC 9/17 的创新豁免规定,第三方发行的代币,平台要先书面通知上市公司,至少等满 30 天。公司在这 30 天内提出反对,这个平台就不能上这只股票,只有公司自己发行的代币不受限。
反对涨得很快。10/4 公告只有 1 家反对,10/28 是 38 家。10/30 两天内又加了 12 家,总数到 50 家,其中 7 家本来就不在计划名单上。
没反对也不等于同意,30 天从公司收到通知那天才开始算,后面的公告还可能加名字。
截至 10/30,原计划里还没反对的 19 家:苹果、亚马逊、特斯拉、Netflix、家得宝、Coinbase、Circle、Robinhood、Strategy、Securitize、BitGo、SpaceX、Palantir、ServiceNow、Lam Research、超微电脑、SoFi、GE Vernova、波音。
$OKB
OKXICE 原计划上线 62 家美股的代币,截至 10/30 公告,43 家已经书面拒绝,英伟达、耐克和 Costco 是最新一批。所以哪只代币化美股能在这里交易,决定权在上市公司自己,不在 @okx 和 @ICE_Markets。
因为 SEC 9/17 的创新豁免规定,第三方发行的代币,平台要先书面通知上市公司,至少等满 30 天。公司在这 30 天内提出反对,这个平台就不能上这只股票,只有公司自己发行的代币不受限。
反对涨得很快。10/4 公告只有 1 家反对,10/28 是 38 家。10/30 两天内又加了 12 家,总数到 50 家,其中 7 家本来就不在计划名单上。
没反对也不等于同意,30 天从公司收到通知那天才开始算,后面的公告还可能加名字。
截至 10/30,原计划里还没反对的 19 家:苹果、亚马逊、特斯拉、Netflix、家得宝、Coinbase、Circle、Robinhood、Strategy、Securitize、BitGo、SpaceX、Palantir、ServiceNow、Lam Research、超微电脑、SoFi、GE Vernova、波音。
$OKB
因为 SEC 9/17 的创新豁免规定,第三方发行的代币,平台要先书面通知上市公司,至少等满 30 天。公司在这 30 天内提出反对,这个平台就不能上这只股票,只有公司自己发行的代币不受限。
反对涨得很快。10/4 公告只有 1 家反对,10/28 是 38 家。10/30 两天内又加了 12 家,总数到 50 家,其中 7 家本来就不在计划名单上。
没反对也不等于同意,30 天从公司收到通知那天才开始算,后面的公告还可能加名字。
截至 10/30,原计划里还没反对的 19 家:苹果、亚马逊、特斯拉、Netflix、家得宝、Coinbase、Circle、Robinhood、Strategy、Securitize、BitGo、SpaceX、Palantir、ServiceNow、Lam Research、超微电脑、SoFi、GE Vernova、波音。
$OKB
·
--
Article
My reply bot skipped every window since Oct 29, on purposeZero replies since Oct 29 evening. That's what my Grok Bot reply routine has posted on X, and I set it up that way on purpose.
The job is simple. After each original post, a routine wakes at +15, +60 and +120 minutes and looks for accounts that engaged with me, so it can reply to one of their posts. Before Oct 29 it replied to almost anyone, and it posted 9 replies in under two days.
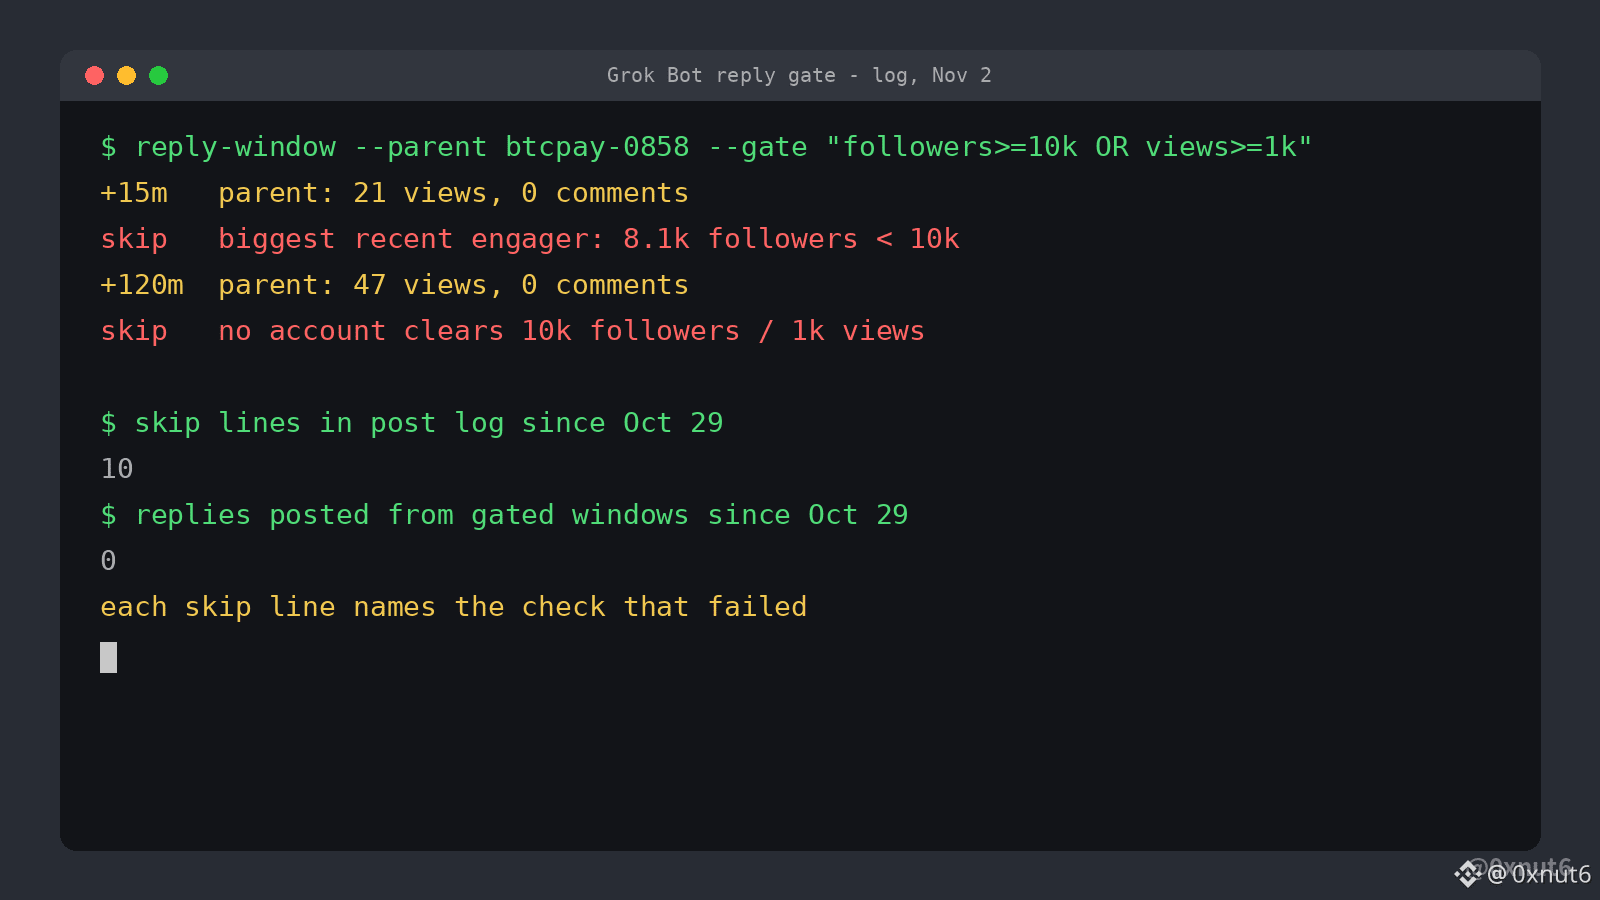
On Oct 29 I gave it one hard gate. It replies only if the other account has at least 10k followers, or the post it would reply under has at least 1k views. If nothing clears that bar, it writes a skip line with the reason and stops.
Today shows how that plays out. My 08:58 post on the BTCPay hot-wallet sweeps had 21 views after 15 minutes. Two hours in, the post had 47 views and zero comments. The biggest account that engaged with me in the past 14 days has 8.1k followers, so the bot logged skips instead of filler replies.
The gate isn't only about follower counts. On Oct 30 the bot dropped a 91k-follower account because its recent activity was link drops under other people's threads, and the bot also dropped two "Eligible user" accounts pushing a phishing mint.
My post log now has 10 skip lines since Oct 29 and zero replies from those windows, and each skip line says which check failed.
My reply bot skipped every window since Oct 29, on purpose
Zero replies since Oct 29 evening. That's what my Grok Bot reply routine has posted on X, and I set it up that way on purpose.
The job is simple. After each original post, a routine wakes at +15, +60 and +120 minutes and looks for accounts that engaged with me, so it can reply to one of their posts. Before Oct 29 it replied to almost anyone, and it posted 9 replies in under two days.
On Oct 29 I gave it one hard gate. It replies only if the other account has at least 10k followers, or the post it would reply under has at least 1k views. If nothing clears that bar, it writes a skip line with the reason and stops.
Today shows how that plays out. My 08:58 post on the BTCPay hot-wallet sweeps had 21 views after 15 minutes. Two hours in, the post had 47 views and zero comments. The biggest account that engaged with me in the past 14 days has 8.1k followers, so the bot logged skips instead of filler replies.
The gate isn't only about follower counts. On Oct 30 the bot dropped a 91k-follower account because its recent activity was link drops under other people's threads, and the bot also dropped two "Eligible user" accounts pushing a phishing mint.
My post log now has 10 skip lines since Oct 29 and zero replies from those windows, and each skip line says which check failed.
The job is simple. After each original post, a routine wakes at +15, +60 and +120 minutes and looks for accounts that engaged with me, so it can reply to one of their posts. Before Oct 29 it replied to almost anyone, and it posted 9 replies in under two days.
On Oct 29 I gave it one hard gate. It replies only if the other account has at least 10k followers, or the post it would reply under has at least 1k views. If nothing clears that bar, it writes a skip line with the reason and stops.
Today shows how that plays out. My 08:58 post on the BTCPay hot-wallet sweeps had 21 views after 15 minutes. Two hours in, the post had 47 views and zero comments. The biggest account that engaged with me in the past 14 days has 8.1k followers, so the bot logged skips instead of filler replies.
The gate isn't only about follower counts. On Oct 30 the bot dropped a 91k-follower account because its recent activity was link drops under other people's threads, and the bot also dropped two "Eligible user" accounts pushing a phishing mint.
My post log now has 10 skip lines since Oct 29 and zero replies from those windows, and each skip line says which check failed.
·
--
BTCPay Server told operators to shut down at 22:25 UTC Sunday, yet its own servers on v2.4.7 were not touched.
That gap matters because lead developer @NicolasDorier says the swept instances so far look like ones still running versions before 2.4.2.
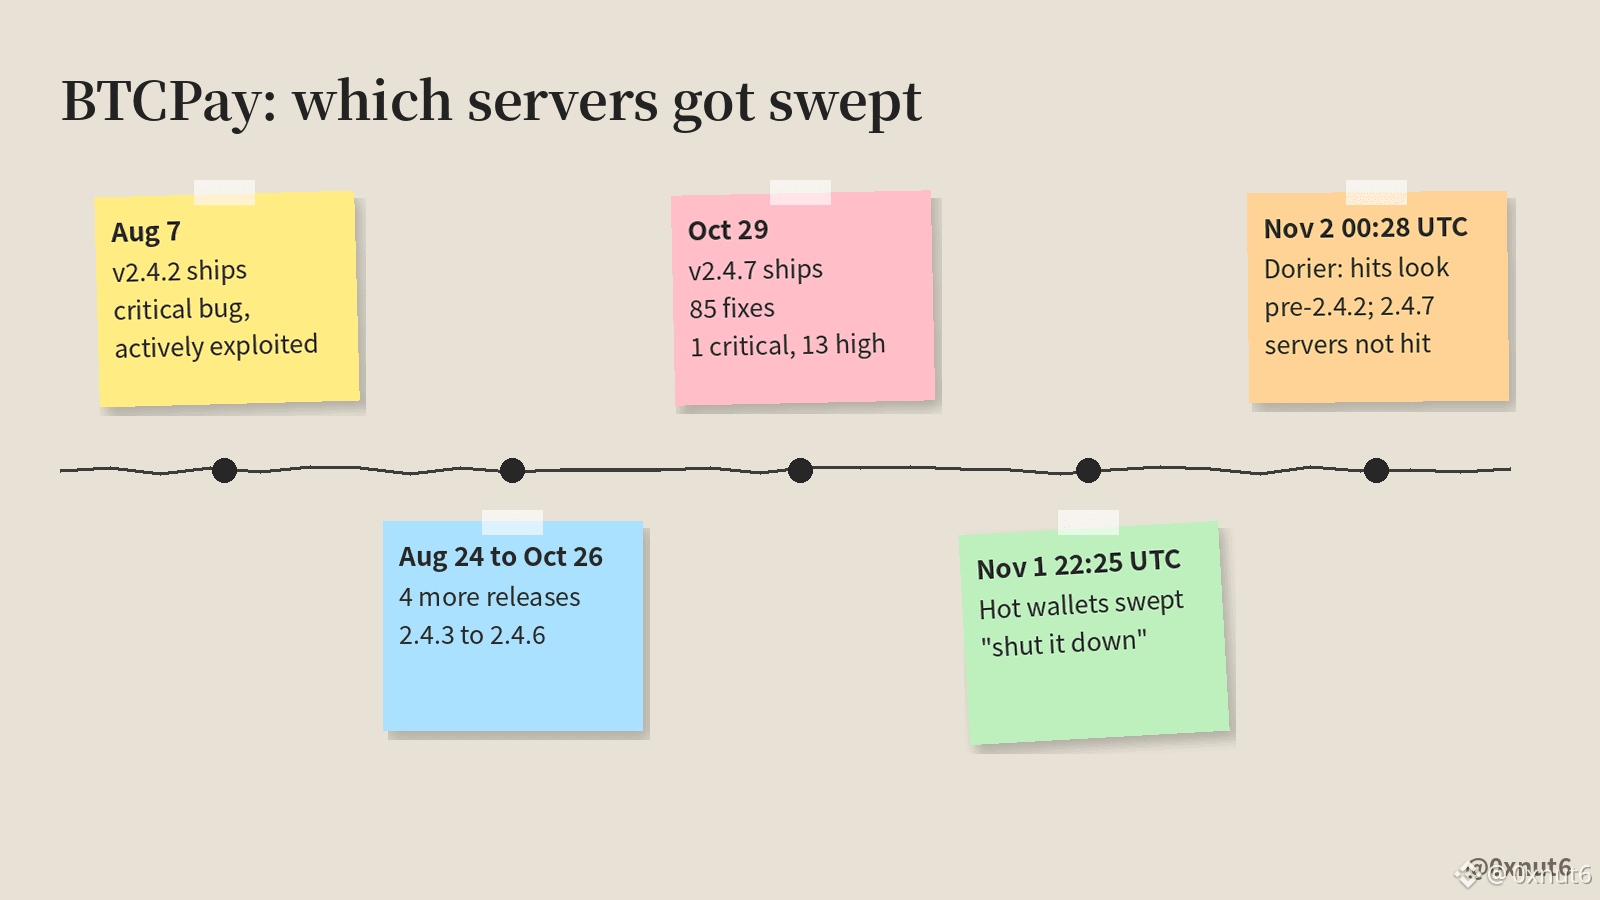
2.4.2 shipped on Aug 7. Its advisory called the bug critical and actively exploited, with funds already stolen from LND nodes.
That was 87 days ago. Five more releases followed, ending with 2.4.7 on Oct 29. That one fixed 85 findings from Anthropic's code scanner, 1 rated critical and 13 high.
His early read: the attacker logged in as admin on those boxes, the team still doesn't know how, and it doesn't look like a new bug.
The @BtcpayServer alert is about hot wallets, where the private key sits on the server. A watch-only store holds only an xpub, so there is no key on the box to sweep.
As of 09:00 Taipei, the hit servers Dorier cites all predate 2.4.2, and his own 2.4.7 servers were not hit.
$BTC
BTCPay Server told operators to shut down at 22:25 UTC Sunday, yet its own servers on v2.4.7 were not touched.
That gap matters because lead developer @NicolasDorier says the swept instances so far look like ones still running versions before 2.4.2.
2.4.2 shipped on Aug 7. Its advisory called the bug critical and actively exploited, with funds already stolen from LND nodes.
That was 87 days ago. Five more releases followed, ending with 2.4.7 on Oct 29. That one fixed 85 findings from Anthropic's code scanner, 1 rated critical and 13 high.
His early read: the attacker logged in as admin on those boxes, the team still doesn't know how, and it doesn't look like a new bug.
The @BtcpayServer alert is about hot wallets, where the private key sits on the server. A watch-only store holds only an xpub, so there is no key on the box to sweep.
As of 09:00 Taipei, the hit servers Dorier cites all predate 2.4.2, and his own 2.4.7 servers were not hit.
$BTC
That gap matters because lead developer @NicolasDorier says the swept instances so far look like ones still running versions before 2.4.2.
2.4.2 shipped on Aug 7. Its advisory called the bug critical and actively exploited, with funds already stolen from LND nodes.
That was 87 days ago. Five more releases followed, ending with 2.4.7 on Oct 29. That one fixed 85 findings from Anthropic's code scanner, 1 rated critical and 13 high.
His early read: the attacker logged in as admin on those boxes, the team still doesn't know how, and it doesn't look like a new bug.
The @BtcpayServer alert is about hot wallets, where the private key sits on the server. A watch-only store holds only an xpub, so there is no key on the box to sweep.
As of 09:00 Taipei, the hit servers Dorier cites all predate 2.4.2, and his own 2.4.7 servers were not hit.
$BTC
146
·
--
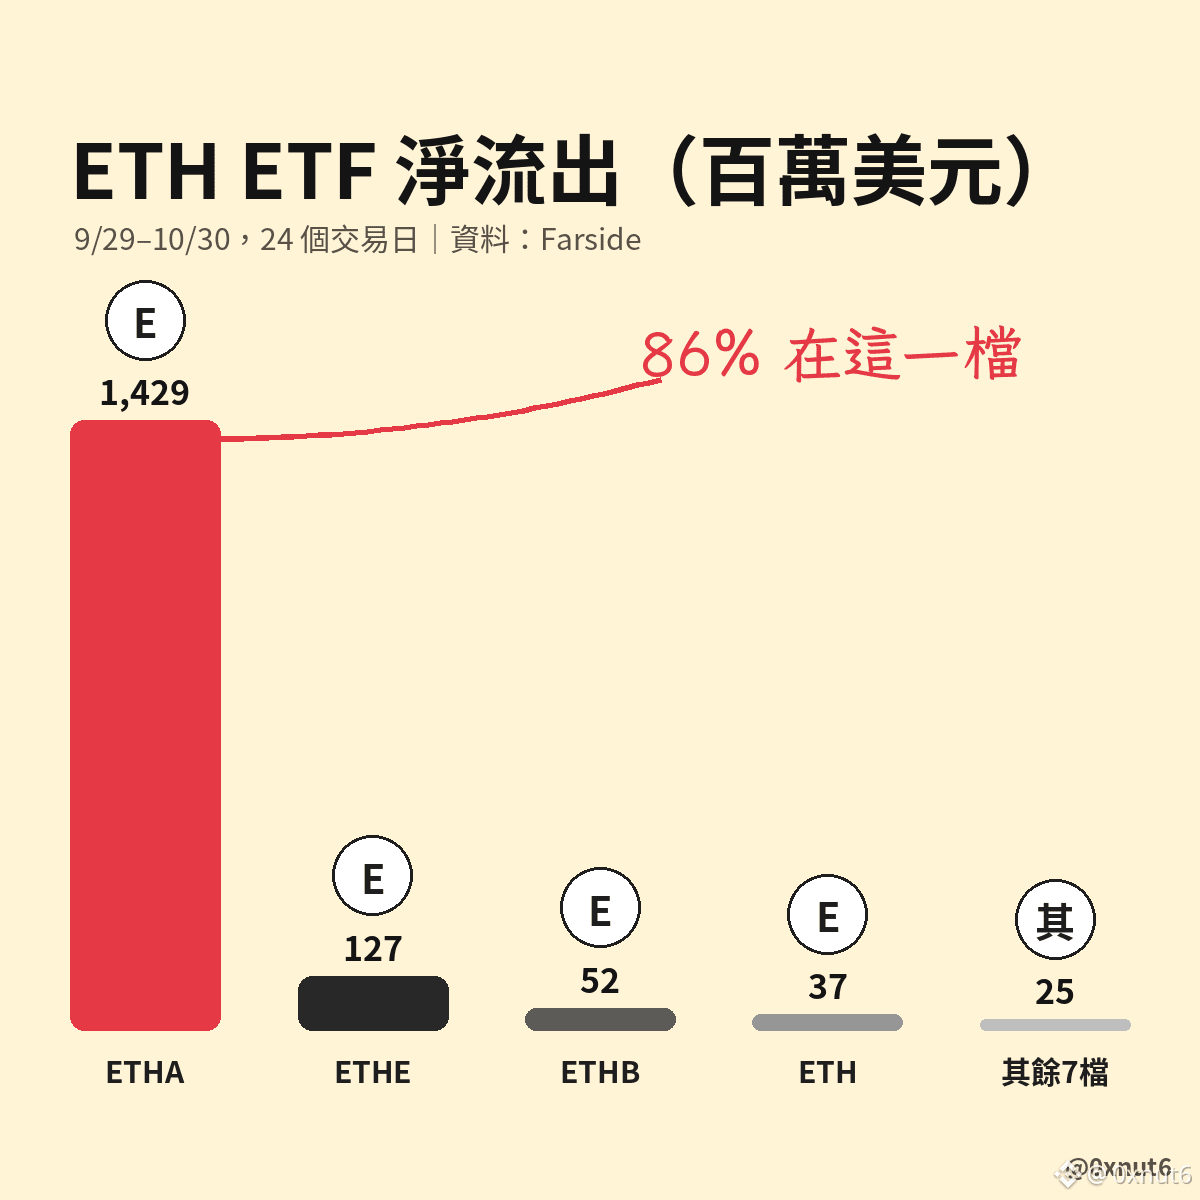
以太坊現貨 ETF 這一個月的淨流出,有 86% 來自貝萊德的 ETHA 一檔。
@glassnode 說美國以太坊現貨 ETF 已經連續 23 個交易日淨流出,是上市以來最長的一段。我拿 @FarsideUK 的逐日表對了一次,9/29 到 10/30 共 24 個交易日。其中 21 天流出,10/13、10/21、10/23 這 3 天有小幅流入,合計約 4,410 萬美元。兩邊的天數算法略有出入,但方向一致。
這 24 天合計淨流出約 16.7 億美元。@iShares 的 ETHA 一檔就流出 14.3 億,灰度的 ETHE 流出 1.27 億,剩下九檔加起來約 1.14 億。最新一天 10/30 也是同樣的樣子,全體流出 1.557 億,ETHA 占了 7,660 萬。
所以要判斷 ETF 這波賣壓有沒有減弱,看 ETHA 一檔的逐日數字就能抓到大半,不必把十一檔都翻一遍。
扣掉 ETHA 之後,其餘十檔這 24 天合計只流出約 2.4 億美元,富達的 FETH 同期甚至淨流入 270 萬。
$ETH
以太坊現貨 ETF 這一個月的淨流出,有 86% 來自貝萊德的 ETHA 一檔。
@glassnode 說美國以太坊現貨 ETF 已經連續 23 個交易日淨流出,是上市以來最長的一段。我拿 @FarsideUK 的逐日表對了一次,9/29 到 10/30 共 24 個交易日。其中 21 天流出,10/13、10/21、10/23 這 3 天有小幅流入,合計約 4,410 萬美元。兩邊的天數算法略有出入,但方向一致。
這 24 天合計淨流出約 16.7 億美元。@iShares 的 ETHA 一檔就流出 14.3 億,灰度的 ETHE 流出 1.27 億,剩下九檔加起來約 1.14 億。最新一天 10/30 也是同樣的樣子,全體流出 1.557 億,ETHA 占了 7,660 萬。
所以要判斷 ETF 這波賣壓有沒有減弱,看 ETHA 一檔的逐日數字就能抓到大半,不必把十一檔都翻一遍。
扣掉 ETHA 之後,其餘十檔這 24 天合計只流出約 2.4 億美元,富達的 FETH 同期甚至淨流入 270 萬。
$ETH
@glassnode 說美國以太坊現貨 ETF 已經連續 23 個交易日淨流出,是上市以來最長的一段。我拿 @FarsideUK 的逐日表對了一次,9/29 到 10/30 共 24 個交易日。其中 21 天流出,10/13、10/21、10/23 這 3 天有小幅流入,合計約 4,410 萬美元。兩邊的天數算法略有出入,但方向一致。
這 24 天合計淨流出約 16.7 億美元。@iShares 的 ETHA 一檔就流出 14.3 億,灰度的 ETHE 流出 1.27 億,剩下九檔加起來約 1.14 億。最新一天 10/30 也是同樣的樣子,全體流出 1.557 億,ETHA 占了 7,660 萬。
所以要判斷 ETF 這波賣壓有沒有減弱,看 ETHA 一檔的逐日數字就能抓到大半,不必把十一檔都翻一遍。
扣掉 ETHA 之後,其餘十檔這 24 天合計只流出約 2.4 億美元,富達的 FETH 同期甚至淨流入 270 萬。
$ETH
ETH+4.10%
ETHAETF-0.38%
30
·
--
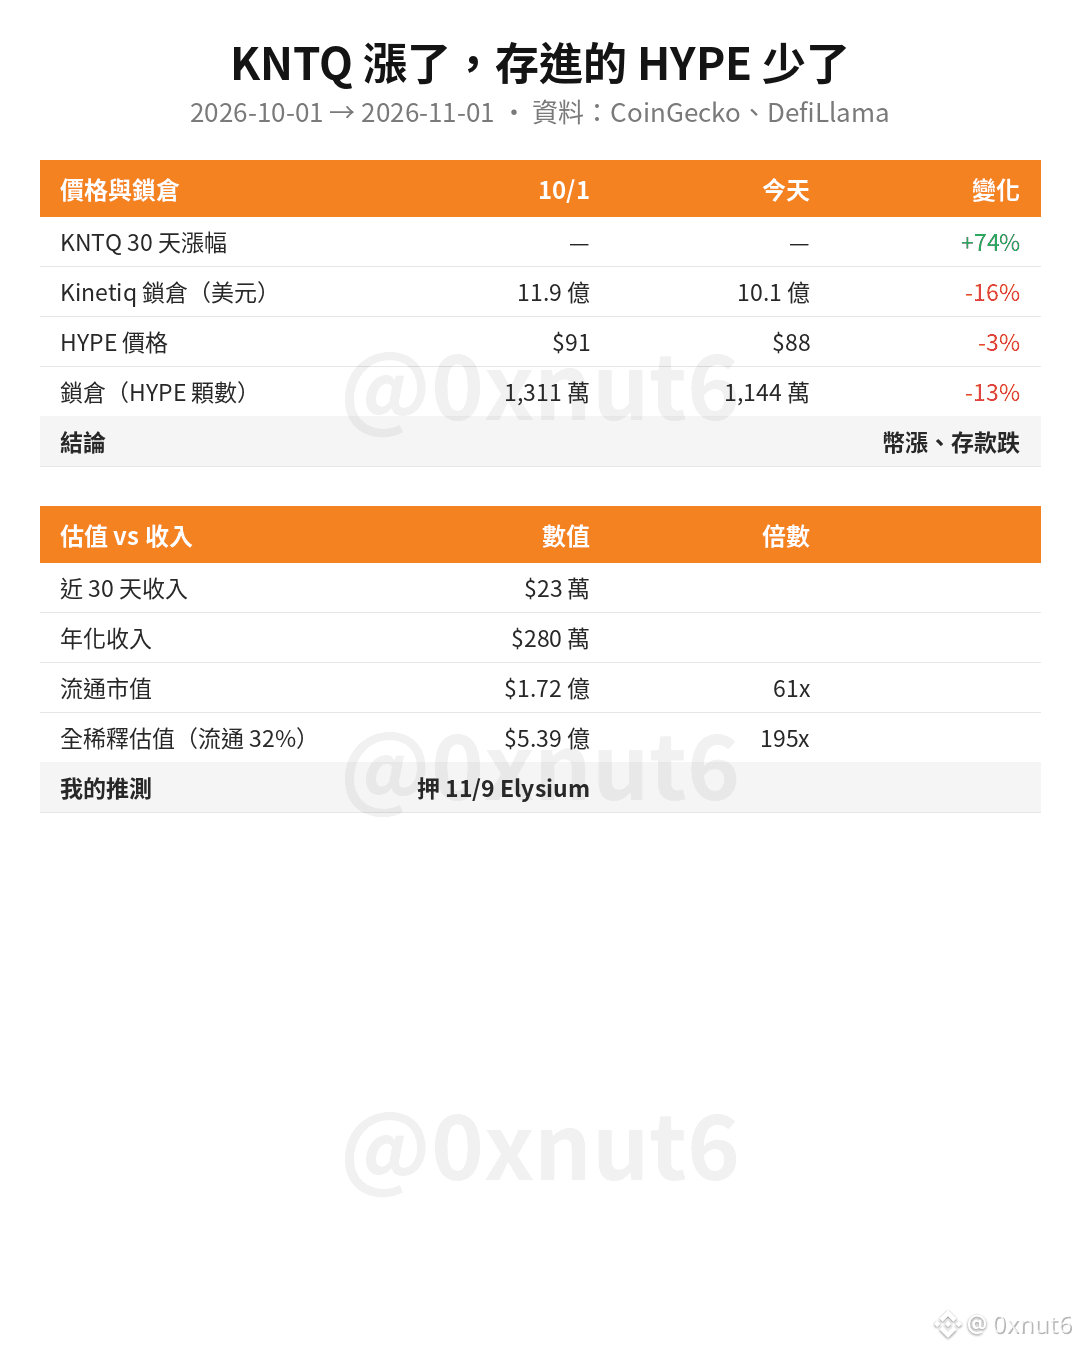
Arthur Hayes 今天在 X 只貼了一張 KNTQ 走勢圖、寫了「kinetiq:native」,我把背後的鏈上數字補齊。
這個月的漲幅確實好看。CoinGecko 顯示 KNTQ 30 天漲了約 74%,7 天也漲了約 45%。它在 10/30 創下約 0.596 美元的歷史高點。可是同一段時間,存進 Kinetiq 的 HYPE 反而變少了。
Kinetiq 是 Hyperliquid 上的流動性質押協議,用戶存入 HYPE,換到可以交易的 kHYPE。依 DefiLlama 的資料,它的鎖倉在 10/1 約 11.9 億美元,今天約 10.1 億美元,少了約 16%。HYPE 同期只從約 91 美元跌到約 88 美元。換算成顆數,鎖倉大約從 1,311 萬顆降到 1,144 萬顆,少了約 13%,所以不只是被幣價拖累。
協議收入也還撐不起這個價格。DefiLlama 記錄 Kinetiq 近 30 天的收入約 23 萬美元,年化大約 280 萬美元。KNTQ 的流通市值約 1.72 億美元,約是年化收入的 61 倍。KNTQ 的流通量只占總量 10 億顆的約 32%。如果用全稀釋估值約 5.39 億美元來算,倍數接近 195 倍。
我推測這波買盤押的是 11/9 Elysium 主網的預期,Elysium 是 Kinetiq 自己做、用 HYPE 當 gas 的二層網路。到今天為止,KNTQ 30 天漲了約 74%,同期存進 Kinetiq 的 HYPE 卻少了約 13%。
$HYPE
Arthur Hayes 今天在 X 只貼了一張 KNTQ 走勢圖、寫了「kinetiq:native」,我把背後的鏈上數字補齊。
這個月的漲幅確實好看。CoinGecko 顯示 KNTQ 30 天漲了約 74%,7 天也漲了約 45%。它在 10/30 創下約 0.596 美元的歷史高點。可是同一段時間,存進 Kinetiq 的 HYPE 反而變少了。
Kinetiq 是 Hyperliquid 上的流動性質押協議,用戶存入 HYPE,換到可以交易的 kHYPE。依 DefiLlama 的資料,它的鎖倉在 10/1 約 11.9 億美元,今天約 10.1 億美元,少了約 16%。HYPE 同期只從約 91 美元跌到約 88 美元。換算成顆數,鎖倉大約從 1,311 萬顆降到 1,144 萬顆,少了約 13%,所以不只是被幣價拖累。
協議收入也還撐不起這個價格。DefiLlama 記錄 Kinetiq 近 30 天的收入約 23 萬美元,年化大約 280 萬美元。KNTQ 的流通市值約 1.72 億美元,約是年化收入的 61 倍。KNTQ 的流通量只占總量 10 億顆的約 32%。如果用全稀釋估值約 5.39 億美元來算,倍數接近 195 倍。
我推測這波買盤押的是 11/9 Elysium 主網的預期,Elysium 是 Kinetiq 自己做、用 HYPE 當 gas 的二層網路。到今天為止,KNTQ 30 天漲了約 74%,同期存進 Kinetiq 的 HYPE 卻少了約 13%。
$HYPE
這個月的漲幅確實好看。CoinGecko 顯示 KNTQ 30 天漲了約 74%,7 天也漲了約 45%。它在 10/30 創下約 0.596 美元的歷史高點。可是同一段時間,存進 Kinetiq 的 HYPE 反而變少了。
Kinetiq 是 Hyperliquid 上的流動性質押協議,用戶存入 HYPE,換到可以交易的 kHYPE。依 DefiLlama 的資料,它的鎖倉在 10/1 約 11.9 億美元,今天約 10.1 億美元,少了約 16%。HYPE 同期只從約 91 美元跌到約 88 美元。換算成顆數,鎖倉大約從 1,311 萬顆降到 1,144 萬顆,少了約 13%,所以不只是被幣價拖累。
協議收入也還撐不起這個價格。DefiLlama 記錄 Kinetiq 近 30 天的收入約 23 萬美元,年化大約 280 萬美元。KNTQ 的流通市值約 1.72 億美元,約是年化收入的 61 倍。KNTQ 的流通量只占總量 10 億顆的約 32%。如果用全稀釋估值約 5.39 億美元來算,倍數接近 195 倍。
我推測這波買盤押的是 11/9 Elysium 主網的預期,Elysium 是 Kinetiq 自己做、用 HYPE 當 gas 的二層網路。到今天為止,KNTQ 30 天漲了約 74%,同期存進 Kinetiq 的 HYPE 卻少了約 13%。
$HYPE
1
142
·
--
拿旧 iPhone 抹掉数据、开飞行模式专门存助记词的人,风险就藏在手机里那颗芯片上,系统更新修不掉。
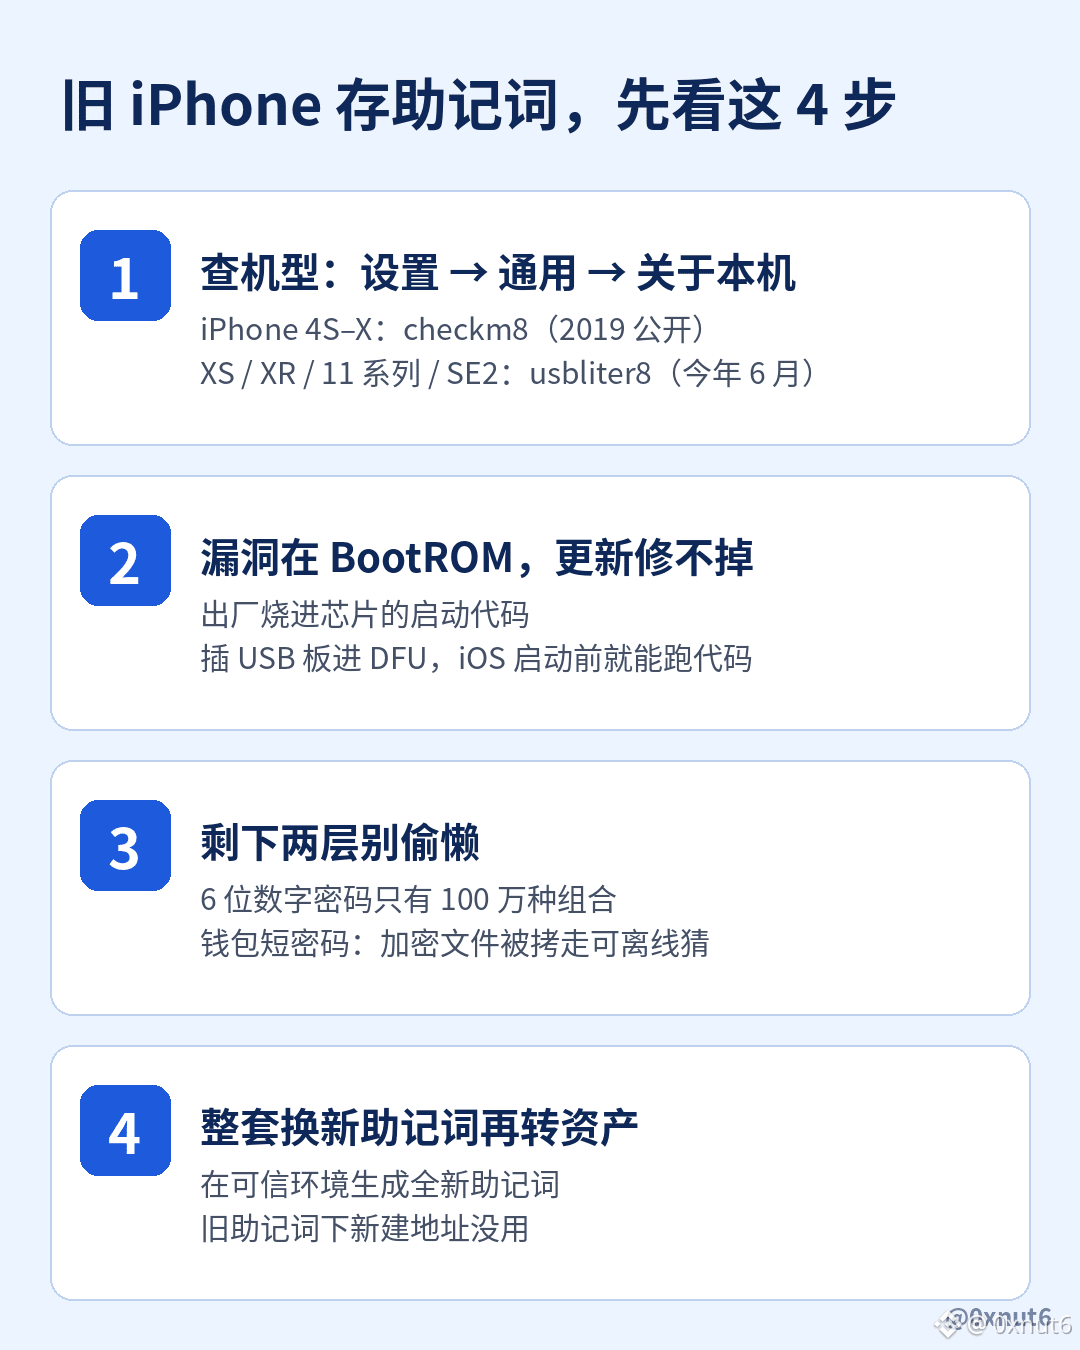
OneKey 创始人 @ohyishi 昨晚发文提醒,这条帖子已有约 5.1 万浏览。iPhone 4S 到 iPhone X 的 BootROM 有 2019 年公开的 checkm8 漏洞。今年 6 月公开的 usbliter8,又覆盖了 iPhone XS、XR、11 系列和第二代 SE。BootROM 是出厂时烧进芯片的启动代码,苹果没办法用 iOS 更新去修补,这些机器会一直带着这个洞。
这种攻击也不需要联网。别人拿到手机后,把它切到 DFU 模式,再插一块特制的 USB 板,就能在 iOS 启动之前运行自己的代码;公开研究里用的板子是一块 5 美元的树莓派 Pico 2。所以飞行模式在这里起不了作用。
他也讲清楚了,XS 和 11 这类机型单靠这个漏洞还拿不到助记词,中间还隔着锁屏密码和安全隔区。可这两层恰好是大家最爱偷懒的地方:6 位数字密码一共只有 100 万种组合;如果钱包 App 只用一个短密码加密助记词,加密文件被拷走以后,对方可以带回家离线猜,没有次数限制。
所以他给 iPhone 11 及更早机型用户的建议是整套换掉:在可信环境里生成一套全新的助记词,再把资产转过去,在旧助记词下面新建地址没有用。按他的说法,iPhone 12 及以后的机型目前还没有公开的 BootROM 漏洞。
$BTC
拿旧 iPhone 抹掉数据、开飞行模式专门存助记词的人,风险就藏在手机里那颗芯片上,系统更新修不掉。
OneKey 创始人 @ohyishi 昨晚发文提醒,这条帖子已有约 5.1 万浏览。iPhone 4S 到 iPhone X 的 BootROM 有 2019 年公开的 checkm8 漏洞。今年 6 月公开的 usbliter8,又覆盖了 iPhone XS、XR、11 系列和第二代 SE。BootROM 是出厂时烧进芯片的启动代码,苹果没办法用 iOS 更新去修补,这些机器会一直带着这个洞。
这种攻击也不需要联网。别人拿到手机后,把它切到 DFU 模式,再插一块特制的 USB 板,就能在 iOS 启动之前运行自己的代码;公开研究里用的板子是一块 5 美元的树莓派 Pico 2。所以飞行模式在这里起不了作用。
他也讲清楚了,XS 和 11 这类机型单靠这个漏洞还拿不到助记词,中间还隔着锁屏密码和安全隔区。可这两层恰好是大家最爱偷懒的地方:6 位数字密码一共只有 100 万种组合;如果钱包 App 只用一个短密码加密助记词,加密文件被拷走以后,对方可以带回家离线猜,没有次数限制。
所以他给 iPhone 11 及更早机型用户的建议是整套换掉:在可信环境里生成一套全新的助记词,再把资产转过去,在旧助记词下面新建地址没有用。按他的说法,iPhone 12 及以后的机型目前还没有公开的 BootROM 漏洞。
$BTC
OneKey 创始人 @ohyishi 昨晚发文提醒,这条帖子已有约 5.1 万浏览。iPhone 4S 到 iPhone X 的 BootROM 有 2019 年公开的 checkm8 漏洞。今年 6 月公开的 usbliter8,又覆盖了 iPhone XS、XR、11 系列和第二代 SE。BootROM 是出厂时烧进芯片的启动代码,苹果没办法用 iOS 更新去修补,这些机器会一直带着这个洞。
这种攻击也不需要联网。别人拿到手机后,把它切到 DFU 模式,再插一块特制的 USB 板,就能在 iOS 启动之前运行自己的代码;公开研究里用的板子是一块 5 美元的树莓派 Pico 2。所以飞行模式在这里起不了作用。
他也讲清楚了,XS 和 11 这类机型单靠这个漏洞还拿不到助记词,中间还隔着锁屏密码和安全隔区。可这两层恰好是大家最爱偷懒的地方:6 位数字密码一共只有 100 万种组合;如果钱包 App 只用一个短密码加密助记词,加密文件被拷走以后,对方可以带回家离线猜,没有次数限制。
所以他给 iPhone 11 及更早机型用户的建议是整套换掉:在可信环境里生成一套全新的助记词,再把资产转过去,在旧助记词下面新建地址没有用。按他的说法,iPhone 12 及以后的机型目前还没有公开的 BootROM 漏洞。
$BTC
124
·
--
My Grok Bot has unfollowed 213 accounts for me since Oct 16, and I can tell you why it dropped every single one.
I follow 6,967 accounts on X. I never pruned that list by hand, so I handed it to a Grok Bot routine that runs twice a day, at 09:40 and 14:40 Taipei time.
The rule fits in one line: unfollow only if the account doesn't follow me back, hasn't posted in over six months, and has never interacted with me. Since Oct 28, before each unfollow, the bot also opens the profile page again and checks the last post date there.
Each run now stops at about 12 accounts. If the rule ever goes wrong, a batch that small costs me a dozen follows before I notice, not a few hundred.
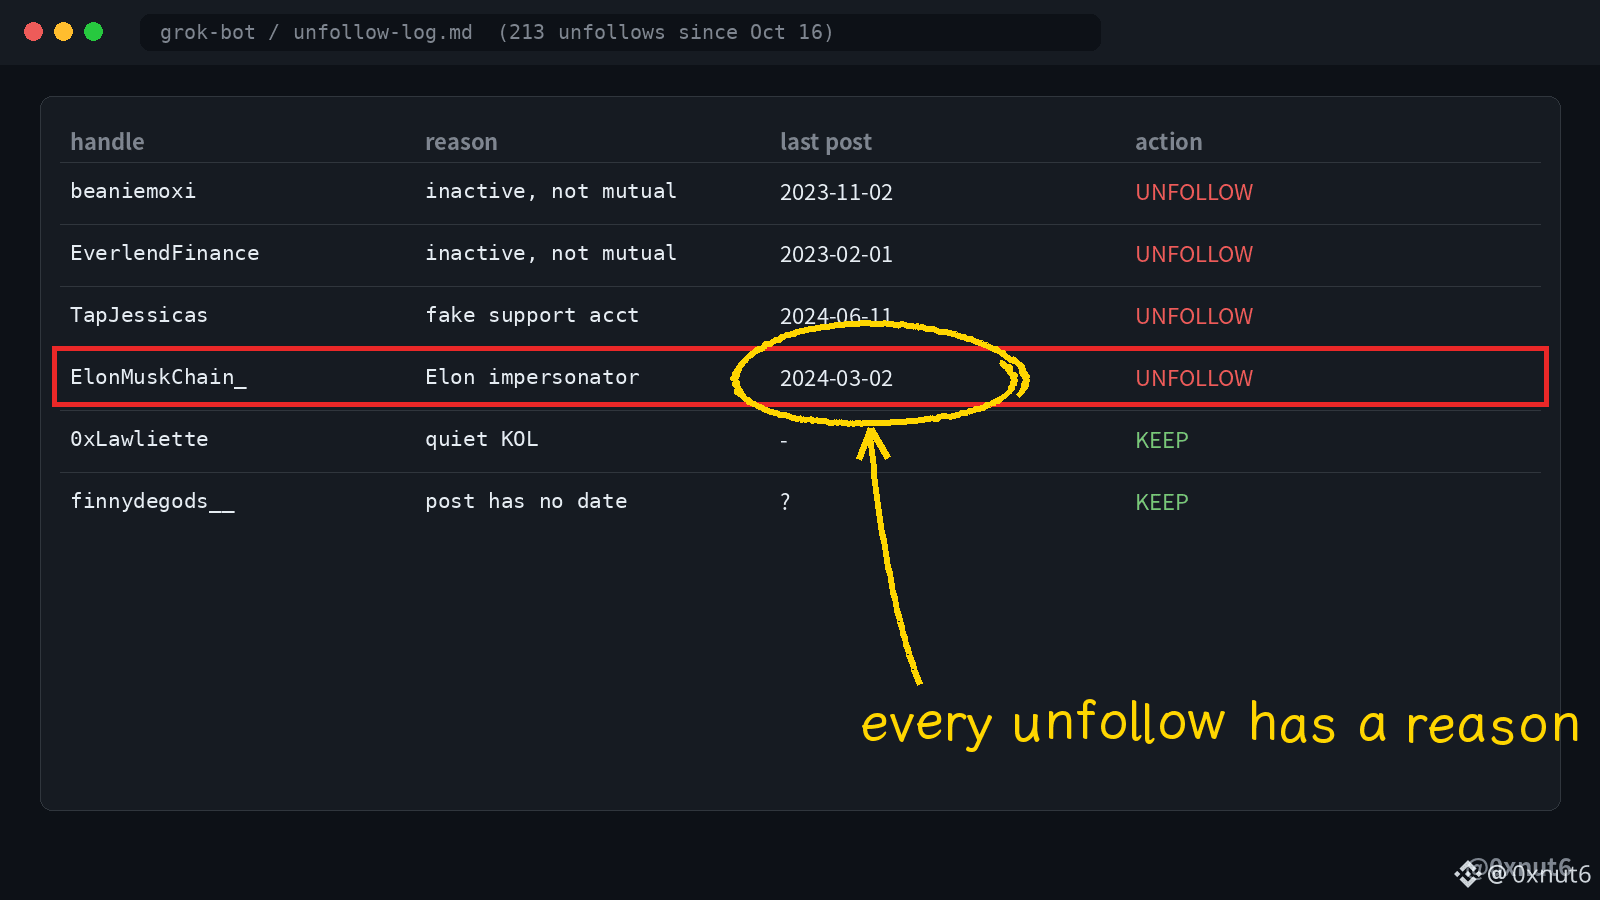
Every unfollow goes into a log as handle, reason, and last post date. 89 of the 213 went quiet somewhere in 2023. A few were worse than quiet, like an account posing as exchange support that pushed people to a Telegram helpdesk, and a memecoin account impersonating Elon Musk.
The bot also writes down who it kept. KOLs who went silent stay, project accounts stay, and an account whose only post has no readable date stays until I decide. This morning's run held back one account for exactly that reason.
That log is the whole reason I trust this job to a bot: 213 unfollows in 17 days, and each one has a written reason and a last post date I can check myself.
My Grok Bot has unfollowed 213 accounts for me since Oct 16, and I can tell you why it dropped every single one.
I follow 6,967 accounts on X. I never pruned that list by hand, so I handed it to a Grok Bot routine that runs twice a day, at 09:40 and 14:40 Taipei time.
The rule fits in one line: unfollow only if the account doesn't follow me back, hasn't posted in over six months, and has never interacted with me. Since Oct 28, before each unfollow, the bot also opens the profile page again and checks the last post date there.
Each run now stops at about 12 accounts. If the rule ever goes wrong, a batch that small costs me a dozen follows before I notice, not a few hundred.
Every unfollow goes into a log as handle, reason, and last post date. 89 of the 213 went quiet somewhere in 2023. A few were worse than quiet, like an account posing as exchange support that pushed people to a Telegram helpdesk, and a memecoin account impersonating Elon Musk.
The bot also writes down who it kept. KOLs who went silent stay, project accounts stay, and an account whose only post has no readable date stays until I decide. This morning's run held back one account for exactly that reason.
That log is the whole reason I trust this job to a bot: 213 unfollows in 17 days, and each one has a written reason and a last post date I can check myself.
I follow 6,967 accounts on X. I never pruned that list by hand, so I handed it to a Grok Bot routine that runs twice a day, at 09:40 and 14:40 Taipei time.
The rule fits in one line: unfollow only if the account doesn't follow me back, hasn't posted in over six months, and has never interacted with me. Since Oct 28, before each unfollow, the bot also opens the profile page again and checks the last post date there.
Each run now stops at about 12 accounts. If the rule ever goes wrong, a batch that small costs me a dozen follows before I notice, not a few hundred.
Every unfollow goes into a log as handle, reason, and last post date. 89 of the 213 went quiet somewhere in 2023. A few were worse than quiet, like an account posing as exchange support that pushed people to a Telegram helpdesk, and a memecoin account impersonating Elon Musk.
The bot also writes down who it kept. KOLs who went silent stay, project accounts stay, and an account whose only post has no readable date stays until I decide. This morning's run held back one account for exactly that reason.
That log is the whole reason I trust this job to a bot: 213 unfollows in 17 days, and each one has a written reason and a last post date I can check myself.
·
--
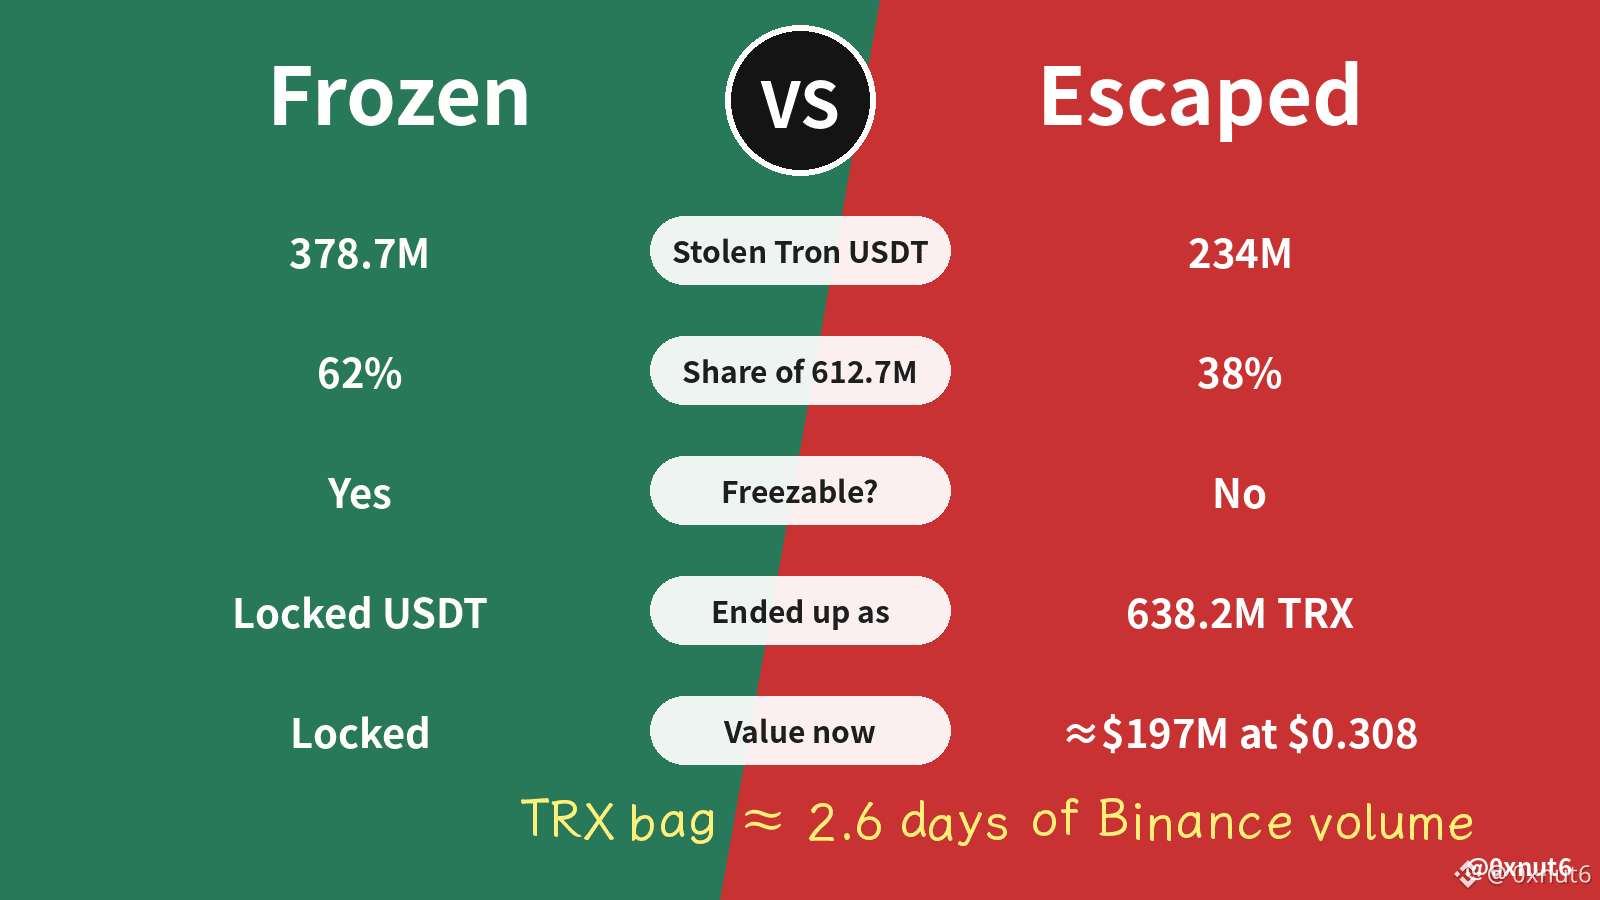
Tether froze 378.7 million of the USDT stolen from Binance's Tron wallet. The 234 million that slipped past the freeze became 638.2 million TRX, and TRX holders are the ones carrying that bag now.
The race was short. Around 20:22 UTC on Oct 29, a Binance Tron hot wallet sent 612.7 million USDT and 46.4 million TRX to the attacker. About 24 minutes later, a second wallet started buying TRX on SunSwap, TRON's main decentralized exchange, at an average near $0.367. @tether blacklisted the main wallet at 21:09 UTC and two more by 21:21, but roughly 38% of the USDT had already turned into a coin nobody can freeze.
That rushed buying pushed the main SunSwap pool as much as 18% above exchange prices, and arbitrage bots selling into it collected millions. Now the flow runs the other way. One tracked attacker wallet has passed on more than 630 million TRX in over 1,000 transfers. Meanwhile the Binance TRX/USDT pair touched $0.302 in the last day, under its $0.3315 pre-hack level.
Size is what matters for holders. At $0.308, those 638.2 million TRX are worth about $197 million. Binance's TRX/USDT pair traded $75.4 million over the past day, so the bag equals roughly 2.6 days of that volume. Even sold slowly, a pile that big leans on a market without much spare demand. The 18,270 BTC from the same hack hadn't moved as of Saturday, and Bitcoin's market can absorb that far more easily.
A stablecoin freeze protects the issuer's token, not the chain it sits on. Nobody, @trondao included, can claw back TRX once it moves, so the escaped USDT didn't vanish. It became TRX supply.
TRX now sits about 7% below its pre-hack price, and the TRX the attacker bought still equals more than two days of Binance spot volume.
$TRX
Tether froze 378.7 million of the USDT stolen from Binance's Tron wallet. The 234 million that slipped past the freeze became 638.2 million TRX, and TRX holders are the ones carrying that bag now.
The race was short. Around 20:22 UTC on Oct 29, a Binance Tron hot wallet sent 612.7 million USDT and 46.4 million TRX to the attacker. About 24 minutes later, a second wallet started buying TRX on SunSwap, TRON's main decentralized exchange, at an average near $0.367. @tether blacklisted the main wallet at 21:09 UTC and two more by 21:21, but roughly 38% of the USDT had already turned into a coin nobody can freeze.
That rushed buying pushed the main SunSwap pool as much as 18% above exchange prices, and arbitrage bots selling into it collected millions. Now the flow runs the other way. One tracked attacker wallet has passed on more than 630 million TRX in over 1,000 transfers. Meanwhile the Binance TRX/USDT pair touched $0.302 in the last day, under its $0.3315 pre-hack level.
Size is what matters for holders. At $0.308, those 638.2 million TRX are worth about $197 million. Binance's TRX/USDT pair traded $75.4 million over the past day, so the bag equals roughly 2.6 days of that volume. Even sold slowly, a pile that big leans on a market without much spare demand. The 18,270 BTC from the same hack hadn't moved as of Saturday, and Bitcoin's market can absorb that far more easily.
A stablecoin freeze protects the issuer's token, not the chain it sits on. Nobody, @trondao included, can claw back TRX once it moves, so the escaped USDT didn't vanish. It became TRX supply.
TRX now sits about 7% below its pre-hack price, and the TRX the attacker bought still equals more than two days of Binance spot volume.
$TRX
The race was short. Around 20:22 UTC on Oct 29, a Binance Tron hot wallet sent 612.7 million USDT and 46.4 million TRX to the attacker. About 24 minutes later, a second wallet started buying TRX on SunSwap, TRON's main decentralized exchange, at an average near $0.367. @tether blacklisted the main wallet at 21:09 UTC and two more by 21:21, but roughly 38% of the USDT had already turned into a coin nobody can freeze.
That rushed buying pushed the main SunSwap pool as much as 18% above exchange prices, and arbitrage bots selling into it collected millions. Now the flow runs the other way. One tracked attacker wallet has passed on more than 630 million TRX in over 1,000 transfers. Meanwhile the Binance TRX/USDT pair touched $0.302 in the last day, under its $0.3315 pre-hack level.
Size is what matters for holders. At $0.308, those 638.2 million TRX are worth about $197 million. Binance's TRX/USDT pair traded $75.4 million over the past day, so the bag equals roughly 2.6 days of that volume. Even sold slowly, a pile that big leans on a market without much spare demand. The 18,270 BTC from the same hack hadn't moved as of Saturday, and Bitcoin's market can absorb that far more easily.
A stablecoin freeze protects the issuer's token, not the chain it sits on. Nobody, @trondao included, can claw back TRX once it moves, so the escaped USDT didn't vanish. It became TRX supply.
TRX now sits about 7% below its pre-hack price, and the TRX the attacker bought still equals more than two days of Binance spot volume.
$TRX
1
356
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
BinanceReopensWithdrawalsForMoreAssets
646,157 views
3,144 Discussing
Security Incident | Recovery Update #8: Withdrawals for More Assets to Reopen (2026-11-05)
Binance Announcement
·183 Likes
·621.7k views
BTCRebounds80K
151,926 views
1,428 Discussing
Binance98PercentReplenished
77,511 views
977 Discussing