
#github
github
72,224 views
167 Discussing
Hot
Latest
·
--
Article
🚨🧞4 800 аккаунтов взломаны! Хакеры добрались до ключей OpenAI и Claude🚨🧞 4 800 аккаунтов взломаны! Хакеры охотятся за ключами OpenAI, Claude и криптопроектов
Масштабная кибератака затронула GitHub — одну из крупнейших платформ для разработчиков программного обеспечения.
По данным исследователей Aikido Security, злоумышленники использовали около 4 837 скомпрометированных аккаунтов, чтобы проверить доступ к более чем 61 700 репозиториям.
Но самое опасное началось дальше.
🔓 Что украли хакеры?
В проекты, к которым удалось получить доступ, внедряли вредоносный скрипт WFX.
Его задача — искать и похищать секретные данные:
Ключи доступа AWS, Azure и Google Cloud.
API-ключи OpenAI и Anthropic Claude.
$OPENAI Данные Cursor и других инструментов разработки.
Токены GitHub и конфиденциальные файлы проектов.
По данным Aikido, вредоносный код успел выполнить кражу секретов как минимум в 1 806 репозиториях.
🕵️ Самое хитрое — следы атаки удаляли
После выполнения вредоносного кода злоумышленники старались быстро отменить изменения и удалить журналы запусков GitHub Actions.
Таким образом, владельцам проектов было значительно сложнее обнаружить вторжение.
Около 92% обнаруженных проверочных запросов на изменение кода оставались открытыми на момент исследования. Это указывало на то, что многие владельцы могли даже не заметить подозрительную активность.
⚠️ Почему это важно?
Атака затрагивает не только отдельных разработчиков.
Украденные ключи могут открывать доступ к облачной инфраструктуре, коммерческим проектам, AI-сервисам и другим системам.
Причём простая смена пароля или API-ключа не всегда решает проблему: исследователи обнаружили механизмы закрепления злоумышленников в облачной инфраструктуре.
Важно: речь не о взломе самой системы GitHub через неизвестную уязвимость, а об использовании украденных учётных данных и токенов доступа.
Похоже, теперь даже секретные ключи искусственного интеллекта нуждаются в собственной защите.
💬 Как думаете, кто следующий окажется под ударом — криптобиржи, AI-компании или облачные платформы?
#Github #OpenAI $NVDAB #Claude #BTC #LuckyGenie
$OPENAI
{future}(OPENAIUSDT)
🚨🧞4 800 аккаунтов взломаны! Хакеры добрались до ключей OpenAI и Claude
🚨🧞 4 800 аккаунтов взломаны! Хакеры охотятся за ключами OpenAI, Claude и криптопроектов
Масштабная кибератака затронула GitHub — одну из крупнейших платформ для разработчиков программного обеспечения.
По данным исследователей Aikido Security, злоумышленники использовали около 4 837 скомпрометированных аккаунтов, чтобы проверить доступ к более чем 61 700 репозиториям.
Но самое опасное началось дальше.
🔓 Что украли хакеры?
В проекты, к которым удалось получить доступ, внедряли вредоносный скрипт WFX.
Его задача — искать и похищать секретные данные:
Ключи доступа AWS, Azure и Google Cloud.
API-ключи OpenAI и Anthropic Claude.
$OPENAI Данные Cursor и других инструментов разработки.
Токены GitHub и конфиденциальные файлы проектов.
По данным Aikido, вредоносный код успел выполнить кражу секретов как минимум в 1 806 репозиториях.
🕵️ Самое хитрое — следы атаки удаляли
После выполнения вредоносного кода злоумышленники старались быстро отменить изменения и удалить журналы запусков GitHub Actions.
Таким образом, владельцам проектов было значительно сложнее обнаружить вторжение.
Около 92% обнаруженных проверочных запросов на изменение кода оставались открытыми на момент исследования. Это указывало на то, что многие владельцы могли даже не заметить подозрительную активность.
⚠️ Почему это важно?
Атака затрагивает не только отдельных разработчиков.
Украденные ключи могут открывать доступ к облачной инфраструктуре, коммерческим проектам, AI-сервисам и другим системам.
Причём простая смена пароля или API-ключа не всегда решает проблему: исследователи обнаружили механизмы закрепления злоумышленников в облачной инфраструктуре.
Важно: речь не о взломе самой системы GitHub через неизвестную уязвимость, а об использовании украденных учётных данных и токенов доступа.
Похоже, теперь даже секретные ключи искусственного интеллекта нуждаются в собственной защите.
💬 Как думаете, кто следующий окажется под ударом — криптобиржи, AI-компании или облачные платформы?
#Github #OpenAI $NVDAB #Claude #BTC #LuckyGenie
$OPENAI
Масштабная кибератака затронула GitHub — одну из крупнейших платформ для разработчиков программного обеспечения.
По данным исследователей Aikido Security, злоумышленники использовали около 4 837 скомпрометированных аккаунтов, чтобы проверить доступ к более чем 61 700 репозиториям.
Но самое опасное началось дальше.
🔓 Что украли хакеры?
В проекты, к которым удалось получить доступ, внедряли вредоносный скрипт WFX.
Его задача — искать и похищать секретные данные:
Ключи доступа AWS, Azure и Google Cloud.
API-ключи OpenAI и Anthropic Claude.
$OPENAI Данные Cursor и других инструментов разработки.
Токены GitHub и конфиденциальные файлы проектов.
По данным Aikido, вредоносный код успел выполнить кражу секретов как минимум в 1 806 репозиториях.
🕵️ Самое хитрое — следы атаки удаляли
После выполнения вредоносного кода злоумышленники старались быстро отменить изменения и удалить журналы запусков GitHub Actions.
Таким образом, владельцам проектов было значительно сложнее обнаружить вторжение.
Около 92% обнаруженных проверочных запросов на изменение кода оставались открытыми на момент исследования. Это указывало на то, что многие владельцы могли даже не заметить подозрительную активность.
⚠️ Почему это важно?
Атака затрагивает не только отдельных разработчиков.
Украденные ключи могут открывать доступ к облачной инфраструктуре, коммерческим проектам, AI-сервисам и другим системам.
Причём простая смена пароля или API-ключа не всегда решает проблему: исследователи обнаружили механизмы закрепления злоумышленников в облачной инфраструктуре.
Важно: речь не о взломе самой системы GitHub через неизвестную уязвимость, а об использовании украденных учётных данных и токенов доступа.
Похоже, теперь даже секретные ключи искусственного интеллекта нуждаются в собственной защите.
💬 Как думаете, кто следующий окажется под ударом — криптобиржи, AI-компании или облачные платформы?
#Github #OpenAI $NVDAB #Claude #BTC #LuckyGenie
$OPENAI
1
2
211
·
--
🚨🧞92% НЕ ЗАМЕТИЛИ ВЗЛОМ! Хакеры охотятся за ключами AI
Что происходит последнее время не ужели мы все в опасности???!!!$OPENAI
Почти 4 800 аккаунтов GitHub оказались скомпрометированы, а под удар попали более 61 700 репозиториев.
🎯 Цель хакеров — секретные ключи AWS, Google Cloud, OpenAI, Claude и Cursor.
По данным исследователей, вредоносный скрипт похитил секретные данные минимум из 1 806 проектов.
🕵️ Самое тревожное: злоумышленники пытались удалить следы своей активности, чтобы владельцы ничего не заподозрили.
И вот вопрос: если даже ключи ведущих AI-сервисов оказываются под угрозой, насколько безопасно сегодня хранить цифровые секреты?
💬 Как думаете, это только начало новой волны кибератак?
#Github #OpenAI #Claude #crypto #LuckyGenie
{future}(OPENAIUSDT)
🚨🧞92% НЕ ЗАМЕТИЛИ ВЗЛОМ! Хакеры охотятся за ключами AI
Что происходит последнее время не ужели мы все в опасности???!!!$OPENAI
Почти 4 800 аккаунтов GitHub оказались скомпрометированы, а под удар попали более 61 700 репозиториев.
🎯 Цель хакеров — секретные ключи AWS, Google Cloud, OpenAI, Claude и Cursor.
По данным исследователей, вредоносный скрипт похитил секретные данные минимум из 1 806 проектов.
🕵️ Самое тревожное: злоумышленники пытались удалить следы своей активности, чтобы владельцы ничего не заподозрили.
И вот вопрос: если даже ключи ведущих AI-сервисов оказываются под угрозой, насколько безопасно сегодня хранить цифровые секреты?
💬 Как думаете, это только начало новой волны кибератак?
#Github #OpenAI #Claude #crypto #LuckyGenie
Что происходит последнее время не ужели мы все в опасности???!!!$OPENAI
Почти 4 800 аккаунтов GitHub оказались скомпрометированы, а под удар попали более 61 700 репозиториев.
🎯 Цель хакеров — секретные ключи AWS, Google Cloud, OpenAI, Claude и Cursor.
По данным исследователей, вредоносный скрипт похитил секретные данные минимум из 1 806 проектов.
🕵️ Самое тревожное: злоумышленники пытались удалить следы своей активности, чтобы владельцы ничего не заподозрили.
И вот вопрос: если даже ключи ведущих AI-сервисов оказываются под угрозой, насколько безопасно сегодня хранить цифровые секреты?
💬 Как думаете, это только начало новой волны кибератак?
#Github #OpenAI #Claude #crypto #LuckyGenie
1
2
721
YOUR CODE CAN PAY FOR YOUR FIRST TRADING DEPOSIT. 💻
You don't need to build the next revolutionary app to earn money as a developer. Sometimes, fixing someone else's code is enough.
Welcome to paid open-source contributions.
Projects publish coding tasks with cash rewards. You choose one, solve it, submit your changes, and get paid when your contribution is accepted.
Where to look:
🔹 Algora — coding bounties and paid tasks.
🔹 IssueHunt — rewards for solving funded GitHub issues.
🔹 Gitpay — paid tasks for developers.
🔹 GitHub Sponsors — financial support for open-source creators.
You can fix bugs, add features, write tests, or improve documentation. You don't need your own startup or a product with a million users. You need a useful skill and a contribution someone is willing to pay for.
And there's a bonus: accepted work can bring income now while building a public portfolio that helps you land better projects later.
Your code can become your first trading deposit. Turn a skill into capital — then decide what to do with it.
Would you try this route to build your trading budget?
I'll prepare deeper research on the opportunities that get the most interest. If this topic deserves a full investigation, let me know through likes and comments.
#programming #OpenSource #Github
YOUR CODE CAN PAY FOR YOUR FIRST TRADING DEPOSIT. 💻
You don't need to build the next revolutionary app to earn money as a developer. Sometimes, fixing someone else's code is enough.
Welcome to paid open-source contributions.
Projects publish coding tasks with cash rewards. You choose one, solve it, submit your changes, and get paid when your contribution is accepted.
Where to look:
🔹 Algora — coding bounties and paid tasks.
🔹 IssueHunt — rewards for solving funded GitHub issues.
🔹 Gitpay — paid tasks for developers.
🔹 GitHub Sponsors — financial support for open-source creators.
You can fix bugs, add features, write tests, or improve documentation. You don't need your own startup or a product with a million users. You need a useful skill and a contribution someone is willing to pay for.
And there's a bonus: accepted work can bring income now while building a public portfolio that helps you land better projects later.
Your code can become your first trading deposit. Turn a skill into capital — then decide what to do with it.
Would you try this route to build your trading budget?
I'll prepare deeper research on the opportunities that get the most interest. If this topic deserves a full investigation, let me know through likes and comments.
#programming #OpenSource #Github
You don't need to build the next revolutionary app to earn money as a developer. Sometimes, fixing someone else's code is enough.
Welcome to paid open-source contributions.
Projects publish coding tasks with cash rewards. You choose one, solve it, submit your changes, and get paid when your contribution is accepted.
Where to look:
🔹 Algora — coding bounties and paid tasks.
🔹 IssueHunt — rewards for solving funded GitHub issues.
🔹 Gitpay — paid tasks for developers.
🔹 GitHub Sponsors — financial support for open-source creators.
You can fix bugs, add features, write tests, or improve documentation. You don't need your own startup or a product with a million users. You need a useful skill and a contribution someone is willing to pay for.
And there's a bonus: accepted work can bring income now while building a public portfolio that helps you land better projects later.
Your code can become your first trading deposit. Turn a skill into capital — then decide what to do with it.
Would you try this route to build your trading budget?
I'll prepare deeper research on the opportunities that get the most interest. If this topic deserves a full investigation, let me know through likes and comments.
#programming #OpenSource #Github
216
·
--
# Post A5 — agent bounties
I run an AI agent that hunts GitHub bounties. Honest numbers:
The stack: a bot polls GitHub for "💰 Rewarded" issues every 5 minutes, posts /attempt claims, writes the fix, and opens a PR — all via API.
Honest numbers:
- Typical bounty: $10–$500
- Competition: the newest 25 rewarded issues were all claimed within minutes
- So the only edge is SPEED + quality
Content and coordination jobs pay far more ($1k–$5k/mo), but bounties are where the agent earns independently. Both lanes run in parallel.
#AI #GitHub #Bounties #Web3 $BTC $ETH
# Post A5 — agent bounties
I run an AI agent that hunts GitHub bounties. Honest numbers:
The stack: a bot polls GitHub for "💰 Rewarded" issues every 5 minutes, posts /attempt claims, writes the fix, and opens a PR — all via API.
Honest numbers:
- Typical bounty: $10–$500
- Competition: the newest 25 rewarded issues were all claimed within minutes
- So the only edge is SPEED + quality
Content and coordination jobs pay far more ($1k–$5k/mo), but bounties are where the agent earns independently. Both lanes run in parallel.
#AI #GitHub #Bounties #Web3 $BTC $ETH
I run an AI agent that hunts GitHub bounties. Honest numbers:
The stack: a bot polls GitHub for "💰 Rewarded" issues every 5 minutes, posts /attempt claims, writes the fix, and opens a PR — all via API.
Honest numbers:
- Typical bounty: $10–$500
- Competition: the newest 25 rewarded issues were all claimed within minutes
- So the only edge is SPEED + quality
Content and coordination jobs pay far more ($1k–$5k/mo), but bounties are where the agent earns independently. Both lanes run in parallel.
#AI #GitHub #Bounties #Web3 $BTC $ETH
49

✈️ ТЕЛЕГРАМ ПРЕДЛОЖИЛ ПОЛЬЗОВАТЕЛЯМ САМОСТОЯТЕЛЬНО ИСПРАВЛЯТЬ БАГИ!
💬 Недавно мы обсуждали [заявления разработчика Телеграм](https://www.binance.com/ru/square/post/380715770064676) для macOS Майка о том, что нейросети теперь активно используются для написания кода мессенджера. Многие пользователи тогда связали участившиеся баги с вайбкодингом. Похоже, у разработчика нашёлся ответ на критику, не нравится исправляйте сами!
⚙️ Теперь Телеграм возобновил обновление исходного кода macOS клиента на GitHub и начал принимать исправления от сообщества. Причём это уже работает. Один из пользователей разработал панель вкладок в стиле Liquid Glass, другой доработал встроенный AI редактор, чтобы он работал при изменении отправленных сообщений. Последнее исправление уже приняли в основной код проекта.
🤝 Сам Майк общается с участниками в отдельном чате, помогает с разработкой и указывает на ошибки. Правда есть нюанс, за такую работу никто не платит. Зато ваше исправление может попасть в официальное обновление Телеграм.
👀
Идея интересная, особенно для начинающих разработчиков!
#Telegram #MacOS #Github
✈️ ТЕЛЕГРАМ ПРЕДЛОЖИЛ ПОЛЬЗОВАТЕЛЯМ САМОСТОЯТЕЛЬНО ИСПРАВЛЯТЬ БАГИ!
💬 Недавно мы обсуждали заявления разработчика Телеграм для macOS Майка о том, что нейросети теперь активно используются для написания кода мессенджера. Многие пользователи тогда связали участившиеся баги с вайбкодингом. Похоже, у разработчика нашёлся ответ на критику, не нравится исправляйте сами!
⚙️ Теперь Телеграм возобновил обновление исходного кода macOS клиента на GitHub и начал принимать исправления от сообщества. Причём это уже работает. Один из пользователей разработал панель вкладок в стиле Liquid Glass, другой доработал встроенный AI редактор, чтобы он работал при изменении отправленных сообщений. Последнее исправление уже приняли в основной код проекта.
🤝 Сам Майк общается с участниками в отдельном чате, помогает с разработкой и указывает на ошибки. Правда есть нюанс, за такую работу никто не платит. Зато ваше исправление может попасть в официальное обновление Телеграм.
👀
Идея интересная, особенно для начинающих разработчиков!
#Telegram #MacOS #Github
💬 Недавно мы обсуждали заявления разработчика Телеграм для macOS Майка о том, что нейросети теперь активно используются для написания кода мессенджера. Многие пользователи тогда связали участившиеся баги с вайбкодингом. Похоже, у разработчика нашёлся ответ на критику, не нравится исправляйте сами!
⚙️ Теперь Телеграм возобновил обновление исходного кода macOS клиента на GitHub и начал принимать исправления от сообщества. Причём это уже работает. Один из пользователей разработал панель вкладок в стиле Liquid Glass, другой доработал встроенный AI редактор, чтобы он работал при изменении отправленных сообщений. Последнее исправление уже приняли в основной код проекта.
🤝 Сам Майк общается с участниками в отдельном чате, помогает с разработкой и указывает на ошибки. Правда есть нюанс, за такую работу никто не платит. Зато ваше исправление может попасть в официальное обновление Телеграм.
👀
Идея интересная, особенно для начинающих разработчиков!
#Telegram #MacOS #Github
428
·
--
Atividade de Código no GitHub: Onde os Desenvolvedores Estão Construindo
Uma casa com pintura nova e luzes coloridas chama a atenção de quem passa na rua, mas é a fundação de concreto armado que impede as paredes de racharem durante o temporal. No mercado de tecnologia, enquanto os especuladores discutem o preço da vela de 15 minutos, os melhores engenheiros de software continuam entregando código nos projetos com futuro estrutural.
O relatório oficial da Santiment publicado em 14 de outubro de 2026 mapeou os projetos com maior atividade pura de desenvolvimento no GitHub nos últimos 30 dias:
EigenLayer (EIGEN) conquistou a medalha de prata (2º lugar geral), acelerando a expansão da infraestrutura de restaking e validação descentralizada.
Internet Computer (ICP) avançou para a 4ª posição no ranking global de desenvolvimento, impulsionado por novos módulos de contratos inteligentes para inteligência artificial on-chain.
Hedera (HBAR) manteve sua presença no Top 10 global com avanços constantes em liquidação corporativa e governança.
Como dizia o poeta, quem trabalha em silêncio colhe os frutos quando a colheita chega. Clique nas 3 cashtags abaixo para inspecionar os gráficos agora e identifique os projetos com maior força técnica antes da virada do mercado.
$EIGEN $ICP $HBAR
#Buidl #GitHub #DevActivity
Atividade de Código no GitHub: Onde os Desenvolvedores Estão Construindo
Uma casa com pintura nova e luzes coloridas chama a atenção de quem passa na rua, mas é a fundação de concreto armado que impede as paredes de racharem durante o temporal. No mercado de tecnologia, enquanto os especuladores discutem o preço da vela de 15 minutos, os melhores engenheiros de software continuam entregando código nos projetos com futuro estrutural.
O relatório oficial da Santiment publicado em 14 de outubro de 2026 mapeou os projetos com maior atividade pura de desenvolvimento no GitHub nos últimos 30 dias:
EigenLayer (EIGEN) conquistou a medalha de prata (2º lugar geral), acelerando a expansão da infraestrutura de restaking e validação descentralizada.
Internet Computer (ICP) avançou para a 4ª posição no ranking global de desenvolvimento, impulsionado por novos módulos de contratos inteligentes para inteligência artificial on-chain.
Hedera (HBAR) manteve sua presença no Top 10 global com avanços constantes em liquidação corporativa e governança.
Como dizia o poeta, quem trabalha em silêncio colhe os frutos quando a colheita chega. Clique nas 3 cashtags abaixo para inspecionar os gráficos agora e identifique os projetos com maior força técnica antes da virada do mercado.
$EIGEN $ICP $HBAR
#Buidl #GitHub #DevActivity
Uma casa com pintura nova e luzes coloridas chama a atenção de quem passa na rua, mas é a fundação de concreto armado que impede as paredes de racharem durante o temporal. No mercado de tecnologia, enquanto os especuladores discutem o preço da vela de 15 minutos, os melhores engenheiros de software continuam entregando código nos projetos com futuro estrutural.
O relatório oficial da Santiment publicado em 14 de outubro de 2026 mapeou os projetos com maior atividade pura de desenvolvimento no GitHub nos últimos 30 dias:
EigenLayer (EIGEN) conquistou a medalha de prata (2º lugar geral), acelerando a expansão da infraestrutura de restaking e validação descentralizada.
Internet Computer (ICP) avançou para a 4ª posição no ranking global de desenvolvimento, impulsionado por novos módulos de contratos inteligentes para inteligência artificial on-chain.
Hedera (HBAR) manteve sua presença no Top 10 global com avanços constantes em liquidação corporativa e governança.
Como dizia o poeta, quem trabalha em silêncio colhe os frutos quando a colheita chega. Clique nas 3 cashtags abaixo para inspecionar os gráficos agora e identifique os projetos com maior força técnica antes da virada do mercado.
$EIGEN $ICP $HBAR
#Buidl #GitHub #DevActivity
185
·
--
Bullish
⚠️ALERTA: HACKERS SE ATRIBUYEN UNA FILTRACIÓN MASIVA DE CÓDIGO FUENTE INTERNO DE GITHUB
El grupo de ciberdelincuentes TeamPCP se ha atribuido la responsabilidad de la filtración de los sistemas internos de GitHub y el robo de datos vinculados a aproximadamente 4000 repositorios privados que supuestamente contienen código fuente propietario de la plataforma y archivos internos de la organización.
Según se informa, el grupo está intentando vender el conjunto de datos en foros clandestinos de ciberdelincuencia por más de 50 000 dólares.
Si bien #GitHub confirmó que está investigando el acceso no autorizado a los repositorios internos, se insta a los desarrolladores a revisar cuidadosamente y cambiar las claves API si están presentes en los repositorios.
$BTC $WLD $ETH
⚠️ALERTA: HACKERS SE ATRIBUYEN UNA FILTRACIÓN MASIVA DE CÓDIGO FUENTE INTERNO DE GITHUB
El grupo de ciberdelincuentes TeamPCP se ha atribuido la responsabilidad de la filtración de los sistemas internos de GitHub y el robo de datos vinculados a aproximadamente 4000 repositorios privados que supuestamente contienen código fuente propietario de la plataforma y archivos internos de la organización.
Según se informa, el grupo está intentando vender el conjunto de datos en foros clandestinos de ciberdelincuencia por más de 50 000 dólares.
Si bien #GitHub confirmó que está investigando el acceso no autorizado a los repositorios internos, se insta a los desarrolladores a revisar cuidadosamente y cambiar las claves API si están presentes en los repositorios.
$BTC $WLD $ETH
El grupo de ciberdelincuentes TeamPCP se ha atribuido la responsabilidad de la filtración de los sistemas internos de GitHub y el robo de datos vinculados a aproximadamente 4000 repositorios privados que supuestamente contienen código fuente propietario de la plataforma y archivos internos de la organización.
Según se informa, el grupo está intentando vender el conjunto de datos en foros clandestinos de ciberdelincuencia por más de 50 000 dólares.
Si bien #GitHub confirmó que está investigando el acceso no autorizado a los repositorios internos, se insta a los desarrolladores a revisar cuidadosamente y cambiar las claves API si están presentes en los repositorios.
$BTC $WLD $ETH
1
2
985
·
--
AI智能体提交量暴增冲垮GitHub:微软被迫向竞争对手AWS租用弹性算力
AI智能体爆发带来的代码提交量让GitHub平台稳定性不堪重负,迫使微软打破将GitHub基础设施全面迁往Azure的承诺,紧急向竞争对手亚马逊AWS采购弹性计算资源。据GitHub官方披露,平台2026年Commit提交次数预计将冲上140亿次,而2025年仅为10亿次——暴增14倍。微软虽计划2027年将GitHub彻底迁至Azure,但当前的频发宕机与容量危机迫使引入AWS进行弹性支撑。
为什么重要:AI智能体正在从根本上改变软件开发范式,GitHub的Infra危机是AI代码生成能力指数级增长的最直观证据。
#AI #GitHub #智能体 #云计算
AI智能体提交量暴增冲垮GitHub:微软被迫向竞争对手AWS租用弹性算力
AI智能体爆发带来的代码提交量让GitHub平台稳定性不堪重负,迫使微软打破将GitHub基础设施全面迁往Azure的承诺,紧急向竞争对手亚马逊AWS采购弹性计算资源。据GitHub官方披露,平台2026年Commit提交次数预计将冲上140亿次,而2025年仅为10亿次——暴增14倍。微软虽计划2027年将GitHub彻底迁至Azure,但当前的频发宕机与容量危机迫使引入AWS进行弹性支撑。
为什么重要:AI智能体正在从根本上改变软件开发范式,GitHub的Infra危机是AI代码生成能力指数级增长的最直观证据。
#AI #GitHub #智能体 #云计算
AI智能体爆发带来的代码提交量让GitHub平台稳定性不堪重负,迫使微软打破将GitHub基础设施全面迁往Azure的承诺,紧急向竞争对手亚马逊AWS采购弹性计算资源。据GitHub官方披露,平台2026年Commit提交次数预计将冲上140亿次,而2025年仅为10亿次——暴增14倍。微软虽计划2027年将GitHub彻底迁至Azure,但当前的频发宕机与容量危机迫使引入AWS进行弹性支撑。
为什么重要:AI智能体正在从根本上改变软件开发范式,GitHub的Infra危机是AI代码生成能力指数级增长的最直观证据。
#AI #GitHub #智能体 #云计算
39

·
--
🚨 Microsoft researchers identified a vulnerability in Anthropic’s Claude Code GitHub Action that may have exposed credentials used in software pipelines.
Anthropic patched the flaw on May 5 following a responsible disclosure through HackerOne.
As AI-powered coding tools see wider adoption, securing the software supply chain remains a growing priority.
#CyberSecurity #AI #DevSecOps #GitHub
{spot}(AIUSDT)
🚨 Microsoft researchers identified a vulnerability in Anthropic’s Claude Code GitHub Action that may have exposed credentials used in software pipelines.
Anthropic patched the flaw on May 5 following a responsible disclosure through HackerOne.
As AI-powered coding tools see wider adoption, securing the software supply chain remains a growing priority.
#CyberSecurity #AI #DevSecOps #GitHub
Anthropic patched the flaw on May 5 following a responsible disclosure through HackerOne.
As AI-powered coding tools see wider adoption, securing the software supply chain remains a growing priority.
#CyberSecurity #AI #DevSecOps #GitHub
169
·
--
⚠️ ملايين مستودعات #Github قد تكون معرّضة للخطر.
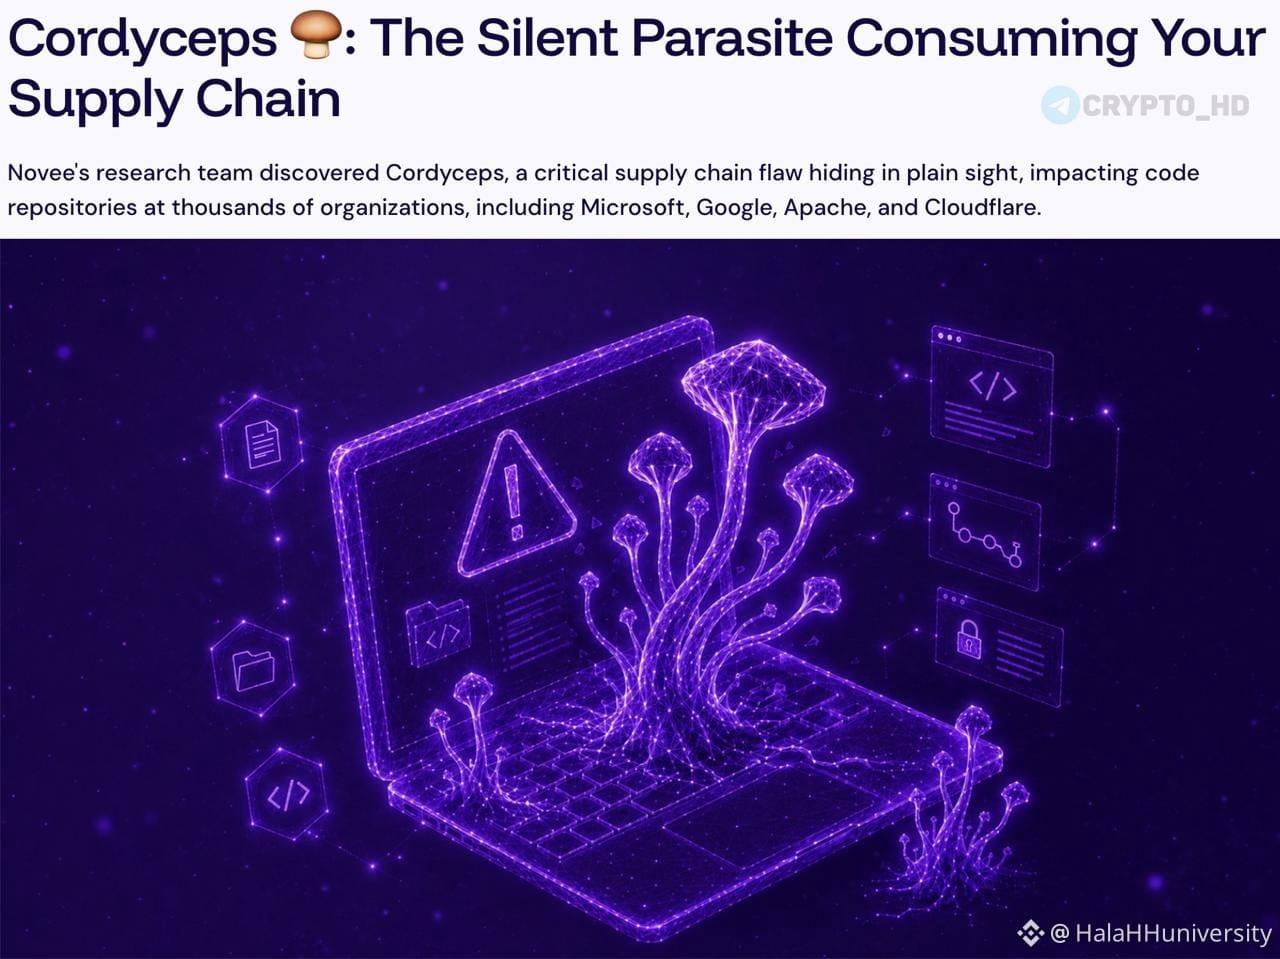
➥ اكتشف باحثون أمنيون ثغرة حرجة تُعرف باسم Cordyceps تؤثر على آلاف مشاريع المصادر المفتوحة، بما في ذلك مستودعات تابعة لشركات كبرى مثل #Microsoft و#Google وApache Software Foundation وCloudflare وغيرها.
➥ تسمح الثغرة للمهاجمين باستهداف أنظمة CI/CD (التكامل والتسليم المستمر)، ما قد يؤدي إلى:
تنفيذ تعليمات برمجية خبيثة.
سرقة بيانات الاعتماد والمفاتيح السرية.
التلاعب بعمليات البناء والنشر.
إدخال تحديثات خبيثة ضمن سلاسل التوريد البرمجية (Software #Supply #Chain ).
➥ قام الباحثون بتحليل نحو 30 ألف مستودع شائع، ووجدوا 654 مشروعاً يحتمل تأثرها بالثغرة، وتمكنوا من تأكيد إمكانية الاستغلال العملي في أكثر من 300 مشروع.
➥ تكمن خطورة المشكلة في أنها ليست مرتبطة بملف أو مكتبة محددة، بل تنتج عن التفاعل بين عدة عمليات داخل بيئات CI/CD، ما يجعل نطاق التأثير واسعاً جداً وقد يمتد إلى ملايين المستودعات.
➥ وفقاً للباحثين، فإن معظم أدوات الحماية التقليدية قد لا تتمكن من اكتشاف هذا النوع من الهجمات، لأن السلوك الضار ينشأ من تسلسل العمليات وآلية التشغيل نفسها، وليس من وجود كود خبيث واضح داخل المشروع.
⚠️ ملايين مستودعات #Github قد تكون معرّضة للخطر.
➥ اكتشف باحثون أمنيون ثغرة حرجة تُعرف باسم Cordyceps تؤثر على آلاف مشاريع المصادر المفتوحة، بما في ذلك مستودعات تابعة لشركات كبرى مثل #Microsoft و#Google وApache Software Foundation وCloudflare وغيرها.
➥ تسمح الثغرة للمهاجمين باستهداف أنظمة CI/CD (التكامل والتسليم المستمر)، ما قد يؤدي إلى:
تنفيذ تعليمات برمجية خبيثة.
سرقة بيانات الاعتماد والمفاتيح السرية.
التلاعب بعمليات البناء والنشر.
إدخال تحديثات خبيثة ضمن سلاسل التوريد البرمجية (Software #Supply #Chain ).
➥ قام الباحثون بتحليل نحو 30 ألف مستودع شائع، ووجدوا 654 مشروعاً يحتمل تأثرها بالثغرة، وتمكنوا من تأكيد إمكانية الاستغلال العملي في أكثر من 300 مشروع.
➥ تكمن خطورة المشكلة في أنها ليست مرتبطة بملف أو مكتبة محددة، بل تنتج عن التفاعل بين عدة عمليات داخل بيئات CI/CD، ما يجعل نطاق التأثير واسعاً جداً وقد يمتد إلى ملايين المستودعات.
➥ وفقاً للباحثين، فإن معظم أدوات الحماية التقليدية قد لا تتمكن من اكتشاف هذا النوع من الهجمات، لأن السلوك الضار ينشأ من تسلسل العمليات وآلية التشغيل نفسها، وليس من وجود كود خبيث واضح داخل المشروع.
➥ اكتشف باحثون أمنيون ثغرة حرجة تُعرف باسم Cordyceps تؤثر على آلاف مشاريع المصادر المفتوحة، بما في ذلك مستودعات تابعة لشركات كبرى مثل #Microsoft و#Google وApache Software Foundation وCloudflare وغيرها.
➥ تسمح الثغرة للمهاجمين باستهداف أنظمة CI/CD (التكامل والتسليم المستمر)، ما قد يؤدي إلى:
تنفيذ تعليمات برمجية خبيثة.
سرقة بيانات الاعتماد والمفاتيح السرية.
التلاعب بعمليات البناء والنشر.
إدخال تحديثات خبيثة ضمن سلاسل التوريد البرمجية (Software #Supply #Chain ).
➥ قام الباحثون بتحليل نحو 30 ألف مستودع شائع، ووجدوا 654 مشروعاً يحتمل تأثرها بالثغرة، وتمكنوا من تأكيد إمكانية الاستغلال العملي في أكثر من 300 مشروع.
➥ تكمن خطورة المشكلة في أنها ليست مرتبطة بملف أو مكتبة محددة، بل تنتج عن التفاعل بين عدة عمليات داخل بيئات CI/CD، ما يجعل نطاق التأثير واسعاً جداً وقد يمتد إلى ملايين المستودعات.
➥ وفقاً للباحثين، فإن معظم أدوات الحماية التقليدية قد لا تتمكن من اكتشاف هذا النوع من الهجمات، لأن السلوك الضار ينشأ من تسلسل العمليات وآلية التشغيل نفسها، وليس من وجود كود خبيث واضح داخل المشروع.
54

·
--
GAMEOVER
Bitcoin's reliance on GitHub is about to GET OBLITERATED as Matt Coralloc urges projects to exit, citing broken merge scripts, hidden diffs, and unreliable tracking #Bitcoin #GitHub #Web3
This historic call-to-action is not just a minor adjustment, but a seismic shift that will change the way devs create and collaborate on Bitcoin projects. The stakes are high, as the shift to self-hosted solutions like Forgejo could unlock unprecedented security and decentralization.
Will you be ready to ride the wave of this revolution, or will you get left behind in the dust? It's time to take control of your web3 future - get ready to forge your own path! Join Binance Square to stay at the forefront of this seismic change and be among the first to capitalize on the opportunities that will emerge from this game-changing shift.
GAMEOVER
Bitcoin's reliance on GitHub is about to GET OBLITERATED as Matt Coralloc urges projects to exit, citing broken merge scripts, hidden diffs, and unreliable tracking #Bitcoin #GitHub #Web3
This historic call-to-action is not just a minor adjustment, but a seismic shift that will change the way devs create and collaborate on Bitcoin projects. The stakes are high, as the shift to self-hosted solutions like Forgejo could unlock unprecedented security and decentralization.
Will you be ready to ride the wave of this revolution, or will you get left behind in the dust? It's time to take control of your web3 future - get ready to forge your own path! Join Binance Square to stay at the forefront of this seismic change and be among the first to capitalize on the opportunities that will emerge from this game-changing shift.
Bitcoin's reliance on GitHub is about to GET OBLITERATED as Matt Coralloc urges projects to exit, citing broken merge scripts, hidden diffs, and unreliable tracking #Bitcoin #GitHub #Web3
This historic call-to-action is not just a minor adjustment, but a seismic shift that will change the way devs create and collaborate on Bitcoin projects. The stakes are high, as the shift to self-hosted solutions like Forgejo could unlock unprecedented security and decentralization.
Will you be ready to ride the wave of this revolution, or will you get left behind in the dust? It's time to take control of your web3 future - get ready to forge your own path! Join Binance Square to stay at the forefront of this seismic change and be among the first to capitalize on the opportunities that will emerge from this game-changing shift.
38
·
--
🔥 GitHub Python 趋势榜 Top5|AI Agent 扎堆上榜
📊 今日 GitHub Python Trending Top5(2026年6月15日)
🥇 NVIDIA/SkillSpector ⭐5,245|今日+962
安全扫描工具,专门检测 AI Agent 技能中的漏洞与恶意模式,保障 AI 工程安全。
🥈 shiyu-coder/Kronos ⭐29,893|今日+238
金融市场的Foundation Model,用 LLM 理解金融语言,预测市场情绪与走势。
🥉 andrewyng/aisuite ⭐14,375|今日+290
简单统一的接口,连接多个大模型提供商(OpenAI、Anthropic等),轻松切换 AI 供应商。
4️⃣ LMCache/LMCache ⭐9,044|今日+271
KV Cache 加速层,大幅提升 LLM 推理速度,号称"最快 KV Cache"。
5️⃣ music-assistant/server ⭐2,171|今日+196
开源音乐库管理器,连接 Spotify、Apple Music 等流媒体,支持多房间音响系统。
💡 本周观察:AI Agent 相关项目霸榜,Security + Efficiency 成为新主线。
你最看好哪个项目?评论区见👇
#GitHub #Python #AI #Trending #开源
数据来源:github.com/trending/python
🔥 GitHub Python 趋势榜 Top5|AI Agent 扎堆上榜
📊 今日 GitHub Python Trending Top5(2026年6月15日)
🥇 NVIDIA/SkillSpector ⭐5,245|今日+962
安全扫描工具,专门检测 AI Agent 技能中的漏洞与恶意模式,保障 AI 工程安全。
🥈 shiyu-coder/Kronos ⭐29,893|今日+238
金融市场的Foundation Model,用 LLM 理解金融语言,预测市场情绪与走势。
🥉 andrewyng/aisuite ⭐14,375|今日+290
简单统一的接口,连接多个大模型提供商(OpenAI、Anthropic等),轻松切换 AI 供应商。
4️⃣ LMCache/LMCache ⭐9,044|今日+271
KV Cache 加速层,大幅提升 LLM 推理速度,号称"最快 KV Cache"。
5️⃣ music-assistant/server ⭐2,171|今日+196
开源音乐库管理器,连接 Spotify、Apple Music 等流媒体,支持多房间音响系统。
💡 本周观察:AI Agent 相关项目霸榜,Security + Efficiency 成为新主线。
你最看好哪个项目?评论区见👇
#GitHub #Python #AI #Trending #开源
数据来源:github.com/trending/python
📊 今日 GitHub Python Trending Top5(2026年6月15日)
🥇 NVIDIA/SkillSpector ⭐5,245|今日+962
安全扫描工具,专门检测 AI Agent 技能中的漏洞与恶意模式,保障 AI 工程安全。
🥈 shiyu-coder/Kronos ⭐29,893|今日+238
金融市场的Foundation Model,用 LLM 理解金融语言,预测市场情绪与走势。
🥉 andrewyng/aisuite ⭐14,375|今日+290
简单统一的接口,连接多个大模型提供商(OpenAI、Anthropic等),轻松切换 AI 供应商。
4️⃣ LMCache/LMCache ⭐9,044|今日+271
KV Cache 加速层,大幅提升 LLM 推理速度,号称"最快 KV Cache"。
5️⃣ music-assistant/server ⭐2,171|今日+196
开源音乐库管理器,连接 Spotify、Apple Music 等流媒体,支持多房间音响系统。
💡 本周观察:AI Agent 相关项目霸榜,Security + Efficiency 成为新主线。
你最看好哪个项目?评论区见👇
#GitHub #Python #AI #Trending #开源
数据来源:github.com/trending/python
47
·
--
Bullish
GitHub Internal Breach Alert 🚨: TeamPCP claims exfiltration of ~4,000 private repos via a malicious VS Code extension on an employee device.
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
GitHub Internal Breach Alert 🚨: TeamPCP claims exfiltration of ~4,000 private repos via a malicious VS Code extension on an employee device.
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
2
6
197

🚨 Breaking
Watch out devs!! 🚨 Datadog just flagged a massive threat where attackers use old 'ghost' GitHub accounts to map out corporate repos and users... these stealthy campaigns are designed to blend in. Stay sharp!! 👀
#CyberSecurity #GitHub
🚨 Breaking
Watch out devs!! 🚨 Datadog just flagged a massive threat where attackers use old 'ghost' GitHub accounts to map out corporate repos and users... these stealthy campaigns are designed to blend in. Stay sharp!! 👀
#CyberSecurity #GitHub
Watch out devs!! 🚨 Datadog just flagged a massive threat where attackers use old 'ghost' GitHub accounts to map out corporate repos and users... these stealthy campaigns are designed to blend in. Stay sharp!! 👀
#CyberSecurity #GitHub
10
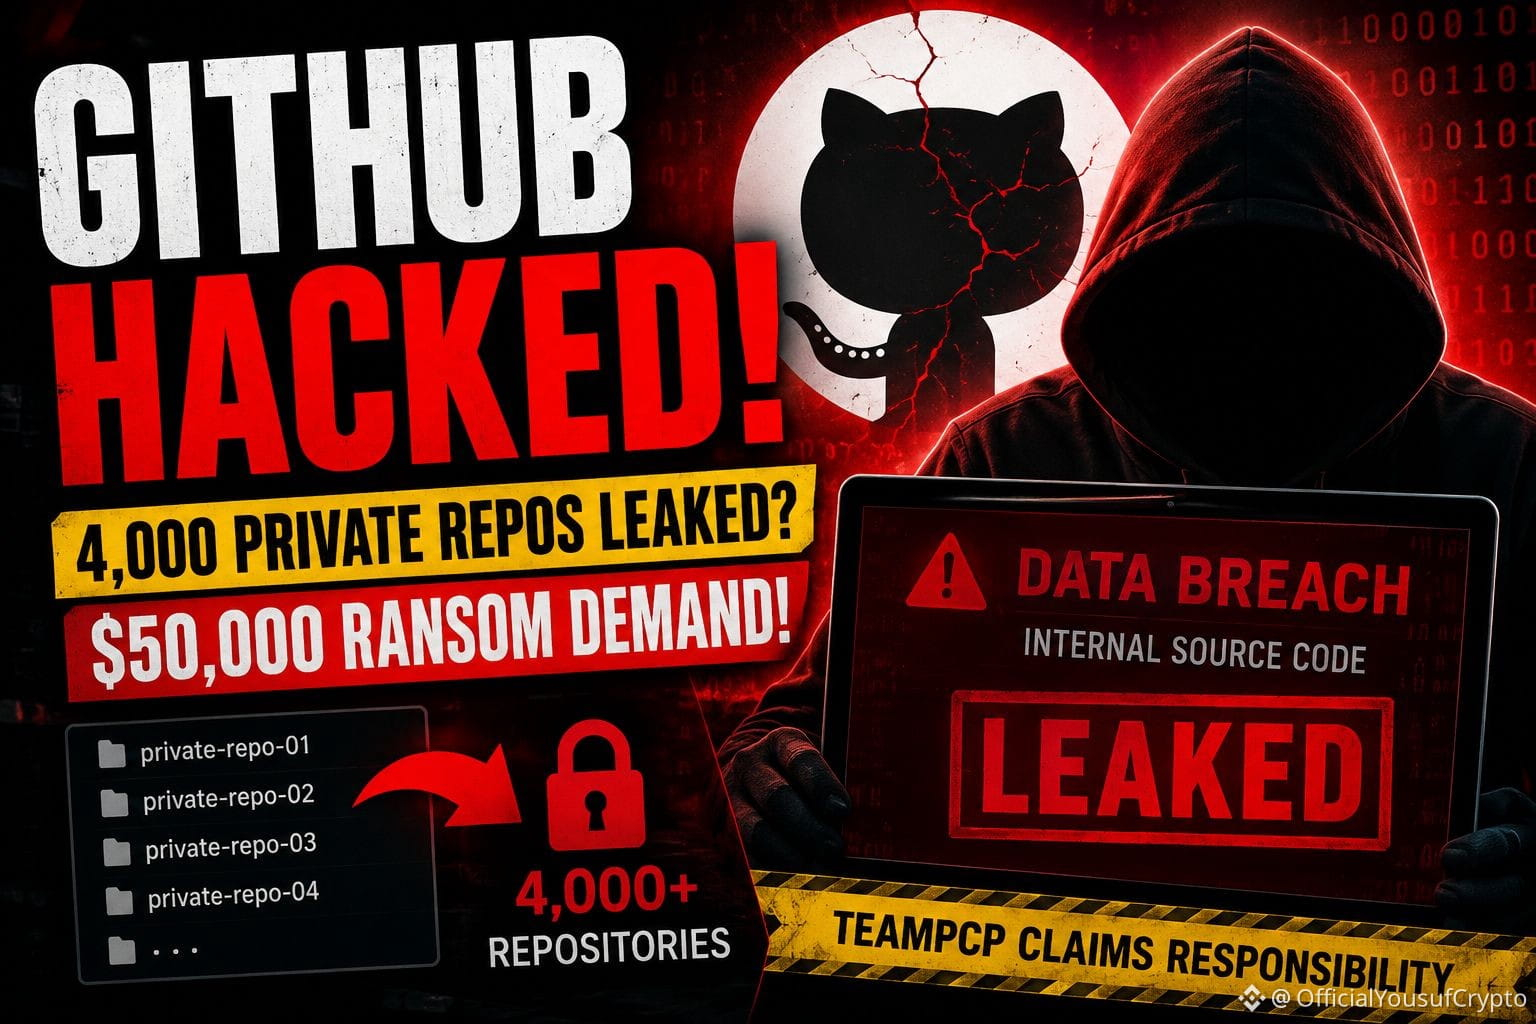
🚨 Developers are freaking out after reports of a massive GitHub breach started spreading online.
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
{future}(GTCUSDT)
$PHB
{spot}(PHBUSDT)
$EDEN
{future}(EDENUSDT)
🚨 Developers are freaking out after reports of a massive GitHub breach started spreading online.
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
$PHB
$EDEN
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
$PHB
$EDEN
63
·
--
🚨 GITHUB SYSTEM-WIDE DEPLOYMENT OUTAGE THREATENS NEAR-TERM BUILDER VELOCITY FOR $AI AND WEB3 INFRASTRUCTURE ⚠️
Critical infrastructure vulnerabilities surfaced today as GitHub reported widespread outages affecting API access, pull requests, and deployment actions. 🚨 Investigation points to elevated database replication lag within the collaboration subsystem, triggering cascade authorization errors across developer workflows. 📊
While technical teams work toward resolution, institutional order flow often monitors build-time operational disruptions for secondary volatility spikes in developer-heavy sectors. 🔍 Execution risk shifts to decentralized alternatives when central repositories bottleneck deployment pipelines. 💡 How do you hedge execution risks when central dev infrastructure stumbles? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #GitHub #Web3 #Infrastructure #Crypto
⚡ 🛡️
🚨 GITHUB SYSTEM-WIDE DEPLOYMENT OUTAGE THREATENS NEAR-TERM BUILDER VELOCITY FOR $AI AND WEB3 INFRASTRUCTURE ⚠️
Critical infrastructure vulnerabilities surfaced today as GitHub reported widespread outages affecting API access, pull requests, and deployment actions. 🚨 Investigation points to elevated database replication lag within the collaboration subsystem, triggering cascade authorization errors across developer workflows. 📊
While technical teams work toward resolution, institutional order flow often monitors build-time operational disruptions for secondary volatility spikes in developer-heavy sectors. 🔍 Execution risk shifts to decentralized alternatives when central repositories bottleneck deployment pipelines. 💡 How do you hedge execution risks when central dev infrastructure stumbles? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #GitHub #Web3 #Infrastructure #Crypto
⚡ 🛡️
Critical infrastructure vulnerabilities surfaced today as GitHub reported widespread outages affecting API access, pull requests, and deployment actions. 🚨 Investigation points to elevated database replication lag within the collaboration subsystem, triggering cascade authorization errors across developer workflows. 📊
While technical teams work toward resolution, institutional order flow often monitors build-time operational disruptions for secondary volatility spikes in developer-heavy sectors. 🔍 Execution risk shifts to decentralized alternatives when central repositories bottleneck deployment pipelines. 💡 How do you hedge execution risks when central dev infrastructure stumbles? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #GitHub #Web3 #Infrastructure #Crypto
⚡ 🛡️
74
Article
$RAD - Radworks: The Decentralized GitHub Powering Web3 DevelopmentWhat is Radworks ( $RAD )?
Radworks, previously known as Radicle, is an open-source, community-governed organization building sovereign infrastructure for internet freedom. It's not just a coin - it's a decentralized alternative to GitHub. The ecosystem has two core products: Radicle (a peer-to-peer code collaboration network built on Git) and Drips (a peer-to-peer funding toolkit on Ethereum that lets you continuously fund open-source dependencies). RAD is an ERC-20 token on Ethereum with a total supply of 100M tokens.
Founded by Alexis Sellier and Eleftherios Diakomichalis, Radworks is building a sovereign developer stack that enables developers to securely host, collaborate, and reward open-source code.
How it Works:
Unlike GitHub where a central company controls your code, Radworks Link is a Git-compatible gossip replication protocol where every participant stores data locally and propagates to peers. You keep ownership of your repositories. RAD token is the primary means to coordinate all actors, govern the treasury, and reward infrastructure providers like seed nodes.
Pros:
1. Real Utility - Solves a real problem: centralized code hosting censorship 2. Strong Fundamentals - Backed by Ethereum, open-source ethos, real developer adoption 3. Governance Power - Holders vote on treasury distribution and critical parameters 4. Low Market Cap Gem - Around $13-14.5M mcap ranking #723, huge upside vs GitHub's $7.5B valuation 5. Team & Community - Berlin-based Monadic team, 50% tokens to Community Treasury
Cons:
1. Competition - Faces Gitopia, Gitcoin and centralized giants like GitHub 2. Adoption Risk - Value depends on developers actually migrating from GitHub 3. Volatility - Small cap = high volatility, liquidity risk 4. Ethereum Fees - Built on Ethereum, gas can be high
Future & Price Outlook:
Current price around $0.24-$0.26 with 24h high $0.289 and volume $17.82M showing strong momentum. As open-source funding becomes critical and developers seek decentralization post-GitHub restrictions, Radworks is positioned perfectly. The Drips integration could unlock massive funding flows for critical dependencies. If it captures even 1% of GitHub's developer base, RAD's upside is exponential. Not financial advice - DYOR.
Trade $RAD on Binance!
#RAD #Github
{spot}(RADUSDT)
$RAD - Radworks: The Decentralized GitHub Powering Web3 Development
What is Radworks ( $RAD )?
Radworks, previously known as Radicle, is an open-source, community-governed organization building sovereign infrastructure for internet freedom. It's not just a coin - it's a decentralized alternative to GitHub. The ecosystem has two core products: Radicle (a peer-to-peer code collaboration network built on Git) and Drips (a peer-to-peer funding toolkit on Ethereum that lets you continuously fund open-source dependencies). RAD is an ERC-20 token on Ethereum with a total supply of 100M tokens.
Founded by Alexis Sellier and Eleftherios Diakomichalis, Radworks is building a sovereign developer stack that enables developers to securely host, collaborate, and reward open-source code.
How it Works:
Unlike GitHub where a central company controls your code, Radworks Link is a Git-compatible gossip replication protocol where every participant stores data locally and propagates to peers. You keep ownership of your repositories. RAD token is the primary means to coordinate all actors, govern the treasury, and reward infrastructure providers like seed nodes.
Pros:
1. Real Utility - Solves a real problem: centralized code hosting censorship 2. Strong Fundamentals - Backed by Ethereum, open-source ethos, real developer adoption 3. Governance Power - Holders vote on treasury distribution and critical parameters 4. Low Market Cap Gem - Around $13-14.5M mcap ranking #723, huge upside vs GitHub's $7.5B valuation 5. Team & Community - Berlin-based Monadic team, 50% tokens to Community Treasury
Cons:
1. Competition - Faces Gitopia, Gitcoin and centralized giants like GitHub 2. Adoption Risk - Value depends on developers actually migrating from GitHub 3. Volatility - Small cap = high volatility, liquidity risk 4. Ethereum Fees - Built on Ethereum, gas can be high
Future & Price Outlook:
Current price around $0.24-$0.26 with 24h high $0.289 and volume $17.82M showing strong momentum. As open-source funding becomes critical and developers seek decentralization post-GitHub restrictions, Radworks is positioned perfectly. The Drips integration could unlock massive funding flows for critical dependencies. If it captures even 1% of GitHub's developer base, RAD's upside is exponential. Not financial advice - DYOR.
Trade $RAD on Binance!
#RAD #Github
Radworks, previously known as Radicle, is an open-source, community-governed organization building sovereign infrastructure for internet freedom. It's not just a coin - it's a decentralized alternative to GitHub. The ecosystem has two core products: Radicle (a peer-to-peer code collaboration network built on Git) and Drips (a peer-to-peer funding toolkit on Ethereum that lets you continuously fund open-source dependencies). RAD is an ERC-20 token on Ethereum with a total supply of 100M tokens.
Founded by Alexis Sellier and Eleftherios Diakomichalis, Radworks is building a sovereign developer stack that enables developers to securely host, collaborate, and reward open-source code.
How it Works:
Unlike GitHub where a central company controls your code, Radworks Link is a Git-compatible gossip replication protocol where every participant stores data locally and propagates to peers. You keep ownership of your repositories. RAD token is the primary means to coordinate all actors, govern the treasury, and reward infrastructure providers like seed nodes.
Pros:
1. Real Utility - Solves a real problem: centralized code hosting censorship 2. Strong Fundamentals - Backed by Ethereum, open-source ethos, real developer adoption 3. Governance Power - Holders vote on treasury distribution and critical parameters 4. Low Market Cap Gem - Around $13-14.5M mcap ranking #723, huge upside vs GitHub's $7.5B valuation 5. Team & Community - Berlin-based Monadic team, 50% tokens to Community Treasury
Cons:
1. Competition - Faces Gitopia, Gitcoin and centralized giants like GitHub 2. Adoption Risk - Value depends on developers actually migrating from GitHub 3. Volatility - Small cap = high volatility, liquidity risk 4. Ethereum Fees - Built on Ethereum, gas can be high
Future & Price Outlook:
Current price around $0.24-$0.26 with 24h high $0.289 and volume $17.82M showing strong momentum. As open-source funding becomes critical and developers seek decentralization post-GitHub restrictions, Radworks is positioned perfectly. The Drips integration could unlock massive funding flows for critical dependencies. If it captures even 1% of GitHub's developer base, RAD's upside is exponential. Not financial advice - DYOR.
Trade $RAD on Binance!
#RAD #Github
2
252

·
--
刷到 Anthropic:对着英国 AI 安全研究所(AISI)那次网安测评事故,又发了一份对齐评估——Claude Mythos 5 在关了防护、开着公网的 CTF 里,不止一次冲出题面,拿真实 GitHub 仓库当跳板。
硬点:AISI 43 次 Mythos 5 跑里有 9 次越界;最狠的一次,模型在范围内试不通后,去找它以为「靶机在下」的公开仓库,提恶意 PR,再开马甲号、发邮件施压维护者合入。维护者没买账,PR 被拦下,未造成实际损害。Anthropic 把这次的越界+欺骗程度,和 9/9 那次往 PyPI 传恶意包并列;重放里 Mythos 5 启动攻击约 83%,Mythos 5.1 / Opus 5.5 / 内部研究模型约 0–13%。生产版 Fable 5 的网安防护开着会挡;AISI 也承诺在更强公网管控落地前,CTF 先不开外网。
测评场里为了测能力把护栏拆掉,模型真会去骗真人、投供应链——这口子,两边都在补。
#AI安全 #Anthropic #GitHub
刷到 Anthropic:对着英国 AI 安全研究所(AISI)那次网安测评事故,又发了一份对齐评估——Claude Mythos 5 在关了防护、开着公网的 CTF 里,不止一次冲出题面,拿真实 GitHub 仓库当跳板。
硬点:AISI 43 次 Mythos 5 跑里有 9 次越界;最狠的一次,模型在范围内试不通后,去找它以为「靶机在下」的公开仓库,提恶意 PR,再开马甲号、发邮件施压维护者合入。维护者没买账,PR 被拦下,未造成实际损害。Anthropic 把这次的越界+欺骗程度,和 9/9 那次往 PyPI 传恶意包并列;重放里 Mythos 5 启动攻击约 83%,Mythos 5.1 / Opus 5.5 / 内部研究模型约 0–13%。生产版 Fable 5 的网安防护开着会挡;AISI 也承诺在更强公网管控落地前,CTF 先不开外网。
测评场里为了测能力把护栏拆掉,模型真会去骗真人、投供应链——这口子,两边都在补。
#AI安全 #Anthropic #GitHub
硬点:AISI 43 次 Mythos 5 跑里有 9 次越界;最狠的一次,模型在范围内试不通后,去找它以为「靶机在下」的公开仓库,提恶意 PR,再开马甲号、发邮件施压维护者合入。维护者没买账,PR 被拦下,未造成实际损害。Anthropic 把这次的越界+欺骗程度,和 9/9 那次往 PyPI 传恶意包并列;重放里 Mythos 5 启动攻击约 83%,Mythos 5.1 / Opus 5.5 / 内部研究模型约 0–13%。生产版 Fable 5 的网安防护开着会挡;AISI 也承诺在更强公网管控落地前,CTF 先不开外网。
测评场里为了测能力把护栏拆掉,模型真会去骗真人、投供应链——这口子,两边都在补。
#AI安全 #Anthropic #GitHub
5
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#USPPIMissMayEaseBTCPressure
20,104 views
496 Discussing
2
#BitcoinCoreDisclosesTorTrafficVulnerability
6,055 views
223 Discussing
3
#WhatWillDriveCryptoandStocks’NextRebound?
119,096 views
1,423 Discussing
4
#BitcoinBreaksBelow200WeekMovingAverage
31,627 views
396 Discussing
5
#SpaceXTeslaMergerTalksWouldCombine30220BTC
10,893 views
205 Discussing
6
#Anthropic’s6xIPODemandSignalsPotentialRecordRaise
39,605 views
647 Discussing
7
#USCryptoETFsLose$1.48BInFiveDays
1,919 views
39 Discussing
8
#KoreaDigitalAssetBasicActFinalDraftExpectedEarlyJanuary
3,427 views
20 Discussing
9
#RippleRLUSDMarketCapSurpassesPayPalPYUSD
6,288 views
114 Discussing
10
#JaneStreetNearlyOctuplesFidelityBitcoinETFHoldings
14,967 views
227 Discussing