

web3亭姐
369 Posts
web3亭姐
Report
Block User
亭姐:资深职业经理人,币圈小菜鸟
25 Following
12 Followers
127 Liked
Posts
All
Quotes
·
--
$FLORK What kind of demon coin is this? I’m shocked—nearly a thousand times in four days 🙊
$FLORK What kind of demon coin is this? I’m shocked—nearly a thousand times in four days 🙊
1
336
·
--
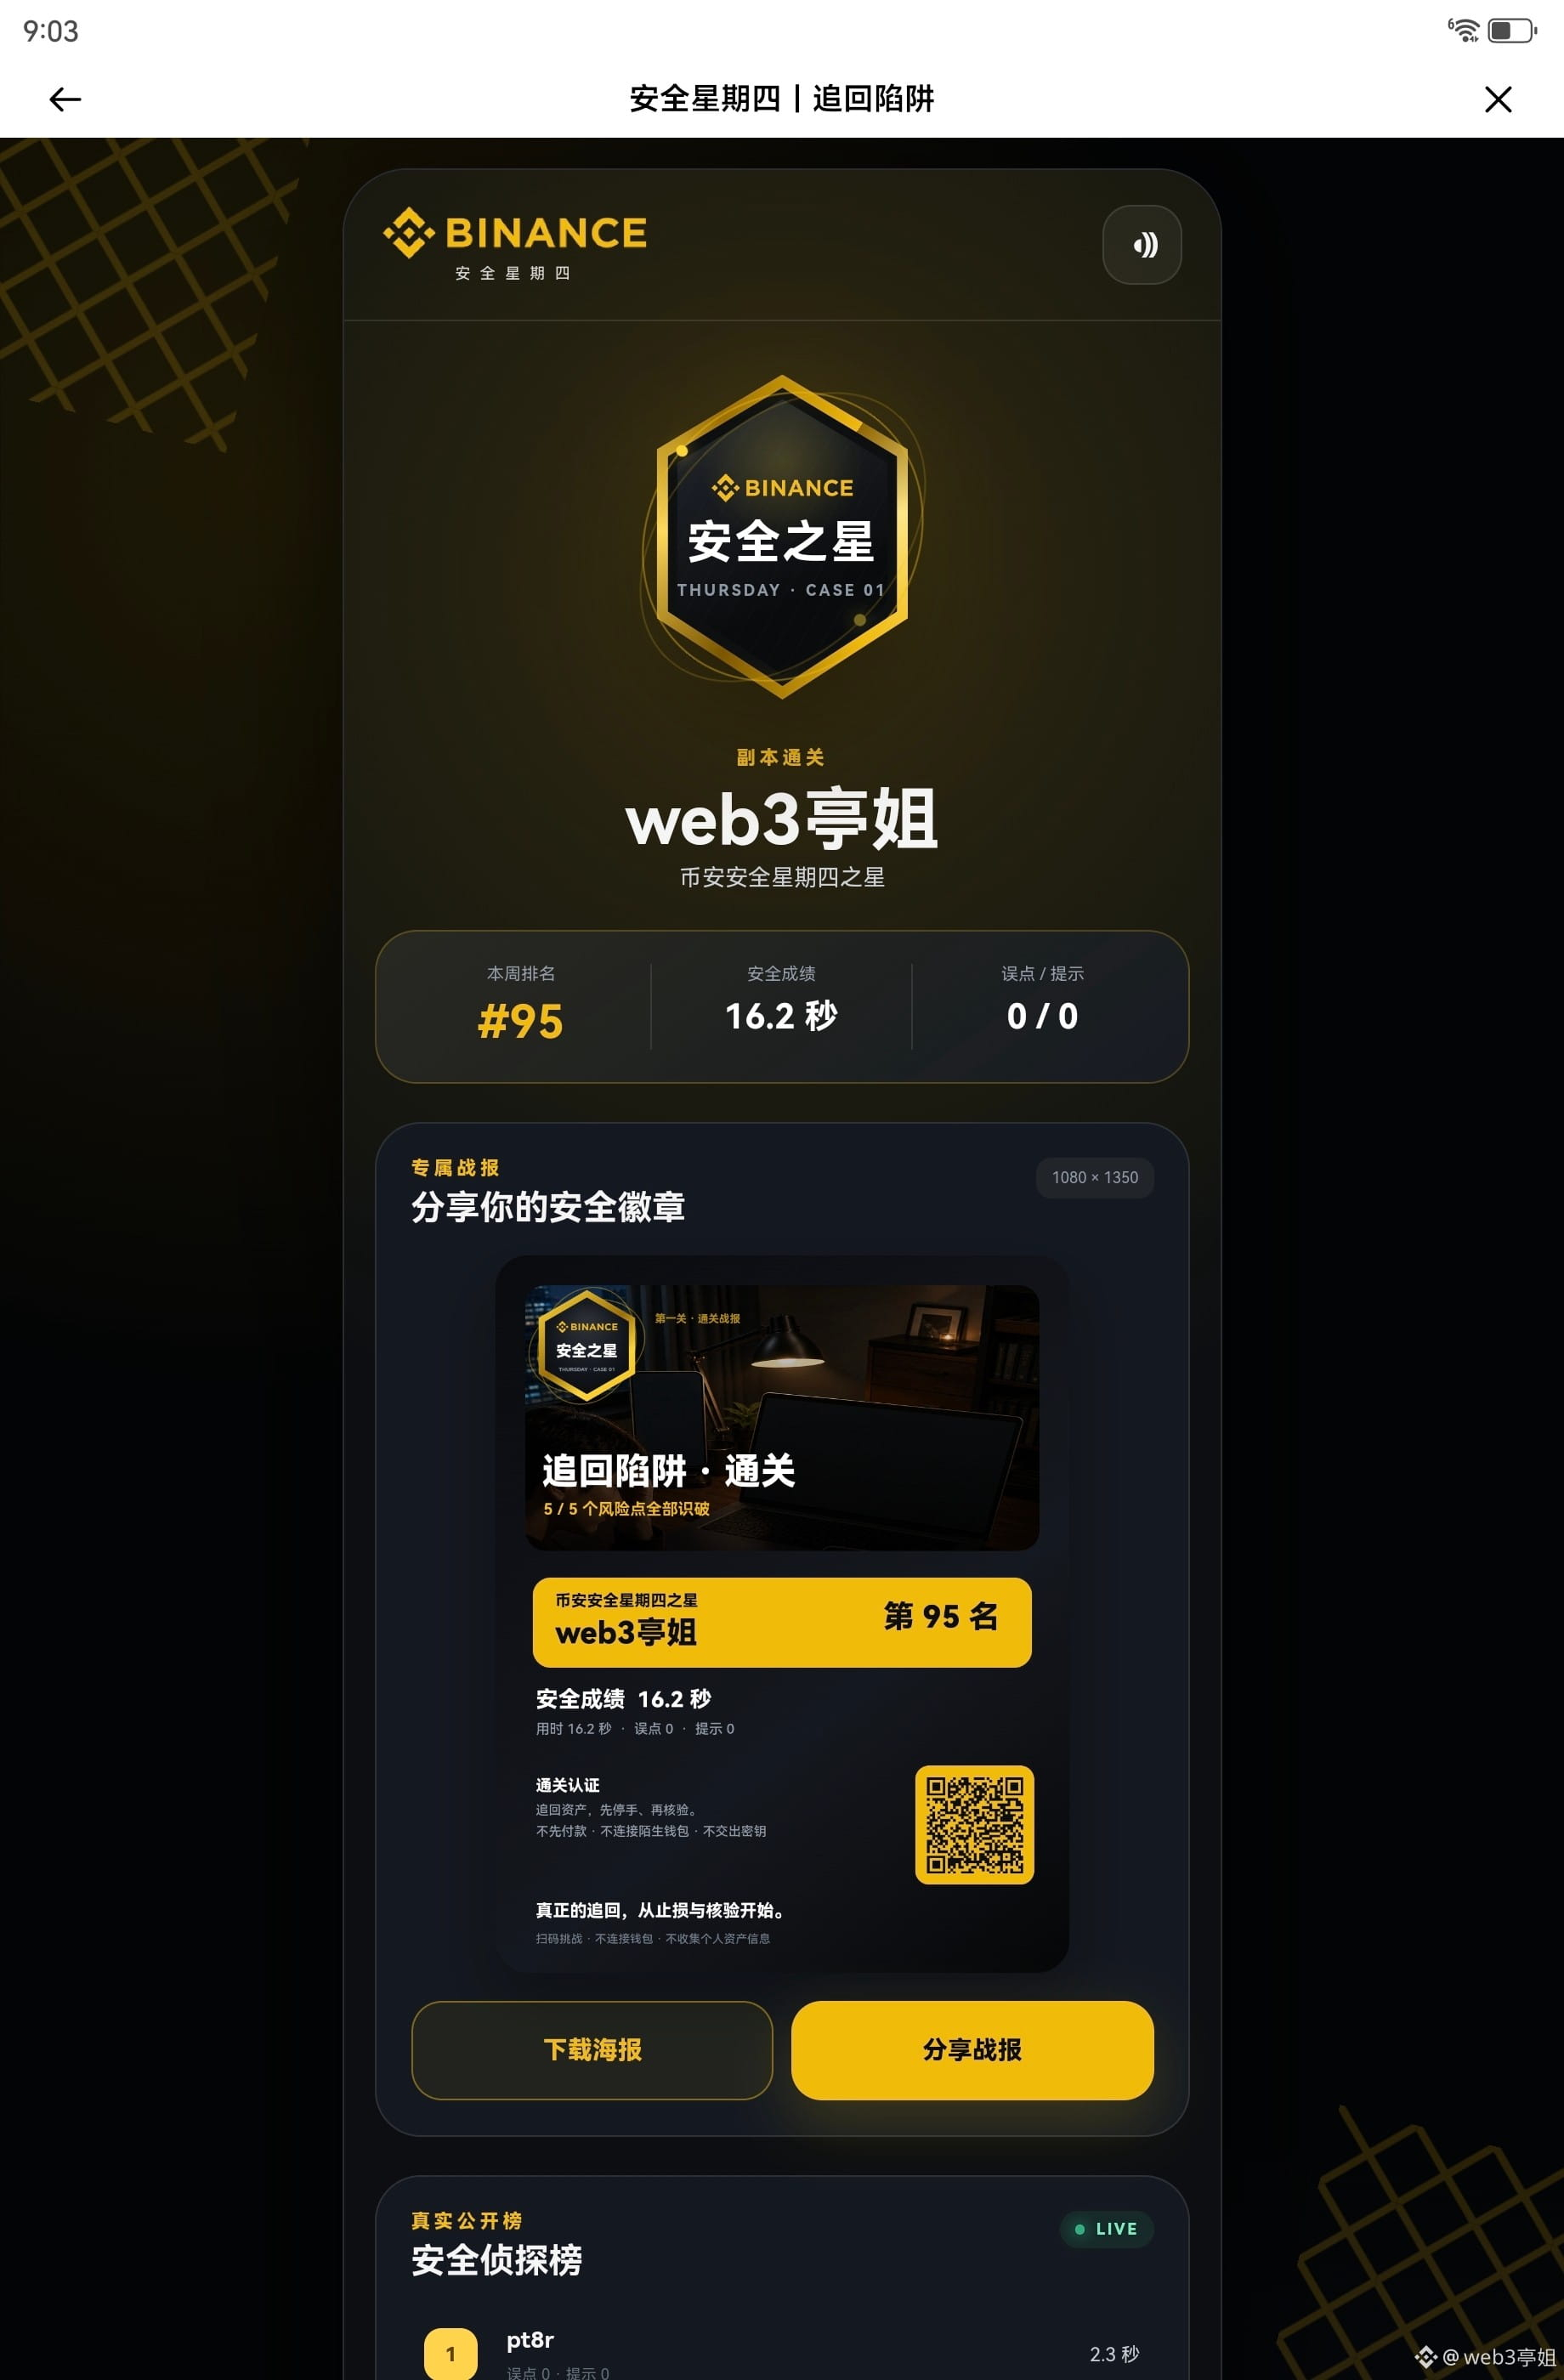
#币安安全星期四
A very fun and also very educational game. Wallet security is very important—these traps are things we might encounter in everyday life. This 17-second time is my best result out of three attempts so far. Friends, come and take on the challenge too—go for it!
#币安安全星期四
A very fun and also very educational game. Wallet security is very important—these traps are things we might encounter in everyday life. This 17-second time is my best result out of three attempts so far. Friends, come and take on the challenge too—go for it!
A very fun and also very educational game. Wallet security is very important—these traps are things we might encounter in everyday life. This 17-second time is my best result out of three attempts so far. Friends, come and take on the challenge too—go for it!

币安Binance华语
·
--
“Don’t laugh—you won’t find the 4th one either 😨”
🪤 They say this is the hardest #币安安全星期四 challenge in history: in the shortest time, can you find all the traps?
👉 点击参与实景陷阱追踪挑战, compete for a spot on the leaderboard 🏆
The top 10 on the leaderboard each get a 100U detective reward, and the top 3 also receive a themed gift box!
Share it and post your clear-through screenshot in the comments, and then 15 people will be selected to receive 44U 🧧
🪤 They say this is the hardest #币安安全星期四 challenge in history: in the shortest time, can you find all the traps?
👉 点击参与实景陷阱追踪挑战, compete for a spot on the leaderboard 🏆
The top 10 on the leaderboard each get a 100U detective reward, and the top 3 also receive a themed gift box!
Share it and post your clear-through screenshot in the comments, and then 15 people will be selected to receive 44U 🧧
60
·
--
$BTC has pulled back about $3,000 from the high. Many friends are calling for bargain buying. I feel that the direction is still unclear—there’s a possibility that BTC could drop again to the 60s. And most altcoins have already fallen back to their starting point.
Let’s recap:
As of September 1, 2026, Bitcoin is consolidating around $78,000. The roughly 24% gain in August was mainly driven by spot buying. But in the short term, the struggle between bulls and bears is intense, and the next direction remains unclear.
The bullish factors are that institutional demand is still strong. Last week, net inflows into U.S. spot Bitcoin ETFs were nearly $1 billion. Technically, if it can effectively hold above $78,340, it may further test the resistance zone at $80,000–$81,000.
The risks are also significant: the probability of a September rate hike by the Fed has risen to 57%, and hawkish expectations limit upside room. In the derivatives market, the biggest pain point for options expiring on September 25 is concentrated in the $70,000–$73,000 range—below the current spot price—and put options have been leading in trading volume, suggesting downside risk.
In the short term, the key is whether the Fed’s September meeting (September 15) and the $80,000 level can be effectively broken through.
$BTC has pulled back about $3,000 from the high. Many friends are calling for bargain buying. I feel that the direction is still unclear—there’s a possibility that BTC could drop again to the 60s. And most altcoins have already fallen back to their starting point.
Let’s recap:
As of September 1, 2026, Bitcoin is consolidating around $78,000. The roughly 24% gain in August was mainly driven by spot buying. But in the short term, the struggle between bulls and bears is intense, and the next direction remains unclear.
The bullish factors are that institutional demand is still strong. Last week, net inflows into U.S. spot Bitcoin ETFs were nearly $1 billion. Technically, if it can effectively hold above $78,340, it may further test the resistance zone at $80,000–$81,000.
The risks are also significant: the probability of a September rate hike by the Fed has risen to 57%, and hawkish expectations limit upside room. In the derivatives market, the biggest pain point for options expiring on September 25 is concentrated in the $70,000–$73,000 range—below the current spot price—and put options have been leading in trading volume, suggesting downside risk.
In the short term, the key is whether the Fed’s September meeting (September 15) and the $80,000 level can be effectively broken through.
Let’s recap:
As of September 1, 2026, Bitcoin is consolidating around $78,000. The roughly 24% gain in August was mainly driven by spot buying. But in the short term, the struggle between bulls and bears is intense, and the next direction remains unclear.
The bullish factors are that institutional demand is still strong. Last week, net inflows into U.S. spot Bitcoin ETFs were nearly $1 billion. Technically, if it can effectively hold above $78,340, it may further test the resistance zone at $80,000–$81,000.
The risks are also significant: the probability of a September rate hike by the Fed has risen to 57%, and hawkish expectations limit upside room. In the derivatives market, the biggest pain point for options expiring on September 25 is concentrated in the $70,000–$73,000 range—below the current spot price—and put options have been leading in trading volume, suggesting downside risk.
In the short term, the key is whether the Fed’s September meeting (September 15) and the $80,000 level can be effectively broken through.
101
·
--
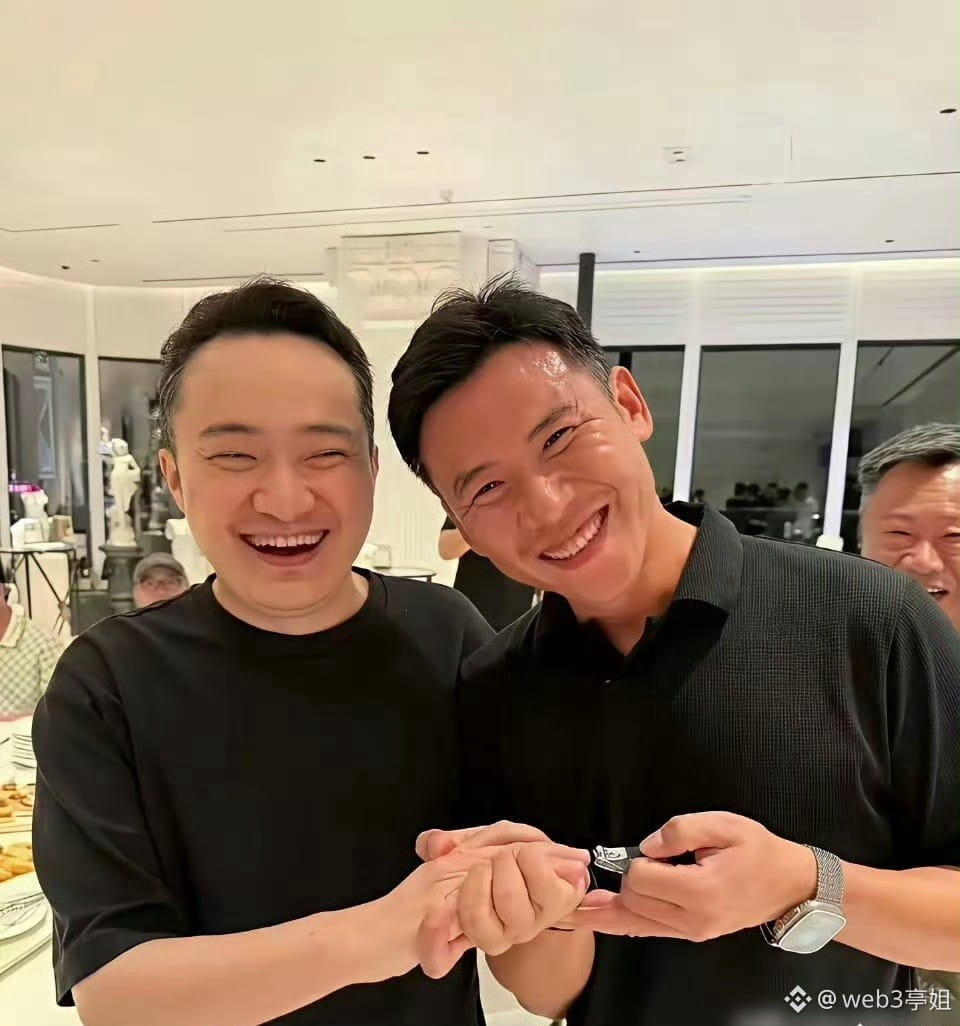
When I saw this picture of Sun Ge cutting nails, how does everyone feel—angry or not? Is it really possible to do something so shameless just for attention? A few days ago, a classmate’s post-writing basically ruined his ex-girlfriend’s career, and now he still keeps stepping on her dignity, rubbing it against the ground again and again. To demand the dowry—didn’t he already sue her, along with her parents? Why is he still so determined to trample on someone? Without even getting into who’s right or wrong, as women, I just feel a chill down my spine. It feels like a thoroughly inhumane mockery. Tell me—who will dare to get close to Sun Ge in the future?
When I saw this picture of Sun Ge cutting nails, how does everyone feel—angry or not? Is it really possible to do something so shameless just for attention? A few days ago, a classmate’s post-writing basically ruined his ex-girlfriend’s career, and now he still keeps stepping on her dignity, rubbing it against the ground again and again. To demand the dowry—didn’t he already sue her, along with her parents? Why is he still so determined to trample on someone? Without even getting into who’s right or wrong, as women, I just feel a chill down my spine. It feels like a thoroughly inhumane mockery. Tell me—who will dare to get close to Sun Ge in the future?
8
1
5.4k
·
--
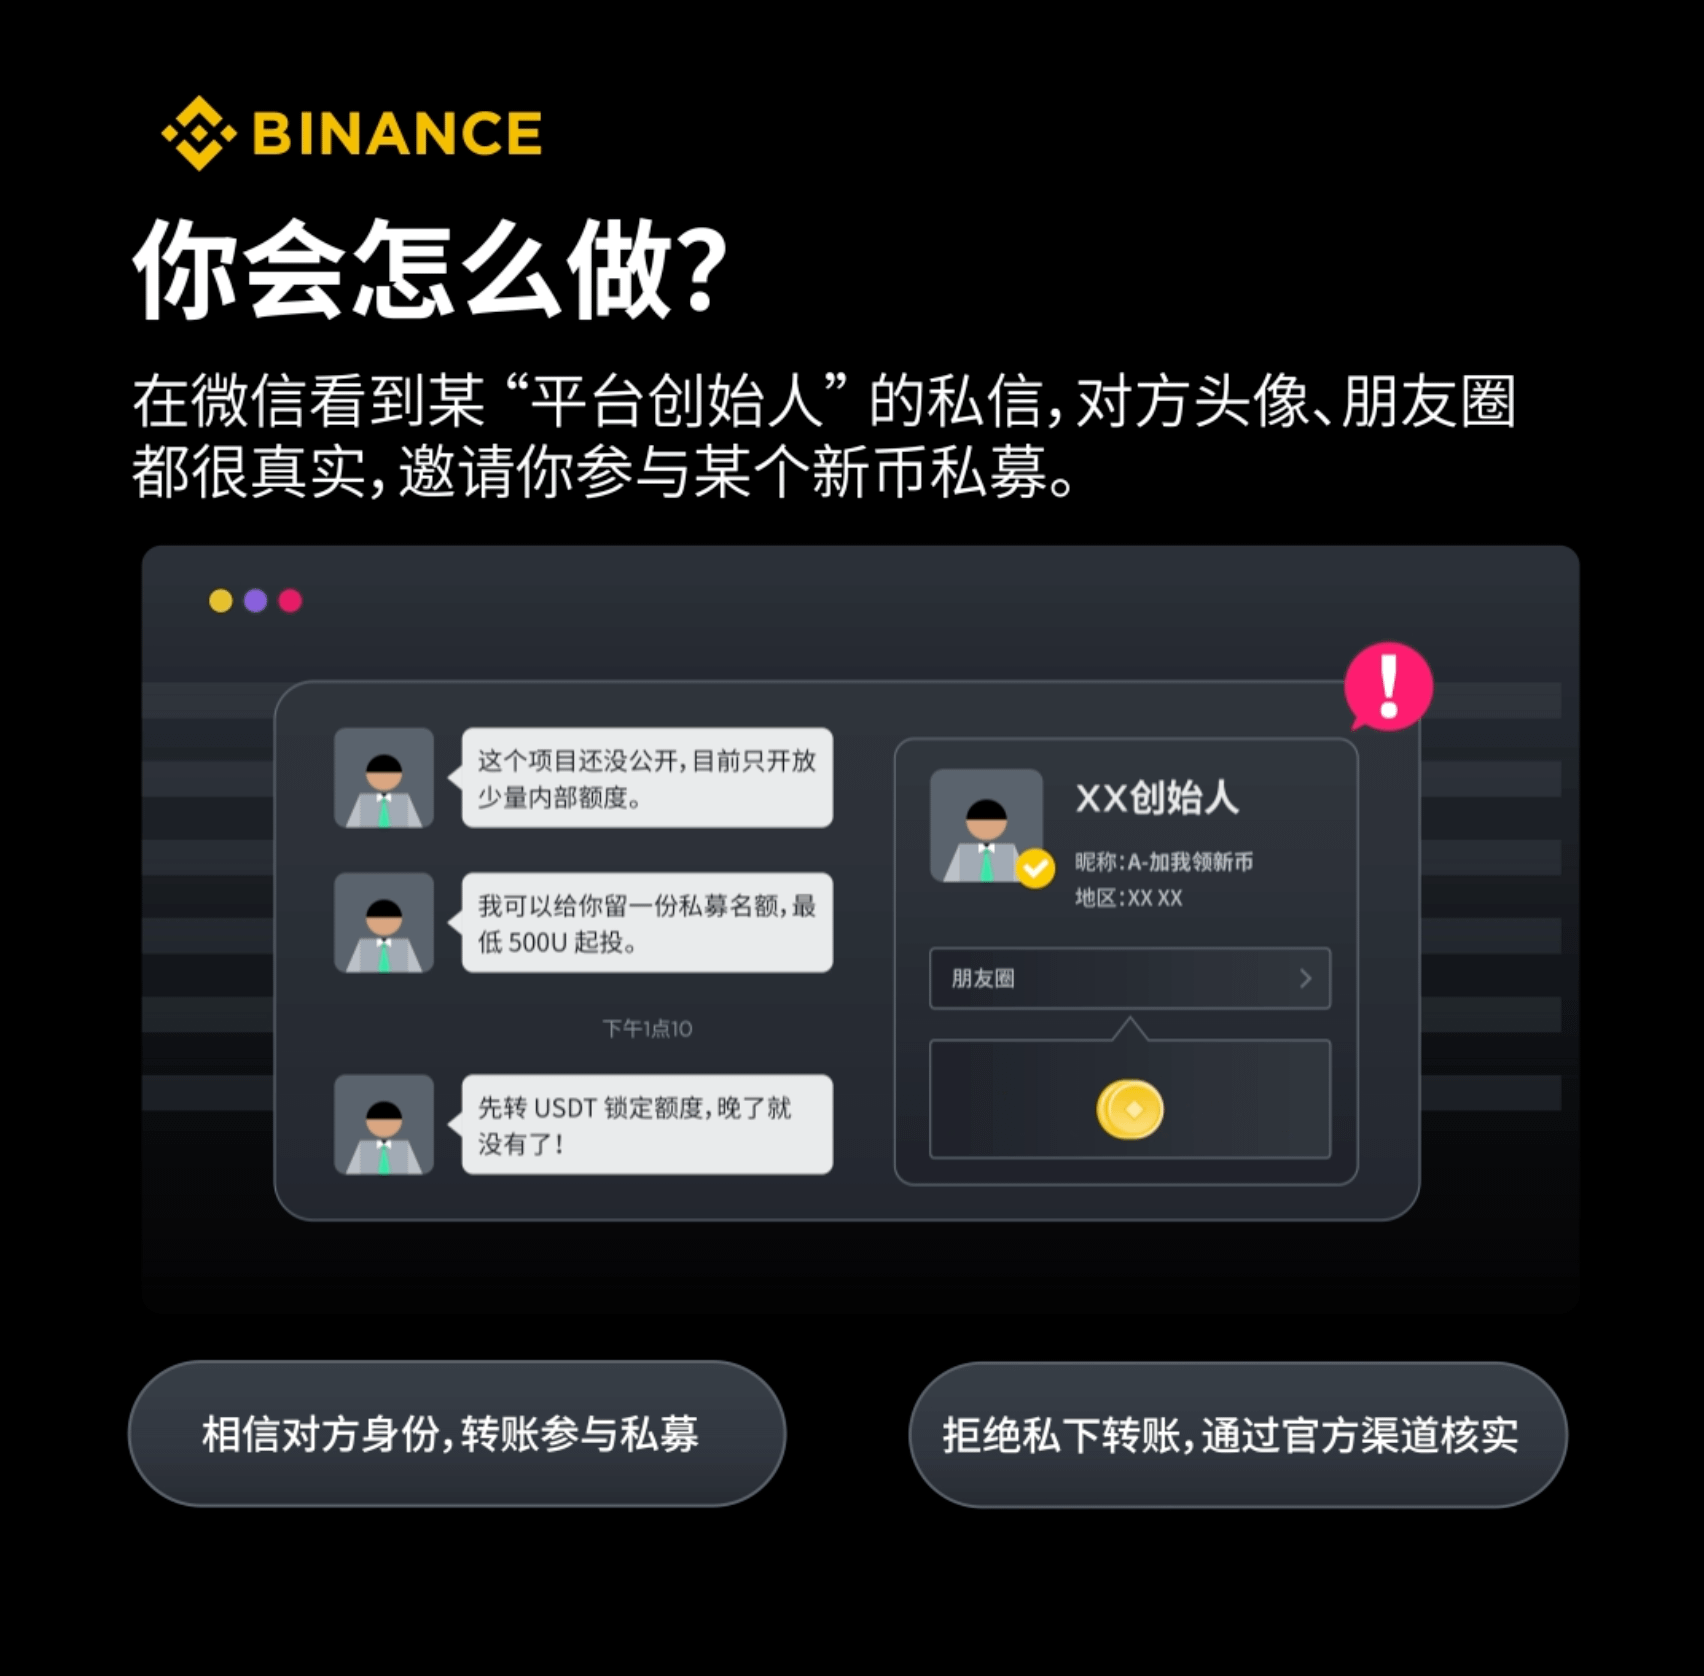
Choose C
Binance official never contacts users privately; social information is easy to forge. Internal quotas are never sold through DMs. Using a sense of urgency is a typical scam. Always verify through official channels and never transfer money.
Choose C
Binance official never contacts users privately; social information is easy to forge. Internal quotas are never sold through DMs. Using a sense of urgency is a typical scam. Always verify through official channels and never transfer money.
Binance official never contacts users privately; social information is easy to forge. Internal quotas are never sold through DMs. Using a sense of urgency is a typical scam. Always verify through official channels and never transfer money.
币安Binance华语
·
--
😈“I’m the founder of the platform. The last spot for the new coin private sale—500 USDT, hop on!”
What would you do❓
A. Finally, the fortune of wealth is my turn—I rush in 🤑
B. Everything matches in my circle of friends—the identity package is real 😎
C. I’d rather not take this luck. Don’t transfer money—go verify with the official first 🔍
⬇️ RT and leave your choice and reasons. We’ll randomly pick 3 people, each gets 40U #币安安全星期四
What would you do❓
A. Finally, the fortune of wealth is my turn—I rush in 🤑
B. Everything matches in my circle of friends—the identity package is real 😎
C. I’d rather not take this luck. Don’t transfer money—go verify with the official first 🔍
⬇️ RT and leave your choice and reasons. We’ll randomly pick 3 people, each gets 40U #币安安全星期四
86
·
--
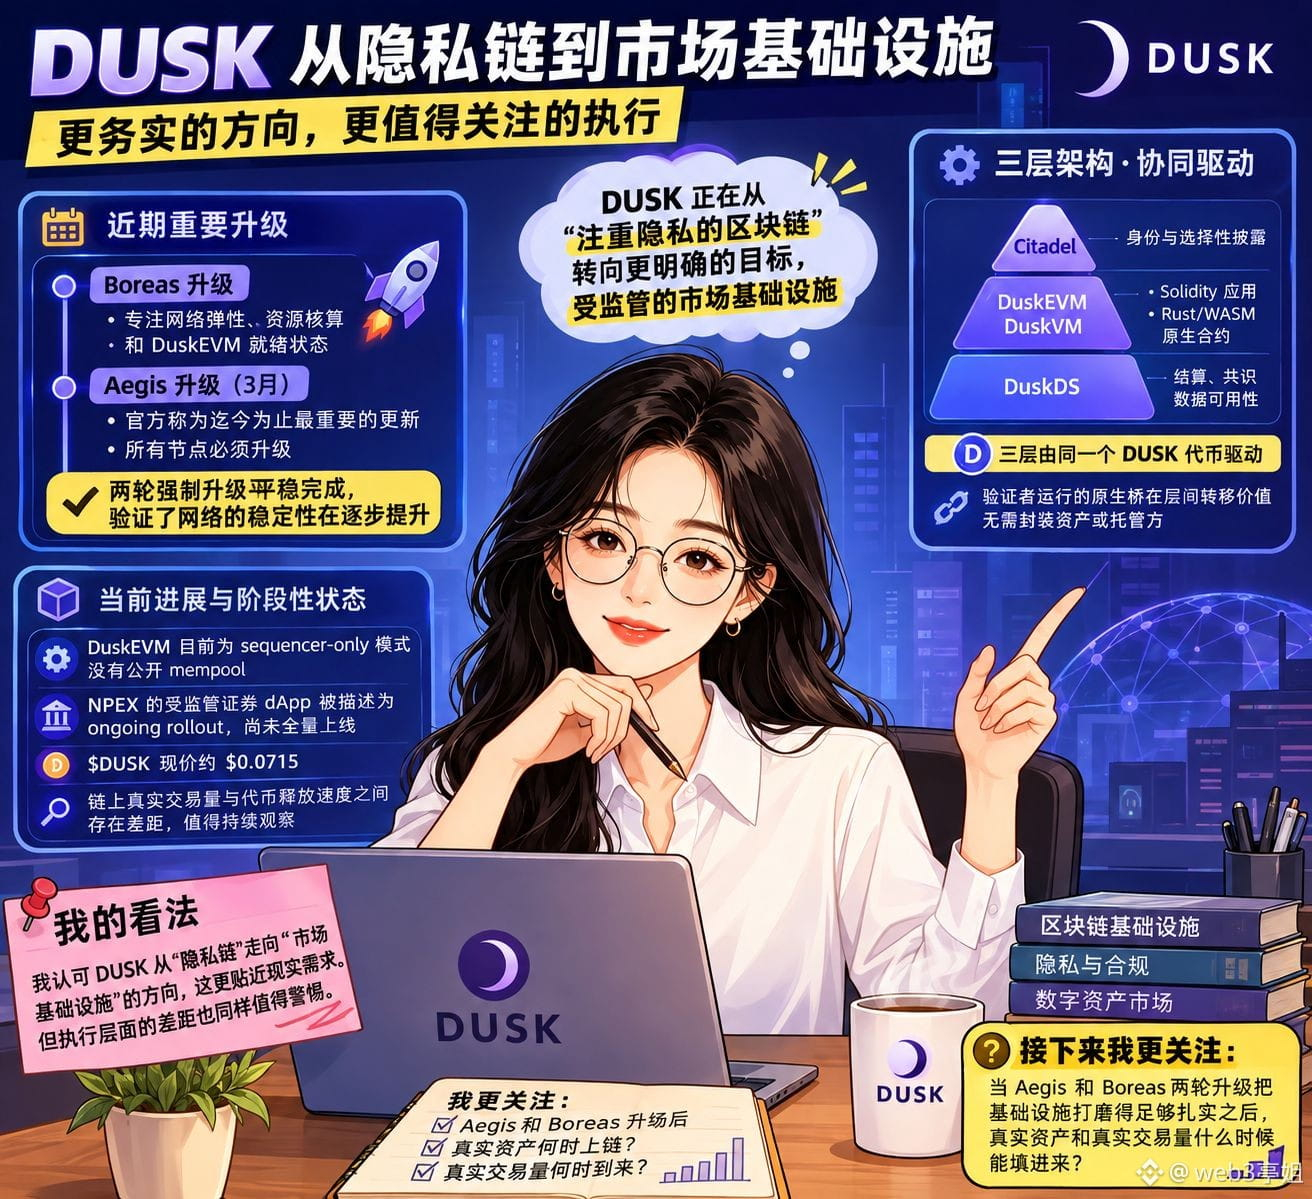
I recently re-read the document for @Dusk_Foundation , and there’s one detail that keeps catching my attention: this project seems to be shifting from a “privacy-focused blockchain” to a more explicitly defined goal—regulated market infrastructure.
This isn’t a flashy narrative shift; it’s a series of engineering adjustments. The recent Boreas upgrade focuses on network resilience, resource accounting, and the readiness state of DuskEVM. In March, there’s another round of the Aegis upgrade, described by the official team as the most important update to date, with all nodes required to upgrade. Two rounds of forced upgrades without any major issues in the process in itself suggests that the network’s stability is being steadily validated. It may sound a bit dry, but for infrastructure, “dry” might actually be the point.
Dusk’s current three-layer architecture is already quite clear: the bottom layer, DuskDS, handles settlement, consensus, and data availability; the middle layer has DuskEVM running Solidity apps, while DuskVM runs Rust/WASM native contracts; the top layer, Citadel, manages identity and selective disclosure. The three layers are driven by the same DUSK token. The native bridges run by validators transfer value between layers without wrapping assets or involving custodians.
But I have to say this is still an evolving system—not a finished product. DuskEVM is currently running in a sequencer-only mode, with no public mempool. NPEX’s regulated securities dApp is described as an “ongoing rollout,” not yet in a full launch state. $DUSK ’s current market price is around $0.0715, and the gap between on-chain real transaction activity and the token release rate is also worth ongoing observation. I support the direction of moving from a “privacy chain” to “market infrastructure,” but the execution-layer gap is something to stay wary of.
What I’m more focused on now is: after Aegis and Boreas have sufficiently hardened the infrastructure, when will real-world assets and real transaction volume actually move in? #dusk
I recently re-read the document for @Dusk , and there’s one detail that keeps catching my attention: this project seems to be shifting from a “privacy-focused blockchain” to a more explicitly defined goal—regulated market infrastructure.
This isn’t a flashy narrative shift; it’s a series of engineering adjustments. The recent Boreas upgrade focuses on network resilience, resource accounting, and the readiness state of DuskEVM. In March, there’s another round of the Aegis upgrade, described by the official team as the most important update to date, with all nodes required to upgrade. Two rounds of forced upgrades without any major issues in the process in itself suggests that the network’s stability is being steadily validated. It may sound a bit dry, but for infrastructure, “dry” might actually be the point.
Dusk’s current three-layer architecture is already quite clear: the bottom layer, DuskDS, handles settlement, consensus, and data availability; the middle layer has DuskEVM running Solidity apps, while DuskVM runs Rust/WASM native contracts; the top layer, Citadel, manages identity and selective disclosure. The three layers are driven by the same DUSK token. The native bridges run by validators transfer value between layers without wrapping assets or involving custodians.
But I have to say this is still an evolving system—not a finished product. DuskEVM is currently running in a sequencer-only mode, with no public mempool. NPEX’s regulated securities dApp is described as an “ongoing rollout,” not yet in a full launch state. $DUSK ’s current market price is around $0.0715, and the gap between on-chain real transaction activity and the token release rate is also worth ongoing observation. I support the direction of moving from a “privacy chain” to “market infrastructure,” but the execution-layer gap is something to stay wary of.
What I’m more focused on now is: after Aegis and Boreas have sufficiently hardened the infrastructure, when will real-world assets and real transaction volume actually move in? #dusk
This isn’t a flashy narrative shift; it’s a series of engineering adjustments. The recent Boreas upgrade focuses on network resilience, resource accounting, and the readiness state of DuskEVM. In March, there’s another round of the Aegis upgrade, described by the official team as the most important update to date, with all nodes required to upgrade. Two rounds of forced upgrades without any major issues in the process in itself suggests that the network’s stability is being steadily validated. It may sound a bit dry, but for infrastructure, “dry” might actually be the point.
Dusk’s current three-layer architecture is already quite clear: the bottom layer, DuskDS, handles settlement, consensus, and data availability; the middle layer has DuskEVM running Solidity apps, while DuskVM runs Rust/WASM native contracts; the top layer, Citadel, manages identity and selective disclosure. The three layers are driven by the same DUSK token. The native bridges run by validators transfer value between layers without wrapping assets or involving custodians.
But I have to say this is still an evolving system—not a finished product. DuskEVM is currently running in a sequencer-only mode, with no public mempool. NPEX’s regulated securities dApp is described as an “ongoing rollout,” not yet in a full launch state. $DUSK ’s current market price is around $0.0715, and the gap between on-chain real transaction activity and the token release rate is also worth ongoing observation. I support the direction of moving from a “privacy chain” to “market infrastructure,” but the execution-layer gap is something to stay wary of.
What I’m more focused on now is: after Aegis and Boreas have sufficiently hardened the infrastructure, when will real-world assets and real transaction volume actually move in? #dusk
1
1
102
·
--
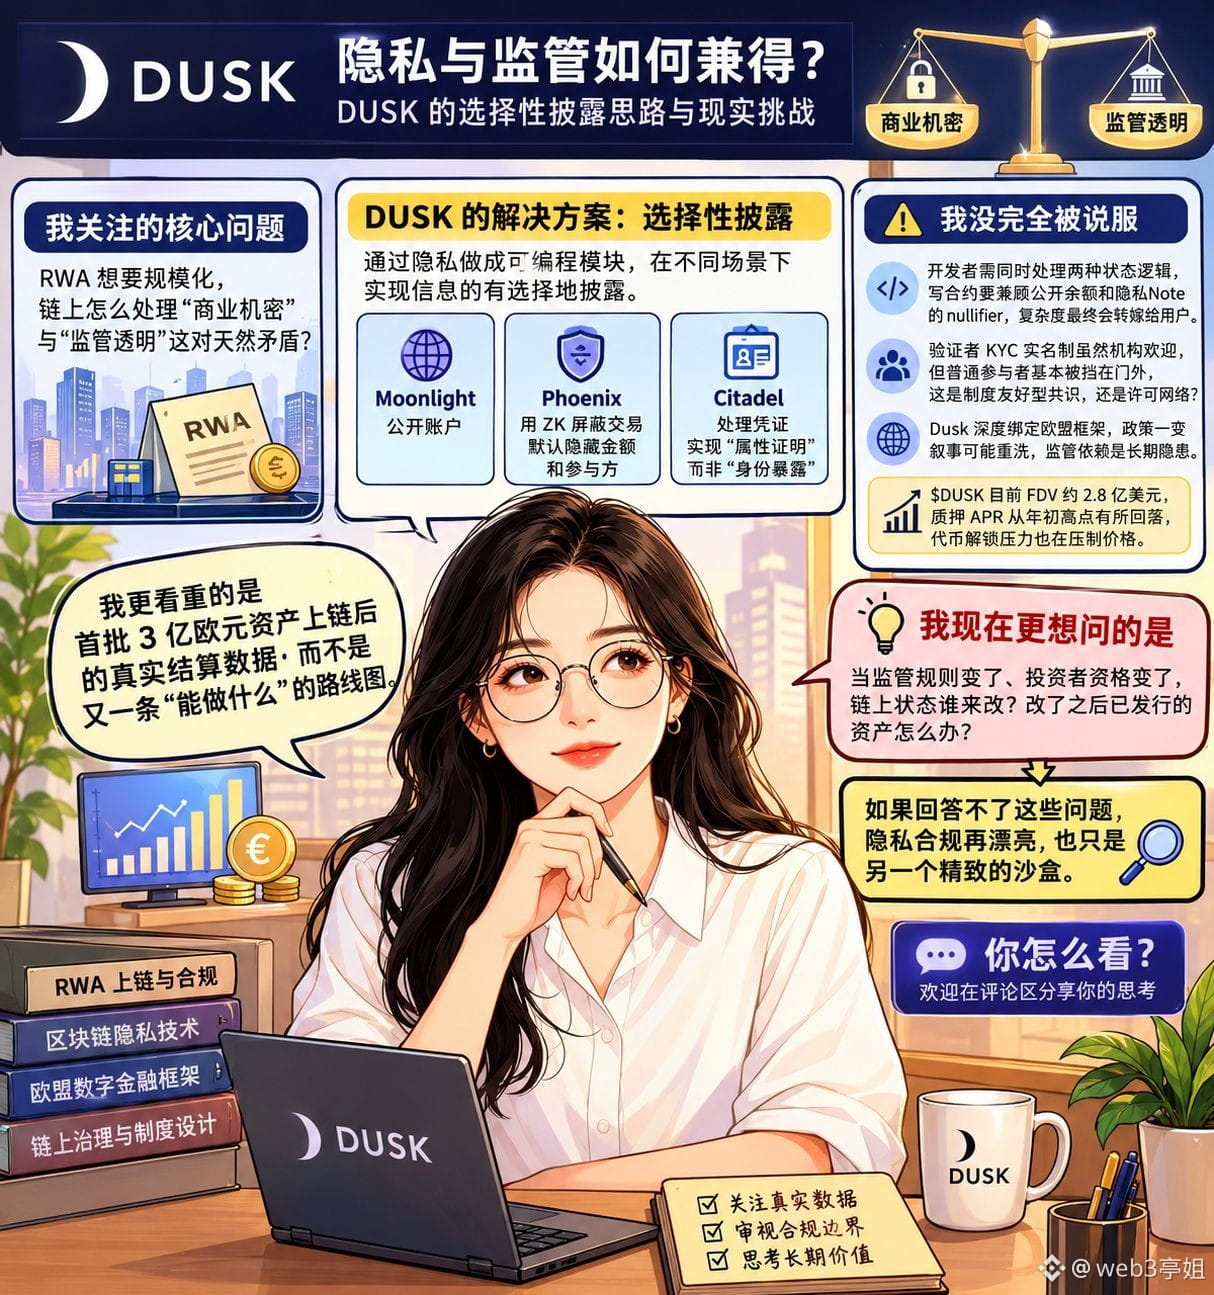
I’ve read the architecture for @Dusk_Foundation several times. What actually made me stop and think wasn’t how hardcore the zero-knowledge proofs are. What I care about is: if RWA wants to scale, how does the chain handle the “commercial secrets” versus “regulatory transparency” conflict, which is inherently irreconcilable? Most public chains are either so transparent that institutions are exposed, or so anonymous that regulators can’t get in.
Dusk’s answer is “selective disclosure.” At the underlying layer, it turns privacy into a programmable module: Moonlight manages public accounts, Phoenix uses ZK to shield transactions, and by default it hides amounts and participants. At the application layer, Citadel handles credentials to enable “attribute proofs” rather than exposing identities. This approach—deriving technical design from regulatory requirements—is worth paying attention to.
But I’m not fully convinced. A few practical issues make me hesitate: developers have to handle two kinds of state logic at once. When writing lending/borrowing contracts, they must compute both public balances and privacy Note nullifiers—complexity that will inevitably be offloaded onto users. Also, while verifier KYC and real-name compliance are welcomed by institutions, ordinary participants are basically kept out. Is this really “institution-friendly consensus,” or is it just a permissioned network wearing the public chain’s costume? There’s also the issue of regulatory dependence: Dusk is deeply tied to the EU framework, and if policies change, the narrative could be rewritten.
$DUSK currently has FDV around $280 million. The pledged APR has fallen from the peak earlier this year, and token unlock pressure is also weighing on the price.
What I care about more is the real settlement data after the first batch of €300 million in assets is on-chain—not yet another roadmap for what can be done. The threshold for RWA has never been simply moving assets onto the chain; it’s whether, after they’re moved, those troublesome rules in the real world can still keep being enforced.
So when I look at Dusk, I’m asking a more specific question: when regulatory rules change and investor eligibility changes, who updates the on-chain state? And after updating, what happens to the already issued assets? If you can’t answer that, no matter how elegant the privacy compliance is, it’s just another polished sandbox. What do you think?#dusk
I’ve read the architecture for @Dusk several times. What actually made me stop and think wasn’t how hardcore the zero-knowledge proofs are. What I care about is: if RWA wants to scale, how does the chain handle the “commercial secrets” versus “regulatory transparency” conflict, which is inherently irreconcilable? Most public chains are either so transparent that institutions are exposed, or so anonymous that regulators can’t get in.
Dusk’s answer is “selective disclosure.” At the underlying layer, it turns privacy into a programmable module: Moonlight manages public accounts, Phoenix uses ZK to shield transactions, and by default it hides amounts and participants. At the application layer, Citadel handles credentials to enable “attribute proofs” rather than exposing identities. This approach—deriving technical design from regulatory requirements—is worth paying attention to.
But I’m not fully convinced. A few practical issues make me hesitate: developers have to handle two kinds of state logic at once. When writing lending/borrowing contracts, they must compute both public balances and privacy Note nullifiers—complexity that will inevitably be offloaded onto users. Also, while verifier KYC and real-name compliance are welcomed by institutions, ordinary participants are basically kept out. Is this really “institution-friendly consensus,” or is it just a permissioned network wearing the public chain’s costume? There’s also the issue of regulatory dependence: Dusk is deeply tied to the EU framework, and if policies change, the narrative could be rewritten.
$DUSK currently has FDV around $280 million. The pledged APR has fallen from the peak earlier this year, and token unlock pressure is also weighing on the price.
What I care about more is the real settlement data after the first batch of €300 million in assets is on-chain—not yet another roadmap for what can be done. The threshold for RWA has never been simply moving assets onto the chain; it’s whether, after they’re moved, those troublesome rules in the real world can still keep being enforced.
So when I look at Dusk, I’m asking a more specific question: when regulatory rules change and investor eligibility changes, who updates the on-chain state? And after updating, what happens to the already issued assets? If you can’t answer that, no matter how elegant the privacy compliance is, it’s just another polished sandbox. What do you think?#dusk
Dusk’s answer is “selective disclosure.” At the underlying layer, it turns privacy into a programmable module: Moonlight manages public accounts, Phoenix uses ZK to shield transactions, and by default it hides amounts and participants. At the application layer, Citadel handles credentials to enable “attribute proofs” rather than exposing identities. This approach—deriving technical design from regulatory requirements—is worth paying attention to.
But I’m not fully convinced. A few practical issues make me hesitate: developers have to handle two kinds of state logic at once. When writing lending/borrowing contracts, they must compute both public balances and privacy Note nullifiers—complexity that will inevitably be offloaded onto users. Also, while verifier KYC and real-name compliance are welcomed by institutions, ordinary participants are basically kept out. Is this really “institution-friendly consensus,” or is it just a permissioned network wearing the public chain’s costume? There’s also the issue of regulatory dependence: Dusk is deeply tied to the EU framework, and if policies change, the narrative could be rewritten.
$DUSK currently has FDV around $280 million. The pledged APR has fallen from the peak earlier this year, and token unlock pressure is also weighing on the price.
What I care about more is the real settlement data after the first batch of €300 million in assets is on-chain—not yet another roadmap for what can be done. The threshold for RWA has never been simply moving assets onto the chain; it’s whether, after they’re moved, those troublesome rules in the real world can still keep being enforced.
So when I look at Dusk, I’m asking a more specific question: when regulatory rules change and investor eligibility changes, who updates the on-chain state? And after updating, what happens to the already issued assets? If you can’t answer that, no matter how elegant the privacy compliance is, it’s just another polished sandbox. What do you think?#dusk
2
1
108
·
--
I recently re-examined @Dusk_Foundation and noticed a more concrete issue than privacy transactions: how can on-chain financial assets determine whether a person meets the holding requirements without revealing their identity information to everyone?
Dusk’s Citadel gave me a clearer way of thinking. Users first obtain credentials from a License Provider, then use zero-knowledge proofs to prove that they possess valid credentials—rather than putting names, addresses, or full identity details directly on-chain. The Citadel contract verifies the proof; whether a specific service accepts these credentials is determined by the Service Provider according to its own rules.
I agree with this layered approach. It separates “proving eligibility” from “publicly stating who you are.” For regulated assets such as securities, investor eligibility, regional restrictions, and holding permissions don’t necessarily need to be visible to all on-chain participants in the first place.
But the problem shows up right here. Citadel can cryptographically prove that the credentials are valid, but it cannot replace market judgment about which issuers can be trusted, which attributes should be accepted, and how to handle things once credentials expire or are revoked. Official specifications also leave choices about whom to trust as the License Provider, attribute acceptance, and session management to the specific service provider. In other words, cryptography reduces the need for trust during verification, but it does not eliminate the trust entry points in the identity system.
Now look at $DUSK . It provides gas and staking functions, with a maximum supply of 1 billion tokens, and some of the tokens are released through long-term emissions. What I care about isn’t just short-term price fluctuations, but whether, as real business volume grows in the future, network transaction fees and staking demand can form more sustained usage demand.
So for me, when looking at Dusk, privacy technology is only the first gate. What truly determines whether it can enter more financial scenarios is who issues trustworthy identities and whether different institutions are willing to accept the same set of proof standards. Technical rules can be written into protocols, but identity trust is hard to solve with code alone. I think this problem is even more worth long-term observation than TPS. #dusk
I recently re-examined @Dusk and noticed a more concrete issue than privacy transactions: how can on-chain financial assets determine whether a person meets the holding requirements without revealing their identity information to everyone?
Dusk’s Citadel gave me a clearer way of thinking. Users first obtain credentials from a License Provider, then use zero-knowledge proofs to prove that they possess valid credentials—rather than putting names, addresses, or full identity details directly on-chain. The Citadel contract verifies the proof; whether a specific service accepts these credentials is determined by the Service Provider according to its own rules.
I agree with this layered approach. It separates “proving eligibility” from “publicly stating who you are.” For regulated assets such as securities, investor eligibility, regional restrictions, and holding permissions don’t necessarily need to be visible to all on-chain participants in the first place.
But the problem shows up right here. Citadel can cryptographically prove that the credentials are valid, but it cannot replace market judgment about which issuers can be trusted, which attributes should be accepted, and how to handle things once credentials expire or are revoked. Official specifications also leave choices about whom to trust as the License Provider, attribute acceptance, and session management to the specific service provider. In other words, cryptography reduces the need for trust during verification, but it does not eliminate the trust entry points in the identity system.
Now look at $DUSK . It provides gas and staking functions, with a maximum supply of 1 billion tokens, and some of the tokens are released through long-term emissions. What I care about isn’t just short-term price fluctuations, but whether, as real business volume grows in the future, network transaction fees and staking demand can form more sustained usage demand.
So for me, when looking at Dusk, privacy technology is only the first gate. What truly determines whether it can enter more financial scenarios is who issues trustworthy identities and whether different institutions are willing to accept the same set of proof standards. Technical rules can be written into protocols, but identity trust is hard to solve with code alone. I think this problem is even more worth long-term observation than TPS. #dusk
Dusk’s Citadel gave me a clearer way of thinking. Users first obtain credentials from a License Provider, then use zero-knowledge proofs to prove that they possess valid credentials—rather than putting names, addresses, or full identity details directly on-chain. The Citadel contract verifies the proof; whether a specific service accepts these credentials is determined by the Service Provider according to its own rules.
I agree with this layered approach. It separates “proving eligibility” from “publicly stating who you are.” For regulated assets such as securities, investor eligibility, regional restrictions, and holding permissions don’t necessarily need to be visible to all on-chain participants in the first place.
But the problem shows up right here. Citadel can cryptographically prove that the credentials are valid, but it cannot replace market judgment about which issuers can be trusted, which attributes should be accepted, and how to handle things once credentials expire or are revoked. Official specifications also leave choices about whom to trust as the License Provider, attribute acceptance, and session management to the specific service provider. In other words, cryptography reduces the need for trust during verification, but it does not eliminate the trust entry points in the identity system.
Now look at $DUSK . It provides gas and staking functions, with a maximum supply of 1 billion tokens, and some of the tokens are released through long-term emissions. What I care about isn’t just short-term price fluctuations, but whether, as real business volume grows in the future, network transaction fees and staking demand can form more sustained usage demand.
So for me, when looking at Dusk, privacy technology is only the first gate. What truly determines whether it can enter more financial scenarios is who issues trustworthy identities and whether different institutions are willing to accept the same set of proof standards. Technical rules can be written into protocols, but identity trust is hard to solve with code alone. I think this problem is even more worth long-term observation than TPS. #dusk
1
2
95
·
--
When I re-examined @Dusk_Foundation , what really made me stop wasn’t privacy technology—but a more realistic question: once assets like securities are put on-chain, can investor eligibility, transfer restrictions, and information disclosure be directly turned into rules on the blockchain?
Dusk’s Phoenix model gave me an interesting answer. Transactions can hide counterparties and amounts, while enabling targeted disclosure via viewing keys. For financial assets, this is more practical than simply chasing “nobody can see.” Regulators often don’t need all the data; they need to verify specific data under specific conditions. Moonlight keeps the public-account model, and DuskDS handles the underlying settlement. The two modes can serve different businesses.
But I also think the biggest advantage of this design—and the potential ecosystem hurdle—may be right there. DuskVM is built for Rust and WASM, making it well-suited for native privacy and zero-knowledge applications. DuskEVM is compatible with Solidity and existing EVM tooling. More choices don’t necessarily mean easier development. If teams ultimately rely mainly on EVM, the technical differences in Dusk itself could be weakened. A more realistic concern is that the computational cost of zero-knowledge proofs, as well as the hardware-resource requirements for provers, will also become engineering problems that must be solved for large-scale adoption.
On the token layer, I care more about the actual usage needs of $DUSK than about looking at the supply in isolation. As a network-native asset, DUSK is directly tied to network functions like transaction fees and staking. That means how much value it can ultimately carry depends—largely—on whether the network continues to add real activity over time. The official supply design uses a long-term release mechanism, with a total cap of 1 billion tokens. For me, this set of numbers isn’t the point in itself. What’s truly worth watching is whether future network usage can match the functional needs of the token.
Now looking at Dusk again, what I care about most is whether it can truly embed privacy, identity, and asset rules into the everyday workflows of financial business. Technical capability answers “can we do it,” but real adoption answers “do we even need to do it.” For Dusk, what’s probably most worth watching next isn’t how many more technical modules get added, but whether more and more real assets are willing to stay. #dusk
When I re-examined @Dusk , what really made me stop wasn’t privacy technology—but a more realistic question: once assets like securities are put on-chain, can investor eligibility, transfer restrictions, and information disclosure be directly turned into rules on the blockchain?
Dusk’s Phoenix model gave me an interesting answer. Transactions can hide counterparties and amounts, while enabling targeted disclosure via viewing keys. For financial assets, this is more practical than simply chasing “nobody can see.” Regulators often don’t need all the data; they need to verify specific data under specific conditions. Moonlight keeps the public-account model, and DuskDS handles the underlying settlement. The two modes can serve different businesses.
But I also think the biggest advantage of this design—and the potential ecosystem hurdle—may be right there. DuskVM is built for Rust and WASM, making it well-suited for native privacy and zero-knowledge applications. DuskEVM is compatible with Solidity and existing EVM tooling. More choices don’t necessarily mean easier development. If teams ultimately rely mainly on EVM, the technical differences in Dusk itself could be weakened. A more realistic concern is that the computational cost of zero-knowledge proofs, as well as the hardware-resource requirements for provers, will also become engineering problems that must be solved for large-scale adoption.
On the token layer, I care more about the actual usage needs of $DUSK than about looking at the supply in isolation. As a network-native asset, DUSK is directly tied to network functions like transaction fees and staking. That means how much value it can ultimately carry depends—largely—on whether the network continues to add real activity over time. The official supply design uses a long-term release mechanism, with a total cap of 1 billion tokens. For me, this set of numbers isn’t the point in itself. What’s truly worth watching is whether future network usage can match the functional needs of the token.
Now looking at Dusk again, what I care about most is whether it can truly embed privacy, identity, and asset rules into the everyday workflows of financial business. Technical capability answers “can we do it,” but real adoption answers “do we even need to do it.” For Dusk, what’s probably most worth watching next isn’t how many more technical modules get added, but whether more and more real assets are willing to stay. #dusk
Dusk’s Phoenix model gave me an interesting answer. Transactions can hide counterparties and amounts, while enabling targeted disclosure via viewing keys. For financial assets, this is more practical than simply chasing “nobody can see.” Regulators often don’t need all the data; they need to verify specific data under specific conditions. Moonlight keeps the public-account model, and DuskDS handles the underlying settlement. The two modes can serve different businesses.
But I also think the biggest advantage of this design—and the potential ecosystem hurdle—may be right there. DuskVM is built for Rust and WASM, making it well-suited for native privacy and zero-knowledge applications. DuskEVM is compatible with Solidity and existing EVM tooling. More choices don’t necessarily mean easier development. If teams ultimately rely mainly on EVM, the technical differences in Dusk itself could be weakened. A more realistic concern is that the computational cost of zero-knowledge proofs, as well as the hardware-resource requirements for provers, will also become engineering problems that must be solved for large-scale adoption.
On the token layer, I care more about the actual usage needs of $DUSK than about looking at the supply in isolation. As a network-native asset, DUSK is directly tied to network functions like transaction fees and staking. That means how much value it can ultimately carry depends—largely—on whether the network continues to add real activity over time. The official supply design uses a long-term release mechanism, with a total cap of 1 billion tokens. For me, this set of numbers isn’t the point in itself. What’s truly worth watching is whether future network usage can match the functional needs of the token.
Now looking at Dusk again, what I care about most is whether it can truly embed privacy, identity, and asset rules into the everyday workflows of financial business. Technical capability answers “can we do it,” but real adoption answers “do we even need to do it.” For Dusk, what’s probably most worth watching next isn’t how many more technical modules get added, but whether more and more real assets are willing to stay. #dusk
86
·
--
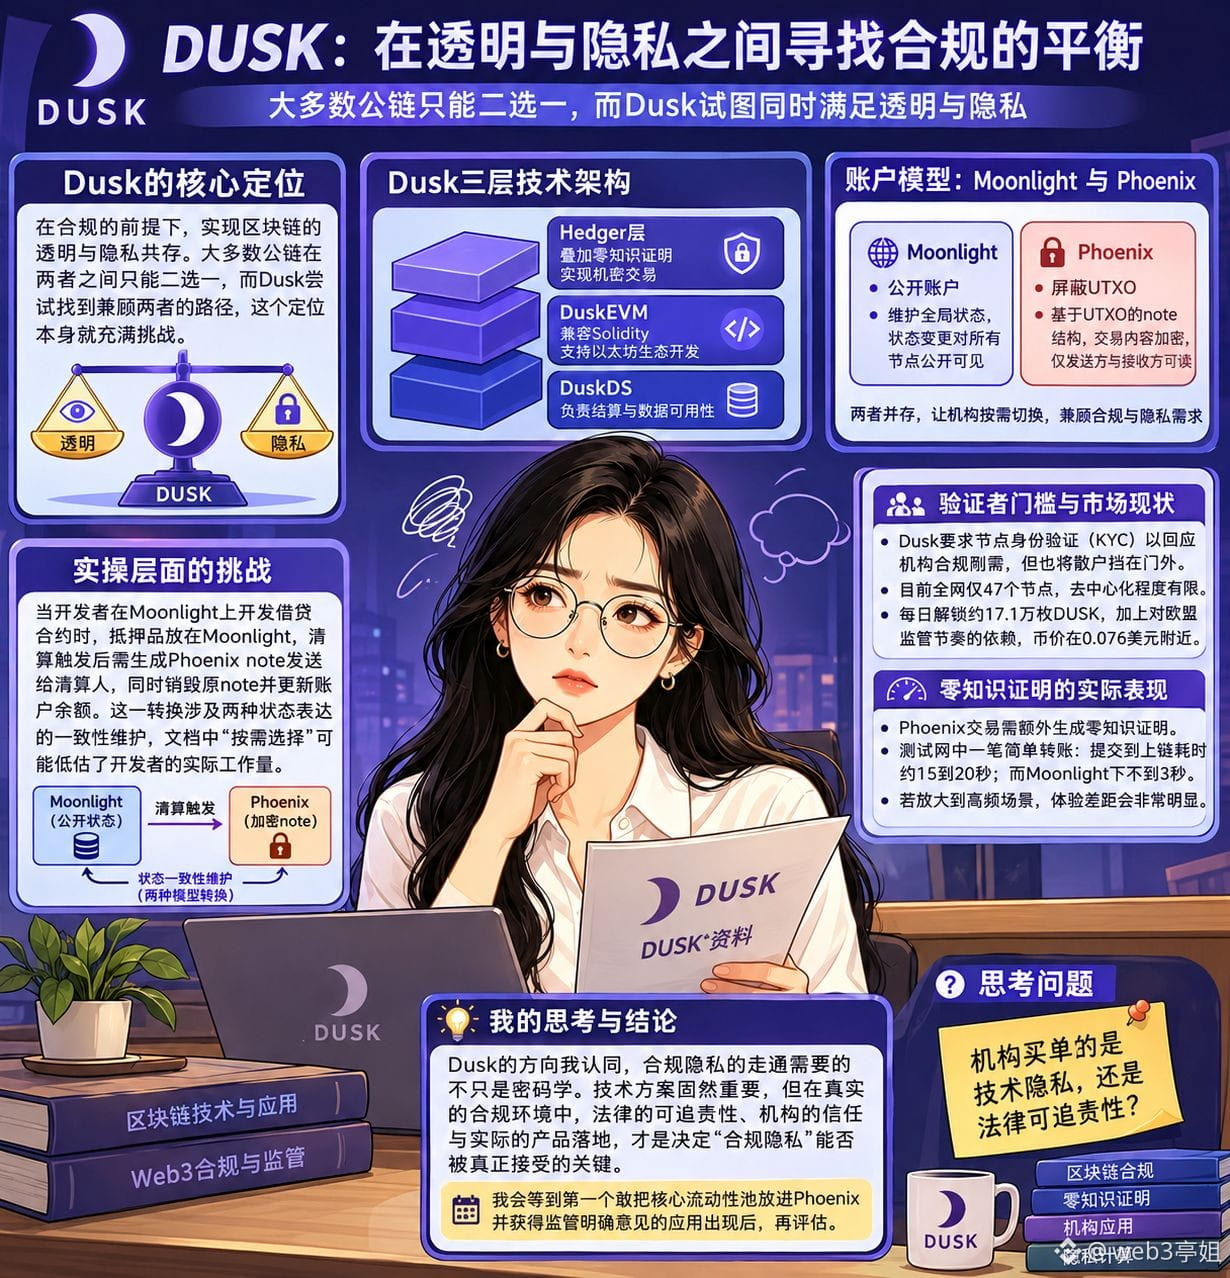
Revisiting Dusk’s materials, what concerns me is how it handles the inherent contradiction between “compliant privacy.” Most public chains force a choice between transparency and privacy, while Dusk tries to satisfy both simultaneously. That positioning in itself is quite conflicted.
From a technical architecture standpoint, the three-layer design (@Dusk_Foundation ) has standout elements: DuskDS handles settlement and data availability, DuskEVM is compatible with Solidity, and a Hedger layer stacked with zero-knowledge proofs enables confidential transactions. Having Moonlight’s public accounts coexist with Phoenix’s UTXO shielding lets institutions switch as needed. Market capitalization for $DUSK is about $28 million, with a total supply of 500 million coins; it serves functions including gas, staking, and governance.
But when I get into the real-world implementation, I start to feel uneasy. Moonlight’s account model maintains global state—state changes are publicly visible to all nodes. Phoenix, in contrast, uses a UTXO-based note structure: each transaction consumes an old note and generates a new one. The note contents are encrypted and readable only by the sender and the recipient. When developers write a lending contract, collateral sits in Moonlight. After liquidation is triggered, the system must generate a Phoenix note to send to the liquidator, then destroy the original note and update account balances. This conversion logic involves maintaining consistency between two different forms of state representation. The line in the documentation about “choosing as needed” may underestimate the actual workload for developers.
The KYC barrier for validators is another issue. Dusk requires node identity verification, which addresses institutions’ compliance needs, but keeps retail users out—right now the entire network has only 47 nodes. Approximately 171,000 DUSK are unlocked per day, and coupled with reliance on the EU regulatory timetable, the coin price hovers around $0.076. What worries me most, though, is the real-world performance of zero-knowledge proofs in the WASM environment. Each Phoenix transaction needs additional proof generation. In my tests on the testnet, a simple transfer took about 15 to 20 seconds from submission to being included on-chain, whereas under Moonlight it took under 3 seconds. If that gap is magnified in high-frequency scenarios, the user experience will be clearly affected.
I agree with Dusk’s direction, but getting “compliant privacy” to work requires more than cryptography. I’ll wait until the first application that puts the core liquidity pool into Phoenix and obtains clear regulatory guidance, then I’ll reassess. Do you think institutions are paying for technical privacy or for legally attributable accountability? #dusk
Revisiting Dusk’s materials, what concerns me is how it handles the inherent contradiction between “compliant privacy.” Most public chains force a choice between transparency and privacy, while Dusk tries to satisfy both simultaneously. That positioning in itself is quite conflicted.
From a technical architecture standpoint, the three-layer design (@Dusk ) has standout elements: DuskDS handles settlement and data availability, DuskEVM is compatible with Solidity, and a Hedger layer stacked with zero-knowledge proofs enables confidential transactions. Having Moonlight’s public accounts coexist with Phoenix’s UTXO shielding lets institutions switch as needed. Market capitalization for $DUSK is about $28 million, with a total supply of 500 million coins; it serves functions including gas, staking, and governance.
But when I get into the real-world implementation, I start to feel uneasy. Moonlight’s account model maintains global state—state changes are publicly visible to all nodes. Phoenix, in contrast, uses a UTXO-based note structure: each transaction consumes an old note and generates a new one. The note contents are encrypted and readable only by the sender and the recipient. When developers write a lending contract, collateral sits in Moonlight. After liquidation is triggered, the system must generate a Phoenix note to send to the liquidator, then destroy the original note and update account balances. This conversion logic involves maintaining consistency between two different forms of state representation. The line in the documentation about “choosing as needed” may underestimate the actual workload for developers.
The KYC barrier for validators is another issue. Dusk requires node identity verification, which addresses institutions’ compliance needs, but keeps retail users out—right now the entire network has only 47 nodes. Approximately 171,000 DUSK are unlocked per day, and coupled with reliance on the EU regulatory timetable, the coin price hovers around $0.076. What worries me most, though, is the real-world performance of zero-knowledge proofs in the WASM environment. Each Phoenix transaction needs additional proof generation. In my tests on the testnet, a simple transfer took about 15 to 20 seconds from submission to being included on-chain, whereas under Moonlight it took under 3 seconds. If that gap is magnified in high-frequency scenarios, the user experience will be clearly affected.
I agree with Dusk’s direction, but getting “compliant privacy” to work requires more than cryptography. I’ll wait until the first application that puts the core liquidity pool into Phoenix and obtains clear regulatory guidance, then I’ll reassess. Do you think institutions are paying for technical privacy or for legally attributable accountability? #dusk
From a technical architecture standpoint, the three-layer design (@Dusk ) has standout elements: DuskDS handles settlement and data availability, DuskEVM is compatible with Solidity, and a Hedger layer stacked with zero-knowledge proofs enables confidential transactions. Having Moonlight’s public accounts coexist with Phoenix’s UTXO shielding lets institutions switch as needed. Market capitalization for $DUSK is about $28 million, with a total supply of 500 million coins; it serves functions including gas, staking, and governance.
But when I get into the real-world implementation, I start to feel uneasy. Moonlight’s account model maintains global state—state changes are publicly visible to all nodes. Phoenix, in contrast, uses a UTXO-based note structure: each transaction consumes an old note and generates a new one. The note contents are encrypted and readable only by the sender and the recipient. When developers write a lending contract, collateral sits in Moonlight. After liquidation is triggered, the system must generate a Phoenix note to send to the liquidator, then destroy the original note and update account balances. This conversion logic involves maintaining consistency between two different forms of state representation. The line in the documentation about “choosing as needed” may underestimate the actual workload for developers.
The KYC barrier for validators is another issue. Dusk requires node identity verification, which addresses institutions’ compliance needs, but keeps retail users out—right now the entire network has only 47 nodes. Approximately 171,000 DUSK are unlocked per day, and coupled with reliance on the EU regulatory timetable, the coin price hovers around $0.076. What worries me most, though, is the real-world performance of zero-knowledge proofs in the WASM environment. Each Phoenix transaction needs additional proof generation. In my tests on the testnet, a simple transfer took about 15 to 20 seconds from submission to being included on-chain, whereas under Moonlight it took under 3 seconds. If that gap is magnified in high-frequency scenarios, the user experience will be clearly affected.
I agree with Dusk’s direction, but getting “compliant privacy” to work requires more than cryptography. I’ll wait until the first application that puts the core liquidity pool into Phoenix and obtains clear regulatory guidance, then I’ll reassess. Do you think institutions are paying for technical privacy or for legally attributable accountability? #dusk
2
1
117
·
--
Previously, I always felt that for a blockchain to serve traditional finance, it had to answer one question first: traders don’t want to expose their cards, while regulators need to see everything clearly. How do you resolve that contradiction? Most projects either focus too much on privacy or go fully transparent—satisfying neither side. It wasn’t until I dug into @Dusk_Foundation that I realized it splits the problem into two sets of models and connects them.
Let me start with what convinced me. Dusk preserves two account models: Phoenix and Moonlight. The former is built on UTXO and uses zero-knowledge proofs to keep both the amounts and the participating parties confidential, while the latter is fully transparent. The more I look at this, the more I agree with it. Corporate holdings and quotes must be kept secret, otherwise the counterparty can target you; but for staking and governance voting, openness is actually the foundation of trust. Forcing everything into a single model would only leave both sides dissatisfied.
What concerns me even more—in a good way—is that it doesn’t treat compliance as a slogan. EURQ, launched in collaboration with Quantoz Payments, is regulated by the Dutch central bank and complies with MiCA. This means that from asset issuance to trading and finally settlement, the entire chain can truly close the loop—more reliable than stablecoins issued by commercial companies. With DuskEVM compatibility with the Solidity toolchain, the migration cost for institutions is pushed down to a level where they can actually make a decision.
That said, there’s also a very real downside. EURQ isn’t an exclusive resource for Dusk—it’s deployed on other chains as well. How long can its differentiated advantage in compliance and settlement last? The mainnet only launched in January 2026, and it still needs time to validate the actual adoption rates of asset migration and payment services. The performance overhead of privacy computation is also significant. Can the experience of confidential transfers get close to that of ordinary transfers? That directly determines whether it will be used.
In the end, Dusk is doing the work of making privacy, compliance, and asset rules coexist long-term—treating it as engineering rather than a show. This direction is worth continuous attention. But whether real adoption can truly take off—I’m still watching as I go. What do you think? #dusk $DUSK
Previously, I always felt that for a blockchain to serve traditional finance, it had to answer one question first: traders don’t want to expose their cards, while regulators need to see everything clearly. How do you resolve that contradiction? Most projects either focus too much on privacy or go fully transparent—satisfying neither side. It wasn’t until I dug into @Dusk that I realized it splits the problem into two sets of models and connects them.
Let me start with what convinced me. Dusk preserves two account models: Phoenix and Moonlight. The former is built on UTXO and uses zero-knowledge proofs to keep both the amounts and the participating parties confidential, while the latter is fully transparent. The more I look at this, the more I agree with it. Corporate holdings and quotes must be kept secret, otherwise the counterparty can target you; but for staking and governance voting, openness is actually the foundation of trust. Forcing everything into a single model would only leave both sides dissatisfied.
What concerns me even more—in a good way—is that it doesn’t treat compliance as a slogan. EURQ, launched in collaboration with Quantoz Payments, is regulated by the Dutch central bank and complies with MiCA. This means that from asset issuance to trading and finally settlement, the entire chain can truly close the loop—more reliable than stablecoins issued by commercial companies. With DuskEVM compatibility with the Solidity toolchain, the migration cost for institutions is pushed down to a level where they can actually make a decision.
That said, there’s also a very real downside. EURQ isn’t an exclusive resource for Dusk—it’s deployed on other chains as well. How long can its differentiated advantage in compliance and settlement last? The mainnet only launched in January 2026, and it still needs time to validate the actual adoption rates of asset migration and payment services. The performance overhead of privacy computation is also significant. Can the experience of confidential transfers get close to that of ordinary transfers? That directly determines whether it will be used.
In the end, Dusk is doing the work of making privacy, compliance, and asset rules coexist long-term—treating it as engineering rather than a show. This direction is worth continuous attention. But whether real adoption can truly take off—I’m still watching as I go. What do you think? #dusk $DUSK
Let me start with what convinced me. Dusk preserves two account models: Phoenix and Moonlight. The former is built on UTXO and uses zero-knowledge proofs to keep both the amounts and the participating parties confidential, while the latter is fully transparent. The more I look at this, the more I agree with it. Corporate holdings and quotes must be kept secret, otherwise the counterparty can target you; but for staking and governance voting, openness is actually the foundation of trust. Forcing everything into a single model would only leave both sides dissatisfied.
What concerns me even more—in a good way—is that it doesn’t treat compliance as a slogan. EURQ, launched in collaboration with Quantoz Payments, is regulated by the Dutch central bank and complies with MiCA. This means that from asset issuance to trading and finally settlement, the entire chain can truly close the loop—more reliable than stablecoins issued by commercial companies. With DuskEVM compatibility with the Solidity toolchain, the migration cost for institutions is pushed down to a level where they can actually make a decision.
That said, there’s also a very real downside. EURQ isn’t an exclusive resource for Dusk—it’s deployed on other chains as well. How long can its differentiated advantage in compliance and settlement last? The mainnet only launched in January 2026, and it still needs time to validate the actual adoption rates of asset migration and payment services. The performance overhead of privacy computation is also significant. Can the experience of confidential transfers get close to that of ordinary transfers? That directly determines whether it will be used.
In the end, Dusk is doing the work of making privacy, compliance, and asset rules coexist long-term—treating it as engineering rather than a show. This direction is worth continuous attention. But whether real adoption can truly take off—I’m still watching as I go. What do you think? #dusk $DUSK
1
1
103
·
--
Choose C.
After on-chain assets are stolen, the so-called “asset-recovery experts” are in most cases a second scam. Blocking them immediately is the safest. A real technical team that can actually recover funds would not proactively direct-message you, nor would they charge you first. It’s better to miss out than to take risks—protecting the remaining assets matters more than fantasizing about recovery.
Choose C.
After on-chain assets are stolen, the so-called “asset-recovery experts” are in most cases a second scam. Blocking them immediately is the safest. A real technical team that can actually recover funds would not proactively direct-message you, nor would they charge you first. It’s better to miss out than to take risks—protecting the remaining assets matters more than fantasizing about recovery.
After on-chain assets are stolen, the so-called “asset-recovery experts” are in most cases a second scam. Blocking them immediately is the safest. A real technical team that can actually recover funds would not proactively direct-message you, nor would they charge you first. It’s better to miss out than to take risks—protecting the remaining assets matters more than fantasizing about recovery.
币安Binance华语
·
--
😈 “Bro, your wallet got stolen? I know some blockchain gurus—your assets can still be recovered!”
What would you do❓
A. Great, it’s a guru—my wallet’s saved. Send the seed phrase directly 🤝
B. Wait, I want to verify the card: who are you? Where are you from? How do you recover it?👀
C. ❌ Don’t trust any asset-recovery channel—block immediately!
⬇️ Follow the account, share, and leave your choice and reasons. 3 winners will be selected to receive a 40U security reward #币安安全星期四
What would you do❓
A. Great, it’s a guru—my wallet’s saved. Send the seed phrase directly 🤝
B. Wait, I want to verify the card: who are you? Where are you from? How do you recover it?👀
C. ❌ Don’t trust any asset-recovery channel—block immediately!
⬇️ Follow the account, share, and leave your choice and reasons. 3 winners will be selected to receive a 40U security reward #币安安全星期四
1
59
·
--
When I was doing fintech before, the conflict between privacy and compliance was always impossible to avoid. To protect customers’ trading data, regulators said they must be able to see it. The blockchain projects out there either go fully transparent and scare institutions away, or go fully anonymous and anger regulators. I kept wondering—can’t there be a third way?
Later I came across <a>@Dusk_Foundation </a>. What caught my attention was that it’s bold enough to rethink the whole issue from the ground up. It splits the chain into two layers: a DuskDS settlement layer and a DuskEVM execution layer—what needs to be verified is verified, what needs to be kept confidential is kept confidential, and they don’t get mixed together. Consensus uses Succinct Attestation, a committee-based PoS, with block production and validation separated, leading to finality being determined. The dual-account model is also interesting: Moonlight is transparent, while Phoenix uses UTXO plus zero-knowledge proofs to hide information. In other words, on one chain, public and confidential data go their separate ways, but in the end they all settle into the same ledger. On top of that, Citadel enables selective disclosure—users only need to prove they meet certain conditions, without exposing their entire identity.
But beyond the technology, there are a few real-world angles worth thinking through. DuskEVM is currently driven by a single sequencer, which is basically the same route as the centralized sequencer on Ethereum L2. Yes, it’s cheaper, but the sequencing switch is still in the project team’s hands. For institutions, finality may secure the ledger, but it doesn’t automatically control the sequencer. In May 2026, <a>OtterSec</a> also revealed a vulnerability in the PLONK implementation: validators didn’t verify multiple polynomial commitments provided by the prover, and in theory DUSK could be minted out of thin air. Although it was fixed afterward, vulnerabilities at that level appearing in core cryptographic modules mean you have to keep watching continuously. And then there’s the ongoing issuance and lockup pressure of token <a>$DUSK </a>.
So my current view is: Dusk’s technical direction is worth placing near the front of the “observation deck,” but in the short term I won’t enter the market just because it says the word “privacy.” Whether this “don’t offend either side” lane it’s trying to build actually has cars running—that’s the key question.
If Wall Street’s clearing and settlement system really goes on-chain, will they choose fully transparent, or something with privacy graded in layers like this? Feel free to leave a comment and discuss. <a>#dusk </a>
When I was doing fintech before, the conflict between privacy and compliance was always impossible to avoid. To protect customers’ trading data, regulators said they must be able to see it. The blockchain projects out there either go fully transparent and scare institutions away, or go fully anonymous and anger regulators. I kept wondering—can’t there be a third way?
Later I came across <a>@Dusk </a>. What caught my attention was that it’s bold enough to rethink the whole issue from the ground up. It splits the chain into two layers: a DuskDS settlement layer and a DuskEVM execution layer—what needs to be verified is verified, what needs to be kept confidential is kept confidential, and they don’t get mixed together. Consensus uses Succinct Attestation, a committee-based PoS, with block production and validation separated, leading to finality being determined. The dual-account model is also interesting: Moonlight is transparent, while Phoenix uses UTXO plus zero-knowledge proofs to hide information. In other words, on one chain, public and confidential data go their separate ways, but in the end they all settle into the same ledger. On top of that, Citadel enables selective disclosure—users only need to prove they meet certain conditions, without exposing their entire identity.
But beyond the technology, there are a few real-world angles worth thinking through. DuskEVM is currently driven by a single sequencer, which is basically the same route as the centralized sequencer on Ethereum L2. Yes, it’s cheaper, but the sequencing switch is still in the project team’s hands. For institutions, finality may secure the ledger, but it doesn’t automatically control the sequencer. In May 2026, <a>OtterSec</a> also revealed a vulnerability in the PLONK implementation: validators didn’t verify multiple polynomial commitments provided by the prover, and in theory DUSK could be minted out of thin air. Although it was fixed afterward, vulnerabilities at that level appearing in core cryptographic modules mean you have to keep watching continuously. And then there’s the ongoing issuance and lockup pressure of token <a>$DUSK </a>.
So my current view is: Dusk’s technical direction is worth placing near the front of the “observation deck,” but in the short term I won’t enter the market just because it says the word “privacy.” Whether this “don’t offend either side” lane it’s trying to build actually has cars running—that’s the key question.
If Wall Street’s clearing and settlement system really goes on-chain, will they choose fully transparent, or something with privacy graded in layers like this? Feel free to leave a comment and discuss. <a>#dusk </a>
Later I came across <a>@Dusk </a>. What caught my attention was that it’s bold enough to rethink the whole issue from the ground up. It splits the chain into two layers: a DuskDS settlement layer and a DuskEVM execution layer—what needs to be verified is verified, what needs to be kept confidential is kept confidential, and they don’t get mixed together. Consensus uses Succinct Attestation, a committee-based PoS, with block production and validation separated, leading to finality being determined. The dual-account model is also interesting: Moonlight is transparent, while Phoenix uses UTXO plus zero-knowledge proofs to hide information. In other words, on one chain, public and confidential data go their separate ways, but in the end they all settle into the same ledger. On top of that, Citadel enables selective disclosure—users only need to prove they meet certain conditions, without exposing their entire identity.
But beyond the technology, there are a few real-world angles worth thinking through. DuskEVM is currently driven by a single sequencer, which is basically the same route as the centralized sequencer on Ethereum L2. Yes, it’s cheaper, but the sequencing switch is still in the project team’s hands. For institutions, finality may secure the ledger, but it doesn’t automatically control the sequencer. In May 2026, <a>OtterSec</a> also revealed a vulnerability in the PLONK implementation: validators didn’t verify multiple polynomial commitments provided by the prover, and in theory DUSK could be minted out of thin air. Although it was fixed afterward, vulnerabilities at that level appearing in core cryptographic modules mean you have to keep watching continuously. And then there’s the ongoing issuance and lockup pressure of token <a>$DUSK </a>.
So my current view is: Dusk’s technical direction is worth placing near the front of the “observation deck,” but in the short term I won’t enter the market just because it says the word “privacy.” Whether this “don’t offend either side” lane it’s trying to build actually has cars running—that’s the key question.
If Wall Street’s clearing and settlement system really goes on-chain, will they choose fully transparent, or something with privacy graded in layers like this? Feel free to leave a comment and discuss. <a>#dusk </a>
1
1
97
·
--
When I entered the industry, the most fascinating part of blockchain to me was transparency. Until I talked with a friend who does asset management—he said: In your industry, all transactions are laid bare under the sun. How can institutions get in? Holdings and strategies are fully exposed, essentially letting your opponents flip your cards anytime. Since then, I’ve had doubts about “full transparency.”
So when looking at Dusk, what I care most about is how it handles “auditable privacy.” DuskDS and the layered DuskEVM architecture separate settlement from execution. With Moonlight and Phoenix operating in dual modes, public and private can be switched as needed. Collaborating with NPEX to put tokenized securities worth 300 million euros on-chain, plus EVM compatibility that attracts Solidity developers—none of this is just talk. @Dusk_Foundation
But the position of token $DUSK makes me spend even more time thinking. It’s not only for paying gas: staking 100,000 can increase your share of transaction fees by 1.2x; over 500,000 comes with ecosystem subsidies. Each block releases 19.86 tokens, with 80% going to block producers. The protocol uses real revenue to buy back and inject liquidity—effectively like a disguised burn. This design truly embeds the token into the network’s operating logic.
But I also have some uneasy points. In January 2026’s bridge incident, the attacker stole the signing wallet permissions, resulting in millions of DUSK being stolen. Later, OtterSec found a serious implementation vulnerability in PLONK zero-knowledge proofs. And who ultimately controls that “special key” that can unlock all privacy? If it can’t be clearly explained, then the boundary between “auditable” and “inspectable” becomes blurry.
My view is that the direction is worth paying attention to—its token economics have structure—but the mainnet still needs time to validate with real-world adoption data. Do you think these risks can be resolved through subsequent fixes? #dusk
When I entered the industry, the most fascinating part of blockchain to me was transparency. Until I talked with a friend who does asset management—he said: In your industry, all transactions are laid bare under the sun. How can institutions get in? Holdings and strategies are fully exposed, essentially letting your opponents flip your cards anytime. Since then, I’ve had doubts about “full transparency.”
So when looking at Dusk, what I care most about is how it handles “auditable privacy.” DuskDS and the layered DuskEVM architecture separate settlement from execution. With Moonlight and Phoenix operating in dual modes, public and private can be switched as needed. Collaborating with NPEX to put tokenized securities worth 300 million euros on-chain, plus EVM compatibility that attracts Solidity developers—none of this is just talk. @Dusk
But the position of token $DUSK makes me spend even more time thinking. It’s not only for paying gas: staking 100,000 can increase your share of transaction fees by 1.2x; over 500,000 comes with ecosystem subsidies. Each block releases 19.86 tokens, with 80% going to block producers. The protocol uses real revenue to buy back and inject liquidity—effectively like a disguised burn. This design truly embeds the token into the network’s operating logic.
But I also have some uneasy points. In January 2026’s bridge incident, the attacker stole the signing wallet permissions, resulting in millions of DUSK being stolen. Later, OtterSec found a serious implementation vulnerability in PLONK zero-knowledge proofs. And who ultimately controls that “special key” that can unlock all privacy? If it can’t be clearly explained, then the boundary between “auditable” and “inspectable” becomes blurry.
My view is that the direction is worth paying attention to—its token economics have structure—but the mainnet still needs time to validate with real-world adoption data. Do you think these risks can be resolved through subsequent fixes? #dusk
So when looking at Dusk, what I care most about is how it handles “auditable privacy.” DuskDS and the layered DuskEVM architecture separate settlement from execution. With Moonlight and Phoenix operating in dual modes, public and private can be switched as needed. Collaborating with NPEX to put tokenized securities worth 300 million euros on-chain, plus EVM compatibility that attracts Solidity developers—none of this is just talk. @Dusk
But the position of token $DUSK makes me spend even more time thinking. It’s not only for paying gas: staking 100,000 can increase your share of transaction fees by 1.2x; over 500,000 comes with ecosystem subsidies. Each block releases 19.86 tokens, with 80% going to block producers. The protocol uses real revenue to buy back and inject liquidity—effectively like a disguised burn. This design truly embeds the token into the network’s operating logic.
But I also have some uneasy points. In January 2026’s bridge incident, the attacker stole the signing wallet permissions, resulting in millions of DUSK being stolen. Later, OtterSec found a serious implementation vulnerability in PLONK zero-knowledge proofs. And who ultimately controls that “special key” that can unlock all privacy? If it can’t be clearly explained, then the boundary between “auditable” and “inspectable” becomes blurry.
My view is that the direction is worth paying attention to—its token economics have structure—but the mainnet still needs time to validate with real-world adoption data. Do you think these risks can be resolved through subsequent fixes? #dusk
2
1
80
·
--
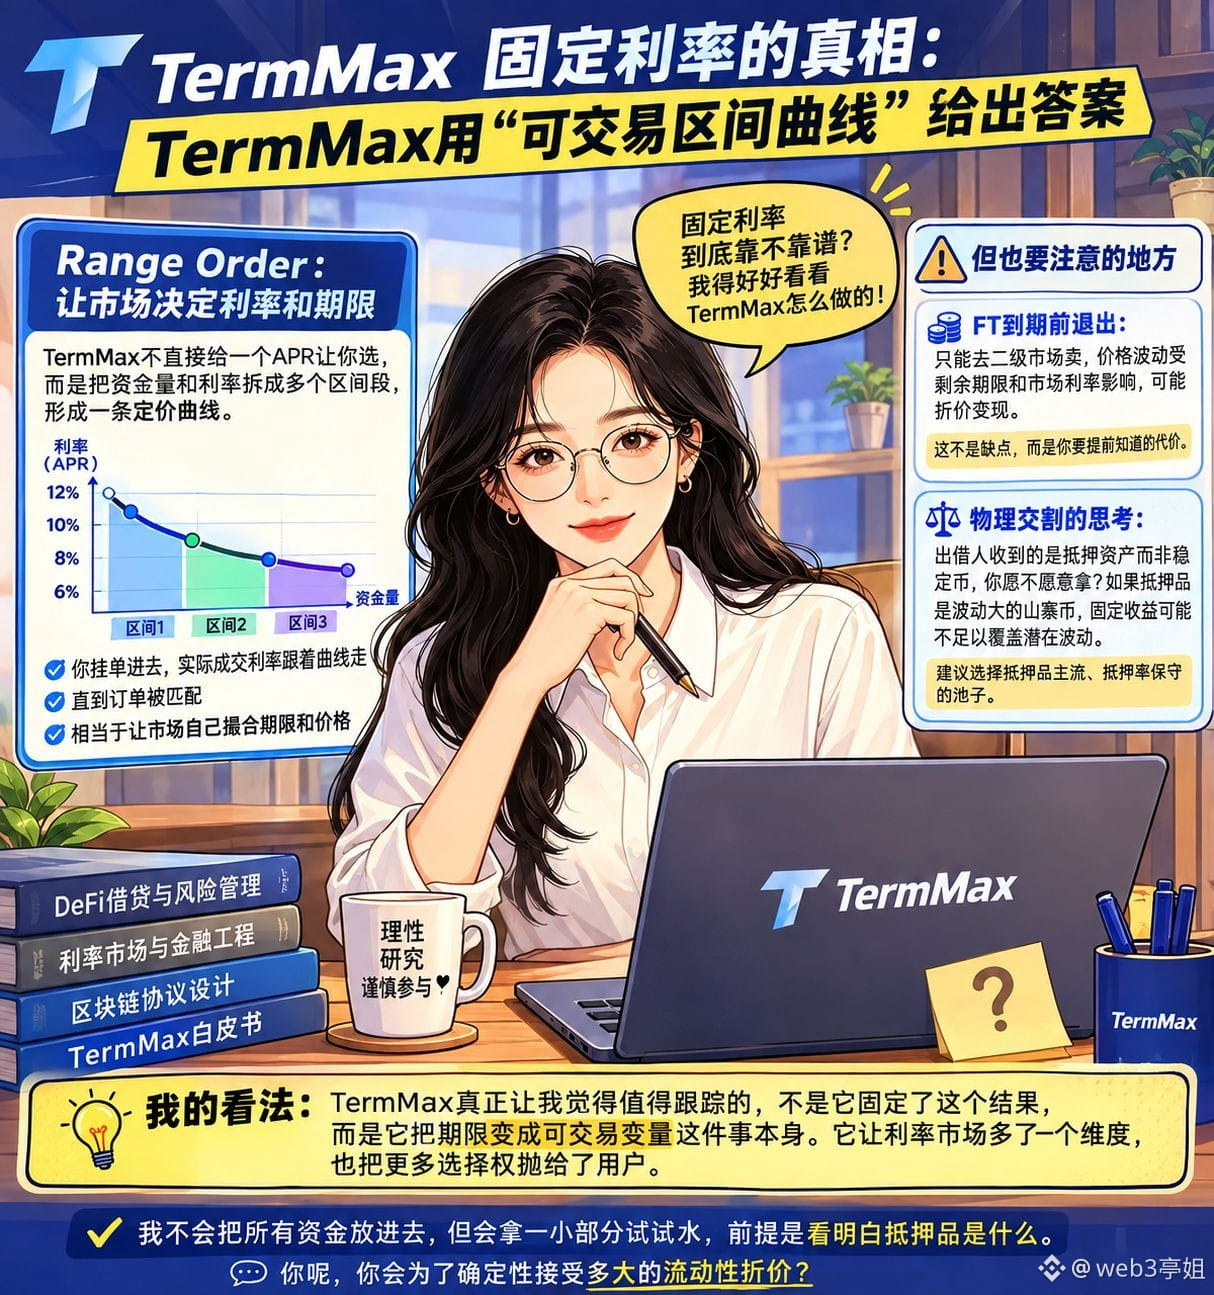
I’ve participated in several agreements that were advertised as fixed-rate, only to find that the underlying was still a floating pool wrapped in a shell, and the yield at maturity simply couldn’t be locked in. After a few times when the actual rate failed to stay fixed, I became very particular about those two words, “fixed rate.”
So when I looked at TermMax, the first thing I checked was how it ensures the rate can truly be fixed. The Range Order struck me as interesting: instead of giving you an APR to choose from, it splits the funding amount and the interest rate into multiple bands, forming a pricing curve. When you place an order, the actual execution rate follows the curve until the order is matched. This design is essentially letting the market match maturity and price by itself, rather than the protocol arbitrarily setting a number. @termmax
But to be honest, I also noticed one thing. If you want to exit FT before maturity, you can only sell on the secondary market. Price fluctuations are affected by the remaining term and market interest rates, which means the fixed return you locked in may be sold at a discount if you cash out early. That’s not really a flaw; it’s a cost you need to understand in advance.
Another thing I kept thinking about is liquidation. Physical delivery sounds more elegant than a centralized sell-off, but if what you receive as a lender is collateral assets rather than stablecoins, would you actually want to hold them? If the collateral is a highly volatile altcoin, that fixed yield may not be enough to cover the potential volatility. So personally, I would lean toward pools with mainstream collateral and conservative loan-to-value ratios.
What really makes TermMax worth following to me is not that it fixes the outcome, but that it turns maturity itself into a tradable variable. It gives the interest-rate market another dimension, while also giving users more choices.
I wouldn’t put all my funds into it, but I would be willing to test it with a small portion, as long as I clearly understand what the collateral is.
What about you—how much liquidity discount would you accept in exchange for certainty?#termmax
I’ve participated in several agreements that were advertised as fixed-rate, only to find that the underlying was still a floating pool wrapped in a shell, and the yield at maturity simply couldn’t be locked in. After a few times when the actual rate failed to stay fixed, I became very particular about those two words, “fixed rate.”
So when I looked at TermMax, the first thing I checked was how it ensures the rate can truly be fixed. The Range Order struck me as interesting: instead of giving you an APR to choose from, it splits the funding amount and the interest rate into multiple bands, forming a pricing curve. When you place an order, the actual execution rate follows the curve until the order is matched. This design is essentially letting the market match maturity and price by itself, rather than the protocol arbitrarily setting a number. @TermMax
But to be honest, I also noticed one thing. If you want to exit FT before maturity, you can only sell on the secondary market. Price fluctuations are affected by the remaining term and market interest rates, which means the fixed return you locked in may be sold at a discount if you cash out early. That’s not really a flaw; it’s a cost you need to understand in advance.
Another thing I kept thinking about is liquidation. Physical delivery sounds more elegant than a centralized sell-off, but if what you receive as a lender is collateral assets rather than stablecoins, would you actually want to hold them? If the collateral is a highly volatile altcoin, that fixed yield may not be enough to cover the potential volatility. So personally, I would lean toward pools with mainstream collateral and conservative loan-to-value ratios.
What really makes TermMax worth following to me is not that it fixes the outcome, but that it turns maturity itself into a tradable variable. It gives the interest-rate market another dimension, while also giving users more choices.
I wouldn’t put all my funds into it, but I would be willing to test it with a small portion, as long as I clearly understand what the collateral is.
What about you—how much liquidity discount would you accept in exchange for certainty?#termmax
So when I looked at TermMax, the first thing I checked was how it ensures the rate can truly be fixed. The Range Order struck me as interesting: instead of giving you an APR to choose from, it splits the funding amount and the interest rate into multiple bands, forming a pricing curve. When you place an order, the actual execution rate follows the curve until the order is matched. This design is essentially letting the market match maturity and price by itself, rather than the protocol arbitrarily setting a number. @TermMax
But to be honest, I also noticed one thing. If you want to exit FT before maturity, you can only sell on the secondary market. Price fluctuations are affected by the remaining term and market interest rates, which means the fixed return you locked in may be sold at a discount if you cash out early. That’s not really a flaw; it’s a cost you need to understand in advance.
Another thing I kept thinking about is liquidation. Physical delivery sounds more elegant than a centralized sell-off, but if what you receive as a lender is collateral assets rather than stablecoins, would you actually want to hold them? If the collateral is a highly volatile altcoin, that fixed yield may not be enough to cover the potential volatility. So personally, I would lean toward pools with mainstream collateral and conservative loan-to-value ratios.
What really makes TermMax worth following to me is not that it fixes the outcome, but that it turns maturity itself into a tradable variable. It gives the interest-rate market another dimension, while also giving users more choices.
I wouldn’t put all my funds into it, but I would be willing to test it with a small portion, as long as I clearly understand what the collateral is.
What about you—how much liquidity discount would you accept in exchange for certainty?#termmax
2
1
117
·
--
After working in compliance-oriented finance for a few years, my biggest confusion is this: why is it that assets on the blockchain can never flow like traditional securities—always both publicly auditable and strictly secret about transaction details? Transparency and privacy always seem like an either-or question.
Until I came across @Dusk_Foundation . It doesn’t treat privacy as a plug-in feature—it’s embedded directly into the L1’s underlying logic.
Pros: Through Confidential Smart Contracts and the XSC standard, it provides a compliance-and-privacy-parallel framework tailored for securities-type assets. On-chain verification focuses on the correctness of state transitions, not exposing transaction amounts and identities. This made me feel like it’s genuinely answering the thorny question: “Once real-world assets are tokenized on-chain, how do we handle compliance?”
Cons: This kind of deep privacy-bound architecture also drives complexity up sharply. It separates the execution layer from the settlement layer: the base layer handles consensus and settlement, while the upper layer is compatible with EVM. The modular design lowers the development barrier, but it also introduces risks for cross-layer asset transfers. In the past, vulnerabilities created by cross-layer design were far more than what existed in smart contracts themselves.
What I care about more is consistency in the privacy assumptions. If the execution layer is transparent, and the settlement layer has confidentiality capabilities, then an asset’s privacy properties depend on which layer it’s at right now. For users and auditors, this split creates extremely high explanation costs. Vaguely marketing it as “everything is supported” at the end will likely mean neither side is truly good enough.
The DUSK project put thought into its node design, but a node system and “true decentralization” are two different things. The staking rewards for $DUSK depend on your share of the staking pool across the entire network; large holders naturally have an advantage. On top of that, there’s a soft-penalty mechanism: if a node is offline for too long, its rewards are paused. Once the threshold is high, nodes will inevitably concentrate among a few.
The real reason Dusk feels worth tracking to me is that it’s not trying to build a faster chain—it’s exploring how transparent verification and privacy protection can truly coexist. But whether it can outperform a centralized clearing system depends on whether the node distribution is sufficiently dispersed, and whether the development documentation clearly guides which scenarios should use which layer. On-chain native compliance—do you think this path is actually workable? Let’s chat in the comments. #dusk
After working in compliance-oriented finance for a few years, my biggest confusion is this: why is it that assets on the blockchain can never flow like traditional securities—always both publicly auditable and strictly secret about transaction details? Transparency and privacy always seem like an either-or question.
Until I came across @Dusk . It doesn’t treat privacy as a plug-in feature—it’s embedded directly into the L1’s underlying logic.
Pros: Through Confidential Smart Contracts and the XSC standard, it provides a compliance-and-privacy-parallel framework tailored for securities-type assets. On-chain verification focuses on the correctness of state transitions, not exposing transaction amounts and identities. This made me feel like it’s genuinely answering the thorny question: “Once real-world assets are tokenized on-chain, how do we handle compliance?”
Cons: This kind of deep privacy-bound architecture also drives complexity up sharply. It separates the execution layer from the settlement layer: the base layer handles consensus and settlement, while the upper layer is compatible with EVM. The modular design lowers the development barrier, but it also introduces risks for cross-layer asset transfers. In the past, vulnerabilities created by cross-layer design were far more than what existed in smart contracts themselves.
What I care about more is consistency in the privacy assumptions. If the execution layer is transparent, and the settlement layer has confidentiality capabilities, then an asset’s privacy properties depend on which layer it’s at right now. For users and auditors, this split creates extremely high explanation costs. Vaguely marketing it as “everything is supported” at the end will likely mean neither side is truly good enough.
The DUSK project put thought into its node design, but a node system and “true decentralization” are two different things. The staking rewards for $DUSK depend on your share of the staking pool across the entire network; large holders naturally have an advantage. On top of that, there’s a soft-penalty mechanism: if a node is offline for too long, its rewards are paused. Once the threshold is high, nodes will inevitably concentrate among a few.
The real reason Dusk feels worth tracking to me is that it’s not trying to build a faster chain—it’s exploring how transparent verification and privacy protection can truly coexist. But whether it can outperform a centralized clearing system depends on whether the node distribution is sufficiently dispersed, and whether the development documentation clearly guides which scenarios should use which layer. On-chain native compliance—do you think this path is actually workable? Let’s chat in the comments. #dusk
Until I came across @Dusk . It doesn’t treat privacy as a plug-in feature—it’s embedded directly into the L1’s underlying logic.
Pros: Through Confidential Smart Contracts and the XSC standard, it provides a compliance-and-privacy-parallel framework tailored for securities-type assets. On-chain verification focuses on the correctness of state transitions, not exposing transaction amounts and identities. This made me feel like it’s genuinely answering the thorny question: “Once real-world assets are tokenized on-chain, how do we handle compliance?”
Cons: This kind of deep privacy-bound architecture also drives complexity up sharply. It separates the execution layer from the settlement layer: the base layer handles consensus and settlement, while the upper layer is compatible with EVM. The modular design lowers the development barrier, but it also introduces risks for cross-layer asset transfers. In the past, vulnerabilities created by cross-layer design were far more than what existed in smart contracts themselves.
What I care about more is consistency in the privacy assumptions. If the execution layer is transparent, and the settlement layer has confidentiality capabilities, then an asset’s privacy properties depend on which layer it’s at right now. For users and auditors, this split creates extremely high explanation costs. Vaguely marketing it as “everything is supported” at the end will likely mean neither side is truly good enough.
The DUSK project put thought into its node design, but a node system and “true decentralization” are two different things. The staking rewards for $DUSK depend on your share of the staking pool across the entire network; large holders naturally have an advantage. On top of that, there’s a soft-penalty mechanism: if a node is offline for too long, its rewards are paused. Once the threshold is high, nodes will inevitably concentrate among a few.
The real reason Dusk feels worth tracking to me is that it’s not trying to build a faster chain—it’s exploring how transparent verification and privacy protection can truly coexist. But whether it can outperform a centralized clearing system depends on whether the node distribution is sufficiently dispersed, and whether the development documentation clearly guides which scenarios should use which layer. On-chain native compliance—do you think this path is actually workable? Let’s chat in the comments. #dusk
2
1
115
·
--
I watched Aave and Compound for three years. I woke up in the middle of the night and saw the interest rate jump from 3% to 8% within just 6 hours. On a 300k loan, the interest cost literally changed into a different number. You can’t explain to LPs why the yield is half gone. So TermMax rolled out “fixed interest rates.” I just want to ask: what’s there to lock the rate down?@termmax
Range Order is the most worth digging into. Instead of having lenders hang their money with a simple APR, borrowers lend, and the funds are split into small chunks. Orders are placed at different prices between 5% and 7%, forming a pricing curve. For each executed trade, the interest rate moves along that curve. This makes it no longer a black box—at what interest rates the funds are willing to come out is transparent to both sides, and you can clearly see how much value is sitting at each rate tier.
The FT issued when borrowing is split into principal and interest. The interest portion is swapped via Range Order into XT. XT is then paired with the principal FT to form a debt token. FT represents the principal redeemed at face value at maturity. XT represents interest earnings that go to zero at maturity. GT is like an accounting ledger that records collateral and debt positions. After the liquidation window ends, if some debt remains uncleared, Physical Delivery lets FT holders claim the underlying assets from the redemption pool pro rata. These mechanics make fixed rates into something tokenized—tradable and verifiable at the token layer.
The counterargument cards aren’t soft either. Officially, they say TVL is over 90 million, registered wallets over 1.5 million, and daily active users over 90k. But DefiLlama shows TermMax’s current TVL is about $34.19 million, with Ethereum accounting for $32.19 million (94%). V2 has been deployed across 10 chains, but the capital hasn’t spread out. Even more worth watching is whether the users who flood in via Binance Wallet check-ins, XP incentives, and Galxe tasks are genuinely coming to borrow and lend, or just farming points and leaving. After one user completes 30 consecutive check-ins and the rewards hit, do they go study Range Order, or do they just withdraw immediately? After the TGE on Aug 25, once XP, AP, and MP expectations are cashed out, when the new-user fuel is burned through, how many people will actually stay with funds?
So I’ll state the conclusion directly: if rewards are burned out and people still stay, that’s what clears the first hurdle. After three months, I won’t just watch TVL—I’ll only look at the list of addresses that proactively initiate borrowing/lending transactions. As long as that number doesn’t drop, I’d say TermMax’s fixed interest rate is real demand.#termmax
I watched Aave and Compound for three years. I woke up in the middle of the night and saw the interest rate jump from 3% to 8% within just 6 hours. On a 300k loan, the interest cost literally changed into a different number. You can’t explain to LPs why the yield is half gone. So TermMax rolled out “fixed interest rates.” I just want to ask: what’s there to lock the rate down?@TermMax
Range Order is the most worth digging into. Instead of having lenders hang their money with a simple APR, borrowers lend, and the funds are split into small chunks. Orders are placed at different prices between 5% and 7%, forming a pricing curve. For each executed trade, the interest rate moves along that curve. This makes it no longer a black box—at what interest rates the funds are willing to come out is transparent to both sides, and you can clearly see how much value is sitting at each rate tier.
The FT issued when borrowing is split into principal and interest. The interest portion is swapped via Range Order into XT. XT is then paired with the principal FT to form a debt token. FT represents the principal redeemed at face value at maturity. XT represents interest earnings that go to zero at maturity. GT is like an accounting ledger that records collateral and debt positions. After the liquidation window ends, if some debt remains uncleared, Physical Delivery lets FT holders claim the underlying assets from the redemption pool pro rata. These mechanics make fixed rates into something tokenized—tradable and verifiable at the token layer.
The counterargument cards aren’t soft either. Officially, they say TVL is over 90 million, registered wallets over 1.5 million, and daily active users over 90k. But DefiLlama shows TermMax’s current TVL is about $34.19 million, with Ethereum accounting for $32.19 million (94%). V2 has been deployed across 10 chains, but the capital hasn’t spread out. Even more worth watching is whether the users who flood in via Binance Wallet check-ins, XP incentives, and Galxe tasks are genuinely coming to borrow and lend, or just farming points and leaving. After one user completes 30 consecutive check-ins and the rewards hit, do they go study Range Order, or do they just withdraw immediately? After the TGE on Aug 25, once XP, AP, and MP expectations are cashed out, when the new-user fuel is burned through, how many people will actually stay with funds?
So I’ll state the conclusion directly: if rewards are burned out and people still stay, that’s what clears the first hurdle. After three months, I won’t just watch TVL—I’ll only look at the list of addresses that proactively initiate borrowing/lending transactions. As long as that number doesn’t drop, I’d say TermMax’s fixed interest rate is real demand.#termmax
Range Order is the most worth digging into. Instead of having lenders hang their money with a simple APR, borrowers lend, and the funds are split into small chunks. Orders are placed at different prices between 5% and 7%, forming a pricing curve. For each executed trade, the interest rate moves along that curve. This makes it no longer a black box—at what interest rates the funds are willing to come out is transparent to both sides, and you can clearly see how much value is sitting at each rate tier.
The FT issued when borrowing is split into principal and interest. The interest portion is swapped via Range Order into XT. XT is then paired with the principal FT to form a debt token. FT represents the principal redeemed at face value at maturity. XT represents interest earnings that go to zero at maturity. GT is like an accounting ledger that records collateral and debt positions. After the liquidation window ends, if some debt remains uncleared, Physical Delivery lets FT holders claim the underlying assets from the redemption pool pro rata. These mechanics make fixed rates into something tokenized—tradable and verifiable at the token layer.
The counterargument cards aren’t soft either. Officially, they say TVL is over 90 million, registered wallets over 1.5 million, and daily active users over 90k. But DefiLlama shows TermMax’s current TVL is about $34.19 million, with Ethereum accounting for $32.19 million (94%). V2 has been deployed across 10 chains, but the capital hasn’t spread out. Even more worth watching is whether the users who flood in via Binance Wallet check-ins, XP incentives, and Galxe tasks are genuinely coming to borrow and lend, or just farming points and leaving. After one user completes 30 consecutive check-ins and the rewards hit, do they go study Range Order, or do they just withdraw immediately? After the TGE on Aug 25, once XP, AP, and MP expectations are cashed out, when the new-user fuel is burned through, how many people will actually stay with funds?
So I’ll state the conclusion directly: if rewards are burned out and people still stay, that’s what clears the first hurdle. After three months, I won’t just watch TVL—I’ll only look at the list of addresses that proactively initiate borrowing/lending transactions. As long as that number doesn’t drop, I’d say TermMax’s fixed interest rate is real demand.#termmax
131
·
--
Everyone who’s done a compliance audit has a common feeling: the thing to fear isn’t the inspection itself—it’s having to prove that a customer hasn’t violated any rules while also not exposing the customer’s privacy in full. Traditional approaches rely on reviewing bank flow records, identity documents, and address proofs; after the audit, everything still has to be archived. Every archived record is a risk.
So when I look at projects like Dusk that play the “compliance and privacy” card, my first reaction is to see how they handle this contradiction. With Citadel’s identity layer, it takes a selective disclosure route: users hold credentials issued by an institution, and during transactions they use zero-knowledge proofs—cryptographic tools that don’t reveal specific information, but can prove that “I meet the requirements.” This proves compliance without having to hand over originals. Moonlight handles ordinary transfers with publicly available accounts. Phoenix uses private UTXOs—similar to Bitcoin’s unspent transaction output model—so each transaction is isolated, doesn’t expose balances, and can handle sensitive transactions by splitting the two paths. @Dusk_Foundation
For regulated assets, this logic holds: asset transfers must pass compliance checks and also protect privacy—you can’t throw away KYC for the sake of privacy.
I won’t sugarcoat it. Citadel’s root of trust is tied to the issuer. Who is authorized to issue, how credentials get revoked, and whether old credentials still count if an institution disappears—these aren’t problems cryptography can solve; they’re governance issues. Flip through the documentation and you’ll find the revocation mechanism details are thin. Cross-jurisdictional use is also a problem: the EU definition of qualified investors differs from the U.S., so credentials can’t be reused directly. A crypto-library vulnerability was patched in April 2026, but it makes you ask one more question: are there any other issues?
The ecosystem is thin too. GitHub updates are slow, there are few third-party applications, and the documentation isn’t beginner-friendly. The technical direction is sound, but no one is building the infrastructure—good foundations don’t matter if the space is empty.
My view: Dusk has tackled the technical challenge of “compliance and privacy at the same time,” and the direction is right. What’s left is all business negotiation and regulatory communication—things that take far longer than writing code.
If you want licensed institutions to give up the customer-data moat they already have, what can you offer that actually gets them to talk? #dusk $DUSK
Everyone who’s done a compliance audit has a common feeling: the thing to fear isn’t the inspection itself—it’s having to prove that a customer hasn’t violated any rules while also not exposing the customer’s privacy in full. Traditional approaches rely on reviewing bank flow records, identity documents, and address proofs; after the audit, everything still has to be archived. Every archived record is a risk.
So when I look at projects like Dusk that play the “compliance and privacy” card, my first reaction is to see how they handle this contradiction. With Citadel’s identity layer, it takes a selective disclosure route: users hold credentials issued by an institution, and during transactions they use zero-knowledge proofs—cryptographic tools that don’t reveal specific information, but can prove that “I meet the requirements.” This proves compliance without having to hand over originals. Moonlight handles ordinary transfers with publicly available accounts. Phoenix uses private UTXOs—similar to Bitcoin’s unspent transaction output model—so each transaction is isolated, doesn’t expose balances, and can handle sensitive transactions by splitting the two paths. @Dusk
For regulated assets, this logic holds: asset transfers must pass compliance checks and also protect privacy—you can’t throw away KYC for the sake of privacy.
I won’t sugarcoat it. Citadel’s root of trust is tied to the issuer. Who is authorized to issue, how credentials get revoked, and whether old credentials still count if an institution disappears—these aren’t problems cryptography can solve; they’re governance issues. Flip through the documentation and you’ll find the revocation mechanism details are thin. Cross-jurisdictional use is also a problem: the EU definition of qualified investors differs from the U.S., so credentials can’t be reused directly. A crypto-library vulnerability was patched in April 2026, but it makes you ask one more question: are there any other issues?
The ecosystem is thin too. GitHub updates are slow, there are few third-party applications, and the documentation isn’t beginner-friendly. The technical direction is sound, but no one is building the infrastructure—good foundations don’t matter if the space is empty.
My view: Dusk has tackled the technical challenge of “compliance and privacy at the same time,” and the direction is right. What’s left is all business negotiation and regulatory communication—things that take far longer than writing code.
If you want licensed institutions to give up the customer-data moat they already have, what can you offer that actually gets them to talk? #dusk $DUSK
So when I look at projects like Dusk that play the “compliance and privacy” card, my first reaction is to see how they handle this contradiction. With Citadel’s identity layer, it takes a selective disclosure route: users hold credentials issued by an institution, and during transactions they use zero-knowledge proofs—cryptographic tools that don’t reveal specific information, but can prove that “I meet the requirements.” This proves compliance without having to hand over originals. Moonlight handles ordinary transfers with publicly available accounts. Phoenix uses private UTXOs—similar to Bitcoin’s unspent transaction output model—so each transaction is isolated, doesn’t expose balances, and can handle sensitive transactions by splitting the two paths. @Dusk
For regulated assets, this logic holds: asset transfers must pass compliance checks and also protect privacy—you can’t throw away KYC for the sake of privacy.
I won’t sugarcoat it. Citadel’s root of trust is tied to the issuer. Who is authorized to issue, how credentials get revoked, and whether old credentials still count if an institution disappears—these aren’t problems cryptography can solve; they’re governance issues. Flip through the documentation and you’ll find the revocation mechanism details are thin. Cross-jurisdictional use is also a problem: the EU definition of qualified investors differs from the U.S., so credentials can’t be reused directly. A crypto-library vulnerability was patched in April 2026, but it makes you ask one more question: are there any other issues?
The ecosystem is thin too. GitHub updates are slow, there are few third-party applications, and the documentation isn’t beginner-friendly. The technical direction is sound, but no one is building the infrastructure—good foundations don’t matter if the space is empty.
My view: Dusk has tackled the technical challenge of “compliance and privacy at the same time,” and the direction is right. What’s left is all business negotiation and regulatory communication—things that take far longer than writing code.
If you want licensed institutions to give up the customer-data moat they already have, what can you offer that actually gets them to talk? #dusk $DUSK
92
·
--
I’ve spent a few years integrating trading systems, and I’m fixated on the question: “Is settlement truly finished?” It’s not that T+1 or T+2 is slow due to technology—it’s because between clearing and settlement there are reconciliation, collateral/guarantees, and handling defaults. For every hour it drags on, the risk exposure grows and the capital-usage cost increases.
In a financial settlement chain like Dusk, the first question is always: once you say you’re done, how done is “done”? @Dusk_Foundation
With Dusk’s Succinct Attestation consensus, validators are randomly selected to produce blocks. Block confirmation is finality—no probabilistic rollback. Blocks are produced in seconds, and settlement completes within 15 seconds. Financial scenarios need this: settlement can’t be “high-probability confirmation.” Being three minutes off is, in accounting terms, a different world.
Can I pretend not to notice the cost of fast confirmation? Impossible. Deterministic consensus demands extremely high uptime from validators. If nodes go offline or the network partitions, then in probabilistic consensus it’s just slower—but here it may directly stall block production. I’ve run it on regular broadband myself: when the IP hops, you miss voting—you have to wait minutes for the next resync. In reality, it’s nowhere near 15 seconds. Institutional-grade settlement requires institutional-grade node quality; the accompanying costs can’t be solved by a whitepaper.
And cross-system integration has to be accounted for too. On-chain confirmation in three seconds, asset linkage with traditional custody—the real settlement still depends on the slowest link. This isn’t Dusk’s fault; it’s the current state of the integration layer, and it directly shapes the user experience. The ecosystem is also still thin. DuskEVM just launched—there aren’t many applications yet, and developers are still in the early stage. The fact that over 300 million euros of tokenized securities have already been on-chain is a signal; we’re still a few steps away from prosperity.
My take: the settlement design is solid, and Succinct Attestation is the right fit. I’m not copying a public-chain template. The weaknesses all lie in the operational layer—node quality, cross-system integration, and ecosystem building. These aren’t pretty, but they decide success or failure.
Someone can say “seconds-level confirmation” in one sentence. But keeping it stable is another matter entirely. Folks—if the price of running the node is upgrading bandwidth and using a static IP, are you willing? #dusk $DUSK
I’ve spent a few years integrating trading systems, and I’m fixated on the question: “Is settlement truly finished?” It’s not that T+1 or T+2 is slow due to technology—it’s because between clearing and settlement there are reconciliation, collateral/guarantees, and handling defaults. For every hour it drags on, the risk exposure grows and the capital-usage cost increases.
In a financial settlement chain like Dusk, the first question is always: once you say you’re done, how done is “done”? @Dusk
With Dusk’s Succinct Attestation consensus, validators are randomly selected to produce blocks. Block confirmation is finality—no probabilistic rollback. Blocks are produced in seconds, and settlement completes within 15 seconds. Financial scenarios need this: settlement can’t be “high-probability confirmation.” Being three minutes off is, in accounting terms, a different world.
Can I pretend not to notice the cost of fast confirmation? Impossible. Deterministic consensus demands extremely high uptime from validators. If nodes go offline or the network partitions, then in probabilistic consensus it’s just slower—but here it may directly stall block production. I’ve run it on regular broadband myself: when the IP hops, you miss voting—you have to wait minutes for the next resync. In reality, it’s nowhere near 15 seconds. Institutional-grade settlement requires institutional-grade node quality; the accompanying costs can’t be solved by a whitepaper.
And cross-system integration has to be accounted for too. On-chain confirmation in three seconds, asset linkage with traditional custody—the real settlement still depends on the slowest link. This isn’t Dusk’s fault; it’s the current state of the integration layer, and it directly shapes the user experience. The ecosystem is also still thin. DuskEVM just launched—there aren’t many applications yet, and developers are still in the early stage. The fact that over 300 million euros of tokenized securities have already been on-chain is a signal; we’re still a few steps away from prosperity.
My take: the settlement design is solid, and Succinct Attestation is the right fit. I’m not copying a public-chain template. The weaknesses all lie in the operational layer—node quality, cross-system integration, and ecosystem building. These aren’t pretty, but they decide success or failure.
Someone can say “seconds-level confirmation” in one sentence. But keeping it stable is another matter entirely. Folks—if the price of running the node is upgrading bandwidth and using a static IP, are you willing? #dusk $DUSK
In a financial settlement chain like Dusk, the first question is always: once you say you’re done, how done is “done”? @Dusk
With Dusk’s Succinct Attestation consensus, validators are randomly selected to produce blocks. Block confirmation is finality—no probabilistic rollback. Blocks are produced in seconds, and settlement completes within 15 seconds. Financial scenarios need this: settlement can’t be “high-probability confirmation.” Being three minutes off is, in accounting terms, a different world.
Can I pretend not to notice the cost of fast confirmation? Impossible. Deterministic consensus demands extremely high uptime from validators. If nodes go offline or the network partitions, then in probabilistic consensus it’s just slower—but here it may directly stall block production. I’ve run it on regular broadband myself: when the IP hops, you miss voting—you have to wait minutes for the next resync. In reality, it’s nowhere near 15 seconds. Institutional-grade settlement requires institutional-grade node quality; the accompanying costs can’t be solved by a whitepaper.
And cross-system integration has to be accounted for too. On-chain confirmation in three seconds, asset linkage with traditional custody—the real settlement still depends on the slowest link. This isn’t Dusk’s fault; it’s the current state of the integration layer, and it directly shapes the user experience. The ecosystem is also still thin. DuskEVM just launched—there aren’t many applications yet, and developers are still in the early stage. The fact that over 300 million euros of tokenized securities have already been on-chain is a signal; we’re still a few steps away from prosperity.
My take: the settlement design is solid, and Succinct Attestation is the right fit. I’m not copying a public-chain template. The weaknesses all lie in the operational layer—node quality, cross-system integration, and ecosystem building. These aren’t pretty, but they decide success or failure.
Someone can say “seconds-level confirmation” in one sentence. But keeping it stable is another matter entirely. Folks—if the price of running the node is upgrading bandwidth and using a static IP, are you willing? #dusk $DUSK
2
1
97
·
--
When I was flipping through Dusk’s 2024 version whitepaper, I happened to land on page 17. Under the same address, Moonlight and Phoenix run as two sets of ledgers in parallel: at the user end, you just click a button and it switches; at the protocol end, they essentially take separate routes. @Dusk_Foundation
In the Phoenix section’s supplementary notes, there’s a line of original text that I kept mulling over. It says the added capability is “identifying the sender of a Phoenix transaction to the receiver,” with the purpose being “turning Phoenix from an anonymity protocol into a privacy-preserving protocol that is compliant with current EU regulations.” In other words, for compliance, the anonymity attribute is adjusted into a privacy mode that allows the sender to be identifiable. Then when I turned to the consensus mechanism section, it says nodes must participate in SBA consensus by submitting DUSK bids. The whitepaper’s Section 3 states it very clearly—effectively embedding privacy protection into the consensus layer, but at the cost that nodes must complete identity verification. In the whitepaper’s opening of Section 1, it also says it wants to “allow users, exchanges, and institutions to transact both publicly and privately.” This design is basically calculating one ledger under the hood.
Moonlight helps regulators audit; Phoenix helps institutions hide their commercial playbook. But looking at it the other way around, it’s effectively shifting the cost of compliance decision-making directly onto ordinary users. Even people who can’t keep their mnemonic phrases straight—you’re asking them to judge before every transfer whether they should use the privacy mode. That requirement is indeed a bit high. But I broadly agree with the direction of DUSK’s architecture. Traditional finance wants both efficiency and to avoid exposing commercial secrets on a public chain for anyone to scrutinize. Compared with something like Zcash’s “privacy above all” approach, DUSK is more likely to get institutions to pay attention and actually commit funds. As for $DUSK , the network’s gas fee and the staked token value anchoring are tied to real-world, implementable business usage.
Still, striking the right balance is hard. Cut too well and you get a moat; cut too far and you please neither side. No matter how polished the whitepaper is, in the end it will depend on whether the Dapp on Phoenix can really run, and whether institutions are willing to put real money in. For now, I’ll just be a spectator. #dusk
When I was flipping through Dusk’s 2024 version whitepaper, I happened to land on page 17. Under the same address, Moonlight and Phoenix run as two sets of ledgers in parallel: at the user end, you just click a button and it switches; at the protocol end, they essentially take separate routes. @Dusk
In the Phoenix section’s supplementary notes, there’s a line of original text that I kept mulling over. It says the added capability is “identifying the sender of a Phoenix transaction to the receiver,” with the purpose being “turning Phoenix from an anonymity protocol into a privacy-preserving protocol that is compliant with current EU regulations.” In other words, for compliance, the anonymity attribute is adjusted into a privacy mode that allows the sender to be identifiable. Then when I turned to the consensus mechanism section, it says nodes must participate in SBA consensus by submitting DUSK bids. The whitepaper’s Section 3 states it very clearly—effectively embedding privacy protection into the consensus layer, but at the cost that nodes must complete identity verification. In the whitepaper’s opening of Section 1, it also says it wants to “allow users, exchanges, and institutions to transact both publicly and privately.” This design is basically calculating one ledger under the hood.
Moonlight helps regulators audit; Phoenix helps institutions hide their commercial playbook. But looking at it the other way around, it’s effectively shifting the cost of compliance decision-making directly onto ordinary users. Even people who can’t keep their mnemonic phrases straight—you’re asking them to judge before every transfer whether they should use the privacy mode. That requirement is indeed a bit high. But I broadly agree with the direction of DUSK’s architecture. Traditional finance wants both efficiency and to avoid exposing commercial secrets on a public chain for anyone to scrutinize. Compared with something like Zcash’s “privacy above all” approach, DUSK is more likely to get institutions to pay attention and actually commit funds. As for $DUSK , the network’s gas fee and the staked token value anchoring are tied to real-world, implementable business usage.
Still, striking the right balance is hard. Cut too well and you get a moat; cut too far and you please neither side. No matter how polished the whitepaper is, in the end it will depend on whether the Dapp on Phoenix can really run, and whether institutions are willing to put real money in. For now, I’ll just be a spectator. #dusk
In the Phoenix section’s supplementary notes, there’s a line of original text that I kept mulling over. It says the added capability is “identifying the sender of a Phoenix transaction to the receiver,” with the purpose being “turning Phoenix from an anonymity protocol into a privacy-preserving protocol that is compliant with current EU regulations.” In other words, for compliance, the anonymity attribute is adjusted into a privacy mode that allows the sender to be identifiable. Then when I turned to the consensus mechanism section, it says nodes must participate in SBA consensus by submitting DUSK bids. The whitepaper’s Section 3 states it very clearly—effectively embedding privacy protection into the consensus layer, but at the cost that nodes must complete identity verification. In the whitepaper’s opening of Section 1, it also says it wants to “allow users, exchanges, and institutions to transact both publicly and privately.” This design is basically calculating one ledger under the hood.
Moonlight helps regulators audit; Phoenix helps institutions hide their commercial playbook. But looking at it the other way around, it’s effectively shifting the cost of compliance decision-making directly onto ordinary users. Even people who can’t keep their mnemonic phrases straight—you’re asking them to judge before every transfer whether they should use the privacy mode. That requirement is indeed a bit high. But I broadly agree with the direction of DUSK’s architecture. Traditional finance wants both efficiency and to avoid exposing commercial secrets on a public chain for anyone to scrutinize. Compared with something like Zcash’s “privacy above all” approach, DUSK is more likely to get institutions to pay attention and actually commit funds. As for $DUSK , the network’s gas fee and the staked token value anchoring are tied to real-world, implementable business usage.
Still, striking the right balance is hard. Cut too well and you get a moat; cut too far and you please neither side. No matter how polished the whitepaper is, in the end it will depend on whether the Dapp on Phoenix can really run, and whether institutions are willing to put real money in. For now, I’ll just be a spectator. #dusk
83
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
StrategyStriveAdd2305BitcoinThisWeek
16,063 views
559 Discussing
#strategystriveadd2305bitcointhisweek 🚨 2,305 BTC just moved into treasuries
While most traders were focused on the Bitcoin price rebound two public companies quietly made big moves. 👀
Strategy and Strive together bought 2,305 BTC for 182.7 million Dollar.
🔹 Strategy bought 950 BTC for 75.7 million dollar
🔹 Strive bought 1,355 BTC for around 107.7 million dollar
This brings their total holdings to:
📊 Strategy. 846,000 BTC
📊 Strive. 26,355 BTC
But the real story isn't the amount of Bitcoin they bought.
It's how they paid for it.
Strategy used cash it already had.
Strive used its stock financing model to fund the purchase. Meaning it’s growing its Bitcoin treasury without relying only on cash flow.
This difference matters.
For traders and investors it adds a layer of analysis: how much Bitcoin is being added, how it’s being funded and what it means for long-term value, per share.
The cost of capital BTC accumulation and share value. These factors are starting to shape the market in ways.
Corporate treasury demand is no longer a side note.
It’s becoming a part of the Bitcoin ecosystem.
💬 What do you think?
Will more companies start buying Bitcoin the way?
Will this trend grow?
#bitcoin #Khan62 #BTC #trading
$MSTR
$MARA $BMNR
Khan 62
·4 Likes
·2.8k views
TrumpRejectsIranHormuzReopening
19,382 views
512 Discussing
TokenizedStockDEXVolumeHits$20.9B
105 views
5 Discussing