

#uxlink
uxlink
2.5M views
1,986 Discussing
Hot
Latest
·
--
#ETH $ETH
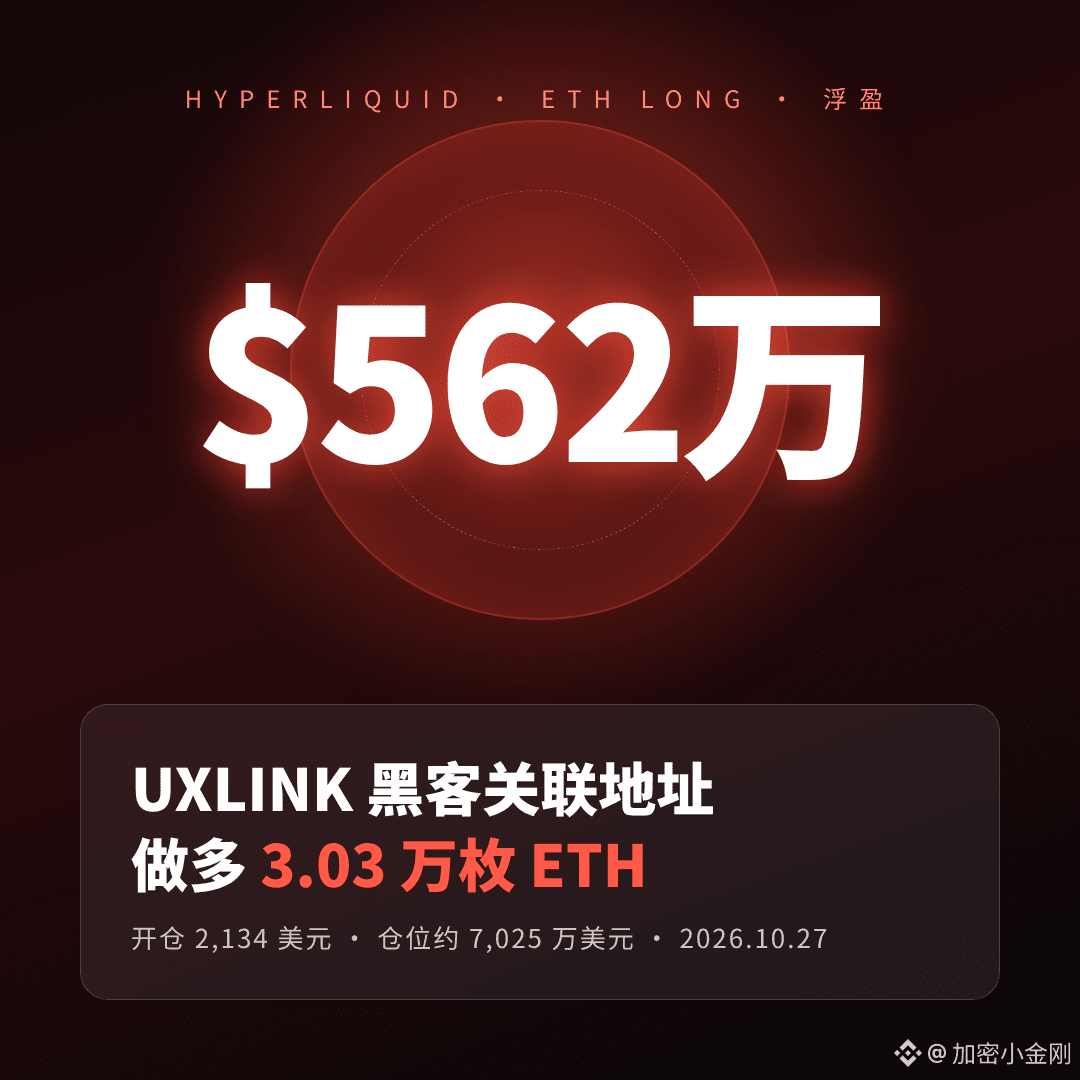
【The UXLINK hacker who stole about $40 million went long 30,000 ETH on Hyperliquid, with $5.62 million in unrealized profit】
Stolen funds used to open leveraged positions—and the profits just keep growing? 😶
On-chain analyst Ember spotted an account with funds linked to an address involved in the UXLINK theft. The account opened a long position of about 30,300 ETH on Hyperliquid:
🔹 Average entry price: $2,134
🔹 Position value: about $70.25 million
🔹 Unrealized profit: about $5.62 million
This account has a track record on Hyperliquid. In early August, it consolidated 11.54 million USDC from multiple sources, then traded ETH back and forth. It made money on 5 of 6 trades, with $5.71 million in realized profit.
Do the math: $11.54 million in starting capital, $5.71 million banked, plus $5.62 million on this open position—that’s about $11.33 million in total, nearly doubling the money.
How did they identify it as the same person? About a month ago, this funding address and the UXLINK hacker’s address swept their remaining ETH gas funds into the same wallet on the same day.
Three caveats:
1️⃣ On-chain fund links ≠ confirmed identity. This is currently an analyst’s inference, and it’s unclear whether the platform will take action.
2️⃣ Public positions ≠ something you can blindly copy. You can see the 5 profitable trades, but not the logic behind holding positions or setting stop-losses.
3️⃣ Today, another user reportedly lost $1.58 million on Ethereum and Base, possibly due to a leaked private key. A hacker’s capital ultimately comes from someone’s wallet.
My own rule: I don’t copy trades from any address, and I keep my seed phrase offline only.
Have you ever copied an on-chain whale’s trades? How did it go?
For informational purposes only; not investment advice. DYOR
#Hyperliquid #加密安全 #uxlink
67
·
--
Bearish
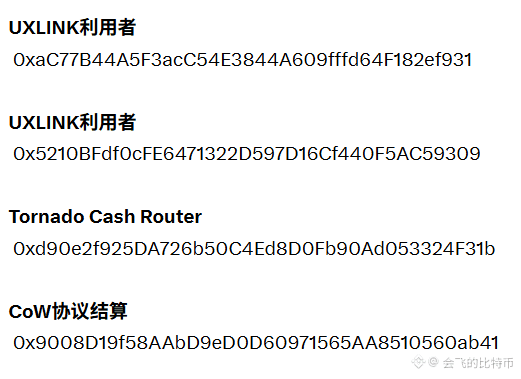
Security Alert|UXLINK Attacker Stole Funds Worth $10.5 Million and Laundered Them via Tornado Cash
First, the hacker exchanged 10.54 million DAI for 6,001 ETH, using coin-mixing to sever on-chain tracking links and greatly increasing the difficulty of tracing the stolen funds
In an early attack that caused UXLINK to plunge by 70%, the hacker continued to launder the stolen assets in batches; the project’s fundamentals have faced long-term pressure, and in the short term it has been avoiding $UXLINK
#UXLINK #链上黑客 #安全预警
86
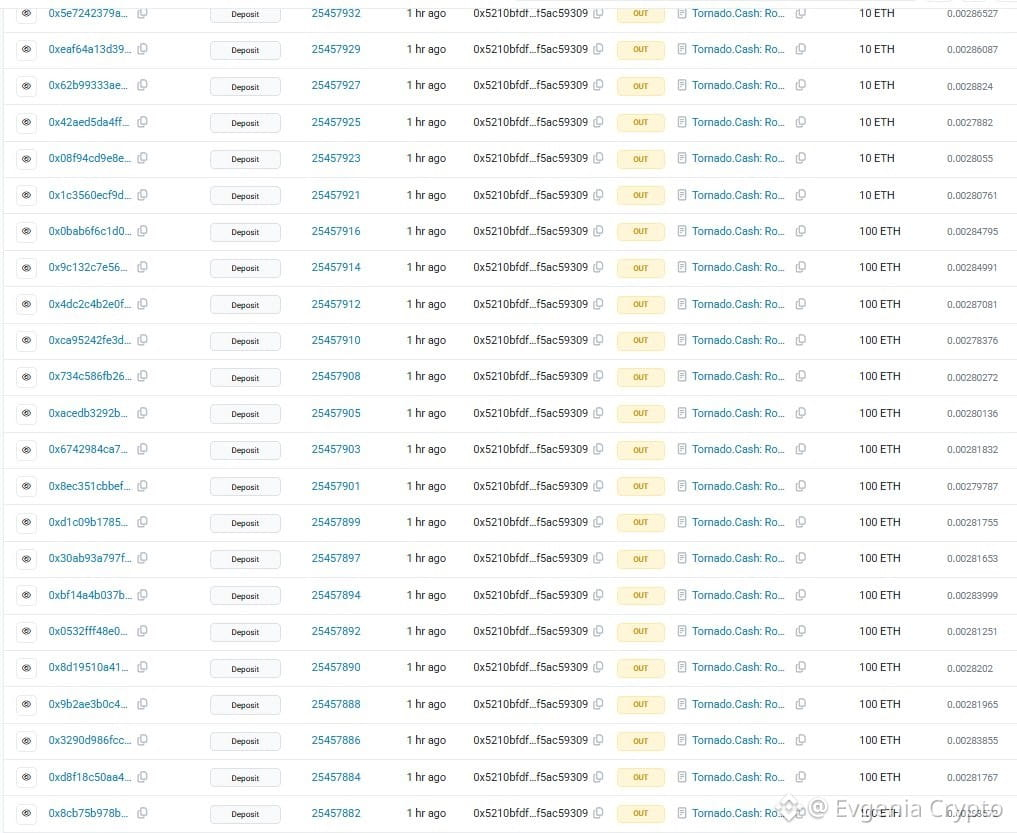
🚨 The UXLINK hacking story is nearing its finale.
The hacker has transferred the last stolen funds—about $10.5 million—to Tornado Cash.
Before that, DAI were exchanged for approximately 6 000 $ETH , after which the funds were sent through a crypto mixer.
Recall that in September, the attacker hacked UXLINK’s multisig, issued billions of new tokens, and stole around $40 million.
Now practically all the stolen assets have gone through a laundering scheme.
Protect your funds and always check which projects you trust.
{future}(ETHUSDT)
#UXLINK
🚨 The UXLINK hacking story is nearing its finale.
The hacker has transferred the last stolen funds—about $10.5 million—to Tornado Cash.
Before that, DAI were exchanged for approximately 6 000 $ETH , after which the funds were sent through a crypto mixer.
Recall that in September, the attacker hacked UXLINK’s multisig, issued billions of new tokens, and stole around $40 million.
Now practically all the stolen assets have gone through a laundering scheme.
Protect your funds and always check which projects you trust.
#UXLINK
363
·
--
Verified
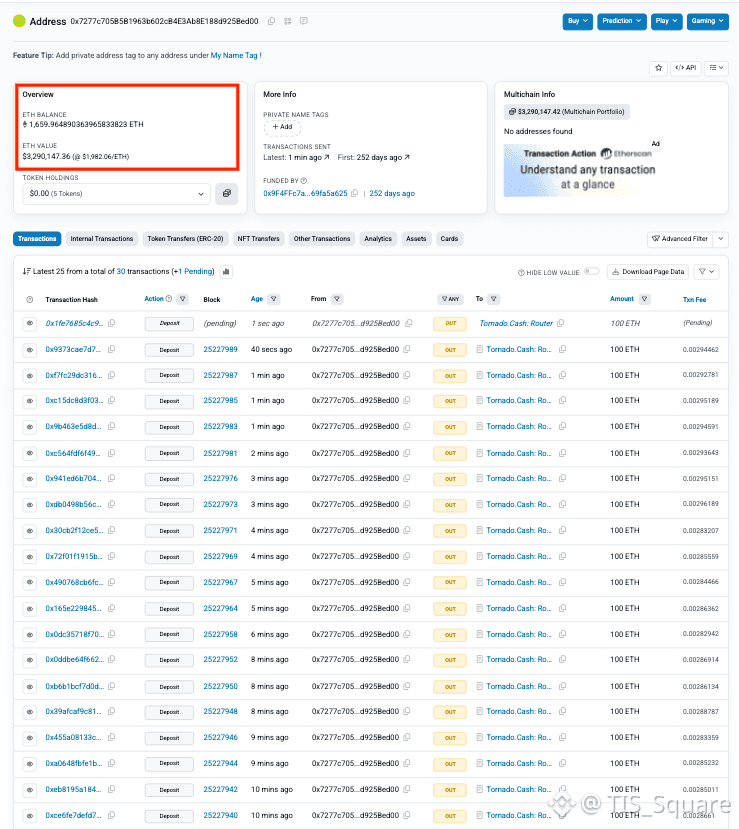
Hackers in the $UXLINK case are converting assets and laundering money through Mixers
According to a warning from PeckShield, the wallet linked to the UXLink attack is still moving stolen assets. So far, this entity has swapped 92 WBTC, around 6.4 million USD, for about 3,248 $ETH
{future}(ETHUSDT)
📊 Notably:
About 1,500 ETH has been transferred to Tornado Cash to obscure the money trail.
The conversion process from WBTC to ETH shows that the hackers are gradually dispersing and processing the stolen assets.
👀 UXLink was attacked in September 2025 after a multisig wallet was compromised, resulting in damages exceeding 44 million USD. Months later, a portion of the assets related to the incident continues to be moved on-chain.
⚠️ The use of mixing tools indicates that hackers are trying to complicate the tracing process. However, all transactions are still recorded on the blockchain and remain under the watchful eye of on-chain analytics companies.
#UXLink #CryptoHack #ETH #Onchain #Crypto
Hackers in the $UXLINK case are converting assets and laundering money through Mixers
According to a warning from PeckShield, the wallet linked to the UXLink attack is still moving stolen assets. So far, this entity has swapped 92 WBTC, around 6.4 million USD, for about 3,248 $ETH
📊 Notably:
About 1,500 ETH has been transferred to Tornado Cash to obscure the money trail.
The conversion process from WBTC to ETH shows that the hackers are gradually dispersing and processing the stolen assets.
👀 UXLink was attacked in September 2025 after a multisig wallet was compromised, resulting in damages exceeding 44 million USD. Months later, a portion of the assets related to the incident continues to be moved on-chain.
⚠️ The use of mixing tools indicates that hackers are trying to complicate the tracing process. However, all transactions are still recorded on the blockchain and remain under the watchful eye of on-chain analytics companies.
#UXLink #CryptoHack #ETH #Onchain #Crypto
597

First, the track record: it’s enough to make plenty of professional traders blush. The suspected hacker who stole about $40 million in assets from UXLINK last year consolidated 11.54 million USDC in early August and charged into Hyperliquid. So far, they’ve opened six positions, made money on five, and netted $5.71 million in total profits. The latest trade is even more aggressive: they went long 30,300 $ETH at $2,134, for a position worth $70.25 million, and are currently sitting on $5.62 million in unrealized gains.
Now, the money trail: every step is on-chain. The address that funded the long position consolidated its remaining ETH Gas into the same wallet as a known UXLINK hacker address on the same day a month ago. On-chain analyst Ember explicitly linked the two. Of course, it’s still only a suspicion—there’s been no conviction.
So here’s the question: the skills are real, but so is the character. Would you follow this trade? Pick a side in the comments: A) Follow the trade based only on the win rate—a hacker can be a trader too; B) Profits made with stolen funds make you an accomplice if you get involved.
$BTC $ETH $SOL #UXLINK #Hyperliquid #Hacker
6
·
--
Bullish
$BICO OBICO maintains positive momentum as cross-chain adoption expands. Strong buying pressure favors higher prices.#BICO #Blockchain #Crypto
$TLM TLM is gaining traction with renewed GameFi interest. Traders are monitoring breakout confirmation.#TLM #Gaming #Altcoins
$UXLINK INKUXLINK continues to see healthy trading activity with improving sentiment.#UXLINK #SocialFi #Binance
{future}(BICOUSDT)
{future}(TLMUSDT)
$BICO OBICO maintains positive momentum as cross-chain adoption expands. Strong buying pressure favors higher prices.#BICO #Blockchain #Crypto
$TLM TLM is gaining traction with renewed GameFi interest. Traders are monitoring breakout confirmation.#TLM #Gaming #Altcoins
$UXLINK INKUXLINK continues to see healthy trading activity with improving sentiment.#UXLINK #SocialFi #Binance
$TLM TLM is gaining traction with renewed GameFi interest. Traders are monitoring breakout confirmation.#TLM #Gaming #Altcoins
$UXLINK INKUXLINK continues to see healthy trading activity with improving sentiment.#UXLINK #SocialFi #Binance
289
·
--
Bullish
🔥 $UXLINK is gaining bullish momentum. 📊 Strong participation supports buyers. 🚀 Higher prices remain possible.
#UXLINK #SocialFi #TradingTales
🔥 $UXLINK is gaining bullish momentum. 📊 Strong participation supports buyers. 🚀 Higher prices remain possible.
#UXLINK #SocialFi #TradingTales
#UXLINK #SocialFi #TradingTales
16
The UXLINK attacker is going on a mad money-laundering spree, buying $6.5 million worth of ETH in 30 minutes and 'disappearing' through Tornado Cash.
On-chain monitoring shows that the UXLINK attacker is ramping up their laundering activities.
Latest move: In the past 30 minutes, this attacker spent 6.5 million DAI, averaging $1,764 to scoop up 3,686 ETH, then washed the funds through Tornado Cash.
This isn't their first rodeo. Previously, the attacker swapped 92 WBTC for about 3,248 ETH and deposited 1,500 ETH into Tornado Cash. On September 22, the UXLINK multi-signature wallet suffered a loss exceeding $44 million due to a security breach.
What does this mean?
Buying $6.5 million in ETH and funneling it into a mixer is a textbook on-chain money laundering procedure. This level of capital means that the ETH market will face ongoing sell pressure in the short term—not from regular traders, but from the cash-out demands of hackers.
Tornado Cash is a privacy mixer, and once the funds go in, they are practically untraceable. The hacker's choice of this method indicates they don’t plan to leave any traces of this money on-chain.
Market impact: The UXLINK attacker is still active, and more ETH could be dumped in the future. Day traders should be wary of the potential sell pressure on ETH. On-chain tracking shows that this attacker still holds a significant amount of DAI and ETH.
#UXLINK #hacker #moneylaundering #ETH #TornadoCash #链上追踪
353
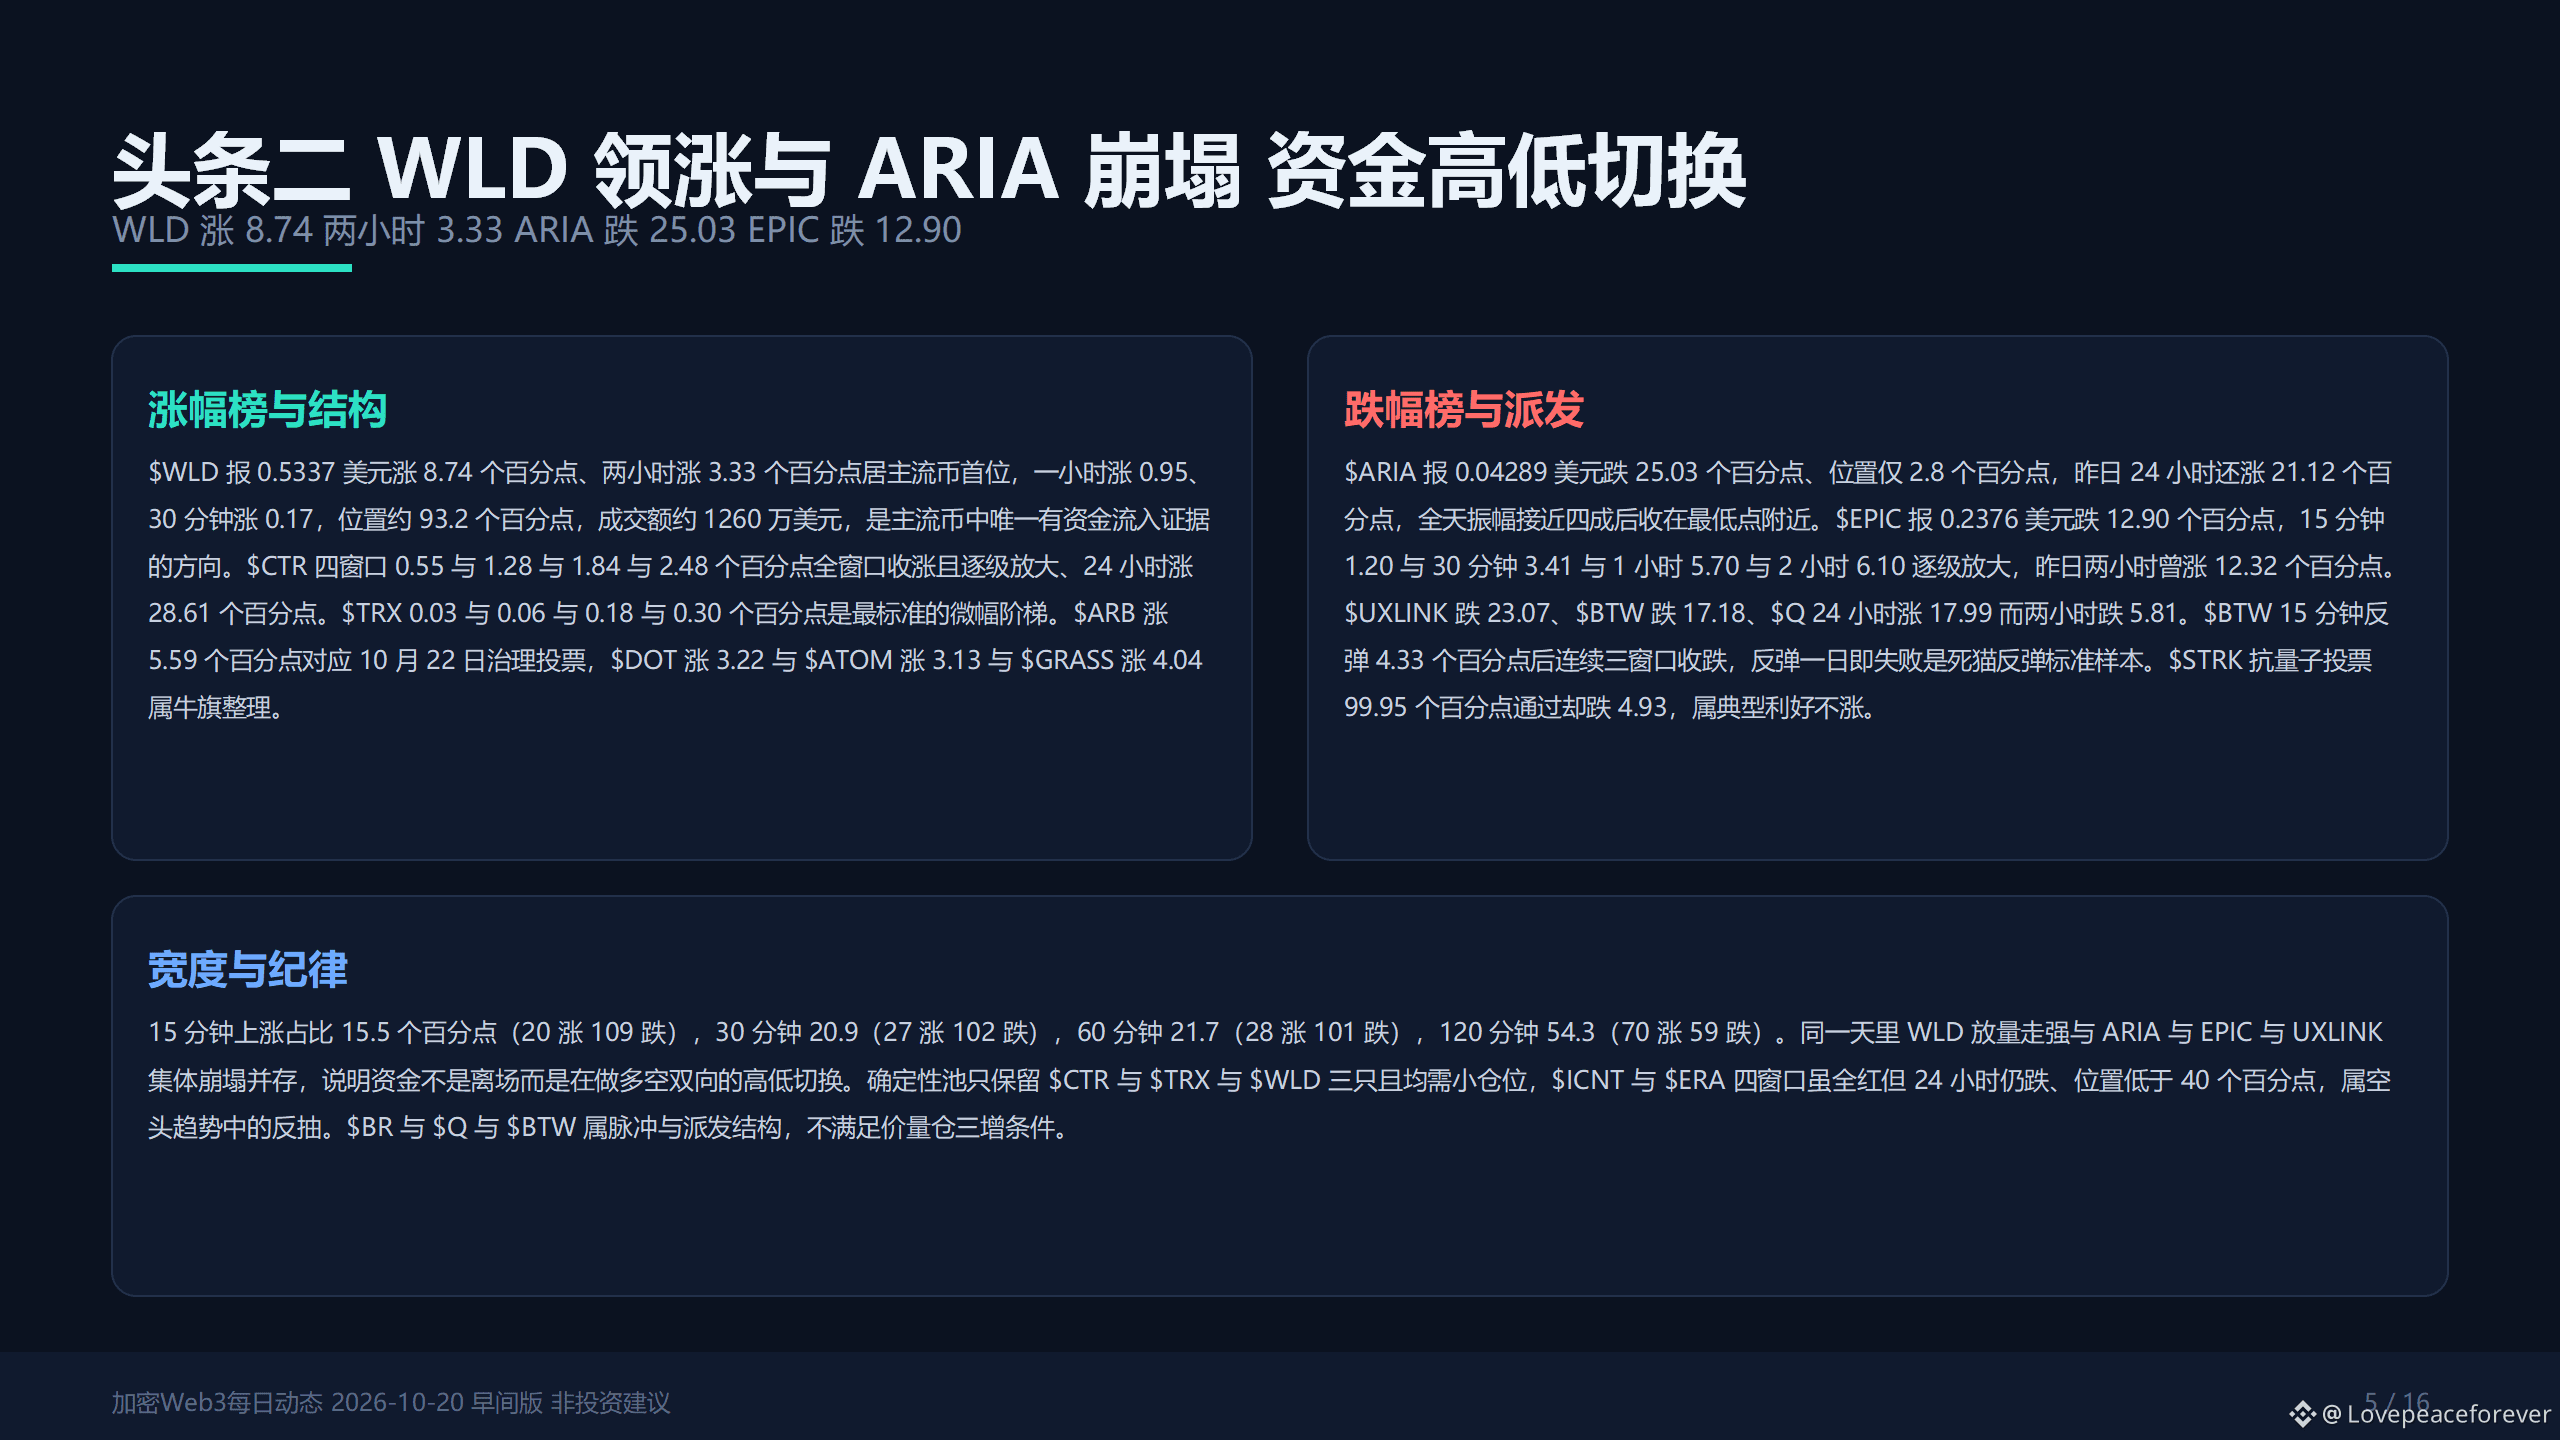
$WLD Leads Major Coins Over Two Hours as $ARIA and $EPIC Collapse from Their Highs
Event: WLD is trading at $0.5337, up 8.74% and 3.33% over two hours, leading major coins over that period. Its position is around 93.2%, with trading volume of approximately $12.6 million. On the downside, ARIA is trading at $0.04289, down 25.03%, with its position at just 2.8%; yesterday, the token was still up 21.12% over 24 hours. EPIC is trading at $0.2376, down 12.90% and 6.10% over two hours; yesterday, it had gained 12.32% in two hours. UXLINK is down 23.07%, and $BTW is down 17.18%.
Reason: WLD's surge on higher volume alongside the collapse of ARIA, #EPIC , and #uxlink on the same day suggests that capital is not exiting, but instead rotating between long and short positions and between high- and low-priced assets. ARIA and EPIC have erased all of yesterday's gains today and hit new lows, marking the second consecutive stage in a pump-and-dump pattern. After extreme cumulative gains over 30 days, BTW has entered an accelerated distribution phase.
Impact and beneficiary tokens: WLD faces resistance at $0.5374 and $0.56, with support at $0.4828 and $0.46; it remains strong but is trading at a relatively high level. ARIA faces resistance at $0.05 and $0.05996, with support at $0.04239 and $0.0404; any rebound to resistance is an opportunity to reduce positions. EPIC faces resistance at $0.3089 and $0.33, with support at $0.2333 and $0.22. BTW faces resistance at $2.00 and $2.4058, with support at $1.6862 and $1.60.
1k

·
--
Article
UXlink is already at 2.3u, you have a staked UXlink waiting to be unstaked, the strongest unstaking process is coming!I've been too busy lately and forgot to write this tutorial. Today I found some time to complete it. UXlink started its airdrop in June, with two options at that time: the first was to withdraw directly; the second was to stake. Those who directly sold their tokens have lost more than 10 times, while those who staked may have based it on luck or just made a wrong click at that time. Now the returns are skyrocketing. Without further ado, ➕ give a follow and let's get started.
uxlink
Preparation needed before unstaking: the staked account + a smart you
Step one: Open the Binance Web3 wallet
UXlink is already at 2.3u, you have a staked UXlink waiting to be unstaked, the strongest unstaking process is coming!
I've been too busy lately and forgot to write this tutorial. Today I found some time to complete it. UXlink started its airdrop in June, with two options at that time: the first was to withdraw directly; the second was to stake. Those who directly sold their tokens have lost more than 10 times, while those who staked may have based it on luck or just made a wrong click at that time. Now the returns are skyrocketing. Without further ado, ➕ give a follow and let's get started.
uxlink
Preparation needed before unstaking: the staked account + a smart you
Step one: Open the Binance Web3 wallet
uxlink
Preparation needed before unstaking: the staked account + a smart you
Step one: Open the Binance Web3 wallet
13
9
10
1.1k
·
--
【 $UXLINK Contract Migration Latest Progress 🛡️】
✅ 1:1 Exchange for New Contract (ETH Mainnet)
✅ Total Supply Remains Unchanged (1 Billion), Economic Model Unchanged
✅ Hacker Address Assets Have Been Identified and Removed
✅ Normal Users (CEX + On-chain) Can Obtain New UXLINK at 1:1
✅ The Timestamp of the Hacker's First Transfer Will Be Snapshotted, and Ordinary Users Holding UXLINK Before This Time Will Be Able to Redeem at 1:1.
⏱️ On-chain Exchange Tool Will Be Launched Within 5 Days
🔄 CEX Initial Exchanges Will Start Within 1–5 Days
🛡️ Additional Compensation Plans Will Follow: Buybacks, Staking Rewards, Trading Incentives, etc.
#uxlink #UXLINK钱包遭黑客攻击
1.1k

·
--
$UXLINK ATTACKER BOUGHT $10.5M IN $ETH – STRUCTURE SHIFT IMMINENT 🔥
This on-chain move saw 6,001 ETH purchased at $1,757 and then funneled through Tornado Cash — a classic distribution pattern. That volume at a precise level often leaves a footprint in order flow, and the market is now digesting that block.
A $10.5M inflow near a key zone can act as resistance if the attacker stages a dump, or as a liquidity grab if the structure holds. The 4H chart shows price sitting right at the previous consolidation range.
Are you watching this level for a sweep or a breakout?
Not financial advice. Always manage your risk.
#UXLINK #ETH #OnChainAnalysis #LiquidityEvent #Crypto
🔥
1
34
·
--
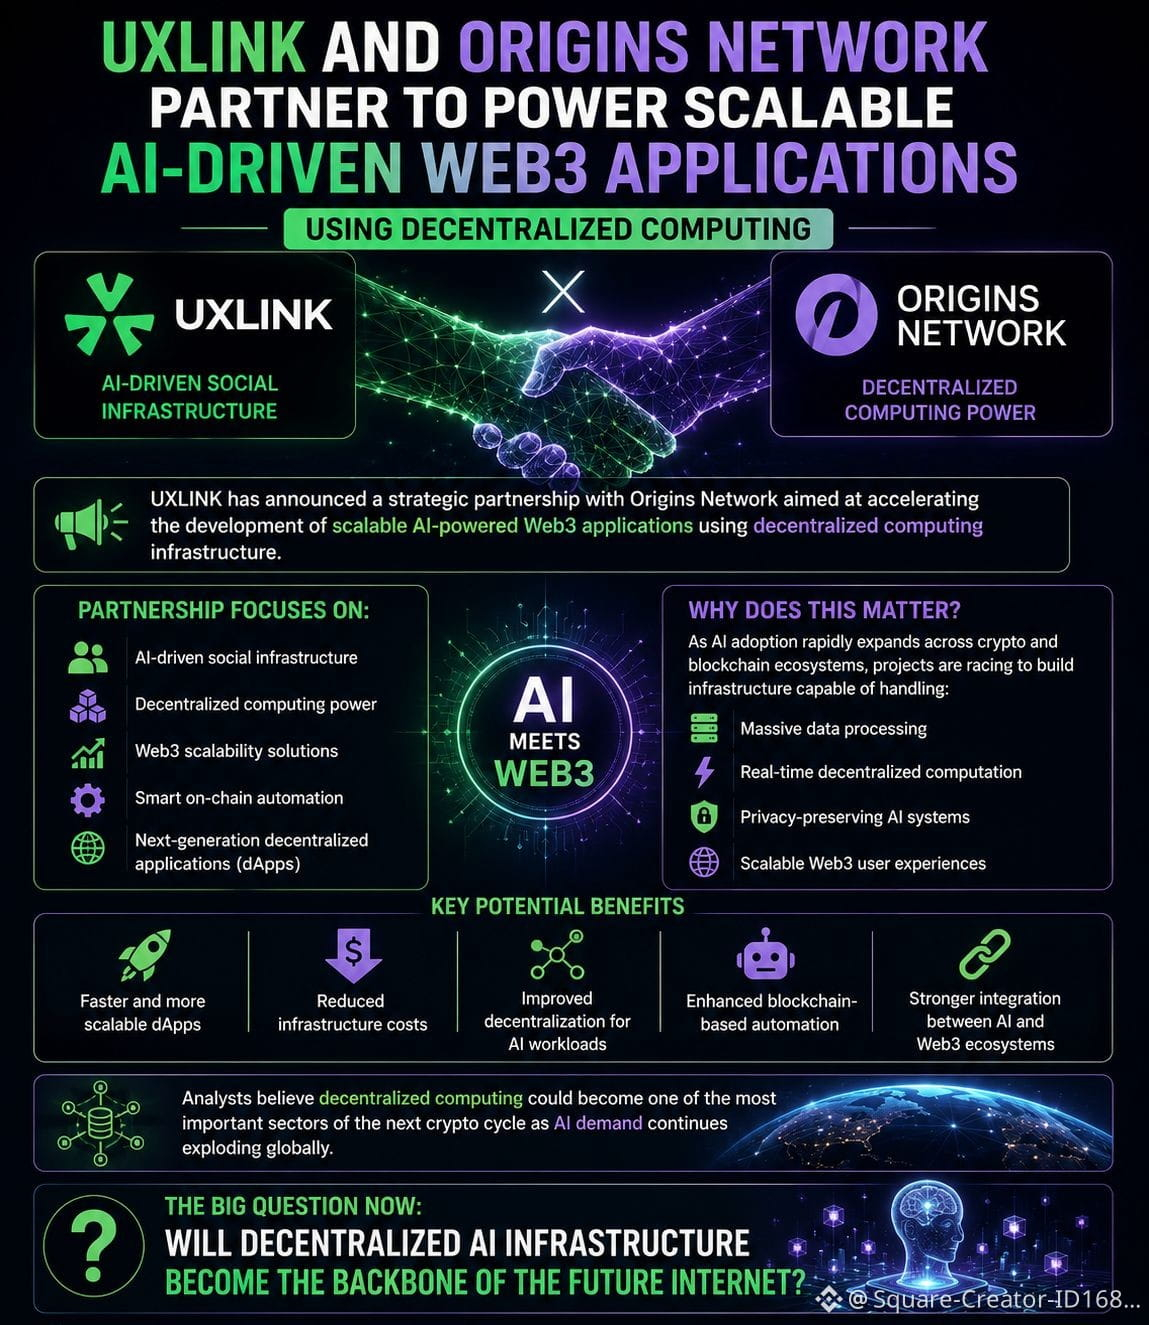
🚨 UXLINK and Origins Network Join Forces to Power AI-Driven Web3 Applications 🌐🤖
UXLINK has announced a strategic partnership with Origins Network aimed at accelerating the development of scalable AI-powered Web3 applications using decentralized computing infrastructure ⚡️
The collaboration focuses on combining:
🔸 AI-driven social infrastructure
🔸 Decentralized computing power
🔸 Web3 scalability solutions
🔸 Smart on-chain automation
🔸 Next-generation decentralized applications (dApps)
💡 Why does this matter?
As AI adoption rapidly expands across crypto and blockchain ecosystems, projects are racing to build infrastructure capable of handling:
📈 Massive data processing
⚡ Real-time decentralized computation
🔐 Privacy-preserving AI systems
🌍 Scalable Web3 user experiences
The partnership between UXLINK and Origins Network aims to create a more efficient decentralized environment where AI applications can operate without relying heavily on centralized cloud providers.
🔥 Key potential benefits:
✅ Faster and more scalable dApps
✅ Reduced infrastructure costs
✅ Improved decentralization for AI workloads
✅ Enhanced blockchain-based automation
✅ Stronger integration between AI and Web3 ecosystems
Analysts believe decentralized computing could become one of the most important sectors of the next crypto cycle as AI demand continues exploding globally 🚀
The big question now:
Will decentralized AI infrastructure become the backbone of the future internet? 👀⚡️
#USAdds115kJobs #bitcoin
#Write2Earn #Binance #uxlink
$LINK
{spot}(LINKUSDT)
$W
{spot}(WUSDT)
$AI
{spot}(AIUSDT)
🚨 UXLINK and Origins Network Join Forces to Power AI-Driven Web3 Applications 🌐🤖
UXLINK has announced a strategic partnership with Origins Network aimed at accelerating the development of scalable AI-powered Web3 applications using decentralized computing infrastructure ⚡️
The collaboration focuses on combining:
🔸 AI-driven social infrastructure
🔸 Decentralized computing power
🔸 Web3 scalability solutions
🔸 Smart on-chain automation
🔸 Next-generation decentralized applications (dApps)
💡 Why does this matter?
As AI adoption rapidly expands across crypto and blockchain ecosystems, projects are racing to build infrastructure capable of handling:
📈 Massive data processing
⚡ Real-time decentralized computation
🔐 Privacy-preserving AI systems
🌍 Scalable Web3 user experiences
The partnership between UXLINK and Origins Network aims to create a more efficient decentralized environment where AI applications can operate without relying heavily on centralized cloud providers.
🔥 Key potential benefits:
✅ Faster and more scalable dApps
✅ Reduced infrastructure costs
✅ Improved decentralization for AI workloads
✅ Enhanced blockchain-based automation
✅ Stronger integration between AI and Web3 ecosystems
Analysts believe decentralized computing could become one of the most important sectors of the next crypto cycle as AI demand continues exploding globally 🚀
The big question now:
Will decentralized AI infrastructure become the backbone of the future internet? 👀⚡️
#USAdds115kJobs #bitcoin
#Write2Earn #Binance #uxlink
$LINK
$W
$AI
179

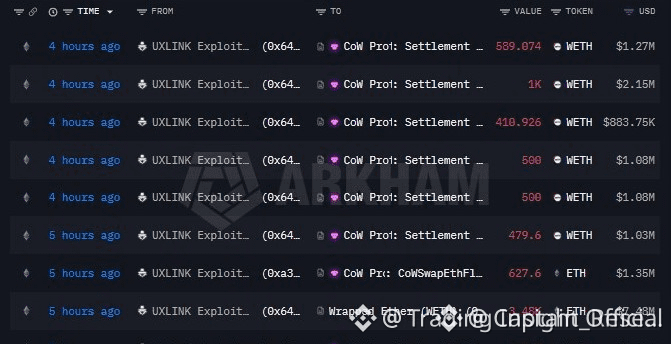
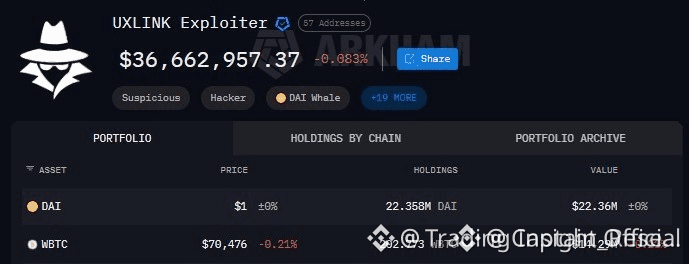
ETH ATTACKER TAKES PROFITS, BAGHOLDING WBTC 🚨 $ETH $WBTC
Entry: 2150 🔥
Target: N/A
Stop Loss: N/A
Whale unloading ETH on top-tier exchange after UXLINK exploit. Significant WBTC position underwater – 203 BTC bought at $83k now facing -2.68M USD loss. Expect potential cascading liquidations if BTC continues to slide. Monitor flow closely.
Not financial advice. Manage your risk.
#ETH #WBTC #DeFi #CryptoWhale #UXLINK
🚀
{spot}(WBTCUSDT)
{future}(ETHUSDT)
ETH ATTACKER TAKES PROFITS, BAGHOLDING WBTC 🚨 $ETH $WBTC
Entry: 2150 🔥
Target: N/A
Stop Loss: N/A
Whale unloading ETH on top-tier exchange after UXLINK exploit. Significant WBTC position underwater – 203 BTC bought at $83k now facing -2.68M USD loss. Expect potential cascading liquidations if BTC continues to slide. Monitor flow closely.
Not financial advice. Manage your risk.
#ETH #WBTC #DeFi #CryptoWhale #UXLINK
🚀
1
104
·
--
#bedrock $BR
The reason many folks are stepping back from DeFi isn’t just because they fear the risk.
It’s more like they’re trying to solve a puzzle under pressure.
Even simple BTC trades can rack up fees of a few bucks, but the real cost is the confusion. There are just too many steps. Too many unknowns. Way too much reliance on guesswork.
That’s why the real battlefield in BTCFi is becoming product design.
What matters isn’t bigger yields or grand promises. It’s about having a clear process: "Deposit → Transfer → Track."
When users can actually see where their funds are headed, anxiety turns into confidence.
But let’s be real. A top-notch UX doesn’t eliminate risk.
Slippage still happens. Liquidations are still a thing. The market remains highly volatile.
What changes is user behavior.
A user-friendly platform not only attracts users but also retains their funds.
Because in the long run, trust isn’t built on APY (Annual Percentage Yield).
Trust is built through understanding.
#BTCFi #DeFi #Crypto #Bedrock #uxlink
4
10
506

·
--
#uxlink This broken ticket has been stolen and will be taken down. Counter-pull explodes me! Sb Follow me and buy back, I am the beacon.
#uxlink This broken ticket has been stolen and will be taken down. Counter-pull explodes me! Sb Follow me and buy back, I am the beacon.
181
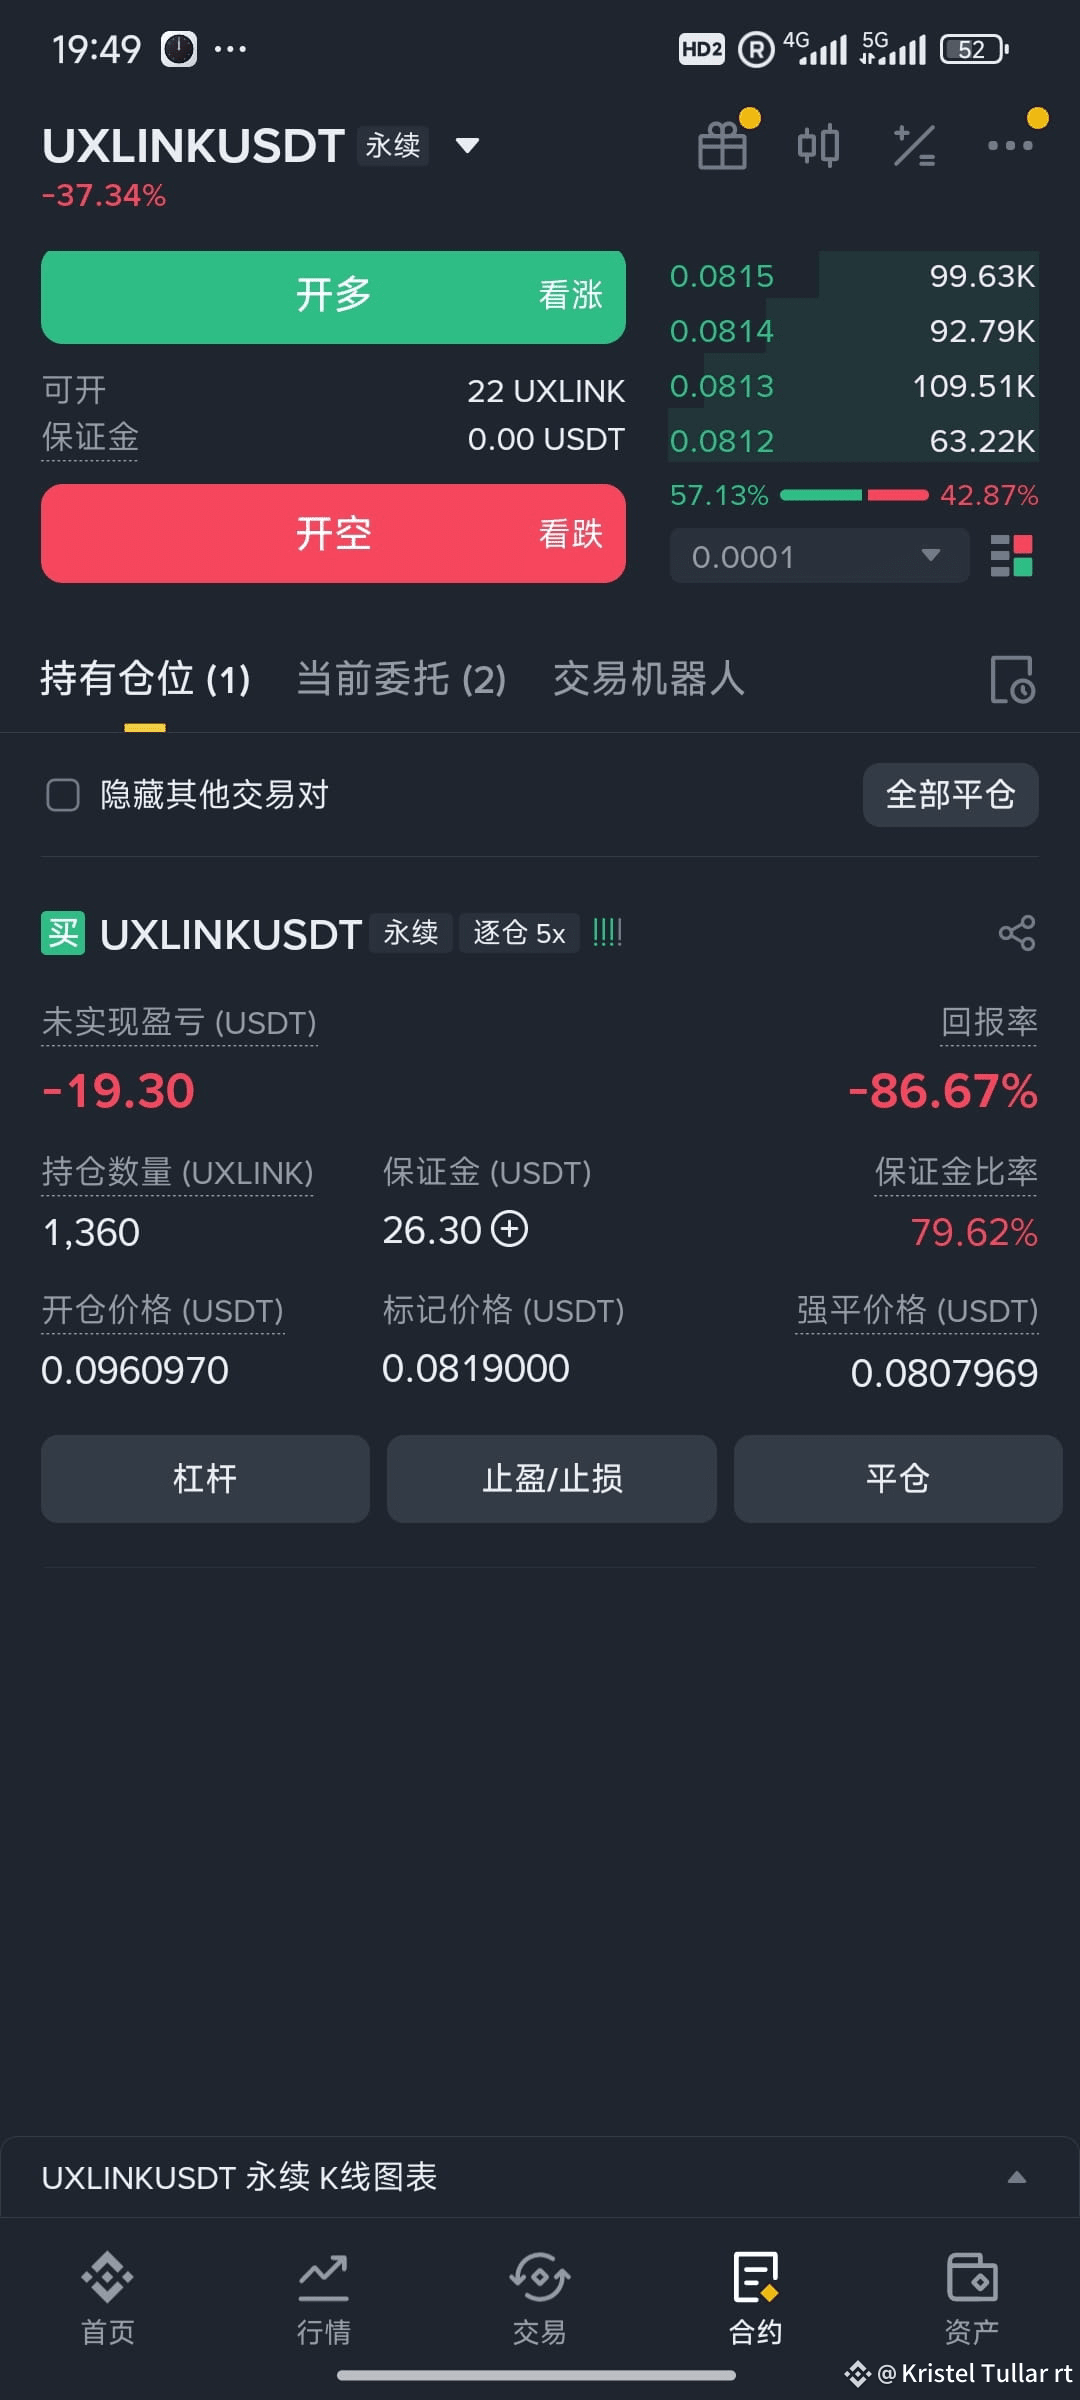
#uxlink This is about to explode, my 26 Us 😂
#uxlink This is about to explode, my 26 Us 😂
3
1
10
1.7k
·
--
Bullish
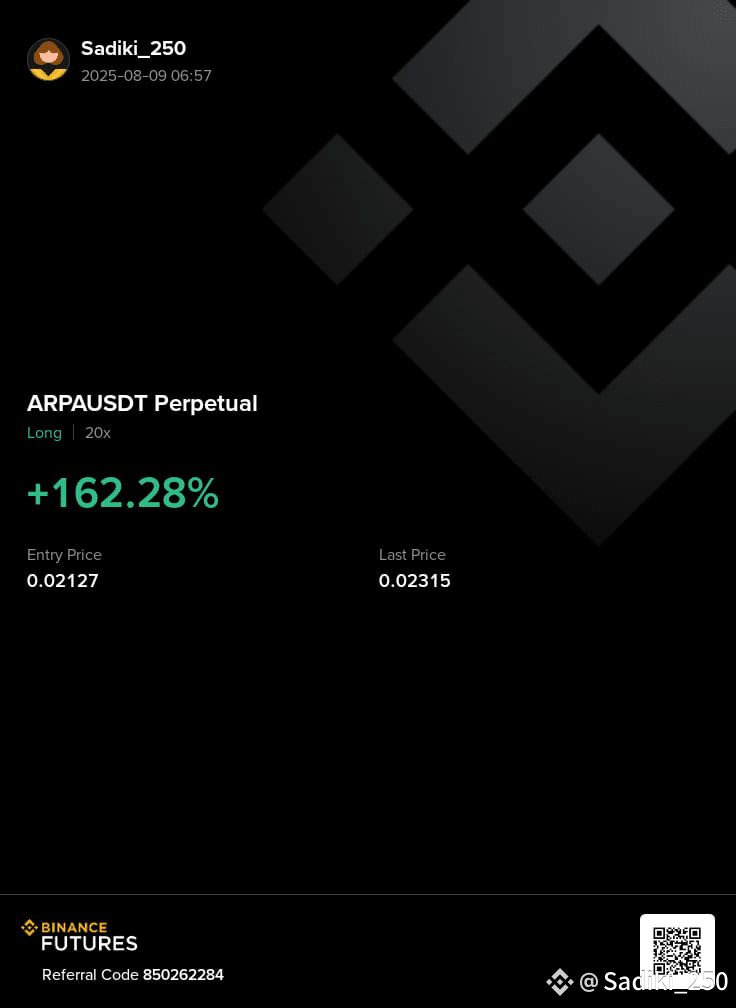
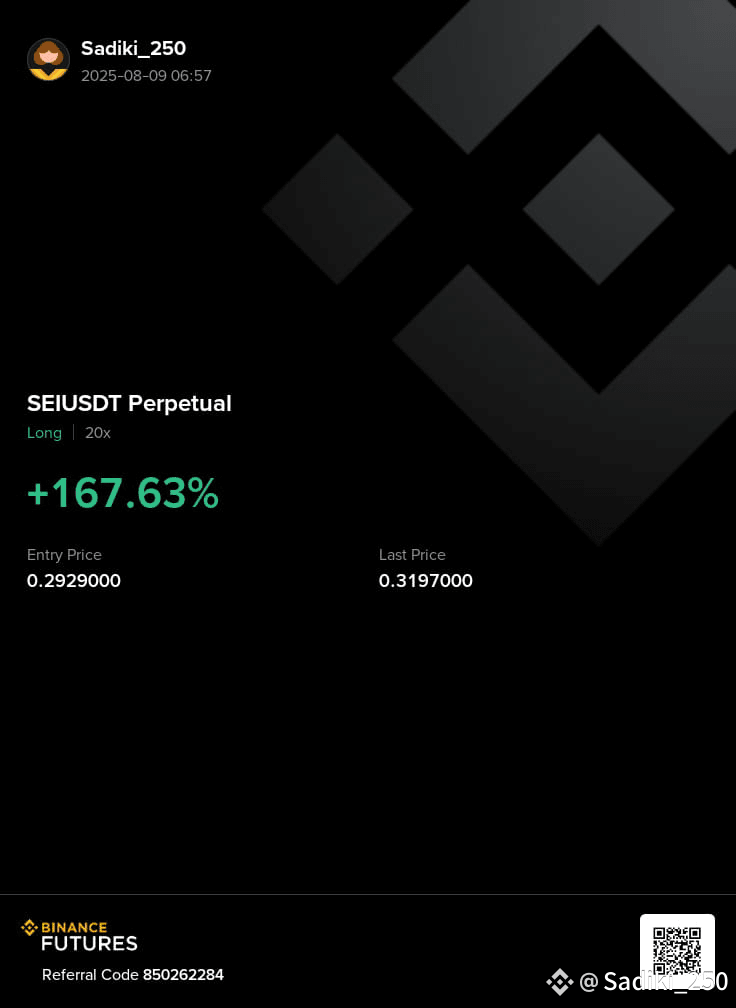
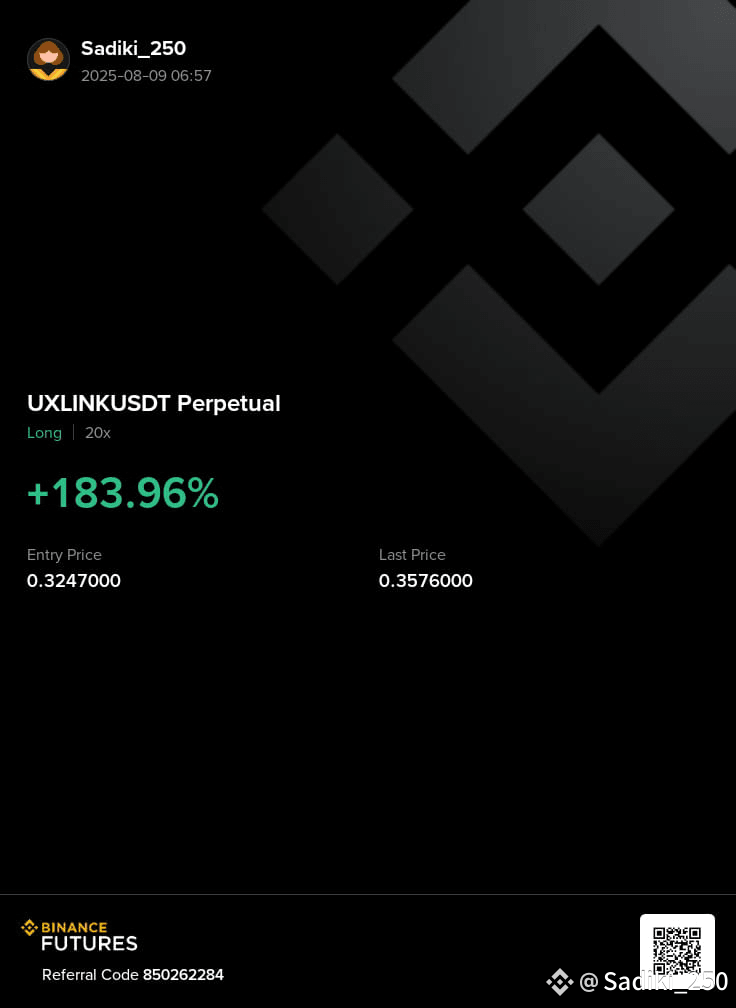
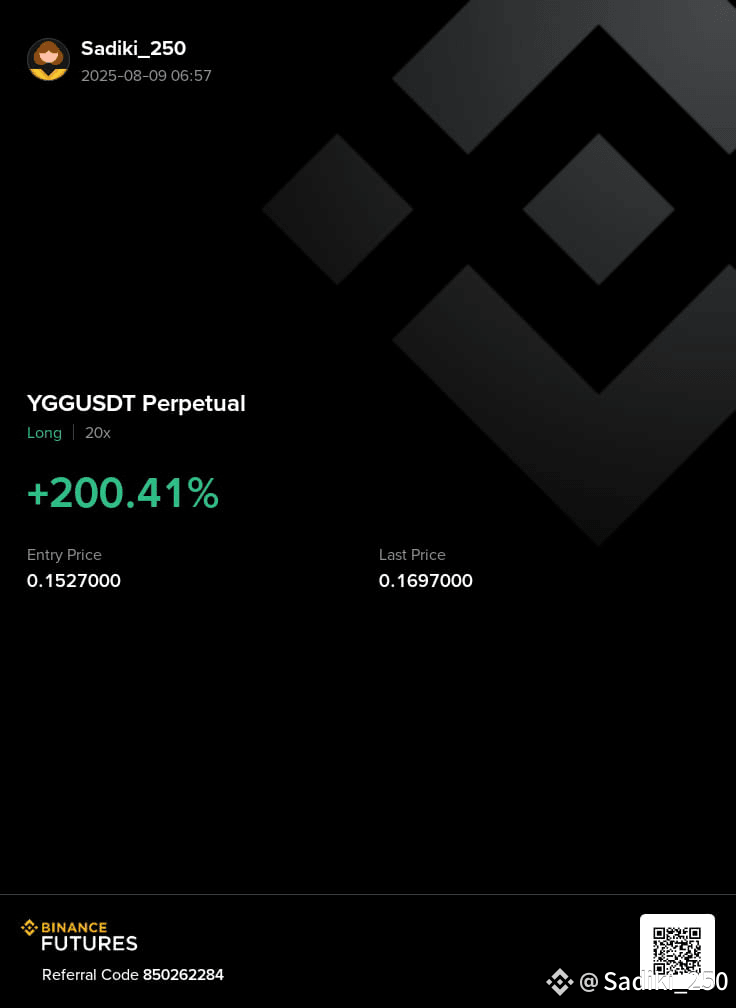
#ARPA/USDT #SEI/USDT #uxlink #YGG/USDT
pump hard.
#ARPA/USDT #SEI/USDT #uxlink #YGG/USDT
pump hard.
pump hard.
1
1.2k
·
--
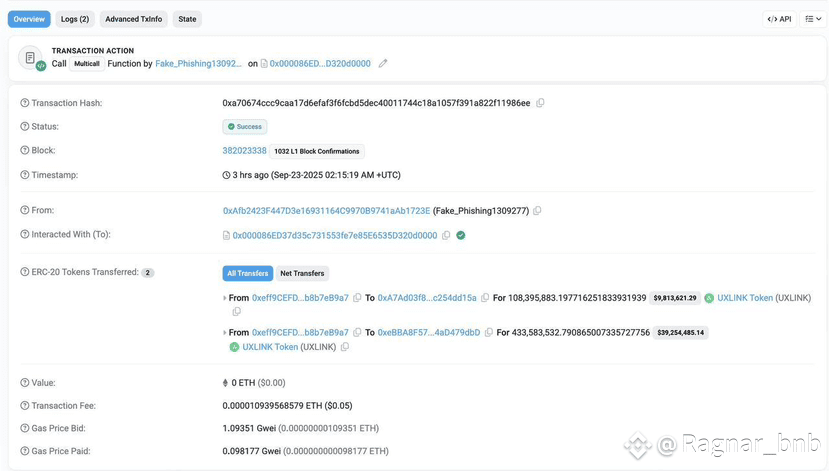
LOL🤡 the hacker who stole millions from UXLINK ended up losing 542 million tokens worth $48 million in a phishing scam.
The attacker who exploited UXLINK’s multi signature wallet then fell victim to a phishing scam that drained about 542 million UXLINK tokens, roughly $48 million in value according to on chain trackers and blockchain-analytics posts. On chain evidence shows the exploiter signed a malicious increaseAllowance approval that allowed the phishers to move the tokens, and security firms and trackers including Lookonchain and Scam Sniffer flagged the transactions and the outflows.
The incident followed an earlier breach that allowed the attacker to mint and dump billions of $UXLINK , which crashed the token price and triggered emergency responses from the UXLINK team and some exchanges to freeze suspicious deposits. Security researchers and commentators have pointed to Inferno Drainer style phishing tooling as a likely method used against the exploiter, and UXLINK has discussed remediation steps such as freezing funds and planning a token swap while investigations continue.
#UXLINK #UXLINKWalletBreach #news
1
1
11
6.4k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
3.4M views
164,520 Discussing
2
#EarningsSeason
5.5M views
26,872 Discussing
3
#StrategySkipsBitcoinPurchasesSpends$205MOnSTRCBuybacks
823 views
24 Discussing
4
#BitmineAdds10452ETH
9,255 views
219 Discussing
5
#SouthKoreaConsidersEducationTaxOnCryptoExchanges
7,508 views
204 Discussing
6
#OCCUrgesCommunityBanksToEnterStablecoinPayments
7,216 views
127 Discussing
7
#RippleWinsFullApprovalAsNationalTrustBank
6,634 views
131 Discussing
8
#AkashSelectsSolanaAsMigrationTarget
4,083 views
60 Discussing
9
#OndoToOpenSubscriptionsForOpenAIPreIPOTokenizedNotes
283 views
17 Discussing
10
#AnthropicTTMRevenueGrewAbout1200%
59,096 views
603 Discussing