
#bitcoincore
bitcoincore
20,008 views
159 Discussing
Hot
Latest

·
--
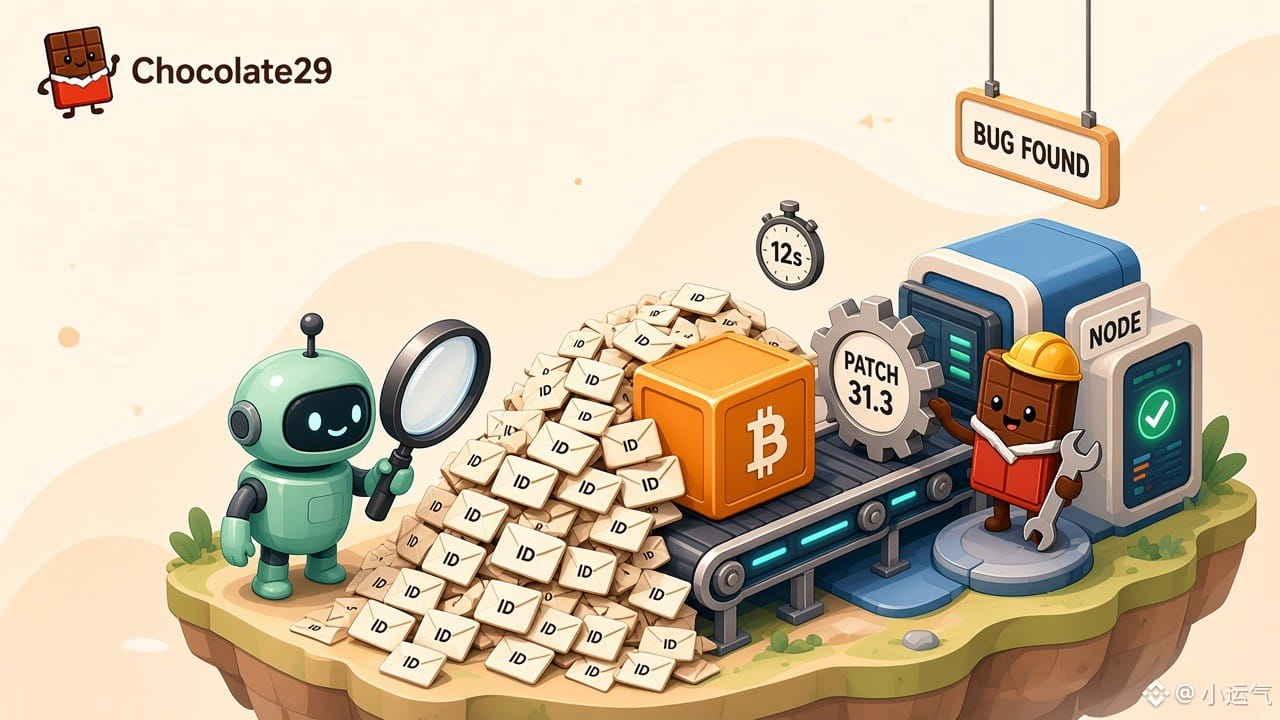
An AI-powered code scanner helped catch a Bitcoin Core bug that could freeze a node for more than 12 seconds at a time.
On November 20, 2026, Bitcoin Core disclosed CVE-2026-117348, rated medium severity, and released fixes in versions 30.5 and 31.3 (version 32.1 already carried the fix from October 27). An attacker could send an orphan transaction with thousands of missing parents, then repeat its ID up to 50,000 times in a single announcement. Each such message stalled the node for over a dozen seconds, and during that time it processed no blocks or transactions from other peers.
The flaw was first reported on July 8, 2026 by an automated LLM scan from Project Loupe at Spiral. Versions 29.0 through 31.2 are affected, and the end-of-life 29.x line will not get a patch, so anyone running $BTC nodes may want to check their version.
#Bitcoin #BitcoinCore #CryptoSecurity
DYOR. Not financial advice.
An AI-powered code scanner helped catch a Bitcoin Core bug that could freeze a node for more than 12 seconds at a time.
On November 20, 2026, Bitcoin Core disclosed CVE-2026-117348, rated medium severity, and released fixes in versions 30.5 and 31.3 (version 32.1 already carried the fix from October 27). An attacker could send an orphan transaction with thousands of missing parents, then repeat its ID up to 50,000 times in a single announcement. Each such message stalled the node for over a dozen seconds, and during that time it processed no blocks or transactions from other peers.
The flaw was first reported on July 8, 2026 by an automated LLM scan from Project Loupe at Spiral. Versions 29.0 through 31.2 are affected, and the end-of-life 29.x line will not get a patch, so anyone running $BTC nodes may want to check their version.
#Bitcoin #BitcoinCore #CryptoSecurity
DYOR. Not financial advice.
On November 20, 2026, Bitcoin Core disclosed CVE-2026-117348, rated medium severity, and released fixes in versions 30.5 and 31.3 (version 32.1 already carried the fix from October 27). An attacker could send an orphan transaction with thousands of missing parents, then repeat its ID up to 50,000 times in a single announcement. Each such message stalled the node for over a dozen seconds, and during that time it processed no blocks or transactions from other peers.
The flaw was first reported on July 8, 2026 by an automated LLM scan from Project Loupe at Spiral. Versions 29.0 through 31.2 are affected, and the end-of-life 29.x line will not get a patch, so anyone running $BTC nodes may want to check their version.
#Bitcoin #BitcoinCore #CryptoSecurity
DYOR. Not financial advice.
72

🚨 AI JUST UNLOCKED A RARE ZERO-DAY FLAW THAT COULD FREEZE $BTC NODES! 💥
Silicon intelligence is now stress-testing network architecture, exposing vulnerabilities long before manual audits catch them. 📊 Project Loupe just flagged an AI-discovered exploit where a single transaction ID spammed fifty thousand times could temporarily freeze unpatched $BTC nodes. ⚡
Bitcoin Core moved swiftly to ship fixes in versions thirty point five and thirty-one point three, neutralizing the threat before bad actors could weaponize it at scale. 💡 Node operators must upgrade immediately to protect exchange deposits and ensure uninterrupted ledger synchronization. 📌
Are you running an updated node version, or are you still vulnerable to automated network stress tests? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
🚨 AI JUST UNLOCKED A RARE ZERO-DAY FLAW THAT COULD FREEZE $BTC NODES! 💥
Silicon intelligence is now stress-testing network architecture, exposing vulnerabilities long before manual audits catch them. 📊 Project Loupe just flagged an AI-discovered exploit where a single transaction ID spammed fifty thousand times could temporarily freeze unpatched $BTC nodes. ⚡
Bitcoin Core moved swiftly to ship fixes in versions thirty point five and thirty-one point three, neutralizing the threat before bad actors could weaponize it at scale. 💡 Node operators must upgrade immediately to protect exchange deposits and ensure uninterrupted ledger synchronization. 📌
Are you running an updated node version, or are you still vulnerable to automated network stress tests? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
Silicon intelligence is now stress-testing network architecture, exposing vulnerabilities long before manual audits catch them. 📊 Project Loupe just flagged an AI-discovered exploit where a single transaction ID spammed fifty thousand times could temporarily freeze unpatched $BTC nodes. ⚡
Bitcoin Core moved swiftly to ship fixes in versions thirty point five and thirty-one point three, neutralizing the threat before bad actors could weaponize it at scale. 💡 Node operators must upgrade immediately to protect exchange deposits and ensure uninterrupted ledger synchronization. 📌
Are you running an updated node version, or are you still vulnerable to automated network stress tests? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
7
🚨 $BTC NETWORK RESILIENCE TESTED AS CRITICAL NODE VULNERABILITY IS PATCHED 🛡️
Network integrity forms the bedrock of institutional confidence in $BTC . 📊 Recent telemetry analysis highlights how automated machine learning scans flagged a node-stalling vector that could temporarily disrupt block propagation and delay top-tier exchange deposits.
Prompt action from development teams deployed patches across recent versions to seal this structural inefficiency before market participants experienced execution friction. Maintaining a robust, decentralized node topology remains paramount for safeguarding transactional finality and ensuring uninterrupted liquidity flow. 🌊
💡 Are node operators upgrading their infrastructure fast enough to protect network consensus? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
🚨 $BTC NETWORK RESILIENCE TESTED AS CRITICAL NODE VULNERABILITY IS PATCHED 🛡️
Network integrity forms the bedrock of institutional confidence in $BTC . 📊 Recent telemetry analysis highlights how automated machine learning scans flagged a node-stalling vector that could temporarily disrupt block propagation and delay top-tier exchange deposits.
Prompt action from development teams deployed patches across recent versions to seal this structural inefficiency before market participants experienced execution friction. Maintaining a robust, decentralized node topology remains paramount for safeguarding transactional finality and ensuring uninterrupted liquidity flow. 🌊
💡 Are node operators upgrading their infrastructure fast enough to protect network consensus? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
Network integrity forms the bedrock of institutional confidence in $BTC . 📊 Recent telemetry analysis highlights how automated machine learning scans flagged a node-stalling vector that could temporarily disrupt block propagation and delay top-tier exchange deposits.
Prompt action from development teams deployed patches across recent versions to seal this structural inefficiency before market participants experienced execution friction. Maintaining a robust, decentralized node topology remains paramount for safeguarding transactional finality and ensuring uninterrupted liquidity flow. 🌊
💡 Are node operators upgrading their infrastructure fast enough to protect network consensus? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
24


·
--
🐞 AI-found bug could stall Bitcoin nodes; Bitcoin Core ships fixes
An AI scan by Project Loupe at Spiral, the open-source unit of Jack Dorsey's Block, found that a Bitcoin node could be frozen by announcing a single transaction ID 50,000 times. Each such message stalls a node for over a dozen seconds, during which it processes nothing from peers, including new blocks. Bitcoin Core rated the flaw medium severity, disclosed it as CVE-2026-117348 and shipped fixes in versions 30.5 and 31.3.
⭐ Unpatched nodes could delay exchange deposits or leave miners working on a stale chain view, and AI is making such bugs cheaper to rediscover, so operators have good reason to upgrade fast.
#Bitcoin #BitcoinCore #CyberSecurity #AI
🐞 AI-found bug could stall Bitcoin nodes; Bitcoin Core ships fixes
An AI scan by Project Loupe at Spiral, the open-source unit of Jack Dorsey's Block, found that a Bitcoin node could be frozen by announcing a single transaction ID 50,000 times. Each such message stalls a node for over a dozen seconds, during which it processes nothing from peers, including new blocks. Bitcoin Core rated the flaw medium severity, disclosed it as CVE-2026-117348 and shipped fixes in versions 30.5 and 31.3.
⭐ Unpatched nodes could delay exchange deposits or leave miners working on a stale chain view, and AI is making such bugs cheaper to rediscover, so operators have good reason to upgrade fast.
#Bitcoin #BitcoinCore #CyberSecurity #AI
An AI scan by Project Loupe at Spiral, the open-source unit of Jack Dorsey's Block, found that a Bitcoin node could be frozen by announcing a single transaction ID 50,000 times. Each such message stalls a node for over a dozen seconds, during which it processes nothing from peers, including new blocks. Bitcoin Core rated the flaw medium severity, disclosed it as CVE-2026-117348 and shipped fixes in versions 30.5 and 31.3.
⭐ Unpatched nodes could delay exchange deposits or leave miners working on a stale chain view, and AI is making such bugs cheaper to rediscover, so operators have good reason to upgrade fast.
#Bitcoin #BitcoinCore #CyberSecurity #AI
42

·
--
Bitcoin Core has just patched a vulnerability that could make nodes stop processing messages — and it was found by an AI scanner.
The facts: Bitcoin Core disclosed CVE-2026-117348 on Friday, Nov. 20, 2026, with a medium severity rating. An attacker could repeat the same transaction ID up to 50,000 times in a single orphan-transaction announcement batch, causing a node to freeze for more than 10 seconds and preventing it from processing blocks or other transactions. Fixes have been released in versions 30.5, 31.3, and 32.1. Nodes still running versions 29.0–31.2 must upgrade; the 29.x series is end-of-life and will not receive a patch. The vulnerability was found by Project Loupe, an AI scanner from Spiral, Block’s open-source unit.
My take: this isn’t a vulnerability that steals coins — but repeatedly freezing nodes could delay deposit credits at exchanges and leave miners working with stale data. What I find interesting is how it was handled: under the policy introduced on Oct. 22, vulnerabilities that are easy to find are fixed publicly alongside their patches, rather than being hidden for months. With BTC hovering around 58,070 this afternoon, this is a reminder that network security is also part of the price — not just ETF flows and liquidations.
What I’m watching next: how quickly major node operators upgrade to the patched versions, and whether reports of exploitation emerge before the patch is widely deployed.
How quickly do you think major node operators usually upgrade after a patch like this?
This is my analysis, not financial advice — always DYOR.
#Bitcoin #BitcoinCore $BTC
Bitcoin Core has just patched a vulnerability that could make nodes stop processing messages — and it was found by an AI scanner.
The facts: Bitcoin Core disclosed CVE-2026-117348 on Friday, Nov. 20, 2026, with a medium severity rating. An attacker could repeat the same transaction ID up to 50,000 times in a single orphan-transaction announcement batch, causing a node to freeze for more than 10 seconds and preventing it from processing blocks or other transactions. Fixes have been released in versions 30.5, 31.3, and 32.1. Nodes still running versions 29.0–31.2 must upgrade; the 29.x series is end-of-life and will not receive a patch. The vulnerability was found by Project Loupe, an AI scanner from Spiral, Block’s open-source unit.
My take: this isn’t a vulnerability that steals coins — but repeatedly freezing nodes could delay deposit credits at exchanges and leave miners working with stale data. What I find interesting is how it was handled: under the policy introduced on Oct. 22, vulnerabilities that are easy to find are fixed publicly alongside their patches, rather than being hidden for months. With BTC hovering around 58,070 this afternoon, this is a reminder that network security is also part of the price — not just ETF flows and liquidations.
What I’m watching next: how quickly major node operators upgrade to the patched versions, and whether reports of exploitation emerge before the patch is widely deployed.
How quickly do you think major node operators usually upgrade after a patch like this?
This is my analysis, not financial advice — always DYOR.
#Bitcoin #BitcoinCore $BTC
The facts: Bitcoin Core disclosed CVE-2026-117348 on Friday, Nov. 20, 2026, with a medium severity rating. An attacker could repeat the same transaction ID up to 50,000 times in a single orphan-transaction announcement batch, causing a node to freeze for more than 10 seconds and preventing it from processing blocks or other transactions. Fixes have been released in versions 30.5, 31.3, and 32.1. Nodes still running versions 29.0–31.2 must upgrade; the 29.x series is end-of-life and will not receive a patch. The vulnerability was found by Project Loupe, an AI scanner from Spiral, Block’s open-source unit.
My take: this isn’t a vulnerability that steals coins — but repeatedly freezing nodes could delay deposit credits at exchanges and leave miners working with stale data. What I find interesting is how it was handled: under the policy introduced on Oct. 22, vulnerabilities that are easy to find are fixed publicly alongside their patches, rather than being hidden for months. With BTC hovering around 58,070 this afternoon, this is a reminder that network security is also part of the price — not just ETF flows and liquidations.
What I’m watching next: how quickly major node operators upgrade to the patched versions, and whether reports of exploitation emerge before the patch is widely deployed.
How quickly do you think major node operators usually upgrade after a patch like this?
This is my analysis, not financial advice — always DYOR.
#Bitcoin #BitcoinCore $BTC
35

·
--
Bearish
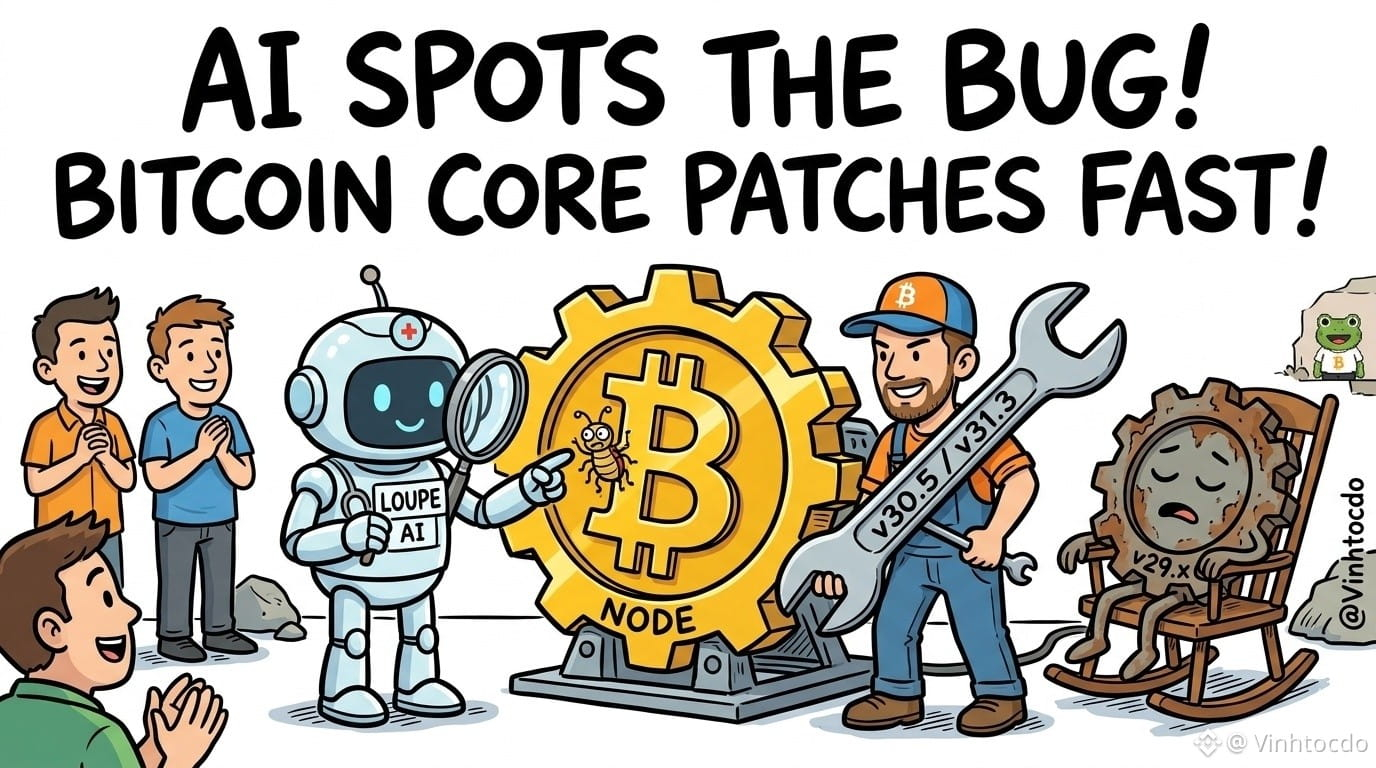
AI SPOTS A BUG, BITCOIN CORE RUSHES OUT A PATCH! 🛠️🤖
#BitcoinCore just released updates 30.5 and 31.3 to fully fix a medium-severity vulnerability. Specifically, Spiral’s Loupe AI tool caught the bug red-handed, which could leave network nodes at risk of getting stuck mid-operation. Notably, the old 29.x branch has been retired, so there won’t be a patch for it!
Luckily, this time AI played the role of a “doctor,” diagnosing the problem and saving the network in time instead of “ratting out” the community!
What should traders do? Stay calm and keep a steady hand! If you’re running your own node, upgrade to 30.5 or 31.3 right away. If you’re just trading as usual, stick to your risk management rules and avoid unnecessary FUD over technical news.
This is not financial advice.
#Bitcoin #CryptoSecurity #BTC #AI #CryptoNews #VINHTOCDO
👇 Click below to trade and support me: $BTC
{future}(BTCUSDT)
$BNB
{future}(BNBUSDT)
$EVAA
{future}(EVAAUSDT)
AI SPOTS A BUG, BITCOIN CORE RUSHES OUT A PATCH! 🛠️🤖
#BitcoinCore just released updates 30.5 and 31.3 to fully fix a medium-severity vulnerability. Specifically, Spiral’s Loupe AI tool caught the bug red-handed, which could leave network nodes at risk of getting stuck mid-operation. Notably, the old 29.x branch has been retired, so there won’t be a patch for it!
Luckily, this time AI played the role of a “doctor,” diagnosing the problem and saving the network in time instead of “ratting out” the community!
What should traders do? Stay calm and keep a steady hand! If you’re running your own node, upgrade to 30.5 or 31.3 right away. If you’re just trading as usual, stick to your risk management rules and avoid unnecessary FUD over technical news.
This is not financial advice.
#Bitcoin #CryptoSecurity #BTC #AI #CryptoNews #VINHTOCDO
👇 Click below to trade and support me: $BTC
$BNB
$EVAA
#BitcoinCore just released updates 30.5 and 31.3 to fully fix a medium-severity vulnerability. Specifically, Spiral’s Loupe AI tool caught the bug red-handed, which could leave network nodes at risk of getting stuck mid-operation. Notably, the old 29.x branch has been retired, so there won’t be a patch for it!
Luckily, this time AI played the role of a “doctor,” diagnosing the problem and saving the network in time instead of “ratting out” the community!
What should traders do? Stay calm and keep a steady hand! If you’re running your own node, upgrade to 30.5 or 31.3 right away. If you’re just trading as usual, stick to your risk management rules and avoid unnecessary FUD over technical news.
This is not financial advice.
#Bitcoin #CryptoSecurity #BTC #AI #CryptoNews #VINHTOCDO
👇 Click below to trade and support me: $BTC
$BNB
$EVAA
6
1.2k

·
--
Article
Bitcoin Core discloses a Tor permission vulnerability: it affects node configuration, not BTC consensusBitcoin Core discloses a Tor permission vulnerability: it affects node configuration, not BTC consensus
In a public snapshot of Binance Square's regional trends page, “Bitcoin Core discloses Tor traffic vulnerability” showed around 433 people discussing it. This is only the visible discussion count on that page, not a site-wide statistic. Still, the topic is worth a look because it puts “node software risk” and “BTC price risk” on the same table.
Bottom line: The CVE-2025-62860 disclosed by Bitcoin Core is a medium-severity, configuration-dependent inbound Tor permission error. It does not mean the BTC consensus layer has been compromised, nor that BTC holders have somehow lost coins. The official announcement says that in certain versions, when a non-default `-whitelist` is used and the Tor daemon's address falls within the whitelisted range, inbound Tor connections may be mistakenly treated as trusted connections, disabling some DoS restrictions and privacy leak mitigations. Nodes that have not set this non-default option are unaffected.
Bitcoin Core discloses a Tor permission vulnerability: it affects node configuration, not BTC consensus
Bitcoin Core discloses a Tor permission vulnerability: it affects node configuration, not BTC consensus
In a public snapshot of Binance Square's regional trends page, “Bitcoin Core discloses Tor traffic vulnerability” showed around 433 people discussing it. This is only the visible discussion count on that page, not a site-wide statistic. Still, the topic is worth a look because it puts “node software risk” and “BTC price risk” on the same table.
Bottom line: The CVE-2025-62860 disclosed by Bitcoin Core is a medium-severity, configuration-dependent inbound Tor permission error. It does not mean the BTC consensus layer has been compromised, nor that BTC holders have somehow lost coins. The official announcement says that in certain versions, when a non-default `-whitelist` is used and the Tor daemon's address falls within the whitelisted range, inbound Tor connections may be mistakenly treated as trusted connections, disabling some DoS restrictions and privacy leak mitigations. Nodes that have not set this non-default option are unaffected.
In a public snapshot of Binance Square's regional trends page, “Bitcoin Core discloses Tor traffic vulnerability” showed around 433 people discussing it. This is only the visible discussion count on that page, not a site-wide statistic. Still, the topic is worth a look because it puts “node software risk” and “BTC price risk” on the same table.
Bottom line: The CVE-2025-62860 disclosed by Bitcoin Core is a medium-severity, configuration-dependent inbound Tor permission error. It does not mean the BTC consensus layer has been compromised, nor that BTC holders have somehow lost coins. The official announcement says that in certain versions, when a non-default `-whitelist` is used and the Tor daemon's address falls within the whitelisted range, inbound Tor connections may be mistakenly treated as trusted connections, disabling some DoS restrictions and privacy leak mitigations. Nodes that have not set this non-default option are unaffected.
124
·
--
#bitcoincoredisclosestortrafficvulnerability
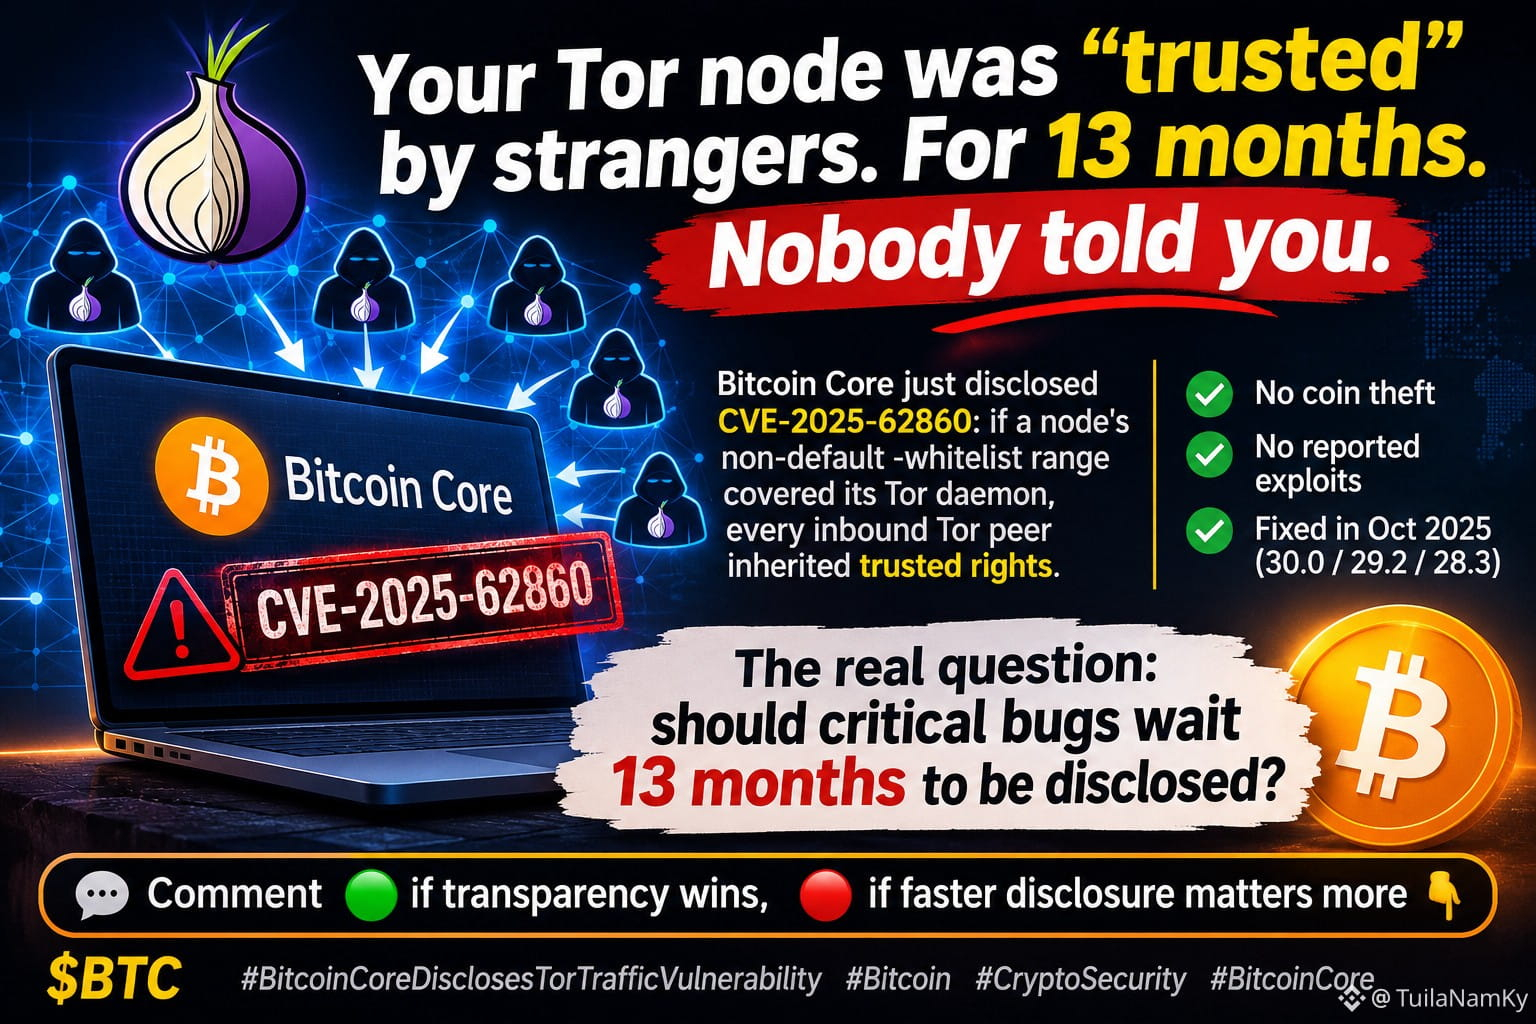
🧅 Your Tor node was "trusted" by strangers. For 13 months. Nobody told you.
Bitcoin Core just disclosed CVE-2025-62860: if a node's non-default -whitelist range covered its Tor daemon, every inbound Tor peer inherited trusted rights.
✅ No coin theft
✅ No reported exploits
✅ Fixed in Oct 2025 (30.0 / 29.2 / 28.3)
The real question: should critical bugs wait 13 months to be disclosed?
Comment 🟢 if transparency wins, 🔴 if faster disclosure matters more 👇
$BTC
{future}(BTCUSDT)
#Bitcoin #CryptoSecurity #BitcoinCore
#bitcoincoredisclosestortrafficvulnerability
🧅 Your Tor node was "trusted" by strangers. For 13 months. Nobody told you.
Bitcoin Core just disclosed CVE-2025-62860: if a node's non-default -whitelist range covered its Tor daemon, every inbound Tor peer inherited trusted rights.
✅ No coin theft
✅ No reported exploits
✅ Fixed in Oct 2025 (30.0 / 29.2 / 28.3)
The real question: should critical bugs wait 13 months to be disclosed?
Comment 🟢 if transparency wins, 🔴 if faster disclosure matters more 👇
$BTC
#Bitcoin #CryptoSecurity #BitcoinCore
🧅 Your Tor node was "trusted" by strangers. For 13 months. Nobody told you.
Bitcoin Core just disclosed CVE-2025-62860: if a node's non-default -whitelist range covered its Tor daemon, every inbound Tor peer inherited trusted rights.
✅ No coin theft
✅ No reported exploits
✅ Fixed in Oct 2025 (30.0 / 29.2 / 28.3)
The real question: should critical bugs wait 13 months to be disclosed?
Comment 🟢 if transparency wins, 🔴 if faster disclosure matters more 👇
$BTC
#Bitcoin #CryptoSecurity #BitcoinCore
2
177
·
--
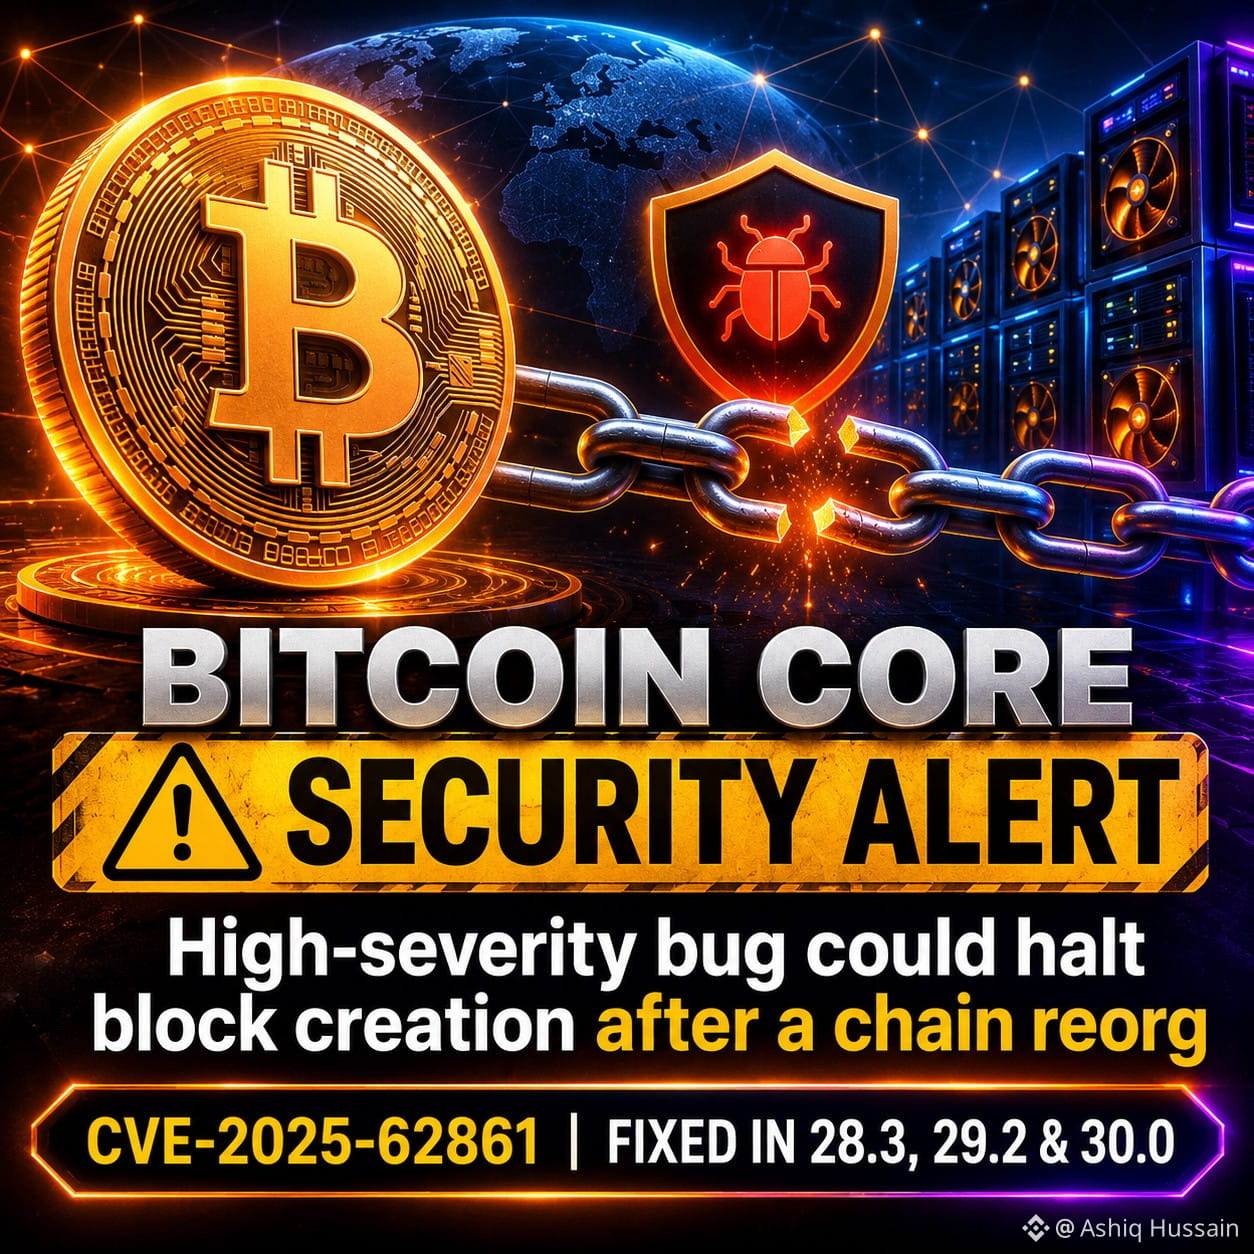
🚨 $BTC CORE SECURITY ALERT! ⚠️
A high-severity vulnerability has been disclosed in Bitcoin Core.
🔴 What happened?
The bug (CVE-2025-62861) could cause affected mining nodes to stop creating valid block templates after a blockchain reorganization.
⚠️ Affected versions:
- Bitcoin Core 28.0–28.2
- Bitcoin Core 29.0–29.1
✅ Fixed versions:
- 28.3
- 29.2
- 30.0
🔐 Important: This issue was already fixed in October 2025 and publicly disclosed on November 10, 2026. It does not directly compromise Bitcoin's consensus rules or user funds.
💡 Node operators should upgrade to a maintained Bitcoin Core release.
{spot}(BTCUSDT)
#Bitcoin $BTC #BitcoinCore #CryptoSecurity #Blockchain #BinanceSquare
🚨 $BTC CORE SECURITY ALERT! ⚠️
A high-severity vulnerability has been disclosed in Bitcoin Core.
🔴 What happened?
The bug (CVE-2025-62861) could cause affected mining nodes to stop creating valid block templates after a blockchain reorganization.
⚠️ Affected versions:
- Bitcoin Core 28.0–28.2
- Bitcoin Core 29.0–29.1
✅ Fixed versions:
- 28.3
- 29.2
- 30.0
🔐 Important: This issue was already fixed in October 2025 and publicly disclosed on November 10, 2026. It does not directly compromise Bitcoin's consensus rules or user funds.
💡 Node operators should upgrade to a maintained Bitcoin Core release.
#Bitcoin $BTC #BitcoinCore #CryptoSecurity #Blockchain #BinanceSquare
A high-severity vulnerability has been disclosed in Bitcoin Core.
🔴 What happened?
The bug (CVE-2025-62861) could cause affected mining nodes to stop creating valid block templates after a blockchain reorganization.
⚠️ Affected versions:
- Bitcoin Core 28.0–28.2
- Bitcoin Core 29.0–29.1
✅ Fixed versions:
- 28.3
- 29.2
- 30.0
🔐 Important: This issue was already fixed in October 2025 and publicly disclosed on November 10, 2026. It does not directly compromise Bitcoin's consensus rules or user funds.
💡 Node operators should upgrade to a maintained Bitcoin Core release.
#Bitcoin $BTC #BitcoinCore #CryptoSecurity #Blockchain #BinanceSquare
158
·
--
#比特币Core披露Tor流量漏洞
A tech explainer: What exactly is this “Tor vulnerability”? Explained in one sentence
$BTC A lot of people panicked when they saw “Bitcoin Core discloses Tor vulnerability.” Don’t rush to judgment—first get the timeline straight.
Vulnerability ID: CVE-2025-62860. The core issue in one sentence: when service providers bundle Bitcoin Core with Tor, incoming Tor traffic is mistakenly classified as “local traffic.” If you have -whitelist enabled and the IP range includes your local Tor proxy, strangers connecting from outside via Tor inherit the permissions you grant to “trusted local nodes,” while spam protections and privacy restrictions are relaxed.
Key facts:
· Fixed versions: 30.0 / 29.2 / 28.3, released back in October 2025
· Public disclosure: November 10, 2026, two weeks after the last affected 29.x series reached end of life
· Nodes that did not enable -whitelist were never affected
This isn’t a “brand-new vulnerability that just appeared today.” It’s a routine disclosure more than a year after the patch was released. Public disclosure ≠ new risk—don’t let the headlines sway you.
#BitcoinCore #安全
#比特币Core披露Tor流量漏洞
A tech explainer: What exactly is this “Tor vulnerability”? Explained in one sentence
$BTC A lot of people panicked when they saw “Bitcoin Core discloses Tor vulnerability.” Don’t rush to judgment—first get the timeline straight.
Vulnerability ID: CVE-2025-62860. The core issue in one sentence: when service providers bundle Bitcoin Core with Tor, incoming Tor traffic is mistakenly classified as “local traffic.” If you have -whitelist enabled and the IP range includes your local Tor proxy, strangers connecting from outside via Tor inherit the permissions you grant to “trusted local nodes,” while spam protections and privacy restrictions are relaxed.
Key facts:
· Fixed versions: 30.0 / 29.2 / 28.3, released back in October 2025
· Public disclosure: November 10, 2026, two weeks after the last affected 29.x series reached end of life
· Nodes that did not enable -whitelist were never affected
This isn’t a “brand-new vulnerability that just appeared today.” It’s a routine disclosure more than a year after the patch was released. Public disclosure ≠ new risk—don’t let the headlines sway you.
#BitcoinCore #安全
A tech explainer: What exactly is this “Tor vulnerability”? Explained in one sentence
$BTC A lot of people panicked when they saw “Bitcoin Core discloses Tor vulnerability.” Don’t rush to judgment—first get the timeline straight.
Vulnerability ID: CVE-2025-62860. The core issue in one sentence: when service providers bundle Bitcoin Core with Tor, incoming Tor traffic is mistakenly classified as “local traffic.” If you have -whitelist enabled and the IP range includes your local Tor proxy, strangers connecting from outside via Tor inherit the permissions you grant to “trusted local nodes,” while spam protections and privacy restrictions are relaxed.
Key facts:
· Fixed versions: 30.0 / 29.2 / 28.3, released back in October 2025
· Public disclosure: November 10, 2026, two weeks after the last affected 29.x series reached end of life
· Nodes that did not enable -whitelist were never affected
This isn’t a “brand-new vulnerability that just appeared today.” It’s a routine disclosure more than a year after the patch was released. Public disclosure ≠ new risk—don’t let the headlines sway you.
#BitcoinCore #安全
230
·
--
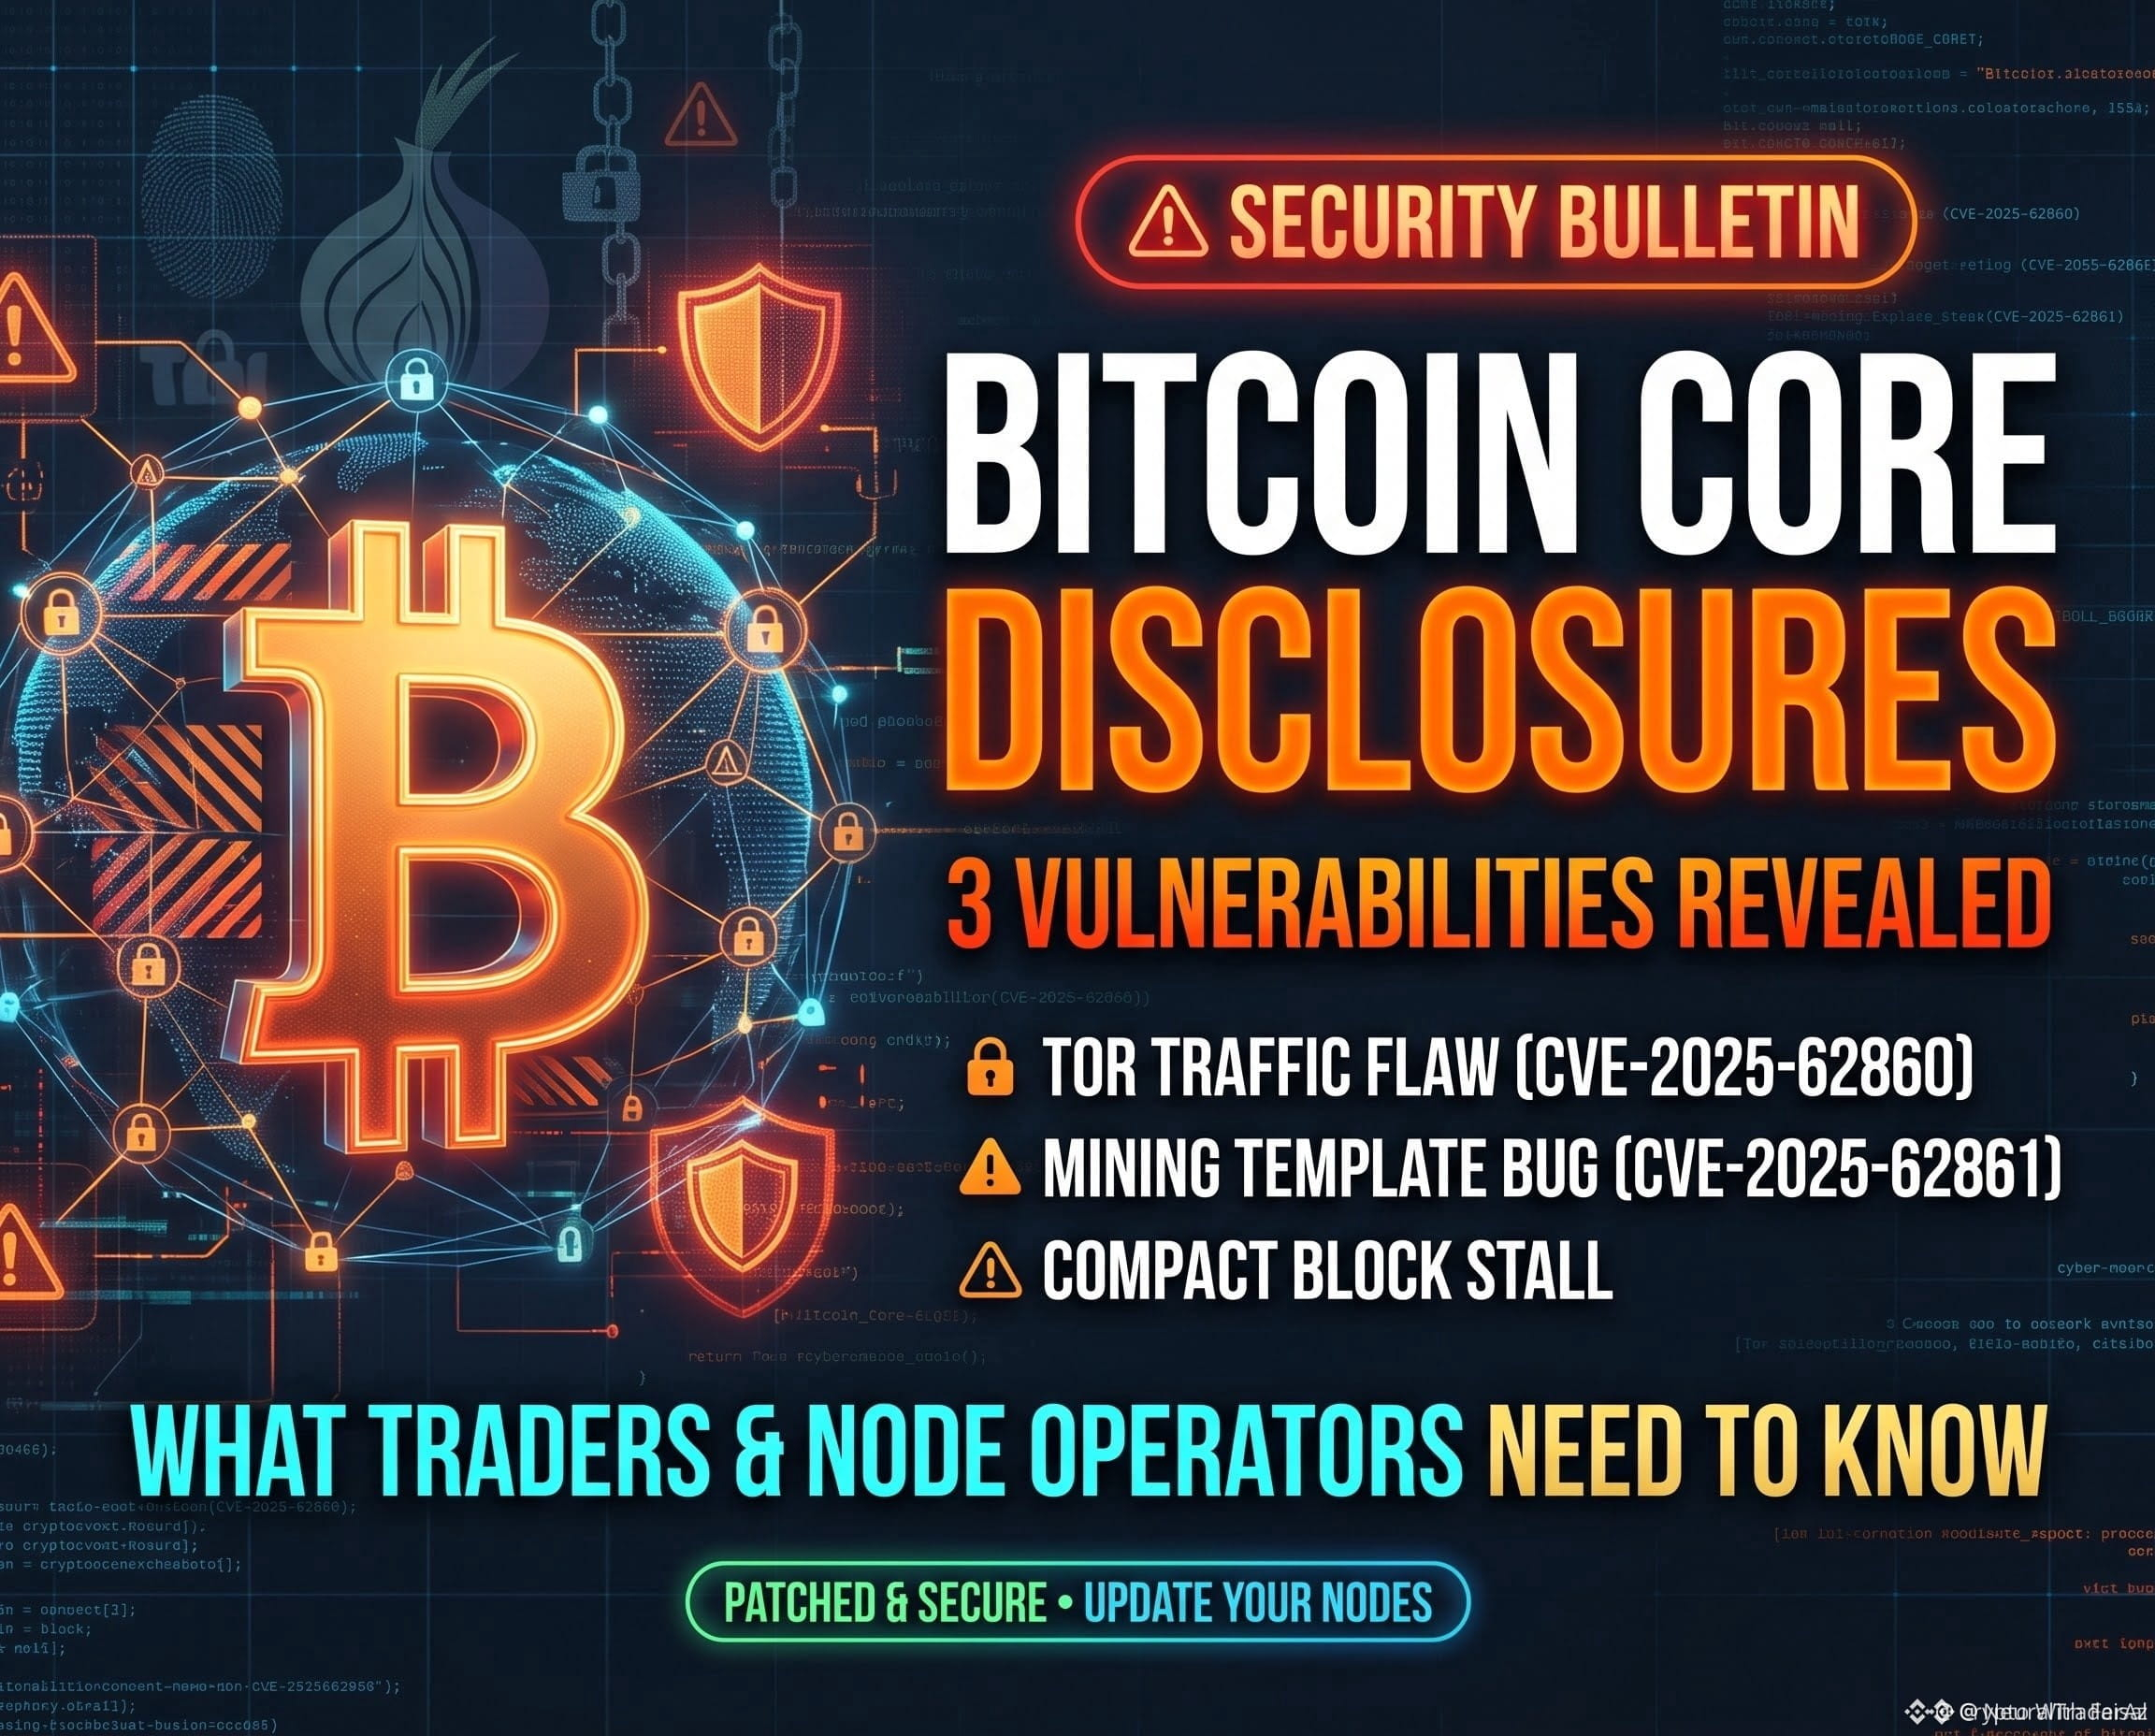
#BitcoinCoreDisclosesTorTrafficVulnerability Don’t panic over the Tor bug news. The real story is “delay,” not “danger.” 🧅
Bitcoin Core disclosed 3 patched vulnerabilities. “Thousands” of reachable mainnet nodes were whitelisting incoming Tor connections, which removed some DoS limits and privacy protections. Nodes that didn’t have this non-default setting were not affected. (theblock)
The truth about the timeline:
✅ The fix was included in Bitcoin Core 30.0 (Oct 10, 2025) and 29.2 (Oct 14, 2025). The last vulnerable version reached end-of-life on Oct 27, 2026.
✅ The project ships the fix first, then shares the vulnerability details later.
⚠️ This is not an issue with consensus rules. The risk was to node privacy and reliability, not to coins or the Bitcoin protocol. (theblock) (cryptovalleyjournal)
My analysis: This is a textbook example of “responsible disclosure.” First the patch, then time for users to upgrade, and only then a public advisory. That’s the power of open source: a bug is found, fixed, and later everything is made public. But there’s a lesson here too: operators running old node versions should upgrade now.
(Not financial advice, DYOR.)
Do you run your own node, or do you trust an exchange/custodian? Why? 👇
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin❗ #Tor #BitcoinCore
#BitcoinCoreDisclosesTorTrafficVulnerability Don’t panic over the Tor bug news. The real story is “delay,” not “danger.” 🧅
Bitcoin Core disclosed 3 patched vulnerabilities. “Thousands” of reachable mainnet nodes were whitelisting incoming Tor connections, which removed some DoS limits and privacy protections. Nodes that didn’t have this non-default setting were not affected. (theblock)
The truth about the timeline:
✅ The fix was included in Bitcoin Core 30.0 (Oct 10, 2025) and 29.2 (Oct 14, 2025). The last vulnerable version reached end-of-life on Oct 27, 2026.
✅ The project ships the fix first, then shares the vulnerability details later.
⚠️ This is not an issue with consensus rules. The risk was to node privacy and reliability, not to coins or the Bitcoin protocol. (theblock) (cryptovalleyjournal)
My analysis: This is a textbook example of “responsible disclosure.” First the patch, then time for users to upgrade, and only then a public advisory. That’s the power of open source: a bug is found, fixed, and later everything is made public. But there’s a lesson here too: operators running old node versions should upgrade now.
(Not financial advice, DYOR.)
Do you run your own node, or do you trust an exchange/custodian? Why? 👇
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin❗ #Tor #BitcoinCore
Bitcoin Core disclosed 3 patched vulnerabilities. “Thousands” of reachable mainnet nodes were whitelisting incoming Tor connections, which removed some DoS limits and privacy protections. Nodes that didn’t have this non-default setting were not affected. (theblock)
The truth about the timeline:
✅ The fix was included in Bitcoin Core 30.0 (Oct 10, 2025) and 29.2 (Oct 14, 2025). The last vulnerable version reached end-of-life on Oct 27, 2026.
✅ The project ships the fix first, then shares the vulnerability details later.
⚠️ This is not an issue with consensus rules. The risk was to node privacy and reliability, not to coins or the Bitcoin protocol. (theblock) (cryptovalleyjournal)
My analysis: This is a textbook example of “responsible disclosure.” First the patch, then time for users to upgrade, and only then a public advisory. That’s the power of open source: a bug is found, fixed, and later everything is made public. But there’s a lesson here too: operators running old node versions should upgrade now.
(Not financial advice, DYOR.)
Do you run your own node, or do you trust an exchange/custodian? Why? 👇
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin❗ #Tor #BitcoinCore
9

🚨 BITCOIN CORE SECURITY DISCLOSURES REVEAL ZERO IMPACT ON $BTC MARKET STRUCTURE 📊
Protocol integrity remains the bedrock of institutional confidence across $BTC and $ETH . Recent disclosures regarding historical network patches highlight standard developer hygiene rather than active vulnerabilities, leaving market liquidity completely unaffected. 📊
Smart money infrastructure relies on robust node maintenance, and these routine disclosures confirm that core developers neutralized these edge cases long ago. 💡
💬 Do you actively monitor network protocol updates for self-custody nodes, or do you leave infrastructure management to third parties? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #BitcoinCore #MarketStructure
🎯 🦈
🚨 BITCOIN CORE SECURITY DISCLOSURES REVEAL ZERO IMPACT ON $BTC MARKET STRUCTURE 📊
Protocol integrity remains the bedrock of institutional confidence across $BTC and $ETH . Recent disclosures regarding historical network patches highlight standard developer hygiene rather than active vulnerabilities, leaving market liquidity completely unaffected. 📊
Smart money infrastructure relies on robust node maintenance, and these routine disclosures confirm that core developers neutralized these edge cases long ago. 💡
💬 Do you actively monitor network protocol updates for self-custody nodes, or do you leave infrastructure management to third parties? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #BitcoinCore #MarketStructure
🎯 🦈
Protocol integrity remains the bedrock of institutional confidence across $BTC and $ETH . Recent disclosures regarding historical network patches highlight standard developer hygiene rather than active vulnerabilities, leaving market liquidity completely unaffected. 📊
Smart money infrastructure relies on robust node maintenance, and these routine disclosures confirm that core developers neutralized these edge cases long ago. 💡
💬 Do you actively monitor network protocol updates for self-custody nodes, or do you leave infrastructure management to third parties? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #BitcoinCore #MarketStructure
🎯 🦈
7

·
--
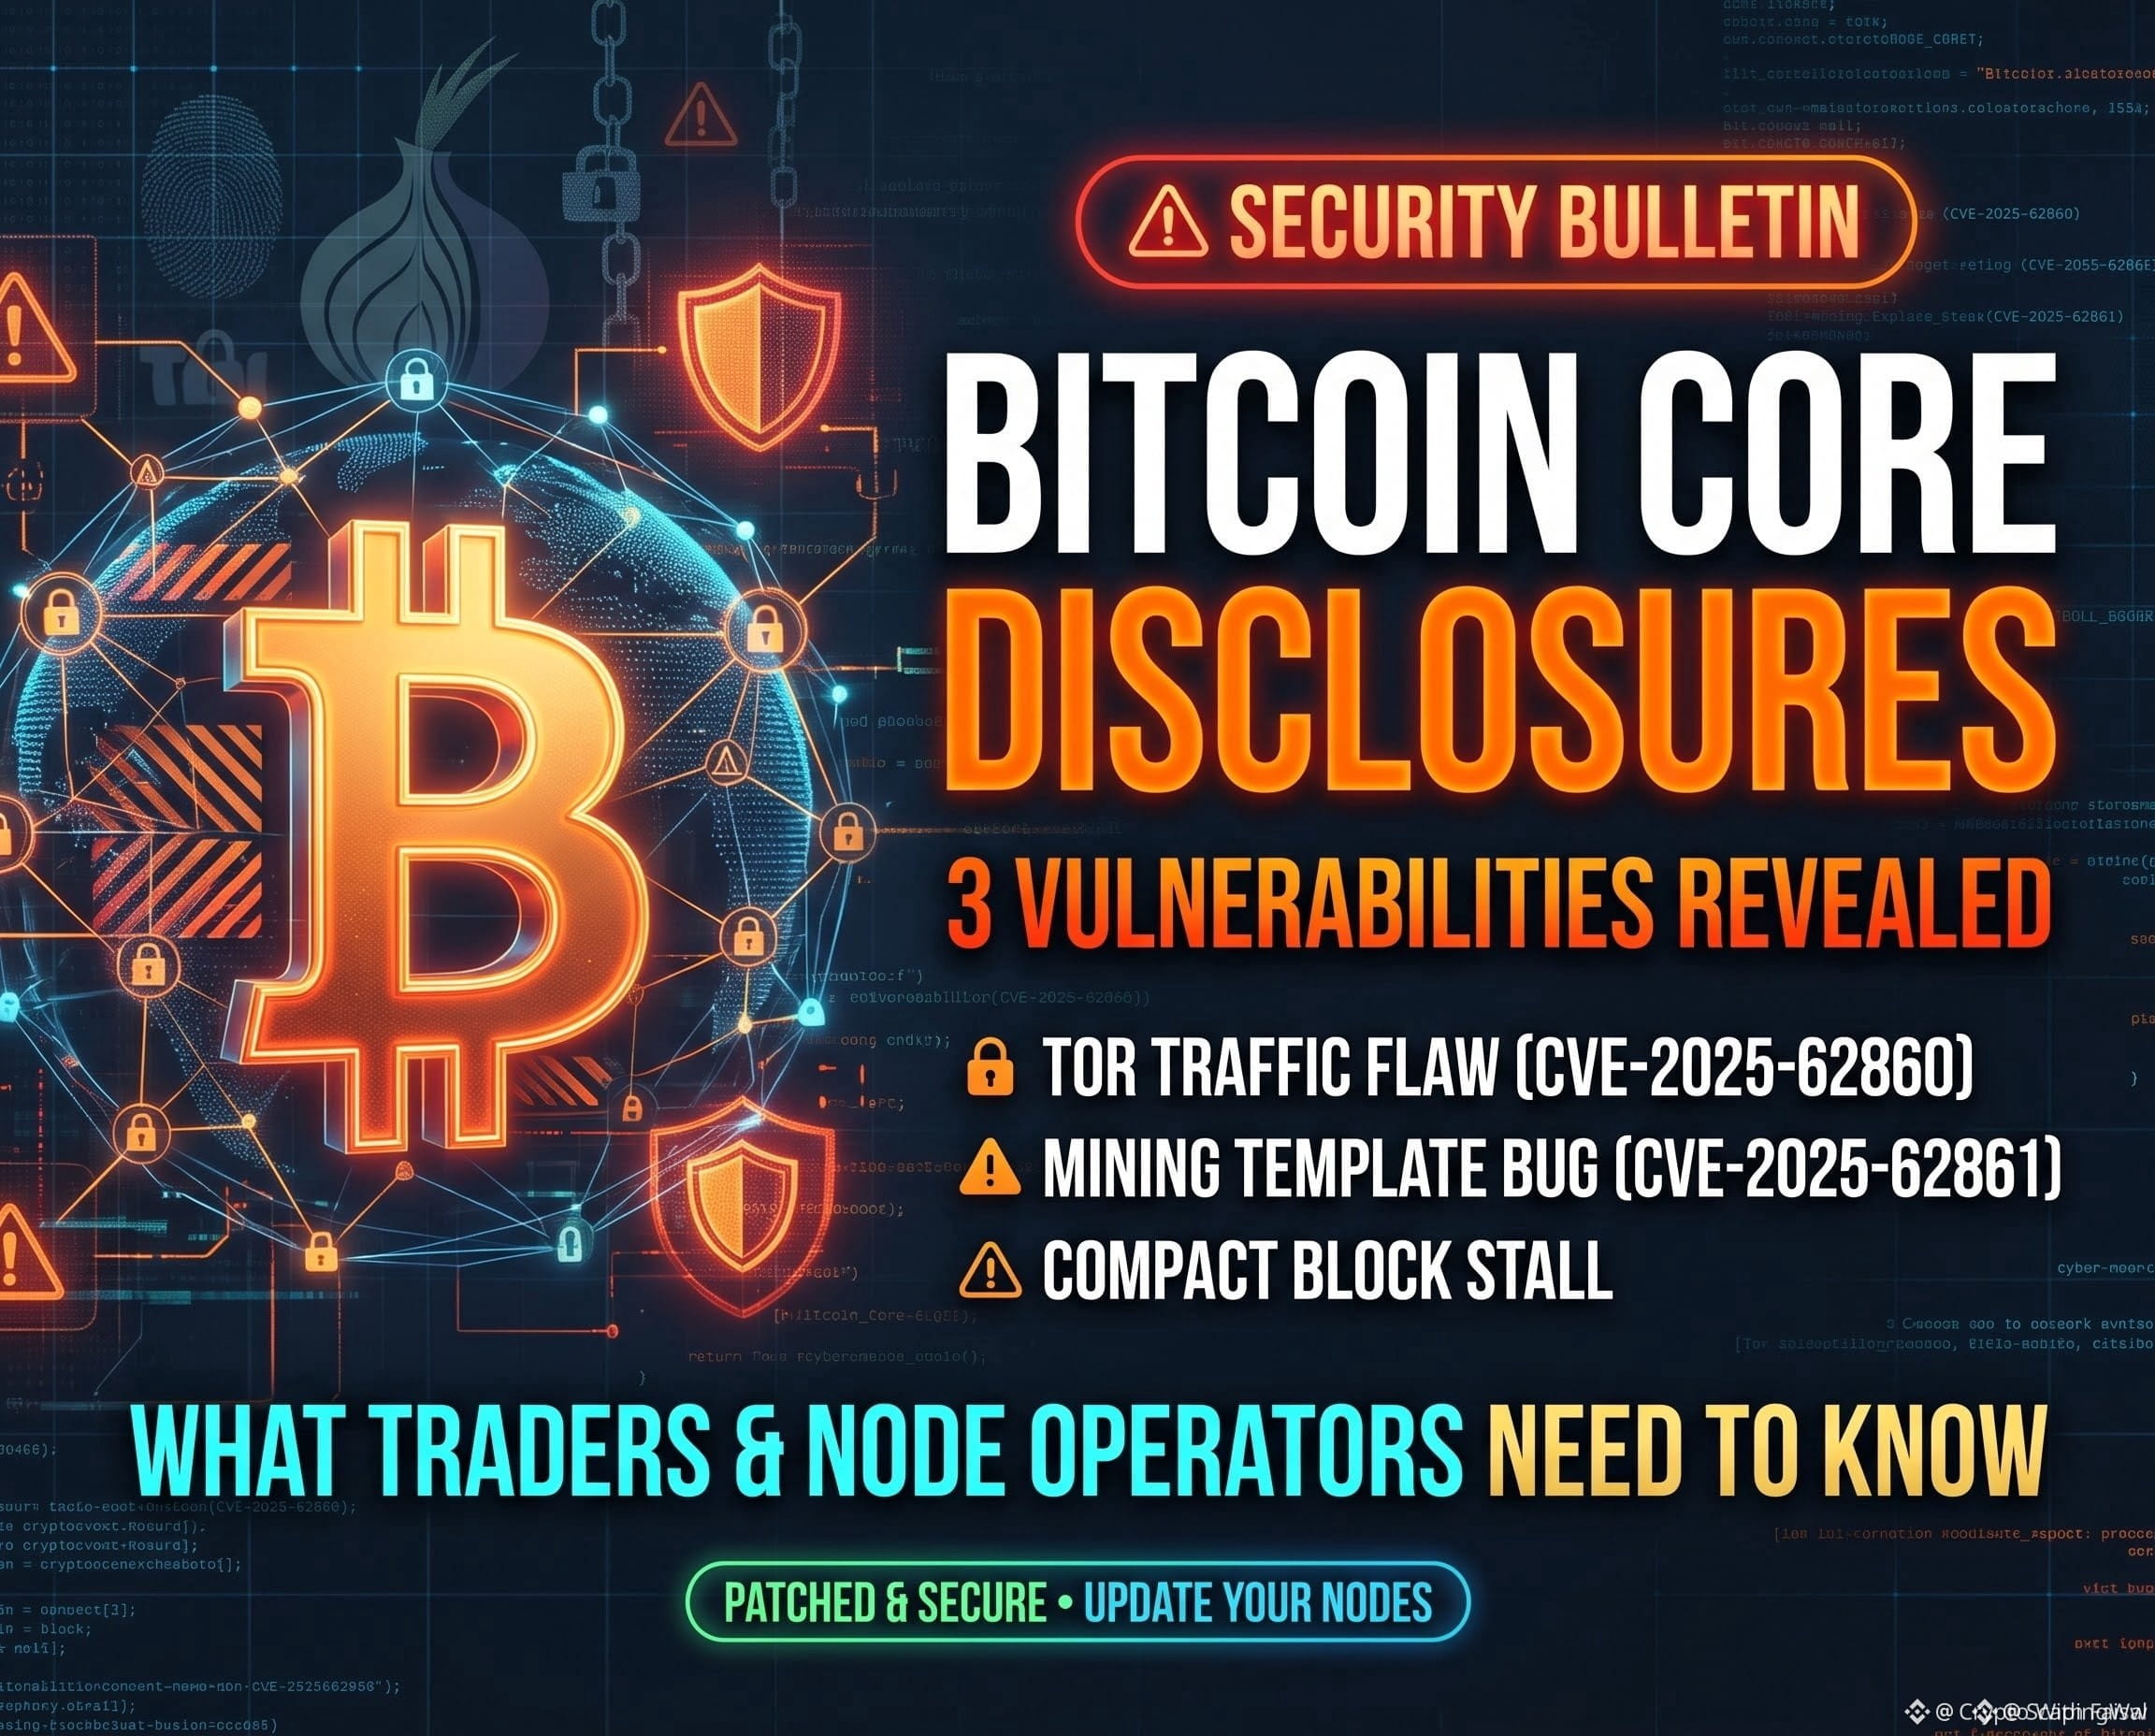
🚨 $BTC CORE PATCH DISCLOSURES HIT THE WIRE WITH ZERO REAL-WORLD THREATS! ⚡
The recent security disclosure surrounding Bitcoin Core might trigger knee-jerk reactions from inexperienced market participants, but smart money sees right through the noise. 📊 These historical code patches were already deployed long ago, leaving node operators and self-custody holders completely safe from harm. 💡
Real decentralization relies on robust maintenance rather than blind faith, proving that transparent developer updates are a hallmark of a healthy monetary network. 💬 Do you run your own local node to secure your stack, or do you rely on a major exchange? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #BitcoinCore #Crypto
🔥 💎
🚨 $BTC CORE PATCH DISCLOSURES HIT THE WIRE WITH ZERO REAL-WORLD THREATS! ⚡
The recent security disclosure surrounding Bitcoin Core might trigger knee-jerk reactions from inexperienced market participants, but smart money sees right through the noise. 📊 These historical code patches were already deployed long ago, leaving node operators and self-custody holders completely safe from harm. 💡
Real decentralization relies on robust maintenance rather than blind faith, proving that transparent developer updates are a hallmark of a healthy monetary network. 💬 Do you run your own local node to secure your stack, or do you rely on a major exchange? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #BitcoinCore #Crypto
🔥 💎
The recent security disclosure surrounding Bitcoin Core might trigger knee-jerk reactions from inexperienced market participants, but smart money sees right through the noise. 📊 These historical code patches were already deployed long ago, leaving node operators and self-custody holders completely safe from harm. 💡
Real decentralization relies on robust maintenance rather than blind faith, proving that transparent developer updates are a hallmark of a healthy monetary network. 💬 Do you run your own local node to secure your stack, or do you rely on a major exchange? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #BitcoinCore #Crypto
🔥 💎
10
#BitcoinCoreDisclosesTorTrafficVulnerability 🧅⚠️
Bitcoin was NOT hacked.
But this disclosure is BIG. Read it.
Bitcoin Core just disclosed 3 vulnerabilities - including a Tor bug that affected *thousands of nodes.
What happened?
Bitcoin Core has a setting called `-whitelist`.
It gives TRUSTED connections extra permissions - like bypassing spam limits and privacy protections.
The bug:
Tor connections look like they come from your local Tor software.
If that local Tor IP was inside the whitelist range, then *EVERY stranger connecting via Tor was treated as TRUSTED.*
Result: Thousands of reachable mainnet nodes were whitelisting ALL incoming Tor connections.
The Facts You Need:
CVE:* CVE-2025-62860
Severity:* Medium
Coins stolen?* NO ❌
Wallets hacked?* NO ❌
Active exploit found?* NO ❌
Nodes without whitelist?* NOT AFFECTED ✅
*Was it already fixed?*
YES.
Fixed in *October 2025* - in v30.0, v29.2, v28.3
Disclosure came on *Nov 10, 2026* - because Core only publishes details AFTER the last affected version reaches end-of-life. That's their security policy.
*2 Other Bugs Disclosed:*
1. *HIGH severity* - Mining node could fail to build valid block templates after a reorg until restart
2. *MEDIUM severity* - Attacker could stall block processing for 10 minutes
*What should you do?
If you run a node, make sure you are on the LATEST version. Update = Safe.
This is not FUD. This is TRANSPARENCY.
This is exactly why Bitcoin is still the most trusted network in crypto. 💪
Question:
Is this late disclosure GOOD security or TOO LATE?
Drop your opinion 👇
#BTC #BitcoinCore #CryptoSecurity
#BitcoinCoreDisclosesTorTrafficVulnerability 🧅⚠️
Bitcoin was NOT hacked.
But this disclosure is BIG. Read it.
Bitcoin Core just disclosed 3 vulnerabilities - including a Tor bug that affected *thousands of nodes.
What happened?
Bitcoin Core has a setting called `-whitelist`.
It gives TRUSTED connections extra permissions - like bypassing spam limits and privacy protections.
The bug:
Tor connections look like they come from your local Tor software.
If that local Tor IP was inside the whitelist range, then *EVERY stranger connecting via Tor was treated as TRUSTED.*
Result: Thousands of reachable mainnet nodes were whitelisting ALL incoming Tor connections.
The Facts You Need:
CVE:* CVE-2025-62860
Severity:* Medium
Coins stolen?* NO ❌
Wallets hacked?* NO ❌
Active exploit found?* NO ❌
Nodes without whitelist?* NOT AFFECTED ✅
*Was it already fixed?*
YES.
Fixed in *October 2025* - in v30.0, v29.2, v28.3
Disclosure came on *Nov 10, 2026* - because Core only publishes details AFTER the last affected version reaches end-of-life. That's their security policy.
*2 Other Bugs Disclosed:*
1. *HIGH severity* - Mining node could fail to build valid block templates after a reorg until restart
2. *MEDIUM severity* - Attacker could stall block processing for 10 minutes
*What should you do?
If you run a node, make sure you are on the LATEST version. Update = Safe.
This is not FUD. This is TRANSPARENCY.
This is exactly why Bitcoin is still the most trusted network in crypto. 💪
Question:
Is this late disclosure GOOD security or TOO LATE?
Drop your opinion 👇
#BTC #BitcoinCore #CryptoSecurity
Bitcoin was NOT hacked.
But this disclosure is BIG. Read it.
Bitcoin Core just disclosed 3 vulnerabilities - including a Tor bug that affected *thousands of nodes.
What happened?
Bitcoin Core has a setting called `-whitelist`.
It gives TRUSTED connections extra permissions - like bypassing spam limits and privacy protections.
The bug:
Tor connections look like they come from your local Tor software.
If that local Tor IP was inside the whitelist range, then *EVERY stranger connecting via Tor was treated as TRUSTED.*
Result: Thousands of reachable mainnet nodes were whitelisting ALL incoming Tor connections.
The Facts You Need:
CVE:* CVE-2025-62860
Severity:* Medium
Coins stolen?* NO ❌
Wallets hacked?* NO ❌
Active exploit found?* NO ❌
Nodes without whitelist?* NOT AFFECTED ✅
*Was it already fixed?*
YES.
Fixed in *October 2025* - in v30.0, v29.2, v28.3
Disclosure came on *Nov 10, 2026* - because Core only publishes details AFTER the last affected version reaches end-of-life. That's their security policy.
*2 Other Bugs Disclosed:*
1. *HIGH severity* - Mining node could fail to build valid block templates after a reorg until restart
2. *MEDIUM severity* - Attacker could stall block processing for 10 minutes
*What should you do?
If you run a node, make sure you are on the LATEST version. Update = Safe.
This is not FUD. This is TRANSPARENCY.
This is exactly why Bitcoin is still the most trusted network in crypto. 💪
Question:
Is this late disclosure GOOD security or TOO LATE?
Drop your opinion 👇
#BTC #BitcoinCore #CryptoSecurity
87

🚨 BITCOIN CORE DISCLOSES 3 VULNERABILITIES: IS THE NETWORK SAFE? 🚨
Bitcoin Core just released details on three security bugs, including a notable Tor traffic flaw. If you are a trader or node operator, here is the verified breakdown of what actually happened and how it impacts the market:
⚠️ The Tor Vulnerability (CVE-2025-62860):
Thousands of reachable mainnet nodes running non-default -whitelist configurations accidentally gave inbound Tor connections trusted permissions. This bypassed vital DoS and privacy protections, leaving nodes exposed.
🛑 The Mining Flaw (CVE-2025-62861):
A high-severity bug caused mempool inconsistencies during chain reorganizations. This could halt block template creation for affected miners, requiring a forced restart to fix.
🛡️ The Bottom Line (Trader Impact = ZERO):
Don't panic. There are zero active exploits and no user funds were ever at risk. Developers quietly patched these bugs back in October 2025 with the v30.0 and v29.2 updates. This delayed disclosure on November 10, 2026, is simply standard security protocol now that older vulnerable versions have reached end-of-life.
Decentralized money requires well-maintained software. Update your nodes!
🗣️ Do you run your own Bitcoin node for self-custody, or do you rely on exchanges? Let’s discuss below! 👇
$AKE
{future}(AKEUSDT)
$BTC
{future}(BTCUSDT)
$ETH
{future}(ETHUSDT)
#bitcoincoredisclosestortrafficvulnerability
#CryptoSecurity #BitcoinCore #CryptoNews
🚨 BITCOIN CORE DISCLOSES 3 VULNERABILITIES: IS THE NETWORK SAFE? 🚨
Bitcoin Core just released details on three security bugs, including a notable Tor traffic flaw. If you are a trader or node operator, here is the verified breakdown of what actually happened and how it impacts the market:
⚠️ The Tor Vulnerability (CVE-2025-62860):
Thousands of reachable mainnet nodes running non-default -whitelist configurations accidentally gave inbound Tor connections trusted permissions. This bypassed vital DoS and privacy protections, leaving nodes exposed.
🛑 The Mining Flaw (CVE-2025-62861):
A high-severity bug caused mempool inconsistencies during chain reorganizations. This could halt block template creation for affected miners, requiring a forced restart to fix.
🛡️ The Bottom Line (Trader Impact = ZERO):
Don't panic. There are zero active exploits and no user funds were ever at risk. Developers quietly patched these bugs back in October 2025 with the v30.0 and v29.2 updates. This delayed disclosure on November 10, 2026, is simply standard security protocol now that older vulnerable versions have reached end-of-life.
Decentralized money requires well-maintained software. Update your nodes!
🗣️ Do you run your own Bitcoin node for self-custody, or do you rely on exchanges? Let’s discuss below! 👇
$AKE
$BTC
$ETH
#bitcoincoredisclosestortrafficvulnerability
#CryptoSecurity #BitcoinCore #CryptoNews
Bitcoin Core just released details on three security bugs, including a notable Tor traffic flaw. If you are a trader or node operator, here is the verified breakdown of what actually happened and how it impacts the market:
⚠️ The Tor Vulnerability (CVE-2025-62860):
Thousands of reachable mainnet nodes running non-default -whitelist configurations accidentally gave inbound Tor connections trusted permissions. This bypassed vital DoS and privacy protections, leaving nodes exposed.
🛑 The Mining Flaw (CVE-2025-62861):
A high-severity bug caused mempool inconsistencies during chain reorganizations. This could halt block template creation for affected miners, requiring a forced restart to fix.
🛡️ The Bottom Line (Trader Impact = ZERO):
Don't panic. There are zero active exploits and no user funds were ever at risk. Developers quietly patched these bugs back in October 2025 with the v30.0 and v29.2 updates. This delayed disclosure on November 10, 2026, is simply standard security protocol now that older vulnerable versions have reached end-of-life.
Decentralized money requires well-maintained software. Update your nodes!
🗣️ Do you run your own Bitcoin node for self-custody, or do you rely on exchanges? Let’s discuss below! 👇
$AKE
$BTC
$ETH
#bitcoincoredisclosestortrafficvulnerability
#CryptoSecurity #BitcoinCore #CryptoNews
1
705

·
--
Bearish
🚨 Bitcoin Core just revealed 3 security flaws — one could stop affected mining nodes from producing blocks
The surprising part?
All three were FIXED over a year ago
On November 10, Bitcoin Core publicly disclosed three vulnerabilities after the last affected release series reached end of life
Here's what the bugs could do 👇
$BTC
{future}(BTCUSDT)
🔴 HIGH severity — A chain reorganization could corrupt an affected node's mempool, preventing miners from creating valid block templates until restarting
🟠 MEDIUM severity — Incoming Tor connections could mistakenly receive trusted-peer privileges on nodes with certain whitelist settings
🟠 MEDIUM severity — A malicious peer could repeatedly delay block processing under specific conditions
But this is NOT evidence that Bitcoin's consensus rules were broken or BTC was stolen
The fixes arrived in October 2025
{spot}(BTCUSDT)
⚠️ For node operators, the important question is whether you're still running vulnerable software
Bitcoin Core 29.2 and 30.0 already included all three fixes — use a currently supported release
The vulnerability disclosure is new
The protection isn't
$BTC #bitcoin #BitcoinCore
🚨 Bitcoin Core just revealed 3 security flaws — one could stop affected mining nodes from producing blocks
The surprising part?
All three were FIXED over a year ago
On November 10, Bitcoin Core publicly disclosed three vulnerabilities after the last affected release series reached end of life
Here's what the bugs could do 👇
$BTC
🔴 HIGH severity — A chain reorganization could corrupt an affected node's mempool, preventing miners from creating valid block templates until restarting
🟠 MEDIUM severity — Incoming Tor connections could mistakenly receive trusted-peer privileges on nodes with certain whitelist settings
🟠 MEDIUM severity — A malicious peer could repeatedly delay block processing under specific conditions
But this is NOT evidence that Bitcoin's consensus rules were broken or BTC was stolen
The fixes arrived in October 2025
⚠️ For node operators, the important question is whether you're still running vulnerable software
Bitcoin Core 29.2 and 30.0 already included all three fixes — use a currently supported release
The vulnerability disclosure is new
The protection isn't
$BTC #bitcoin #BitcoinCore
The surprising part?
All three were FIXED over a year ago
On November 10, Bitcoin Core publicly disclosed three vulnerabilities after the last affected release series reached end of life
Here's what the bugs could do 👇
$BTC
🔴 HIGH severity — A chain reorganization could corrupt an affected node's mempool, preventing miners from creating valid block templates until restarting
🟠 MEDIUM severity — Incoming Tor connections could mistakenly receive trusted-peer privileges on nodes with certain whitelist settings
🟠 MEDIUM severity — A malicious peer could repeatedly delay block processing under specific conditions
But this is NOT evidence that Bitcoin's consensus rules were broken or BTC was stolen
The fixes arrived in October 2025
⚠️ For node operators, the important question is whether you're still running vulnerable software
Bitcoin Core 29.2 and 30.0 already included all three fixes — use a currently supported release
The vulnerability disclosure is new
The protection isn't
$BTC #bitcoin #BitcoinCore
3
·
--
🚨 BREAKING NEWS: THE SOFTWARE THAT RUNS THE BITCOIN NETWORK JUST ADMITTED IT HAS 3 VULNERABILITIES!
Bitcoin Core, the software that runs most Bitcoin nodes, publicly disclosed 3 security vulnerabilities on November 10. The most serious bug could prevent miners’ nodes from creating a new block after a chain reorganization, until they are restarted.
The good news: all 3 bugs were patched in October 2025, no exploits have been reported, and not a single BTC was lost.
But here’s the chilling part: nearly 9% of nodes on the network—about 1,885 nodes—are STILL running an outdated, vulnerable version.
Meanwhile, BTC is hovering around $73,000, ETH is languishing around $2,050, and the Fear & Greed Index is down to 28. The market is fearful, but the Bitcoin network keeps running.
Save this—hardly anyone is paying attention to this news, but it’s extremely important. Follow me; I post it here first.
$BTC $ETH
#Bitcoin #BitcoinCore
🚨 BREAKING NEWS: THE SOFTWARE THAT RUNS THE BITCOIN NETWORK JUST ADMITTED IT HAS 3 VULNERABILITIES!
Bitcoin Core, the software that runs most Bitcoin nodes, publicly disclosed 3 security vulnerabilities on November 10. The most serious bug could prevent miners’ nodes from creating a new block after a chain reorganization, until they are restarted.
The good news: all 3 bugs were patched in October 2025, no exploits have been reported, and not a single BTC was lost.
But here’s the chilling part: nearly 9% of nodes on the network—about 1,885 nodes—are STILL running an outdated, vulnerable version.
Meanwhile, BTC is hovering around $73,000, ETH is languishing around $2,050, and the Fear & Greed Index is down to 28. The market is fearful, but the Bitcoin network keeps running.
Save this—hardly anyone is paying attention to this news, but it’s extremely important. Follow me; I post it here first.
$BTC $ETH
#Bitcoin #BitcoinCore
Bitcoin Core, the software that runs most Bitcoin nodes, publicly disclosed 3 security vulnerabilities on November 10. The most serious bug could prevent miners’ nodes from creating a new block after a chain reorganization, until they are restarted.
The good news: all 3 bugs were patched in October 2025, no exploits have been reported, and not a single BTC was lost.
But here’s the chilling part: nearly 9% of nodes on the network—about 1,885 nodes—are STILL running an outdated, vulnerable version.
Meanwhile, BTC is hovering around $73,000, ETH is languishing around $2,050, and the Fear & Greed Index is down to 28. The market is fearful, but the Bitcoin network keeps running.
Save this—hardly anyone is paying attention to this news, but it’s extremely important. Follow me; I post it here first.
$BTC $ETH
#Bitcoin #BitcoinCore
115

Critical Bitcoin Core Vulnerability Found in Tor Node Communications
A vulnerability in Bitcoin Core could allow malicious actors via the Tor network to compromise the trust model of over 1,000 nodes.
#BitcoinSecurity #BitcoinCore
Critical Bitcoin Core Vulnerability Found in Tor Node Communications
A vulnerability in Bitcoin Core could allow malicious actors via the Tor network to compromise the trust model of over 1,000 nodes.
#BitcoinSecurity #BitcoinCore
A vulnerability in Bitcoin Core could allow malicious actors via the Tor network to compromise the trust model of over 1,000 nodes.
#BitcoinSecurity #BitcoinCore
68
·
--
🔧 Bitcoin Core disclosed 3 vulnerabilities all at once, after keeping them under wraps for 13 months!
According to CoinDesk: Bitcoin Core published a security advisory on 11/10. The three vulnerabilities had actually been fixed in October 2025, but disclosure was delayed until now under its policy of publishing details two weeks after support for affected versions ends.
⚠️ 1) Tor allowlist vulnerability (medium severity): External Tor connections could be treated as trusted machines. “Thousands of mainnet nodes” were affected, bypassing anti-spam and privacy restrictions.
⚠️ 2) High severity: A rule introduced in version 28.0 could prevent mining nodes from generating valid block templates during a chain reorganization. Restarting was required to restore functionality.
⚠️ 3) Medium severity: A malicious connection could cause a node to stall while processing new blocks for 10 minutes. Repeated attacks could prolong the disruption.
✅ The advisory reported no real-world attacks. Patches were released long ago, so simply upgrade to the latest version. Nodes without the allowlist enabled are unaffected.
📌 My take: This is neutral news for the price, but a reminder that BTC’s security depends on continuous patching. Starting in October, core developers changed the rules: bugs that can be found with a single AI prompt will be fixed and disclosed more quickly.
BTC is currently around 73,000, ETFs have seen outflows for four consecutive days, and the Fear & Greed Index is at 28. Which do you think has more impact on your positioning: bearish fundamentals or technical news like this? Let’s talk in the comments 👇
$BTC $ETH
#比特币 #BitcoinCore #CryptoSecurity
Personal opinions only; this is not investment advice
🔧 Bitcoin Core disclosed 3 vulnerabilities all at once, after keeping them under wraps for 13 months!
According to CoinDesk: Bitcoin Core published a security advisory on 11/10. The three vulnerabilities had actually been fixed in October 2025, but disclosure was delayed until now under its policy of publishing details two weeks after support for affected versions ends.
⚠️ 1) Tor allowlist vulnerability (medium severity): External Tor connections could be treated as trusted machines. “Thousands of mainnet nodes” were affected, bypassing anti-spam and privacy restrictions.
⚠️ 2) High severity: A rule introduced in version 28.0 could prevent mining nodes from generating valid block templates during a chain reorganization. Restarting was required to restore functionality.
⚠️ 3) Medium severity: A malicious connection could cause a node to stall while processing new blocks for 10 minutes. Repeated attacks could prolong the disruption.
✅ The advisory reported no real-world attacks. Patches were released long ago, so simply upgrade to the latest version. Nodes without the allowlist enabled are unaffected.
📌 My take: This is neutral news for the price, but a reminder that BTC’s security depends on continuous patching. Starting in October, core developers changed the rules: bugs that can be found with a single AI prompt will be fixed and disclosed more quickly.
BTC is currently around 73,000, ETFs have seen outflows for four consecutive days, and the Fear & Greed Index is at 28. Which do you think has more impact on your positioning: bearish fundamentals or technical news like this? Let’s talk in the comments 👇
$BTC $ETH
#比特币 #BitcoinCore #CryptoSecurity
Personal opinions only; this is not investment advice
According to CoinDesk: Bitcoin Core published a security advisory on 11/10. The three vulnerabilities had actually been fixed in October 2025, but disclosure was delayed until now under its policy of publishing details two weeks after support for affected versions ends.
⚠️ 1) Tor allowlist vulnerability (medium severity): External Tor connections could be treated as trusted machines. “Thousands of mainnet nodes” were affected, bypassing anti-spam and privacy restrictions.
⚠️ 2) High severity: A rule introduced in version 28.0 could prevent mining nodes from generating valid block templates during a chain reorganization. Restarting was required to restore functionality.
⚠️ 3) Medium severity: A malicious connection could cause a node to stall while processing new blocks for 10 minutes. Repeated attacks could prolong the disruption.
✅ The advisory reported no real-world attacks. Patches were released long ago, so simply upgrade to the latest version. Nodes without the allowlist enabled are unaffected.
📌 My take: This is neutral news for the price, but a reminder that BTC’s security depends on continuous patching. Starting in October, core developers changed the rules: bugs that can be found with a single AI prompt will be fixed and disclosed more quickly.
BTC is currently around 73,000, ETFs have seen outflows for four consecutive days, and the Fear & Greed Index is at 28. Which do you think has more impact on your positioning: bearish fundamentals or technical news like this? Let’s talk in the comments 👇
$BTC $ETH
#比特币 #BitcoinCore #CryptoSecurity
Personal opinions only; this is not investment advice
·
--
Bitcoin Core discloses 3 vulnerabilities at once: Is your node version up to date?
The bottom line: According to three disclosures published on the Bitcoin Core website on November 10, these issues affect the node’s mempool, block propagation, and connection permissions. None involves private keys or forged transactions. The fixes were released back in October 2025; only now are the details being made public.
What each of the 3 vulnerabilities does:
1. CVE-2025-62861 (high severity): During a chain reorganization, the “sibling replacement” rule for TRUC (v3) transactions can be triggered incorrectly, leaving transactions in the mempool that spend outputs that no longer exist. As a result, the node cannot generate block templates until it is restarted. Affected versions: 28.0–28.2 and 29.0–29.1. This is most damaging for miners and mining pools.
2. CVE-2025-62860 (medium severity): Nodes configured with -whitelist to allow IP ranges can also treat incoming Tor connections as whitelisted, disabling some DoS protections and privacy safeguards. The official disclosure says that because some bundled packages use this configuration by default, thousands of reachable nodes on the mainnet are affected. Nodes without -whitelist configured were never affected.
3. CVE-2025-62859 (medium severity): A malicious node can use compact blocks with tampered witness data to make a victim node get stuck waiting for the 10-minute timeout. This can be repeated indefinitely if the attacker controls all 3 of your high-bandwidth nodes, or if you have -blocksonly enabled.
The timeline is also worth noting: The earliest issue (62859) was reported on April 28, 2025, about 18 months before it was publicly disclosed. The reason is that the developers waited until the last affected release branch, 29.x, reached end of support on October 27, 2026, before publishing the details.
How to check, in two steps:
1. Run bitcoin-cli getnetworkinfo and check the subversion field. Version 30.0 and later fix all three; 29.2 fixes all three; 28.3 fixes the first two (the original disclosure for 62859 lists only 29.2 and 30.0). Version 29.x reached end of support on October 27, so the safest option is to upgrade to a release branch that is still supported.
2. If you use a bundled node package with a graphical interface, check its settings to see whether an IP range is configured under -whitelist, and confirm that the Core version included in the package is later than the versions listed above.
According to the disclosures, people who only hold coins on exchanges or in mobile wallets and do not run their own nodes do not need to take any action in response to this issue.
This article does not constitute investment advice.
#比特币 #安全 #BitcoinCore #节点 $BTC
Bitcoin Core discloses 3 vulnerabilities at once: Is your node version up to date?
The bottom line: According to three disclosures published on the Bitcoin Core website on November 10, these issues affect the node’s mempool, block propagation, and connection permissions. None involves private keys or forged transactions. The fixes were released back in October 2025; only now are the details being made public.
What each of the 3 vulnerabilities does:
1. CVE-2025-62861 (high severity): During a chain reorganization, the “sibling replacement” rule for TRUC (v3) transactions can be triggered incorrectly, leaving transactions in the mempool that spend outputs that no longer exist. As a result, the node cannot generate block templates until it is restarted. Affected versions: 28.0–28.2 and 29.0–29.1. This is most damaging for miners and mining pools.
2. CVE-2025-62860 (medium severity): Nodes configured with -whitelist to allow IP ranges can also treat incoming Tor connections as whitelisted, disabling some DoS protections and privacy safeguards. The official disclosure says that because some bundled packages use this configuration by default, thousands of reachable nodes on the mainnet are affected. Nodes without -whitelist configured were never affected.
3. CVE-2025-62859 (medium severity): A malicious node can use compact blocks with tampered witness data to make a victim node get stuck waiting for the 10-minute timeout. This can be repeated indefinitely if the attacker controls all 3 of your high-bandwidth nodes, or if you have -blocksonly enabled.
The timeline is also worth noting: The earliest issue (62859) was reported on April 28, 2025, about 18 months before it was publicly disclosed. The reason is that the developers waited until the last affected release branch, 29.x, reached end of support on October 27, 2026, before publishing the details.
How to check, in two steps:
1. Run bitcoin-cli getnetworkinfo and check the subversion field. Version 30.0 and later fix all three; 29.2 fixes all three; 28.3 fixes the first two (the original disclosure for 62859 lists only 29.2 and 30.0). Version 29.x reached end of support on October 27, so the safest option is to upgrade to a release branch that is still supported.
2. If you use a bundled node package with a graphical interface, check its settings to see whether an IP range is configured under -whitelist, and confirm that the Core version included in the package is later than the versions listed above.
According to the disclosures, people who only hold coins on exchanges or in mobile wallets and do not run their own nodes do not need to take any action in response to this issue.
This article does not constitute investment advice.
#比特币 #安全 #BitcoinCore #节点 $BTC
The bottom line: According to three disclosures published on the Bitcoin Core website on November 10, these issues affect the node’s mempool, block propagation, and connection permissions. None involves private keys or forged transactions. The fixes were released back in October 2025; only now are the details being made public.
What each of the 3 vulnerabilities does:
1. CVE-2025-62861 (high severity): During a chain reorganization, the “sibling replacement” rule for TRUC (v3) transactions can be triggered incorrectly, leaving transactions in the mempool that spend outputs that no longer exist. As a result, the node cannot generate block templates until it is restarted. Affected versions: 28.0–28.2 and 29.0–29.1. This is most damaging for miners and mining pools.
2. CVE-2025-62860 (medium severity): Nodes configured with -whitelist to allow IP ranges can also treat incoming Tor connections as whitelisted, disabling some DoS protections and privacy safeguards. The official disclosure says that because some bundled packages use this configuration by default, thousands of reachable nodes on the mainnet are affected. Nodes without -whitelist configured were never affected.
3. CVE-2025-62859 (medium severity): A malicious node can use compact blocks with tampered witness data to make a victim node get stuck waiting for the 10-minute timeout. This can be repeated indefinitely if the attacker controls all 3 of your high-bandwidth nodes, or if you have -blocksonly enabled.
The timeline is also worth noting: The earliest issue (62859) was reported on April 28, 2025, about 18 months before it was publicly disclosed. The reason is that the developers waited until the last affected release branch, 29.x, reached end of support on October 27, 2026, before publishing the details.
How to check, in two steps:
1. Run bitcoin-cli getnetworkinfo and check the subversion field. Version 30.0 and later fix all three; 29.2 fixes all three; 28.3 fixes the first two (the original disclosure for 62859 lists only 29.2 and 30.0). Version 29.x reached end of support on October 27, so the safest option is to upgrade to a release branch that is still supported.
2. If you use a bundled node package with a graphical interface, check its settings to see whether an IP range is configured under -whitelist, and confirm that the Core version included in the package is later than the versions listed above.
According to the disclosures, people who only hold coins on exchanges or in mobile wallets and do not run their own nodes do not need to take any action in response to this issue.
This article does not constitute investment advice.
#比特币 #安全 #BitcoinCore #节点 $BTC
267
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanBTCReboundAfterFallingBelow60K?
388,957 views
1,660 Discussing
2
#GlobalStocksFaceLongestLosingStreakSince2023
129,378 views
1,154 Discussing
3
#BlackRockIBITPostsRecord$541MSingleDayOutflow
1,028 views
30 Discussing
4
#AnthropicPlungesTowardIPOPriceonDay2
61,498 views
620 Discussing
5
#TwentyOneCapitalAdds172.25BTC
14,326 views
180 Discussing
6
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
1,432 views
18 Discussing
7
#BNBDropsBelow540USDTWith8.46%DailyDecline
34,954 views
294 Discussing
8
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,141 views
17 Discussing
9
#BitMineFaces$10.1BUnrealizedETHLoss
2,166 views
20 Discussing
10
#StrategyReports$35BNetReserves
2,128 views
18 Discussing