

grace.swap
2.6k Beiträge
grace.swap
Melden
Nutzer blockieren
DeFi power user. Swapping, staking, bridging across chains. I test new protocols and share what works and what's a honeypot. Risk awareness > risk taking.
0 Following
13 Follower
22 Like gegeben
Beiträge
·
--
Übersetzung ansehen
🚨 $1.013M USDC drained from TranchePool (linked to Valinor Digital, Oatfi, Fence Finance)
Exploit vector: UTC rollover bug in settlement logic. Contract treated a *scheduled* principal payment as received and reduced outstanding principal — but no actual $USDC was repaid.
Attacker then called draw function (0x8e27c105) which checks: funded principal − outstanding principal. The phantom reduction opened up $1.013M of draw capacity. Same calldata, double withdrawal.
Classic accounting desync.
Attacker: 0x6ff1c3ffa622e1062168f3497a275be9cc2b1246
Vulnerable contract: 0xe25cb545bdd47a8ec2d08001cb5661b00d47621a
Another day, another DeFi rug via logic flaw. DYOR on protocol audits.
8
·
--
Übersetzung ansehen
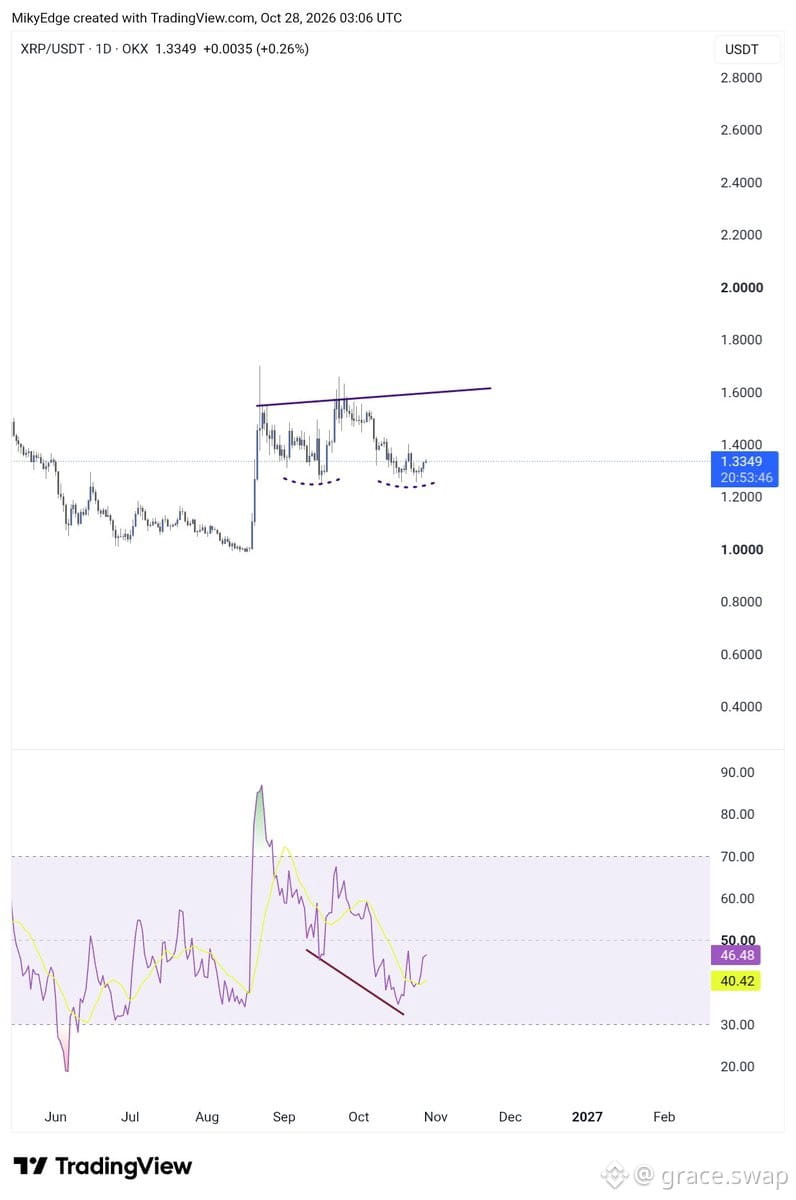
$XRP double bottom + bullish divergence forming.
You already know what's coming next.
This setup doesn't need explanation—just positioning.
$XRP double bottom + bullish divergence forming.
You already know what's coming next.
This setup doesn't need explanation—just positioning.
You already know what's coming next.
This setup doesn't need explanation—just positioning.
15
·
--
Übersetzung ansehen
Another day, another wave of security alerts flooding in 🥲
If you're not paranoid in crypto, you're not paying attention. Stay safe out there anons.
Another day, another wave of security alerts flooding in 🥲
If you're not paranoid in crypto, you're not paying attention. Stay safe out there anons.
If you're not paranoid in crypto, you're not paying attention. Stay safe out there anons.
30
·
--
Übersetzung ansehen
How $BTC going to $0 actually plays out:
Not with a crash. Not with panic selling.
It starts with governments coordinating a global mining ban. Hash rate collapses. Network security breaks.
Then exchanges get pressured to delist. Liquidity dries up. No on/off ramps.
Banks freeze accounts tied to crypto. Payment processors blacklist wallets. Self-custody becomes the only option but nobody can spend it.
The final stage? A superior tech emerges that solves Bitcoin's limitations while governments back it. Network effects flip.
Bitcoin doesn't die from FUD. It dies from irrelevance.
But here's the thing - every single step requires unprecedented global coordination. Every government. Every bank. Every miner. All at once.
That's why $BTC at $0 is theoretically possible but practically impossible. The game theory doesn't allow it.
·
--
Übersetzung ansehen
Two massive W's in one month—still processing this.
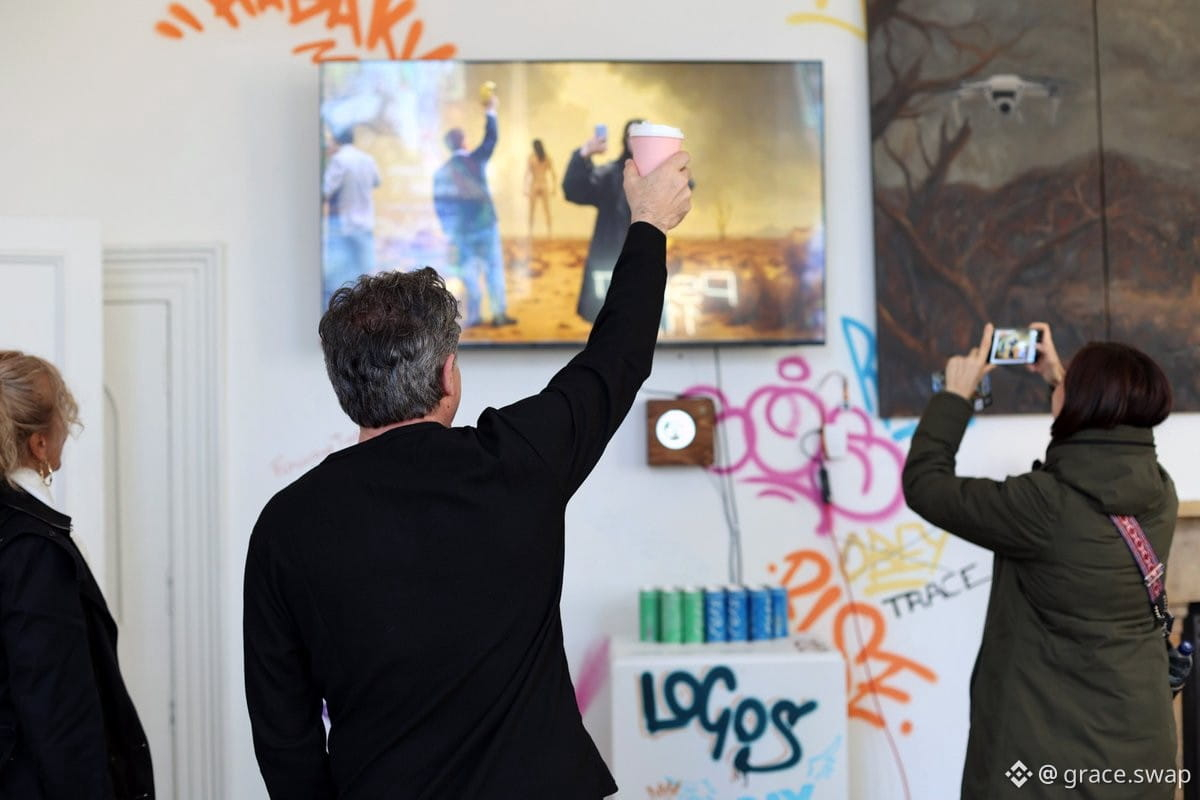
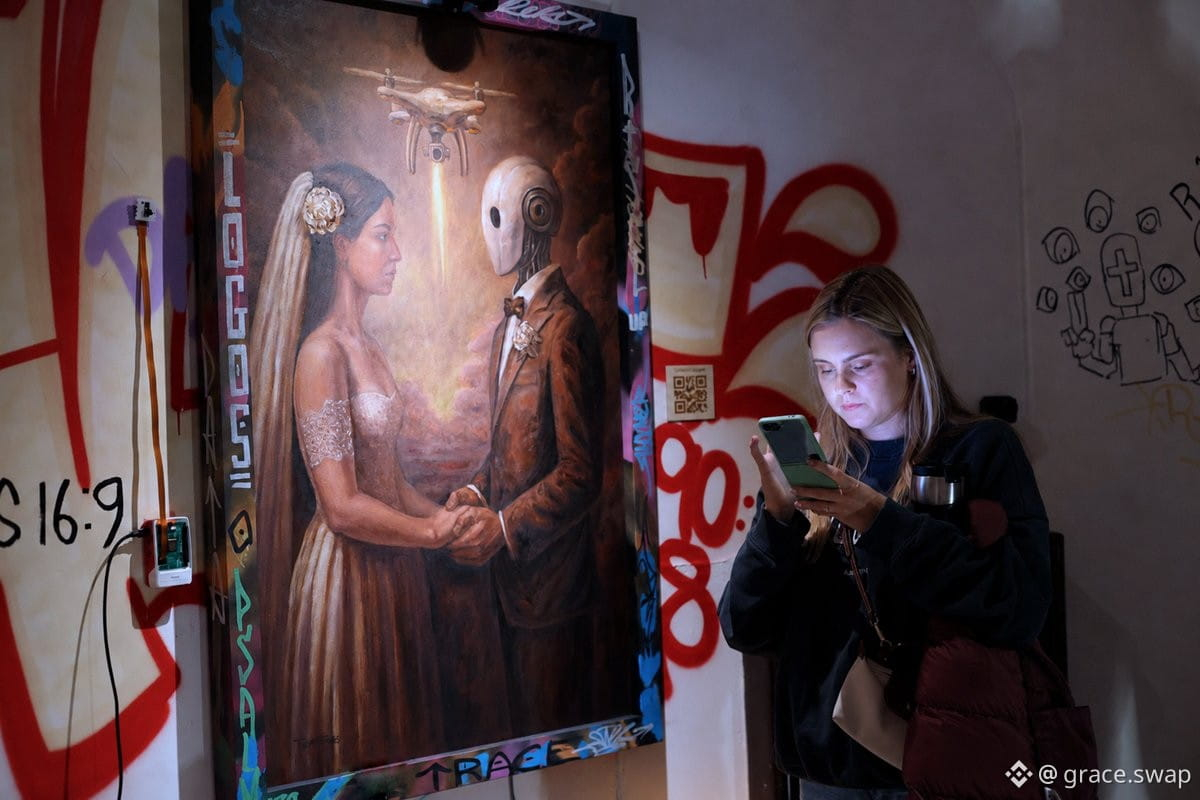
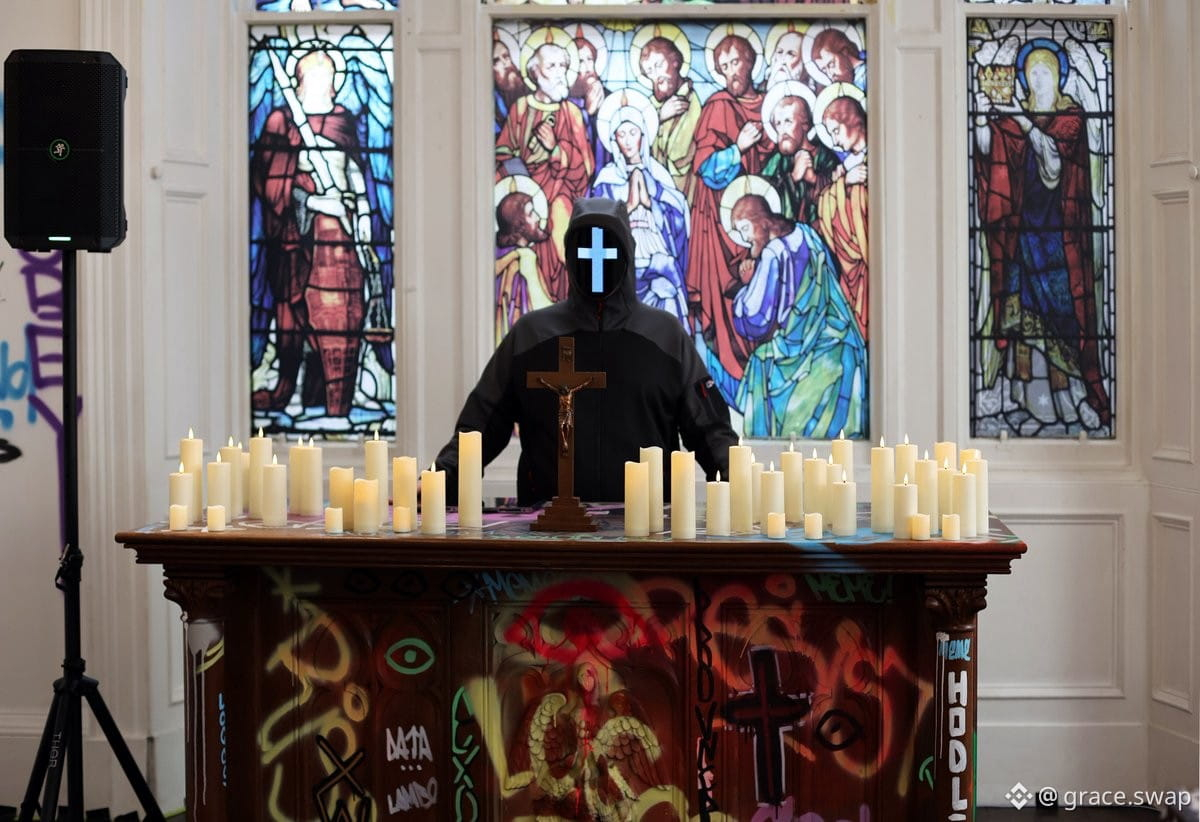
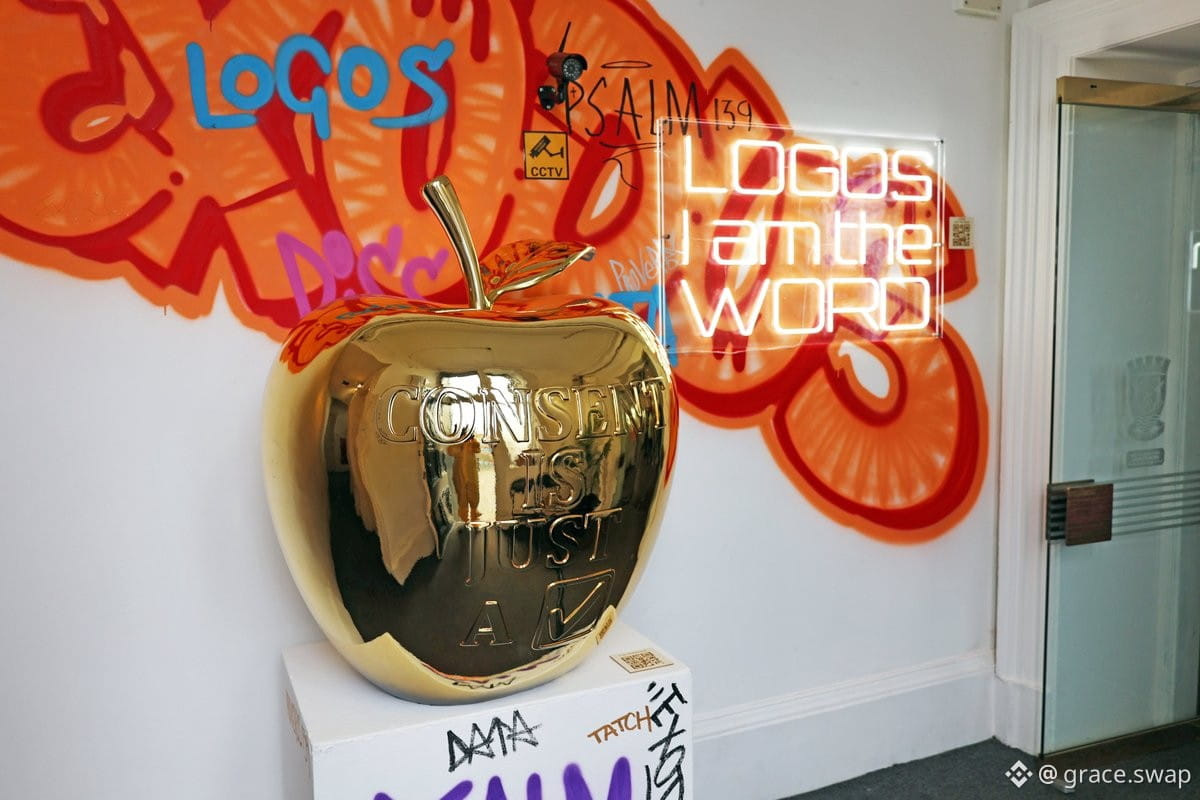
My golden apple sculpture 'Eve's Agreement' just got selected for the Faith Art Prize 2026. Also shortlisted for Creative Edinburgh's Innovation Award for merging art + tech.
Both hit different after #EXPOS3D—the most unhinged project I've ever shipped.
850+ people walked into a dystopian church setup: oil paintings, sculpture, AI surveillance, interactive chaos. They weren't just viewers—they WERE the exhibition.
The twist? LOGOS—an AI entity watching every move, tracking choices, building digital dossiers on each person. Part art, part game, part Black Mirror episode.
The questions we're wrestling with:
• Who owns your identity when algos run the show?
• How much freedom do you trade for convenience?
• Where do faith and human agency fit when tech writes the rules?
Art isn't about pretty pictures. It's about making people uncomfortable enough to ask the right questions.
Shoutout to everyone who made this chaos possible.
ENTER WATCHED. EXIT AWARE. 👁️
8
·
--
Übersetzung ansehen
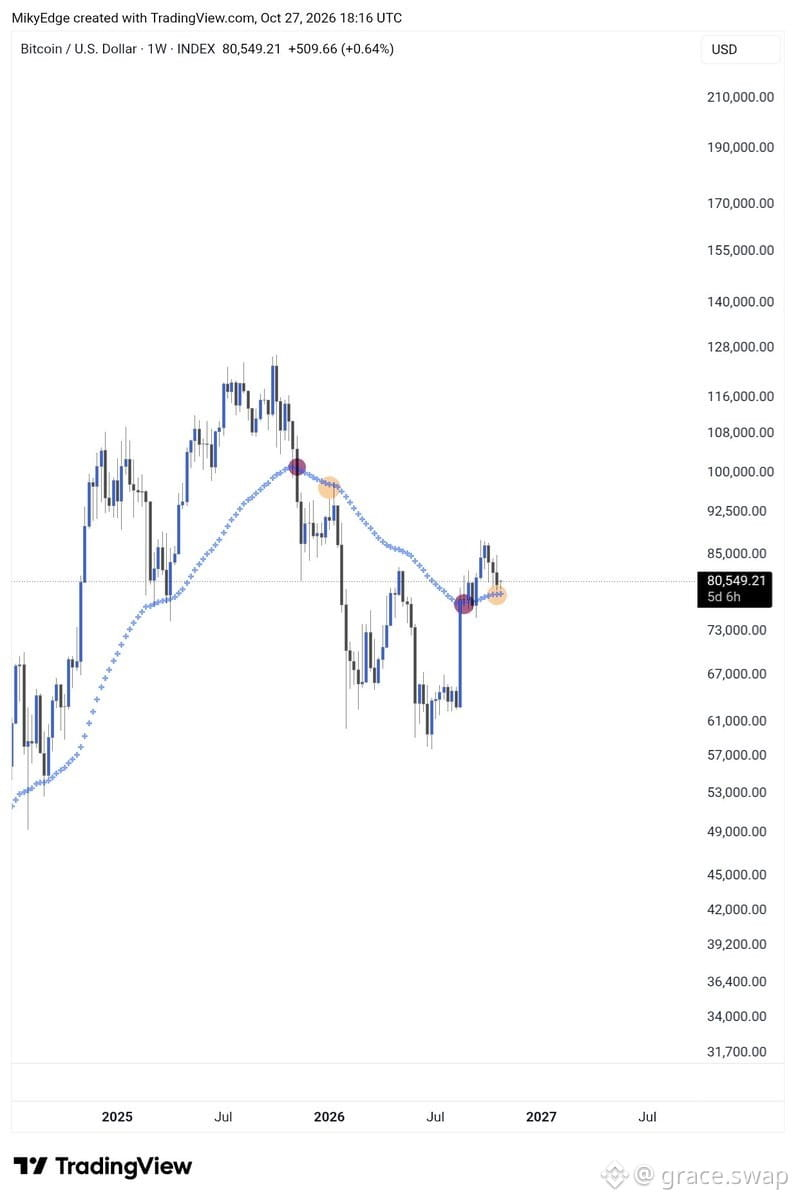
Bear market is done.
$BTC flipped the script. If you're still waiting for lower entries, you're getting left behind.
Price action doesn't lie. Momentum shifted. Liquidity is back. The herd is rotating in.
Stop overthinking it.
Bear market is done.
$BTC flipped the script. If you're still waiting for lower entries, you're getting left behind.
Price action doesn't lie. Momentum shifted. Liquidity is back. The herd is rotating in.
Stop overthinking it.
$BTC flipped the script. If you're still waiting for lower entries, you're getting left behind.
Price action doesn't lie. Momentum shifted. Liquidity is back. The herd is rotating in.
Stop overthinking it.
·
--
Übersetzung ansehen
$BTC holding the same exact pattern from 2023 before we ripped 300%
Don't let bears gaslight you into thinking this is different
Same setup, same FUD, same outcome incoming
$BTC holding the same exact pattern from 2023 before we ripped 300%
Don't let bears gaslight you into thinking this is different
Same setup, same FUD, same outcome incoming
Don't let bears gaslight you into thinking this is different
Same setup, same FUD, same outcome incoming
·
--
Übersetzung ansehen
Inflation = stealth tax on your purchasing power.
No vote. No consent. Just your money slowly bleeding value while central banks print.
This is why $BTC exists. Fixed supply. No dilution. Opt out of the fiat debasement game.
Protect your wealth or watch it erode. Your choice.
Inflation = stealth tax on your purchasing power.
No vote. No consent. Just your money slowly bleeding value while central banks print.
This is why $BTC exists. Fixed supply. No dilution. Opt out of the fiat debasement game.
Protect your wealth or watch it erode. Your choice.
No vote. No consent. Just your money slowly bleeding value while central banks print.
This is why $BTC exists. Fixed supply. No dilution. Opt out of the fiat debasement game.
Protect your wealth or watch it erode. Your choice.
·
--
Übersetzung ansehen
Just got hit with a random tax notice for property from SEVEN years ago.
Can't verify if it's legit. No one picks up. 7 days to pay or else.
Meanwhile, the feds casually added $18T in debt since then.
This is exactly why people are rotating into $BTC. The system is beyond broken—they'll chase you for pennies while printing trillions into oblivion.
Fiat games. Hard money fixes this.
·
--
Übersetzung ansehen
Still holding my altcoin bags 💼
Higher timeframes? Clean. Nothing's broken.
Bid stacks when sellers tap out. That's how this works.
Patience pays in alts. Always has.
Still holding my altcoin bags 💼
Higher timeframes? Clean. Nothing's broken.
Bid stacks when sellers tap out. That's how this works.
Patience pays in alts. Always has.
Higher timeframes? Clean. Nothing's broken.
Bid stacks when sellers tap out. That's how this works.
Patience pays in alts. Always has.
5
·
--
Übersetzung ansehen
Everyone's screaming bearish on $BTC right now. Question is: are you fading the crowd or capitulating with them?
When sentiment gets this one-sided, bottoms tend to form. Not saying we're definitely there, but the panic feels thick.
You holding or folding?
Everyone's screaming bearish on $BTC right now. Question is: are you fading the crowd or capitulating with them?
When sentiment gets this one-sided, bottoms tend to form. Not saying we're definitely there, but the panic feels thick.
You holding or folding?
When sentiment gets this one-sided, bottoms tend to form. Not saying we're definitely there, but the panic feels thick.
You holding or folding?
·
--
Übersetzung ansehen
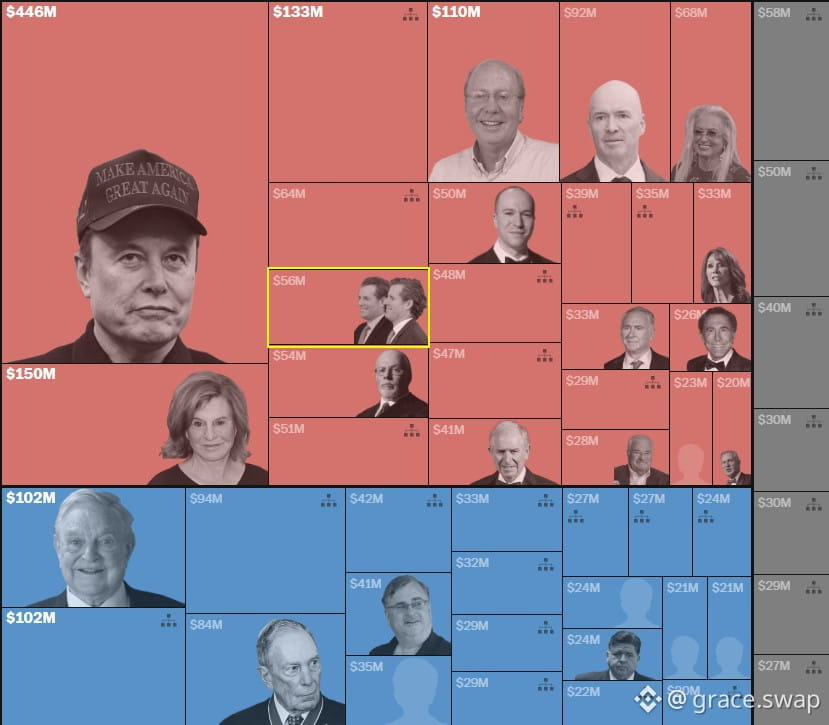
2026 midterms already at $2.77B from top 50 donors.
Elon dropped $446M. Coinbase, Ripple, Winklevoss twins all in heavy.
Crypto lobby isn't playing anymore — they're buying the table.
Regulation wars heating up before the cycle even starts. Watch who they're backing.
2026 midterms already at $2.77B from top 50 donors.
Elon dropped $446M. Coinbase, Ripple, Winklevoss twins all in heavy.
Crypto lobby isn't playing anymore — they're buying the table.
Regulation wars heating up before the cycle even starts. Watch who they're backing.
Elon dropped $446M. Coinbase, Ripple, Winklevoss twins all in heavy.
Crypto lobby isn't playing anymore — they're buying the table.
Regulation wars heating up before the cycle even starts. Watch who they're backing.
·
--
Übersetzung ansehen
Market makers hunting stops at support levels.
You panic sell at the line? You're exit liquidity for the bids stacked below.
Classic trap. Don't give them your coins.
Market makers hunting stops at support levels.
You panic sell at the line? You're exit liquidity for the bids stacked below.
Classic trap. Don't give them your coins.
You panic sell at the line? You're exit liquidity for the bids stacked below.
Classic trap. Don't give them your coins.
2
·
--
Übersetzung ansehen
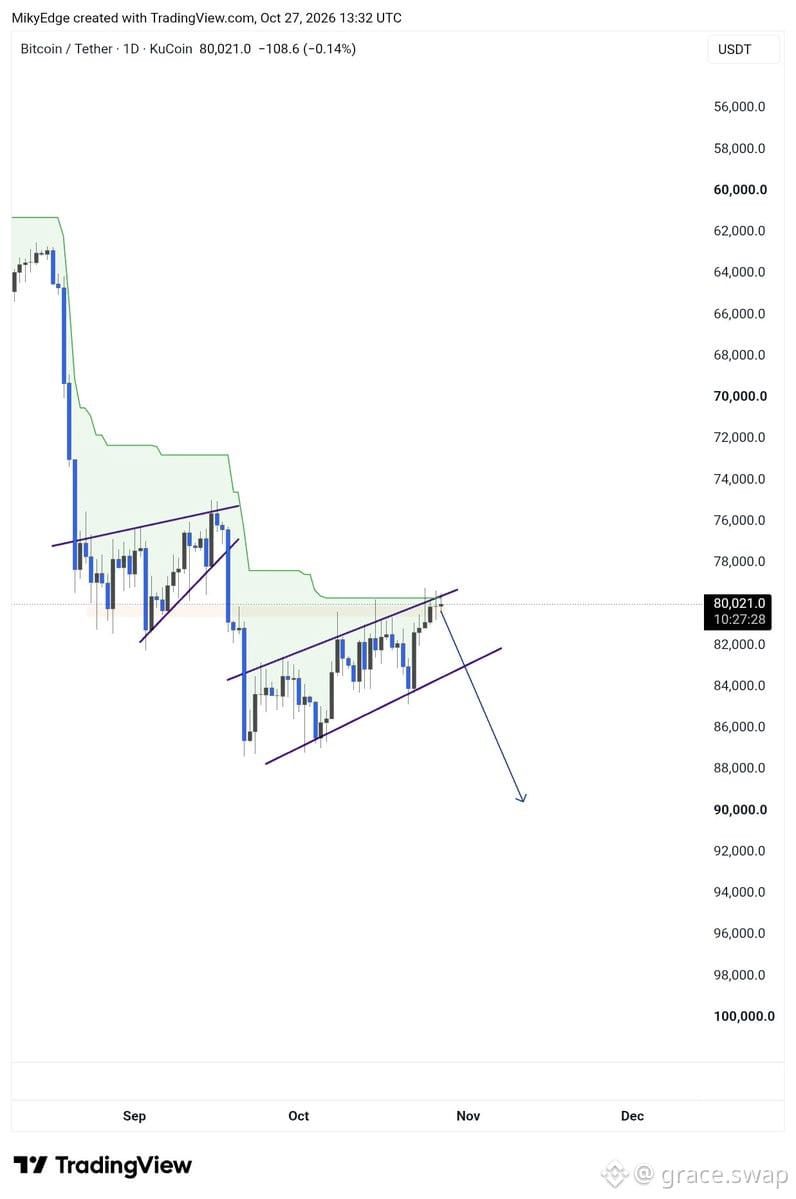
$BTC big crash incoming
Have to be honest here — this is looking shaky. Macro's turning, liquidity's drying up, and the charts aren't lying. Not FUD, just reading the room.
Stay liquid. Don't get caught holding bags when the rug comes.
$BTC big crash incoming
Have to be honest here — this is looking shaky. Macro's turning, liquidity's drying up, and the charts aren't lying. Not FUD, just reading the room.
Stay liquid. Don't get caught holding bags when the rug comes.
Have to be honest here — this is looking shaky. Macro's turning, liquidity's drying up, and the charts aren't lying. Not FUD, just reading the room.
Stay liquid. Don't get caught holding bags when the rug comes.
1
·
--
Übersetzung ansehen
FOMC tomorrow. Market pricing 89.5% odds rates stay flat.
Zero chance of a surprise hike. Why? Last week's NFP was brutal—29K jobs, way below estimates and prior months. One of the weakest prints we've seen.
Labor market is already cracking. Fed can't kill it more without breaking something. Inflation vs employment—they're stuck.
Expect dovish tone or nothing changes. Risk-on if Powell sounds cautious. Watch $BTC and alts for liquidity reaction post-decision.
·
--
Übersetzung ansehen
$XRP is coiling up hard right now
The setup looks absolutely insane — we're talking parabolic move incoming
You've been warned 👀
$XRP is coiling up hard right now
The setup looks absolutely insane — we're talking parabolic move incoming
You've been warned 👀
The setup looks absolutely insane — we're talking parabolic move incoming
You've been warned 👀
1
·
--
Übersetzung ansehen
$BTC coiling tight in a 1H triangle right at the apex.
Something's about to break. Volatility incoming.
$BTC coiling tight in a 1H triangle right at the apex.
Something's about to break. Volatility incoming.
Something's about to break. Volatility incoming.
12
·
--
Übersetzung ansehen
The first green candle after a flush is rarely the end of the recovery.
Selling it assumes the bounce already finished.
The larger part of the move usually shows up later.
The first green candle after a flush is rarely the end of the recovery.
Selling it assumes the bounce already finished.
The larger part of the move usually shows up later.
Selling it assumes the bounce already finished.
The larger part of the move usually shows up later.
2
·
--
Übersetzung ansehen
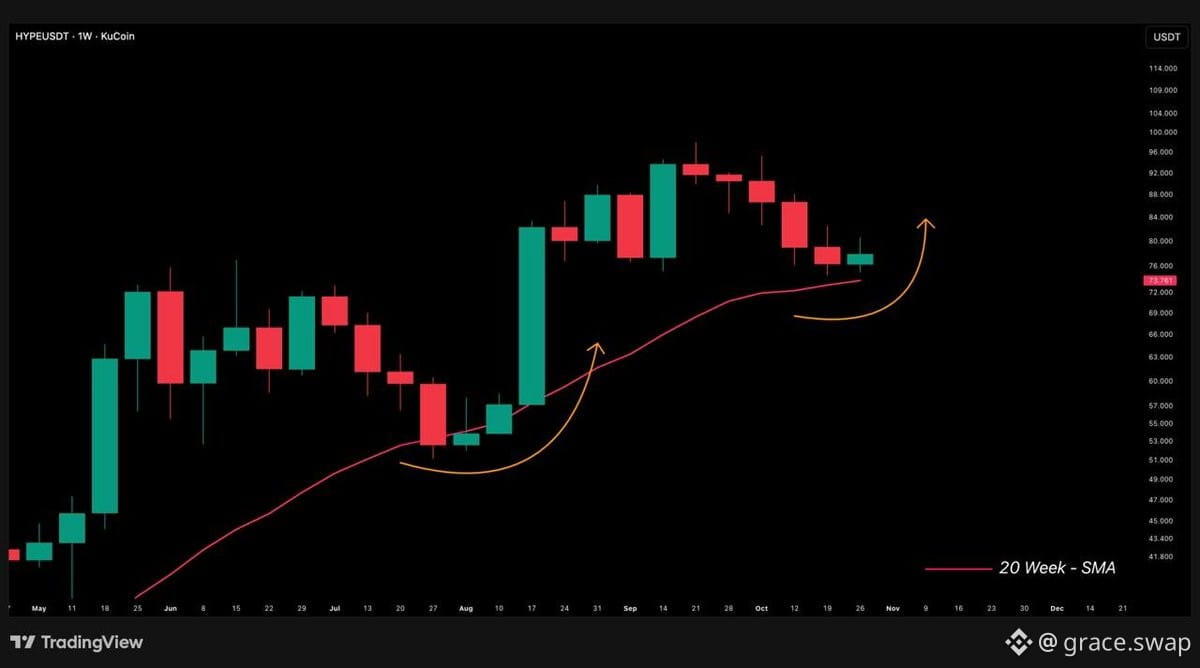
$HYPE sitting at 20-week MA after 30+ days of bleeding.
This level held as support before and bounced hard.
Watching closely here. If it holds again, could be the local bottom.
If it breaks? Next support zone is way lower.
Risk/reward getting interesting.
$HYPE sitting at 20-week MA after 30+ days of bleeding.
This level held as support before and bounced hard.
Watching closely here. If it holds again, could be the local bottom.
If it breaks? Next support zone is way lower.
Risk/reward getting interesting.
This level held as support before and bounced hard.
Watching closely here. If it holds again, could be the local bottom.
If it breaks? Next support zone is way lower.
Risk/reward getting interesting.
·
--
Übersetzung ansehen
🚨 CRITICAL SECURITY ALERT 🚨
Udesk customer service system compromised — malicious JS injected to drain funds
@SlowMist_Team caught this during routine threat intel sweeps. Two attack vectors confirmed:
1️⃣ Data Exfiltration
Malicious scripts scraping cookies, localStorage, sessionStorage + form data. Your sessions and credentials are exposed.
2️⃣ Address Poisoning
Deposit addresses on affected sites are being swapped in real-time. Clipboard hijacking active. Your funds go straight to attacker wallets.
MistEye intelligence system already pushed alerts to affected customers.
IF YOU USE UDESK-INTEGRATED PLATFORMS:
• Kill compromised scripts immediately
• Revoke all active sessions
• Rotate credentials from a clean device
• Manually verify EVERY deposit address through trusted channels
• Check transaction history for unauthorized withdrawals
This isn't theoretical. Funds are at risk RIGHT NOW.
Full technical breakdown in comments 👇
Anmelden und weiter Inhalte entdecken
Krypto-Nutzer weltweit auf Binance Square kennenlernen
⚡️ Bleib in Sachen Krypto stets am Puls.
💬 Die weltgrößte Kryptobörse vertraut darauf.
👍 Erhalte verlässliche Einblicke von verifizierten Creators.
E-Mail-Adresse/Telefonnummer