
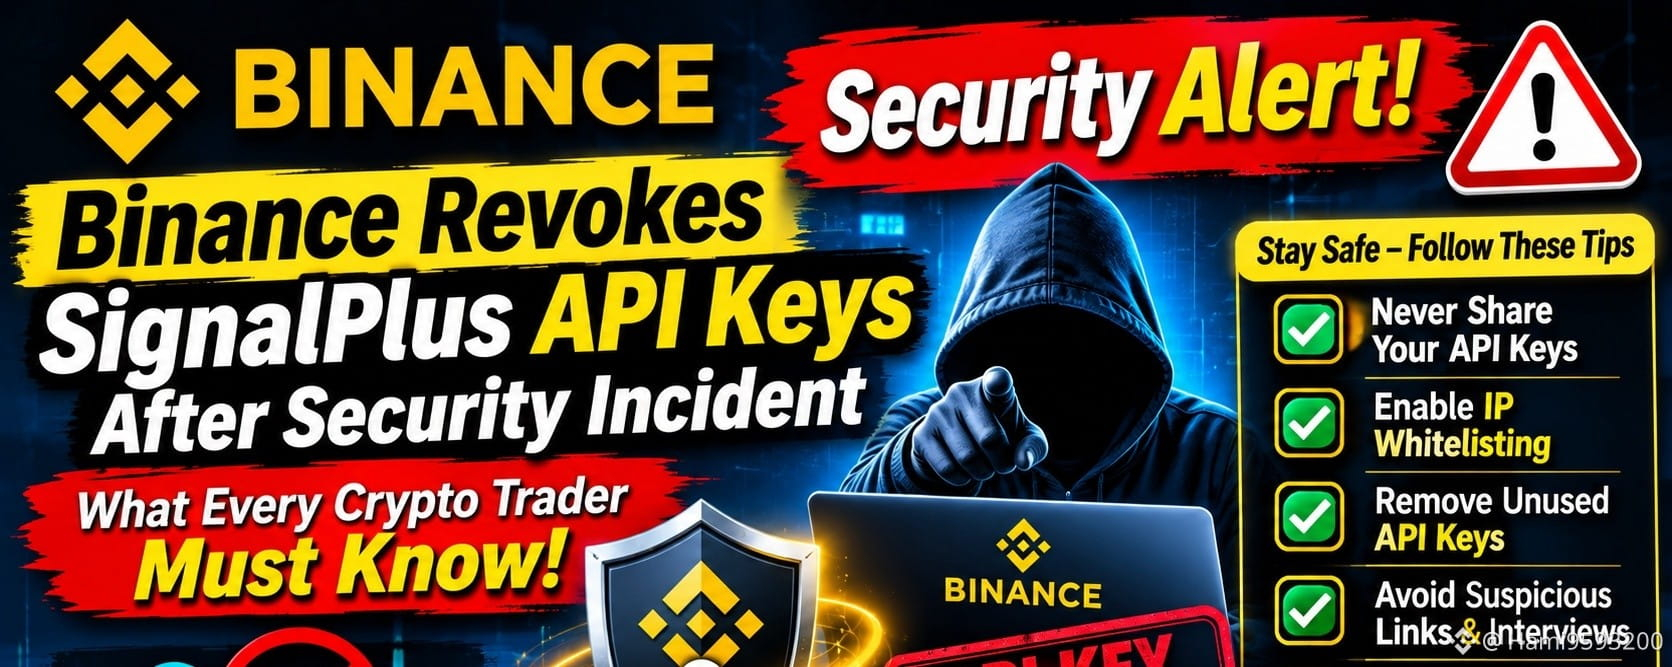
🚨 BINANCE REVOKES SIGNALPLUS API KEYS AFTER SECURITY INCIDENT: WHAT EVERY CRYPTO TRADER MUST KNOW
Crypto Security Alert | November 10, 2026
The cryptocurrency industry has received another important cybersecurity warning. This time, the focus is on third-party trading platform SignalPlus, following a security incident that prompted Binance and Deribit to take immediate protective action.
On November 5, 2026, Binance announced that it had proactively removed all API keys connected to SignalPlus after the platform reported a potential security issue. Binance emphasized that its own systems were unaffected and customer funds remained safe.
Although this incident was not a breach of Binance's own systems, it highlights a serious security risk that many cryptocurrency traders overlook: third-party applications connected to exchange accounts.
🔍 1. What Actually Happened?
According to SignalPlus's incident disclosure, the attack began through a compromised Telegram account belonging to a contact at one of its third-party technology vendors.
The attacker reportedly impersonated that contact and approached a SignalPlus engineer with a fake Microsoft Teams meeting invitation.
Unfortunately, the social engineering attempt compromised the engineer's computer.
The attacker subsequently used the engineer's access privileges to target the company's internal network. SignalPlus detected suspicious activity on November 4 and said it contained the intrusion.
The company reported that losses were below $82,000 and committed to reimbursing affected users.
SignalPlus also temporarily suspended its services while conducting security reviews and implementing additional protections.
🛡️ 2. Why Did Binance Remove API Keys?
Binance responded by removing every API key associated with SignalPlus as a precautionary measure.
This action was designed to prevent the third-party platform from continuing to access connected Binance accounts through those credentials.
Binance also advised affected users to:
Log in directly to their Binance accounts.
Review open orders and trading positions.
Avoid reconnecting API keys until SignalPlus confirms the issue is resolved.
Enable IP whitelisting when using API connections.
Deribit also removed SignalPlus-connected API keys and reported no indication that its own systems or data had been affected.
🔐 3. Understanding API Keys: A Hidden Security Risk
An API (Application Programming Interface) key allows an external application to communicate with your cryptocurrency exchange account.
Traders commonly use API connections for:
Automated trading bots.
Portfolio management.
Market analysis tools.
Trading strategy automation.
Account monitoring.
However, API keys can become dangerous when they are exposed, stolen or stored insecurely.
Depending on the permissions granted, an attacker could potentially execute unauthorized trades or access account information.
Even when withdrawal permissions are disabled, compromised trading permissions can still create significant financial risks.
This is why traders should never treat API keys like ordinary passwords.
⚠️ 4. Five Important Security Lessons for Crypto Traders
Every cryptocurrency investor and trader should follow these basic security practices:
1. Never share your API Secret Key
Keep your API credentials private. Never send them to unknown individuals or suspicious websites.
2. Enable IP Whitelisting
Whenever supported, restrict API access to approved IP addresses.
3. Remove Unused API Keys
Regularly review connected applications and immediately revoke keys you no longer need.
4. Avoid Suspicious Meeting Invitations
Fake recruitment interviews, Telegram messages and Microsoft Teams invitations can be used in social engineering attacks.
Never download unknown software or open suspicious attachments.
5. Monitor Your Trading Activity
Regularly check your account history, open orders and connected applications for unusual activity.
🌍 5. What Does This Mean for the Future of Crypto Security?
The SignalPlus incident demonstrates that cybersecurity is not only about protecting cryptocurrency exchanges.
Third-party trading platforms, software providers, employees and individual users are also important parts of the security ecosystem.
A single compromised device or stolen credential can create risks across multiple connected services.
For the cryptocurrency industry, stronger API management, mandatory IP restrictions, employee security training and improved monitoring should become essential standards.
Exchanges and external service providers must work together to identify threats before they become larger incidents.
💡 Final Thoughts
Crypto security is everyone's responsibility.
Binance's decision to revoke SignalPlus-linked API keys shows why precautionary action and rapid communication matter when a potential security issue appears.
For traders, the lesson is simple: never give an application more access than it needs, and never connect your account to a platform you do not trust.
Your cryptocurrency investment deserves the same protection as your bank account.
Remember: Protect your keys, verify every connection, and think before you click.
💬 Let's Discuss!
Do you use third-party trading bots or API connections with your Binance account?
What do you think is the biggest security threat in crypto today?
API Key Theft
Phishing and Fake Interviews
Malware and Hacking
Weak Account Security
Share your opinion in the comments!
#BinanceSquare #Binance #CryptoSecurity #API3USDT #BlockchainSecurity