🚨 BINANCE REVEALS HOW THE OCTOBER 29 ATTACK HAPPENED — A WAKE-UP CALL FOR THE ENTIRE CRYPTO INDUSTRY!
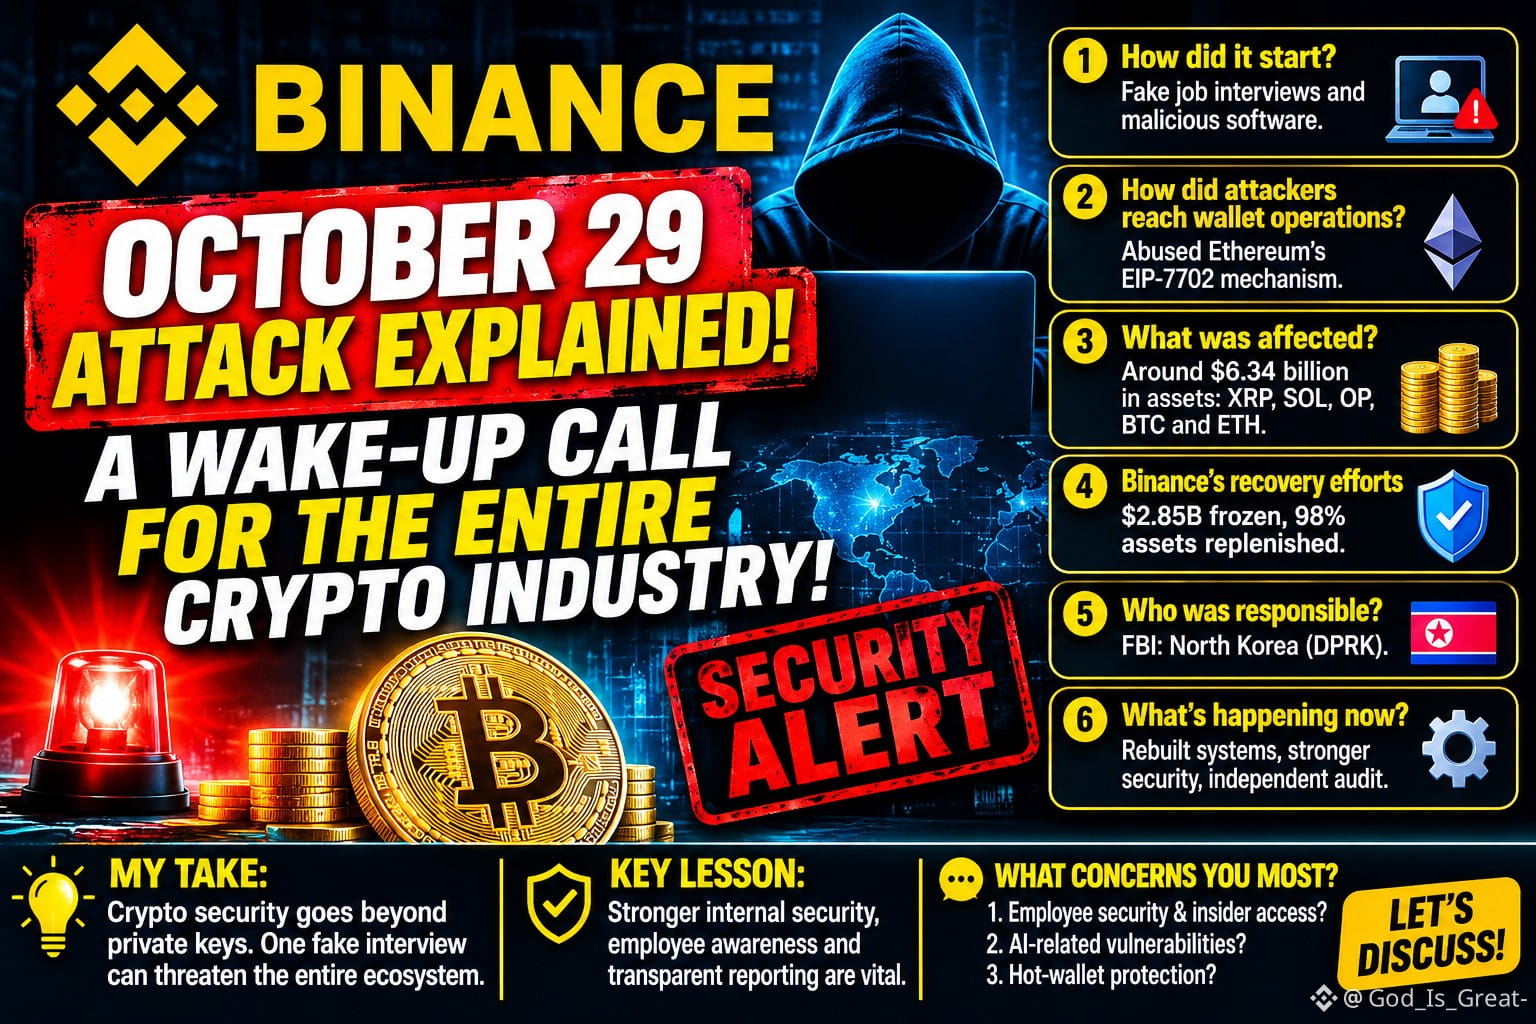
Binance has released new investigation details about the October 29 security incident, revealing a sophisticated attack that went far beyond traditional crypto hacking.
According to Binance's November 3 update, attackers reportedly used fake recruitment interviews, malicious software and compromised employee access to penetrate internal systems.
Here's what we learned:
1. How did it start?
Attackers reportedly targeted employees through fake job interviews and malicious software, compromising devices and internal credentials.
2. How did attackers reach wallet operations?
They allegedly exploited compromised internal access and abused Ethereum's EIP-7702 authorization mechanism to obtain unauthorized execution rights over a Binance hot wallet.
3. What was affected?
Binance reported approximately $6.34 billion in affected digital assets, including XRP, SOL, OP, BTC and ETH.
4. Binance's recovery efforts
As of October 31, Binance reported that approximately $2.85 billion had been frozen or intercepted, while 98% of impacted token assets had been replenished
5. Who was responsible?
Binance reported that the FBI attributed the incident to North Korea (DPRK)
6. What's happening now?
Binance says it has rebuilt affected wallet systems, replaced compromised devices, strengthened access controls and initiated an independent cybersecurity review.
MY TAKE:
The biggest lesson is that crypto security goes far beyond protecting private keys.
A fake job interview, one malicious download or compromised employee credentials can create a serious threat to an entire financial ecosystem.
Exchanges must invest in stronger internal security, employee awareness, independent audits and transparent incident reporting.
One security incident should make the entire crypto industry stronger.
💬 What concerns you most?
Employee security and insider access?
AI-related cybersecurity vulnerabilities?
Hot-wallet protection and authorization mechanisms?
Let's discuss!
#BinanceIncidentReport
Binance has released new investigation details about the October 29 security incident, revealing a sophisticated attack that went far beyond traditional crypto hacking.
According to Binance's November 3 update, attackers reportedly used fake recruitment interviews, malicious software and compromised employee access to penetrate internal systems.
Here's what we learned:
1. How did it start?
Attackers reportedly targeted employees through fake job interviews and malicious software, compromising devices and internal credentials.
2. How did attackers reach wallet operations?
They allegedly exploited compromised internal access and abused Ethereum's EIP-7702 authorization mechanism to obtain unauthorized execution rights over a Binance hot wallet.
3. What was affected?
Binance reported approximately $6.34 billion in affected digital assets, including XRP, SOL, OP, BTC and ETH.
4. Binance's recovery efforts
As of October 31, Binance reported that approximately $2.85 billion had been frozen or intercepted, while 98% of impacted token assets had been replenished
5. Who was responsible?
Binance reported that the FBI attributed the incident to North Korea (DPRK)
6. What's happening now?
Binance says it has rebuilt affected wallet systems, replaced compromised devices, strengthened access controls and initiated an independent cybersecurity review.
MY TAKE:
The biggest lesson is that crypto security goes far beyond protecting private keys.
A fake job interview, one malicious download or compromised employee credentials can create a serious threat to an entire financial ecosystem.
Exchanges must invest in stronger internal security, employee awareness, independent audits and transparent incident reporting.
One security incident should make the entire crypto industry stronger.
💬 What concerns you most?
Employee security and insider access?
AI-related cybersecurity vulnerabilities?
Hot-wallet protection and authorization mechanisms?
Let's discuss!
#BinanceIncidentReport