

The biggest lesson from a major crypto security incident isn't always about how much money was lost. Sometimes, it's about how easily the systems protecting billions of dollars can be compromised.
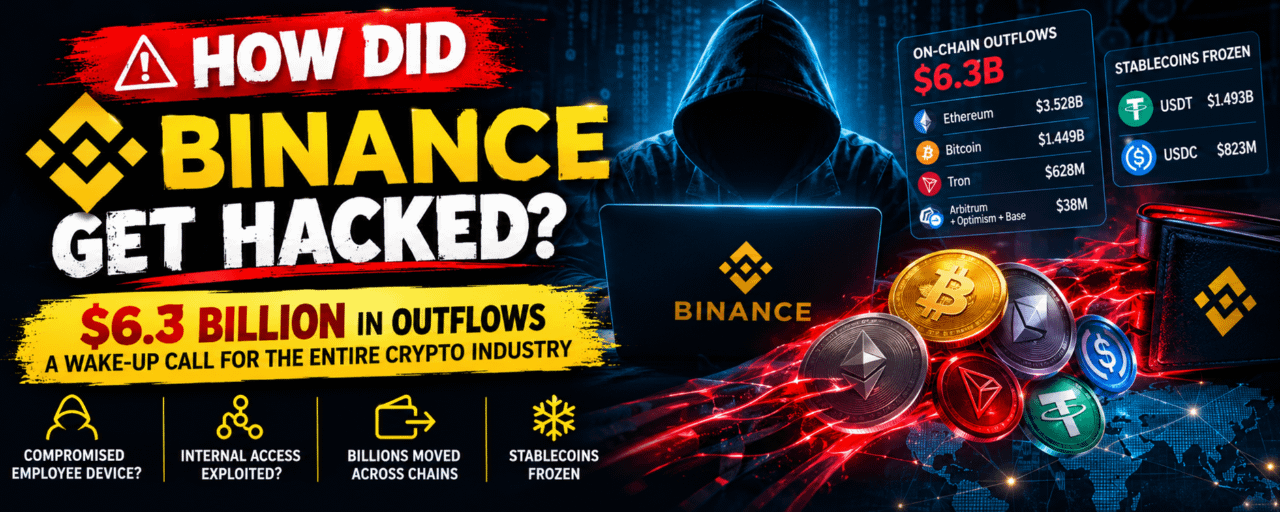
On October 29, 2026, on-chain investigators identified massive outflows from Binance-labeled wallets, with estimates reaching approximately $6.3 billion. Meanwhile, Tether and Circle reportedly froze billions in suspicious stablecoin assets.
But here's what makes this incident particularly concerning:
The reported attack may not have required hackers to steal Binance's wallet private keys.
🔍 How Did the Attack Happen?
According to initial reporting, the attack involved a compromised DevOps engineer's laptop.
The suspected attack chain highlights how a single compromised employee device can potentially expose critical internal infrastructure.
Employee device compromised: Attackers reportedly gained access to an engineer's laptop.
Internal infrastructure accessed: They allegedly used that access to reach an internal service environment.
Withdrawal infrastructure exploited: The attackers reportedly manipulated a trusted internal withdrawal process to authorize unauthorized transactions.
Funds moved across blockchains: Billions in assets were transferred through networks including Ethereum, Bitcoin and Tron.
Stablecoins frozen: Tether and Circle took action to freeze identified suspicious funds.
This is the frightening part: You don't necessarily need to break the strongest vault if you can compromise the system that authorizes access to it.
💰 Billions in Outflows: What Happened On-Chain?
Initial on-chain figures reported significant movements:
Ethereum: $3.528 billion
Bitcoin: $1.449 billion
Tron: $628 million
Arbitrum, Optimism and Base: $38 million combined
Stablecoins reportedly frozen:
USDT: $1.493 billion
USDC: $823 million
These figures represent reported blockchain movements and freezes, not independently verified final theft or recovery totals. The investigation remains important for establishing exactly what happened.
⚠️ The Bigger Problem: Centralized Infrastructure
Crypto was supposed to give people financial freedom without depending entirely on centralized institutions.
Yet this incident raises some uncomfortable questions:
How secure are centralized exchanges if employee devices can become potential attack entry points?
Are internal withdrawal systems sufficiently isolated from employee workstations?
Can exchanges provide meaningful transparency when billions of dollars move unexpectedly?
How much of our crypto security depends on a handful of companies and their internal controls?
Even if an exchange has advanced encryption, cold storage and multiple security layers, a weakness in its operational infrastructure can create serious risks.
🧠 What Should Crypto Investors Learn?
This incident is a reminder that exchange security and blockchain security are not the same thing.
Investors should:
Avoid keeping unnecessary funds on centralized exchanges.
Enable strong 2FA and withdrawal protection.
Never expose API keys or account credentials.
Verify security announcements through official channels.
Never trust fake recovery services or compensation links.
🔥 My Final Thoughts
The crypto industry cannot keep promoting decentralization while leaving critical infrastructure vulnerable to centralized points of failure.
If one compromised device can potentially create access to billions of dollars, the industry needs to rethink how it protects its most sensitive systems.
This is bigger than Binance.
It is a warning to every centralized exchange, every crypto investor and every company holding billions in digital assets.
The real question isn't just how much money moved. It's how the attackers managed to get inside the system in the first place.
What do you think?
Is keeping funds on centralized exchanges still worth the risk, or is self-custody becoming more important than ever?
@Binance


#Binance #CryptoSecurity #Blockchain #CryptoNews #EarningsSeason