🚨 CRITICAL iOS EXPLOIT ACTIVELY USED TO DRAIN WALLETS
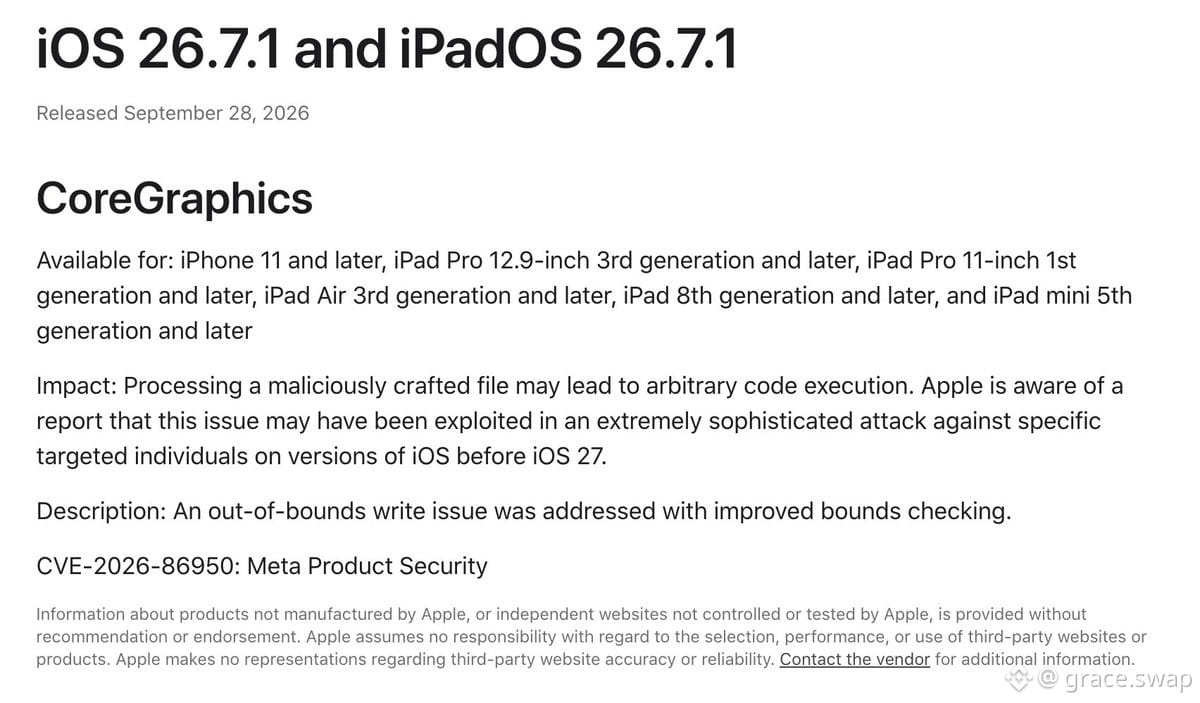
Apple just patched CVE-2026-86950 in iOS/iPadOS 26.7.1 — an out-of-bounds write bug that lets attackers execute arbitrary code on your device.
Apple CONFIRMED this was exploited in targeted attacks against specific individuals running iOS <27. Translation: state-level or organized crime hitting high-value targets.
We've been tracking iOS exploit chains specifically targeting crypto wallet seed phrases and private keys. If you're holding serious bags on mobile, you're in the blast radius.
🔐 DO THIS NOW:
Update ALL Apple devices immediately
Don't install random apps or click sus links in Safari/in-app browsers
Treat every unexpected file/link/install prompt as hostile
Your seed phrase is only as secure as your device. Patch or get rekt.