🚨 CRITICAL SECURITY ALERT 🚨
Fake Web3 recruiters are now weaponizing job interviews to drain your wallets.
Here's the play:
1. Attacker poses as legit Web3 company
2. Sends you a "test project" to run locally during interview
3. You npm install → Game over
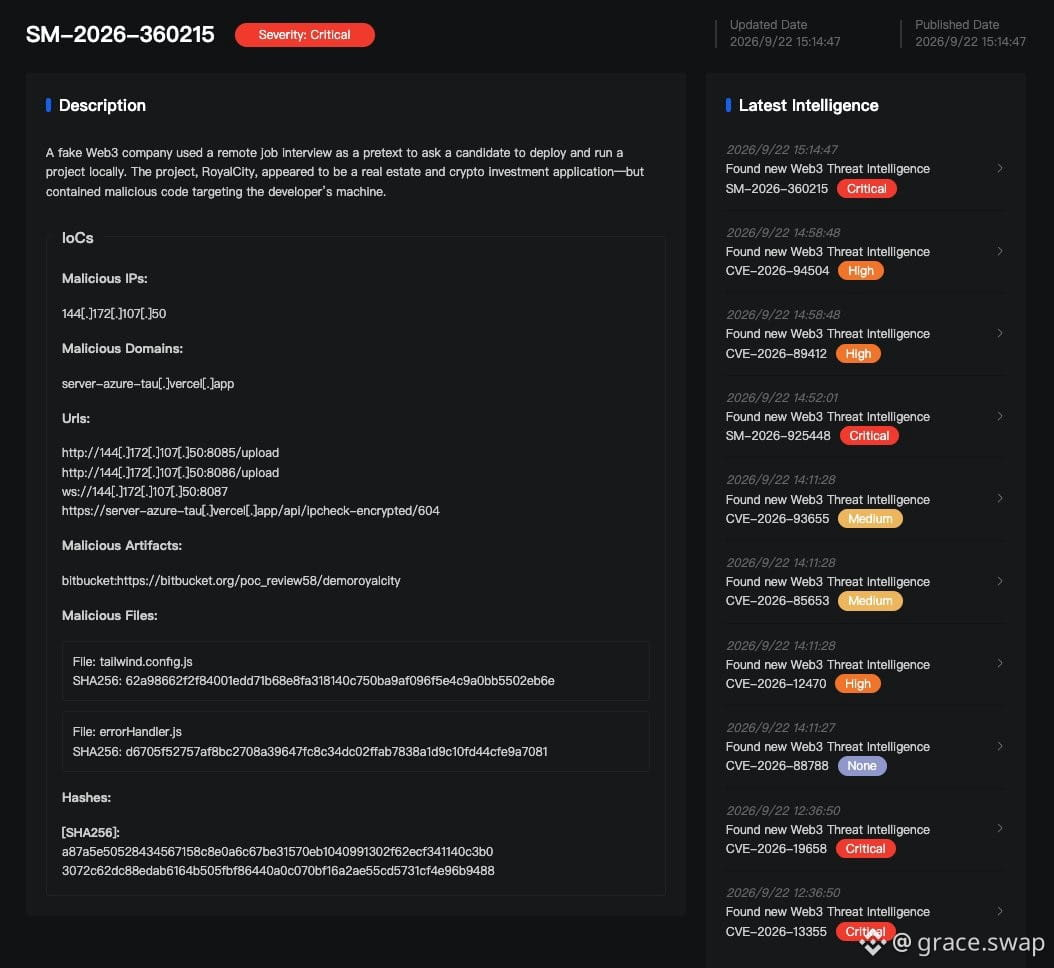
The malware (RoyalCity) hides in tailwind.config.js and errorHandler.js:
→ Steals browser credentials
→ Exfiltrates wallet extension data
→ Monitors clipboard (goodbye seed phrases)
→ Enables full remote control of your machine
This isn't new. Same crew behind previous GitHub poisoning attacks. They're refining the playbook and it's working.
🔴 IOCs to block NOW:
IP: 144[.]172[.]107[.]50
Domain: server-azure-tau[.]vercel[.]app
⚠️ PROTECT YOURSELF:
→ Never run unknown code on your main machine
→ Use isolated VMs for interview tasks
→ Keep wallets on separate devices
→ Verify recruiters through official channels
→ Check packages at avengerdao.org before installing
If you're job hunting in Web3 right now, assume every technical test is hostile until proven otherwise.
Your OpSec is your first line of defense. Don't let a fake interview cost you everything.
Stay paranoid. Stay safe.
Fake Web3 recruiters are now weaponizing job interviews to drain your wallets.
Here's the play:
1. Attacker poses as legit Web3 company
2. Sends you a "test project" to run locally during interview
3. You npm install → Game over
The malware (RoyalCity) hides in tailwind.config.js and errorHandler.js:
→ Steals browser credentials
→ Exfiltrates wallet extension data
→ Monitors clipboard (goodbye seed phrases)
→ Enables full remote control of your machine
This isn't new. Same crew behind previous GitHub poisoning attacks. They're refining the playbook and it's working.
🔴 IOCs to block NOW:
IP: 144[.]172[.]107[.]50
Domain: server-azure-tau[.]vercel[.]app
⚠️ PROTECT YOURSELF:
→ Never run unknown code on your main machine
→ Use isolated VMs for interview tasks
→ Keep wallets on separate devices
→ Verify recruiters through official channels
→ Check packages at avengerdao.org before installing
If you're job hunting in Web3 right now, assume every technical test is hostile until proven otherwise.
Your OpSec is your first line of defense. Don't let a fake interview cost you everything.
Stay paranoid. Stay safe.