

 Project Binance has become the center of one of the most alarming cryptocurrency security stories of 2026. What makes this incident particularly disturbing is not just the reported $6.3 billion in stolen digital assets, but the growing picture of how carefully the operation may have been planned.
The FBI has attributed the attack to North Korean-linked hackers known as TraderTraitor. That name carries weight in the crypto industry because North Korea has repeatedly been linked to major digital asset thefts. But this latest incident takes the conversation to another level. We are talking about an operation involving billions of dollars, multiple blockchain networks and security systems that millions of cryptocurrency users trust every day.
According to blockchain intelligence firm TRM Labs, approximately $6.36 billion moved from Binance-attributed wallets across ten different blockchains. A large portion of the transactions reportedly happened within around 20 minutes. Just imagine watching that much money move in such a short period. For an ordinary investor, a delayed withdrawal can be frustrating. For an exchange dealing with billions in assets, an incident like this can turn into a full-scale crisis before most customers even understand what is happening.
What makes the story more interesting is the possible way the attackers gained access. Binance's initial investigation pointed toward a compromised laptop belonging to a DevOps engineer. The company said it had not found evidence of a direct private-key leak at that stage. This detail deserves more attention because it suggests the problem may have involved access to internal systems rather than somebody simply breaking into a wallet.
And that is where things get uncomfortable.
People often imagine crypto hacks as someone sitting behind a computer, guessing passwords or exploiting a coding mistake. The reality can be much more complicated. Large exchanges depend on employees, internal permissions, cloud services, transaction approvals and several layers of software. Every connection has to work properly. If an attacker finds a way into the wrong part of that environment, even a company with substantial security resources can face serious trouble.
TRM Labs also reported signs that the attackers had prepared for the operation well before the major transfers began. Its analysis identified preliminary activity, testing and wallet preparations before the large-scale movement of assets. In other words, the visible theft may have been the final step of a much longer process.
The FBI's involvement has now added another dimension to the investigation. US authorities have publicly connected the incident to North Korea's TraderTraitor operation and issued warnings about cryptocurrency addresses associated with the stolen funds. Investigators are also asking exchanges, blockchain services and other industry participants to help identify and restrict suspicious transactions.
But identifying the people or group responsible is not the same as recovering the money.
That distinction is important. Cryptocurrency transactions can be traced through public blockchains, but tracing funds does not automatically give investigators the power to reverse them. Some assets can be frozen by their issuers, while others move through decentralized systems where there is no central authority capable of stopping a transaction.
There has already been some progress on that front. TRM Labs reported that several companies, including Tether, Circle and Ripple, froze approximately $2.67 billion in stablecoins connected to the incident. Arbitrum's Security Council also froze certain assets on its network. That is a substantial response, although it does not mean the entire stolen amount has been recovered.
Meanwhile, Binance has been trying to reassure customers that the financial damage will not simply be passed on to them. The exchange said it would cover the losses using its own resources and its Secure Asset Fund for Users. Its subsequent updates reported that approximately 95% of the affected amount had been covered.
For customers, that commitment matters. Nobody wants to wake up, open an exchange account and discover that their money has disappeared because of something happening behind the scenes. Still, replacing the affected assets is only one part of the responsibility. Users also deserve a clear explanation of what happened and what the exchange is changing to prevent another incident.
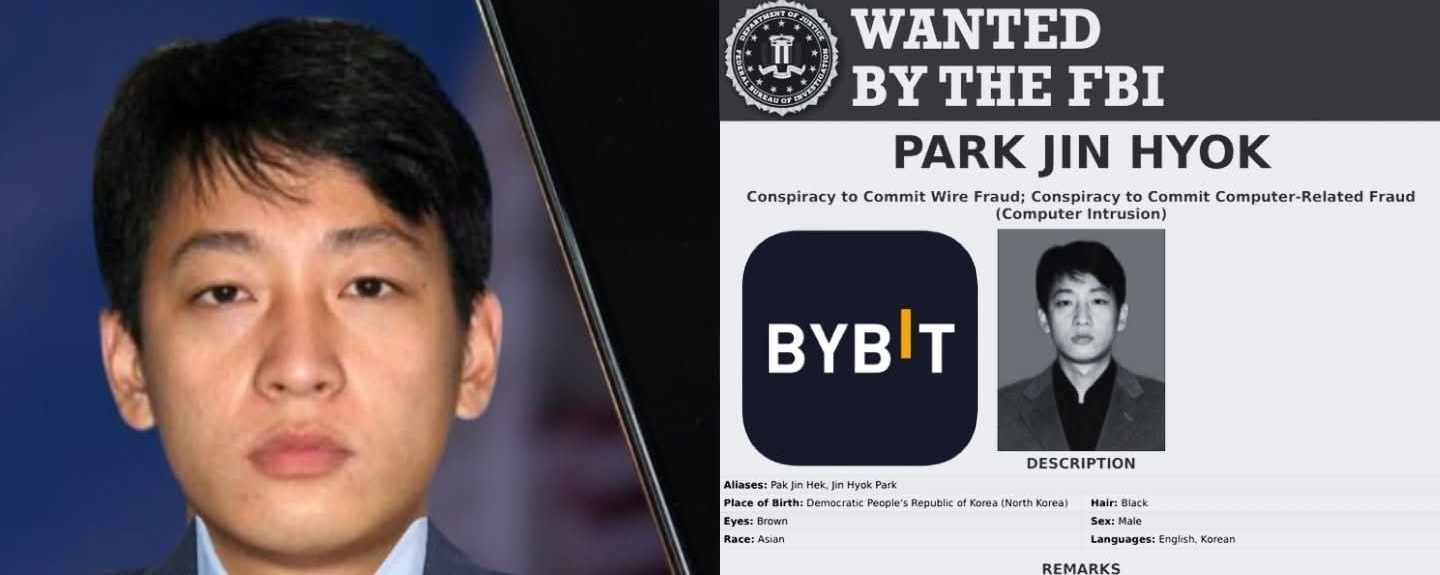
There is another reason this story deserves attention. North Korean-linked hackers have previously been connected to some of the largest cryptocurrency thefts on record. The FBI also attributed the 2025 Bybit attack, involving approximately $1.5 billion, to TraderTraitor. The reported Binance theft is considerably larger, making the latest incident another serious warning for the entire digital asset industry.
For smaller investors, it may be tempting to dismiss this as a problem that only affects billion-dollar exchanges. But the consequences can reach ordinary users through delayed withdrawals, market uncertainty and reduced confidence in centralized platforms. When a major exchange experiences a security crisis, the impact rarely stays within the company.
It also raises a question about how much responsibility people should place on exchanges to protect their assets. Keeping cryptocurrency on a trading platform is convenient, especially for people who buy and sell regularly. Holding assets in a personal wallet offers greater control, but it also means taking responsibility for private keys and recovery phrases. Neither approach is completely free of risk.
The Binance incident is a reminder that cryptocurrency security is not just about protecting wallets. It is about protecting the entire system surrounding them, including the people and devices that have access to sensitive operations.
The FBI has named the North Korean-linked operation. Investigators are following the stolen funds, companies have frozen some assets, and Binance is working through the aftermath. But several important questions remain unanswered. How exactly did the attackers gain access? Which security measures failed to stop the operation? And how much of the money can eventually be recovered?
Those answers matter more than another dramatic headline about billions disappearing.
Because the real test for Binance and the wider crypto industry will not be how quickly they respond to this particular attack. It will be whether they learn enough from it to make sure another exchange does not face the same situation a few months down the road.
Trust in cryptocurrency is difficult to build and remarkably easy to damage. This incident has given the industry another reason to prove that protecting customers' money is more than a promise.
#BinanceUpdatesProofofReservesAddresses #BinanceUpdatesProofofReservesAddresses #BinanceProcesses$4.65BWithdrawals